wpa_supplicant_8_CVE-2021-0326.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

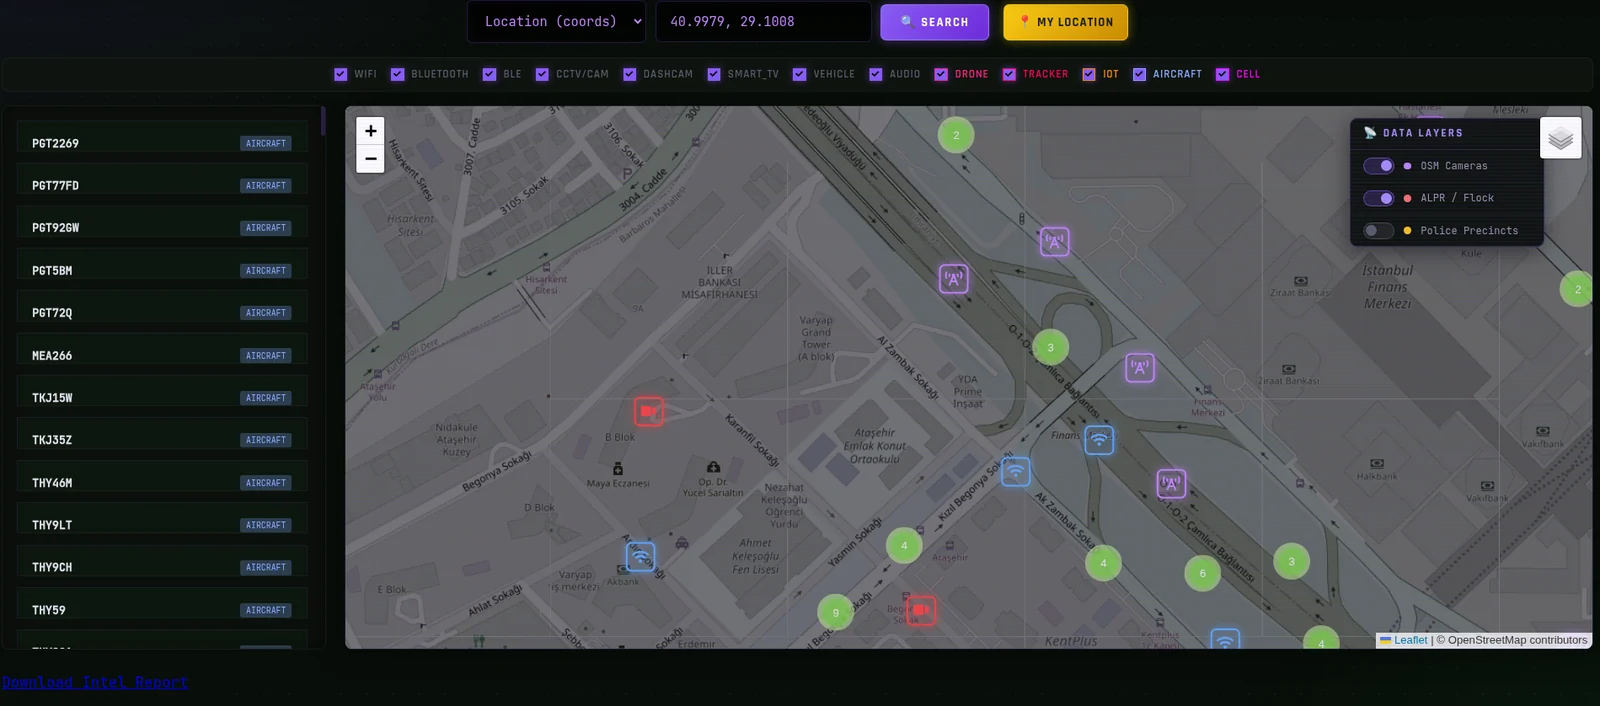
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

A full-featured open-source Wi-Fi fuzzer

Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…

Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.

IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…

Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…

Curated collection of proof-of-concept exploits for 16 CVEs targeting web applications (ASUS, D-Link, Netgear, TP-Link, Xiaomi) and Wi-Fi WPA3-SAE,…

Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.

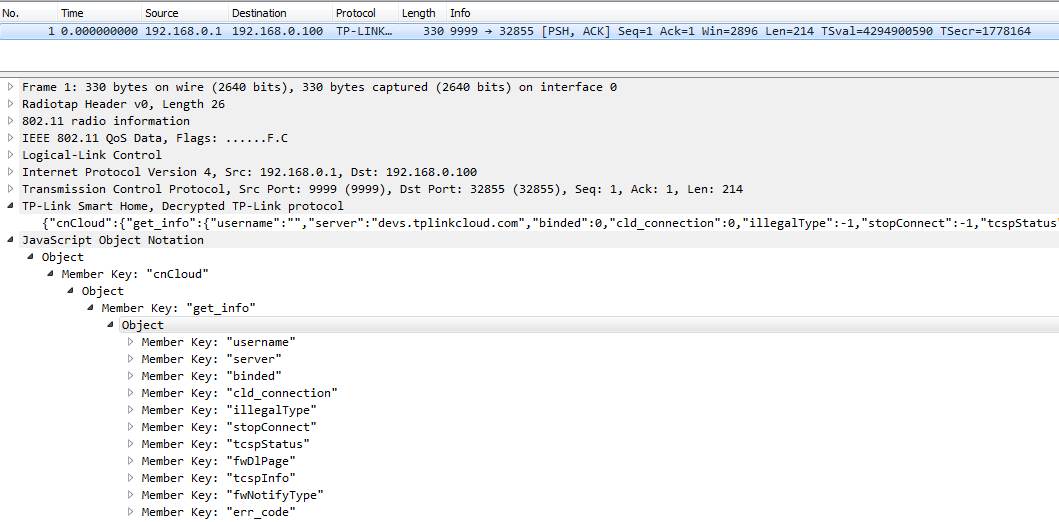
TP-Link WiFi SmartPlug Client and Wireshark Dissector

Reolink Duo 2 WiFi v1.0.280 - Account Enumeration Vulnerability


Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…

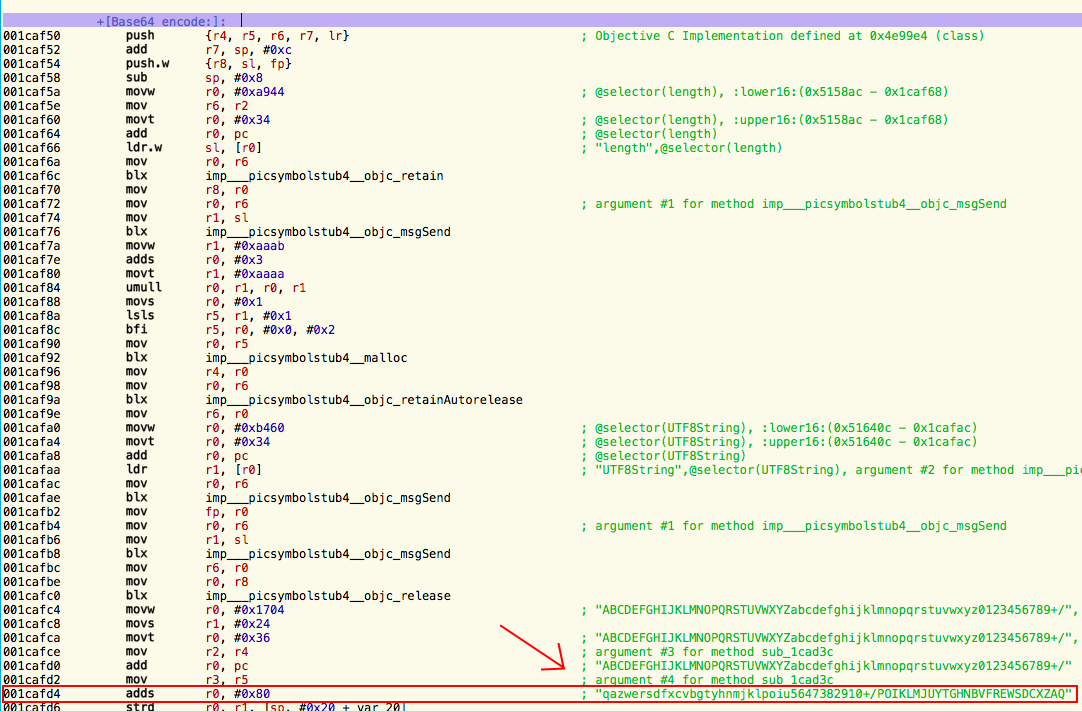
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…

📡🔍Searches for wifi-pineapple traces and calculate wireless network security score 🍍

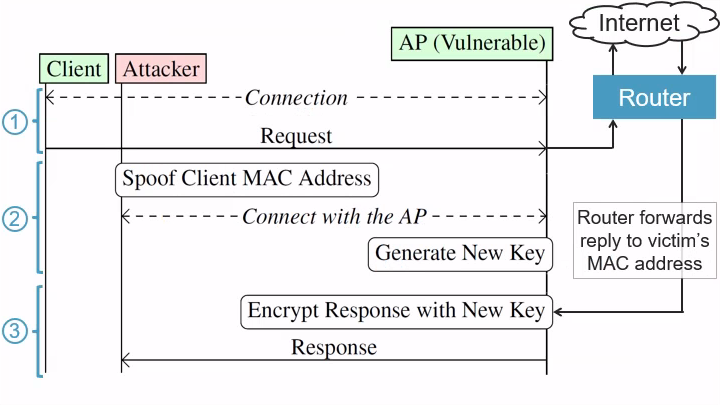
MacStealer: Wi-Fi Client Isolation Bypass

PoC vulnerability disclosures for consumer IoT cameras, detailing BLE buffer overflow and WiFi disassociation attacks that can take devices offline.

CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…