

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.9k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
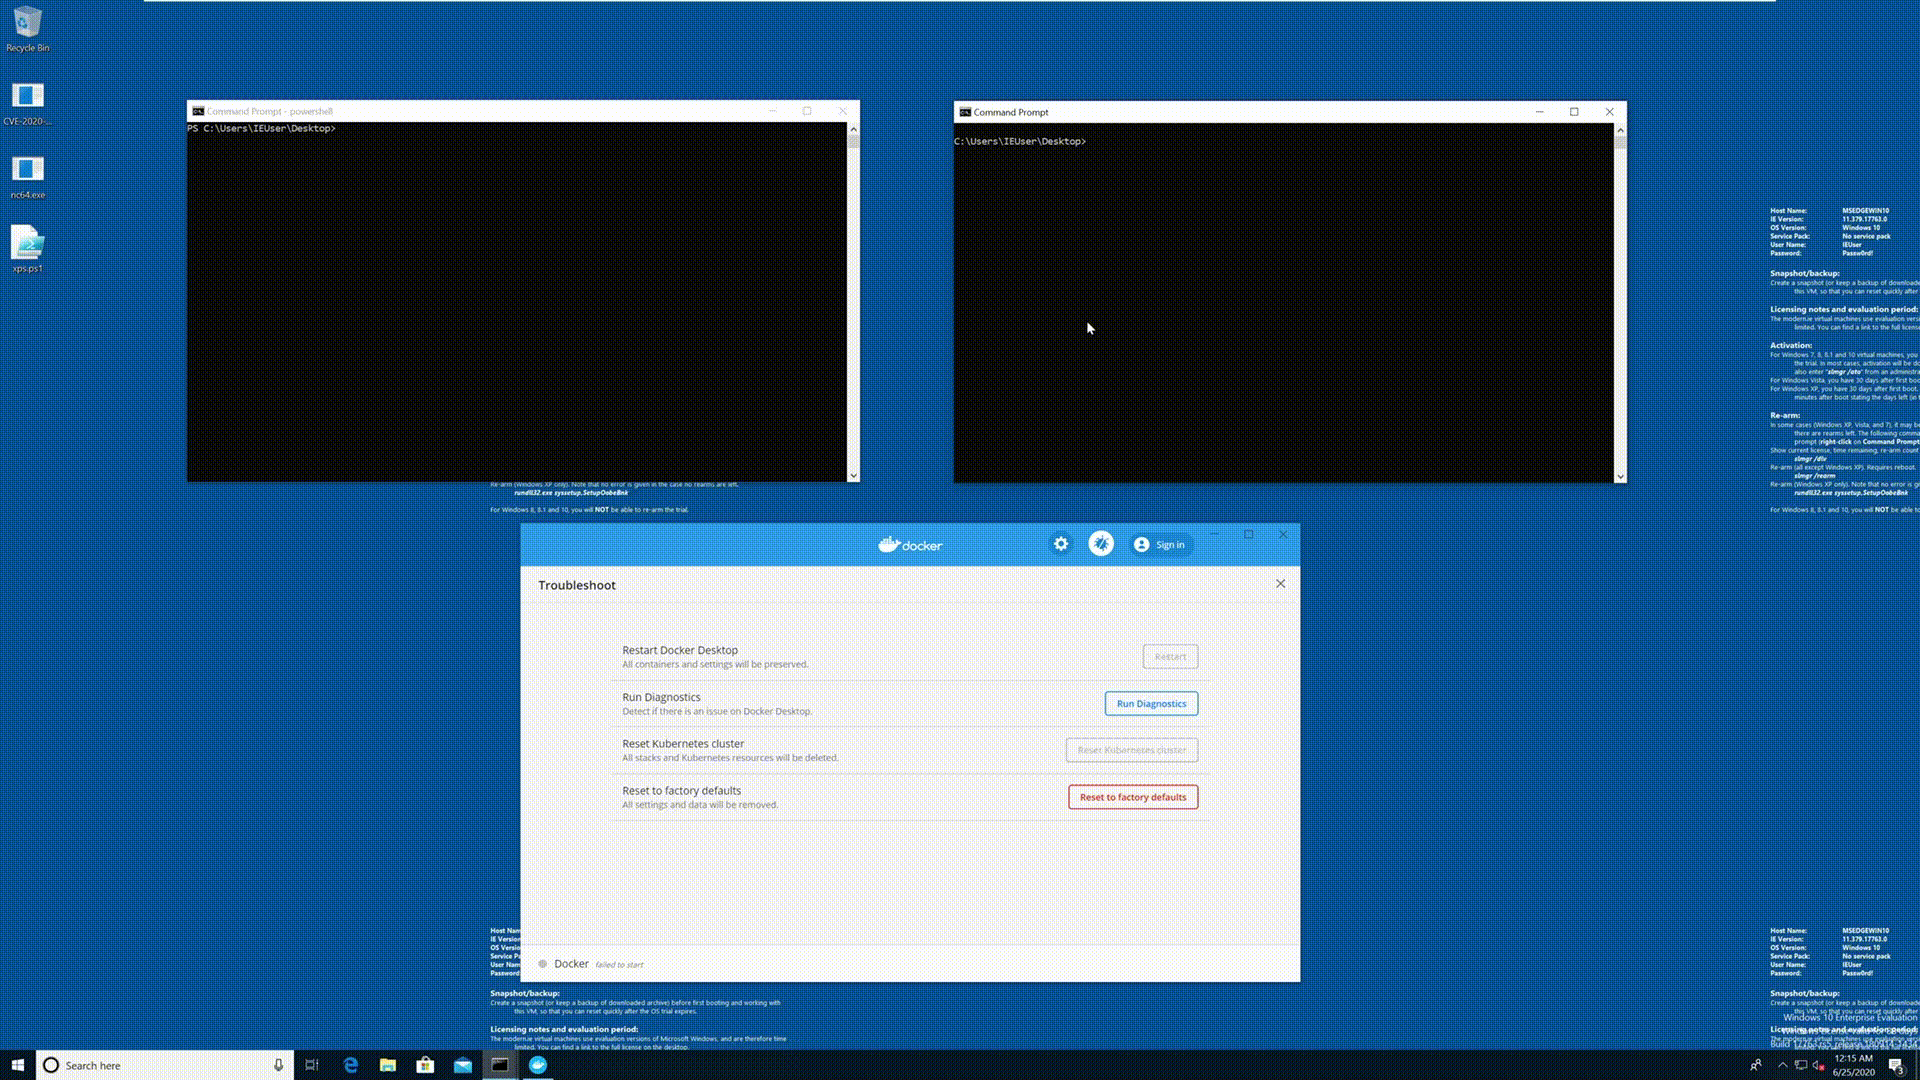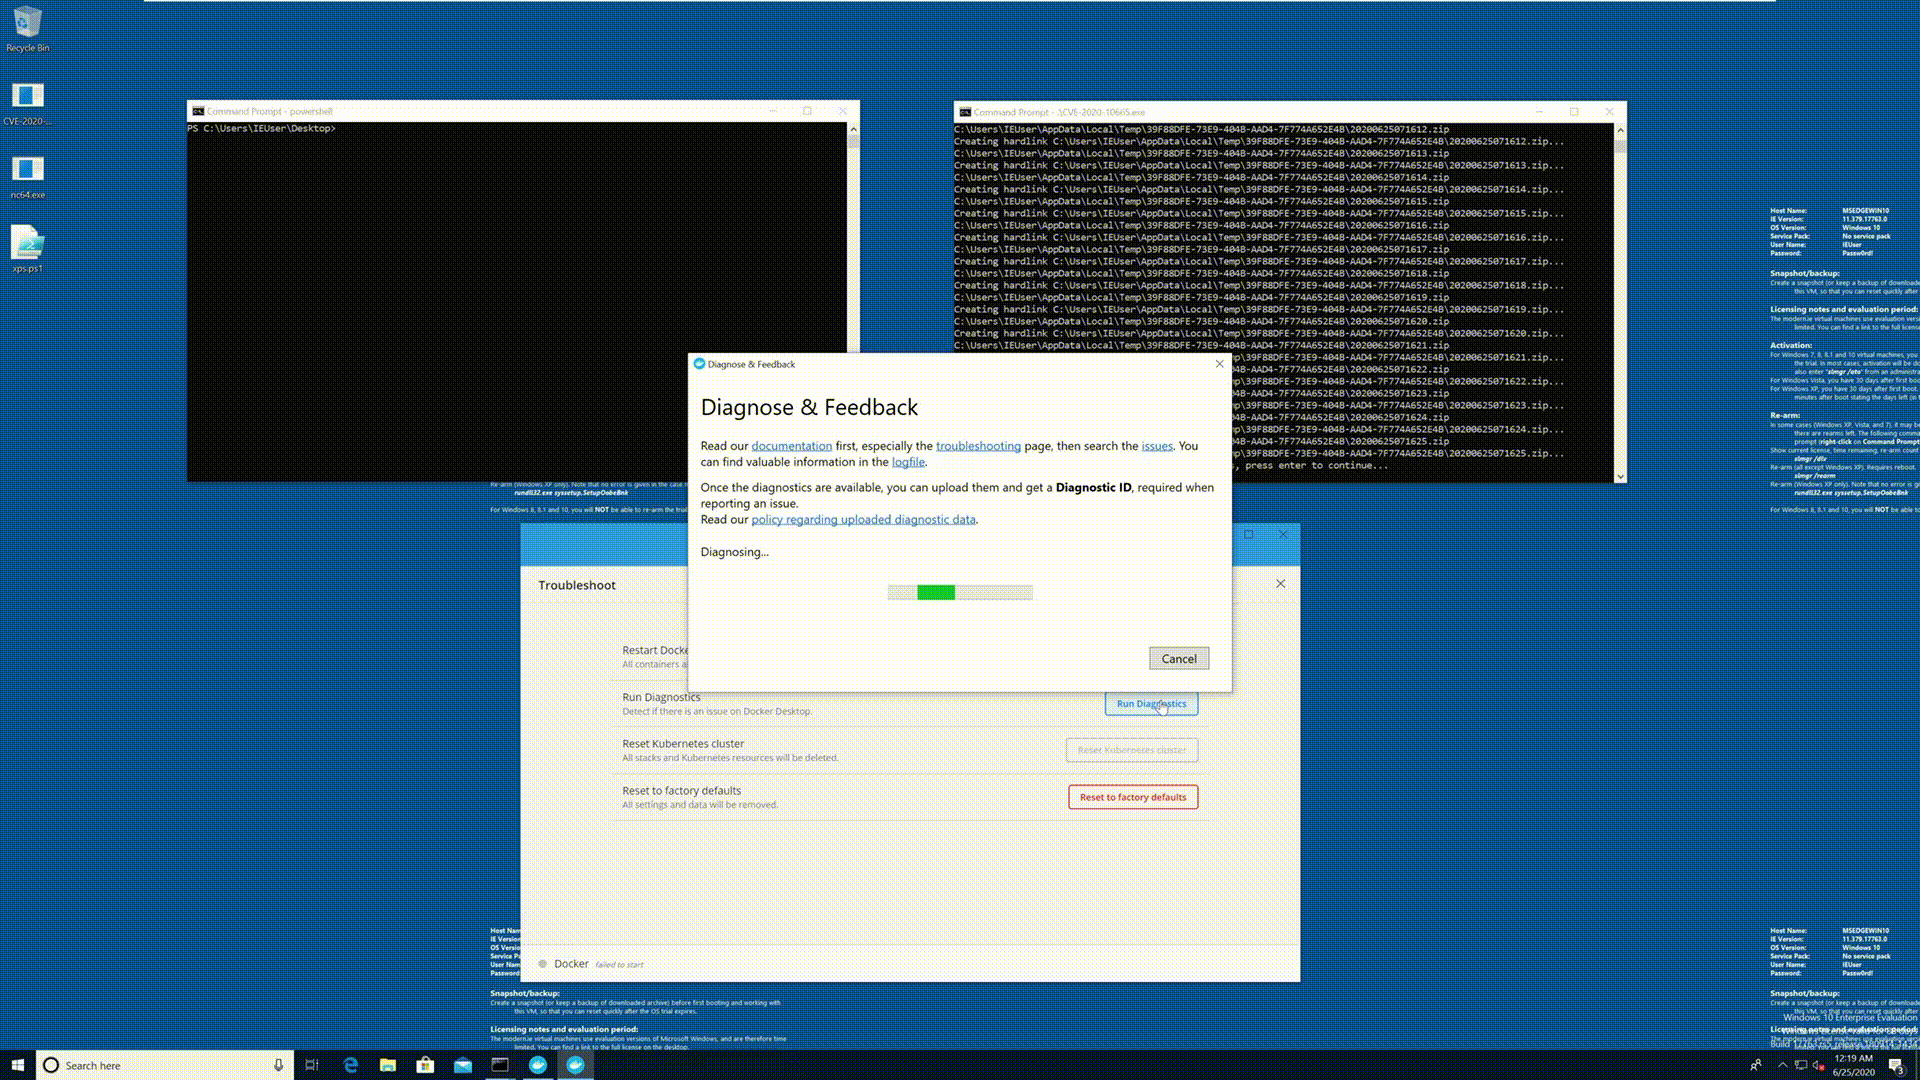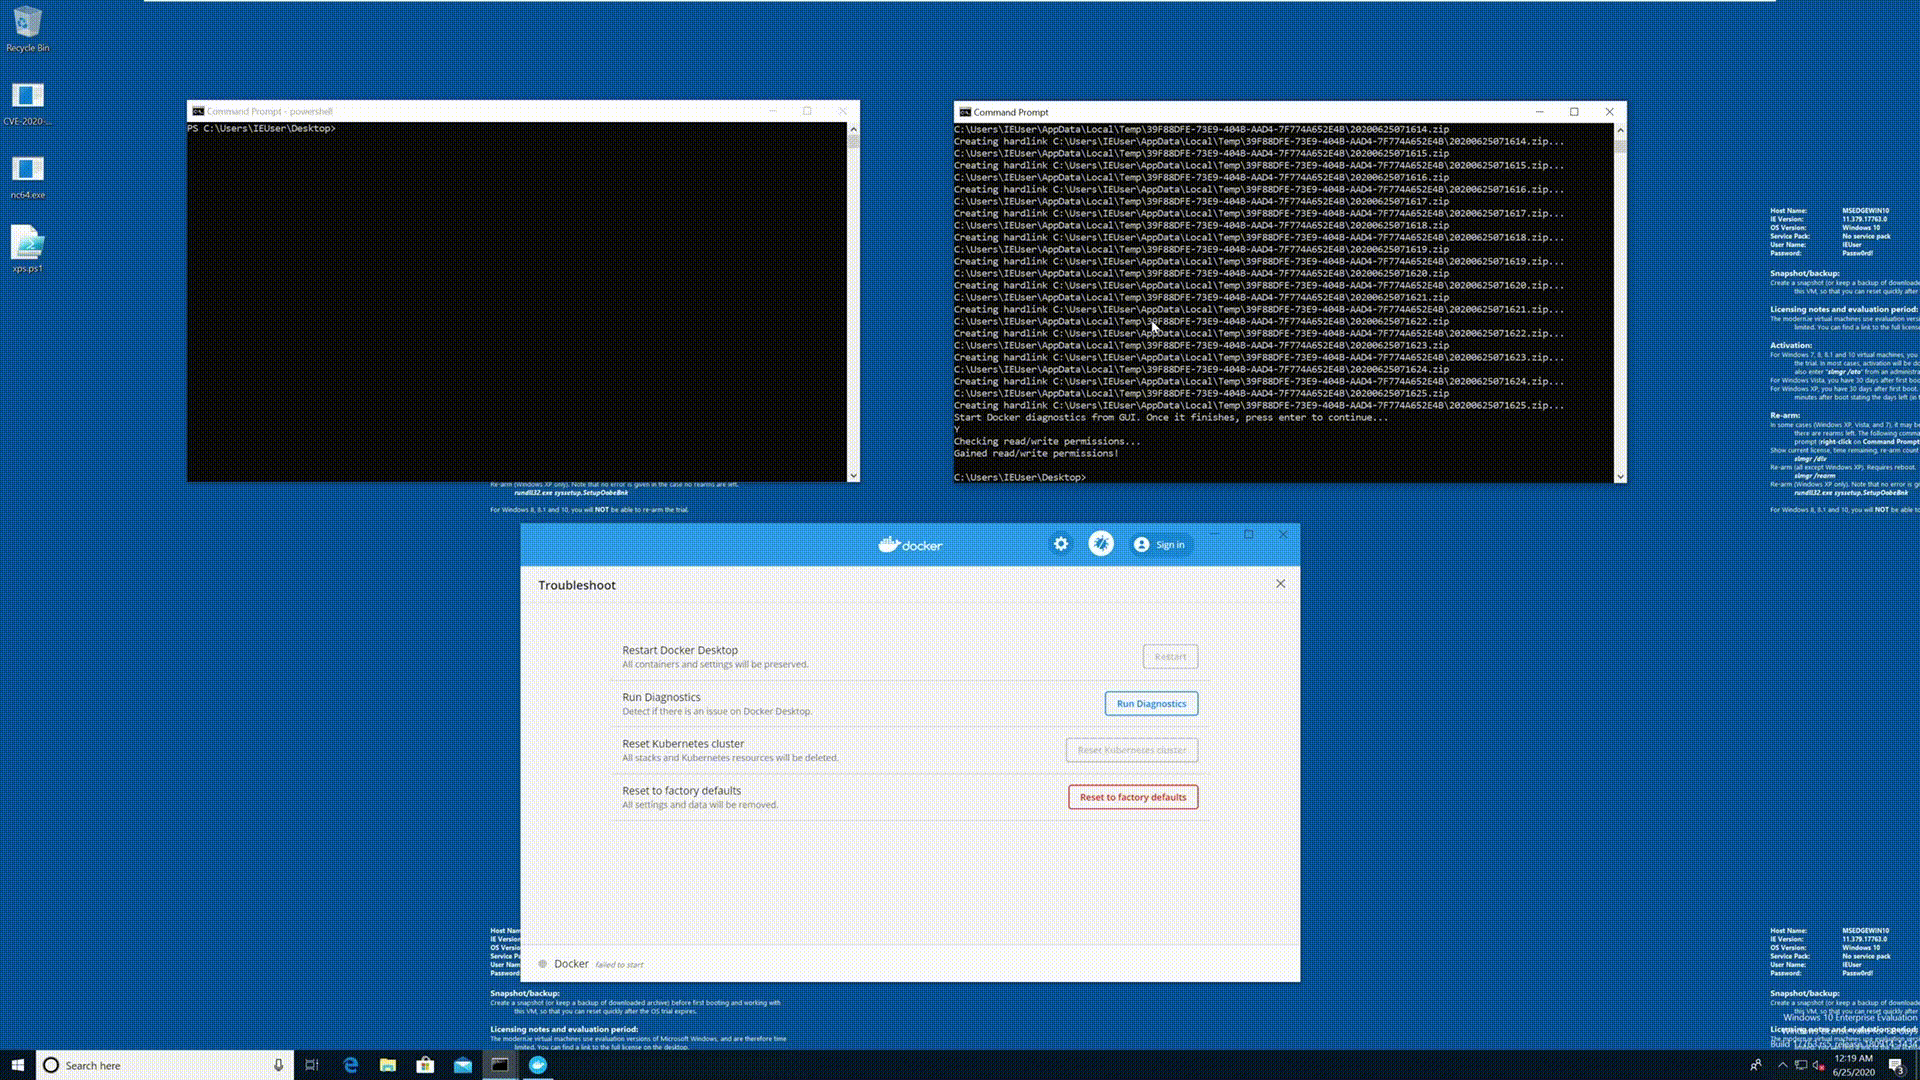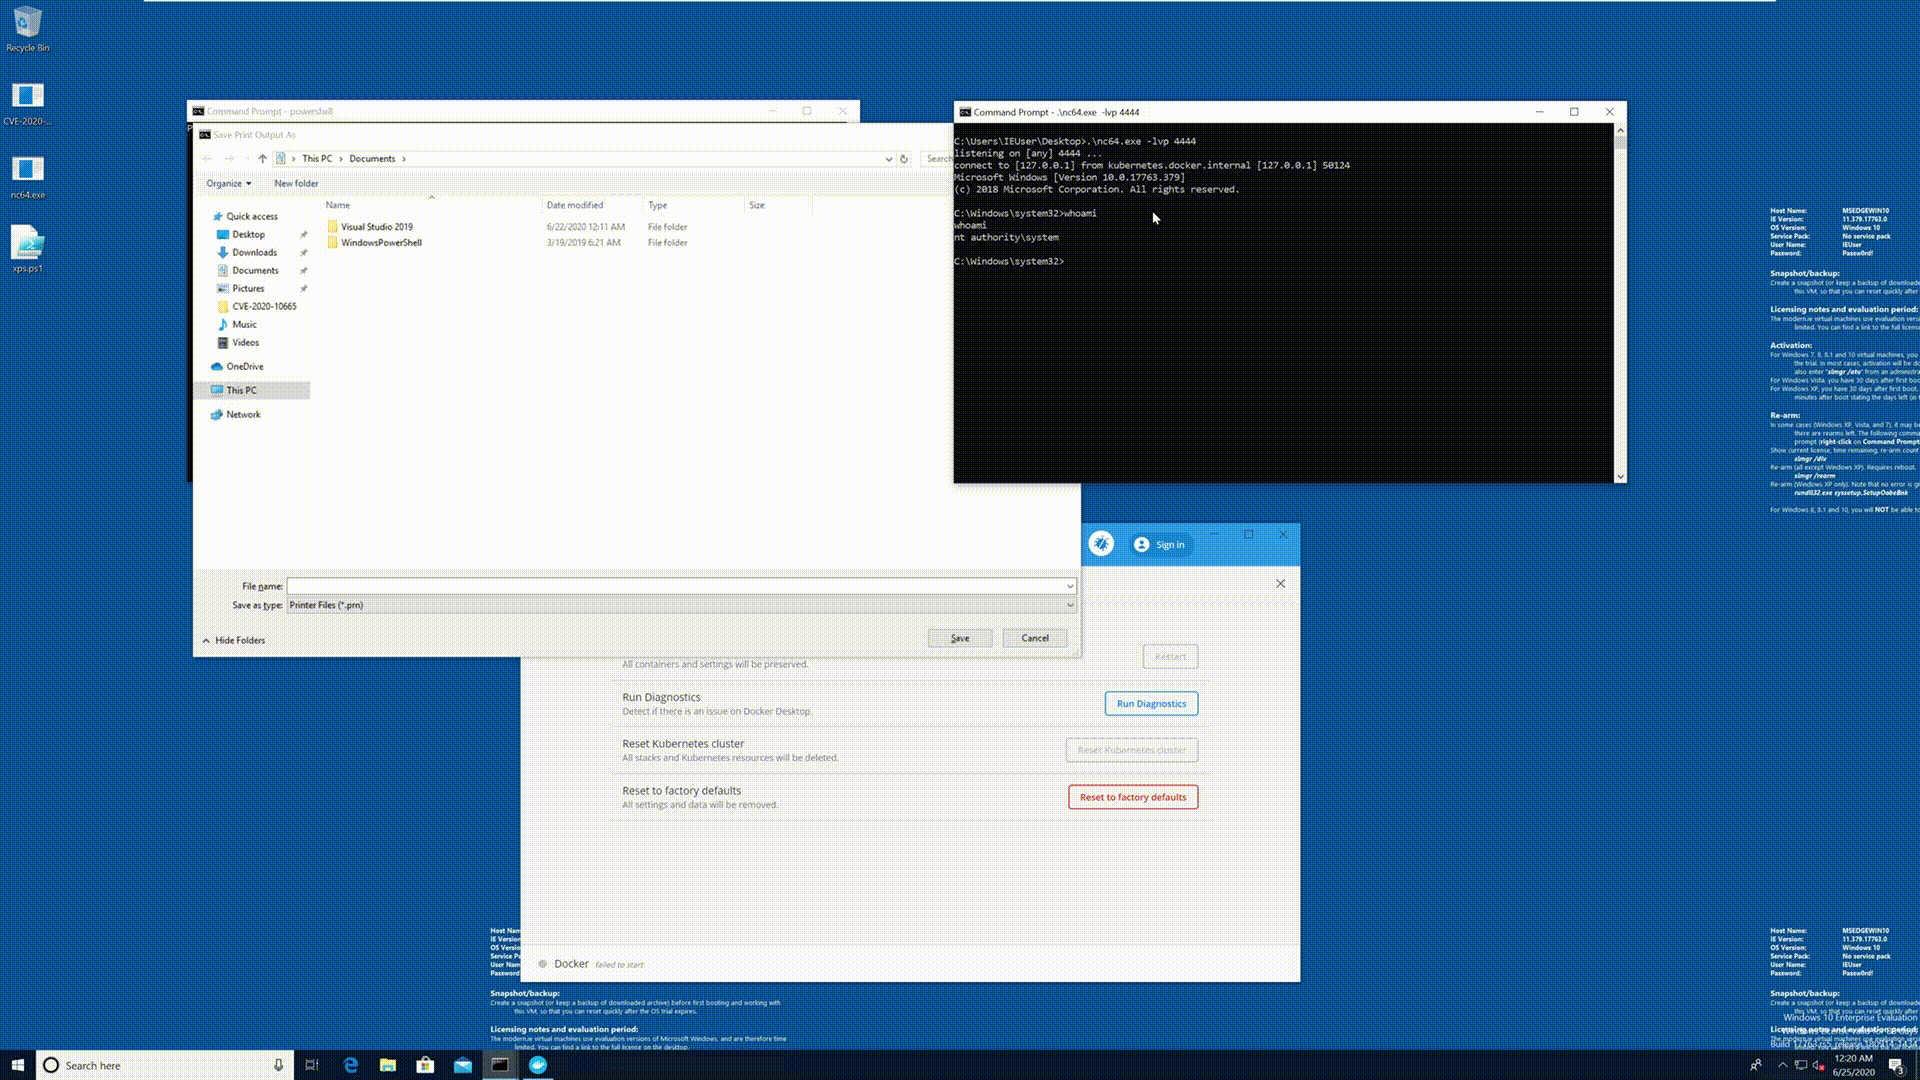 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 colton1skees/dna
LLVM based static binary analysis framework
 chuzoux/cve-2025-32433-exploit-edited
Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 mathisvickie/cve-2021-27965
stack based buffer overflow in MsIo64.sys, Proof of Concept Local Privilege Escalation to nt authority/system
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 rvn0xsy/cve_2020_0796_cna
Cobalt Strike AggressorScripts CVE-2020-0796
 axcheron/crestron_getsudopwd
Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices
 lsw29475/cve-2020-17057
Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
 seadragnol/cve-2024-29943
Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
 rt1252/cve-2021-34427
Windows POC for CVE-2021-34427 affecting Birt Viewer
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.