
CVE-2026-54390
 shinthink/cve-2026-54390
CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
exploitationpenetration-testingreconnaissance+2
shinthink/cve-2026-54390CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
 24520597-blip/cve-2026-999999
A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…
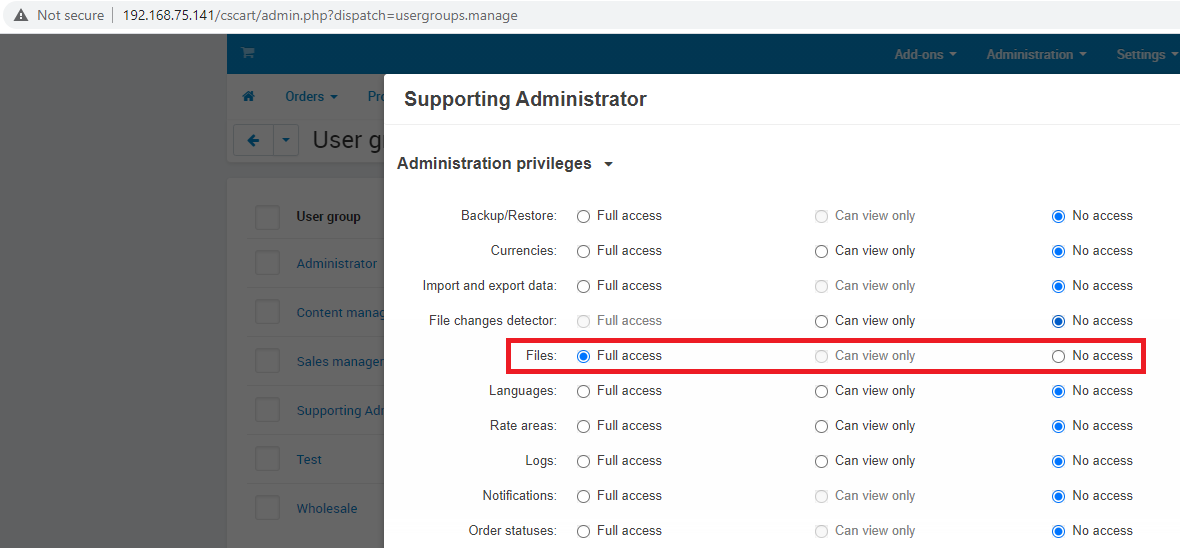 sourceincite/cve-2021-26121
Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
 drkbcn/lblfixer_cve_2023_28447
Module for PrestaShop 1.7.X to fix CVE-2023-28447 vulnerability (Smarty XSS)
 sbani/cve-2022-29221-poc
CVE-2022-29221 Proof of Concept Code - Smarty RCE
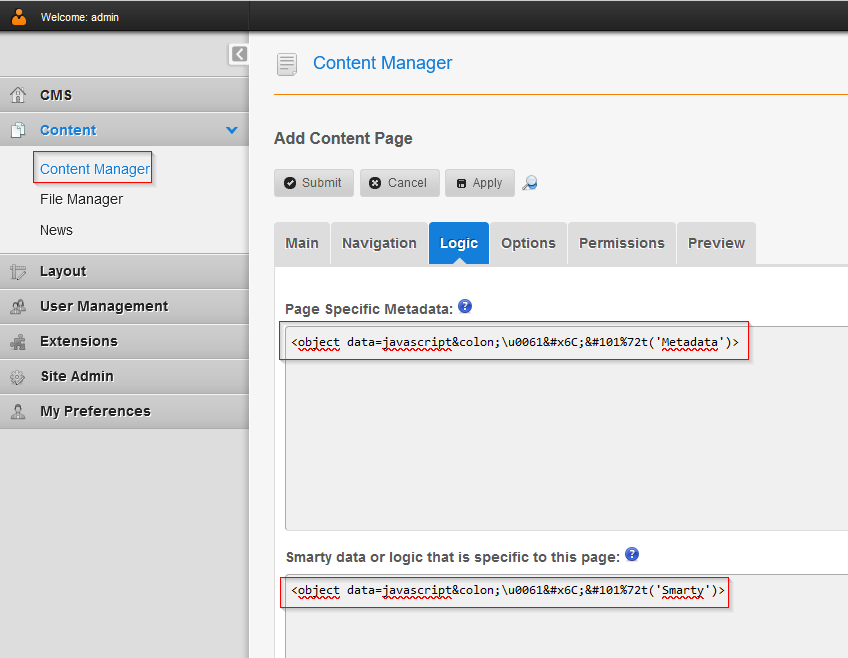 sromanhu/cve-2023-43359-cmsmadesimple-stored-xss----content-manager
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to Page Specific…