
PHP2SHELL-POC
 ghxstsec/php2shell-poc
Python exploit for CVE-2026-109618: abuses PHP session.upload_progress heap corruption to overwrite zend_call_function and achieve remote command…
exploitationpayload-generationpenetration-testing+2
2
ghxstsec/php2shell-pocPython exploit for CVE-2026-109618: abuses PHP session.upload_progress heap corruption to overwrite zend_call_function and achieve remote command…
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 jonaschen0103/cve-2026-33439-poc
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…
 liaomilk/cve-2025-69212-for-myself
just record for myself
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…

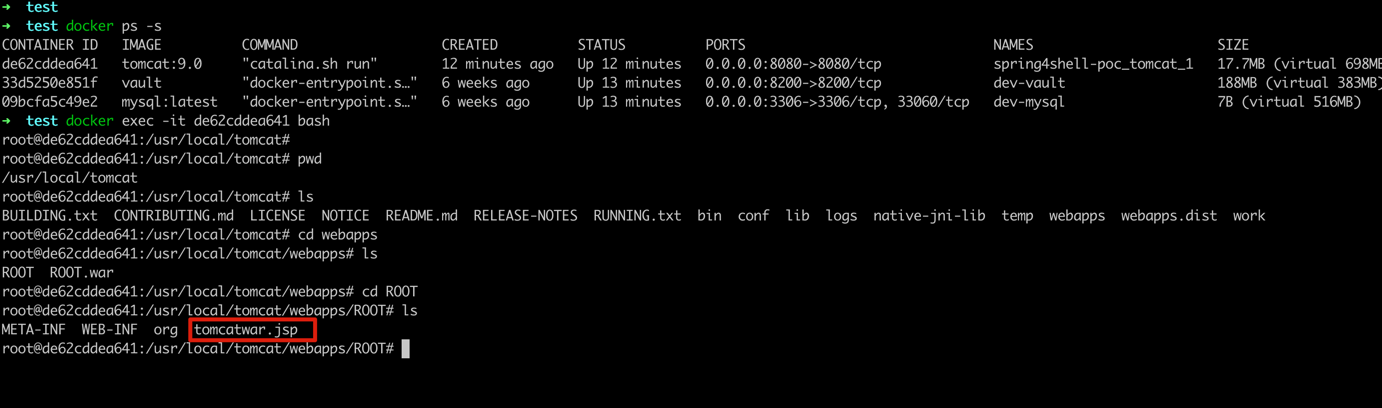 weijilab/spring4shell-poc
Reproduces the Spring4Shell (CVE-2022-22965) remote code execution vulnerability with a Python exploit script, deploying a JSP webshell on Apache…
 jas502n/cve-2019-11043
php-fpm+Nginx RCE
 ridter/cve-2018-15982_exp
exp of CVE-2018-15982
 zephrfish/cve-2024-3400-canary
Have we not learnt from HoneyPoC?
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 ovi3/cve_2021_27850_poc
Apache Tapestry CVE-2021-27850 PoC