wpa_supplicant_8_CVE-2021-0326.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

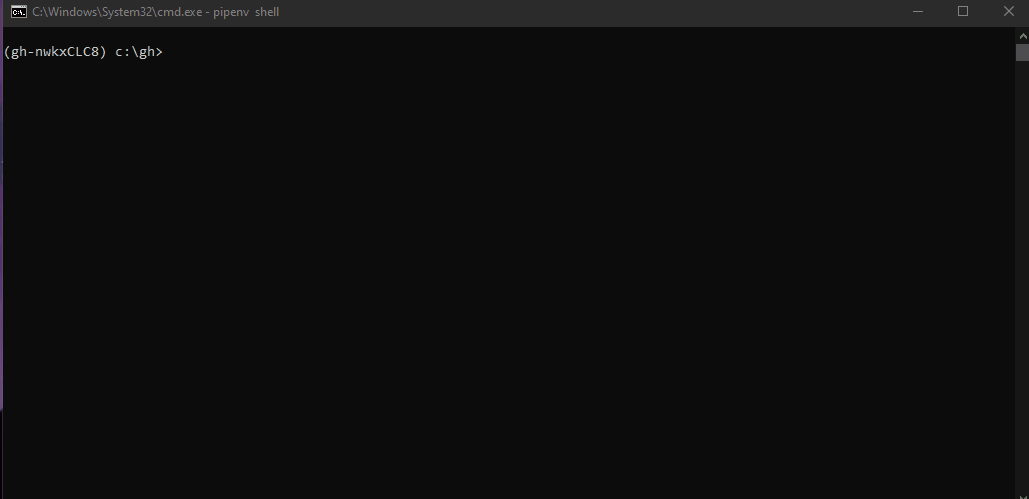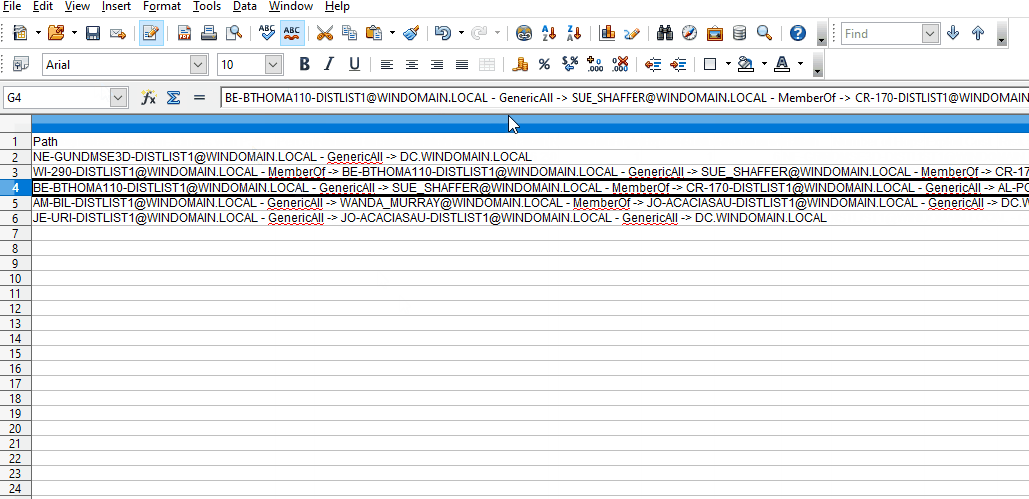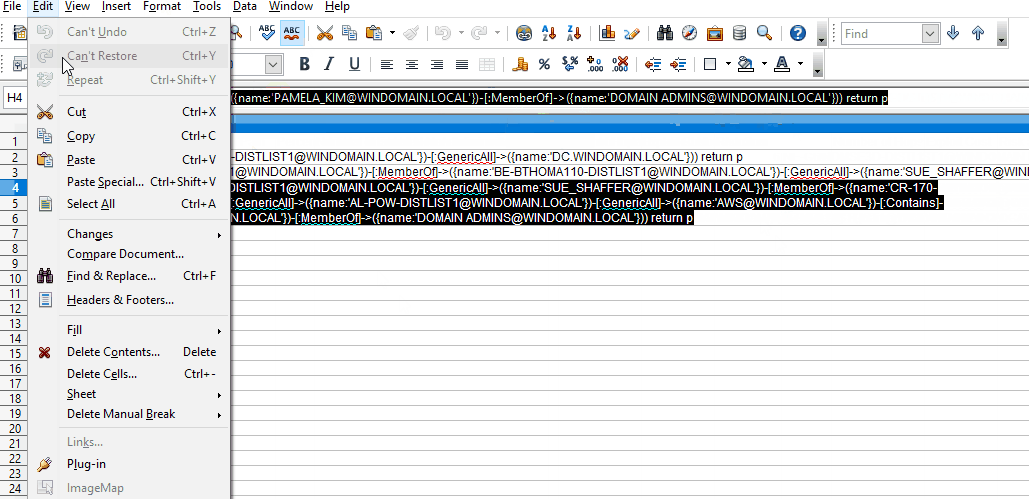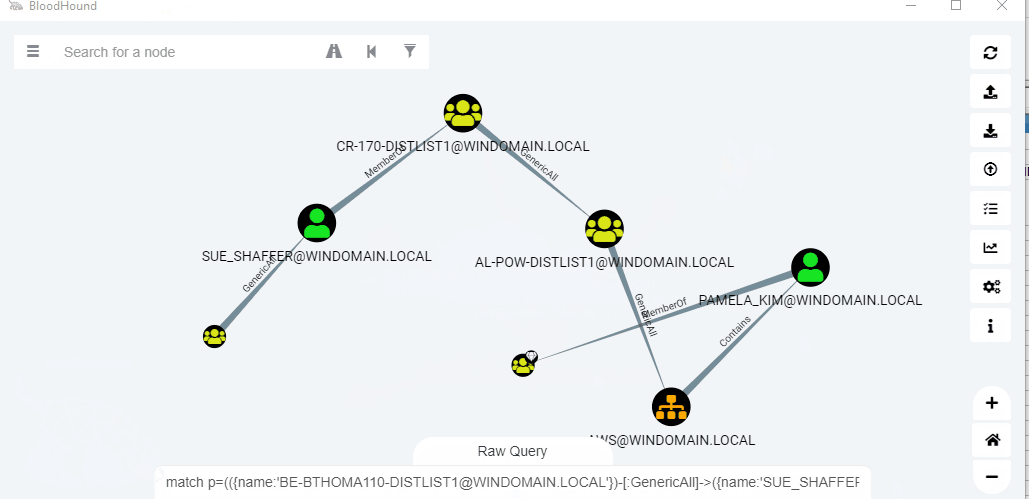
Uses Sharphound, Bloodhound and Neo4j to produce an actionable list of attack paths for targeted remediation.

Open Source Deep Packet Inspection Software Toolkit

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

Geoserver RCE


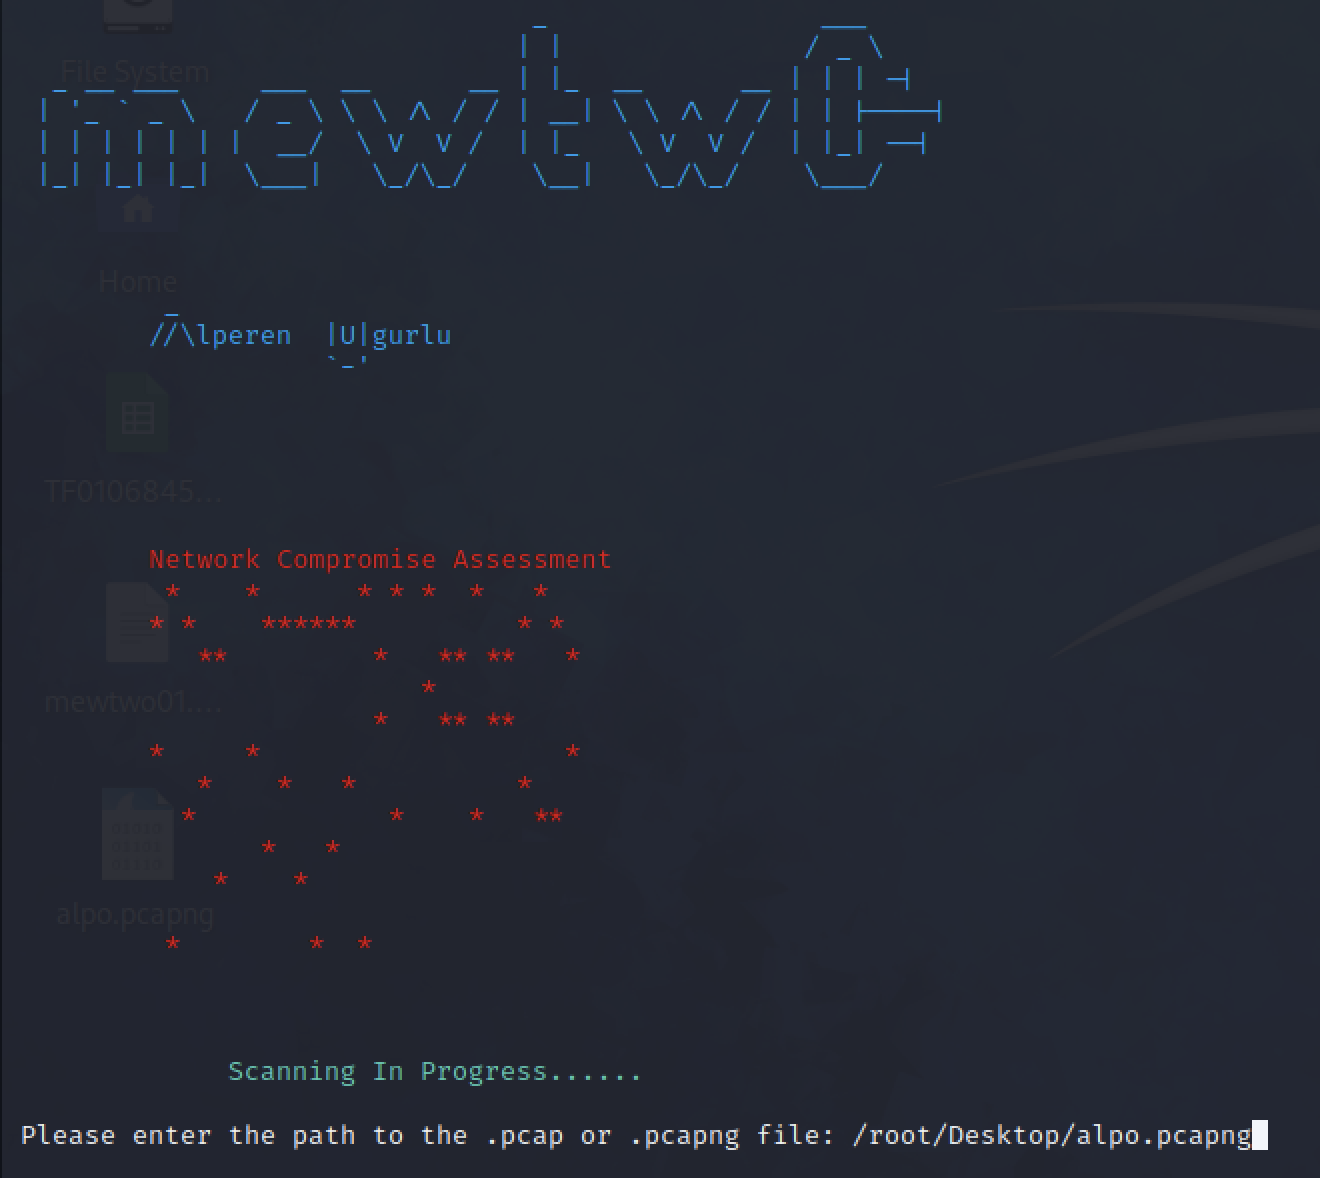
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…

UPnP Pentest Toolkit for Windows

The porte_plume plugin used by SPIP before 4.30-alpha2, 4.2.13, and 4.1.16 is vulnerable to an arbitrary code execution vulnerability. A remote and…

Proof-of-concept exploit for CVE-2024-48307, a SQL injection vulnerability in the Jeecg-Boot getDictItemsByTable API. Supports single and batch URL…

Proof-of-concept exploit for CVE-2022-31793 with IP/file-based target scanning, validation mode, and arbitrary file read via HTTP requests.

Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…

Proof-of-concept for CVE-2021-21972, a remote code execution vulnerability in vCenter Server 6.5-7.0. Verifies vulnerable paths without exploitation.

Filechucker filter bypass Proof Of Concept

VMware Workspace ONE Access and Identity Manager RCE via SSTI - Test script for shodan, file or manual.

Proof-of-concept exploit for CVE-2022-22954, a critical server-side template injection in VMware Workspace ONE Access. Enables remote code execution…

Detects subdomain takeover vulnerabilities by analyzing DNS records and HTTP responses. Automatically identifies takeover-prone subdomains for…

Automated scanner and exploit tool for CVE-2021-26855 targeting Microsoft Exchange servers, enabling remote code execution on vulnerable instances…