
tcpdump
 the-tcpdump-group/tcpdump
the TCPdump network dissector
dns-analysisforensicslog-analysis+5
3.2k2 days ago
the-tcpdump-group/tcpdumpthe TCPdump network dissector
 motikan2010/cve-2021-34646
CVE-2021-34646 PoC
 ishwardeepp/cve-2025-26794-exim-mail-sqli
Exploit for CVE-2025-26794, a SQL injection vulnerability in Exim Mail Server. Provides proof-of-concept code for testing and exploitation of the…
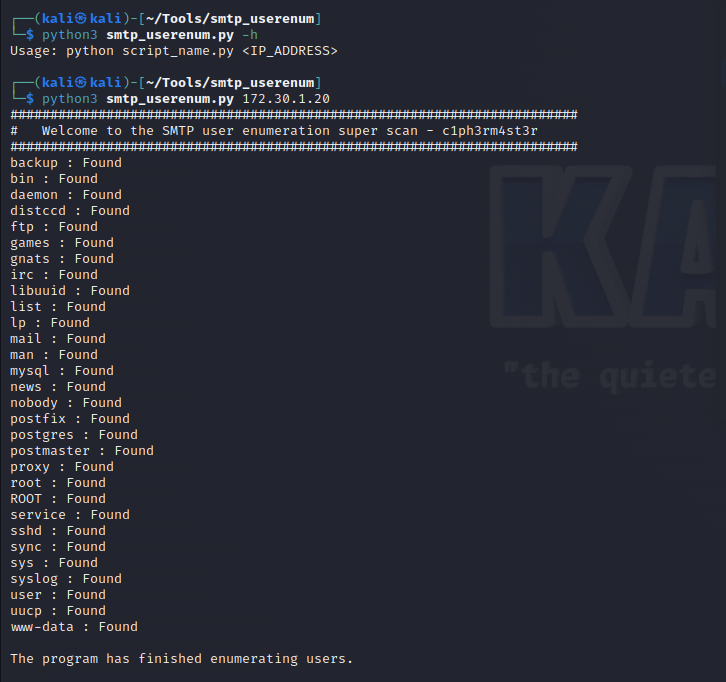 h3x0v3rl0rd/smtp_userenum
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
 rootdirective-sec/cve-2026-8206-lab
Local Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…
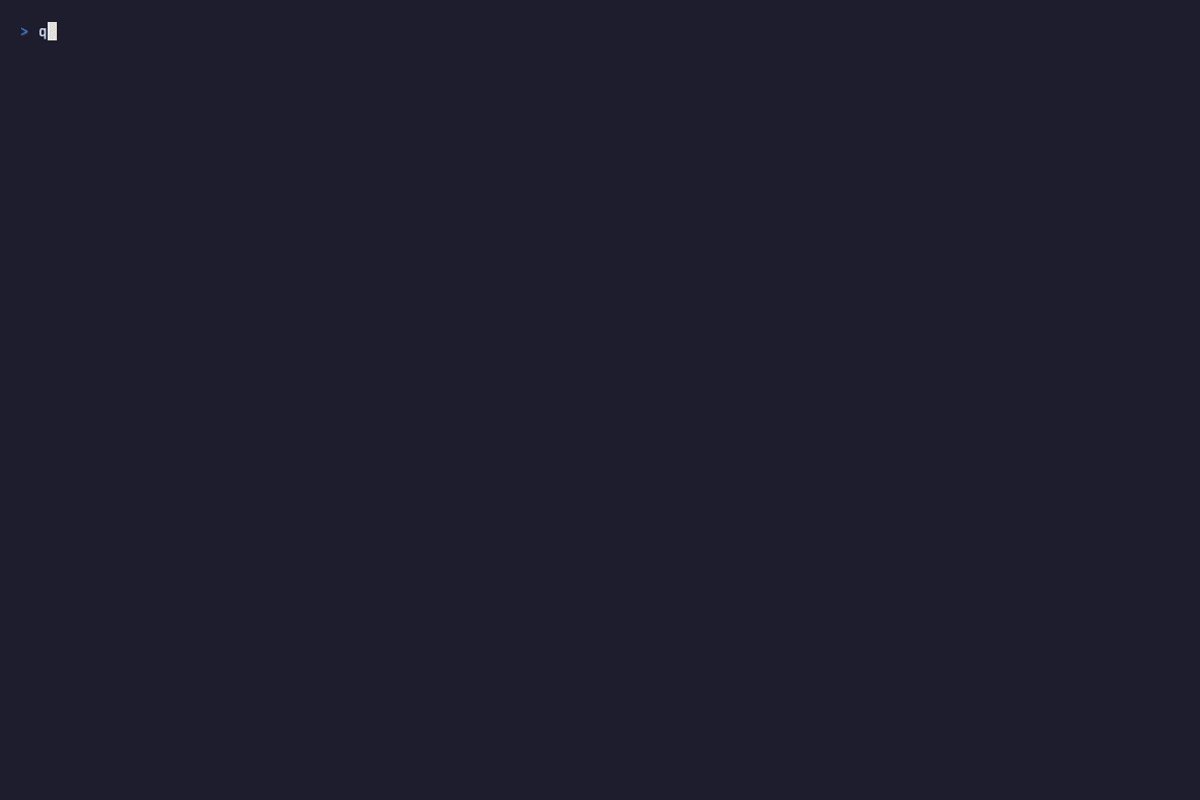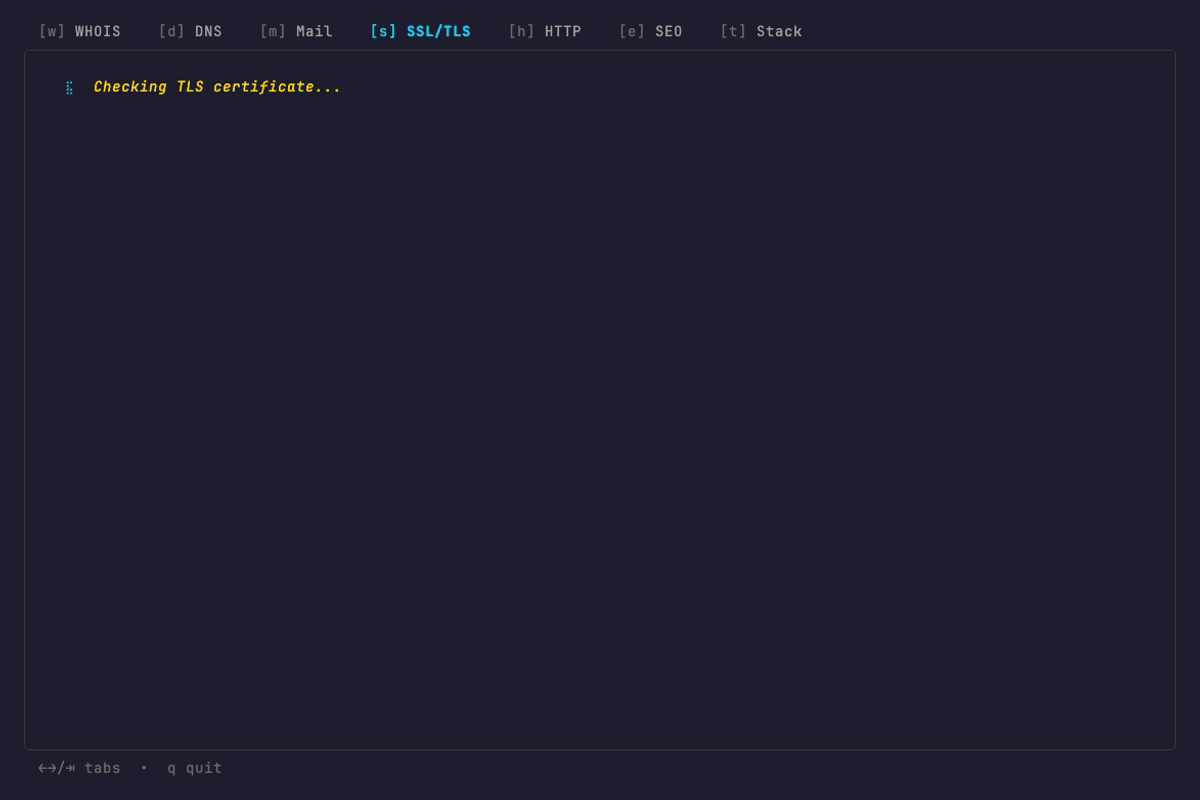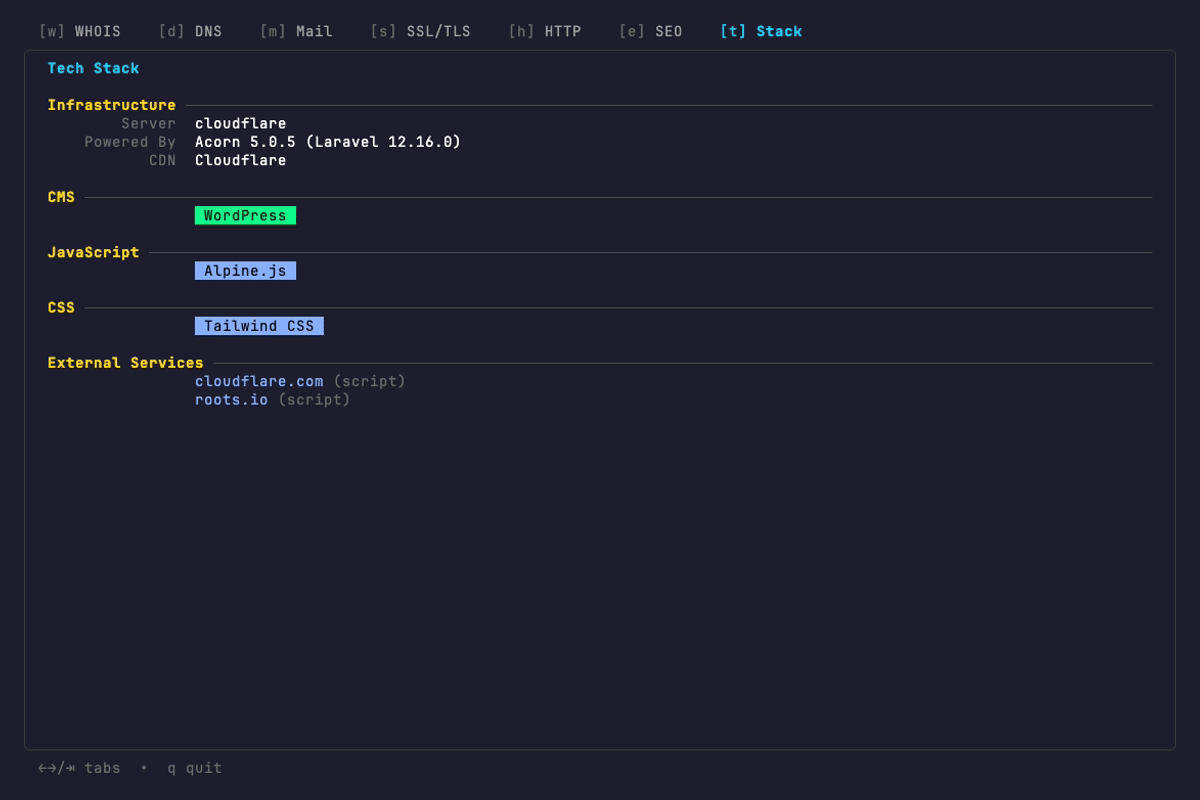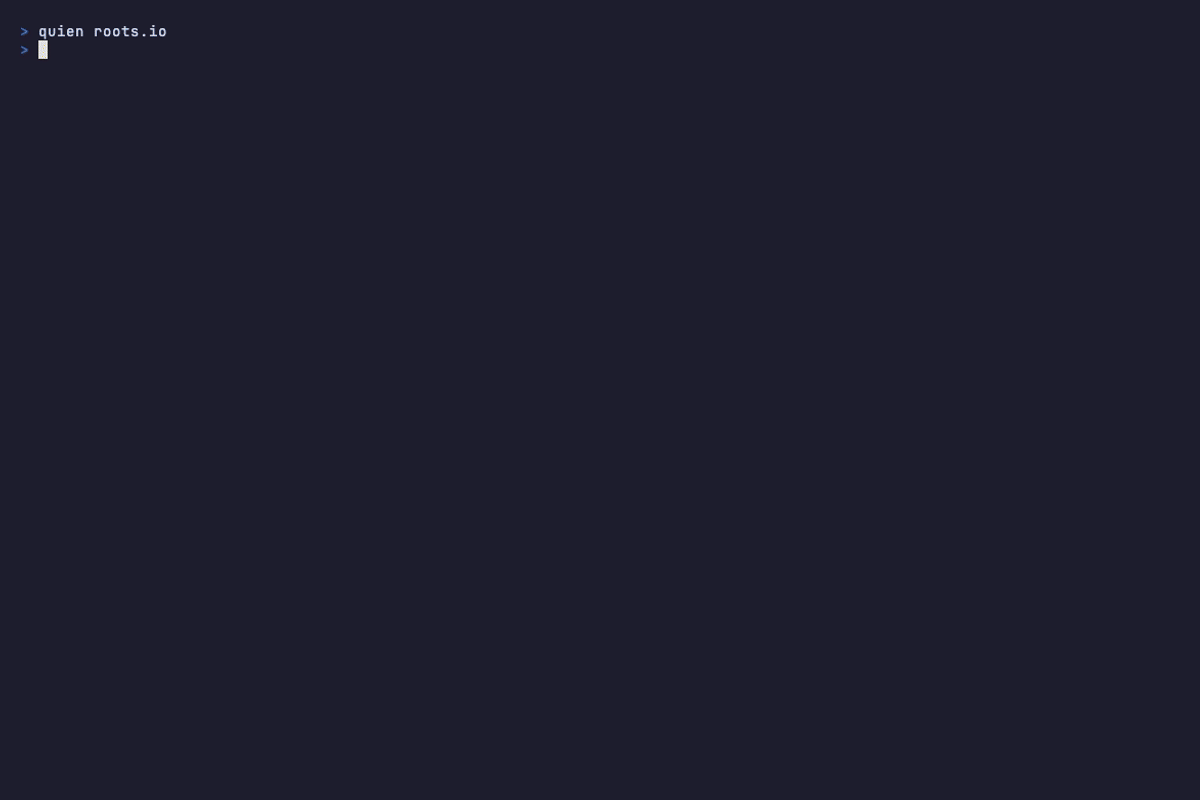 retlehs/quien
A better whois and domain intelligence toolkit
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 demossl/cve-2021-33766-proxytoken
Proof-of-concept exploit for CVE-2021-33766 (ProxyToken) authentication bypass in Microsoft Exchange Server. Supports single and batch target…
 george0papasotiriou/cve-2026-8080-dkim-signature-verification-bypass-header-canonicalization-flaw-
Simulated Python demonstration of CVE-2026-8080 DKIM verification bypass, showing how non-compliant header canonicalization lets attackers inject…
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
 themalwareguardian/cve-2003-0264
Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.
 cscli/cve-2017-5223
Proof-of-concept exploit for CVE-2017-5223 demonstrating arbitrary file read via PHPMailer's attachment and email content injection.
 cr4ckc4t/cve-2022-41352-zimbra-rce
Zimbra <9.0.0.p27 RCE
 t0kx/exploit-cve-2016-9920
Roundcube 1.0.0 <= 1.2.2 Remote Code Execution exploit and vulnerable container
 h4x0r-dz/cve-2021-26855
PoC exploit for CVE-2021-26855 (Exchange Server SSRF) with user enumeration, mail header reading, and vulnerability detection. Supports…
 wowfunhappy/fix-apple-mail-cve-2020-9922
Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
 abraxas/cve-2026-84753
Proof-of-concept exploit and lab for CVE-2026-84753, an unauthenticated PHP Object Injection in Mail Mint <= 1.31.0 via the mint-form-submit REST…