
cve-2020-16012
 aleksejspopovs/cve-2020-16012
PoC for CVE-2020-16012, a timing side channel in drawImage in Firefox & Chrome
exploitationinformation-gatheringreconnaissance+2
aleksejspopovs/cve-2020-16012PoC for CVE-2020-16012, a timing side channel in drawImage in Firefox & Chrome
 alecblance/s3bucketlist
Chrome and Firefox extension that lists Amazon S3 Buckets while browsing
 defineid/palimpsest
CVE-2026-74945, Uninitialized heap disclosure via a crafted web font (sec-high)
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…
 sneakynachos/cve-2026-84118-who-labeled-the-crit-as-a-high
Proof-of-concept for CVE-2026-84118, a SpiderMonkey GC use-after-free leading to out-of-bounds read/write and potential code execution. Includes…
 dangokyo/cve-2016-9079
Proof-of-concept exploit for CVE-2016-9079 targeting Firefox on Ubuntu x64, demonstrating a use-after-free vulnerability in the SVG animation…
 leopoldabgn/cve-2020-16012-poc
PoC for CVE-2020-16012, a timing side channel in drawImage in Firefox & Chrome
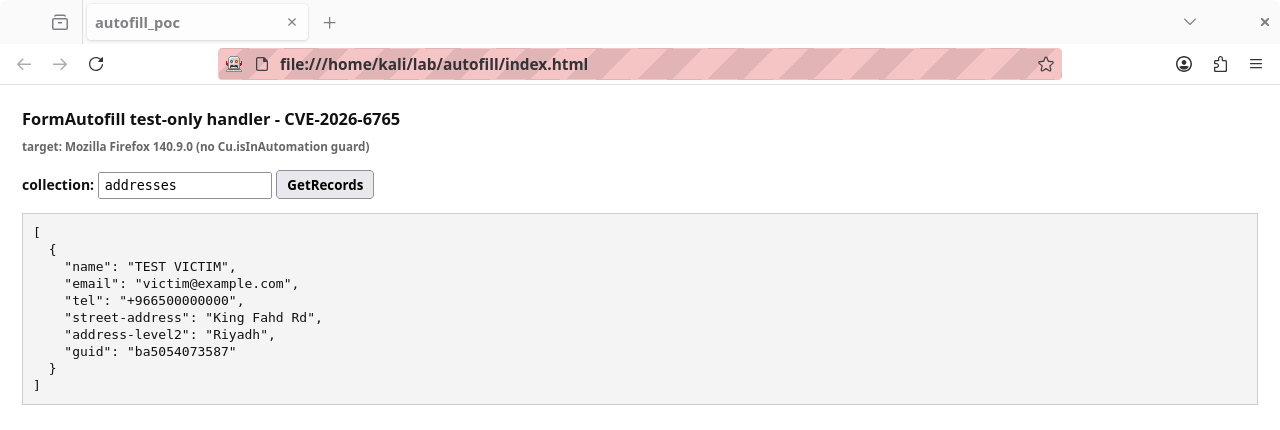 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
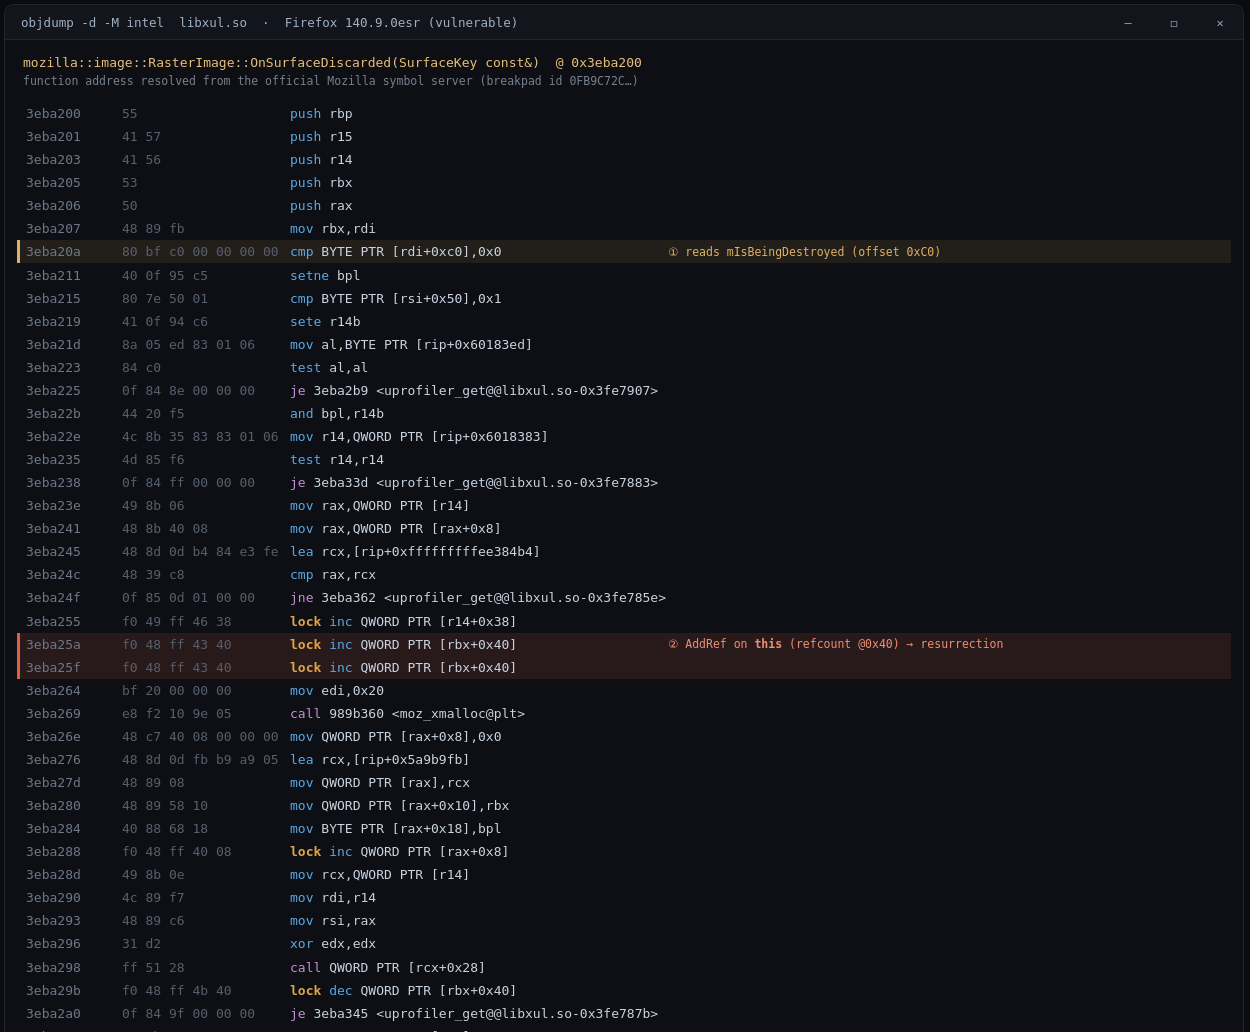 defineid/revenant
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
 sophoslabs/cve-2018-18500
PoC for CVE-2018-18500 - Firefox Use-After-Free
 sneakynachos/cve-2026-12295-uxxs-in-my-wasm
Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 vigneshsrao/cve-2019-11707
Exploit code for CVE-2019-11707 on Firefox 66.0.3 running on Ubuntu
 crixpwn/cve-2026-8389
Technical analysis and proof-of-concept exploit for CVE-2026-8389, a SpiderMonkey BaselineJIT type confusion vulnerability in Firefox, demonstrated…
 argp/cve-2011-3026-firefox
Example of exploiting CVE-2011-3026 on Firefox (Linux/x86)
 praiseimafidon/version_vulnerability_scanner
A vulnerability scanner for Firefox and Thunderbird that checks if your versions are out of date and susceptible to CVE-2024-9680.