wpa_supplicant_8_CVE-2021-0326.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.

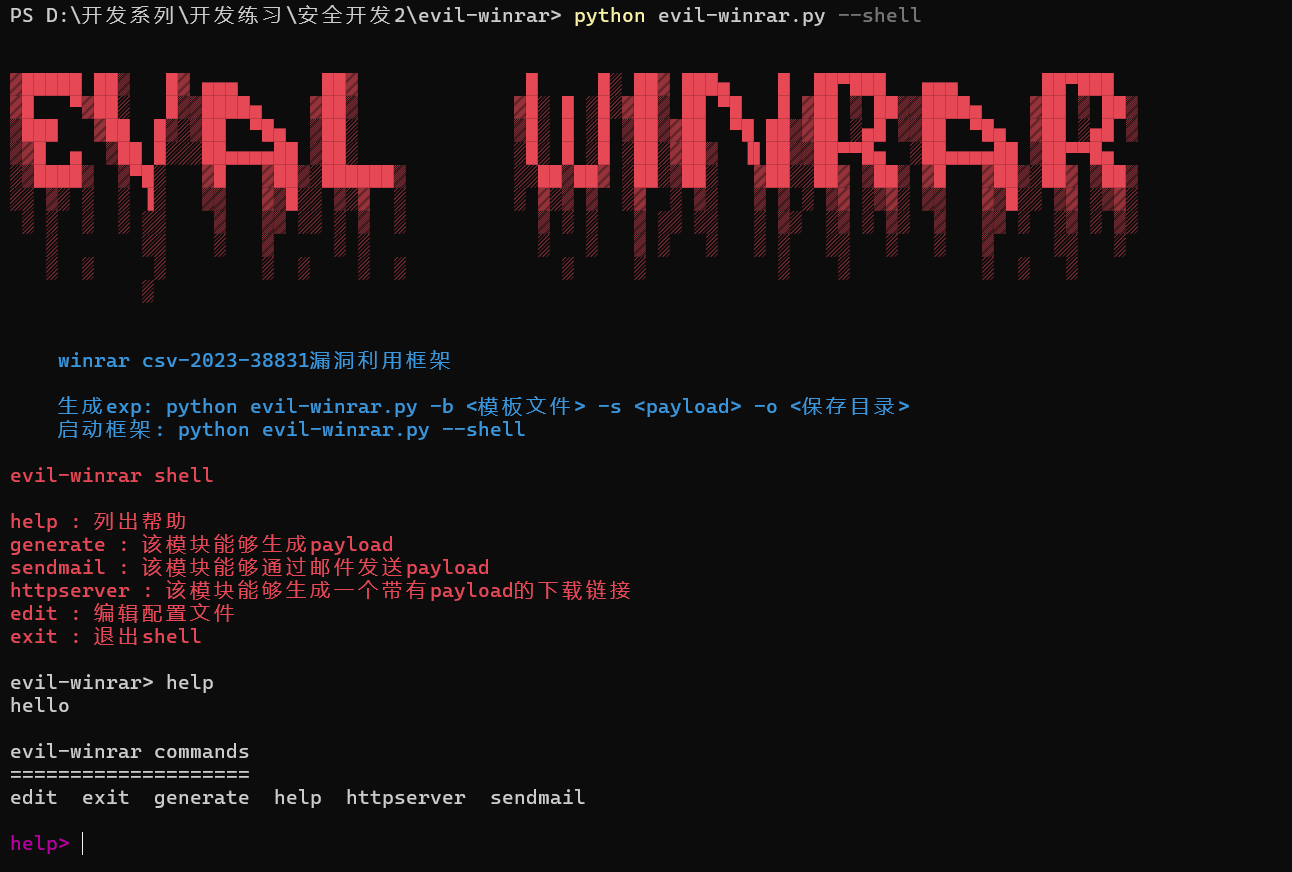
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)

Proof of Concept for CVE-2021-1585: Cisco ASA Device Manager RCE

The Demo for CVE-2017-11427

Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.

CVE-2023-38831 winrar exploit generator

CVE-2019-5010 Exploit PoC - Python Denial of Service via Malformed X.509v3 Extension

Explore CVE-2022-41741 with the Evil MP4 repository. It offers educational PoCs,and documentation on securing nginx against MP4 file vulnerabilities.…

Proof-of-concept exploit for CVE-2025-1562, a WordPress plugin activation vulnerability allowing remote code execution via crafted REST API requests.

An evil RMI server that can launch an arbitrary command. May be useful for CVE-2021-44228

Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…

Python exploit for Moodle Evil Teacher vulnerability (CVE-2018-1133) enabling authenticated remote command execution with proxy support.

Python-based exploit generator for CVE-2023-38831 WinRAR vulnerability. Creates malicious RAR archives with bait files (PDF, images) and payload…

Don't be evil.


Spring Cloud Gateway < 3.0.7 & < 3.1.1 Code Injection (RCE)