
docker-onion-nmap
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
container-securitydns-analysisinformation-gathering+8
542
milesrichardson/docker-onion-nmapScan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 cybersecsi/raudi
A repo to automatically generate and keep updated a series of Docker images through GitHub Actions.
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 sensepost/dwn
d(ockerp)wn - a docker pwn tool manager
 thirdbyte/ssj
Your everyday Linux distribution gone Super Saiyan.
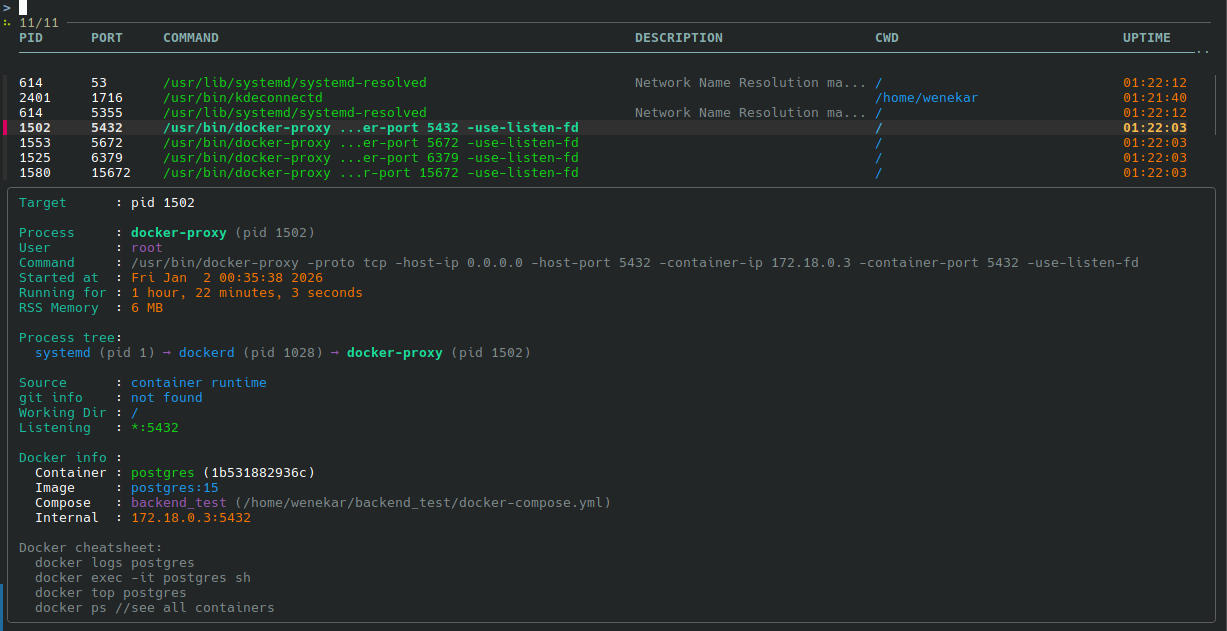 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
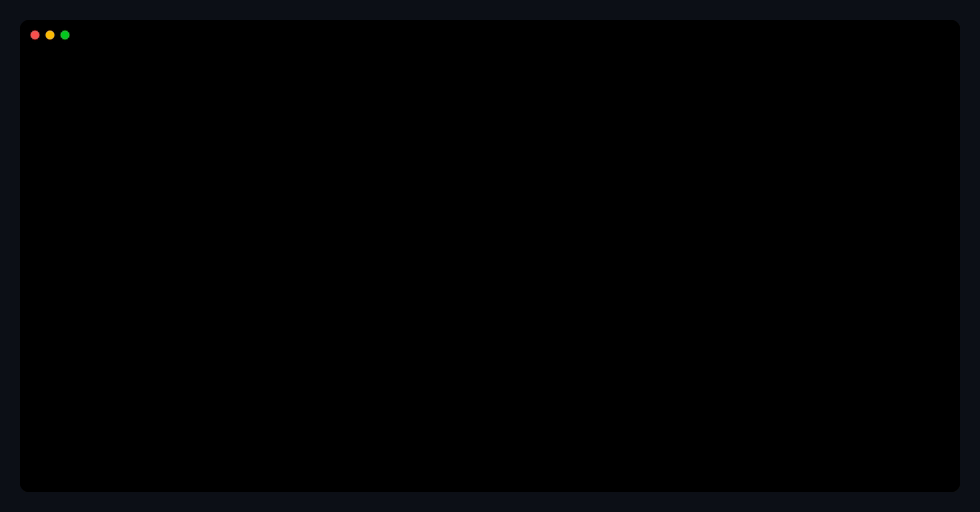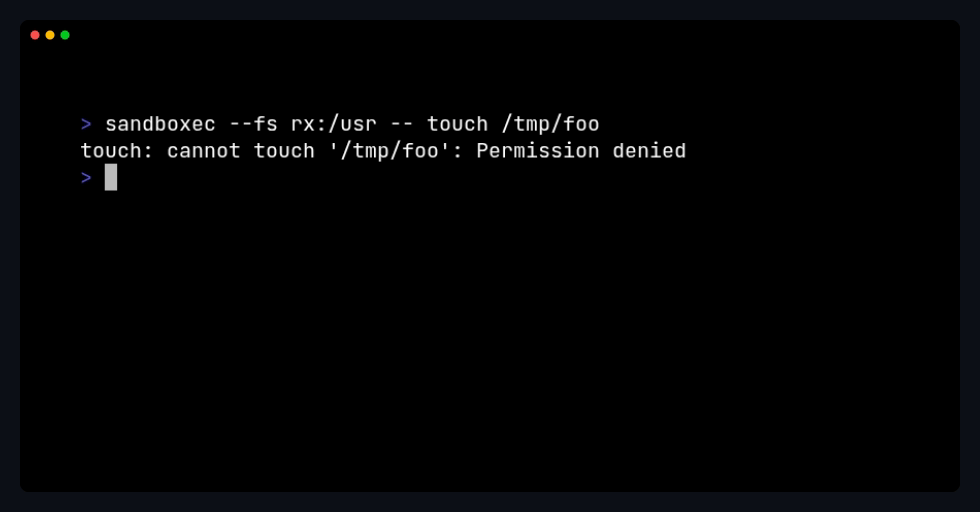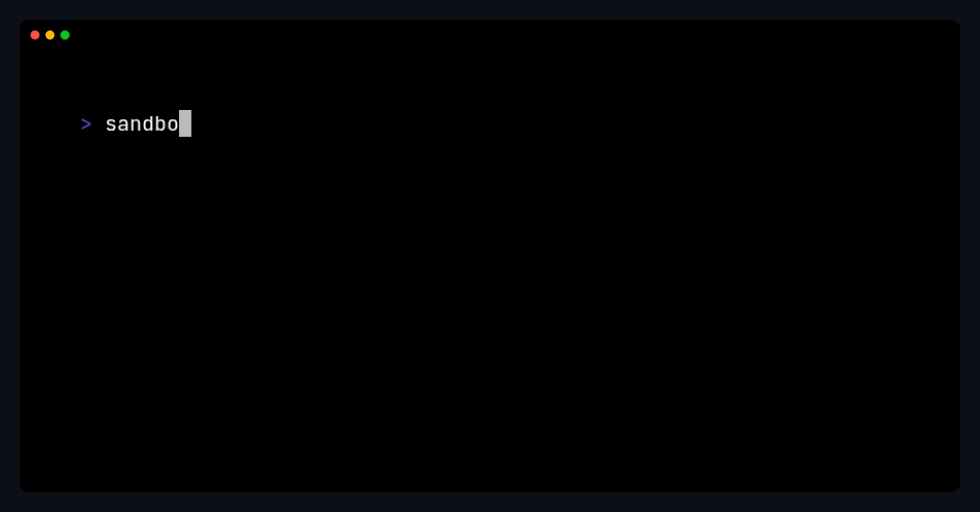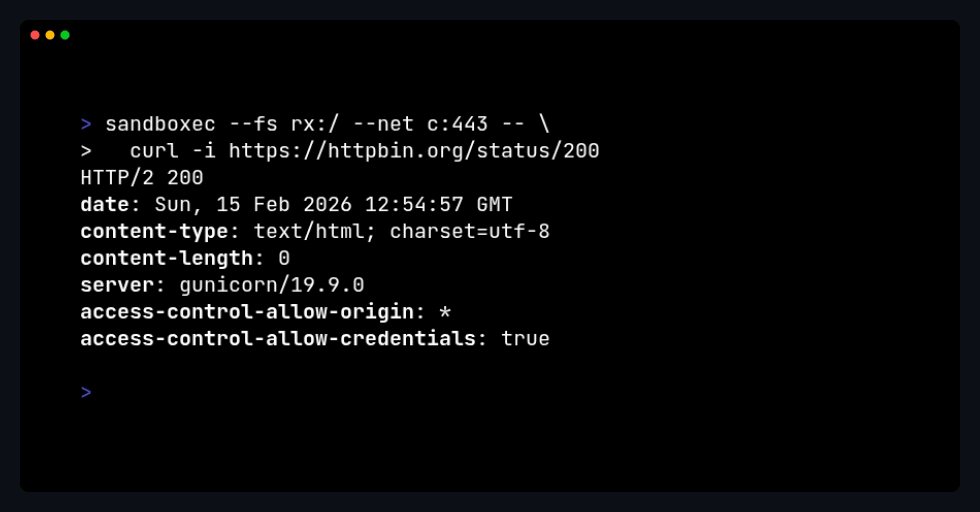 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 sshwarts/skillscript
Skillscript — a small declarative language for authoring agent workflows. Runtime, compiler, and CLI.
 darlinghq/darling
Darwin/macOS emulation layer for Linux
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…