
writehat
 blacklanternsecurity/writehat
A pentest reporting tool written in Python. Free yourself from Microsoft Word.
educationpenetration-testingutilities-frameworks
blacklanternsecurity/writehatA pentest reporting tool written in Python. Free yourself from Microsoft Word.
 ricardojoserf/p-invoke.net
Curated collection of P/Invoke definitions from pinvoke.net with Microsoft documentation links, enabling quick Windows API prototyping for security…
 henkru/cs-get-last-error
An aggressor script for Cobalt Strike to query Windows' GetLastError messages
 samratashok/admodule
Microsoft signed ActiveDirectory PowerShell module
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
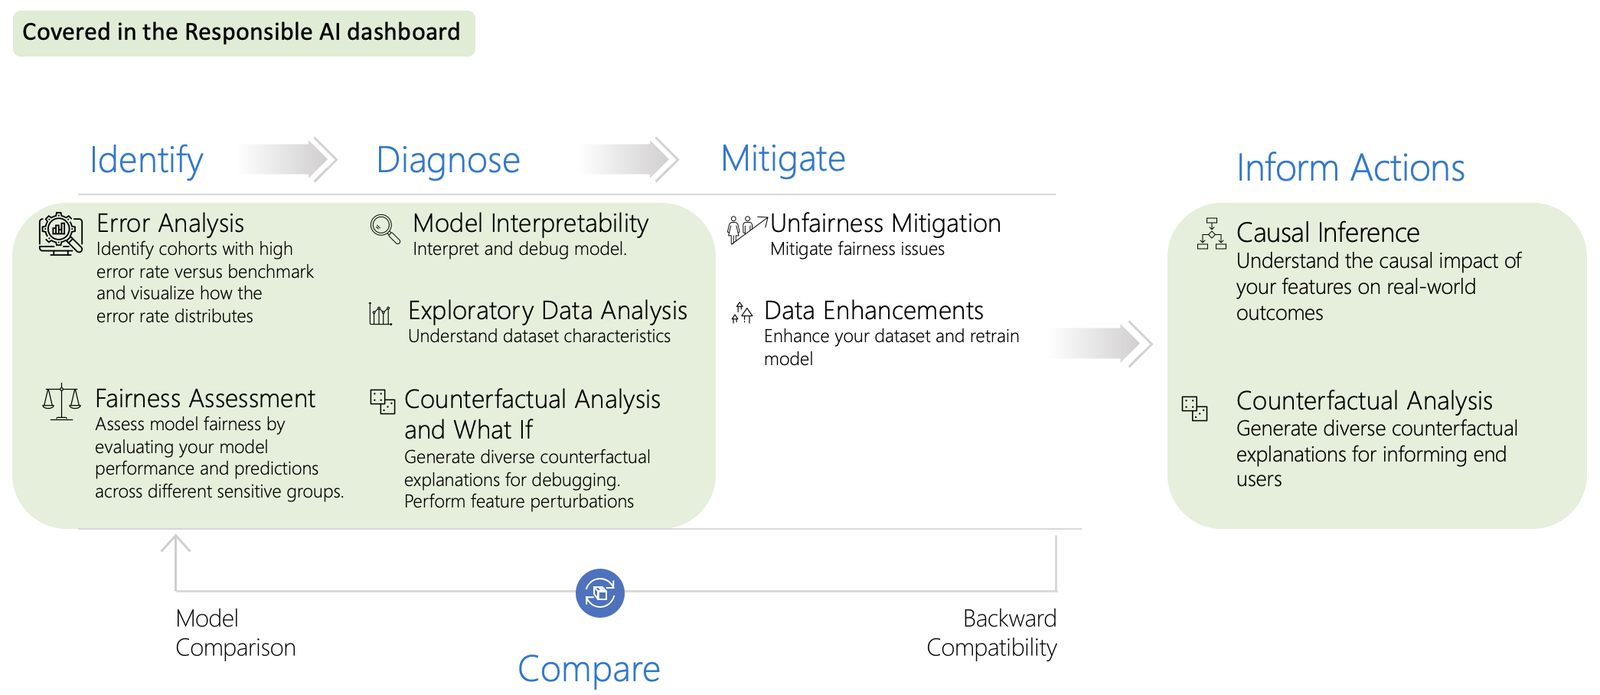 microsoft/responsible-ai-toolbox
Interactive dashboards and libraries for responsible AI model debugging, covering error analysis, fairness, interpretability, counterfactuals, causal…
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
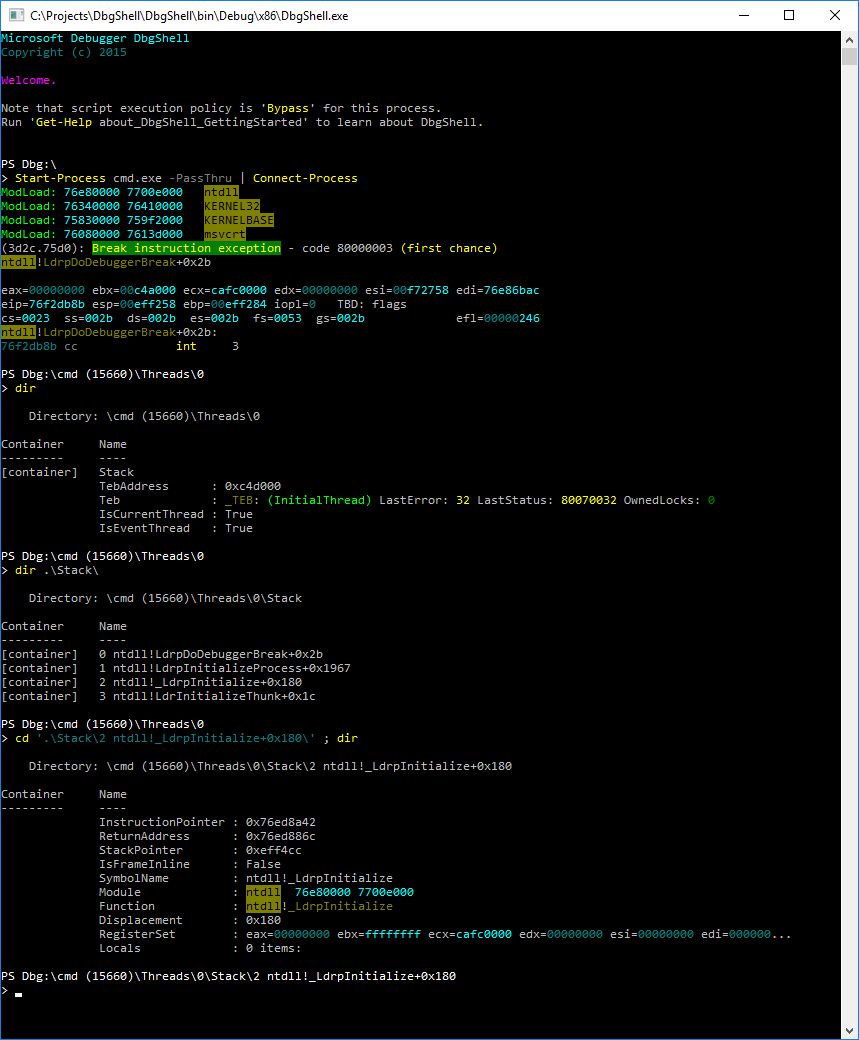 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
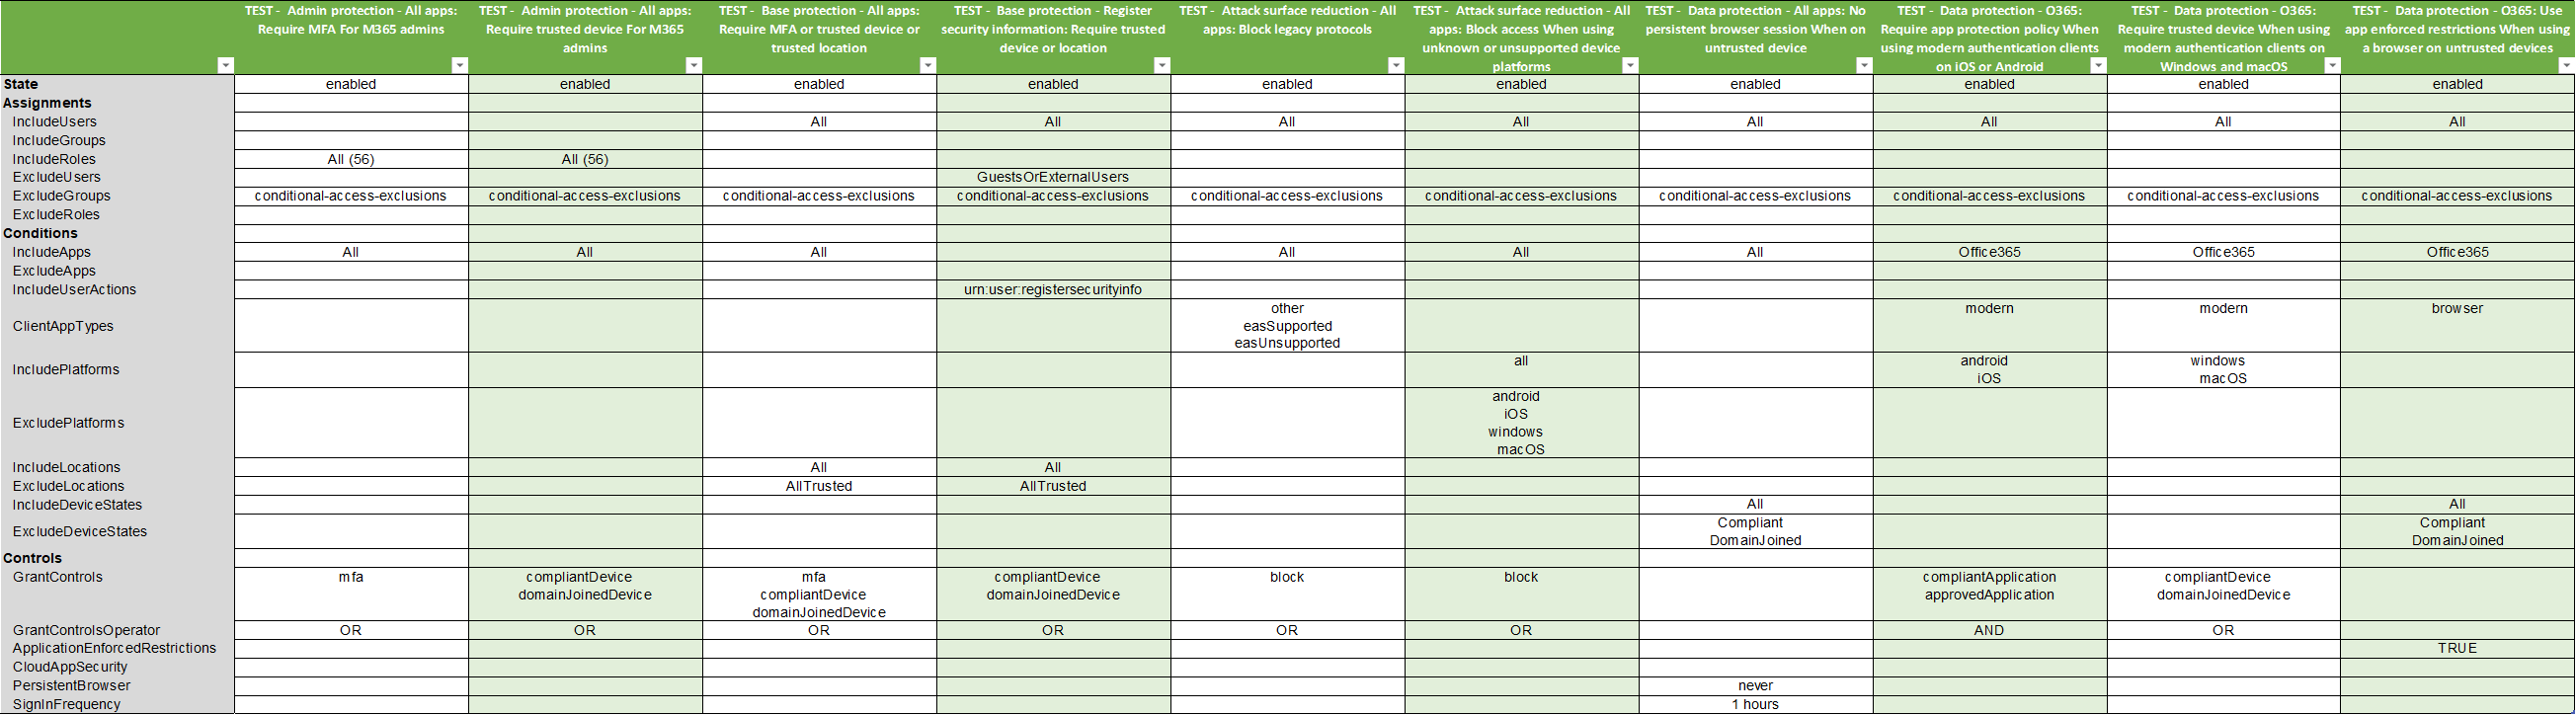 nicolonsky/conditionalaccessdocumentation
Microsoft Entra Conditional Access Documentation with PowerShell
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response

 kit-lang/packages/kit-oauth
OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 nccgroup/windowsjoblock
Windows Process Lockdown Tool using Job Objects