

Doozer
 coalfire-research/doozer
Password cracking utility
hash-analysispassword-crackingpenetration-testing+2
coalfire-research/doozerPassword cracking utility
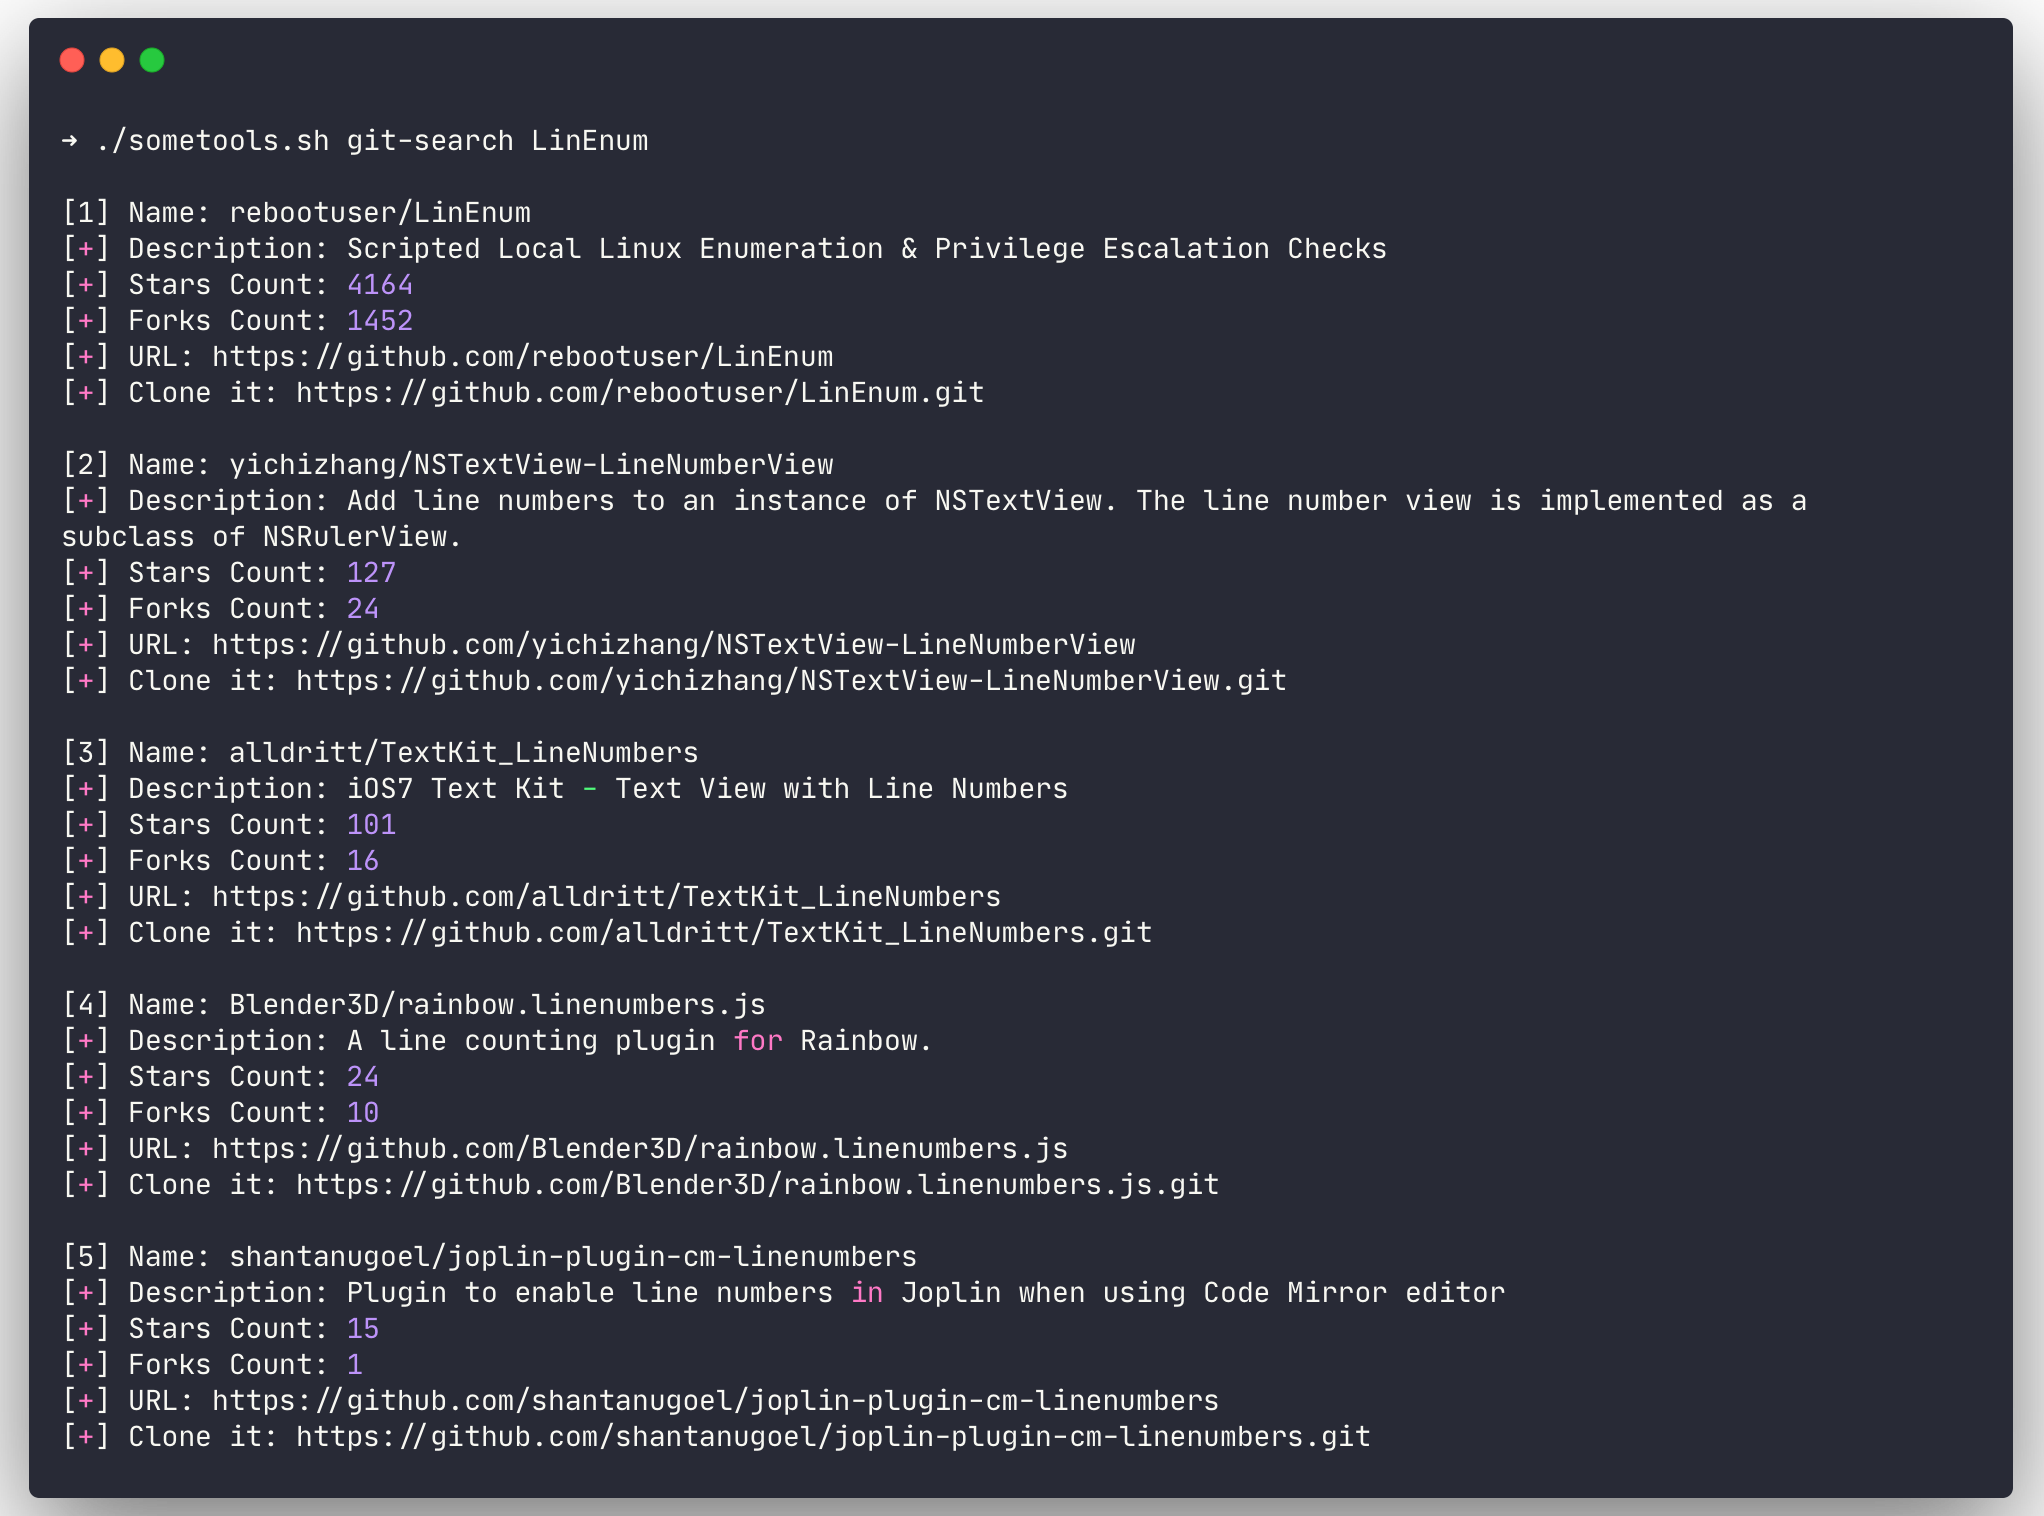 som3canadian/some-tools
Some Pentest Tools. Install and keep up to date some pentesting tools. I used this to pass my OSCP exam.
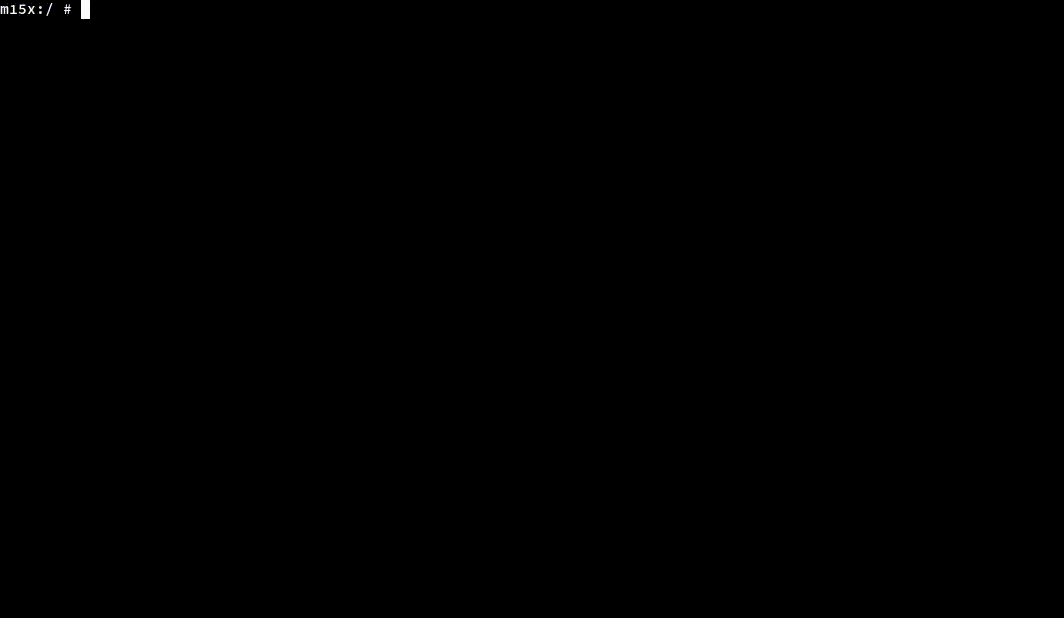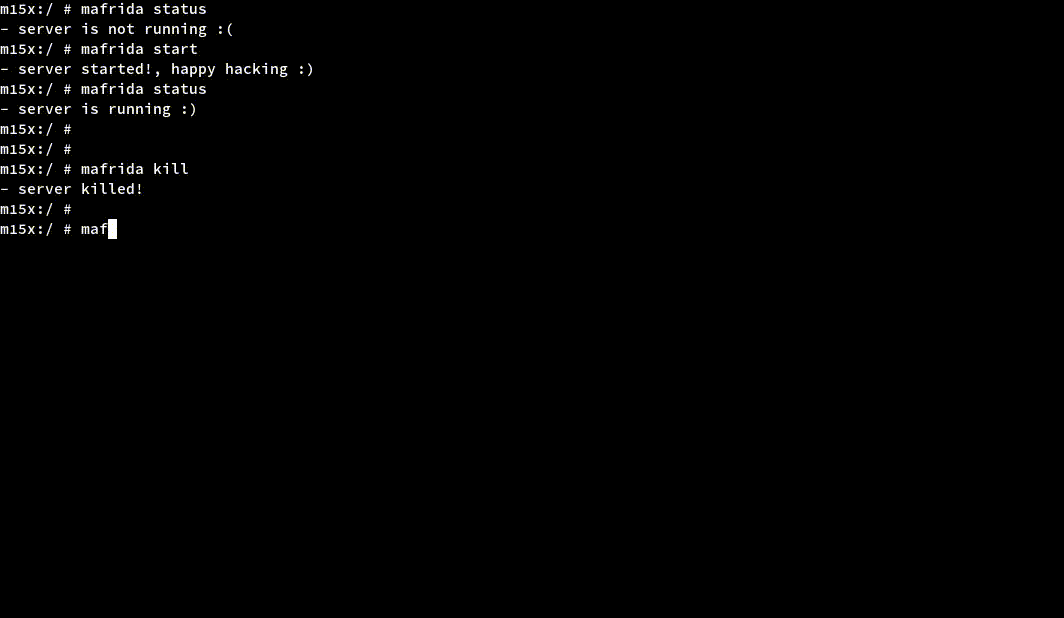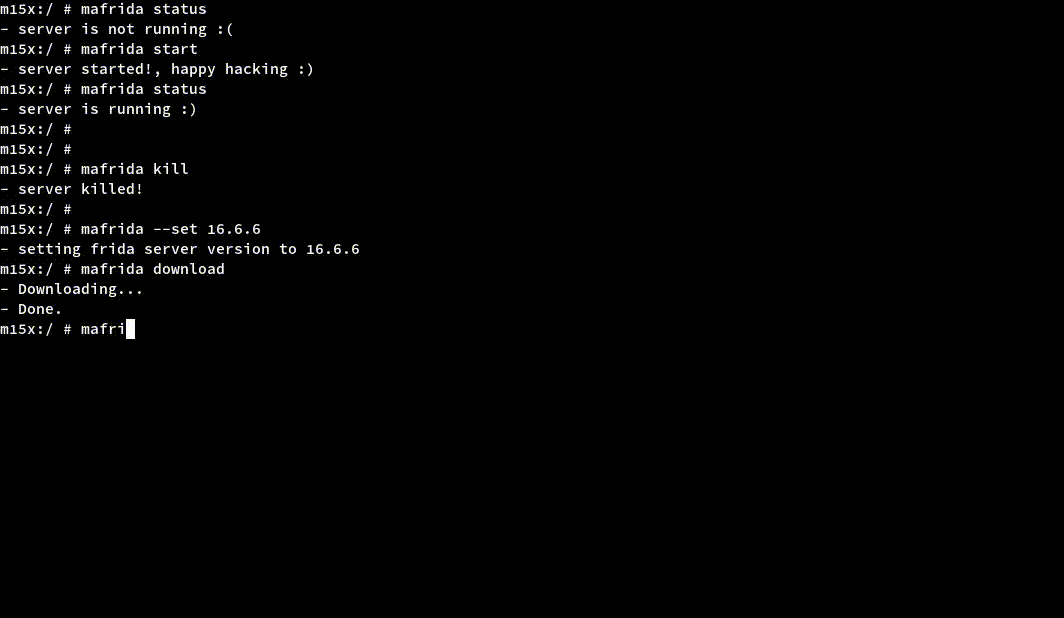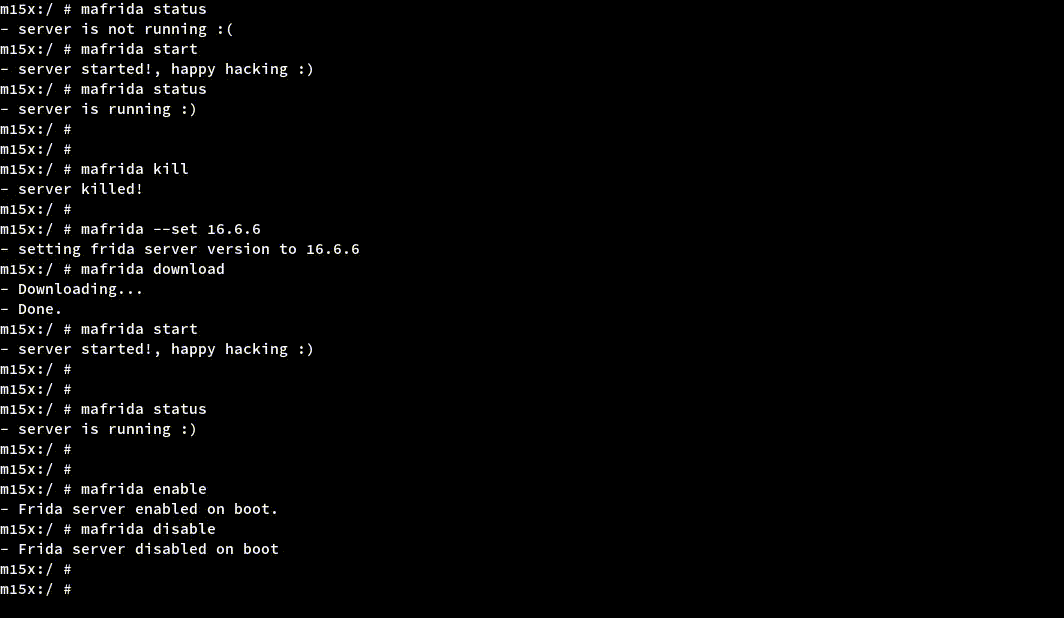 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
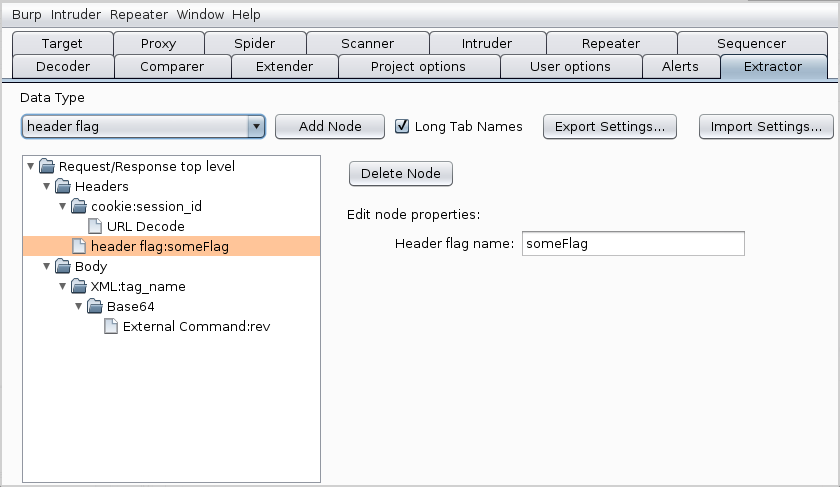 nccgroup/extractor
Extension adds a new tab in Burp Suite called Extractor
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 nccgroup/readable-thrift
Human-friendly Thrift encoder/decoder
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
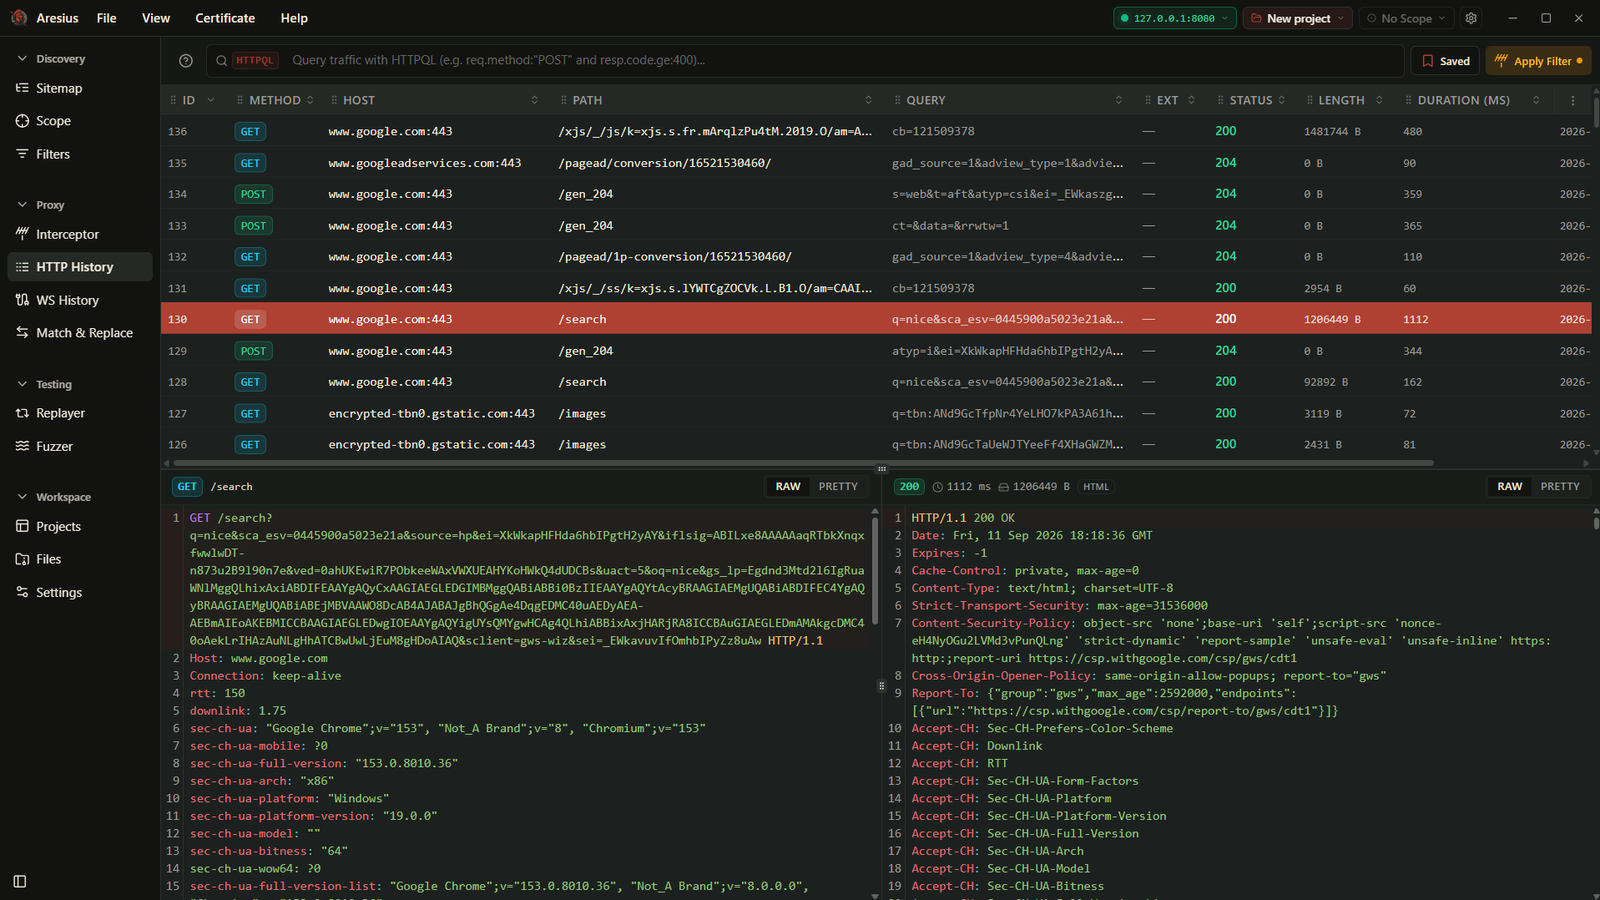 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 vid4l-07/roxy
Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 splinters-io/blinder
Content-blind reverse proxy for exposure-protected security scanning
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…