

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
30.4k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 saml-toolkits/ruby-saml
Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
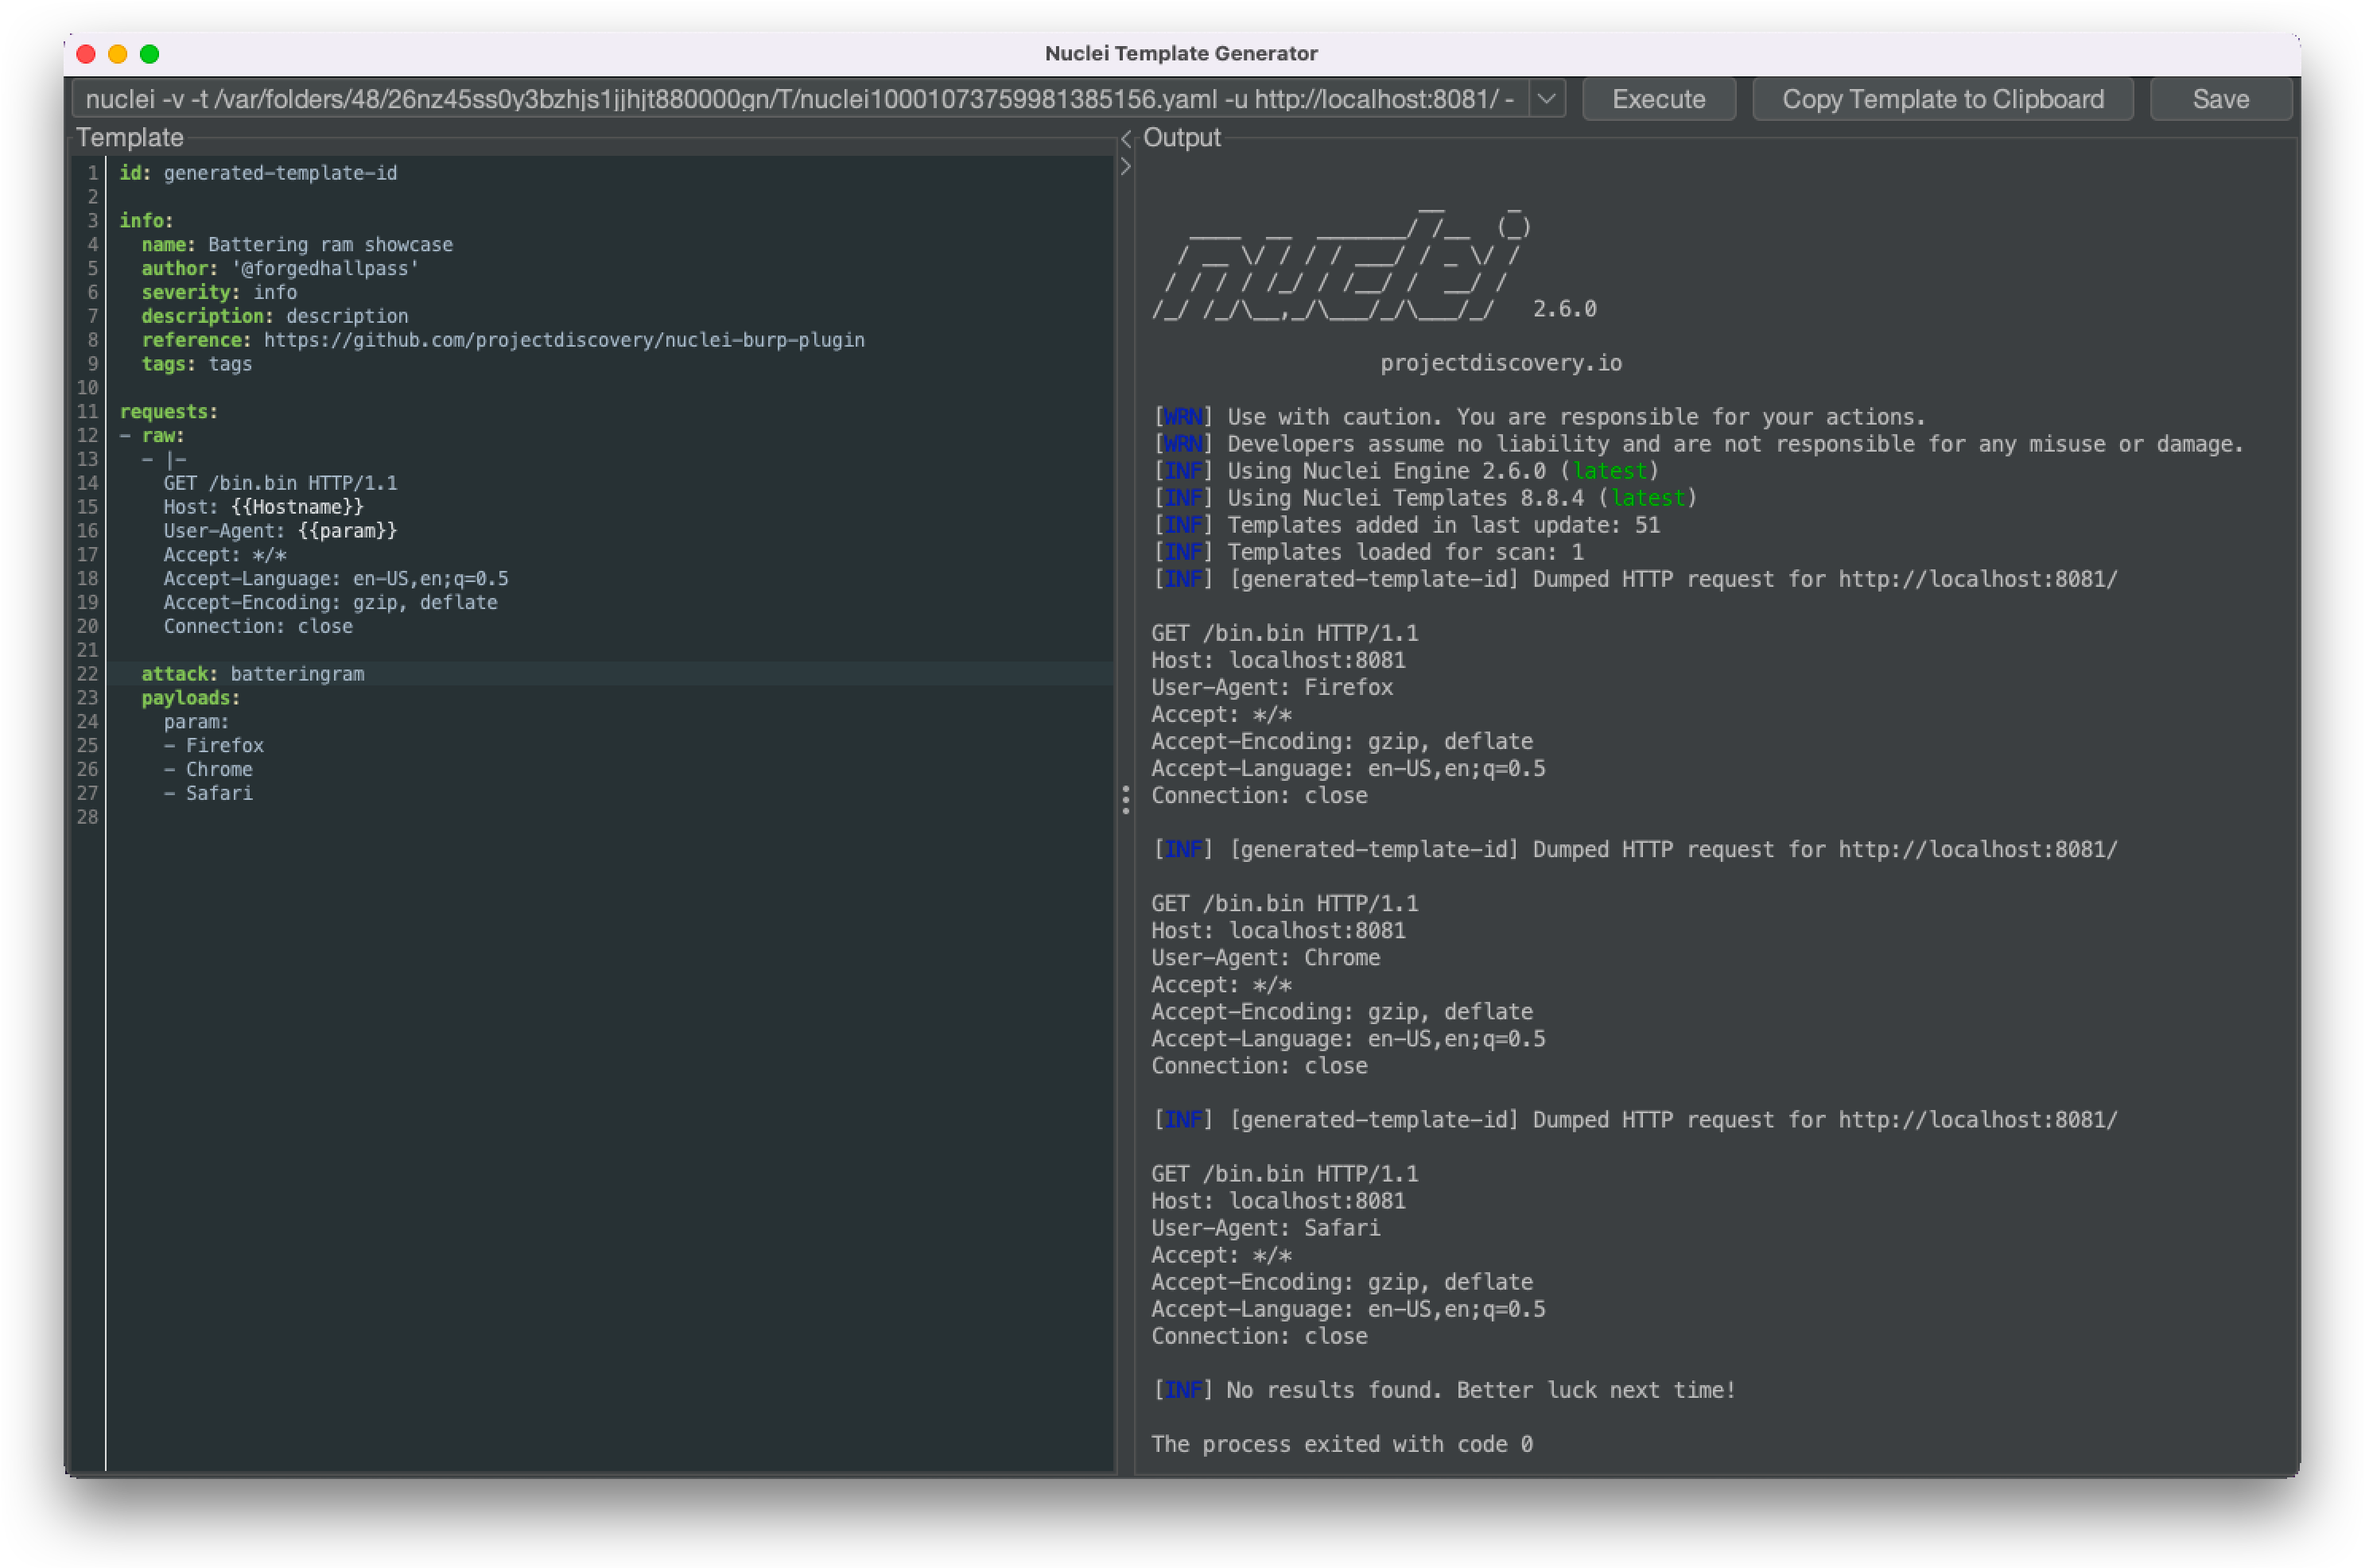 projectdiscovery/nuclei-burp-plugin
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
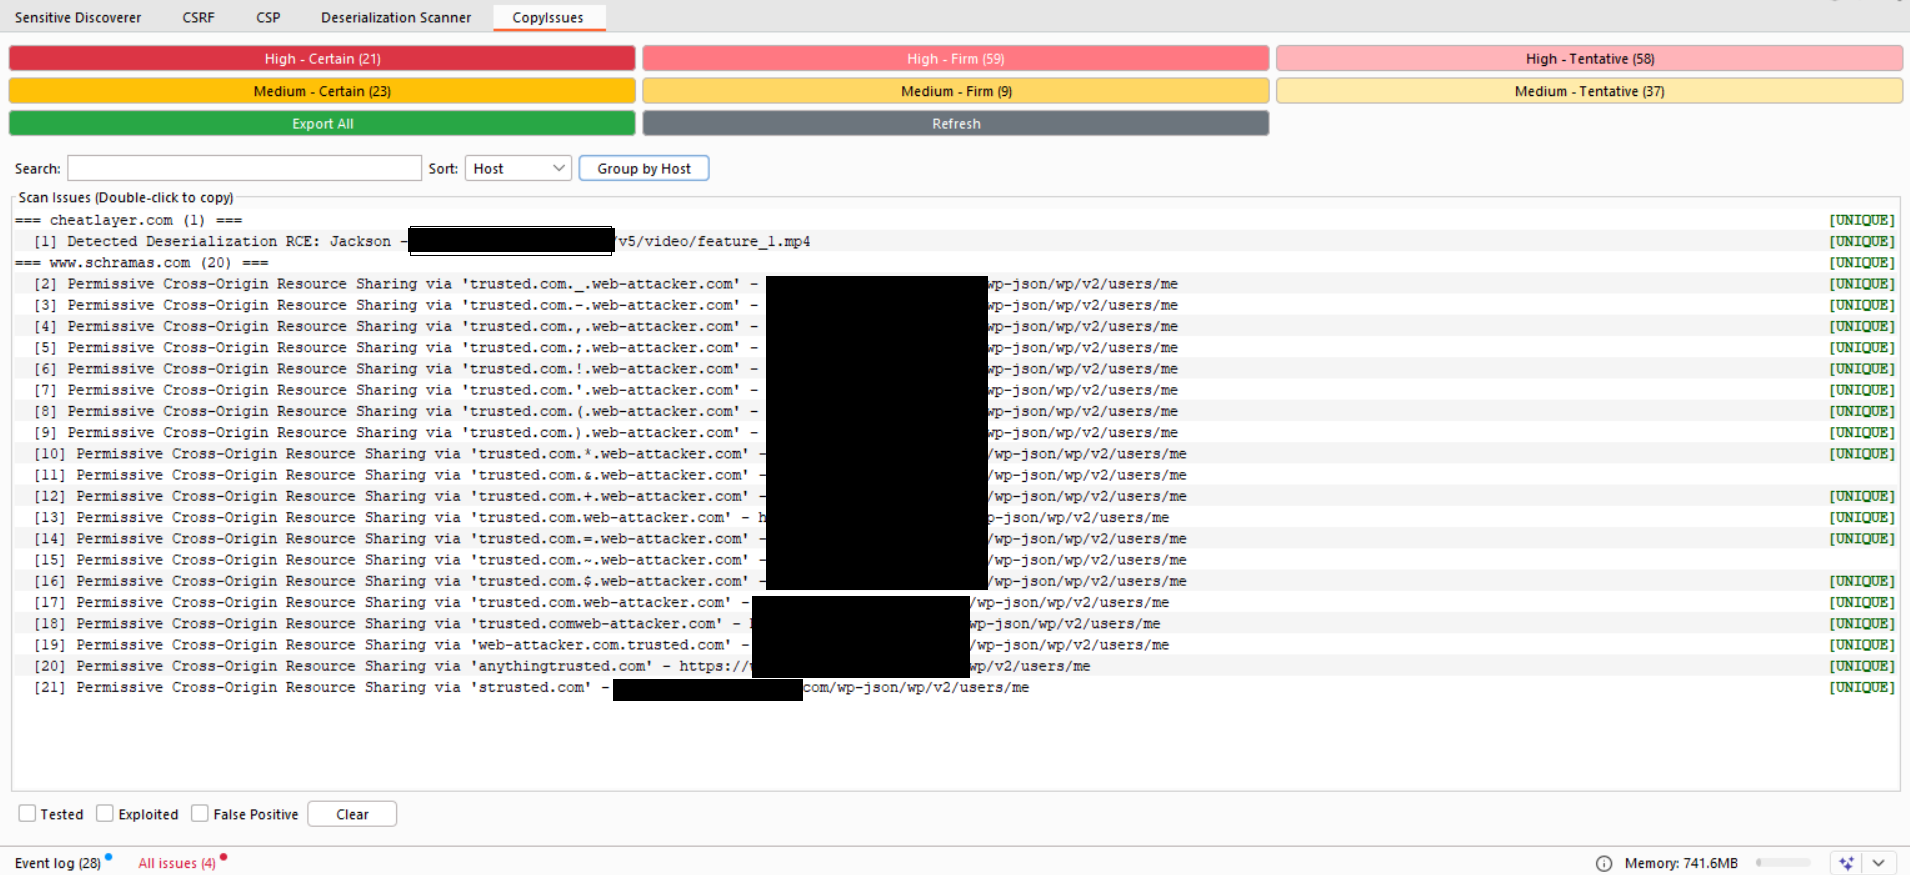 teycir/burpcopyissues
Burp suite extension that lets you easily copy issues
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2023-37460_4-7-1
Java library for creating and extracting archives (ZIP, tar, JAR) with integrated security patch for a reported vulnerability, used as a dependency…
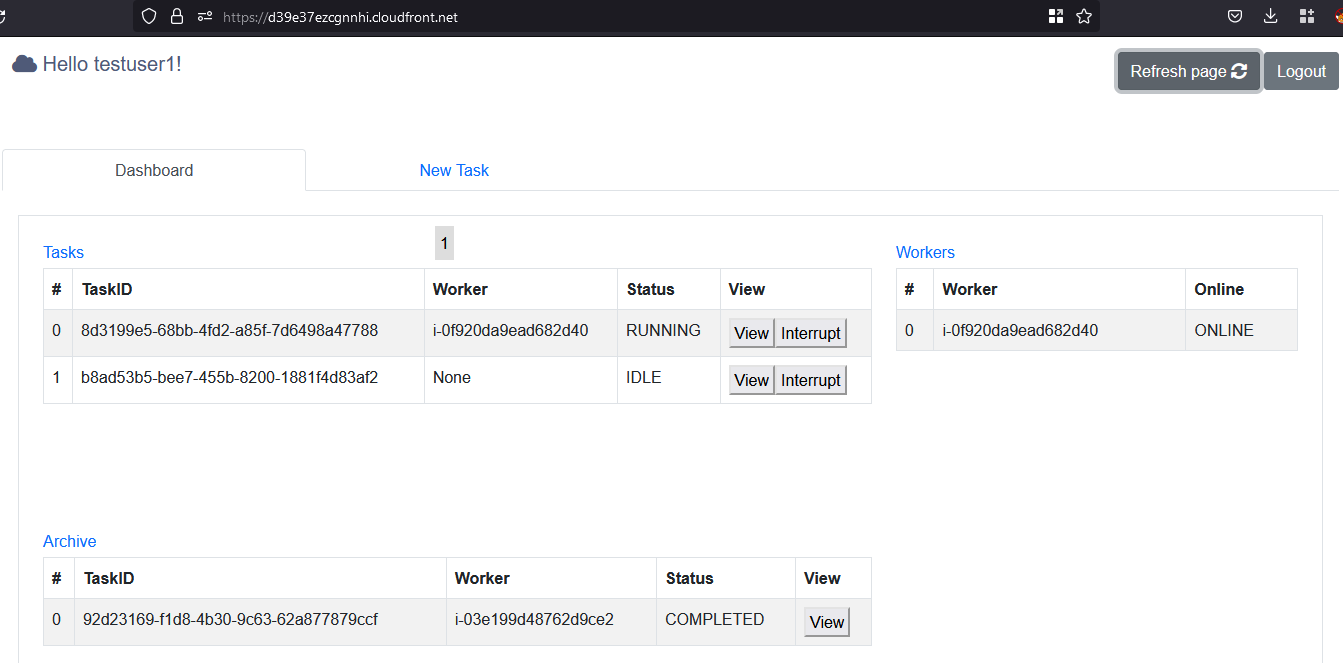 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
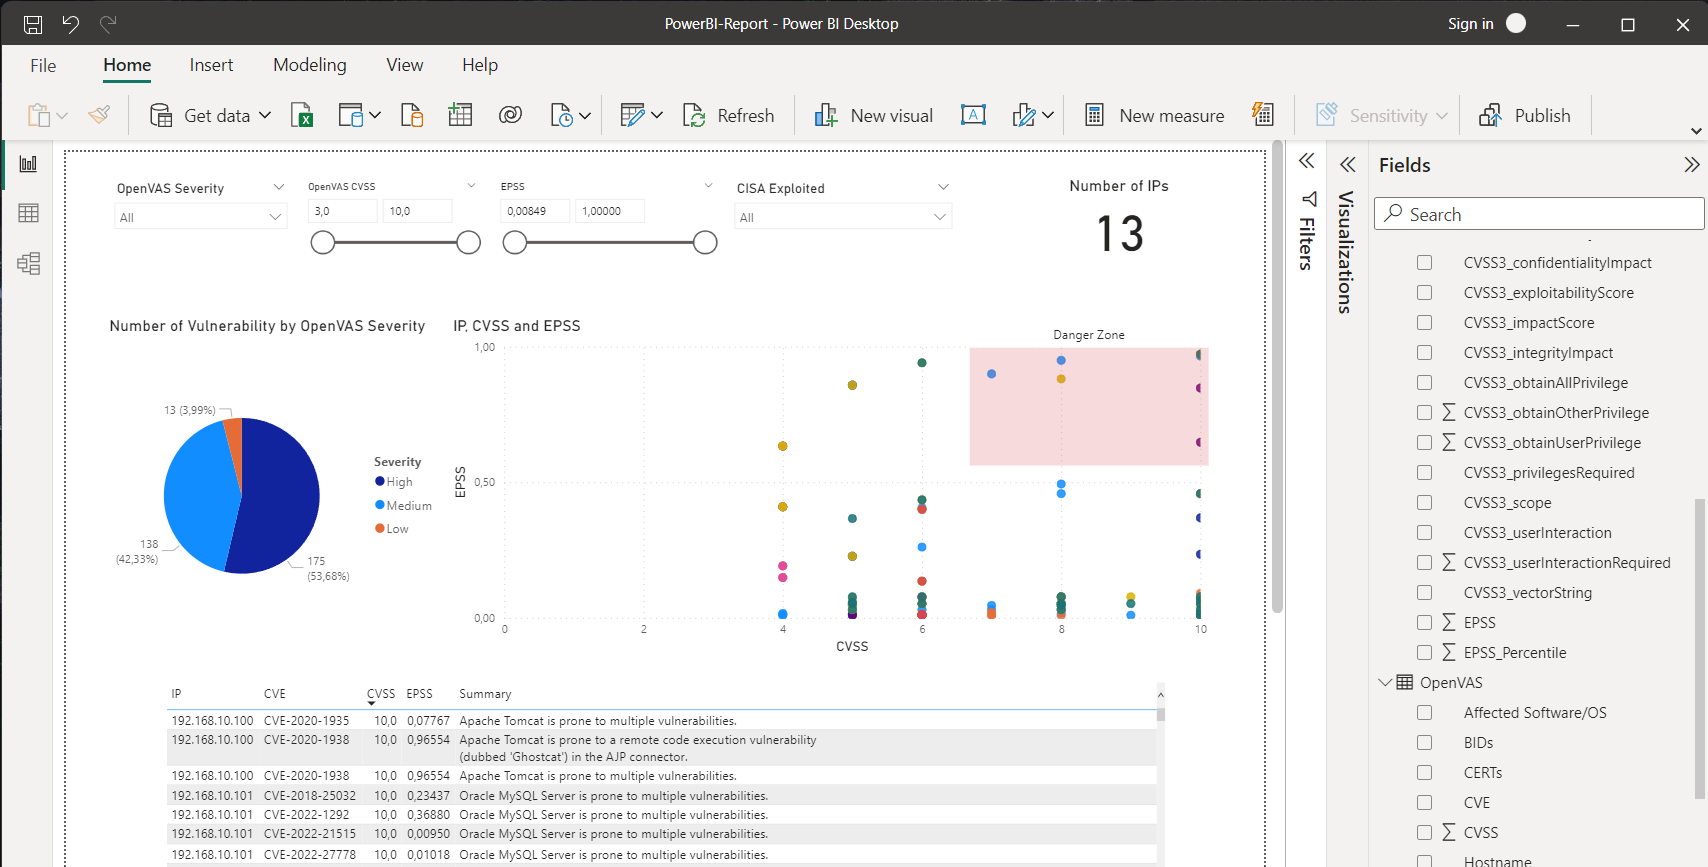 trinitor/cve-vulnerability-information-downloader
Downloads and aggregates CVSS, EPSS, and CISA known exploited vulnerability data into unified JSON/CSV files and a SQLite database. Enriches…
 infobyte/faraday-client
GTK client of FaradaySEC
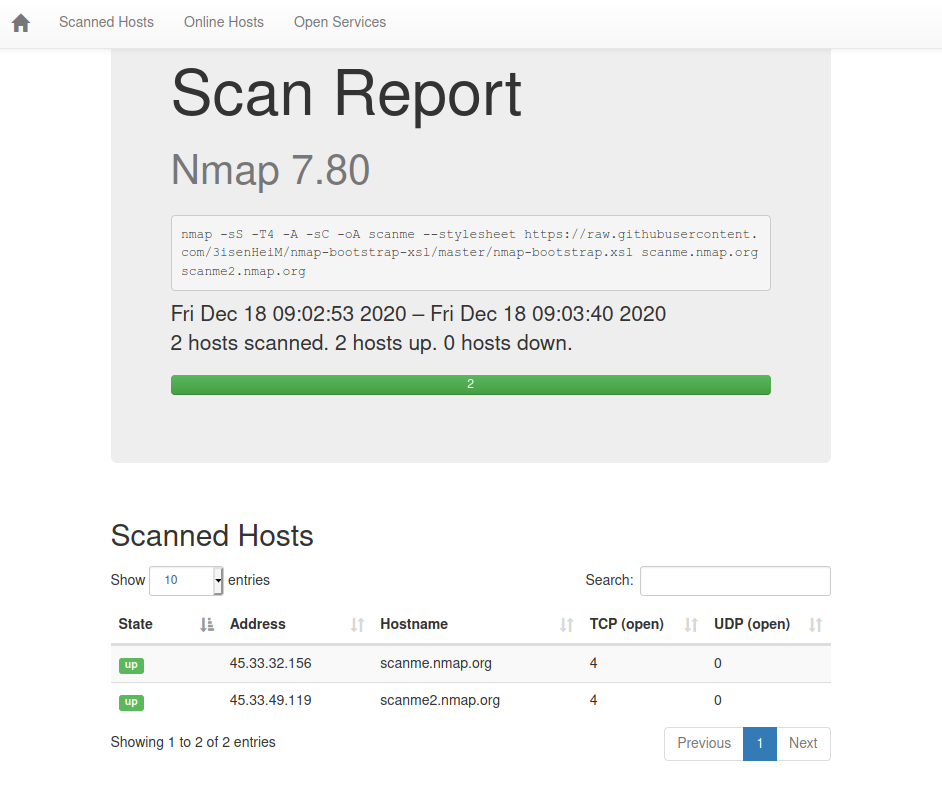 honze-net/nmap-bootstrap-xsl
A Nmap XSL implementation with Bootstrap.
 secxena/credcheck
Modular credential validation framework with active and passive (regex-based) checking modes for penetration testers. Supports multiple services via…
 daehee/nvd
Fast, simple library in Go to fetch CVEs from the National Vulnerability Database feeds
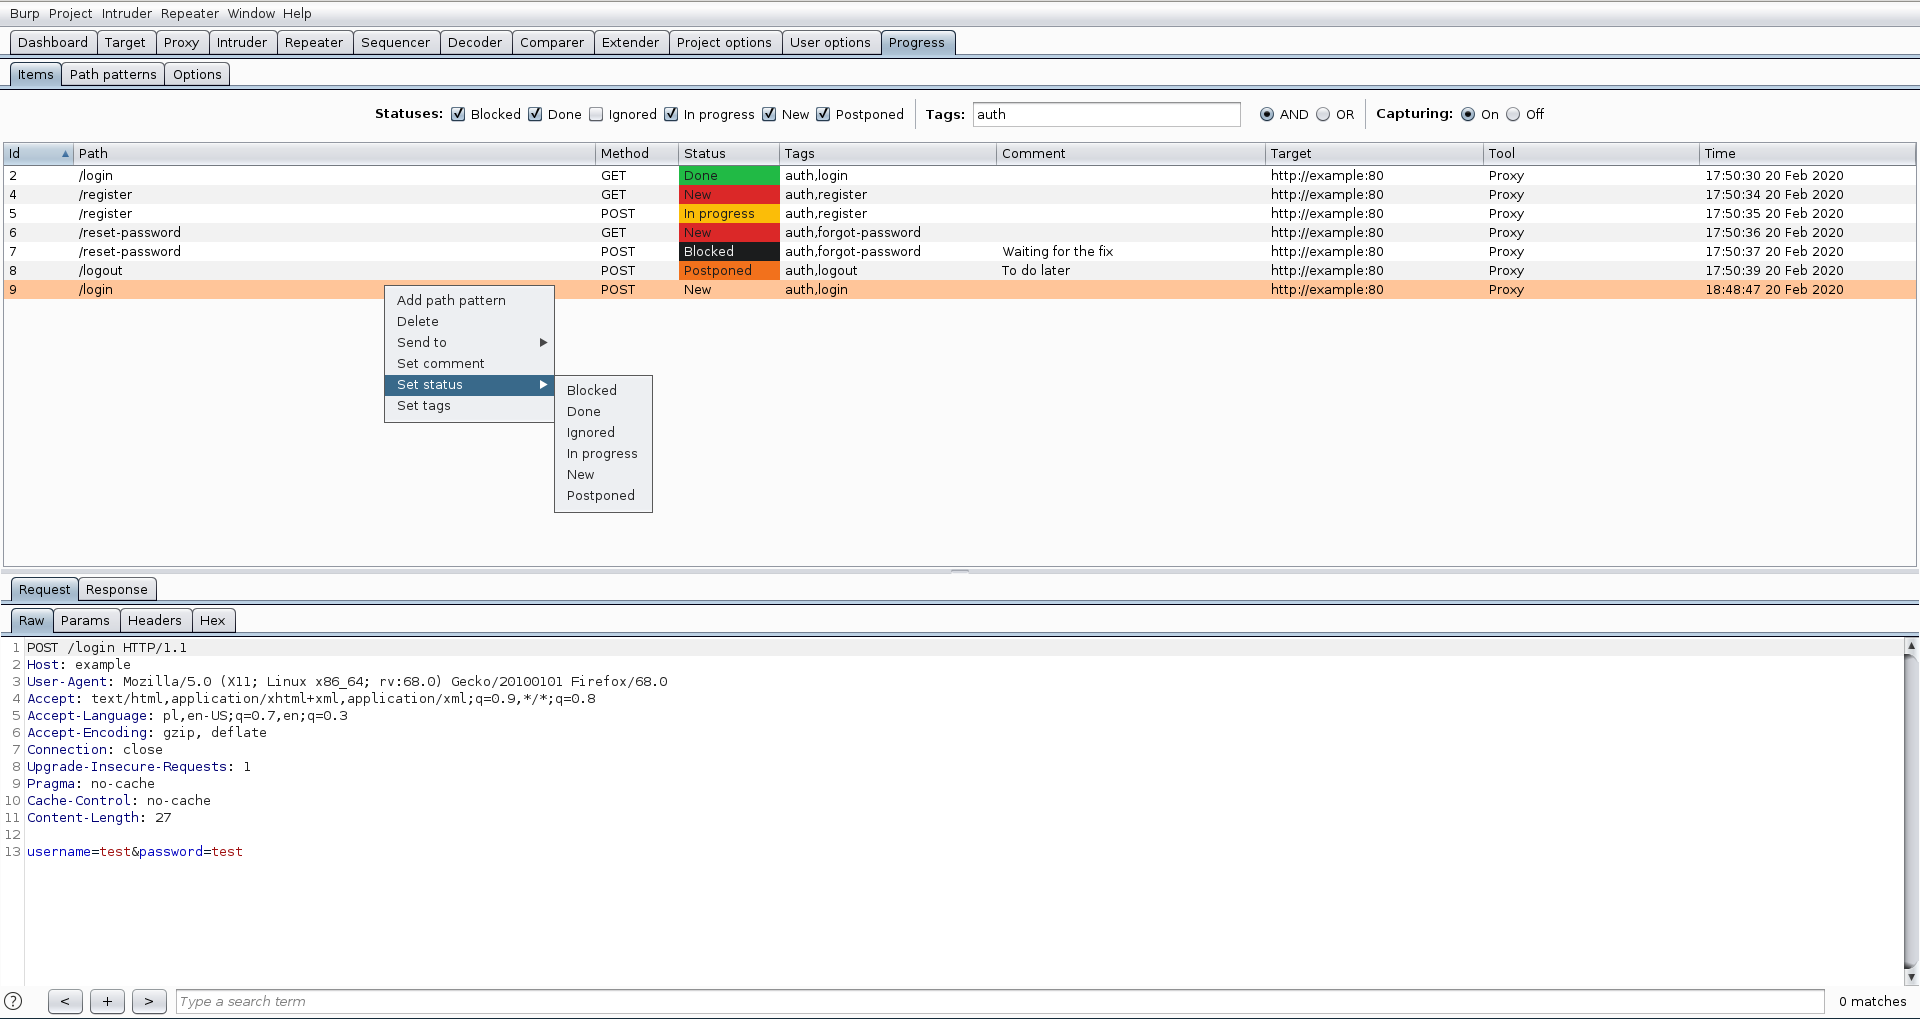 dariusztytko/progress-burp
Burp Suite extension to track vulnerability assessment progress
 infobyte/alexafaraday
Alexa skill example for Faraday API