

PcapPlusPlus
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.1k
seladb/pcapplusplusMultiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 corelight/ecs-templates
Corelight or Zeek Elastic Common Schema Templates
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 elandio-com/sharemylogin
Zero-Knowledge Credential Sharing
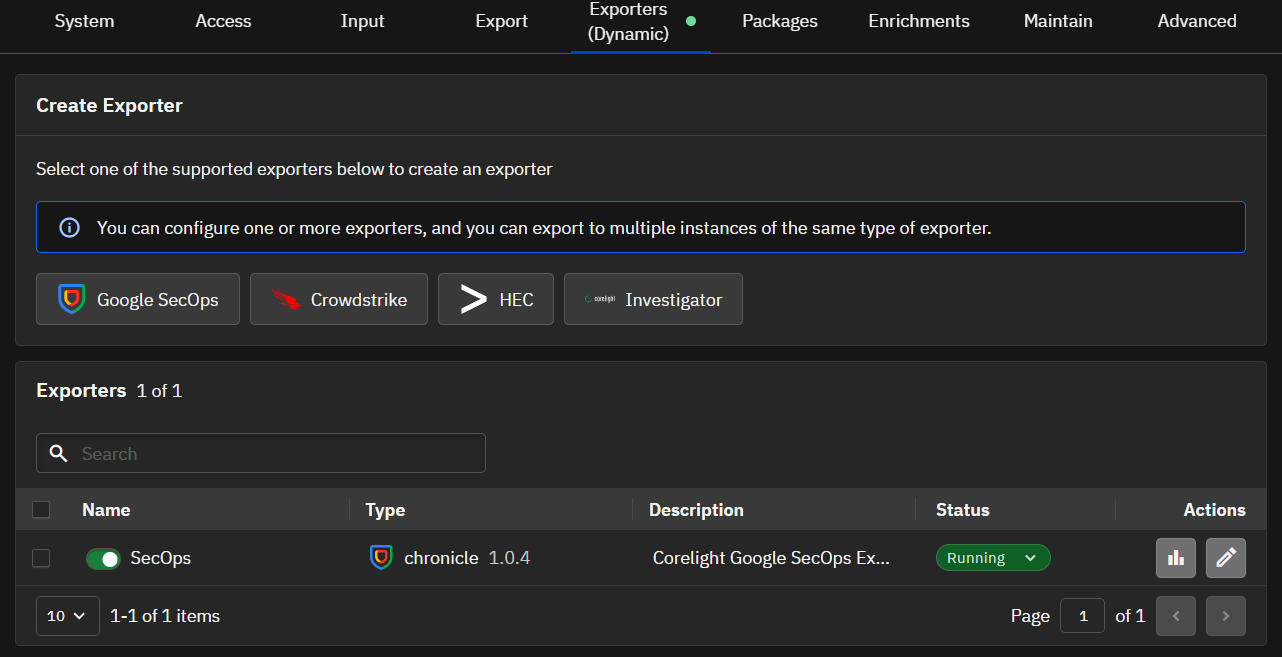 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 google/gopacket
Provides packet processing capabilities for Go
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
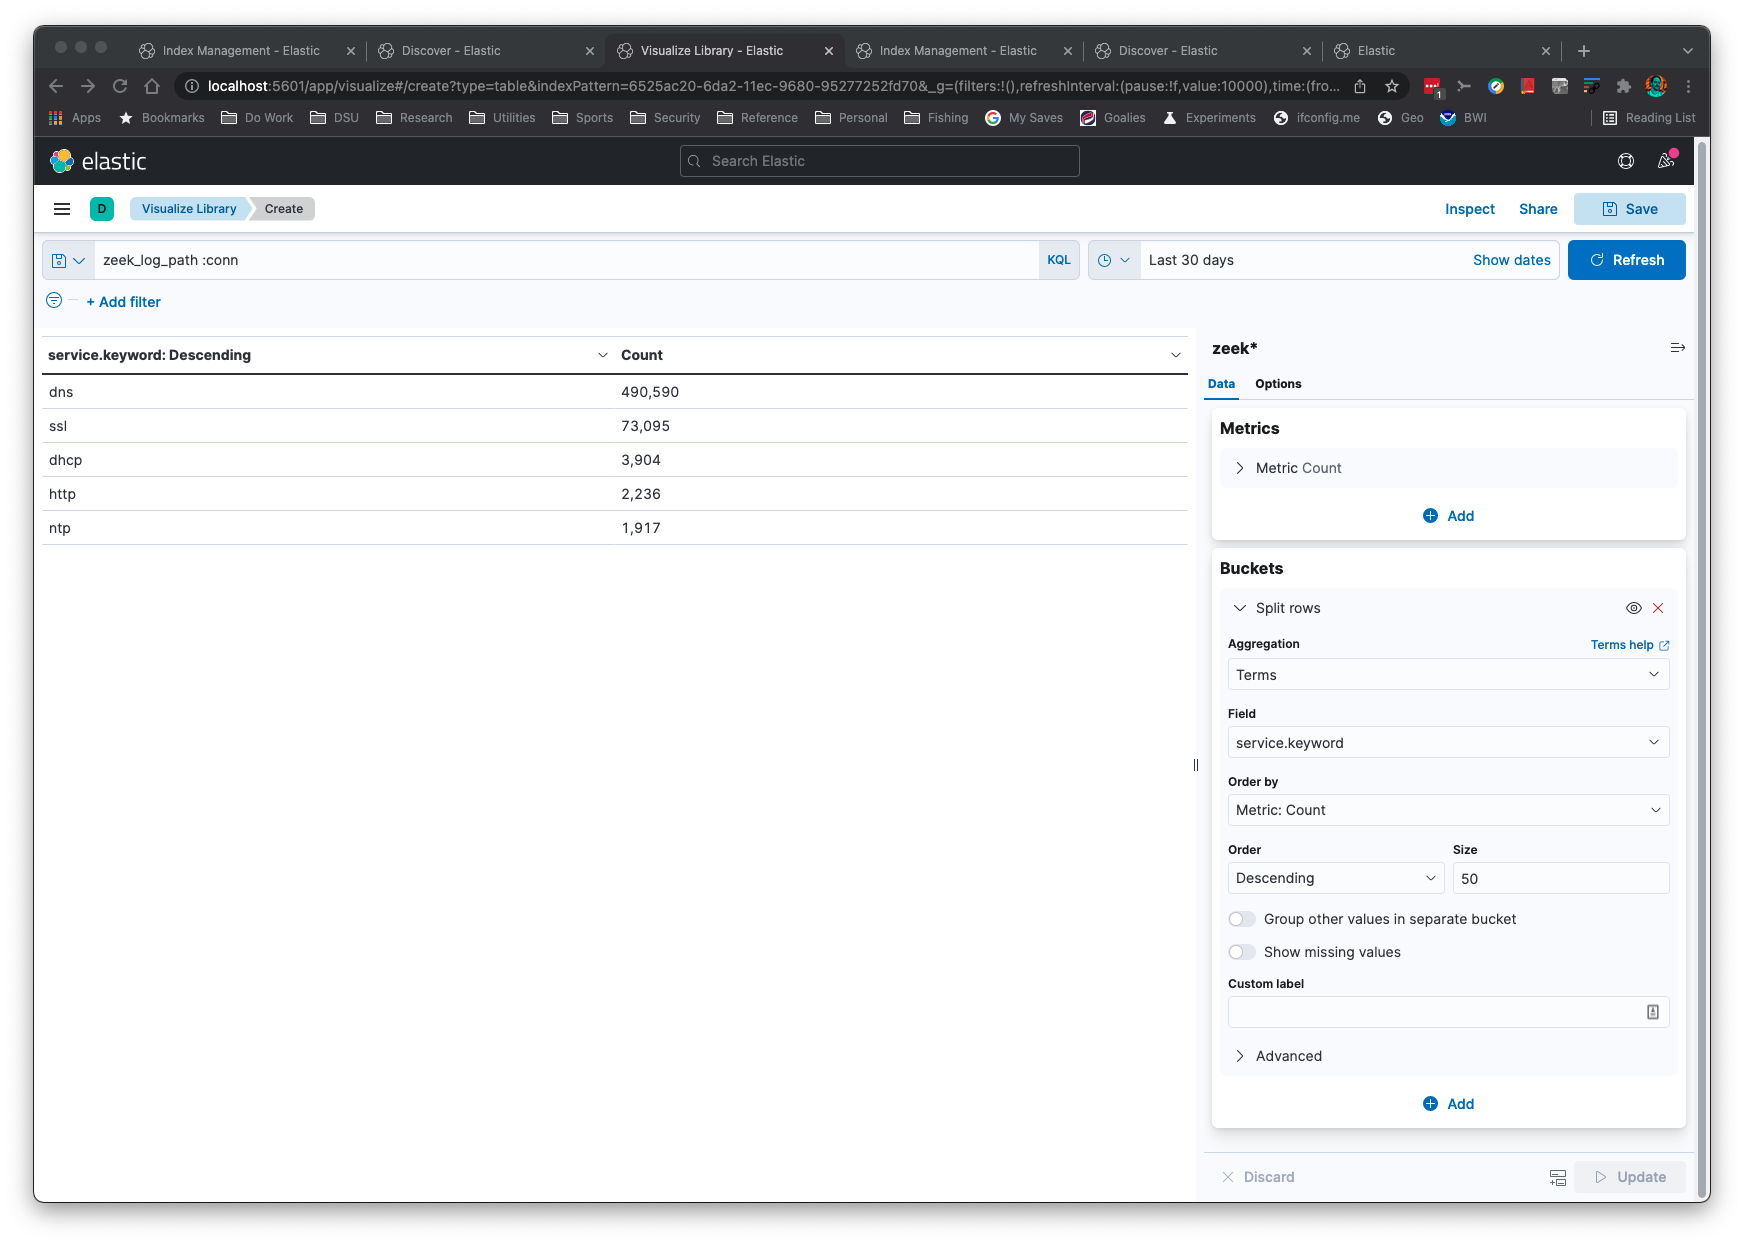 corelight/zeek2es
A Python application to filter and transfer Zeek logs to Elastic/OpenSearch+Humio. This app can also output pure JSON logs to stdout for further…
 tvdstaaij/telegram-history-dump
Backup Telegram chat logs with incremental support, multiple output formats (JSON, HTML, plaintext), and media download via telegram-cli remote…