
loki
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
general-purpose-utilitiesincident-responselog-analysis+1
29.0k
grafana/lokiHorizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 corelight/ecs-templates
Corelight or Zeek Elastic Common Schema Templates
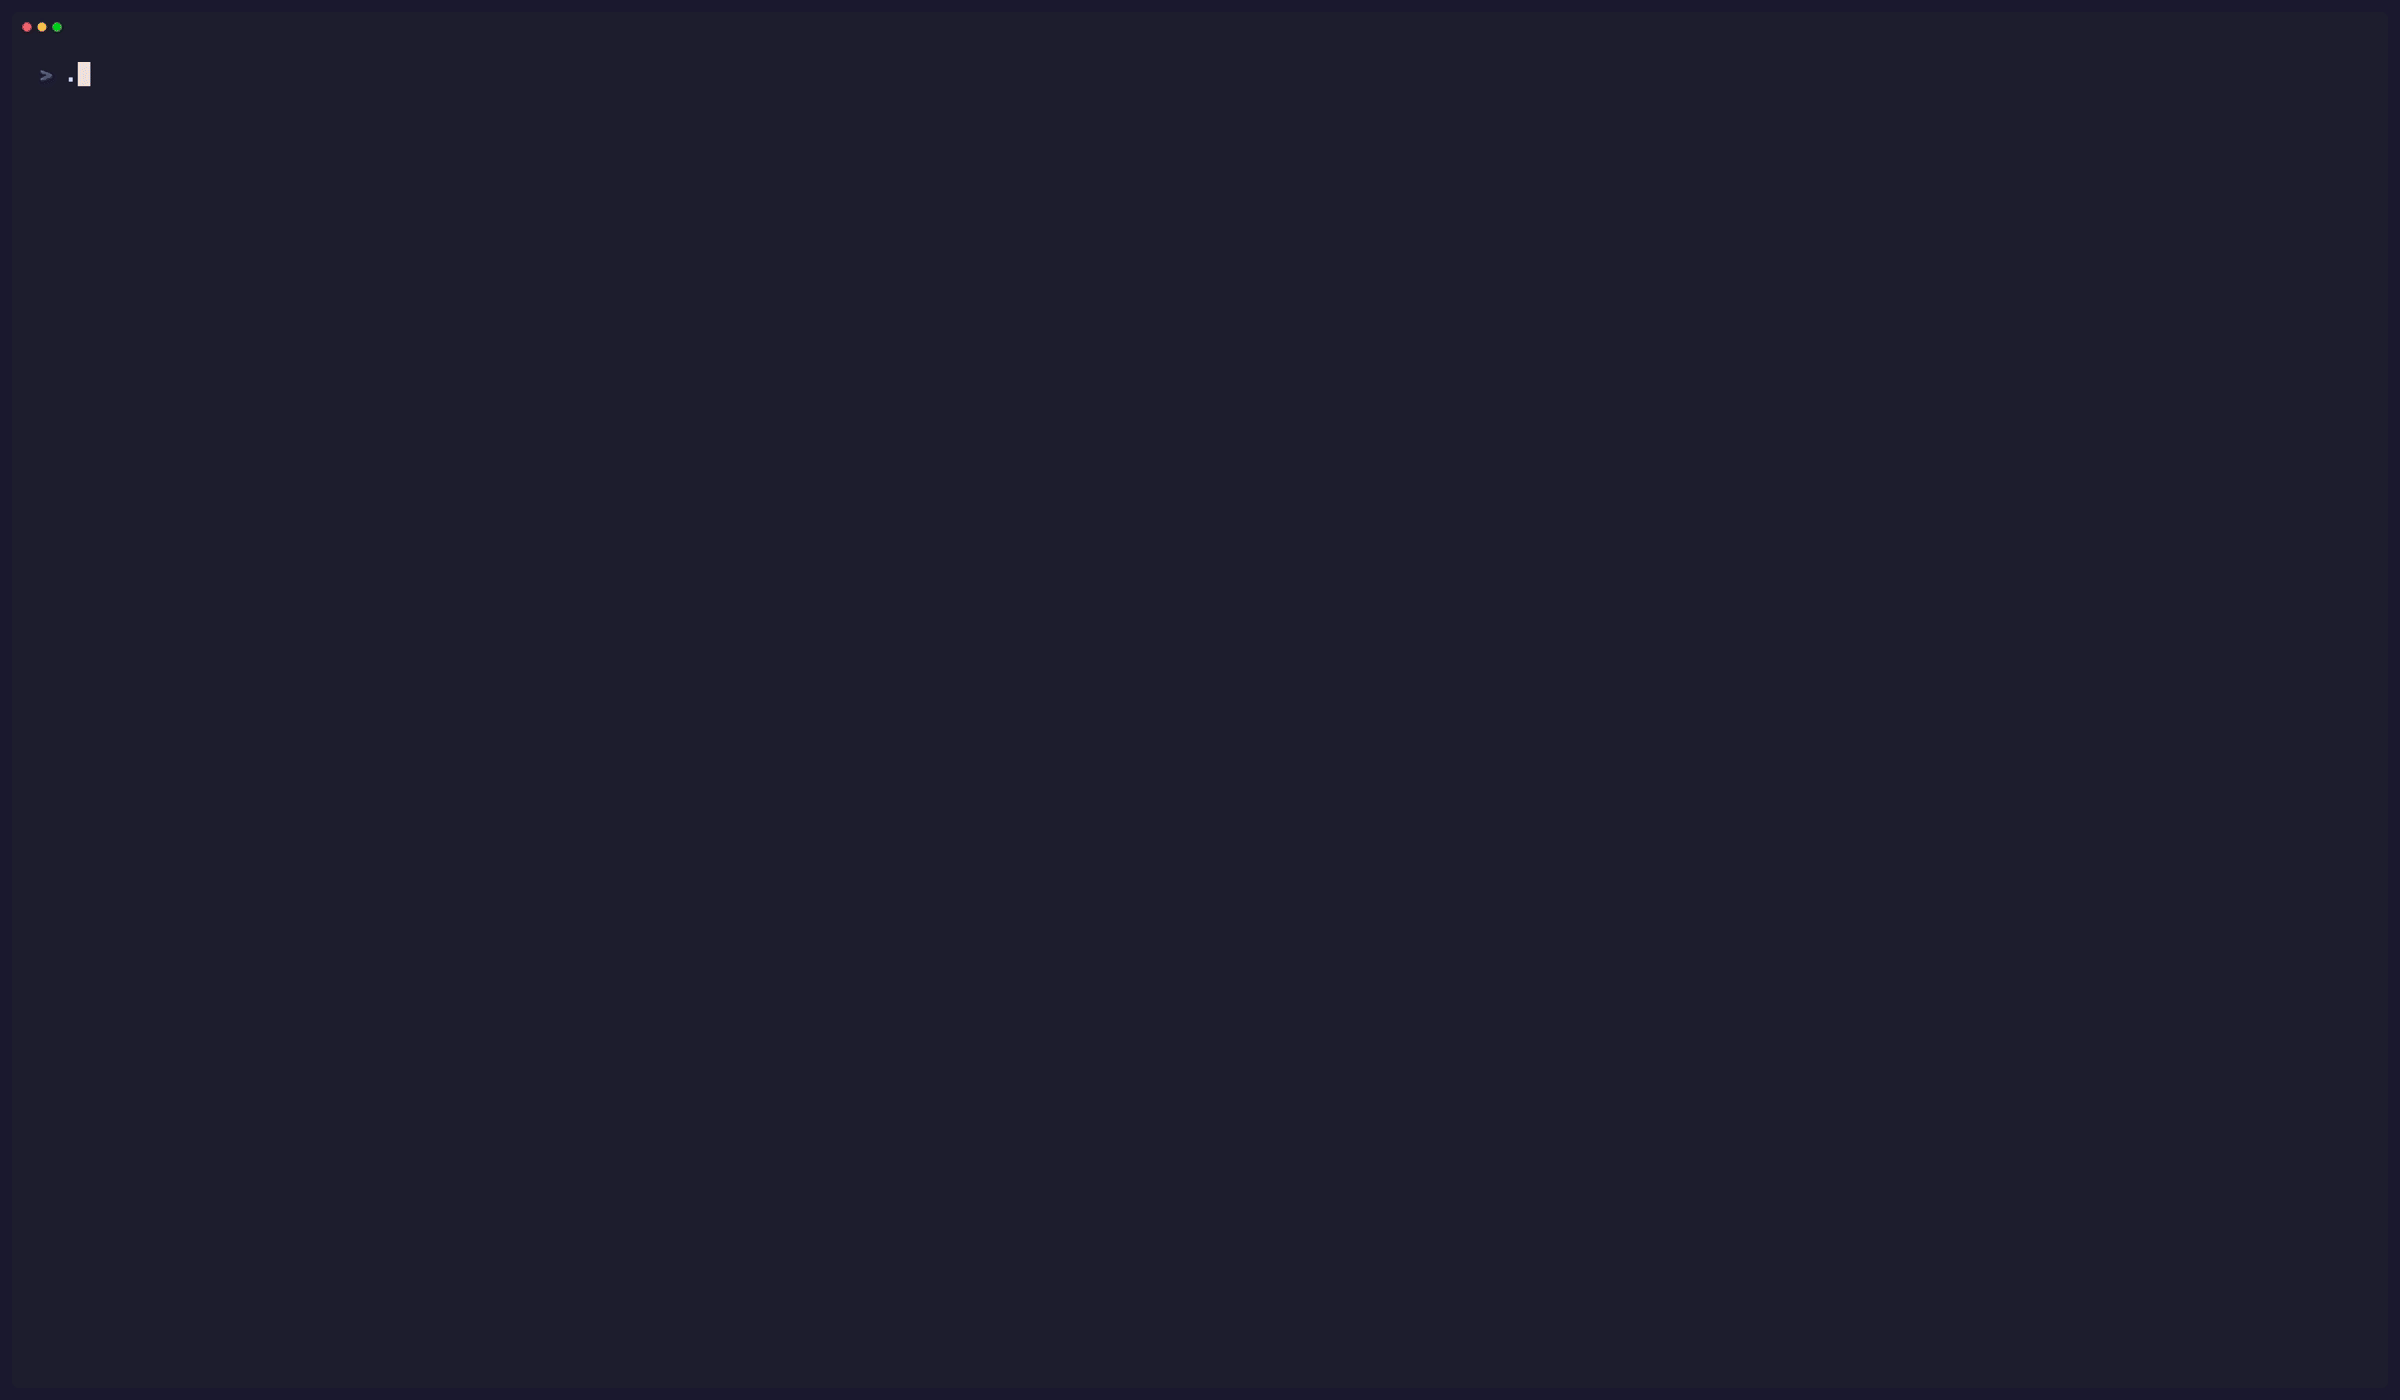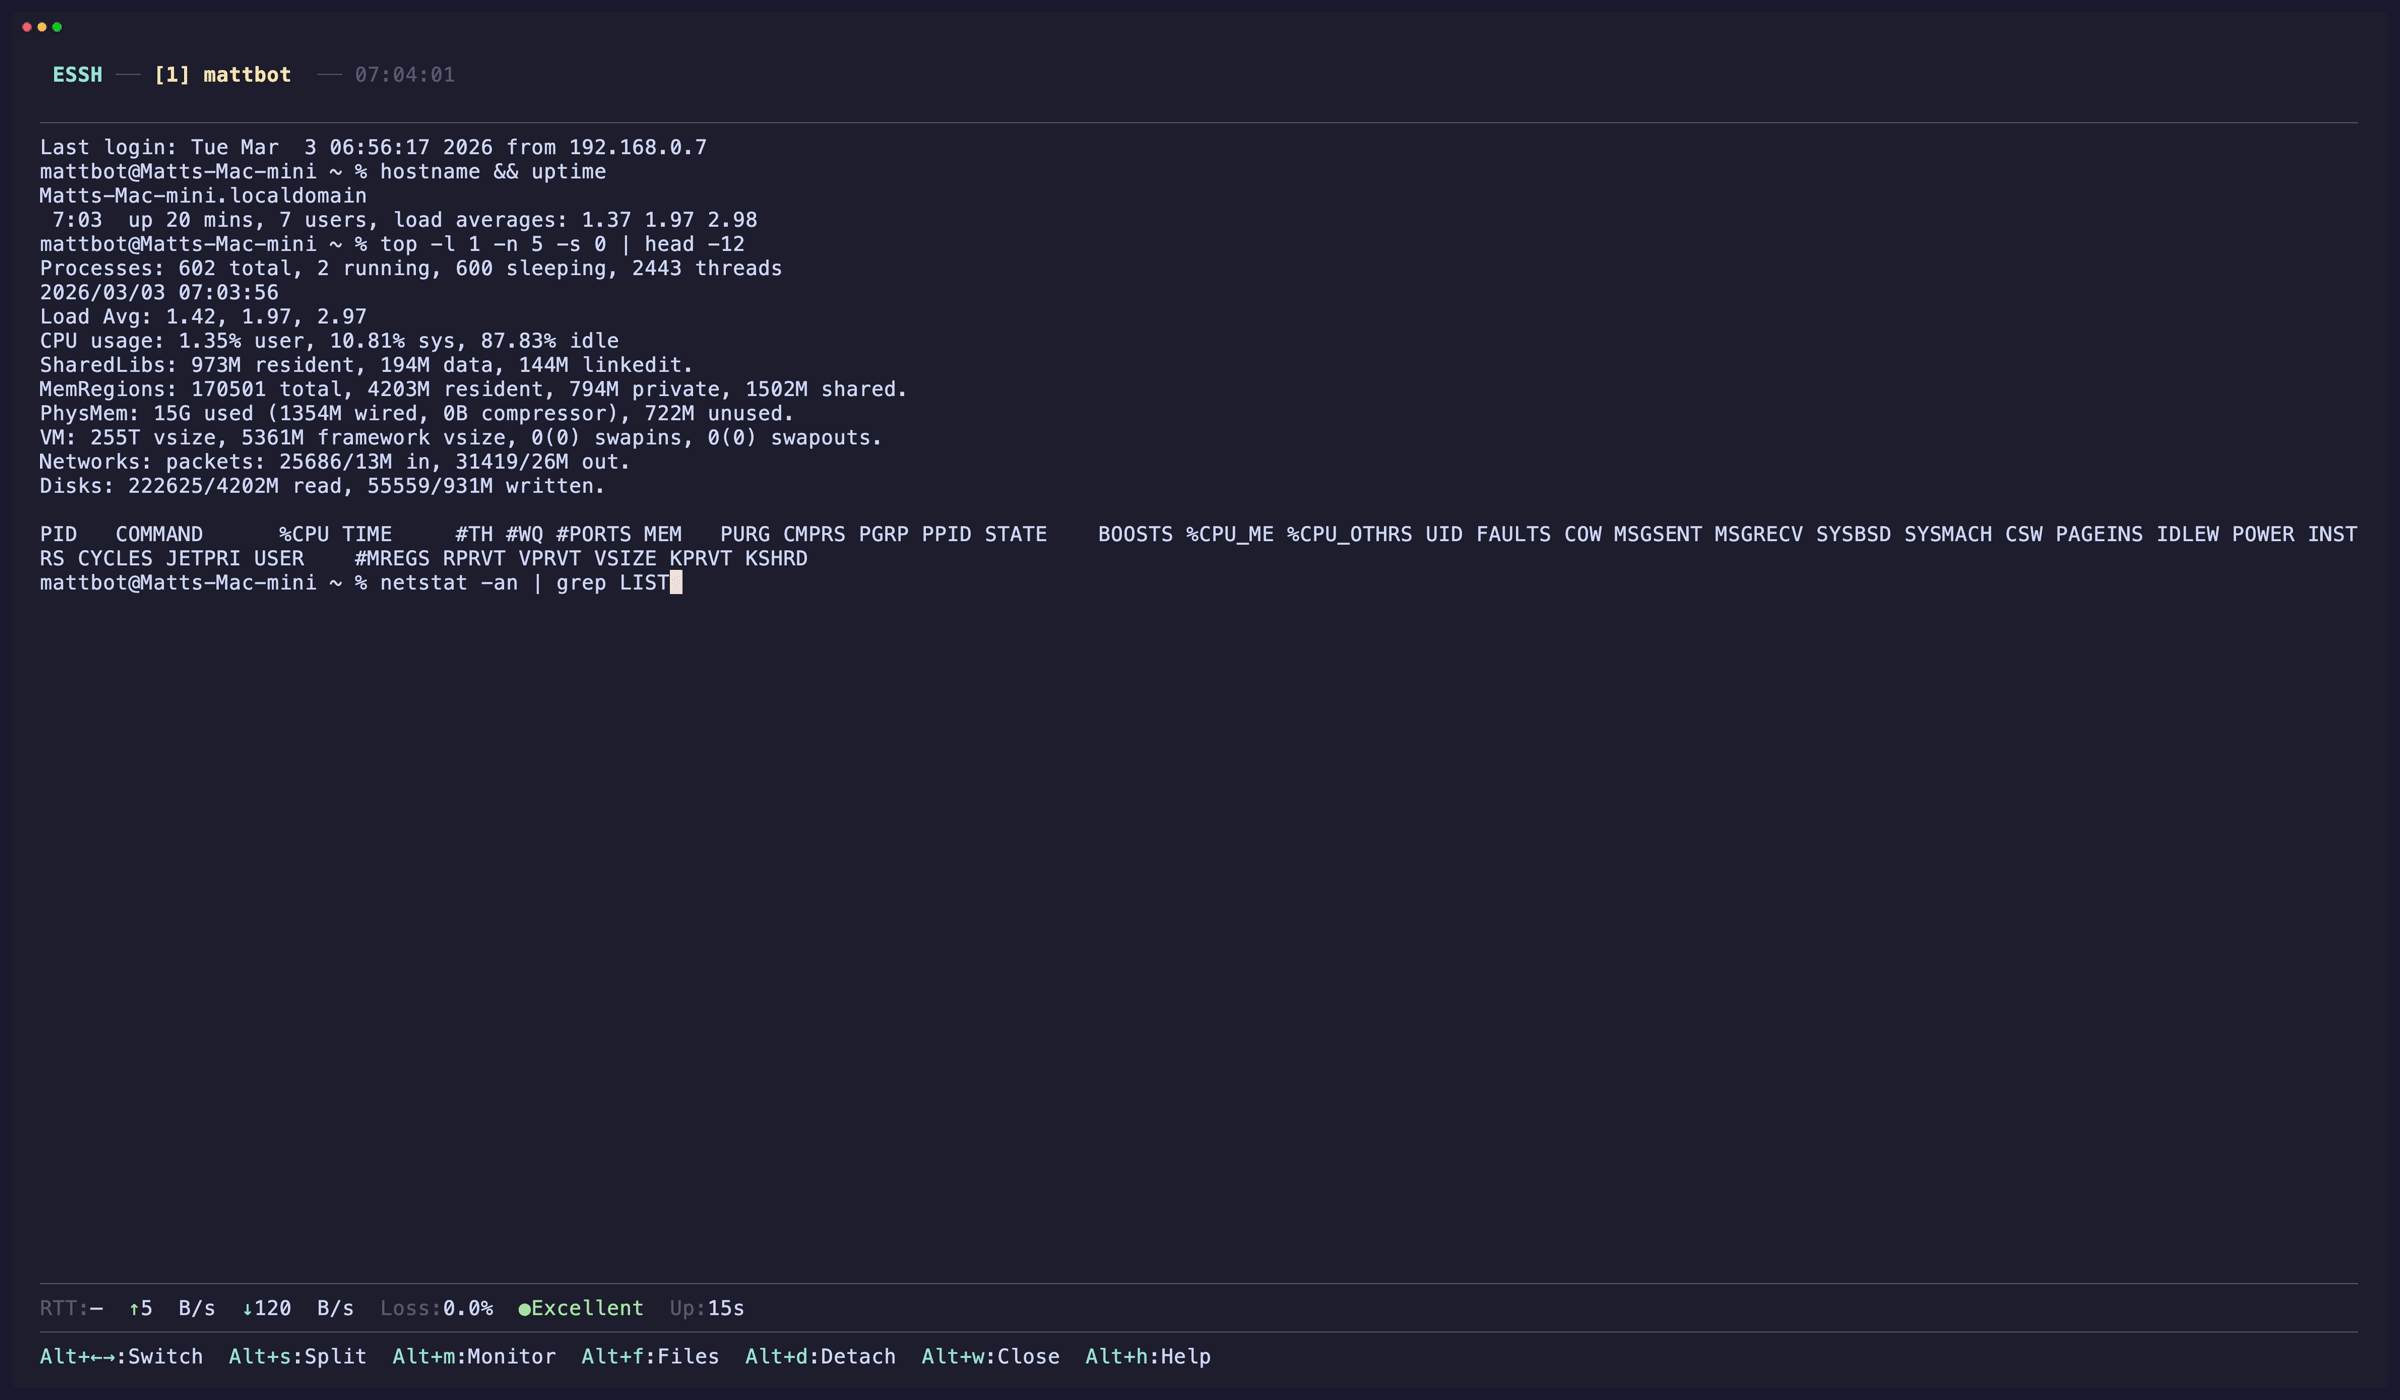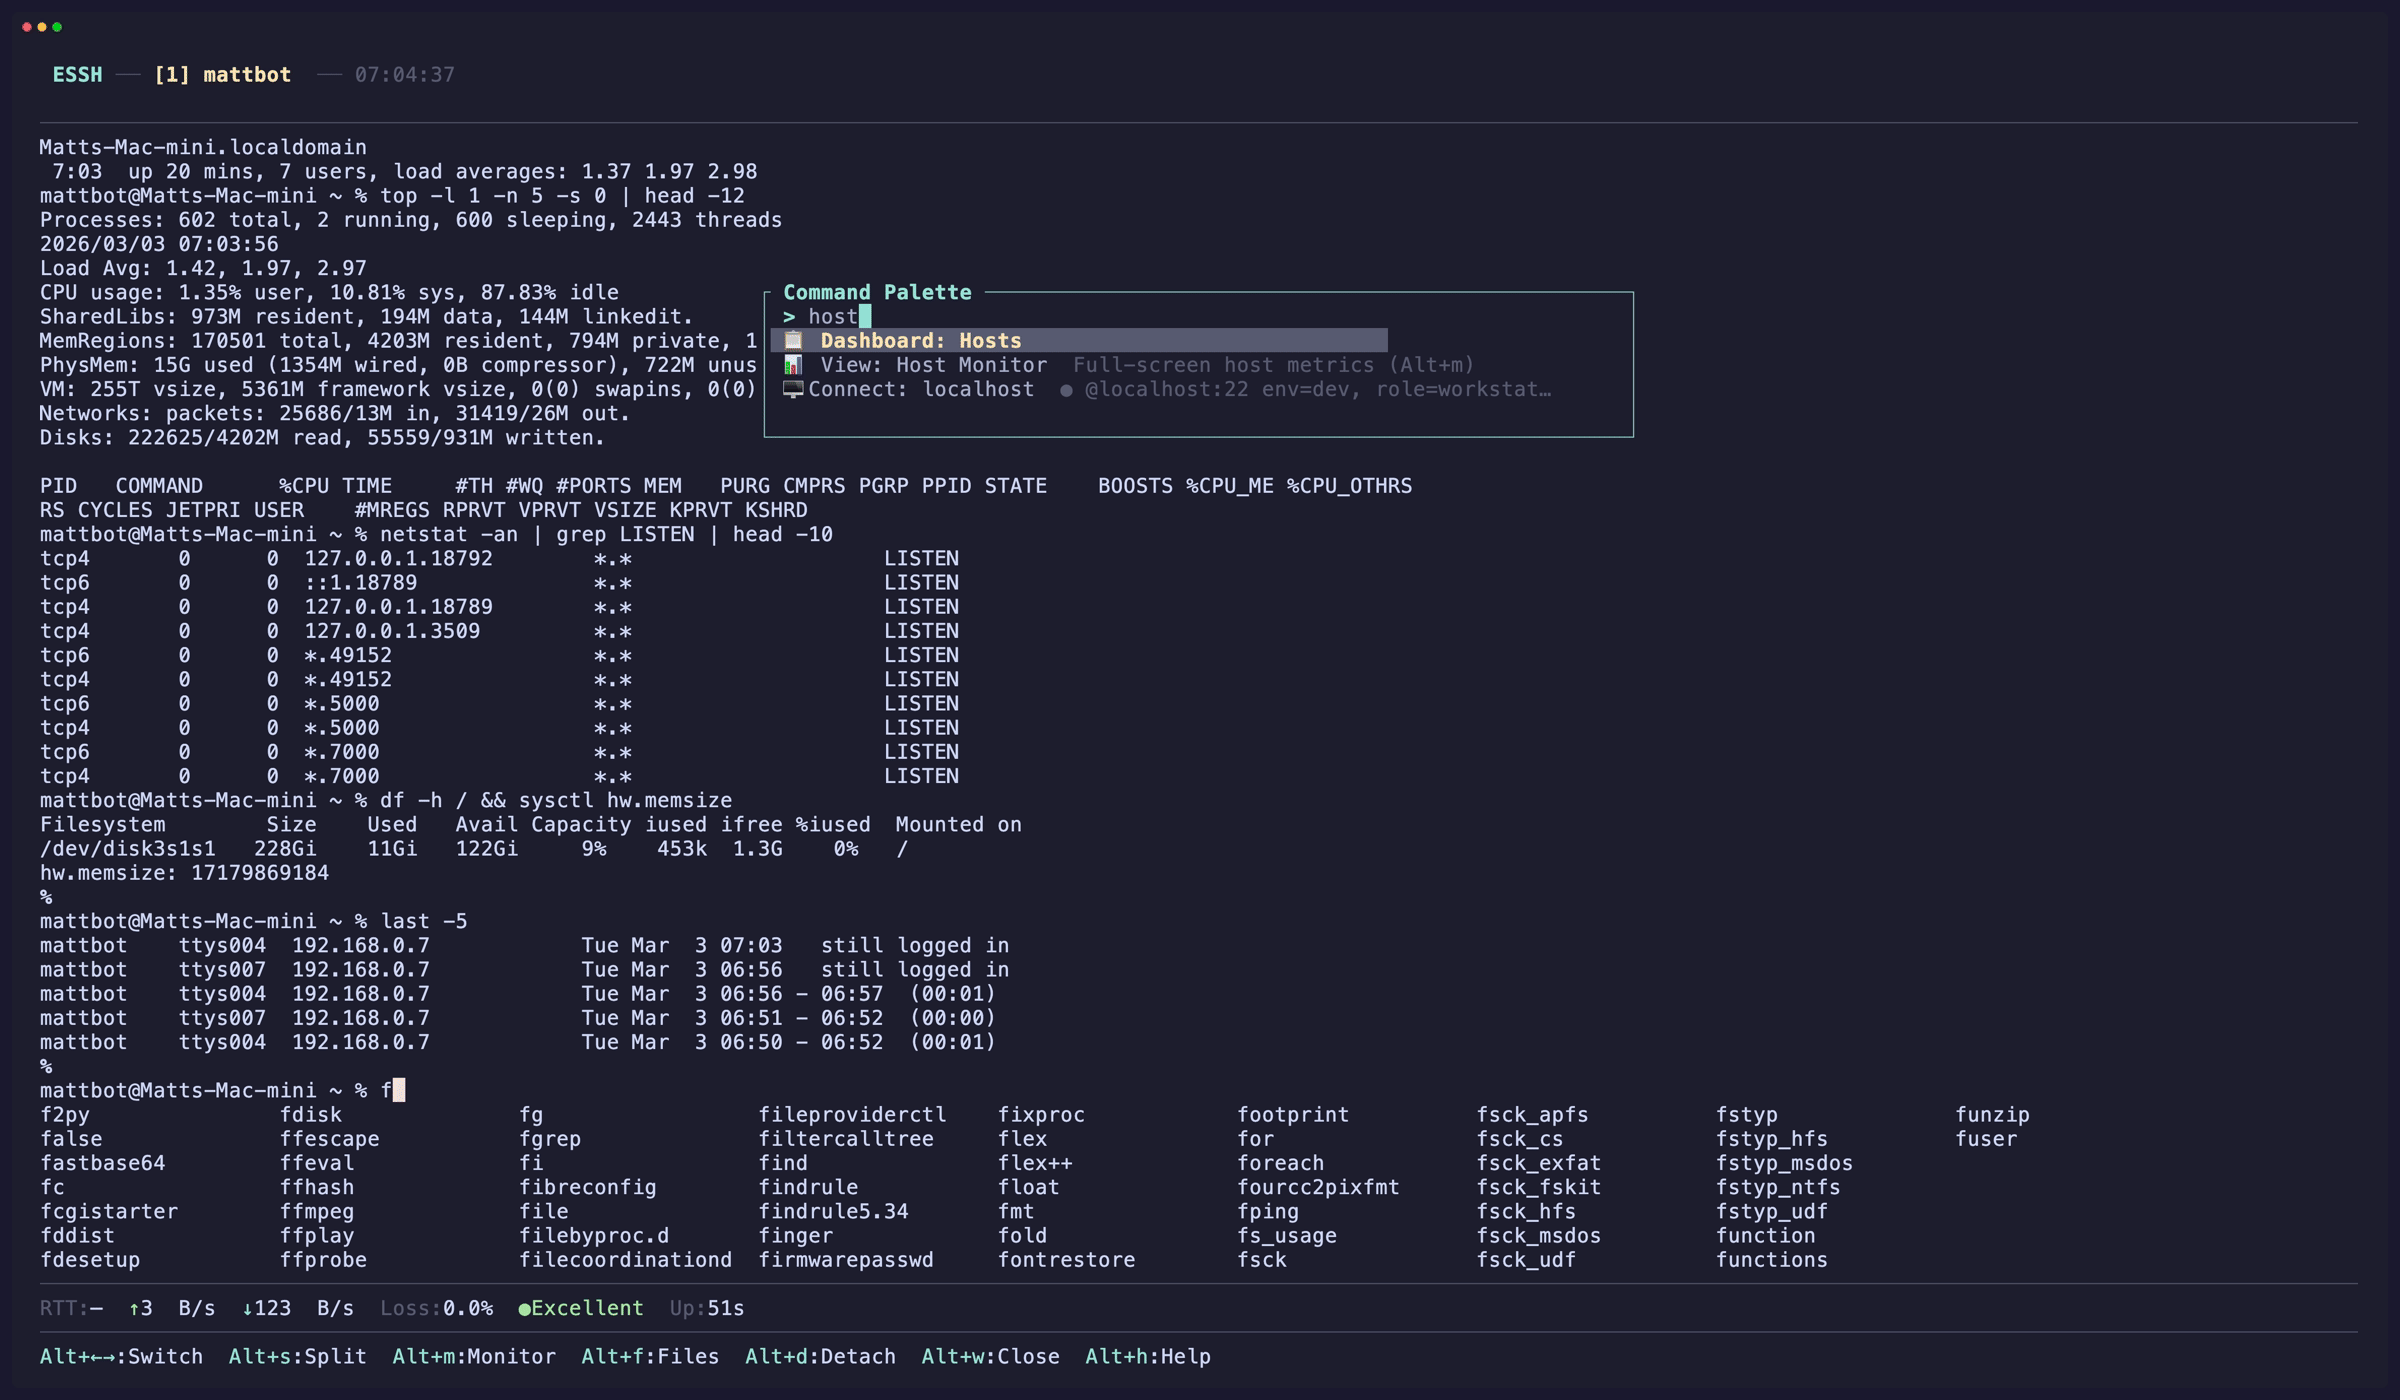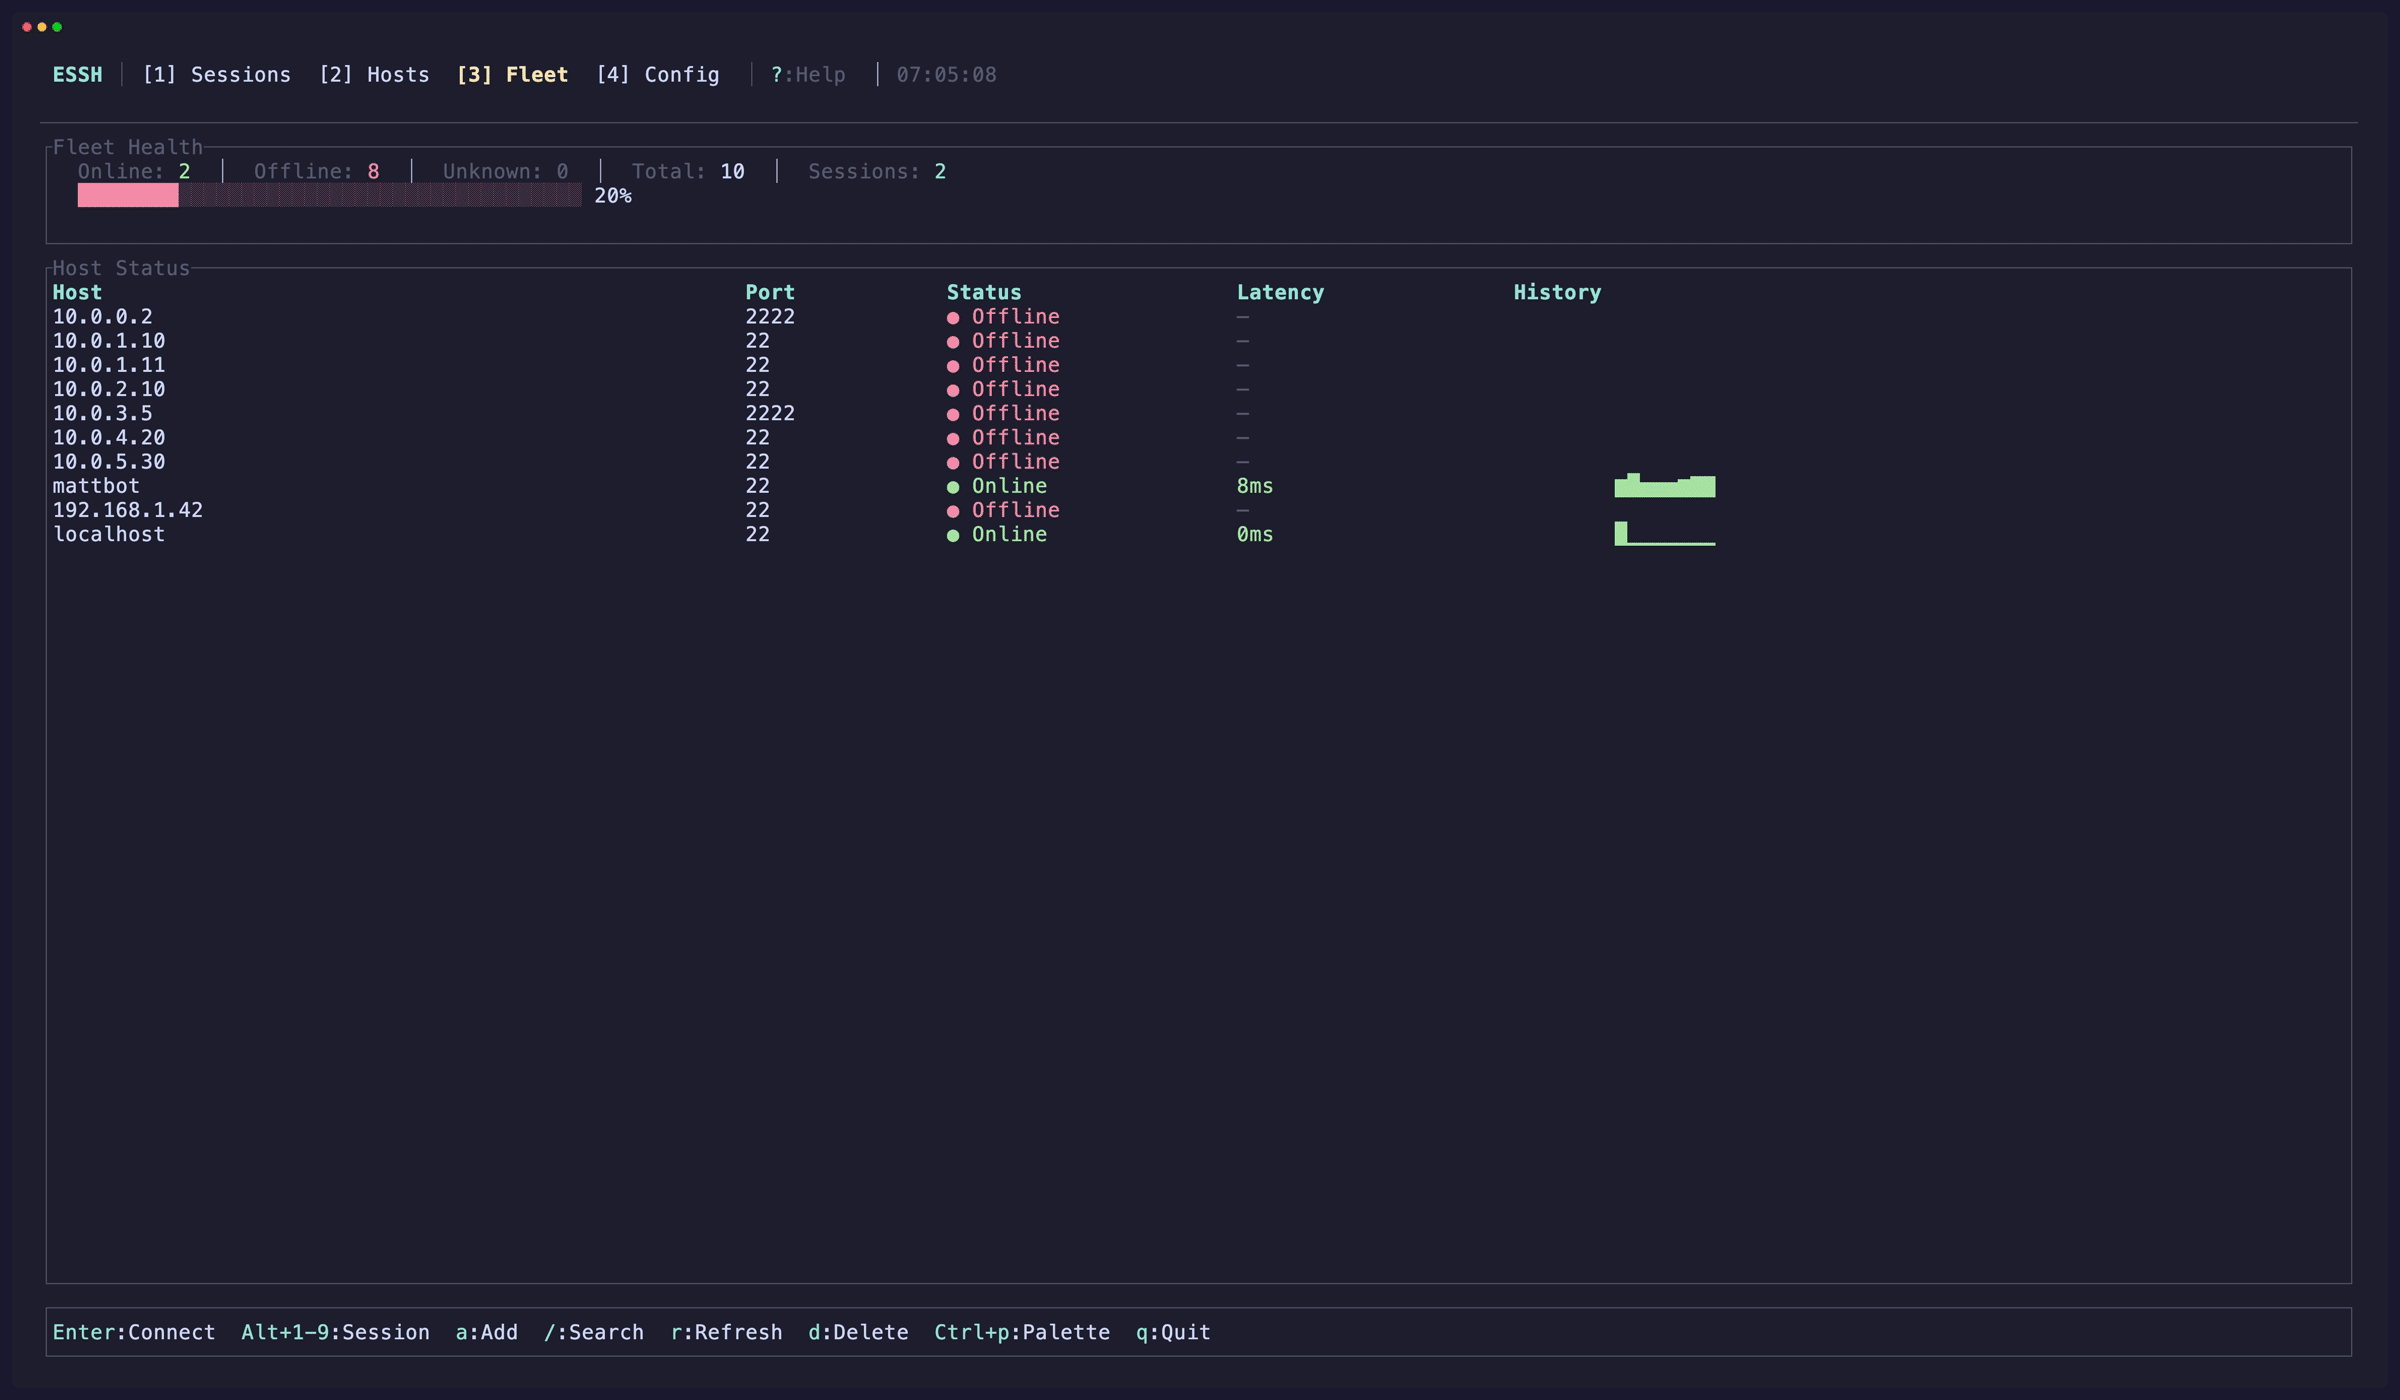 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
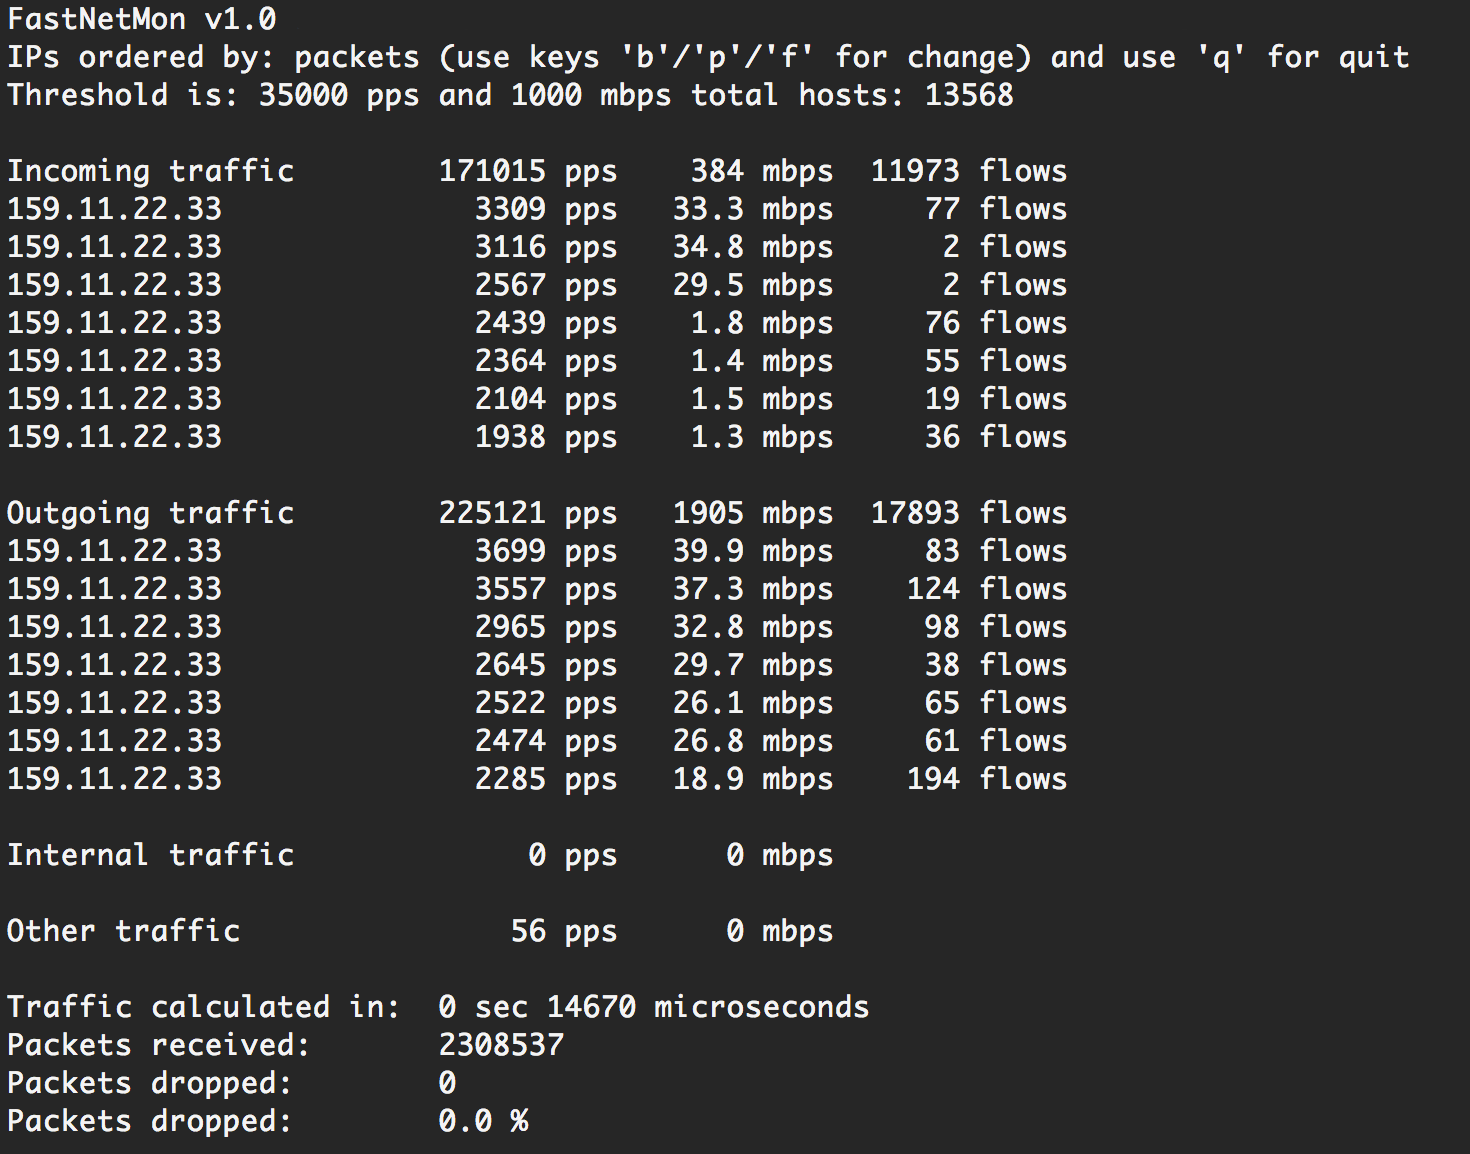 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
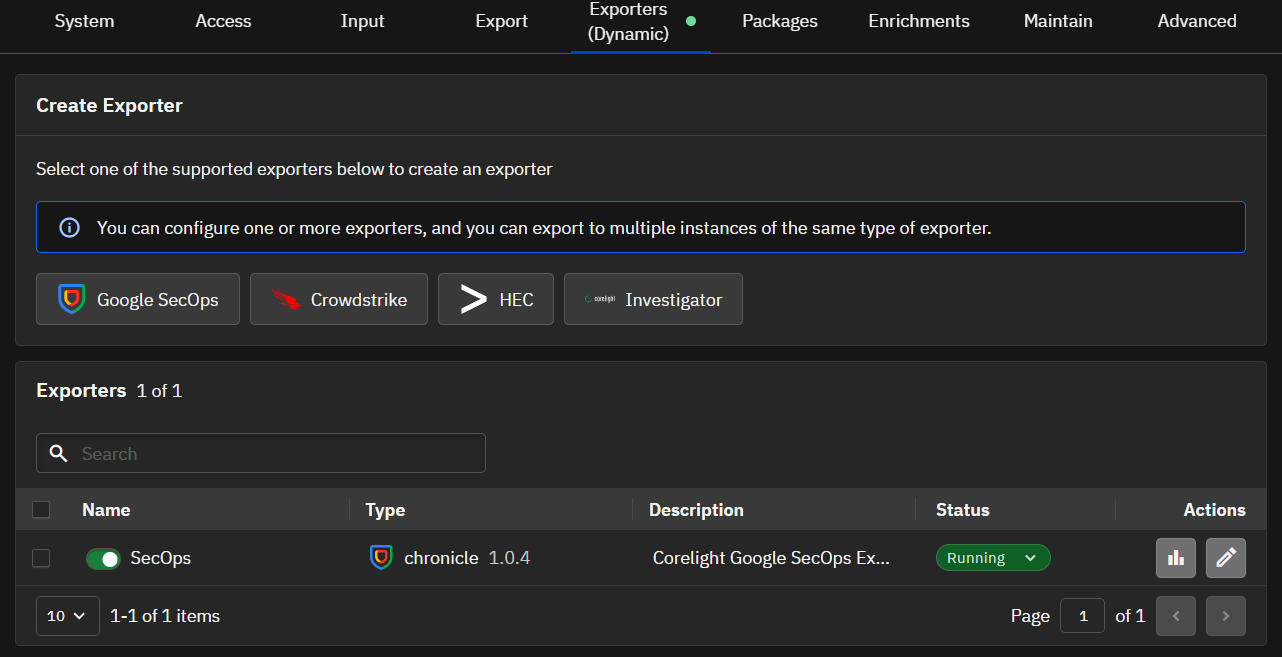 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
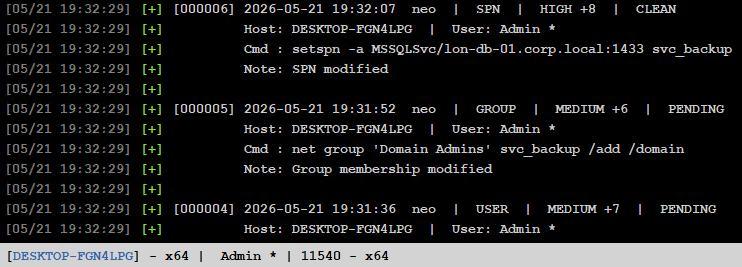 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
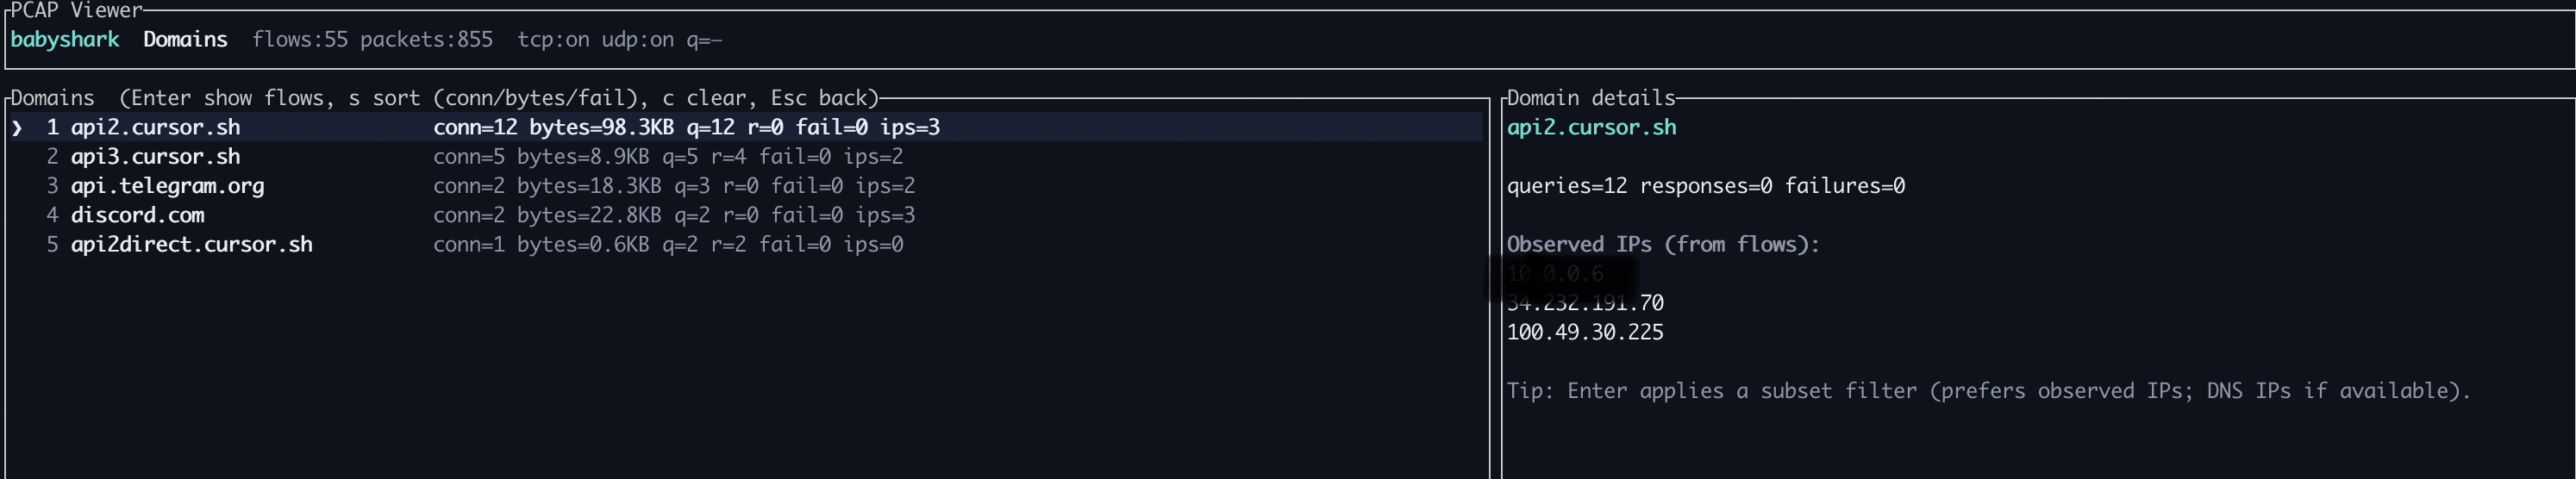 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 hackwarts12/burp-recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
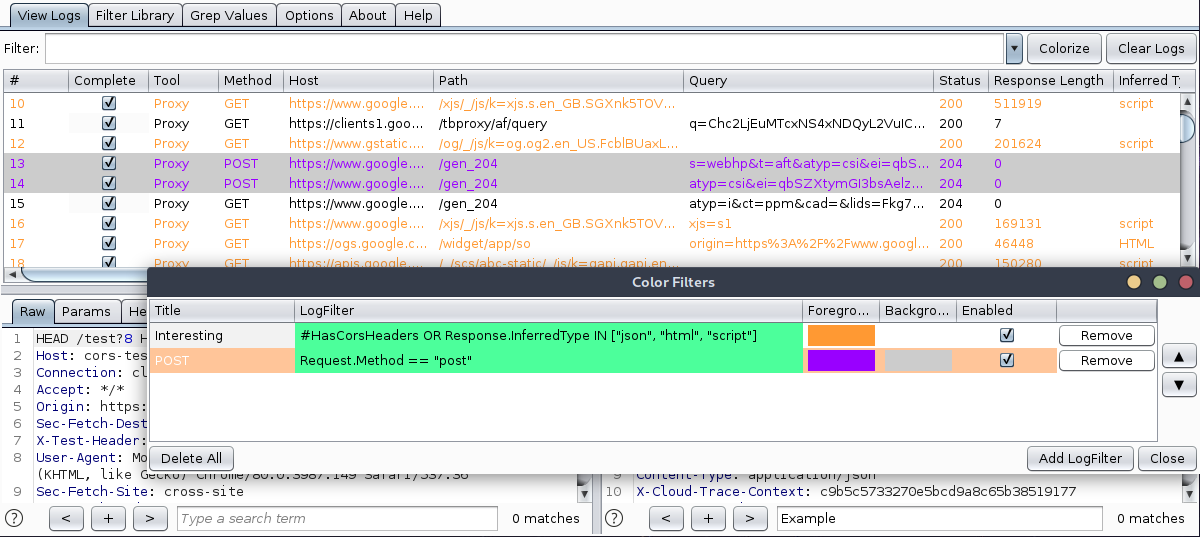 nccgroup/loggerplusplus
Advanced Burp Suite Logging Extension
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
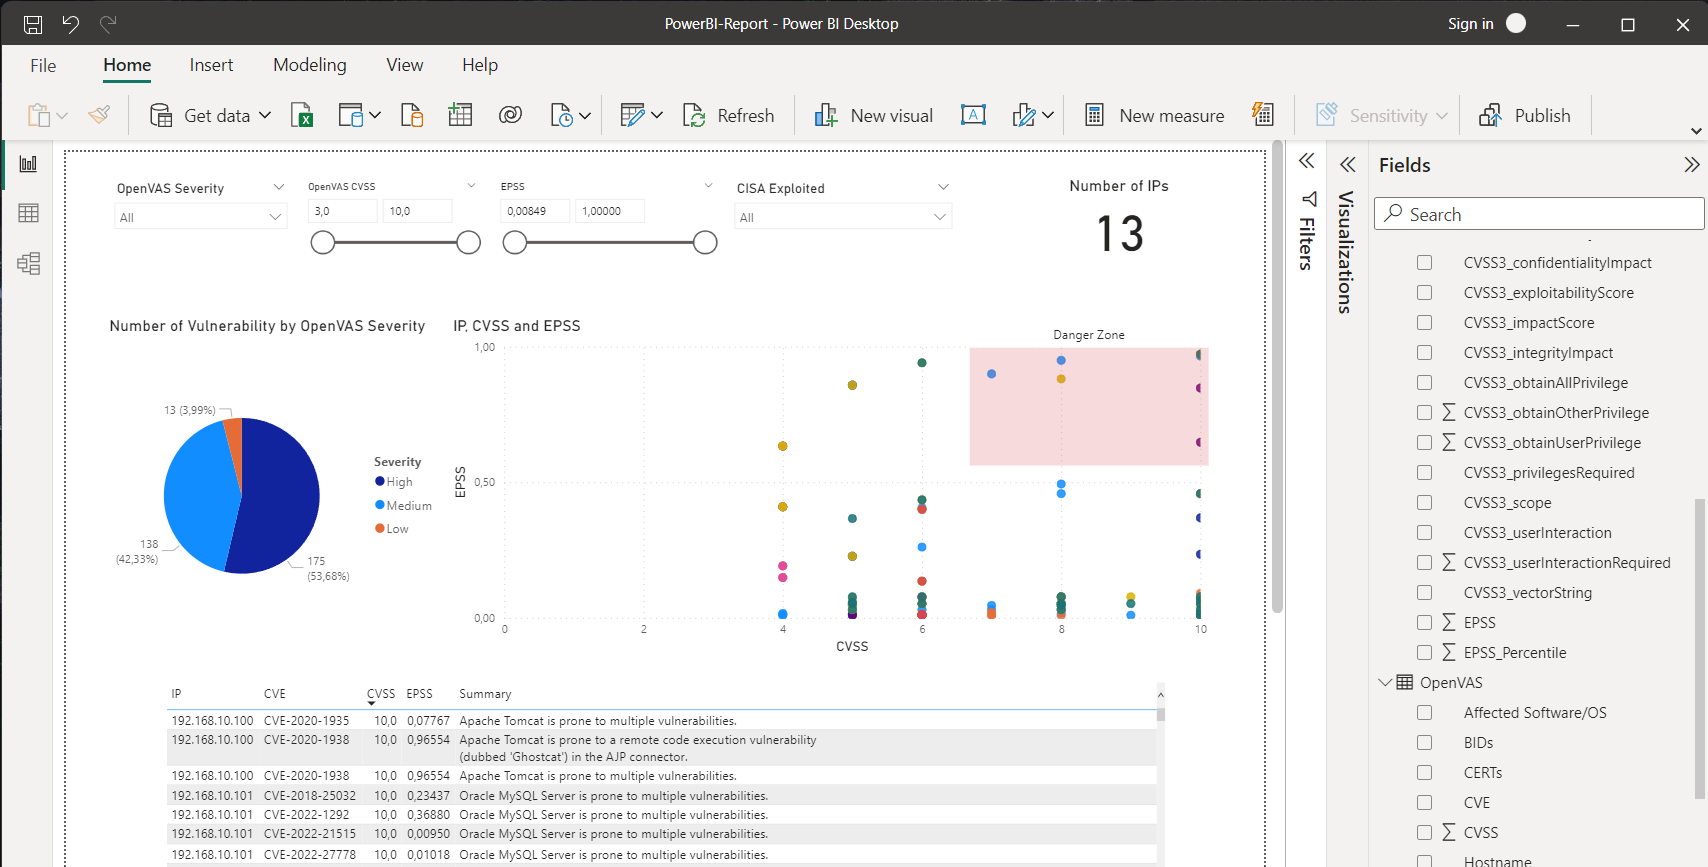 trinitor/cve-vulnerability-information-downloader
Downloads and aggregates CVSS, EPSS, and CISA known exploited vulnerability data into unified JSON/CSV files and a SQLite database. Enriches…