
trivy-db
 aquasecurity/trivy-db
Build and manage Trivy vulnerability databases by aggregating security advisories from NVD, Red Hat, Debian, and more. A CLI tool and library for…
threat-intelligenceutilities-frameworksvulnerability-analysis
aquasecurity/trivy-dbBuild and manage Trivy vulnerability databases by aggregating security advisories from NVD, Red Hat, Debian, and more. A CLI tool and library for…
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 aquasecurity/trivy-java-db
Builds a SQLite database of Maven artifacts (ArtifactID, GroupID, Version, SHA1) for Trivy's Java component vulnerability detection, enabling scans…
 google/tsunami-security-scanner
Tsunami is a general purpose network security scanner with an extensible plugin system for detecting high severity vulnerabilities with high…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
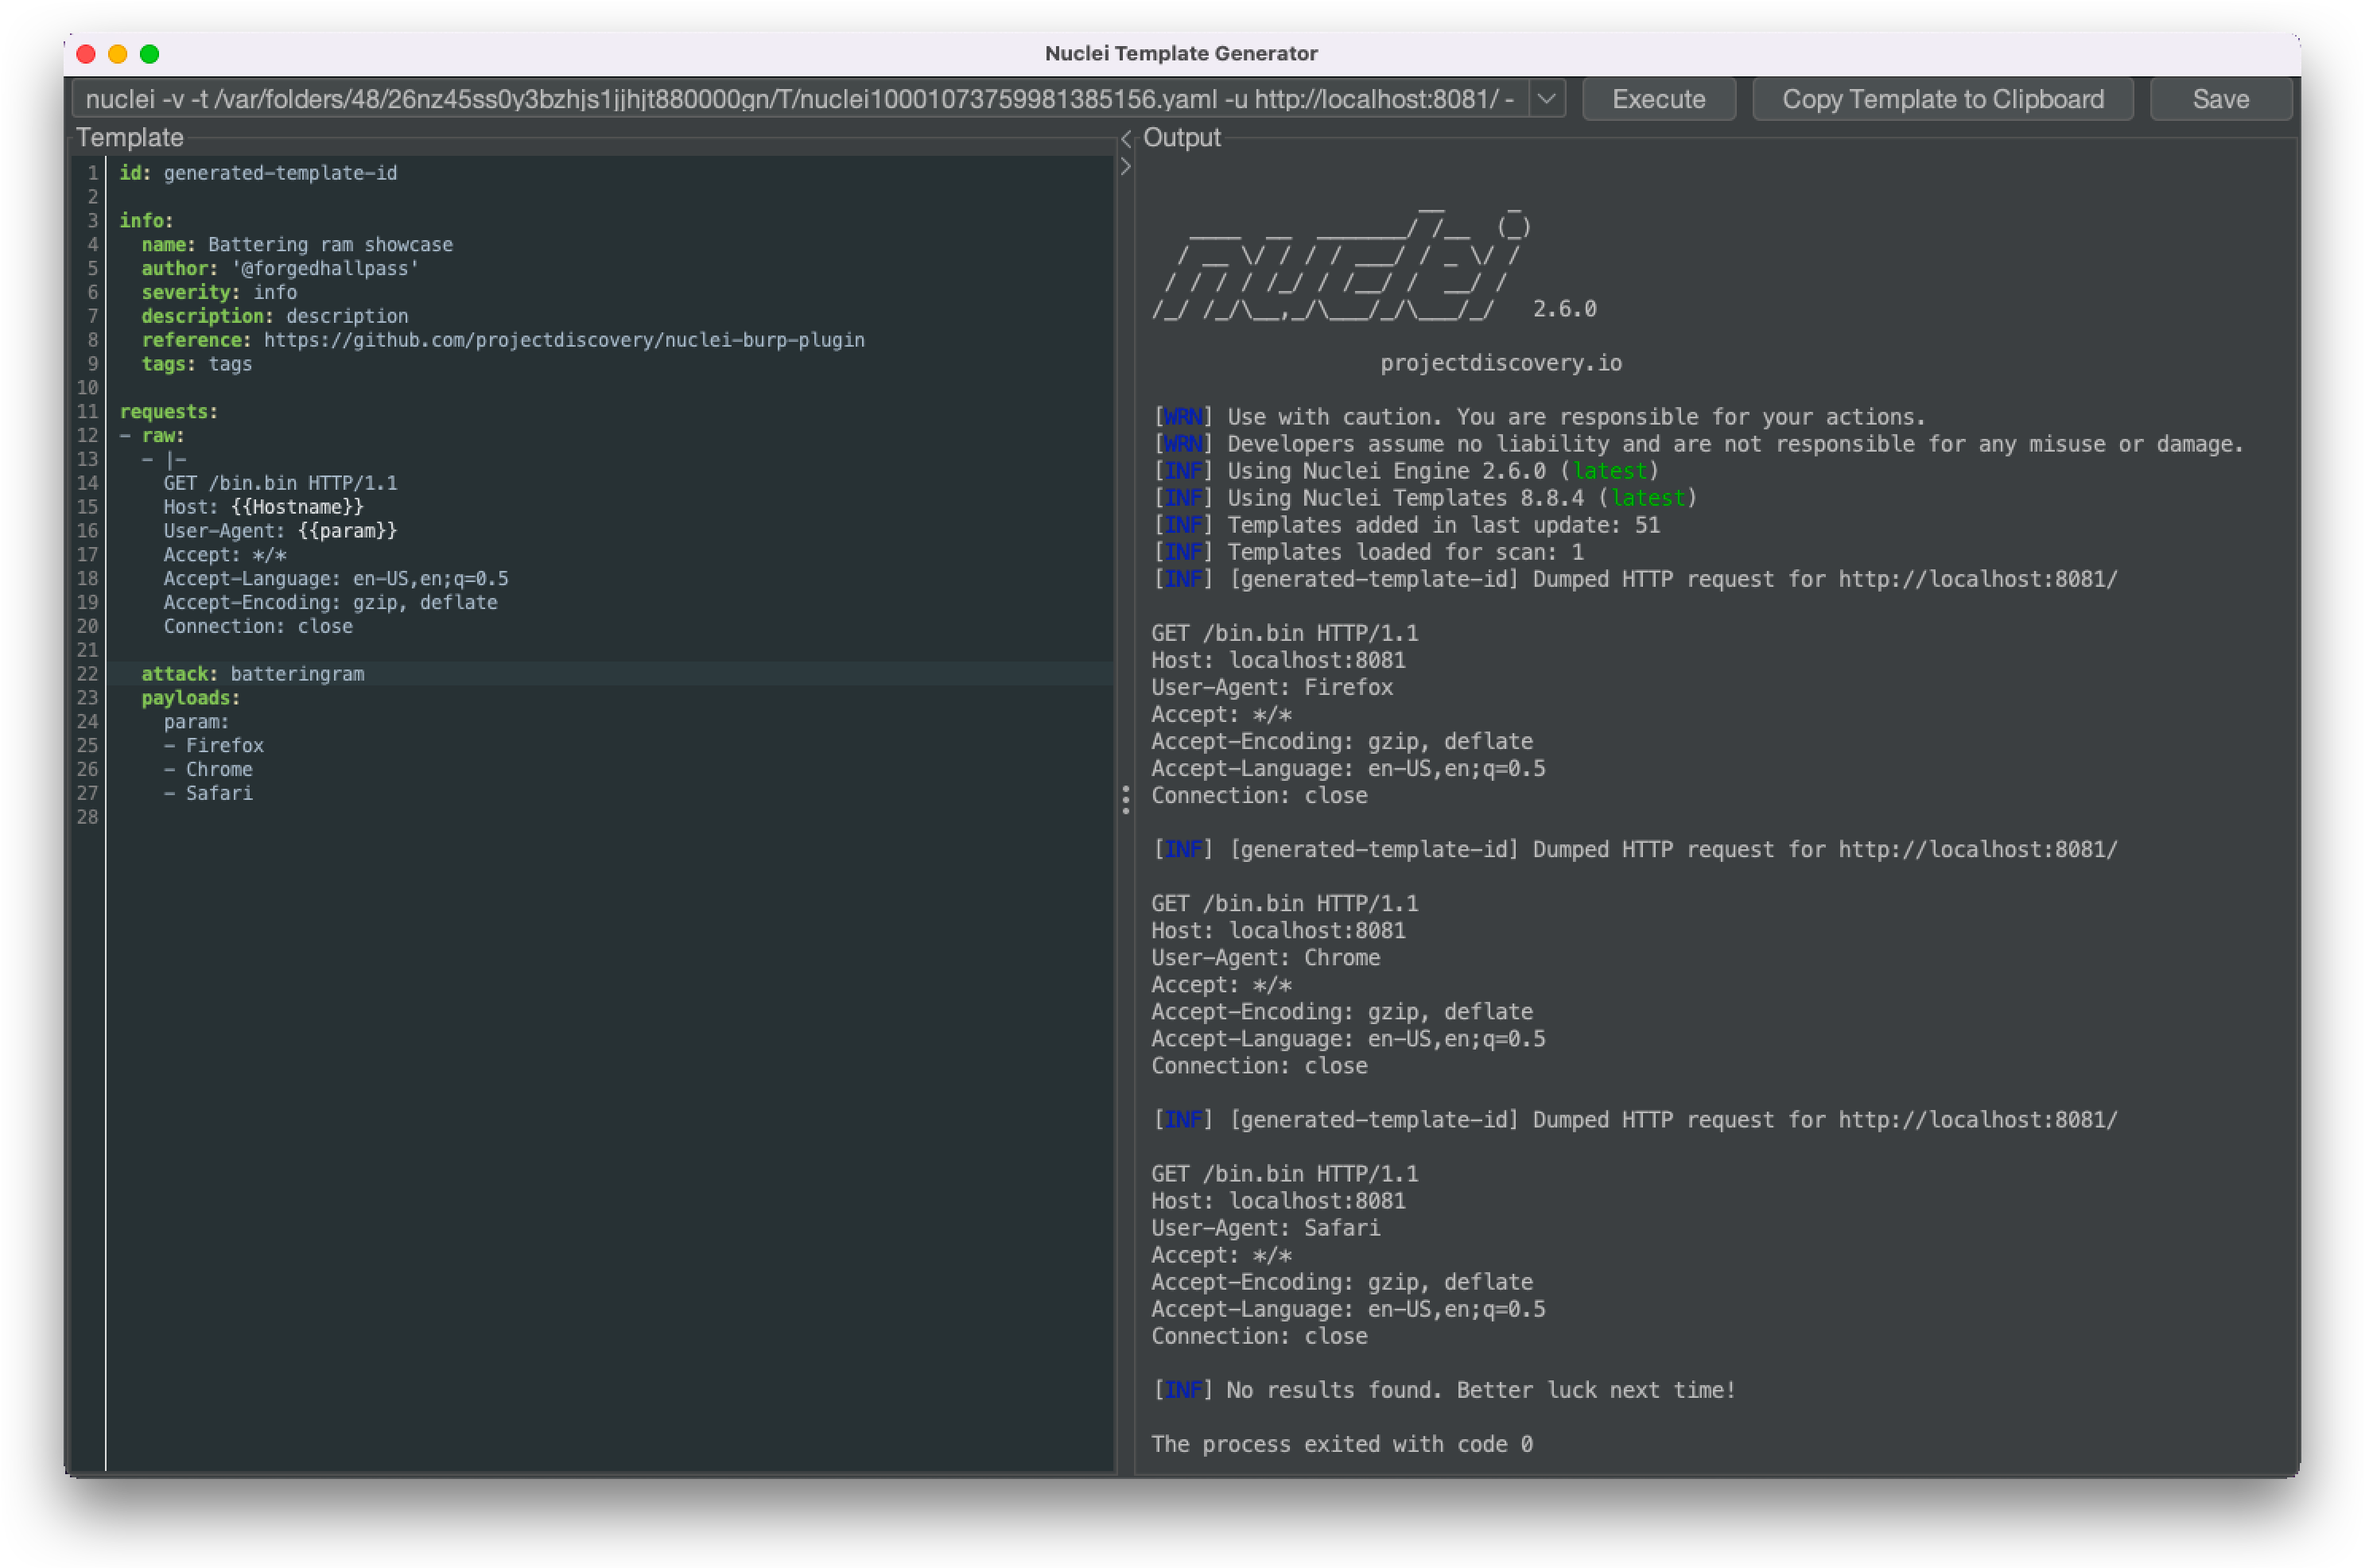 projectdiscovery/nuclei-burp-plugin
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 saml-toolkits/ruby-saml
Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…
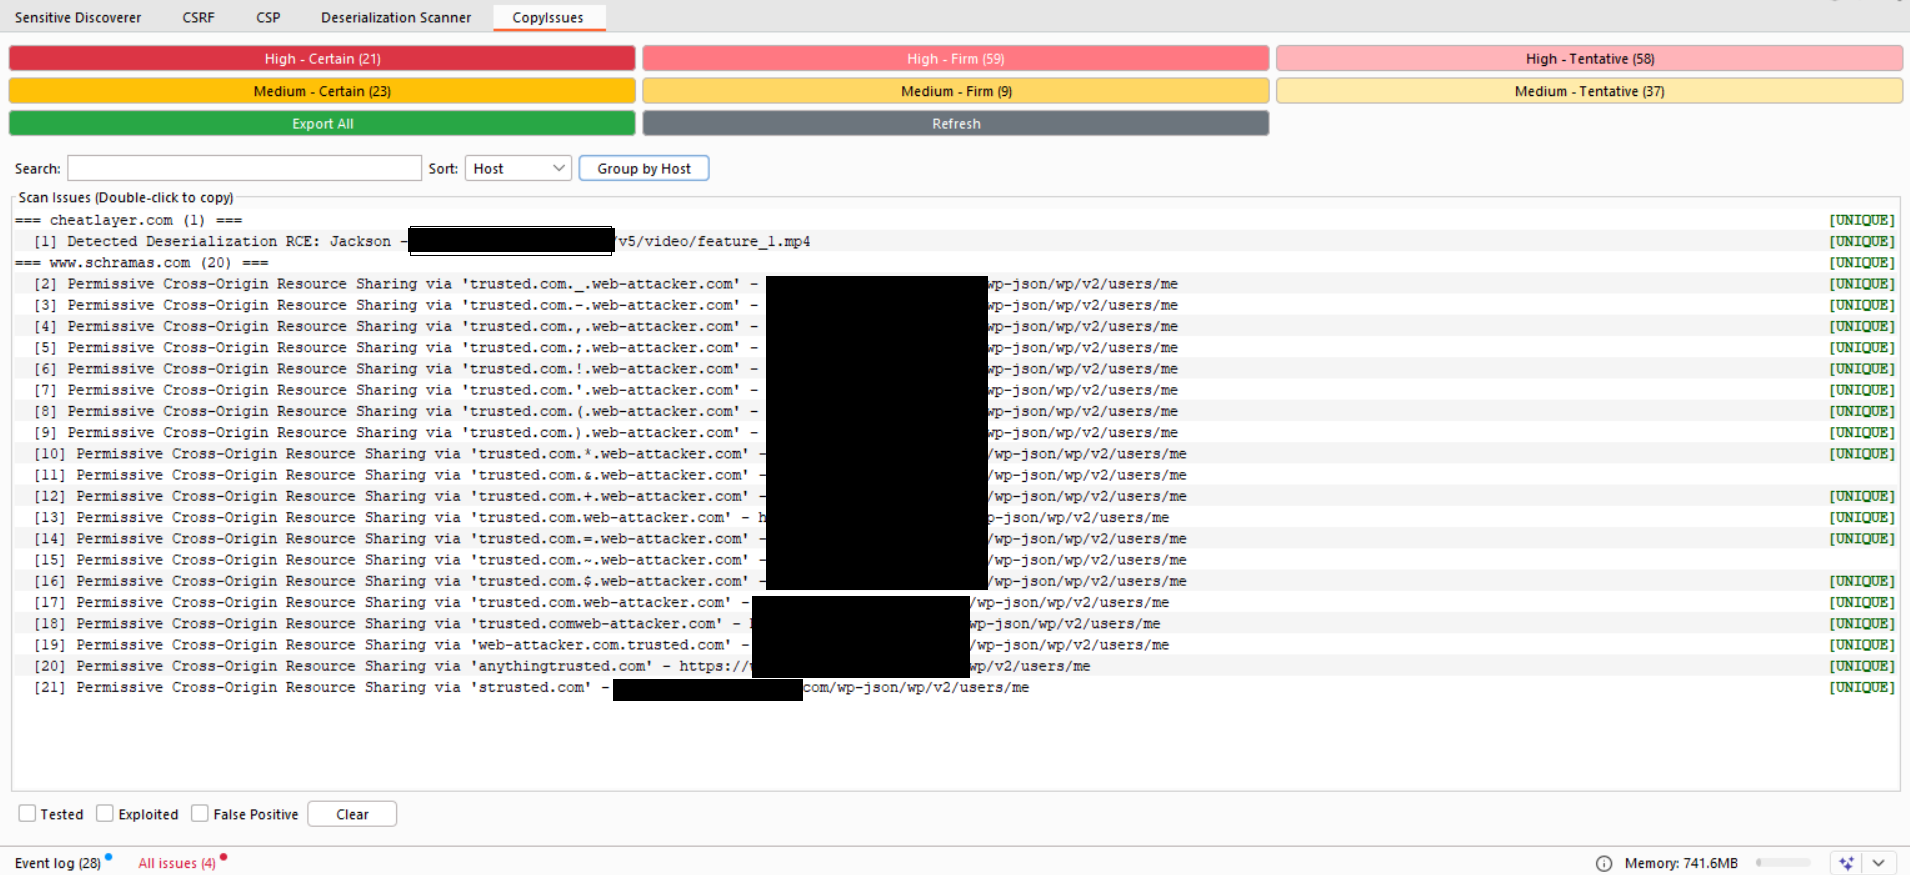 teycir/burpcopyissues
Burp suite extension that lets you easily copy issues
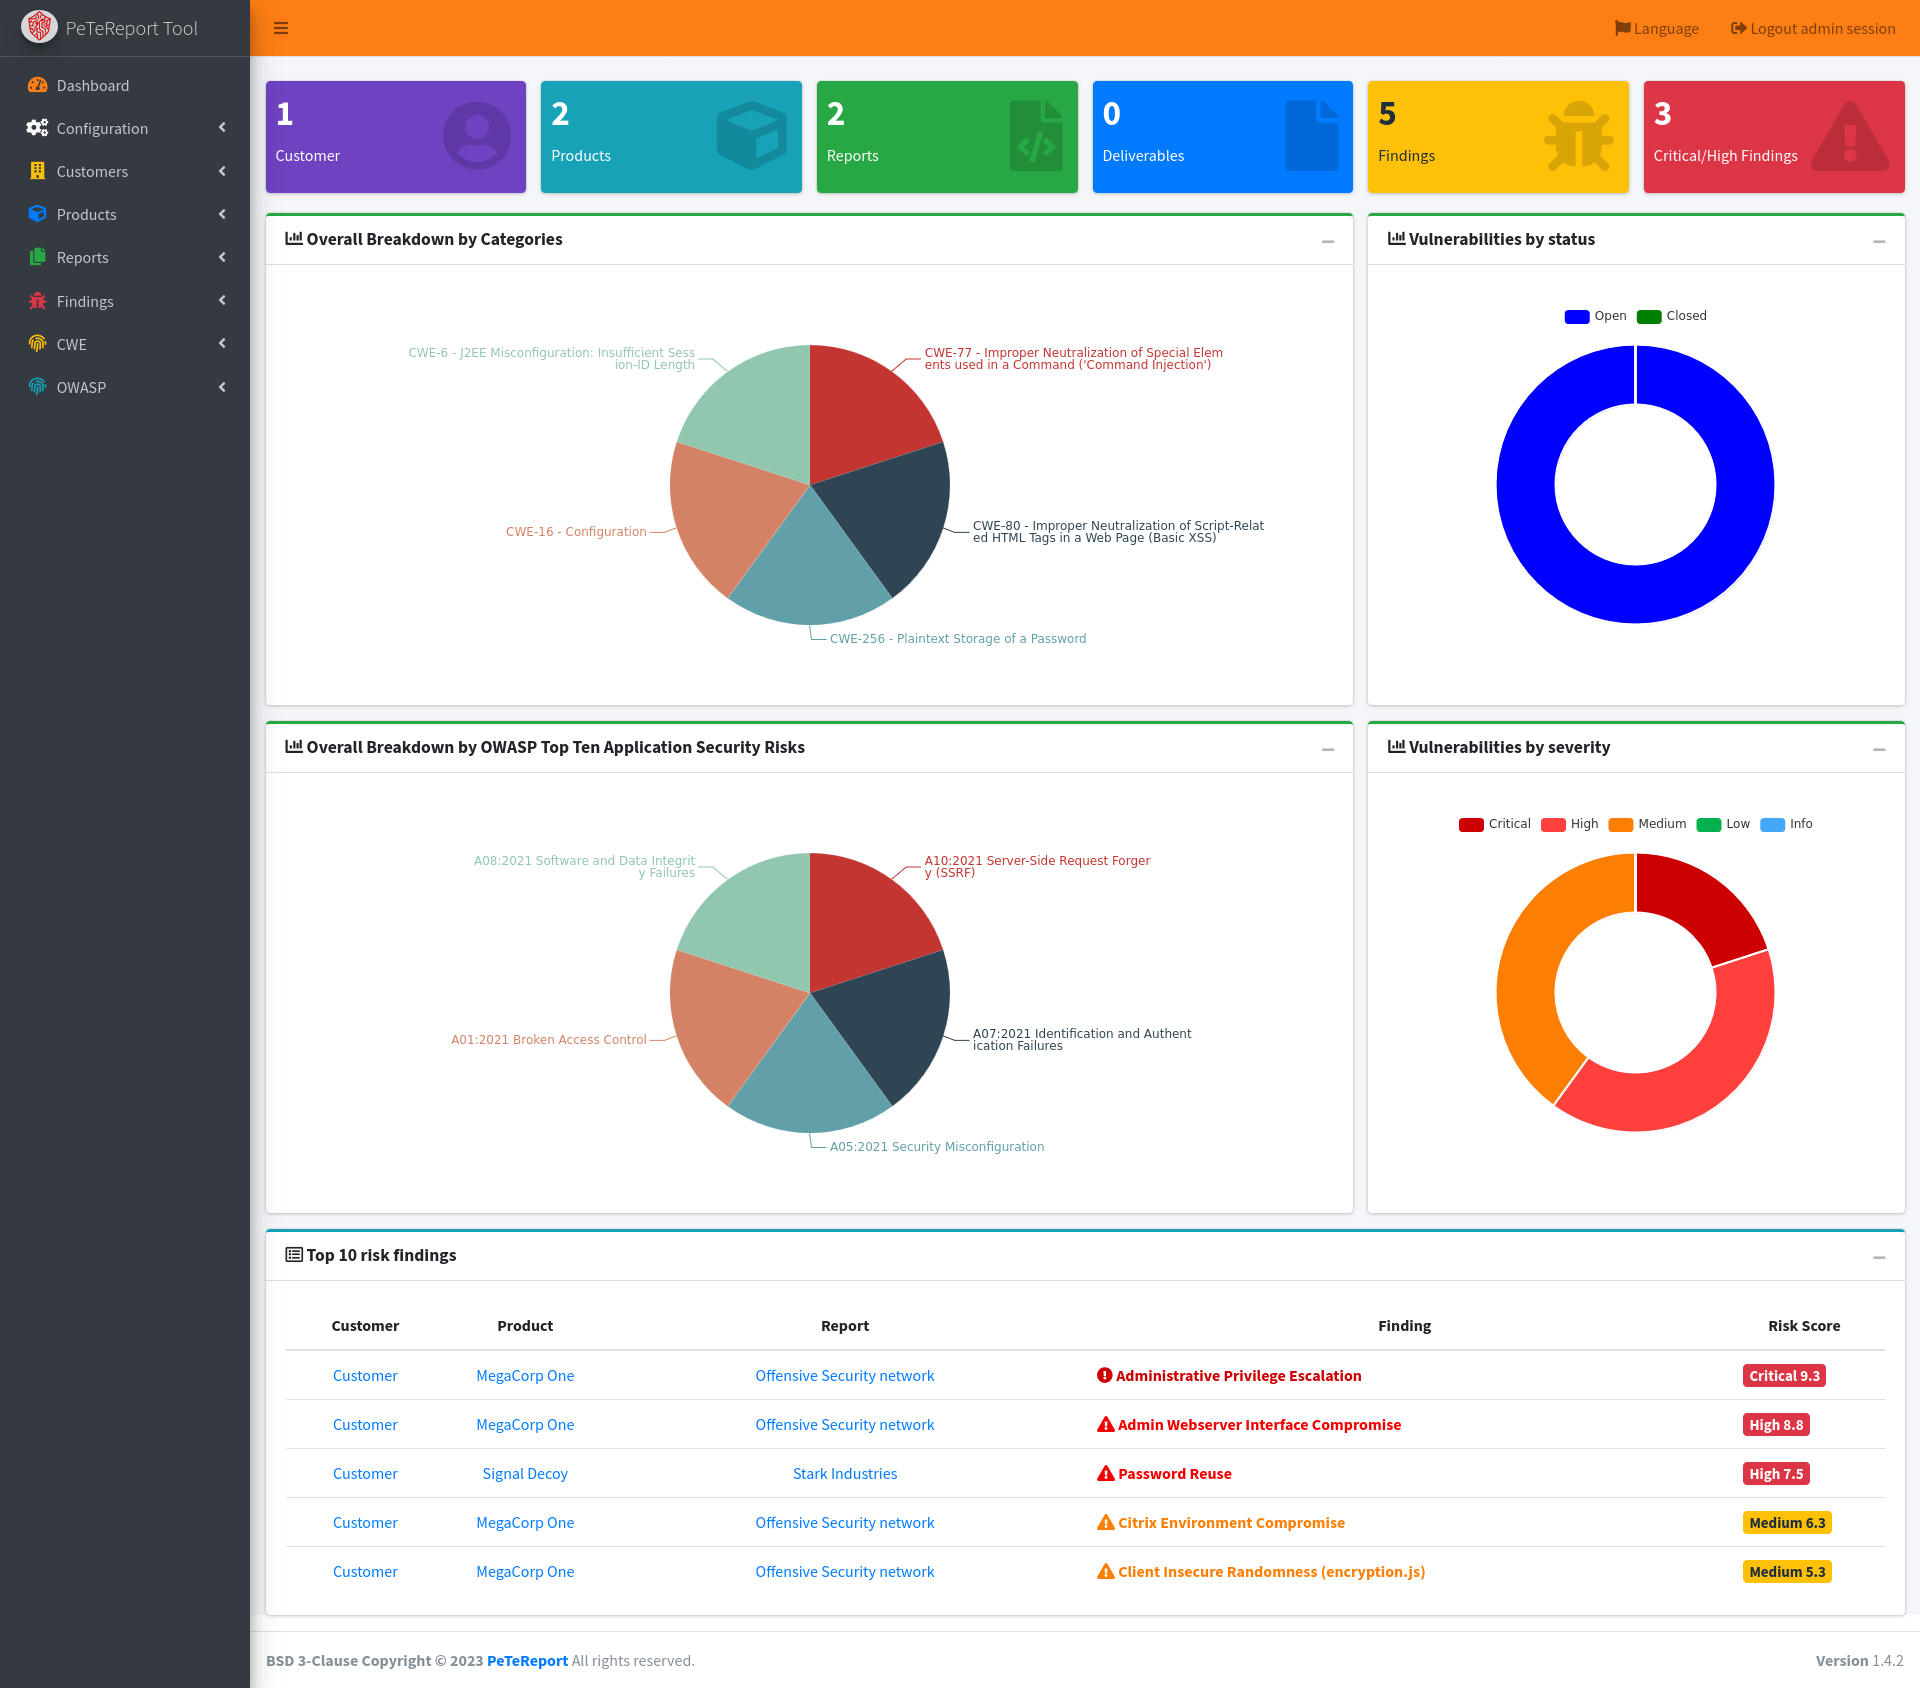 1modm/petereport
Open-source vulnerability reporting tool for pentesters and security researchers. Manages finding templates, generates reports in HTML, PDF, CSV,…
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2023-37460_4-7-1
Java library for creating and extracting archives (ZIP, tar, JAR) with integrated security patch for a reported vulnerability, used as a dependency…
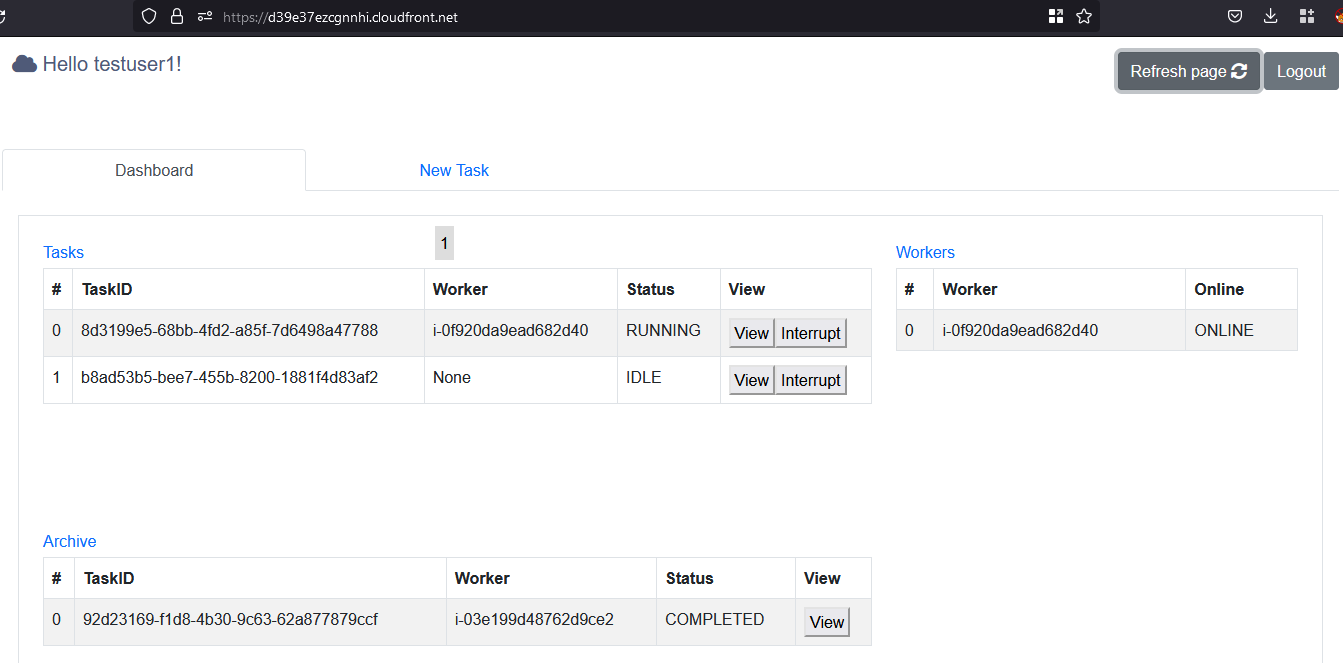 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
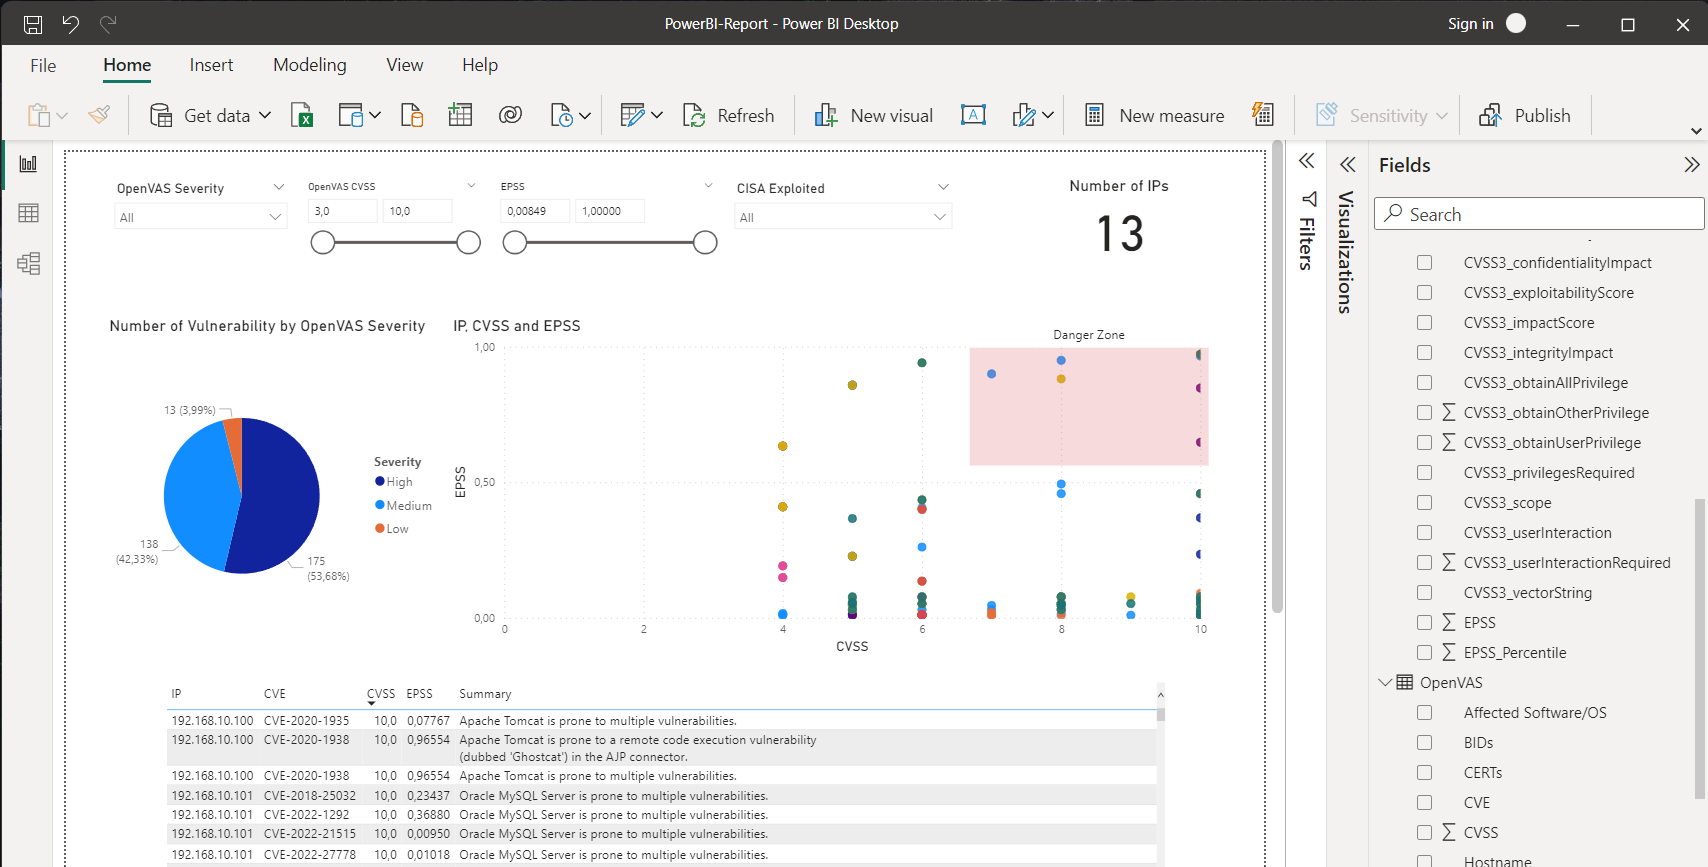 trinitor/cve-vulnerability-information-downloader
Downloads and aggregates CVSS, EPSS, and CISA known exploited vulnerability data into unified JSON/CSV files and a SQLite database. Enriches…
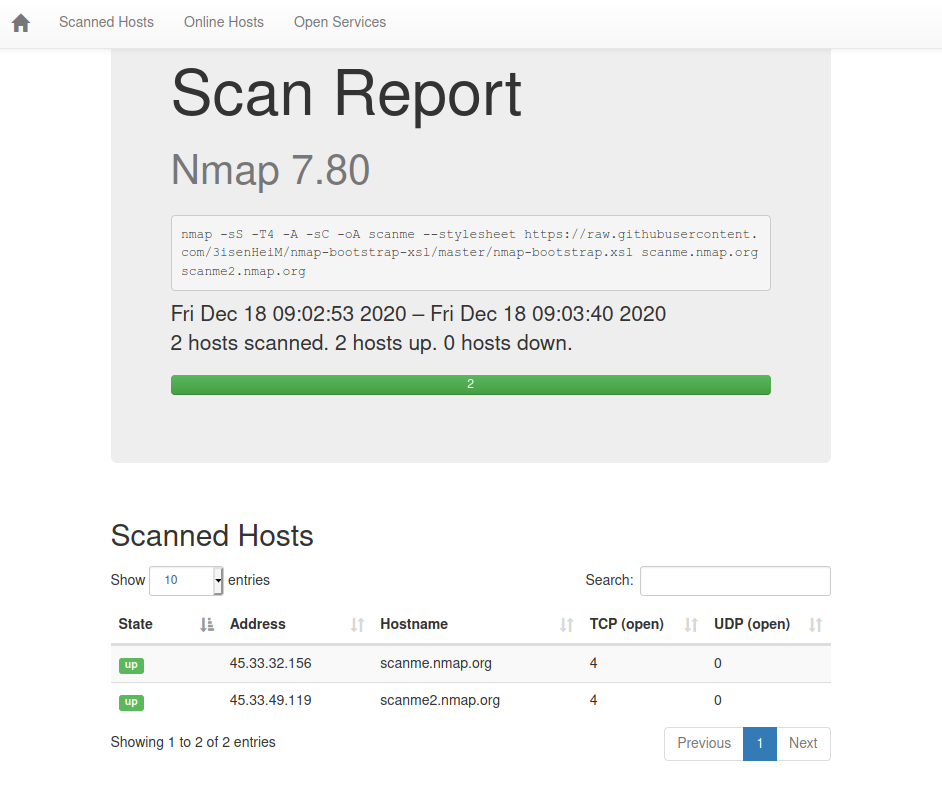 honze-net/nmap-bootstrap-xsl
A Nmap XSL implementation with Bootstrap.
 secxena/credcheck
Modular credential validation framework with active and passive (regex-based) checking modes for penetration testers. Supports multiple services via…
 daehee/nvd
Fast, simple library in Go to fetch CVEs from the National Vulnerability Database feeds
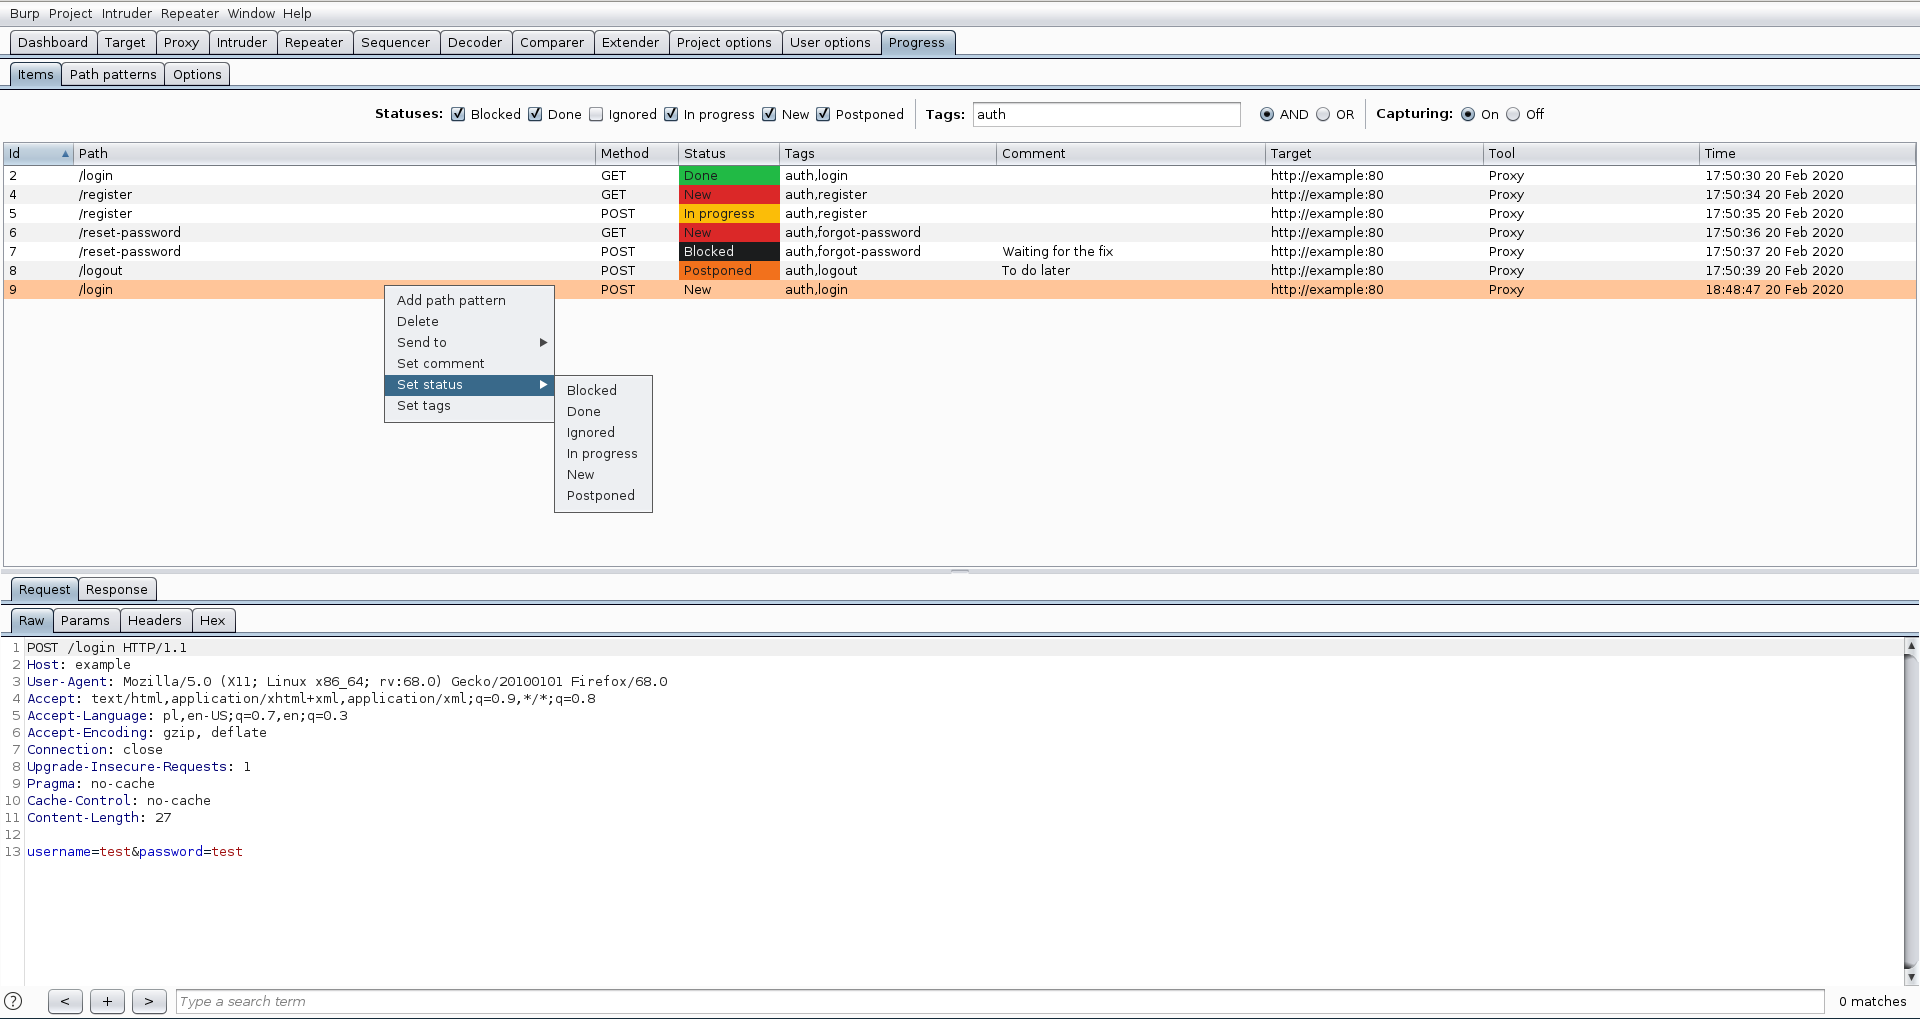 dariusztytko/progress-burp
Burp Suite extension to track vulnerability assessment progress
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis