

scripts
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
84
clausing/scriptsCollection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
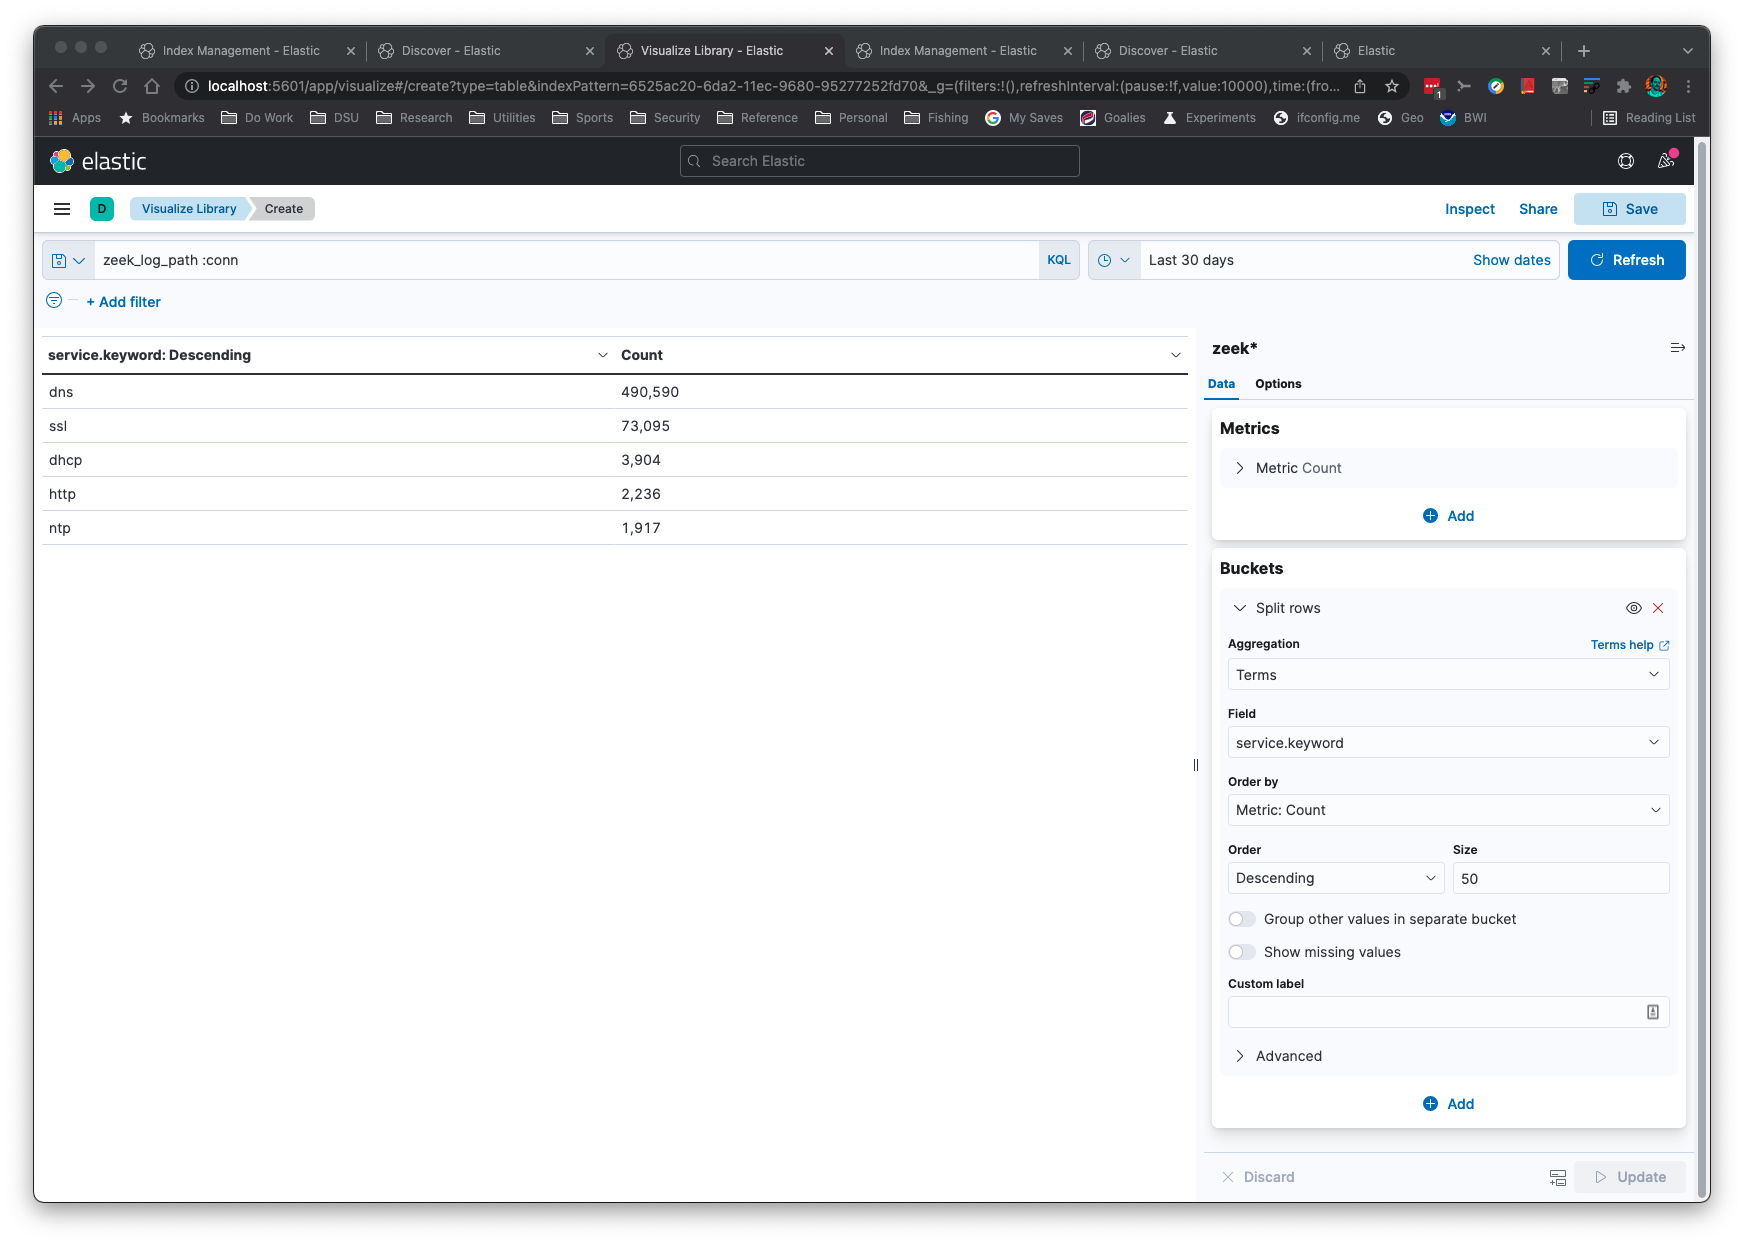 corelight/zeek2es
A Python application to filter and transfer Zeek logs to Elastic/OpenSearch+Humio. This app can also output pure JSON logs to stdout for further…
 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 corelight/ecs-templates
Corelight or Zeek Elastic Common Schema Templates
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
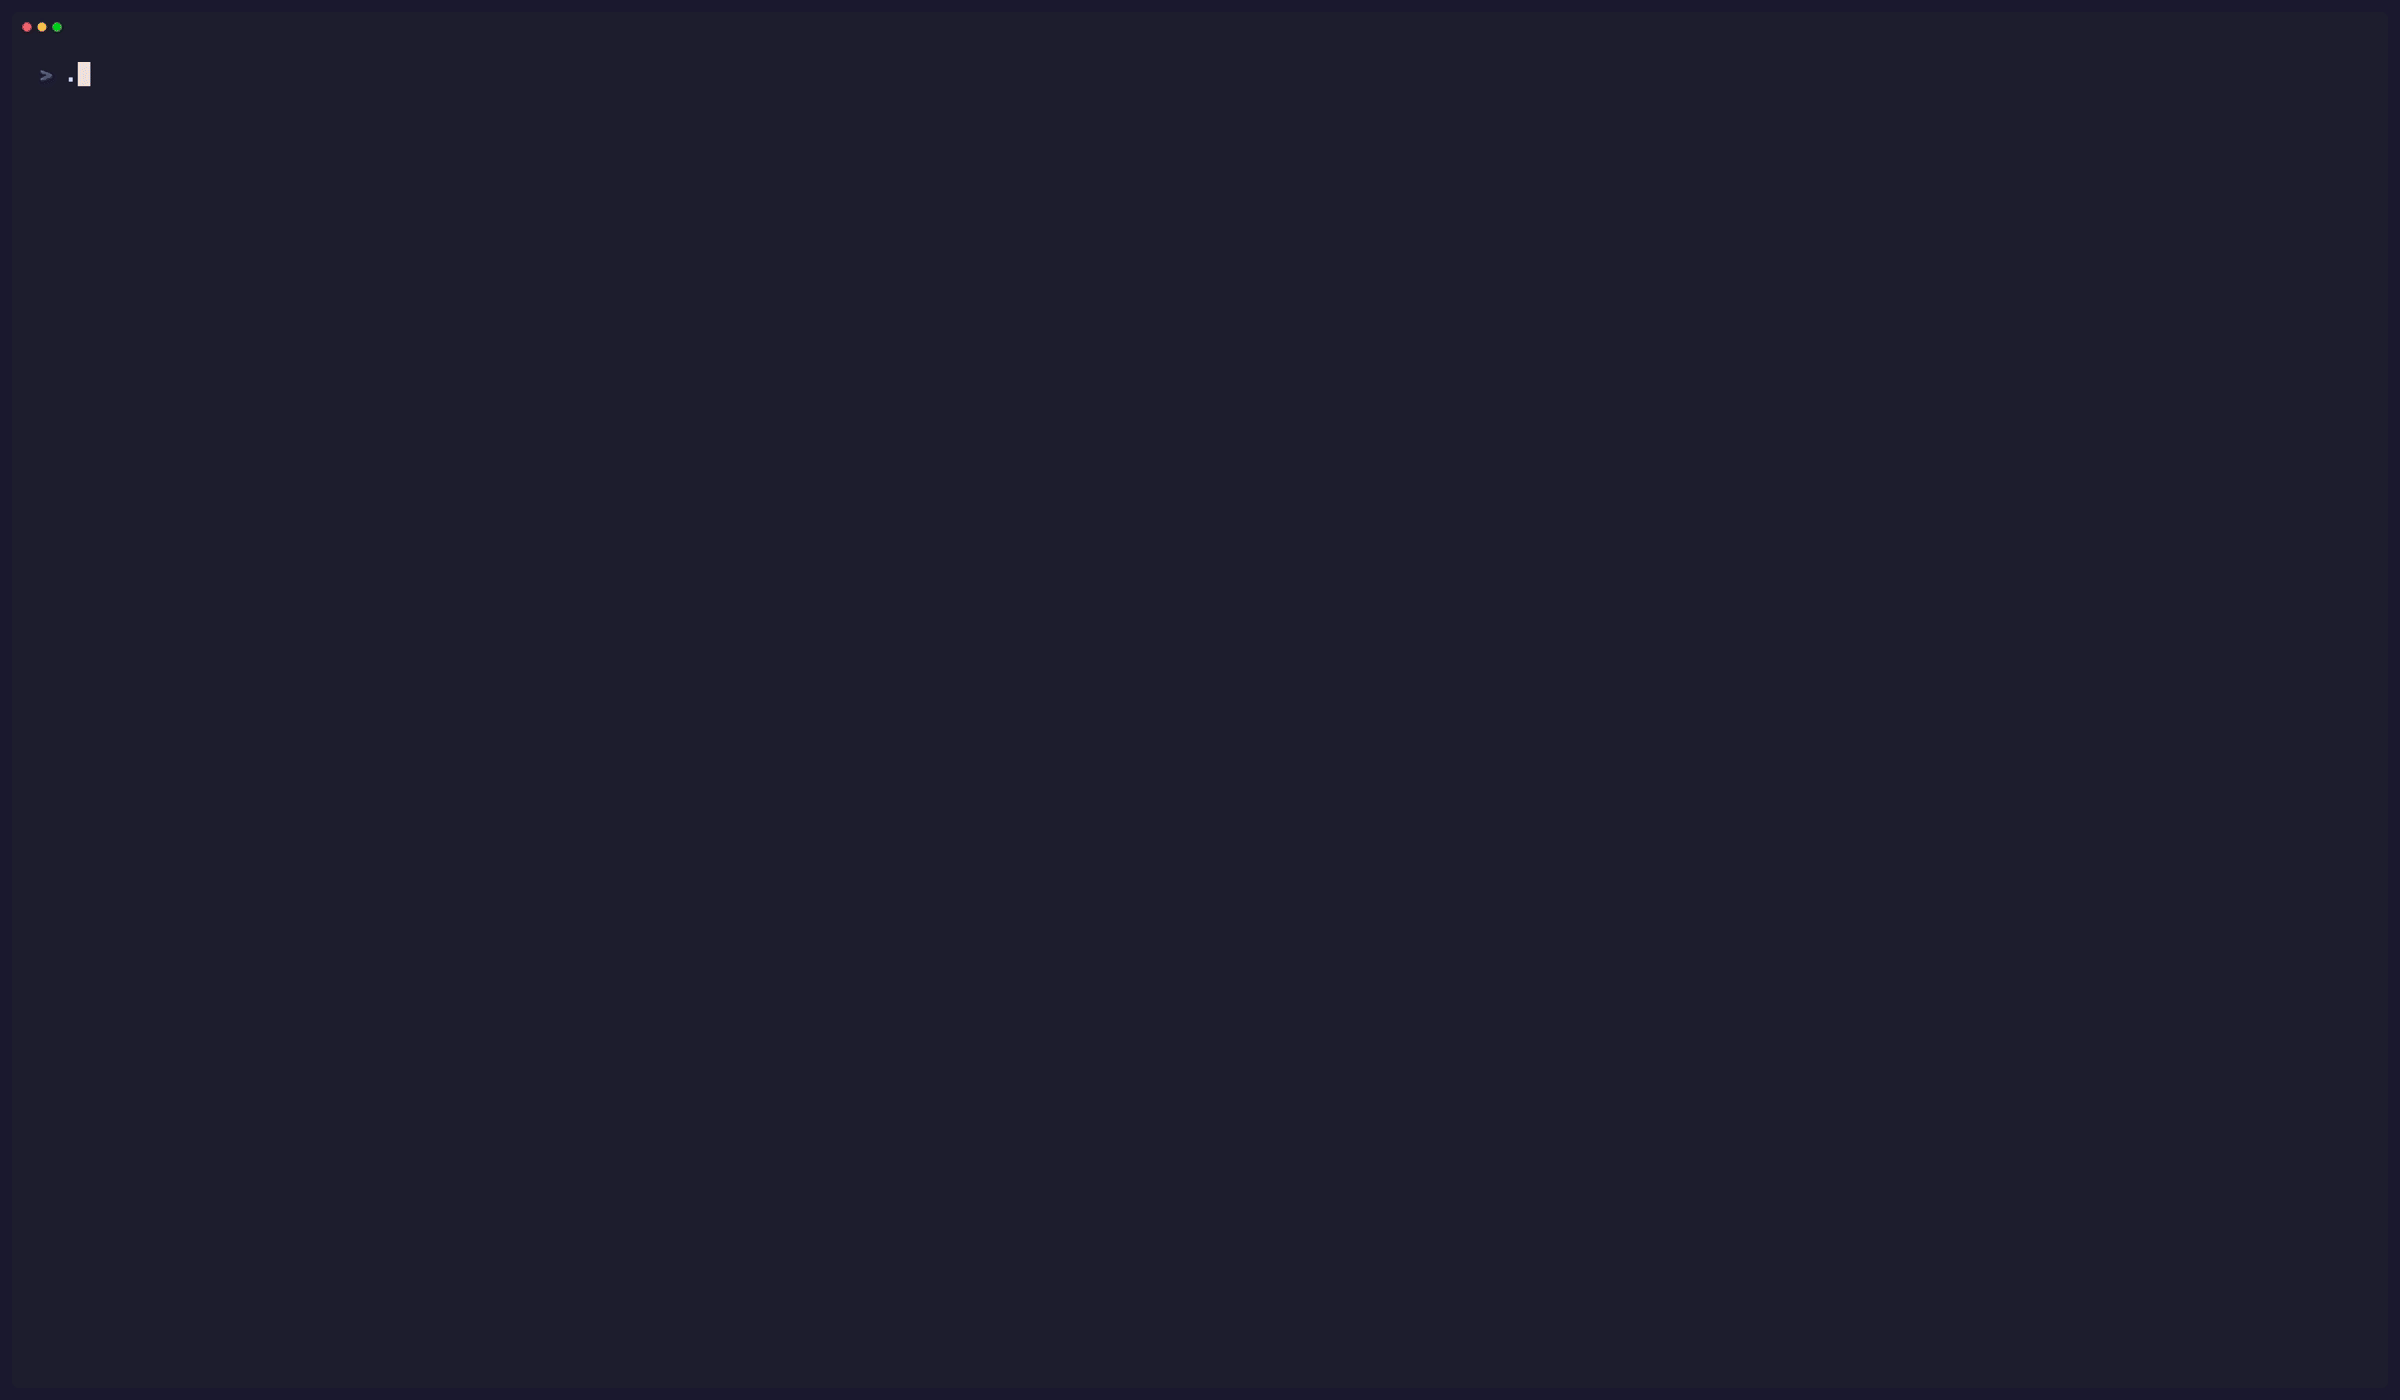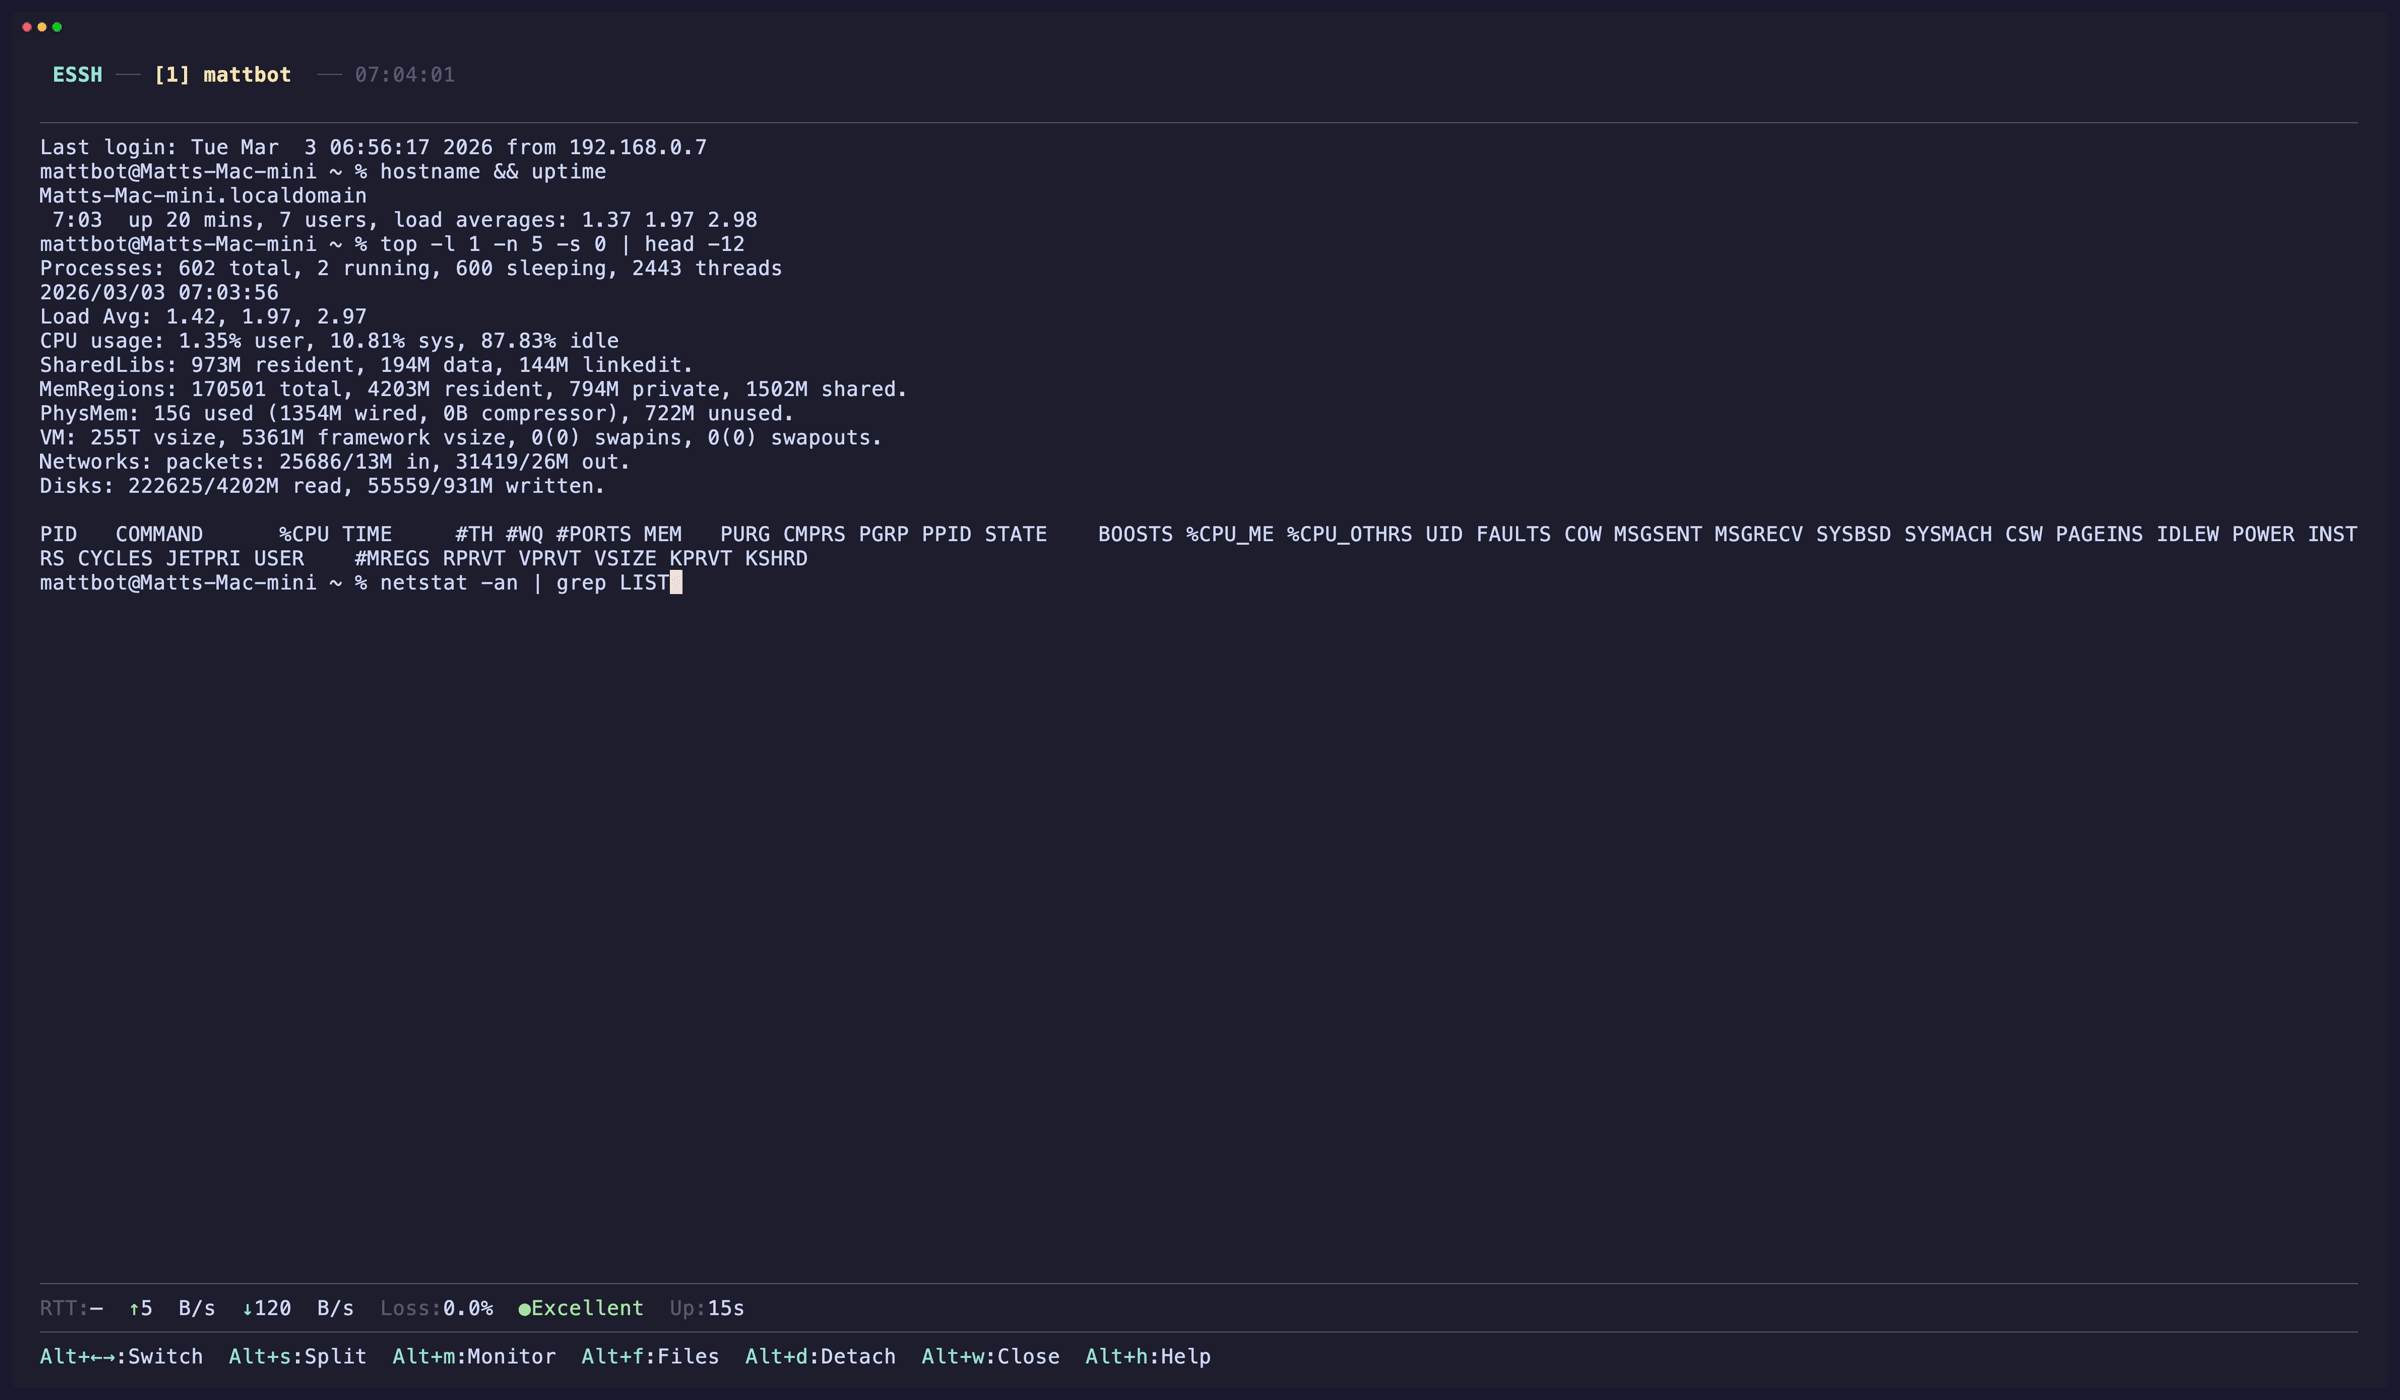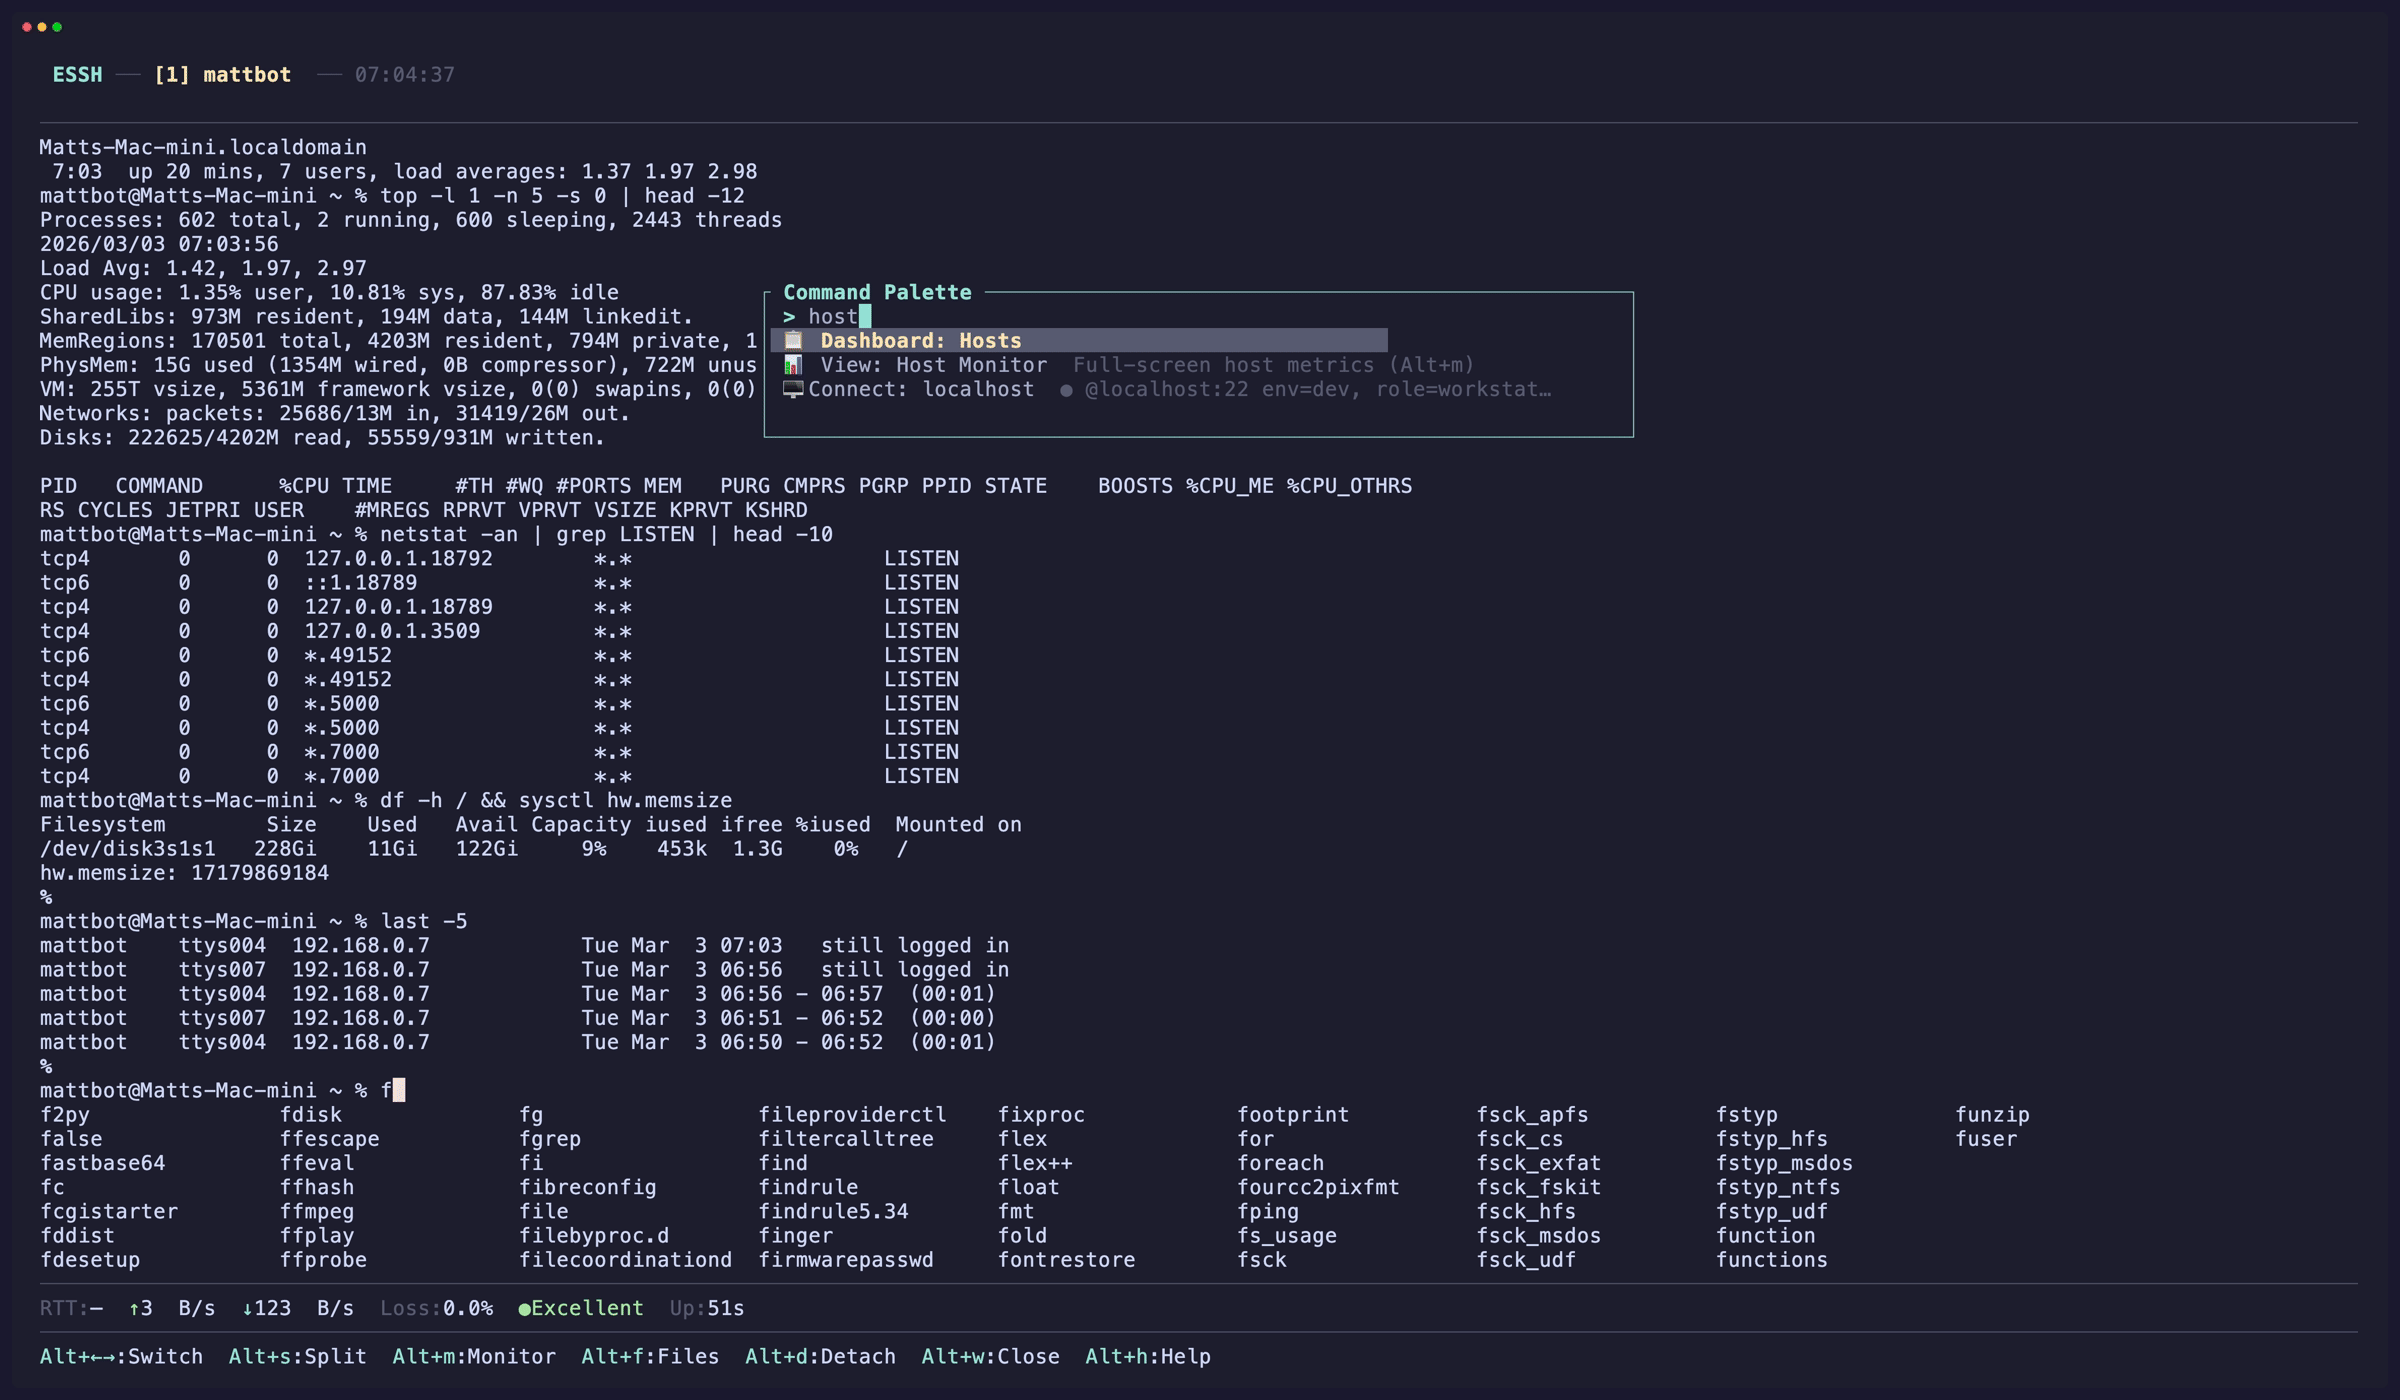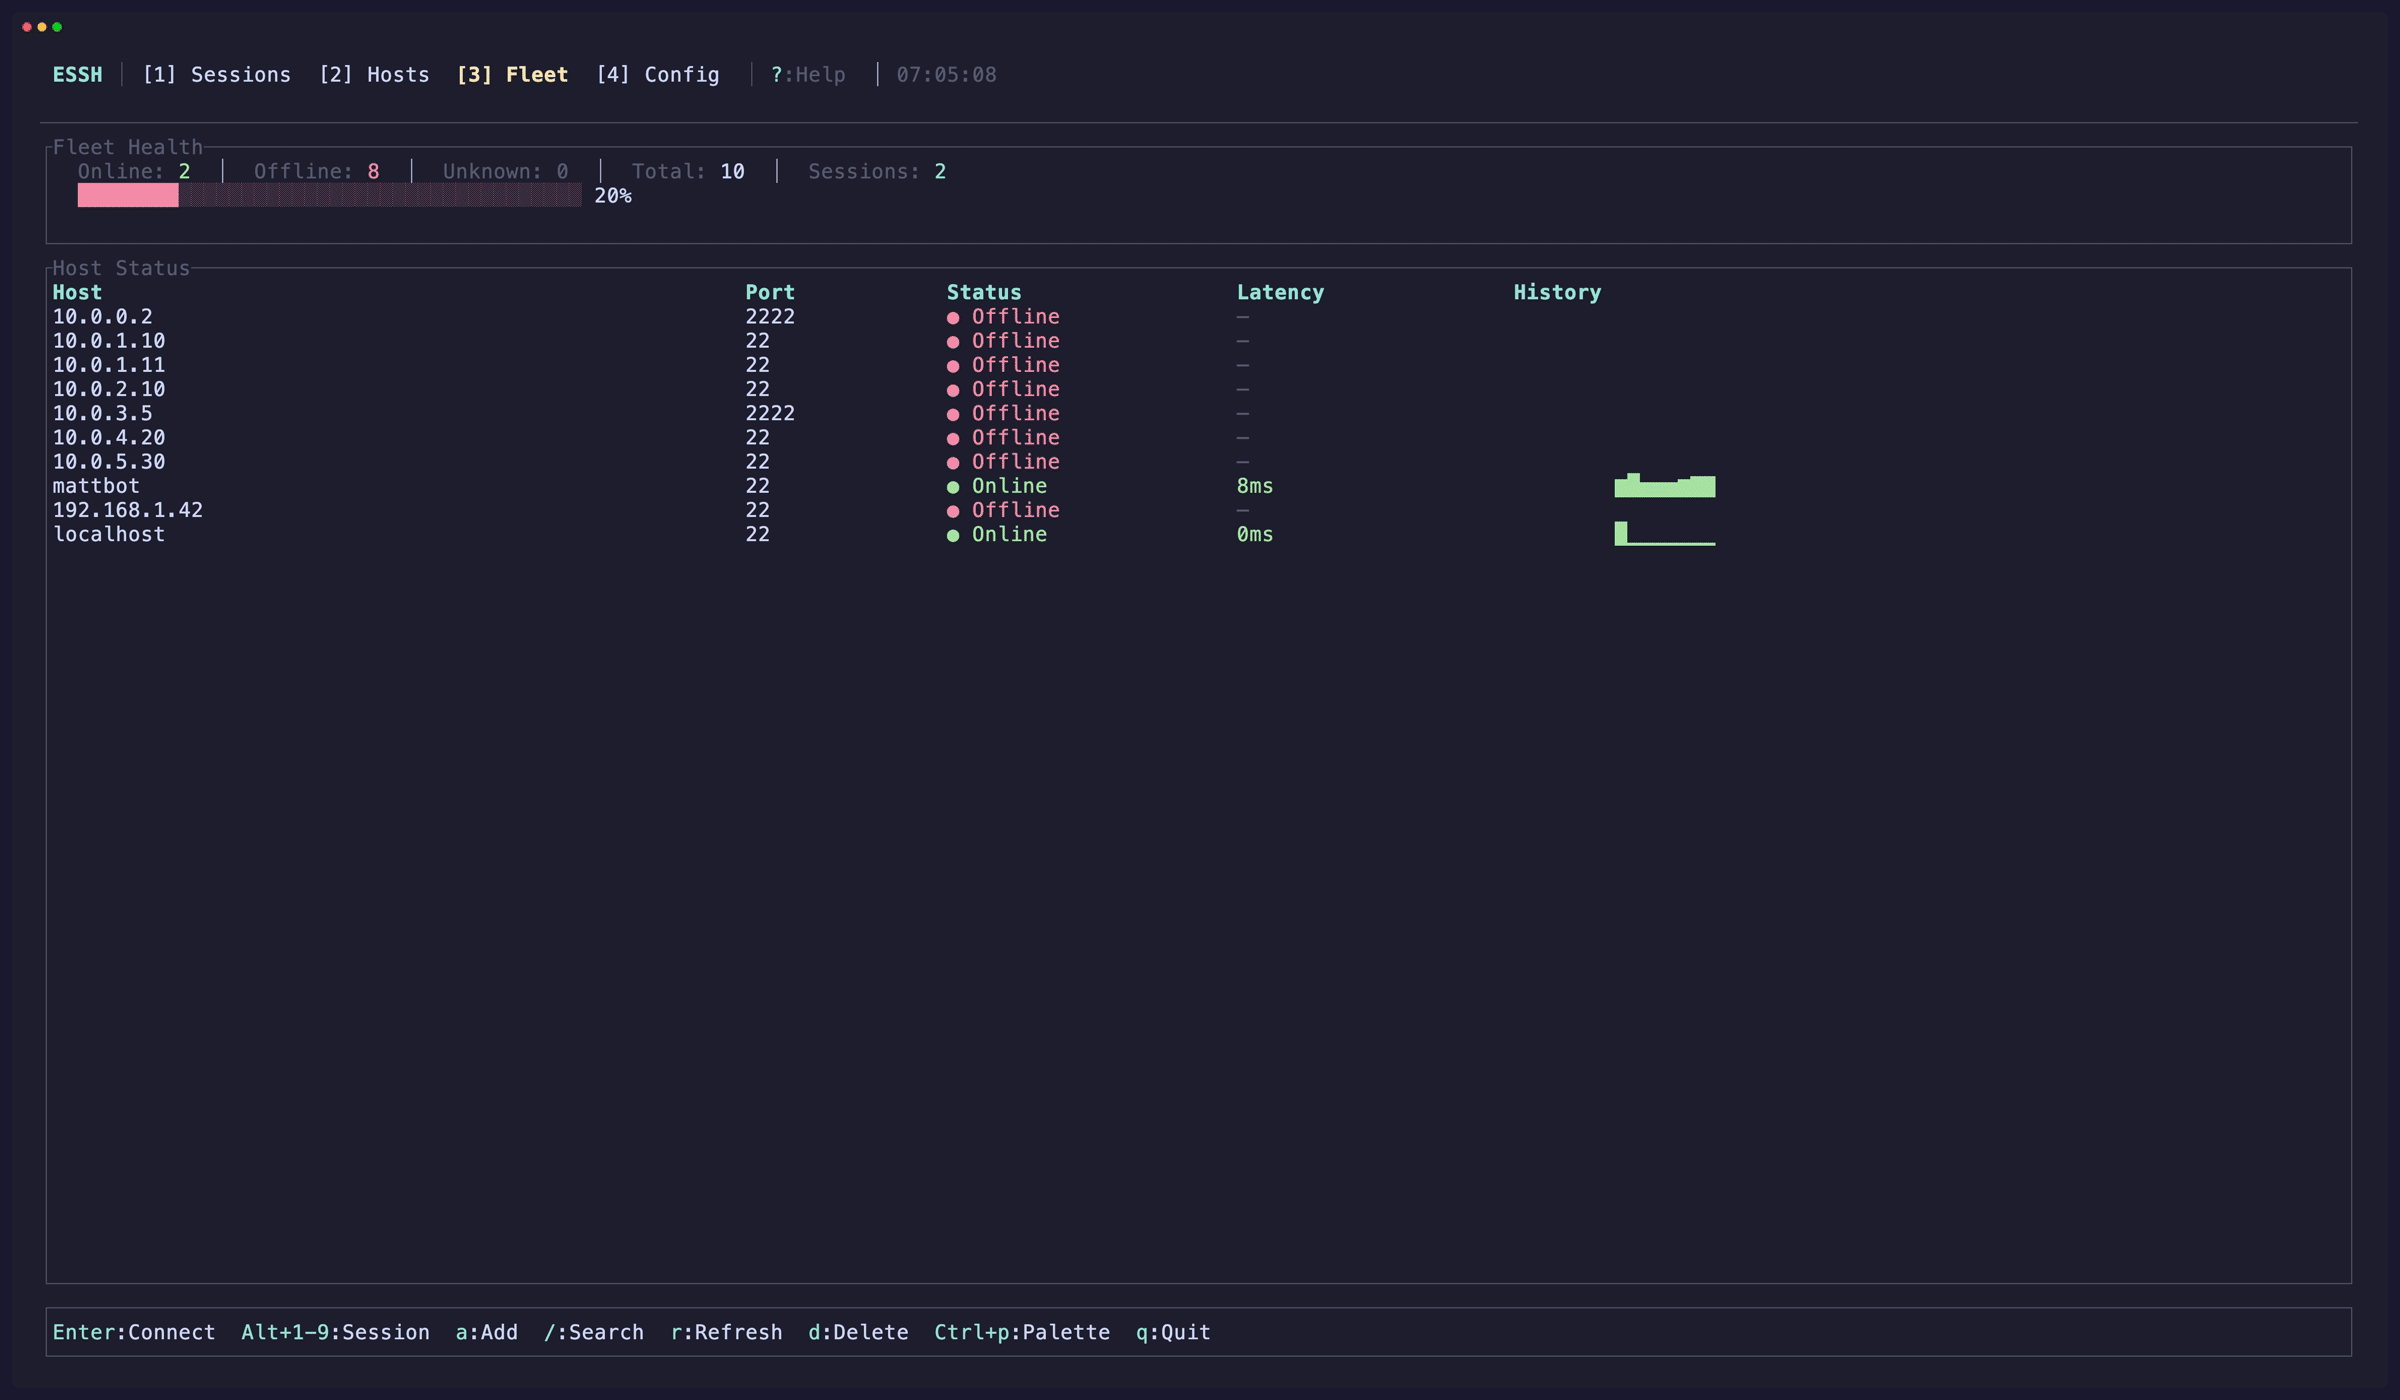 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
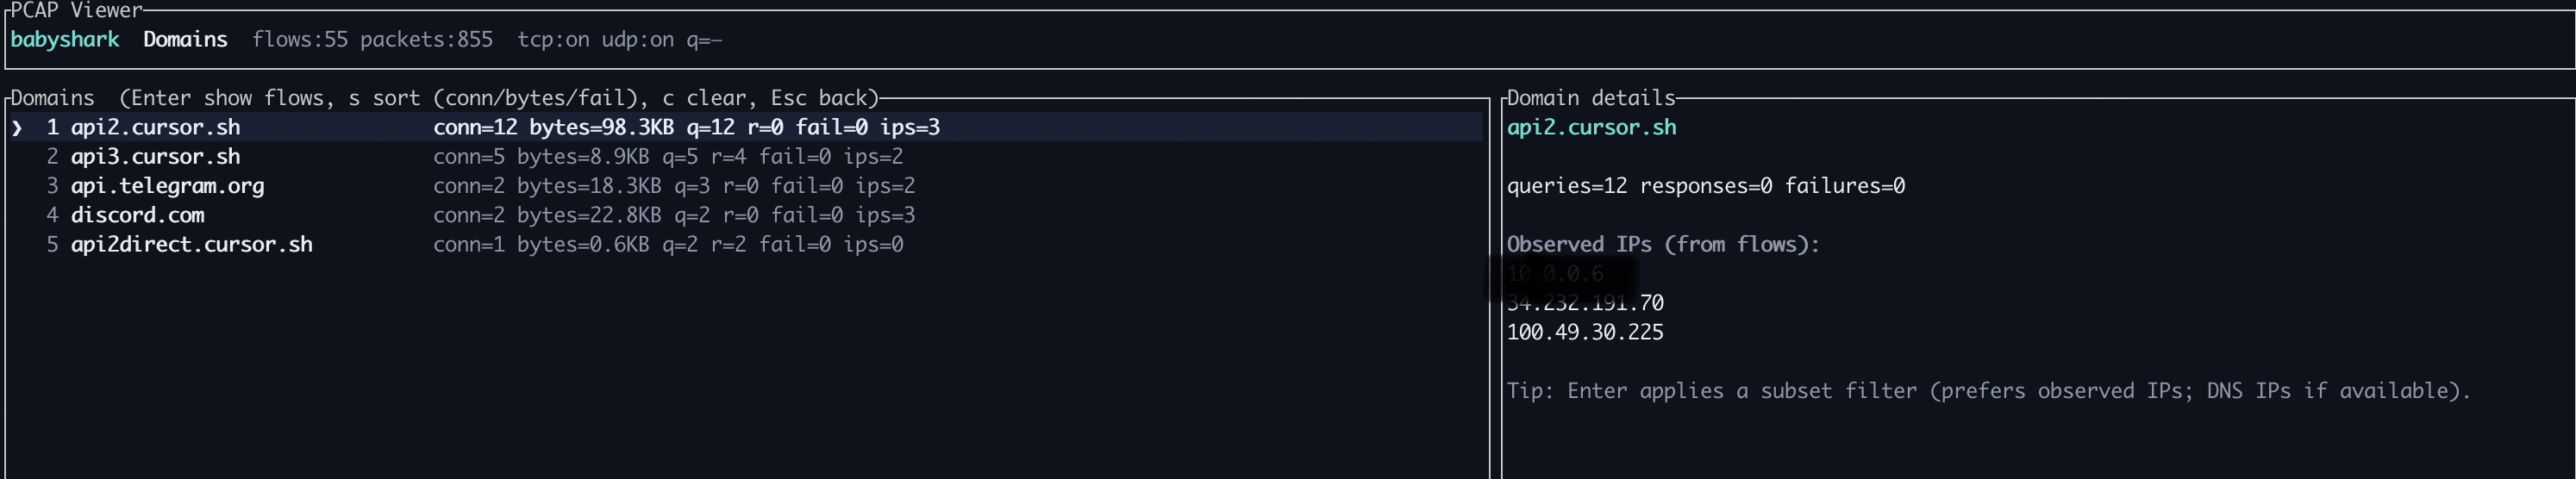 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
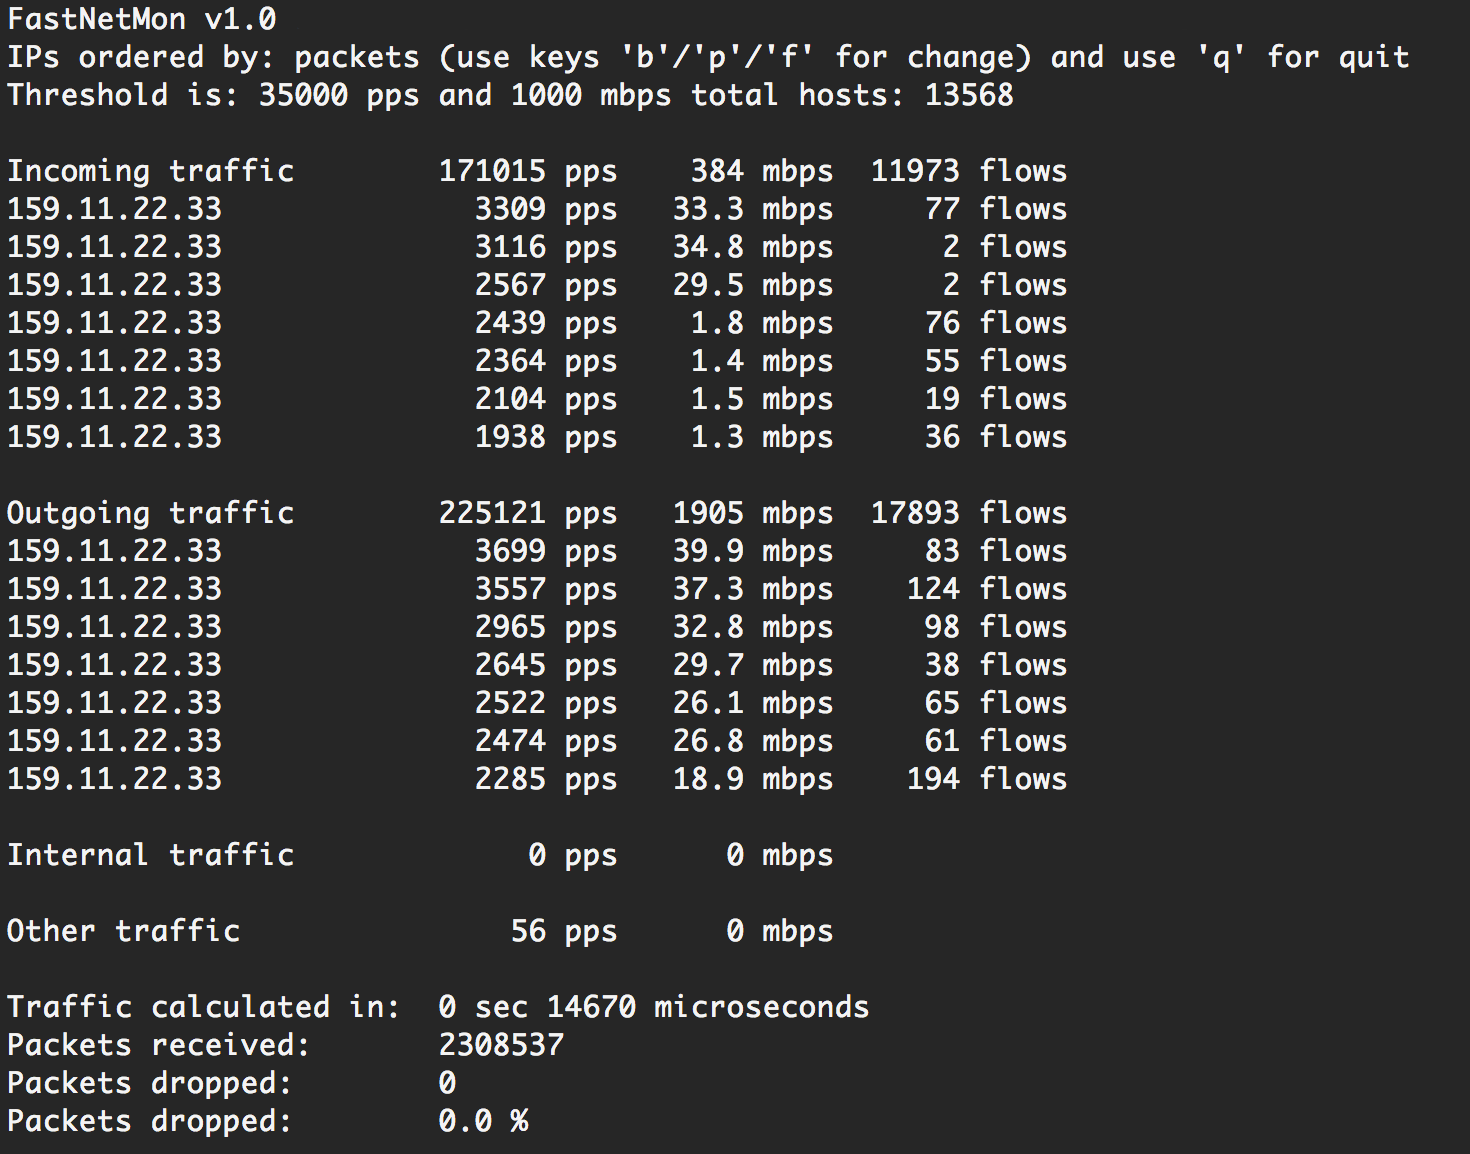 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 cristianzsh/forensictools
Collection of forensic tools
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…