
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
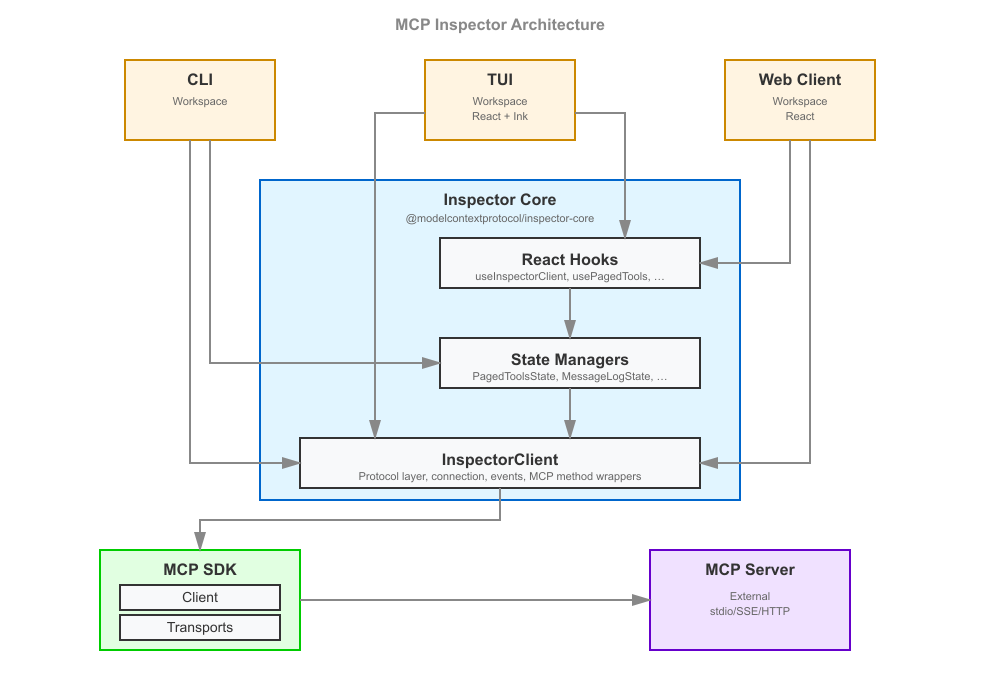
inspector preview

inspector

GitHubmodelcontextprotocol/inspector

Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…

ai-securityauthenticationdebuggers+2
11.2k
6 days ago
icicle-python preview

icicle-python

GitHubicicle-emu/icicle-python

Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
431 year ago
CnaEmulator preview

CnaEmulator

GitHubiterat0r/cnaemulator

Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…

command-and-controldynamic-analysis-sandboxingeducation+7
221 month ago
Jackalope preview

Jackalope

GitHubgoogleprojectzero/jackalope

Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
binary-analysisdebuggersdynamic-analysis-sandboxing+6
1.4k2 months ago
libptrace preview

libptrace

GitHubimmunityinc/libptrace

An event driven multi-core process debugging, tracing, and manipulation framework.

binary-analysisdebuggersdynamic-analysis-sandboxing+3
1726 years ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

defensive-toolsdynamic-analysis-sandboxingforensics+7
6026 days ago
ghidra-mcp preview

ghidra-mcp

GitHubbethington/ghidra-mcp

MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
ai-assisted-reversingbinary-analysisdebuggers+7
6.0k3h 29m ago
voltron preview

voltron

GitHubsnare/voltron

Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…

binary-analysisdebuggersreverse-engineering+1
6.3k1 year ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

binary-analysisdebuggersexploitation+5
1133 years ago
ret-sync preview

ret-sync

GitHubbootleg/ret-sync

ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
binary-analysisdebuggersdynamic-analysis-sandboxing+2
2.4k8 months ago
binary-ninja-headless-mcp preview

binary-ninja-headless-mcp

GitHubmrphrazer/binary-ninja-headless-mcp

Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
ai-assisted-reversingbinary-analysisdebuggers+5
2611 month ago
DbgShell preview

DbgShell

GitHubmicrosoft/dbgshell

A PowerShell front-end for the Windows debugger engine.
binary-analysisdebuggersreverse-engineering+2
7022 years ago
multiscanner preview

multiscanner

GitHubmitre/multiscanner

Modular file scanning/analysis framework
dynamic-analysis-sandboxingmalware-analysisstatic-analysis+1
6217 years ago
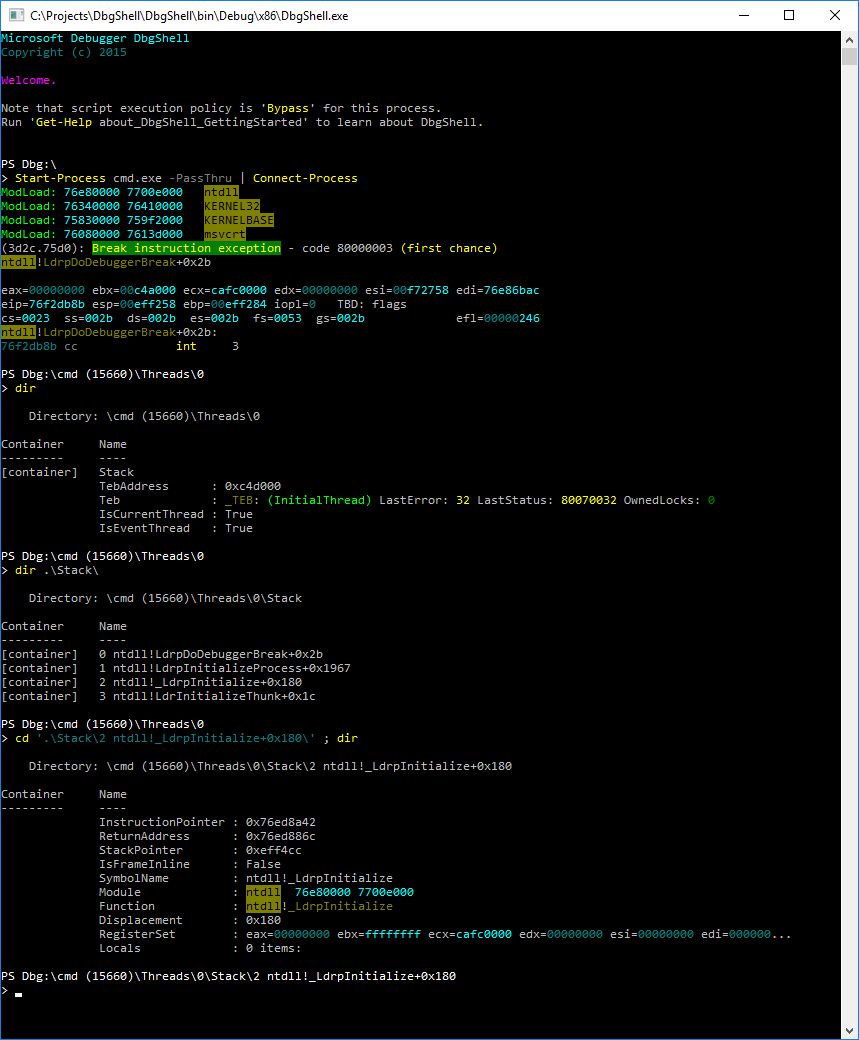
pocket_disasm preview

pocket_disasm

GitHubwhoisqwerz/pocket_disasm

Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.

ai-assisted-reversingbinary-analysisdebuggers+5
413 months ago
pycdc preview

pycdc

GitHubejfkdev/pycdc

Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
binary-analysiscode-analysisdebuggers+4
84 days ago
xed preview

xed

GitHubintelxed/xed

Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
binary-analysiscode-analysisdebuggers+3
1.6k2 months ago
IDArling preview
Archived

IDArling

GitHubidarlingteam/idarling

Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
binary-analysisdebuggerseducation+2
6705 years ago
gdbgui preview

gdbgui

GitHubcs01/gdbgui

Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…

binary-analysisdebuggersreverse-engineering+1
10.4k1 year ago
Previous12Next