

Wireshark
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
3
kirkdjohnson/wiresharkDownloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
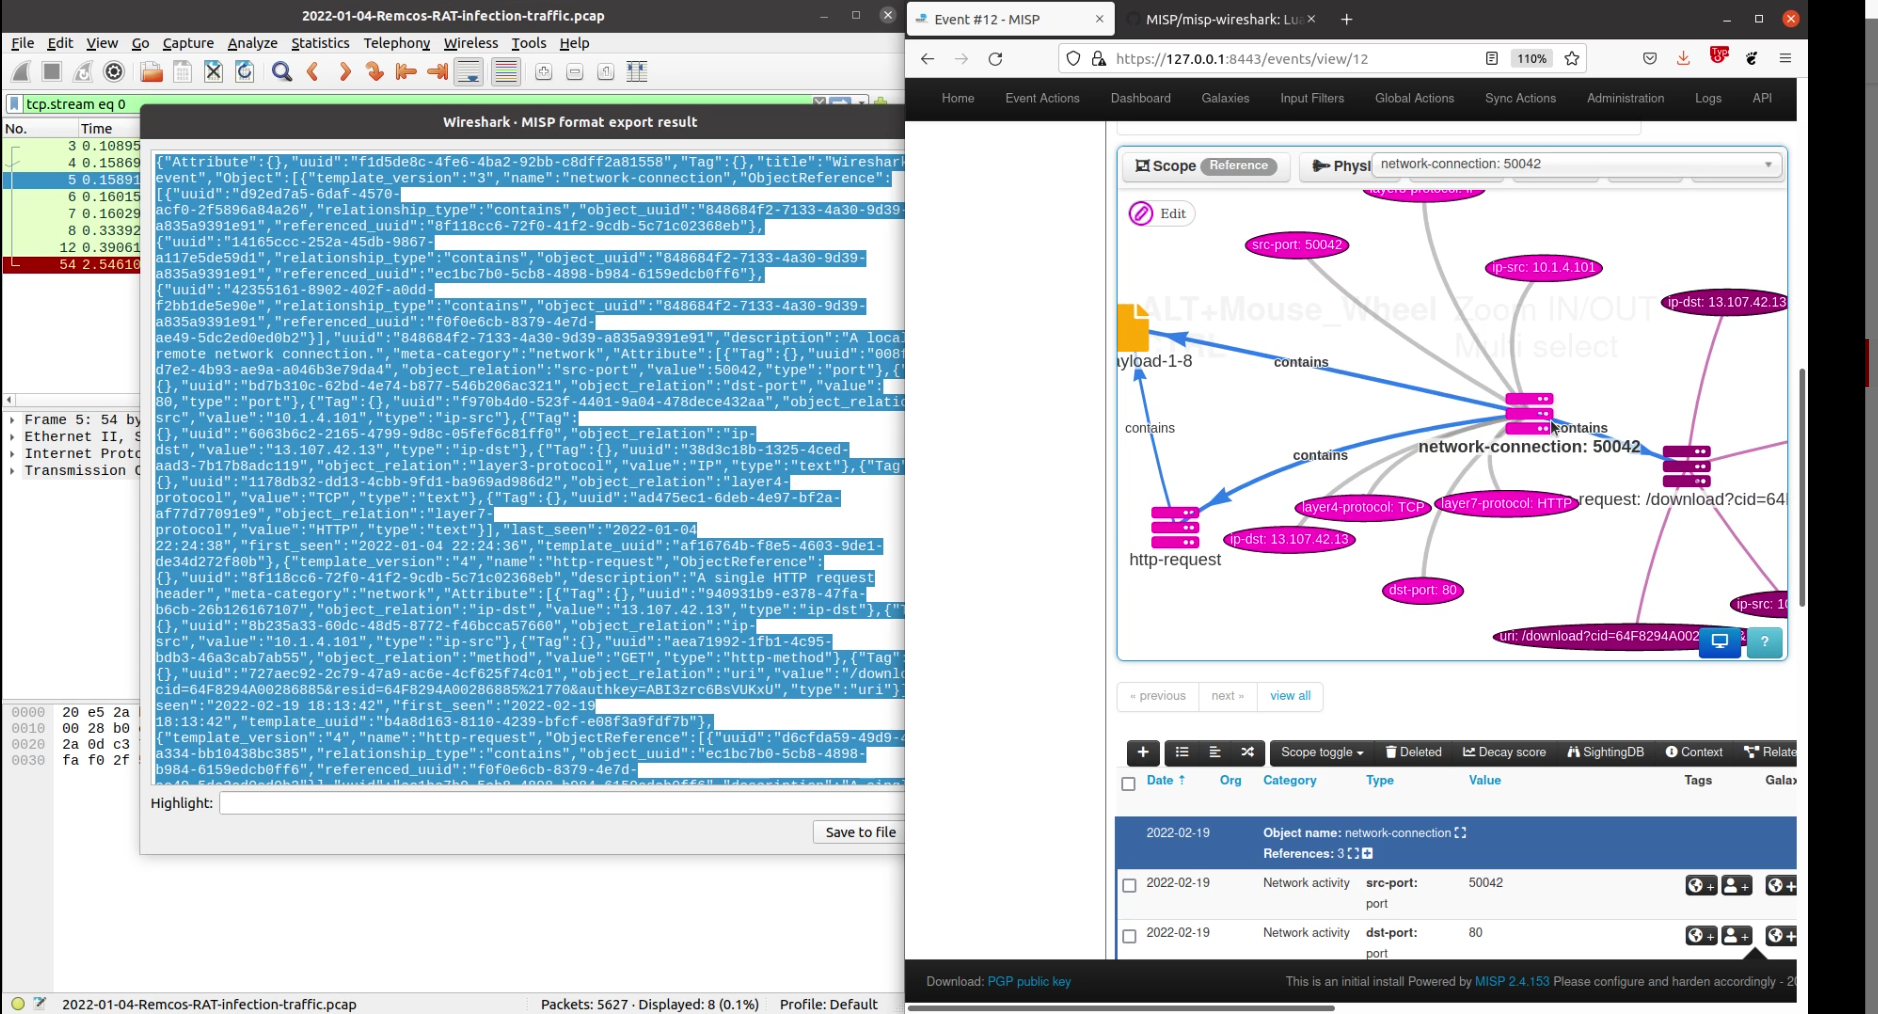 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 pentesteracademy/patoolkit
PA Toolkit is a collection of traffic analysis plugins focused on security
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…