
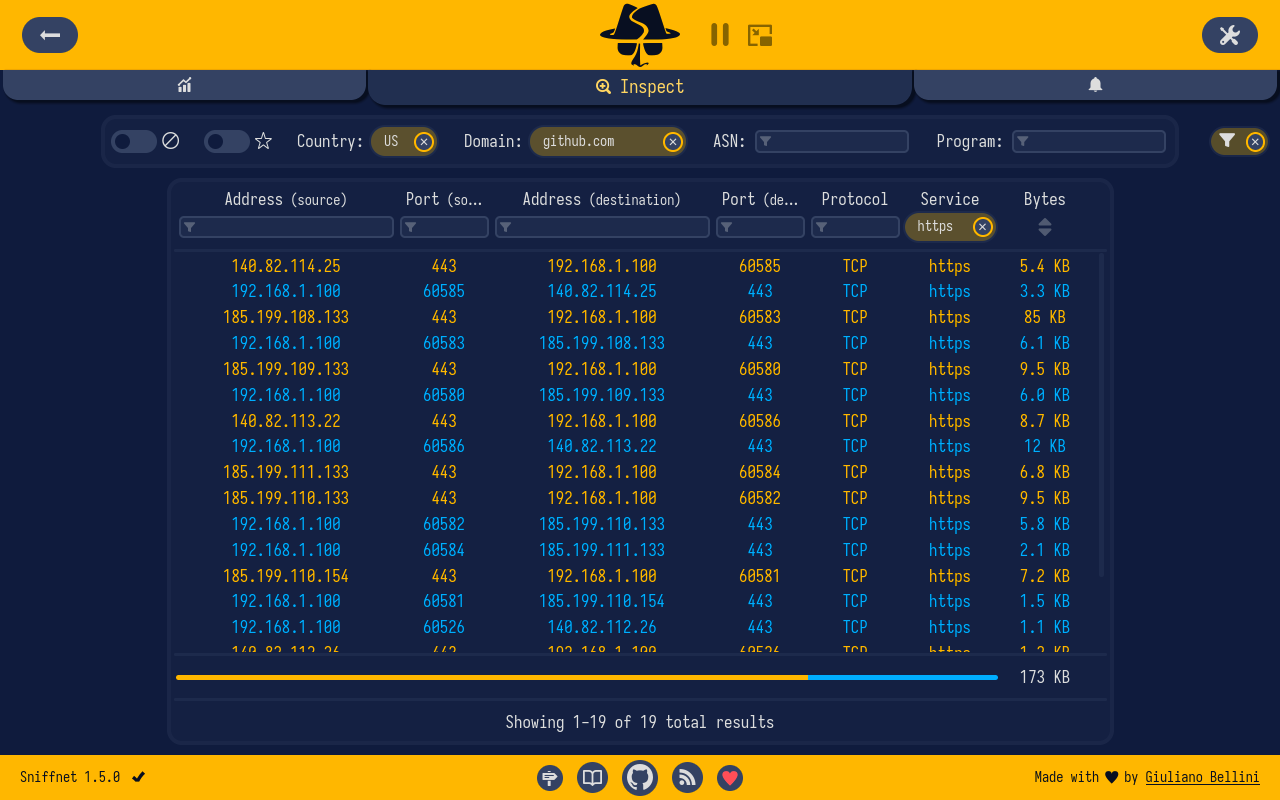
sniffnet
 gyulyvgc/sniffnet
Comfortably monitor your network traffic 🕵️♂️
dns-analysisinformation-gatheringpacket-sniffing-analysis+1
gyulyvgc/sniffnetComfortably monitor your network traffic 🕵️♂️
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
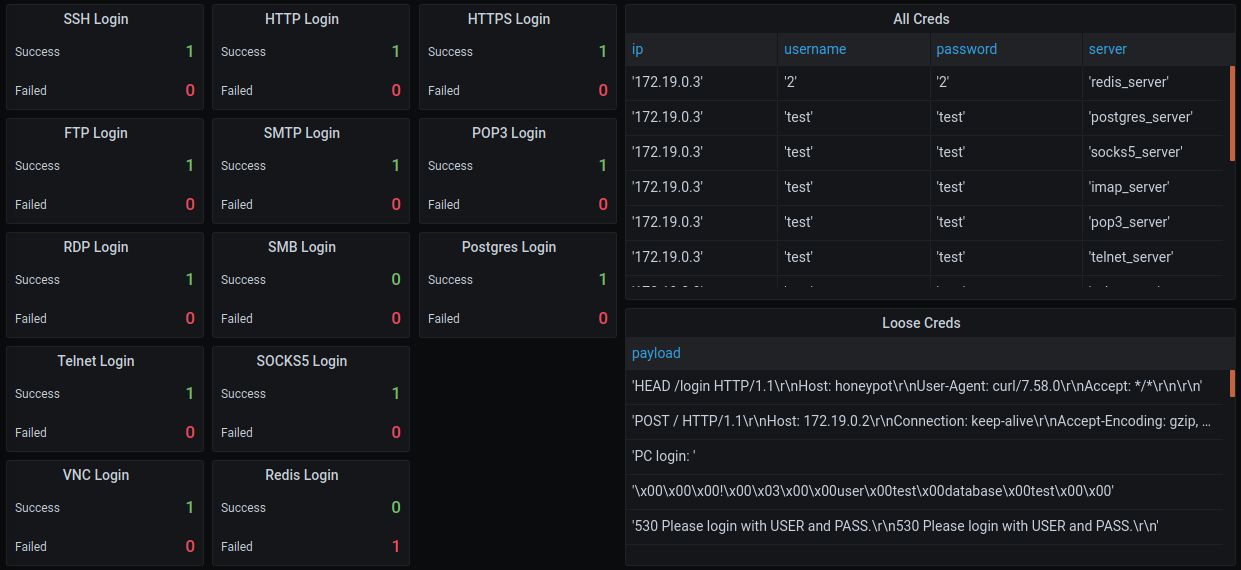 qeeqbox/chameleon
19 Customizable honeypots for monitoring network traffic, bots activities and username\password credentials (DNS, HTTP Proxy, HTTP, HTTPS, SSH, POP3,…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
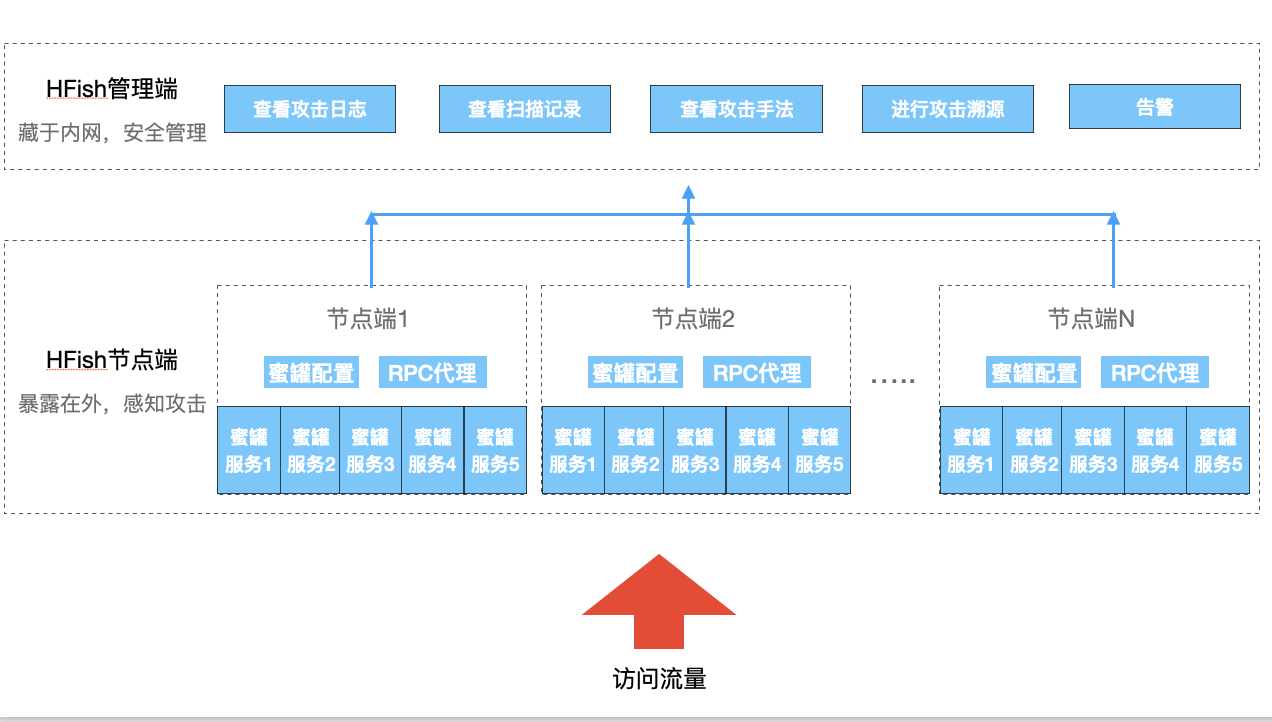 hacklcx/hfish
Enterprise-grade honeypot system for detecting internal network breaches, external threats, and producing threat intelligence with 90+ service…
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.