MongoBleed-DFIR-Triage-Script-CVE-2025-14847

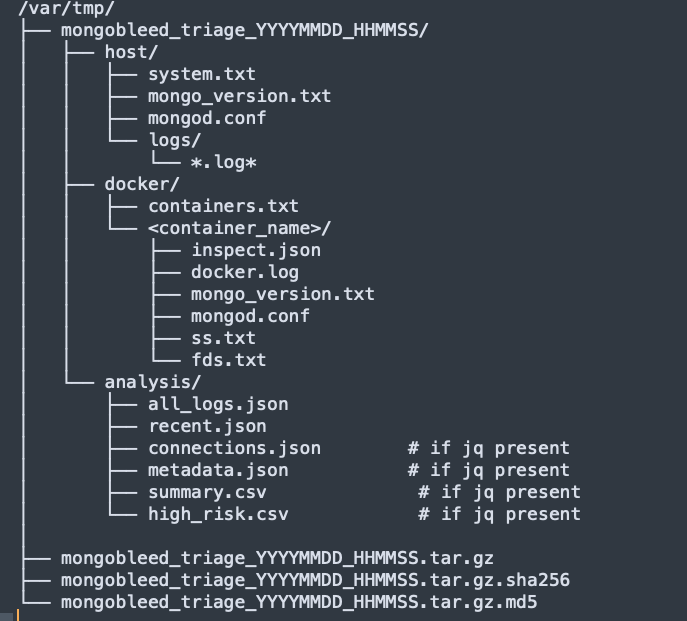
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)

A tool to retrieve malware directly from the source for security researchers.


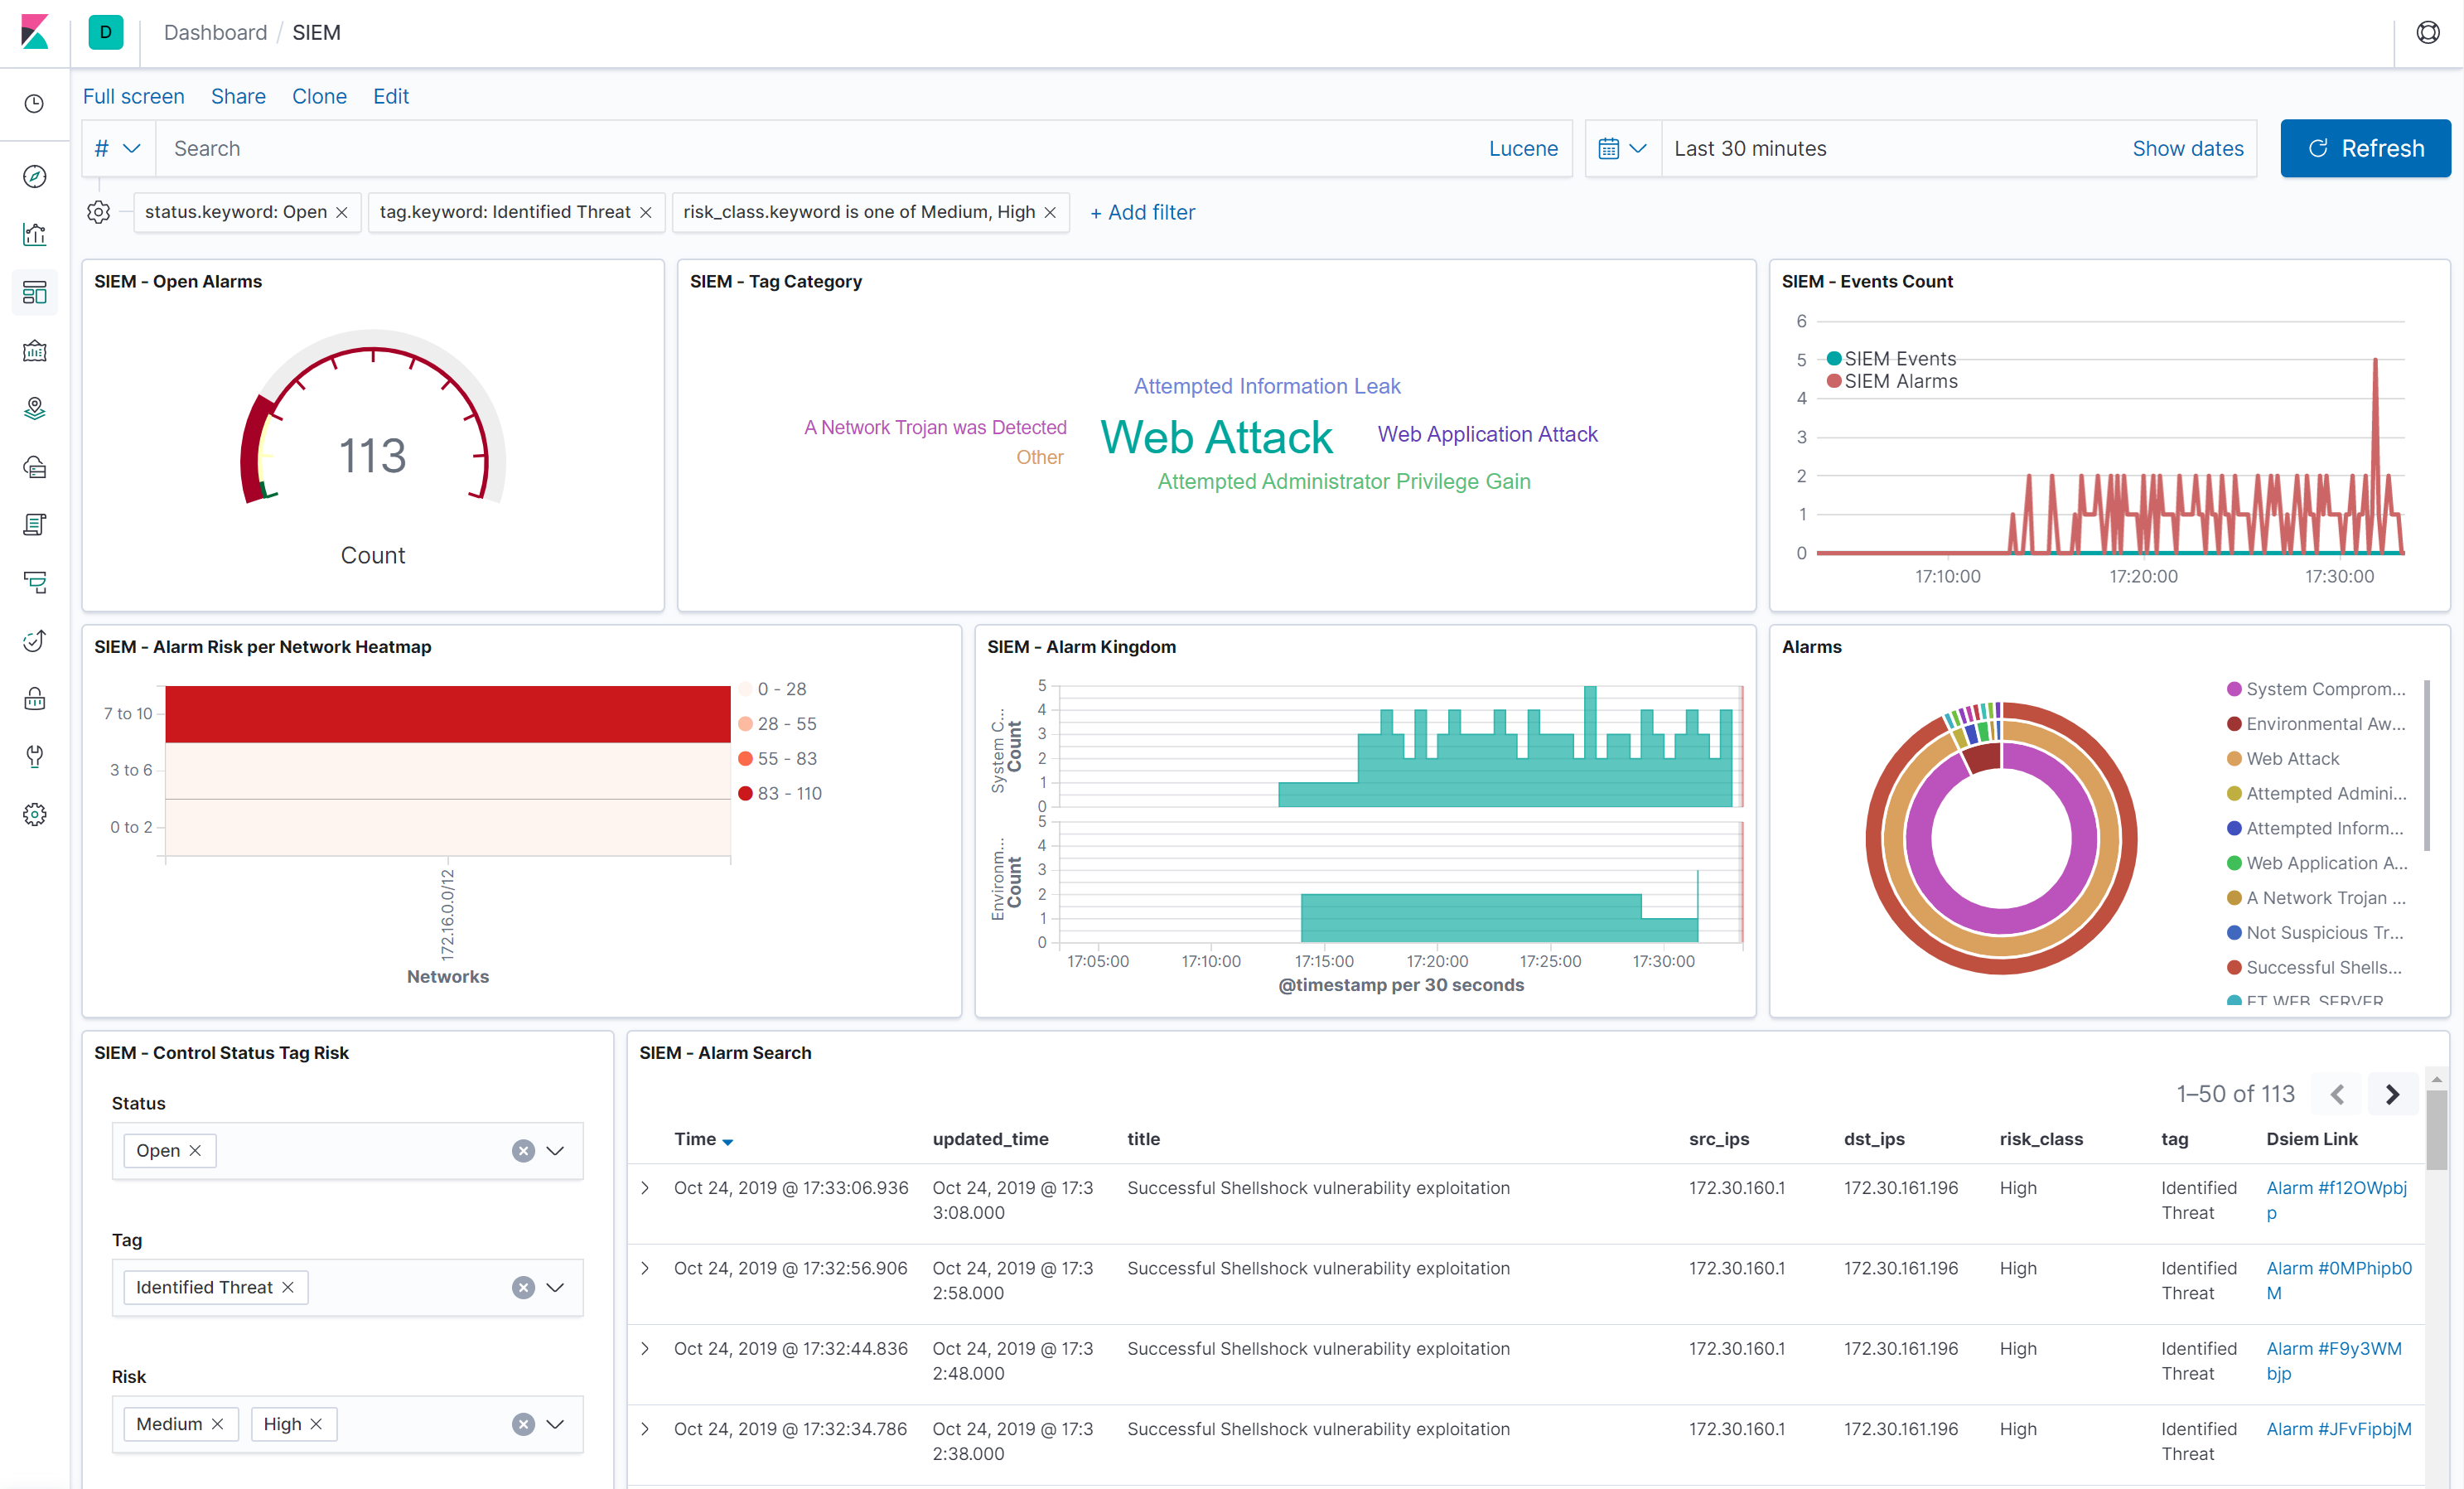
Security event correlation engine for ELK stack

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

Cloud-native system telemetry pipeline that collects, processes, and exports system call events into a compact object-relational format for…

The recursive internet scanner for hackers. 🧡

DShield Sensor Log Collection with ELK

Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities

Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape

eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…

Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…

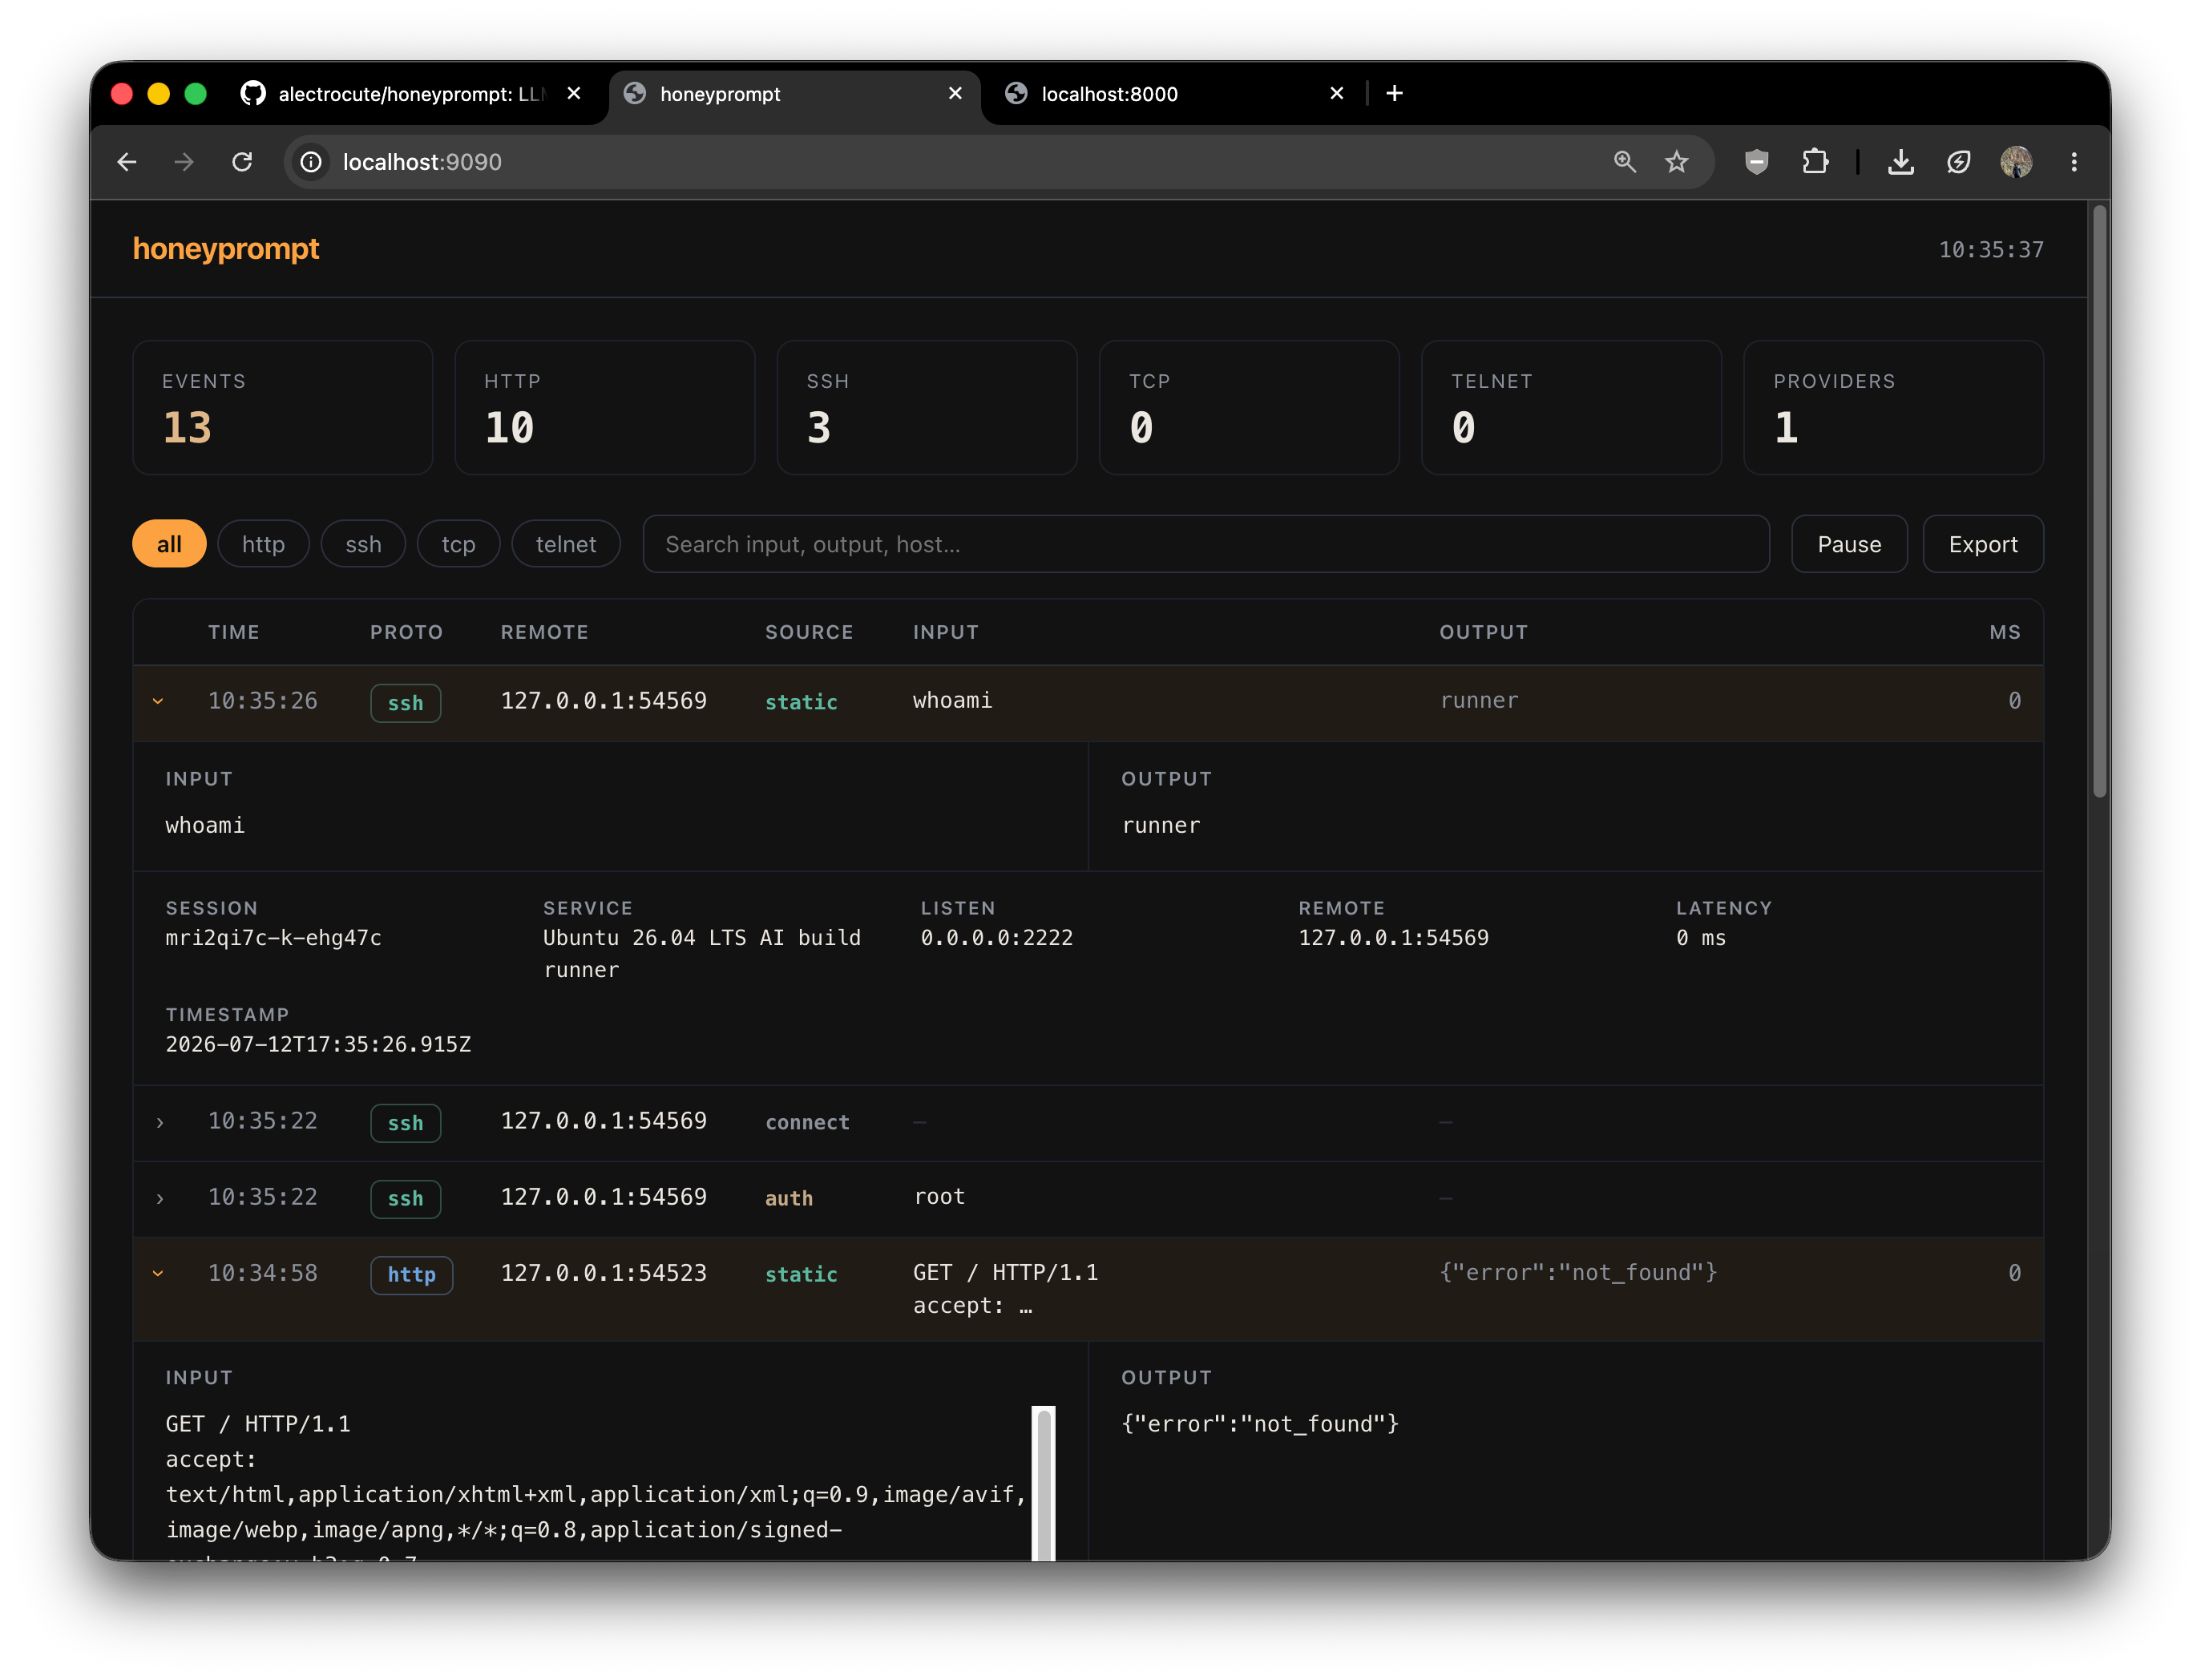
LLM-first deception framework: "The honeypot that talks back!™"

CVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.

A Public Package Scanner for The Community

CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…

Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…