
LogonTracer
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
jpcertcc/logontracerInvestigate malicious Windows logon by visualizing and analyzing Windows event log
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
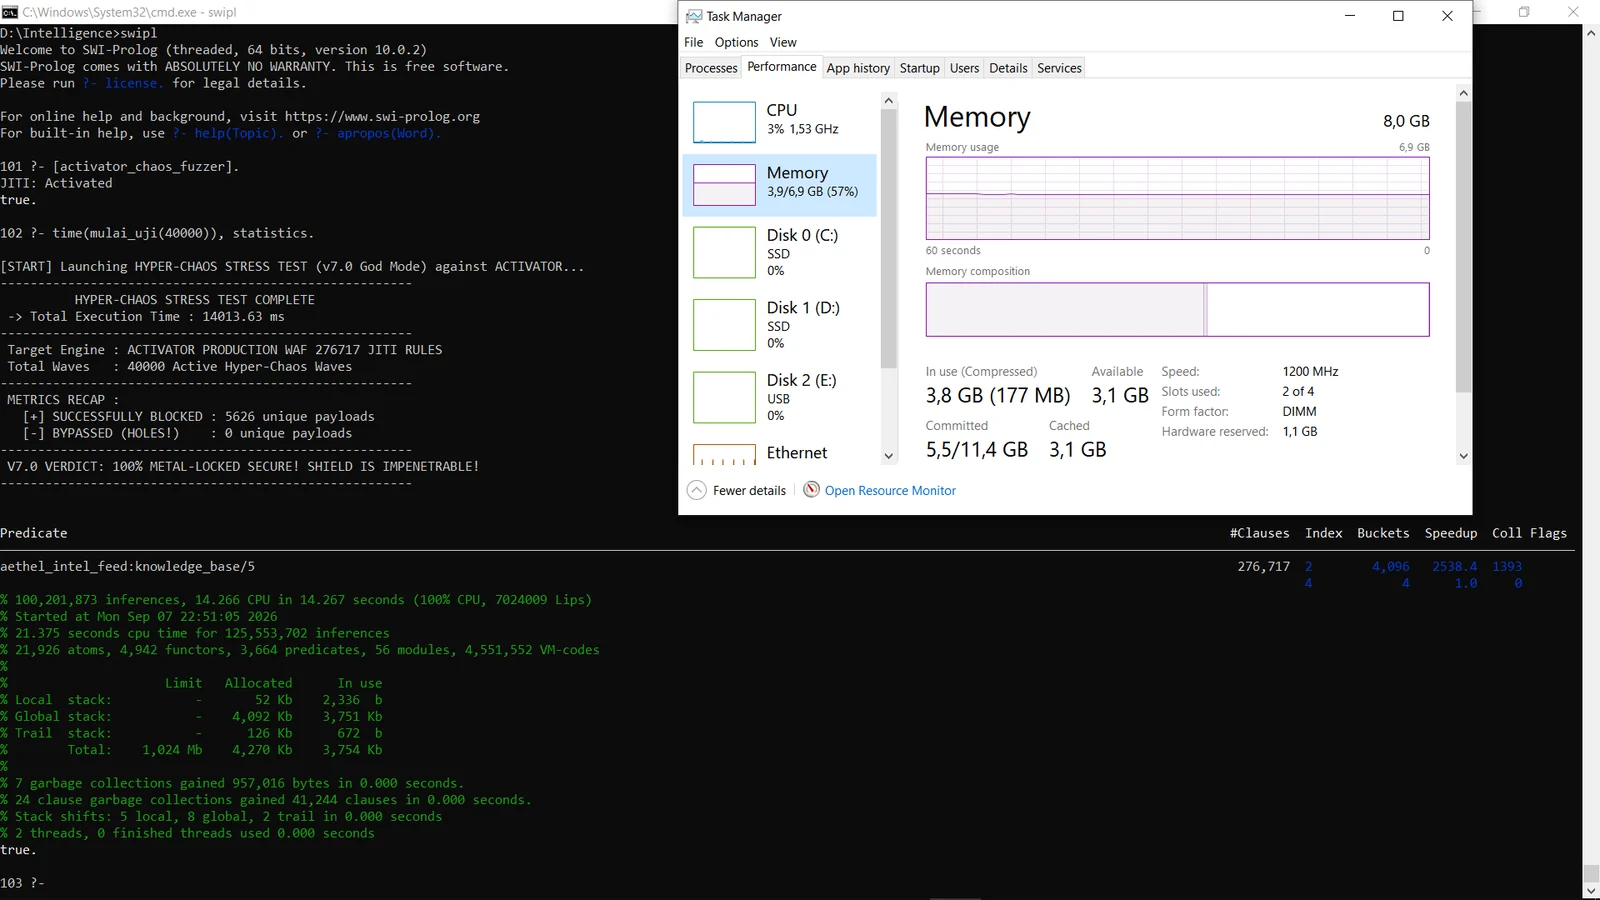 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 gmh5225/nova-framework
YARA-inspired prompt pattern matching engine that combines keyword, regex, semantic similarity, and LLM evaluation rules to detect jailbreaks and…