
Search_CVE
 k3ystr0k3r/search_cve
ntroducing Search_CVE: Unleash the Power of CVE Searching Search_CVE is a cutting-edge tool designed to simplify and optimize the process of…
information-gatheringreconnaissancethreat-intelligence+1
3
k3ystr0k3r/search_cventroducing Search_CVE: Unleash the Power of CVE Searching Search_CVE is a cutting-edge tool designed to simplify and optimize the process of…
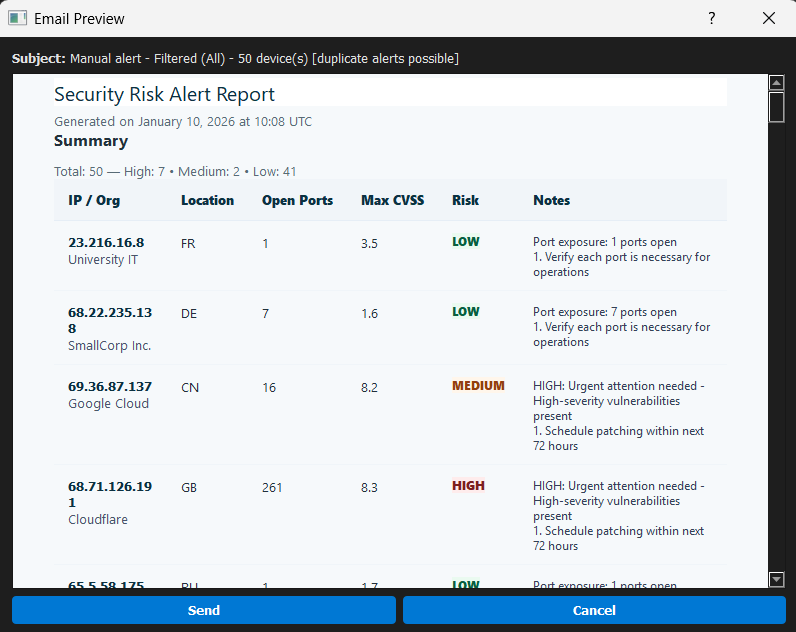 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 chiasmod0n/chiasmodon
Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 xaitax/sploitscan
Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 ernestak/sigma-rule-for-cve-2022-30190
Sigma rule for detecting exploitation of CVE-2022-30190 (Follina) via Windows process creation events, enabling SOC teams to identify malicious…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 emrekybs/douglas-042
Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…
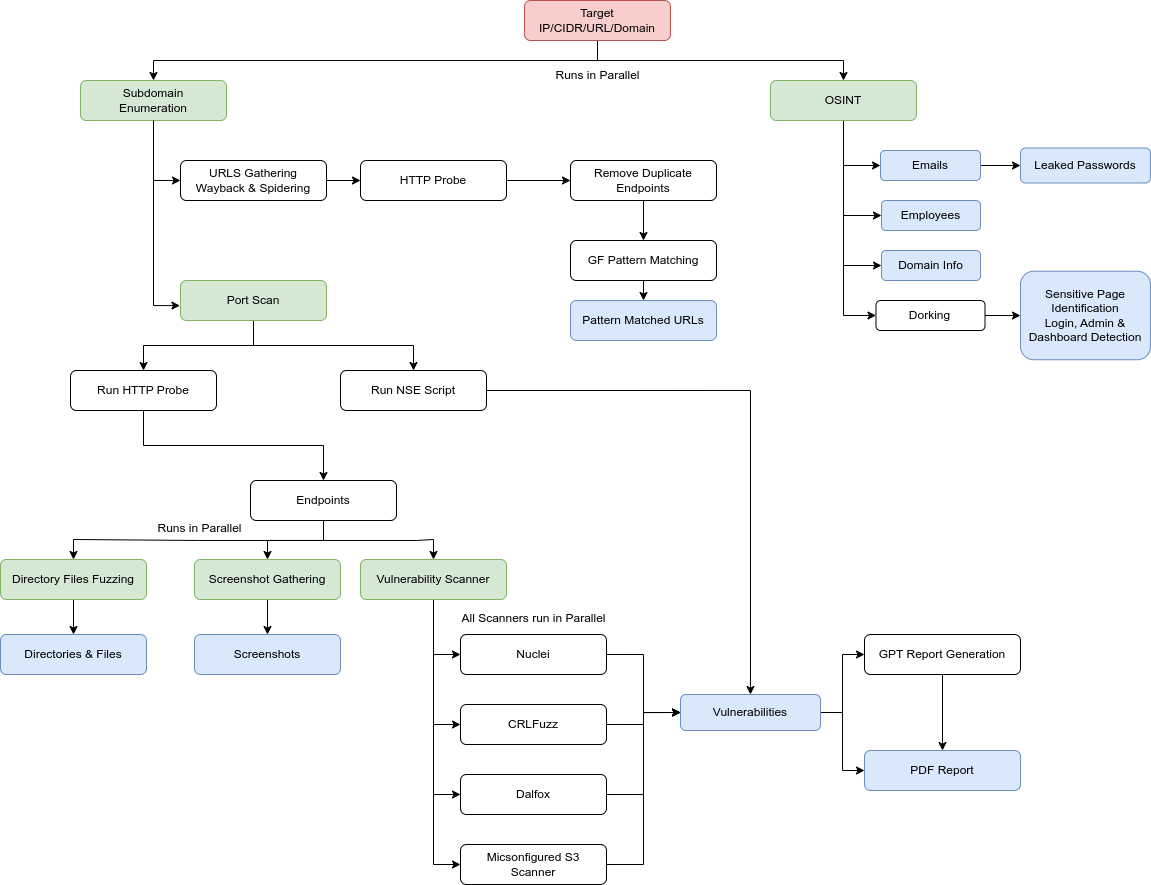 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 sentinelblue/cve-2022-29072
** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
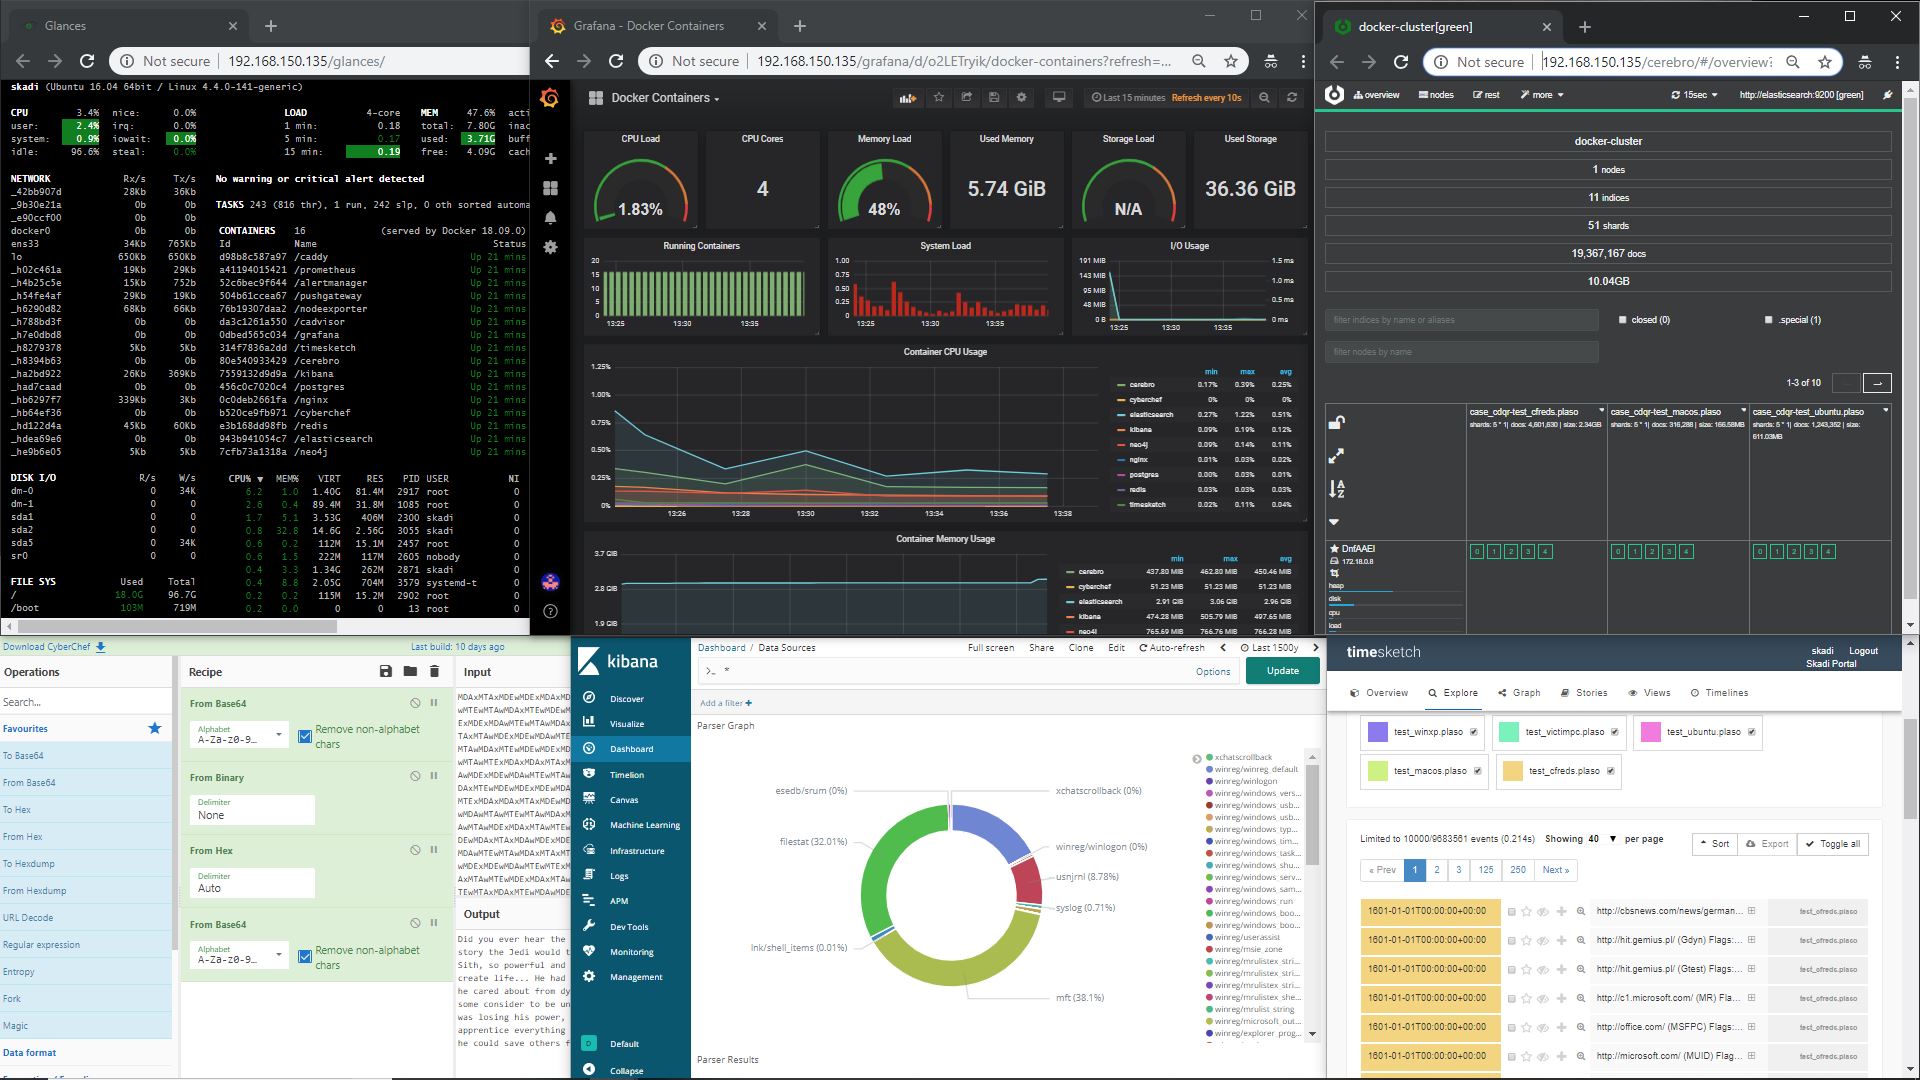 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux