
hfinger
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
information-gatheringmalware-analysisthreat-intelligence
cert-polska/hfingerGenerates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 zmap/zannotate
Utility for annotating Internet datasets with contextual metadata (e.g., origin AS, MaxMind GeoIP2, reverse DNS, and WHOIS)
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
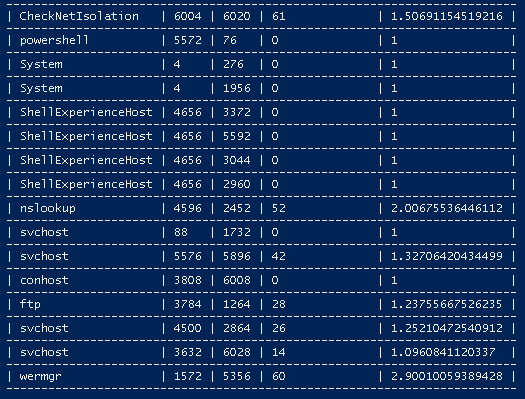 3lp4tr0n/beaconhunter
Detect and respond to Cobalt Strike beacons using ETW.
 philarkwright/dga-detection
DGA Domain Detection using Bigram Frequency Analysis
 corelight/detect-ransomware-filenames
Zeek script that monitors SMB traffic and alerts on known ransomware filenames using the Anti-Ransomware File System Resource Manager list.
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy
 tomchop/malcom
Malcom - Malware Communications Analyzer
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 khast3x/h8mail
Email OSINT & Password breach hunting tool, locally or using premium services. Supports chasing down related email
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…