
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
45 results
SIPI preview

SIPI

GitHubst2labs/sipi

Simple IP Information Tools for Reputation Data Analysis

incident-responseinformation-gatheringosint+2
237 years ago
AIP preview

AIP

GitHubstratosphereips/aip

Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…

information-gatheringintrusion-detectioniot-security+3
321 year ago
IP-reputation-snort-rule-generator preview

IP-reputation-snort-rule-generator

GitHubnccgroup/ip-reputation-snort-rule-generator

A tool to generate Snort rules based on public IP reputation data

dns-analysisids-ips-evasionintrusion-detection+2
5713 years ago
Just-Metadata preview

Just-Metadata

GitHubredsiege/just-metadata

Just-Metadata is a tool that gathers and analyzes metadata about IP addresses. It attempts to find relationships between systems within a large…
information-gatheringosintreconnaissance+1
6337 years ago
cve-lfi-lab preview

cve-lfi-lab

GitHubthecyberfairy/cve-lfi-lab

A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
ctfeducationincident-response+5
1 year ago
netlas-cookbook preview

netlas-cookbook

GitHubnetlas-io/netlas-cookbook

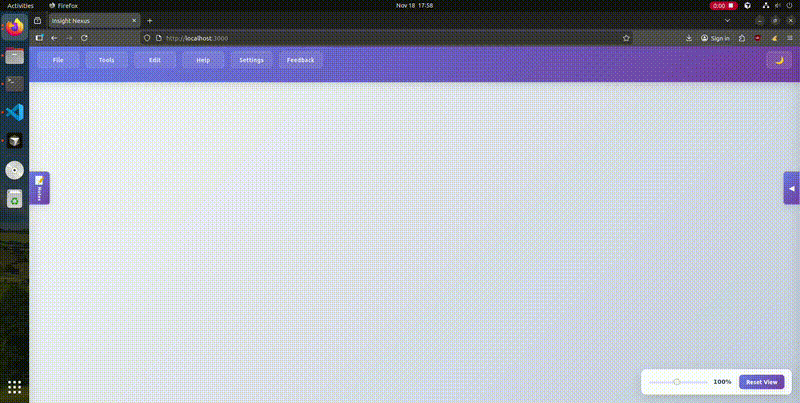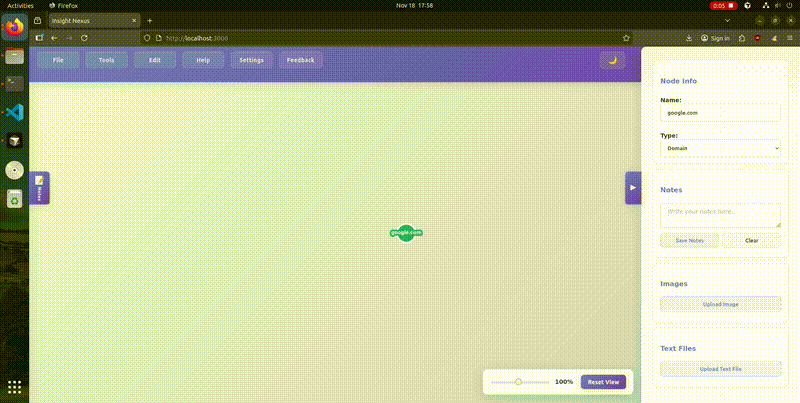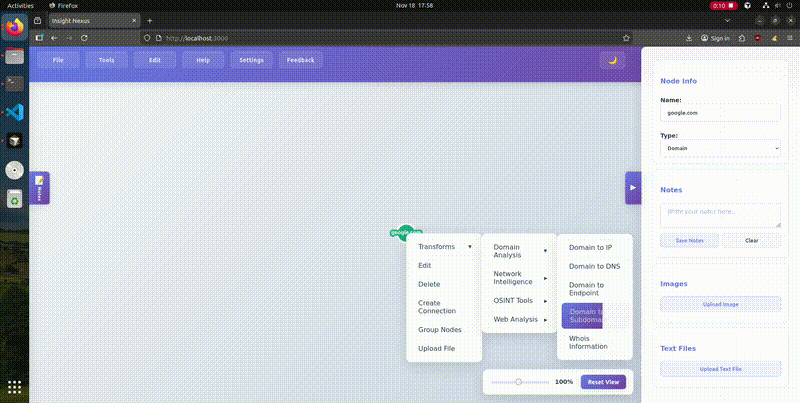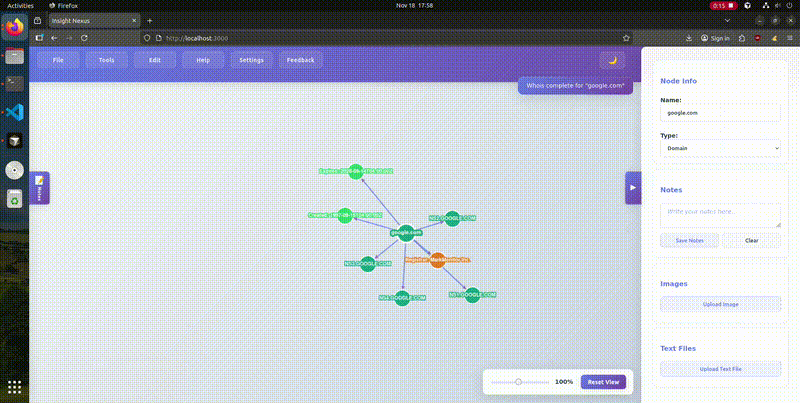
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
curated-resourcesdigital-forensicseducation+9
8891 year ago
insightsnexus preview

insightsnexus

GitHubcyberintel-labs/insightsnexus

OSINT Graph Investigation Application
curated-resourcesdns-subdomain-enumerationeducation+7
349 months ago
wtfis preview

wtfis

GitHubpirxthepilot/wtfis

Passive hostname, domain and IP lookup tool for non-robots

dns-analysisinformation-gatheringosint+3
1.8k4 months ago
C2-Tracker preview
Archived

C2-Tracker

GitHubmontysecurity/c2-tracker

Live Feed of C2 servers, tools, and botnets
command-and-controlinformation-gatheringioc-management+5
7855 months ago
BearFTP preview
Archived

BearFTP

GitHubkolya5544/bearftp

Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
defensive-toolsincident-responseinformation-gathering+4
143 years ago
StickyExim preview

StickyExim

GitHubbrets0150/stickyexim

Exim Honey Pot for CVE-2019-10149 exploit attempts.
email-securityincident-responsethreat-intelligence+1
37 years ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
PoC_CVEs preview
Archived

PoC_CVEs

GitHubtg12/poc_cves

PoC_CVEs

curated-resourceseducationexploit-frameworks+5
1714 months ago
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k1 day ago
bothan preview

bothan

GitHubaudibleblink/bothan

Is this IP a C2 server?
command-and-controldefensive-toolsinformation-gathering+3
276 years ago
LetsDefend-SOC235-Atlassian-Confluence-Broken-Access-Control-0-Day-CVE-2023-22515-EventID-197 preview

LetsDefend-SOC235-Atlassian-Confluence-Broken-Access-Control-0-Day-CVE-2023-22515-EventID-197

GitHubarkha-corvus/letsdefend-soc235-atlassian-confluence-broken-access-control-0-day-cve-2023-22515-eventid-197

I was presented with a high-severity alert indicating a potential exploit attempt of CVE-2023-22515, a zero-day vulnerability in Atlassian…

educationincident-responselog-analysis+3
110 months ago
CVE-2019-19781_IOCs preview

CVE-2019-19781_IOCs

GitHubdigitalshadows/cve-2019-19781_iocs

Curated indicators of compromise (IOCs) for CVE-2019-19781, including IP addresses and whois data from honeypot logs to aid threat detection and…
incident-responseioc-managementnetwork-security+2
6 years ago
ioccheck preview
Archived

ioccheck

GitHubranguli/ioccheck

A tool for simplifying the process of researching IOCs.

defensive-toolshash-analysisinformation-gathering+3
254 years ago
Previous123Next