
Archived
Invoke-ATTACKAPI
 cyb3rward0g/invoke-attackapi
A PowerShell script to interact with the MITRE ATT&CK Framework via its own API
curated-resourceseducationinformation-gathering+3
cyb3rward0g/invoke-attackapiA PowerShell script to interact with the MITRE ATT&CK Framework via its own API
 soteria-security/hafnium-ioc
A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
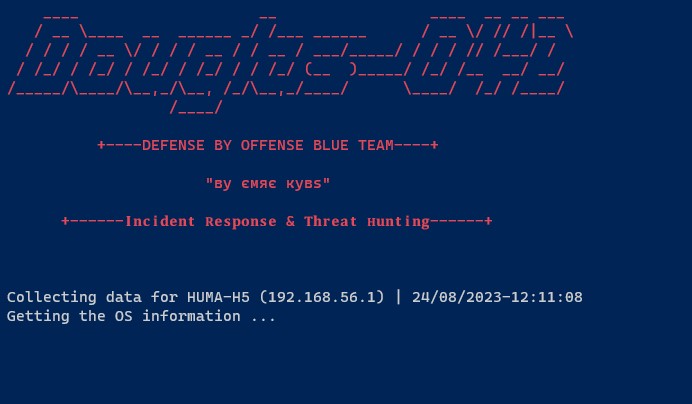 emrekybs/douglas-042
Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…
 rjsudlow/proxynotshell-ioc-checker
Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
 ace-responder/cve-2022-47966_checker
Run on your ManageEngine server
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
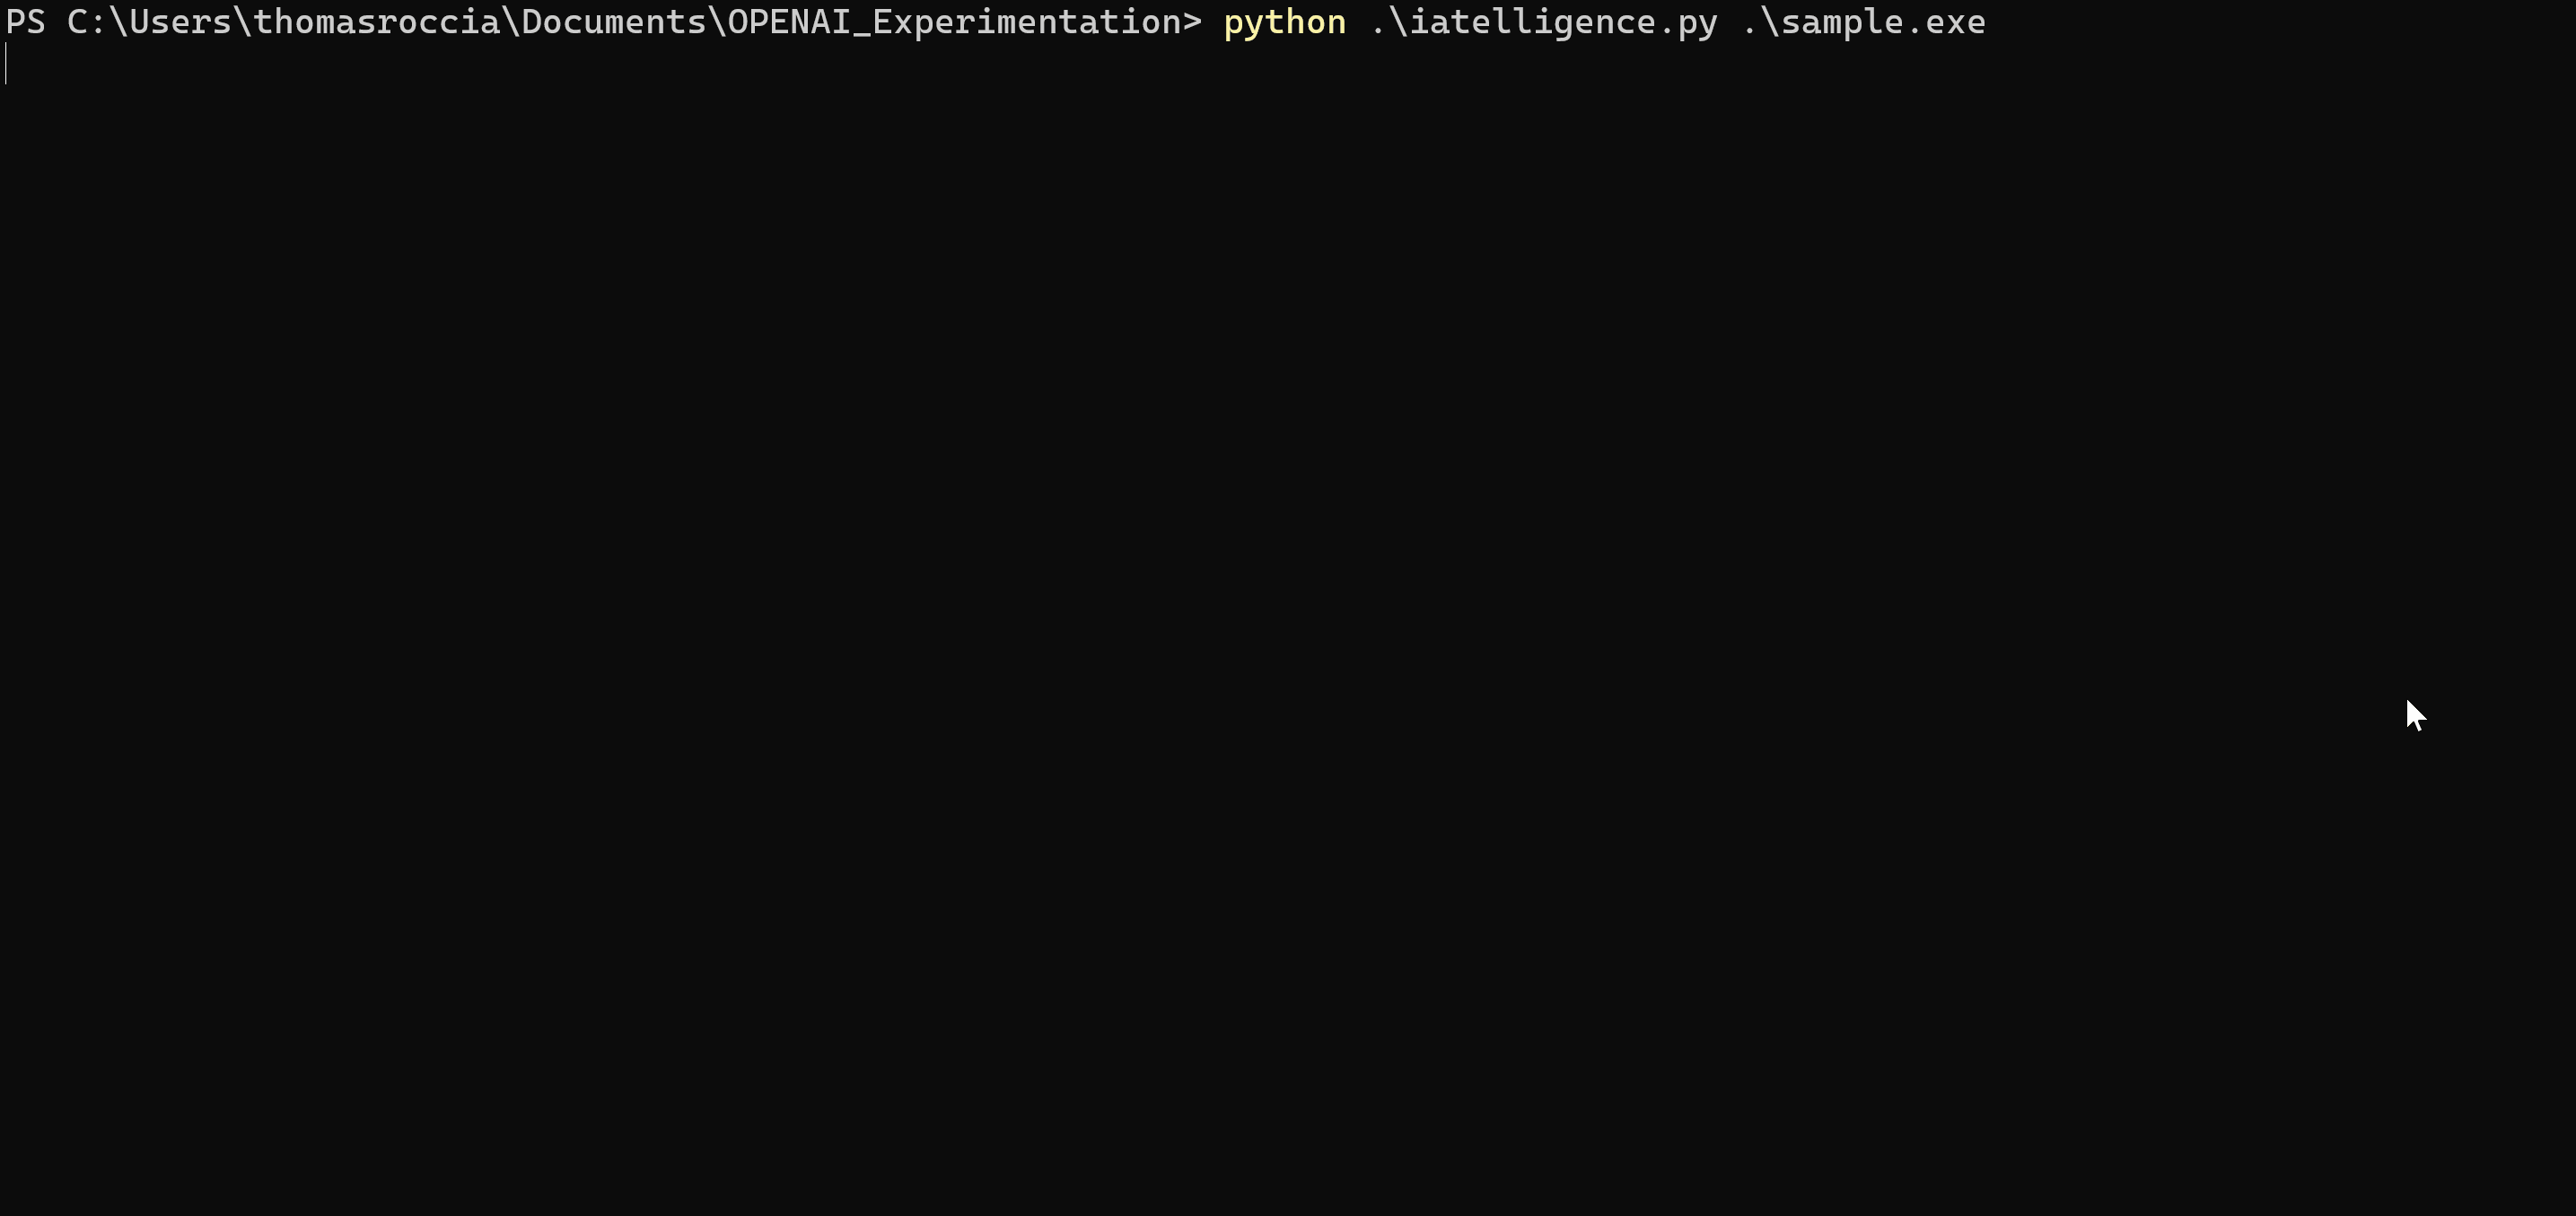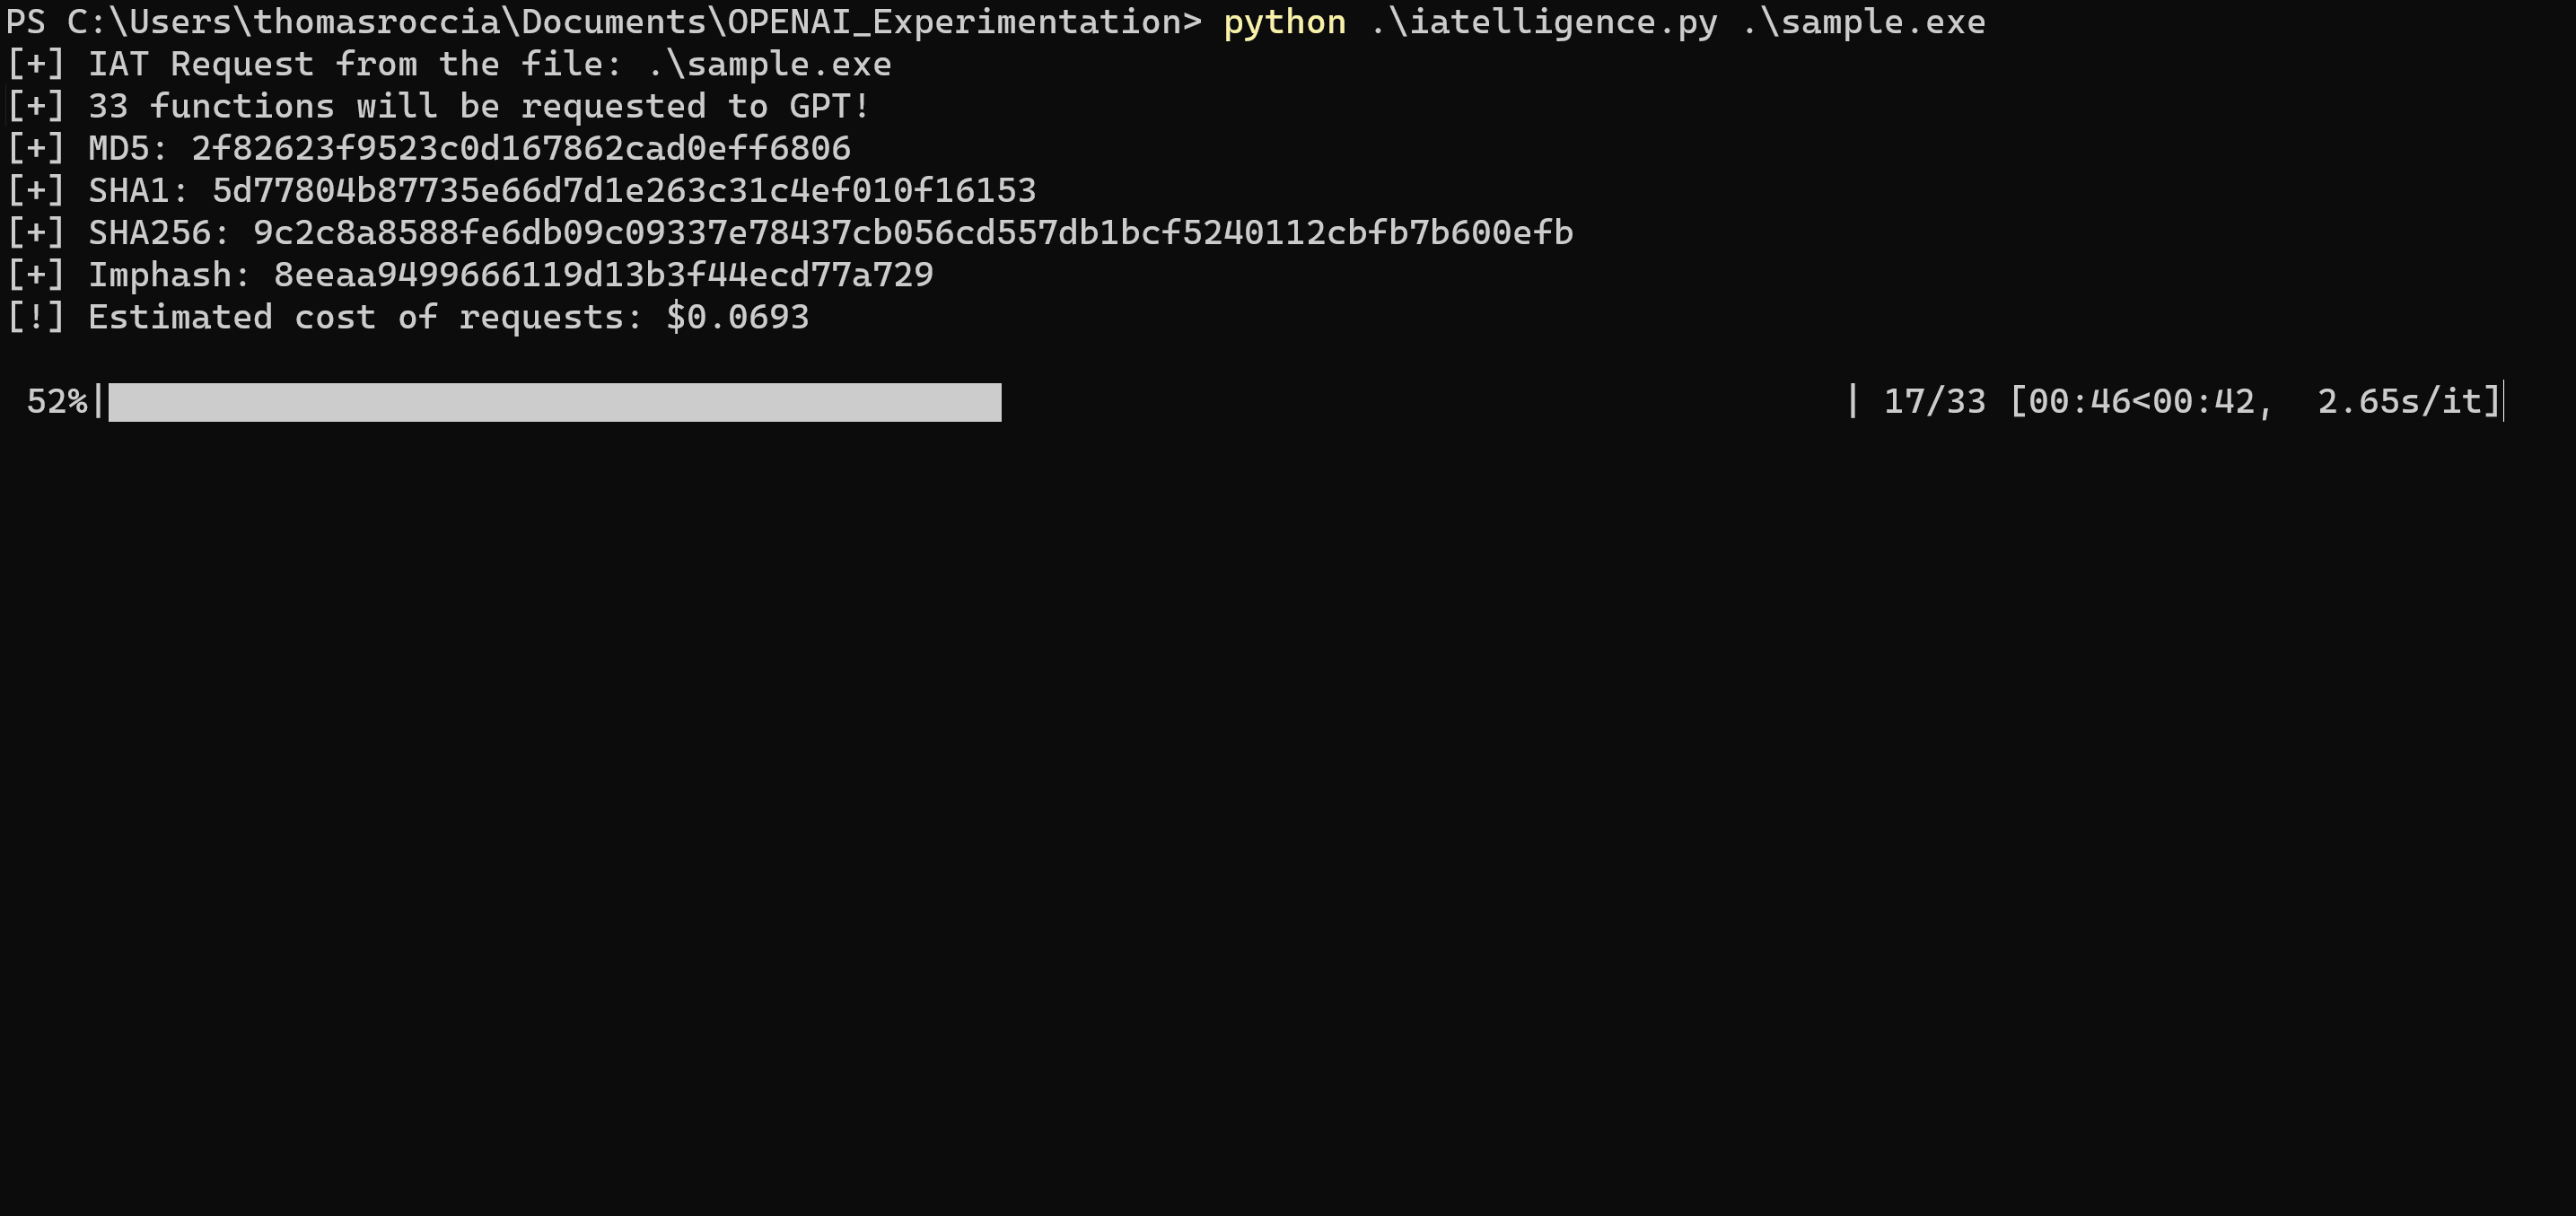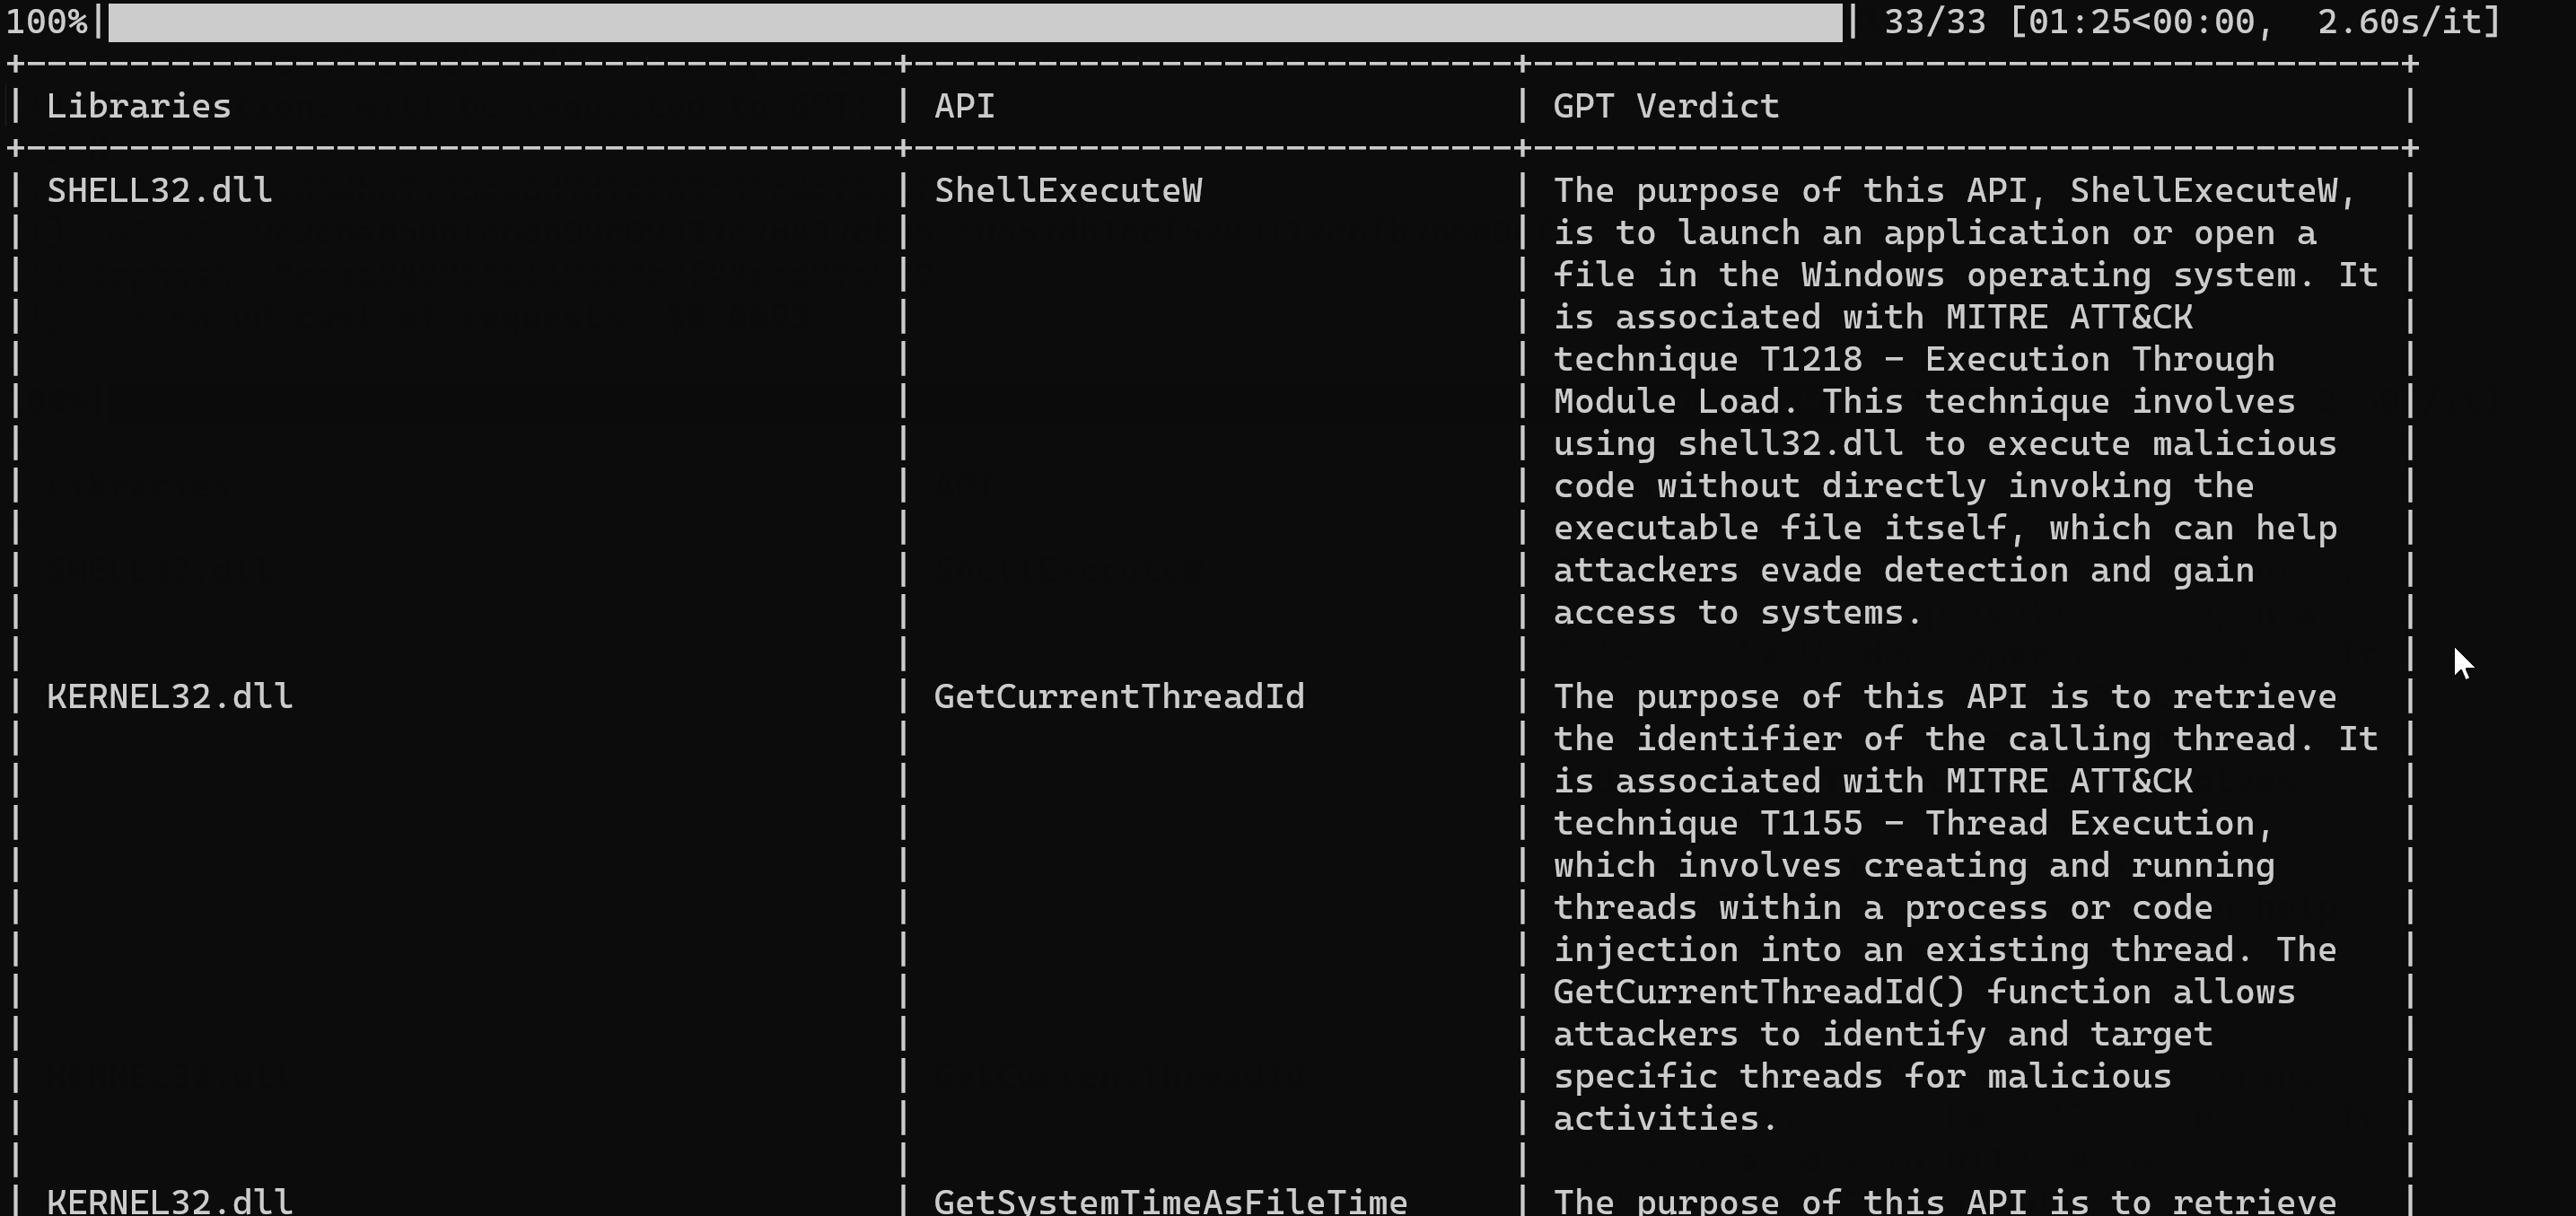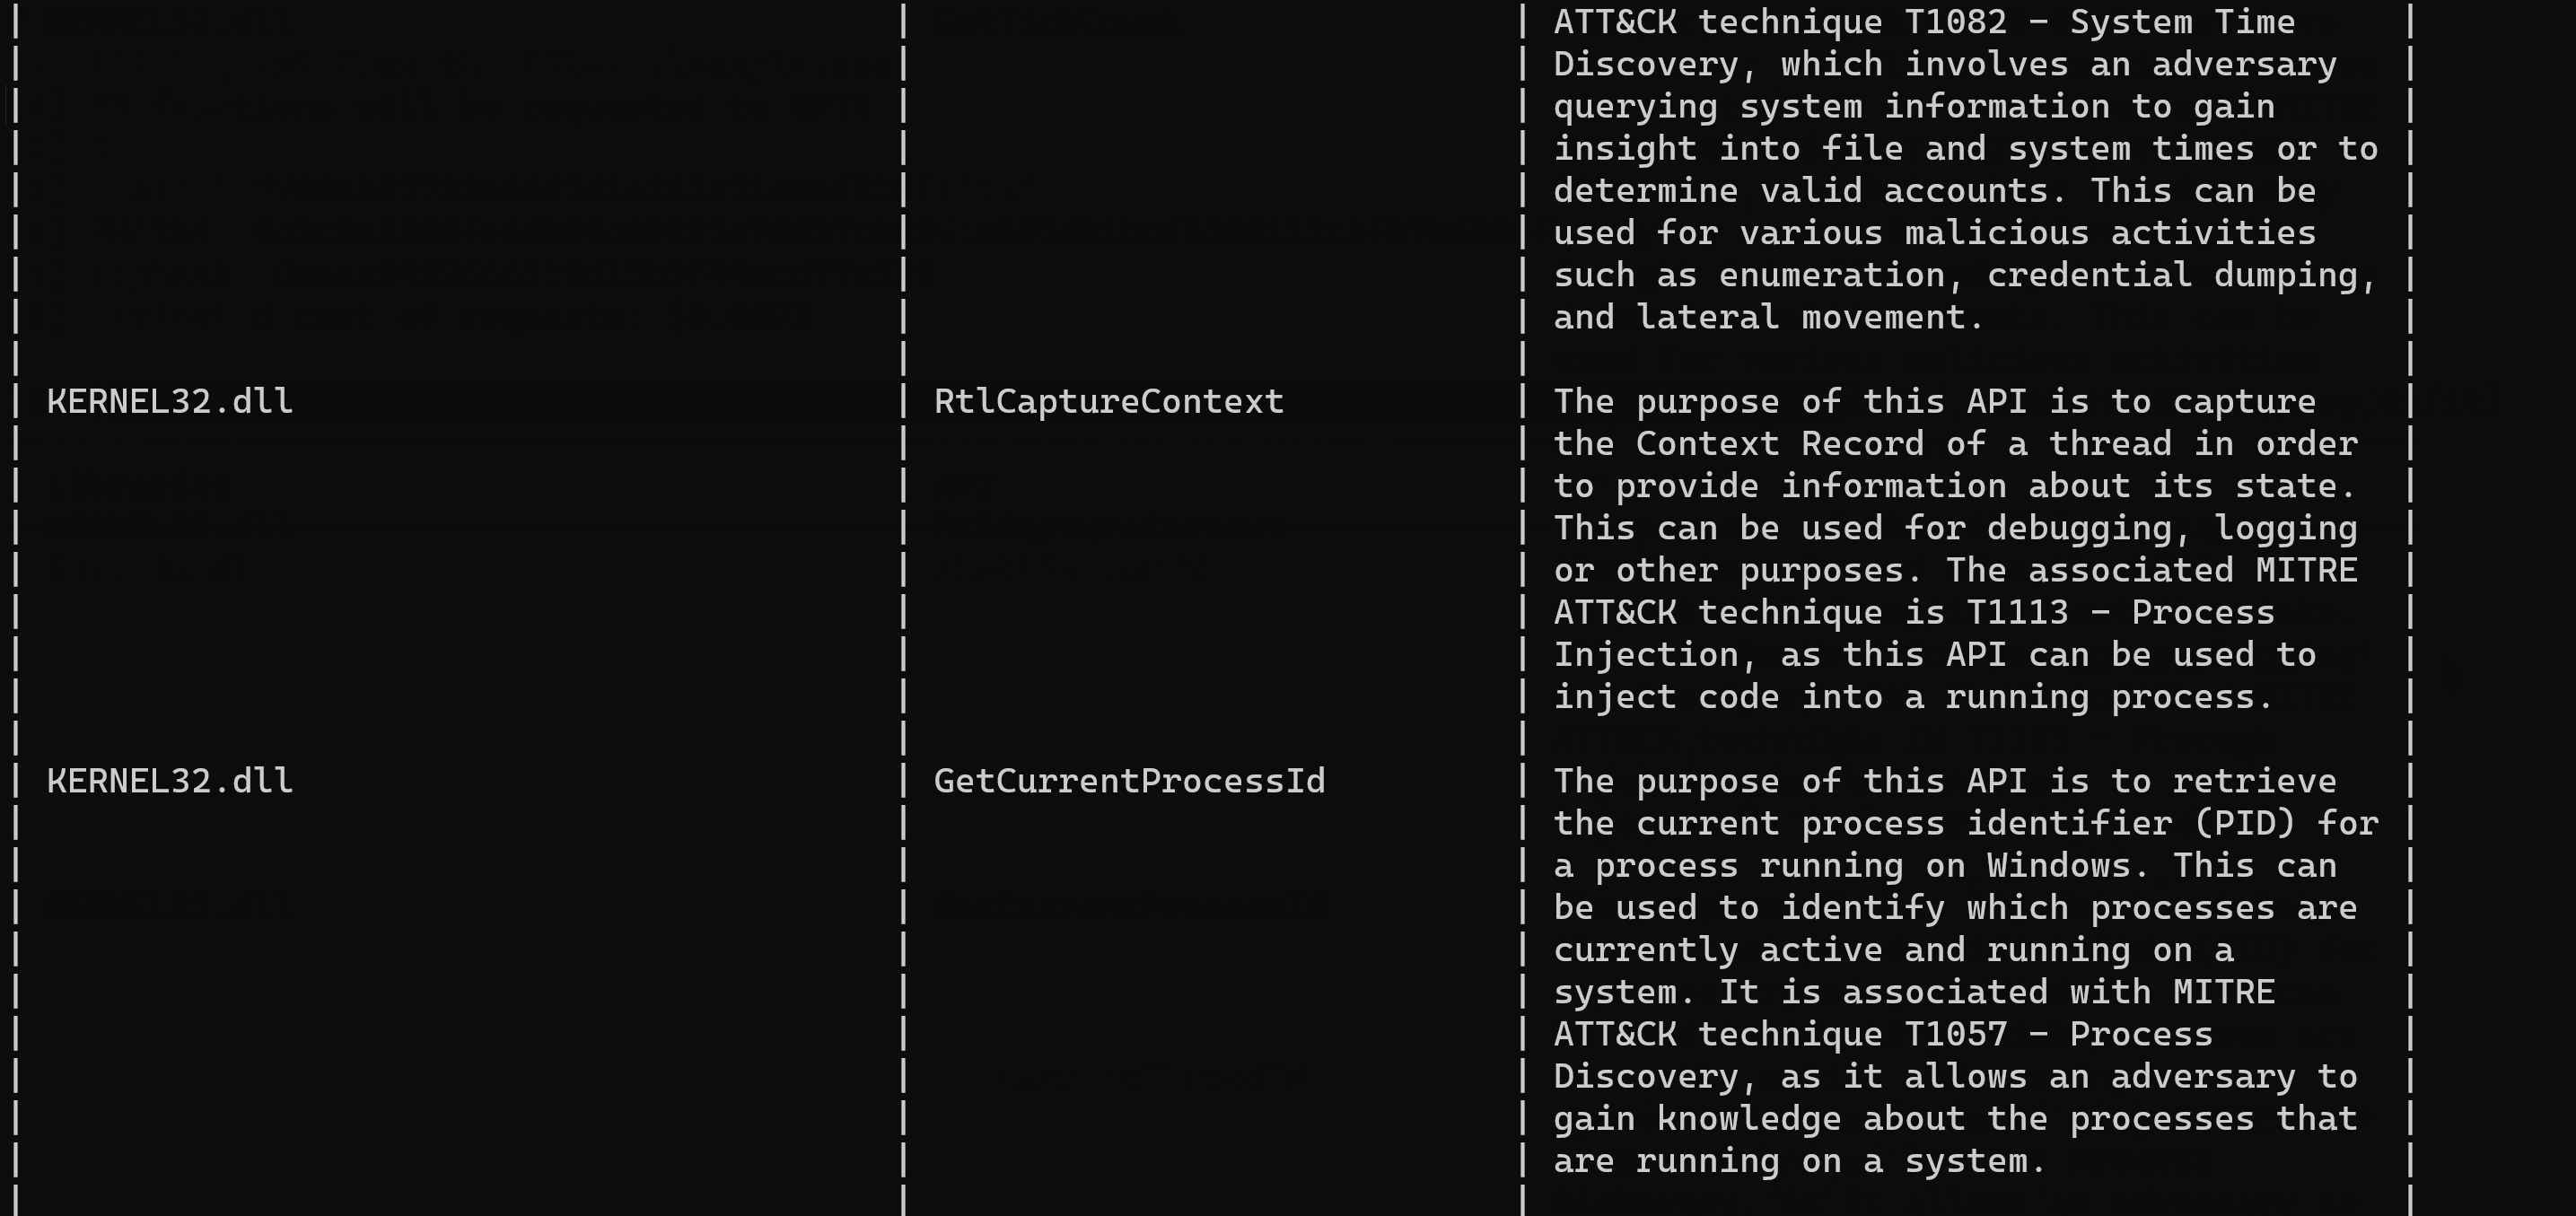 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 fr0gger/vthunting
Vthunting is a tiny script used to generate report about Virus Total hunting and send it by email, slack or telegram.
 gr4ym4ntx/attackintel
A python script to query the MITRE ATT&CK API for tactics, techniques, mitigations, & detection methods for specific threat groups.
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 ciprianster/osips
A Python script that gathers all valid IP addresses from all text files from a directory, and checks them against Whois database, TOR relays and…
 corelight/detect-ransomware-filenames
Zeek script that monitors SMB traffic and alerts on known ransomware filenames using the Anti-Ransomware File System Resource Manager list.
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…