
beelzebub
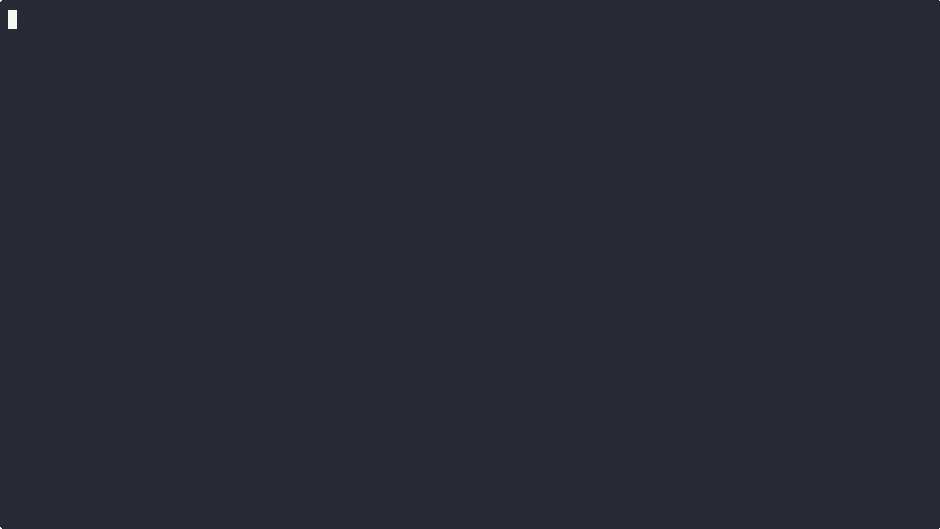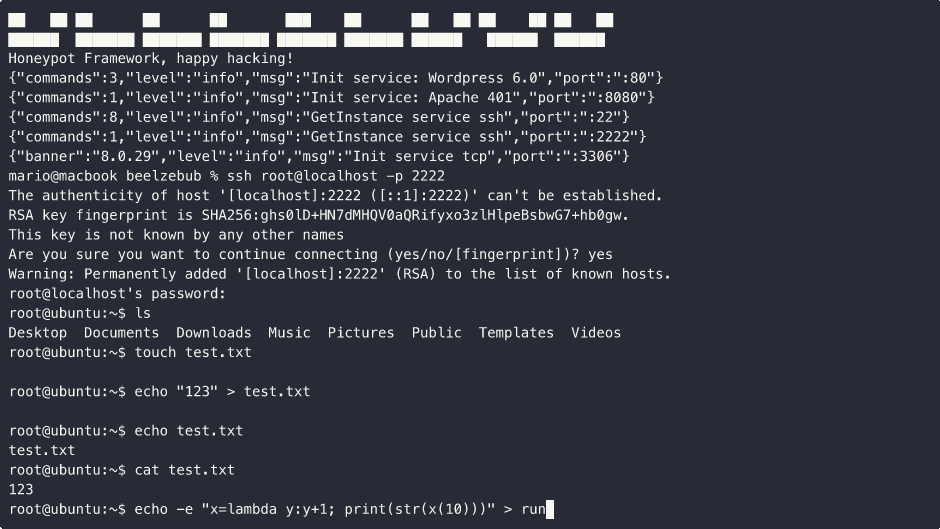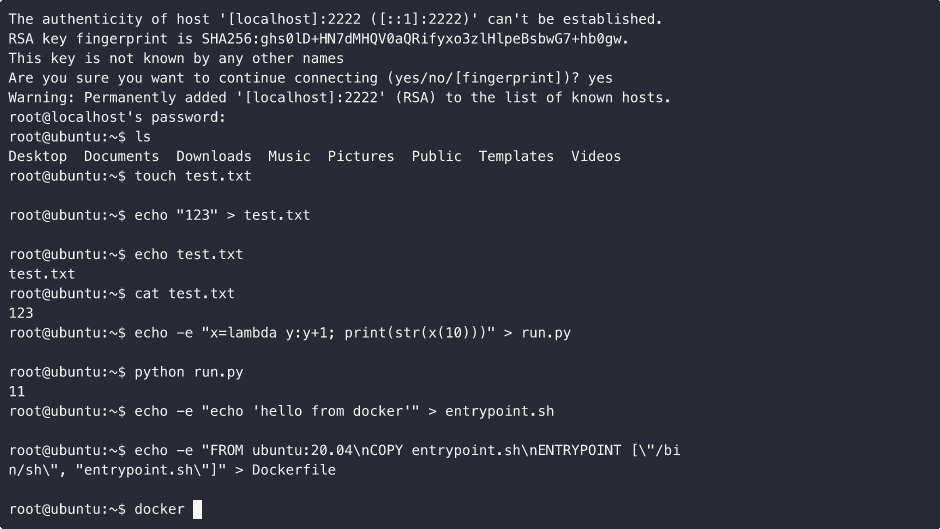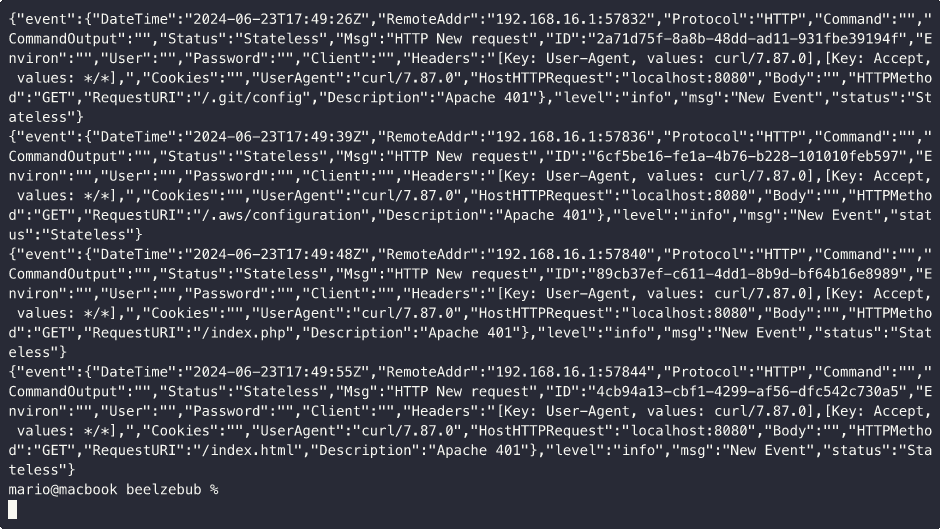
 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
ai-securityapi-securitycontainer-security+7
2.2k
beelzebub-labs/beelzebubA secure low code deception runtime framework, leveraging AI for System Virtualization.
 bhavsec/reconspider
🔎 Most Advanced Open Source Intelligence (OSINT) Framework for scanning IP Address, Emails, Websites, Organizations.
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 nox-project/nox-framework
High-performance OSINT/CTI framework for automated identity pivoting and risk analysis across 120+ sources.
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
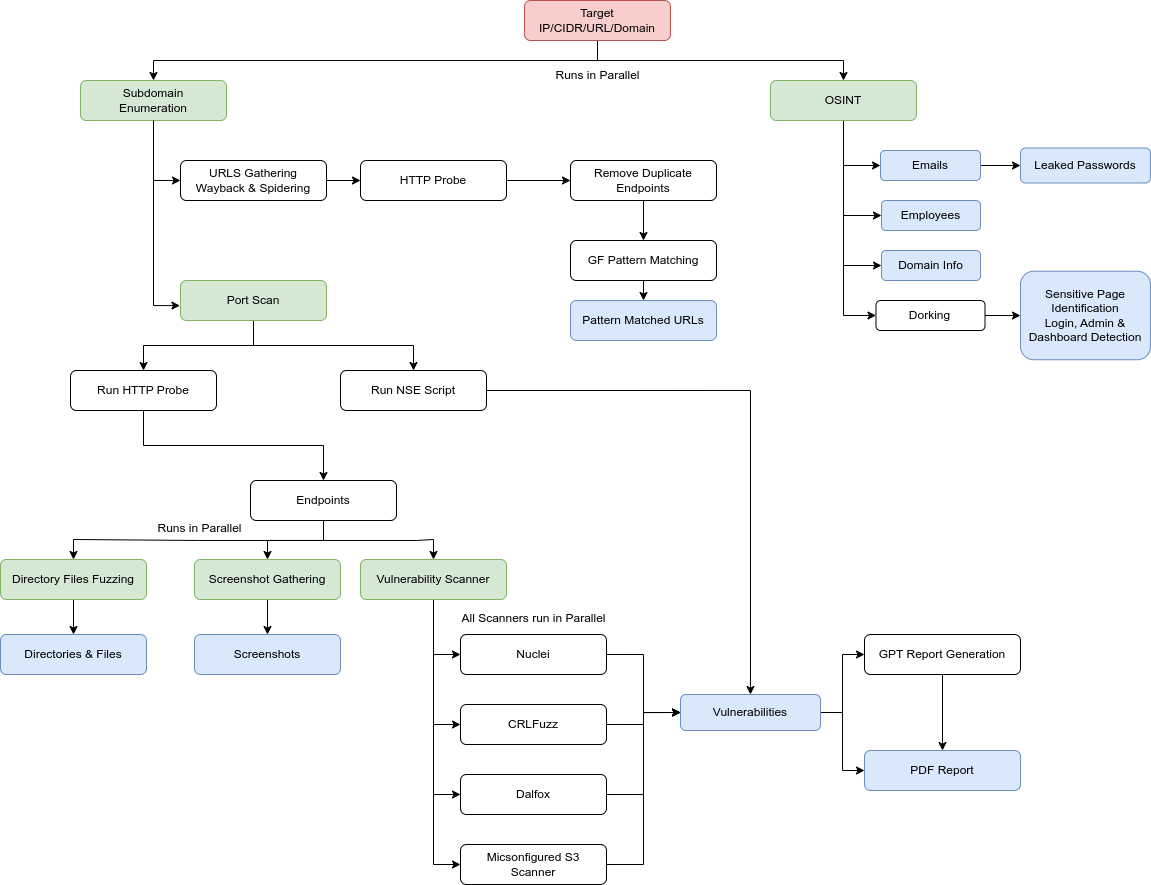 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
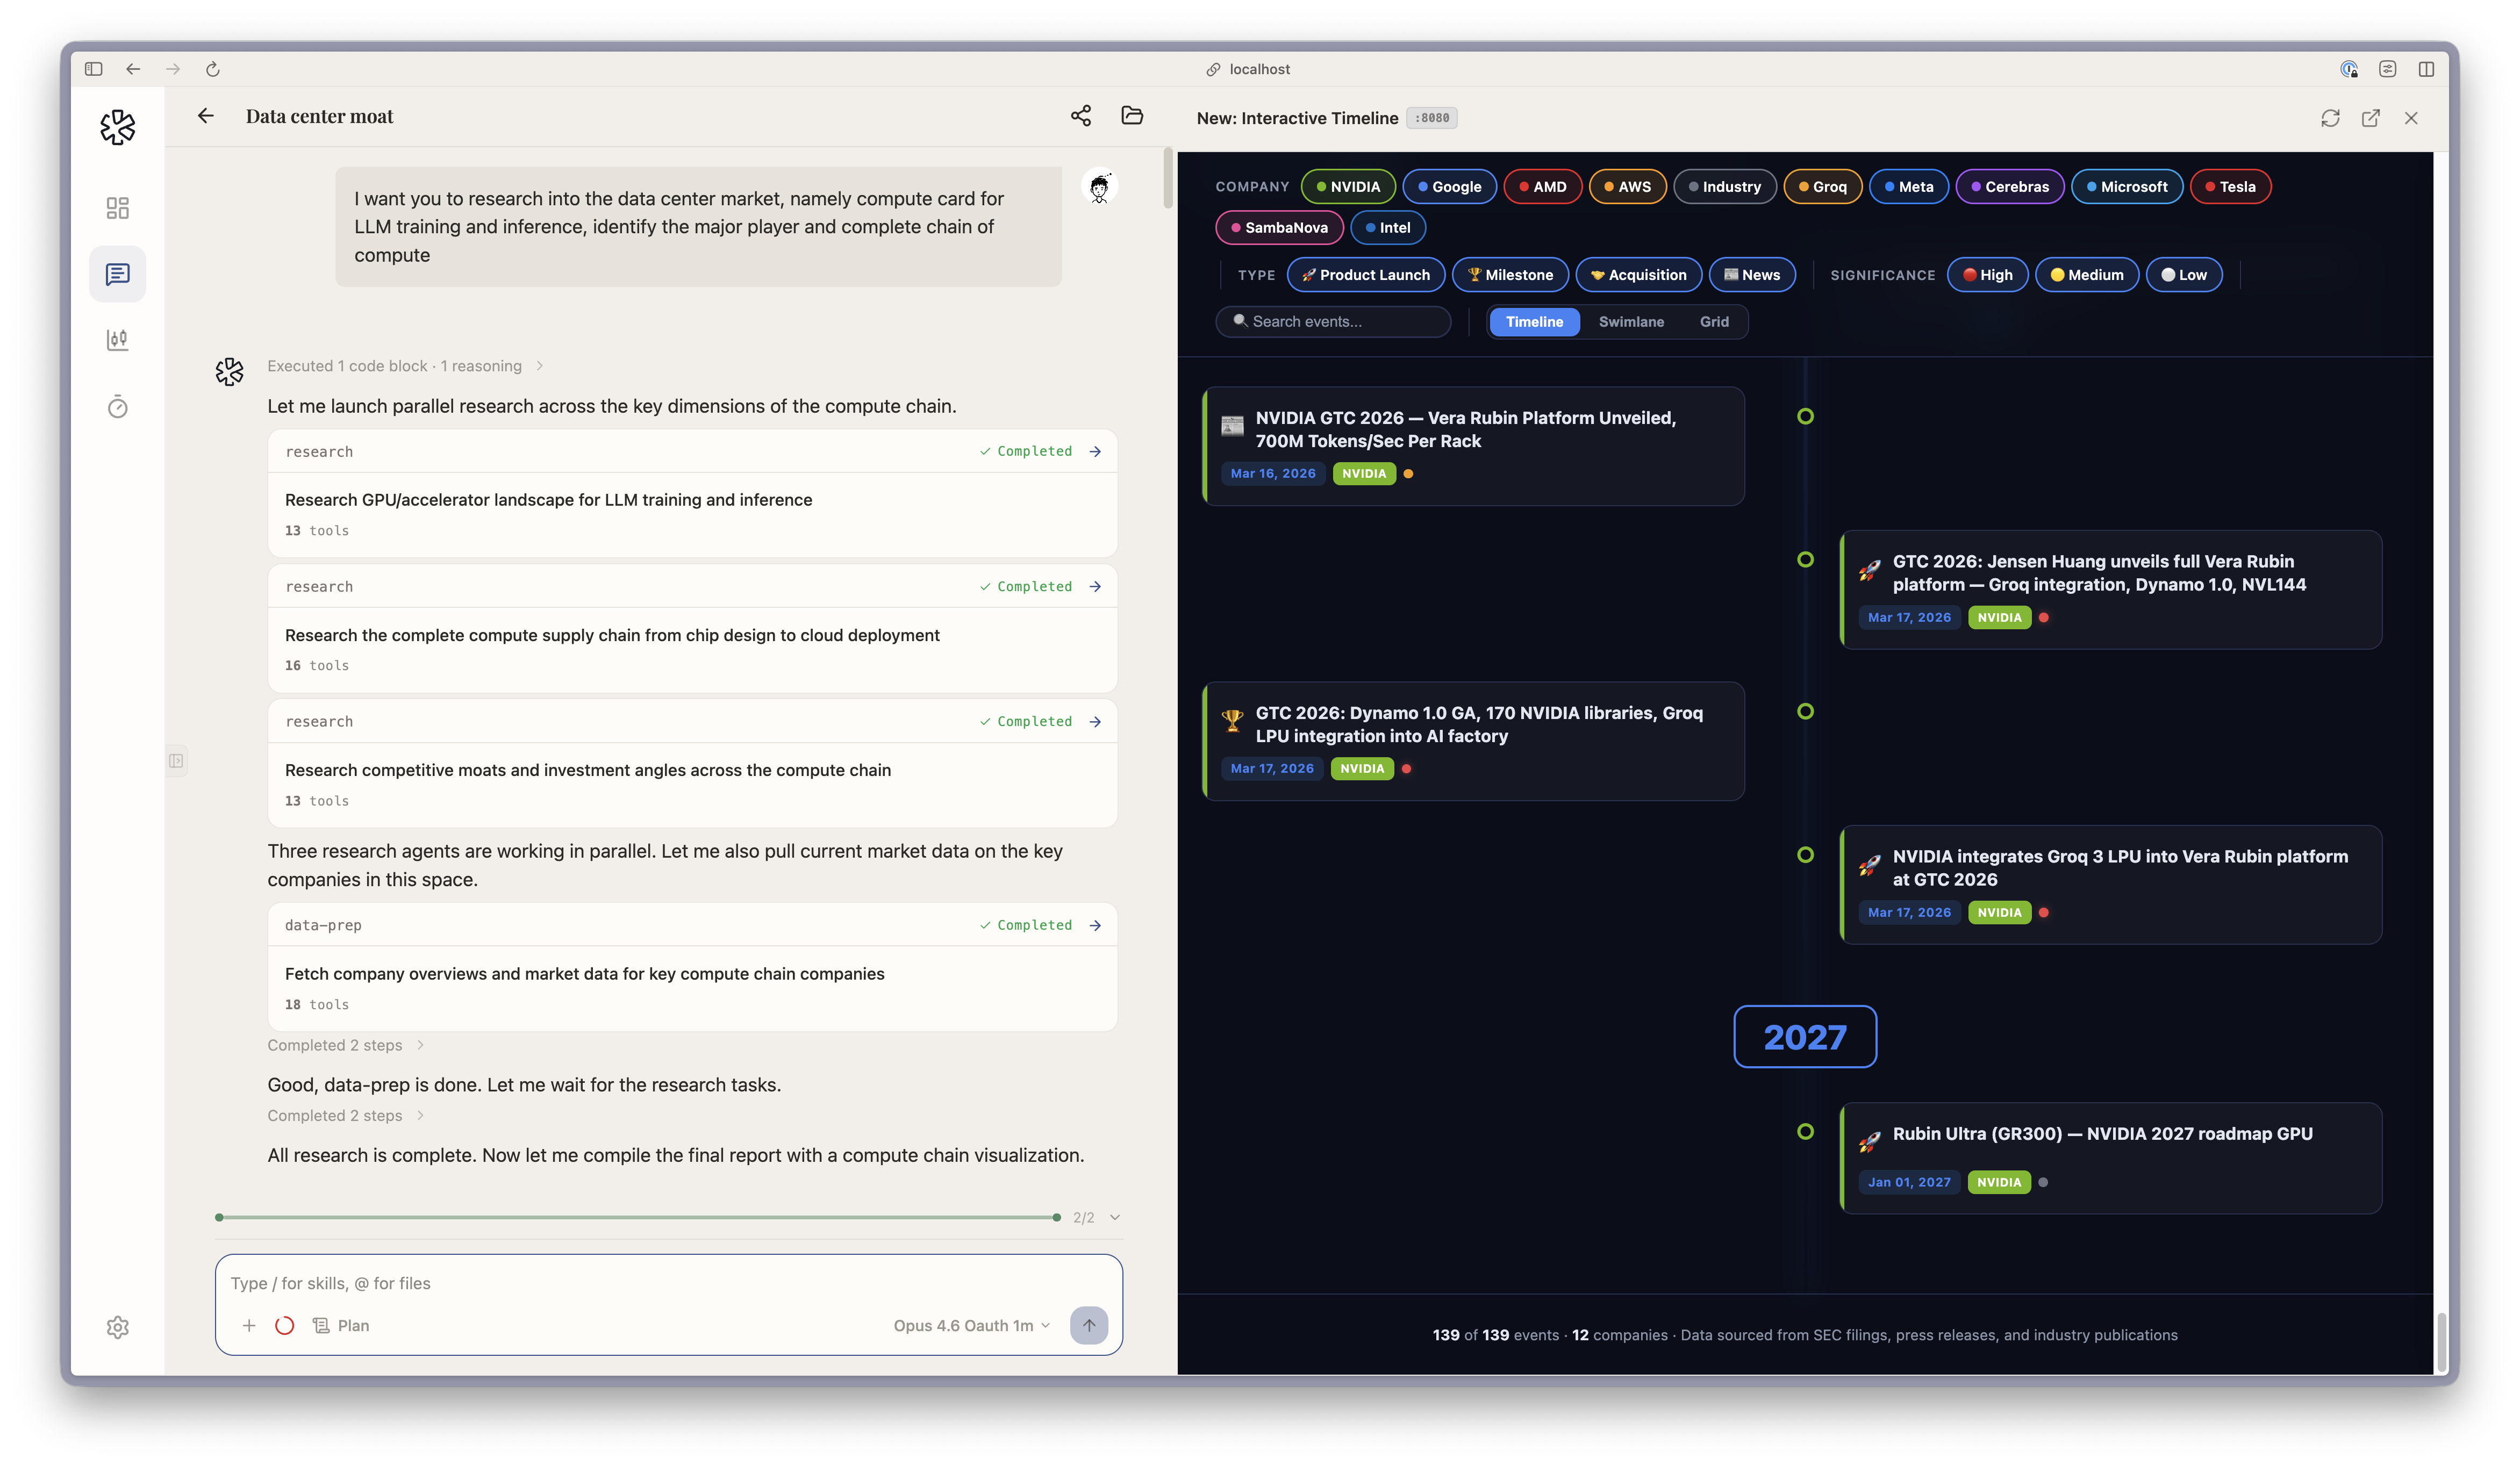 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
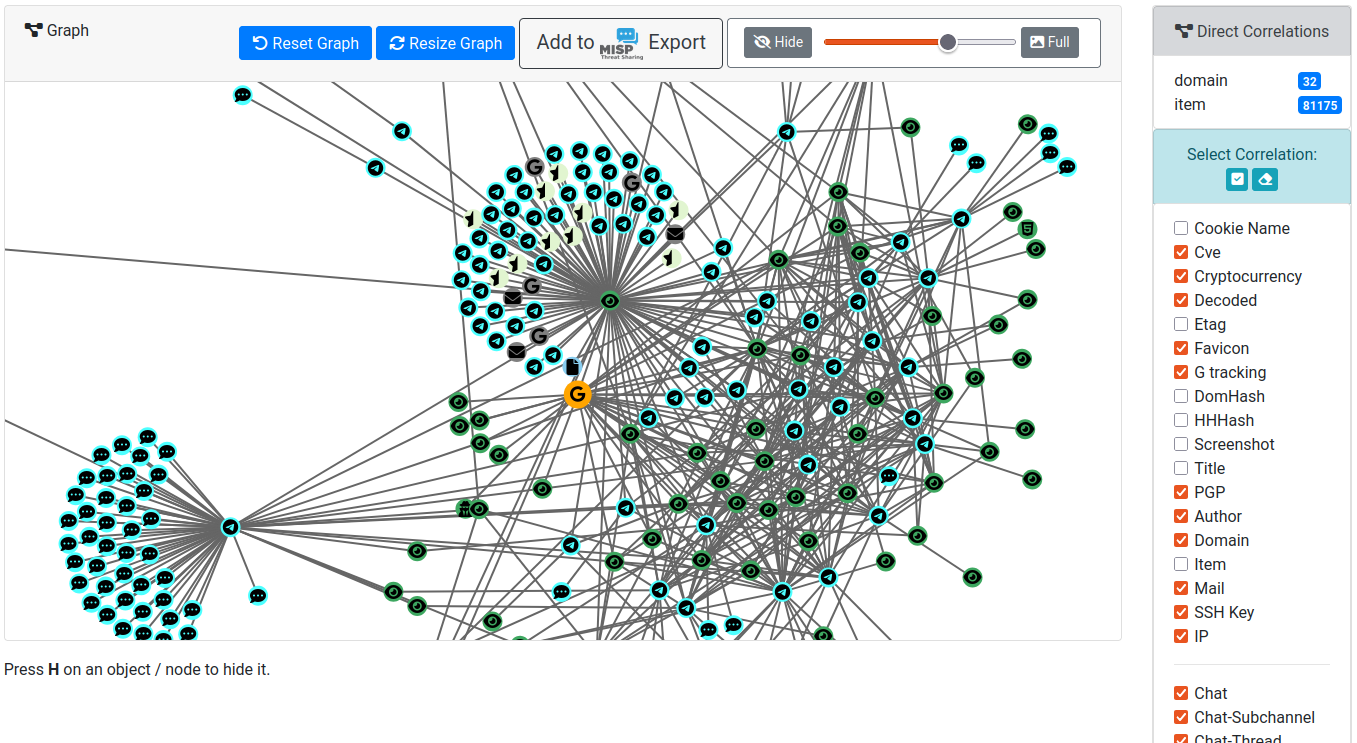 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
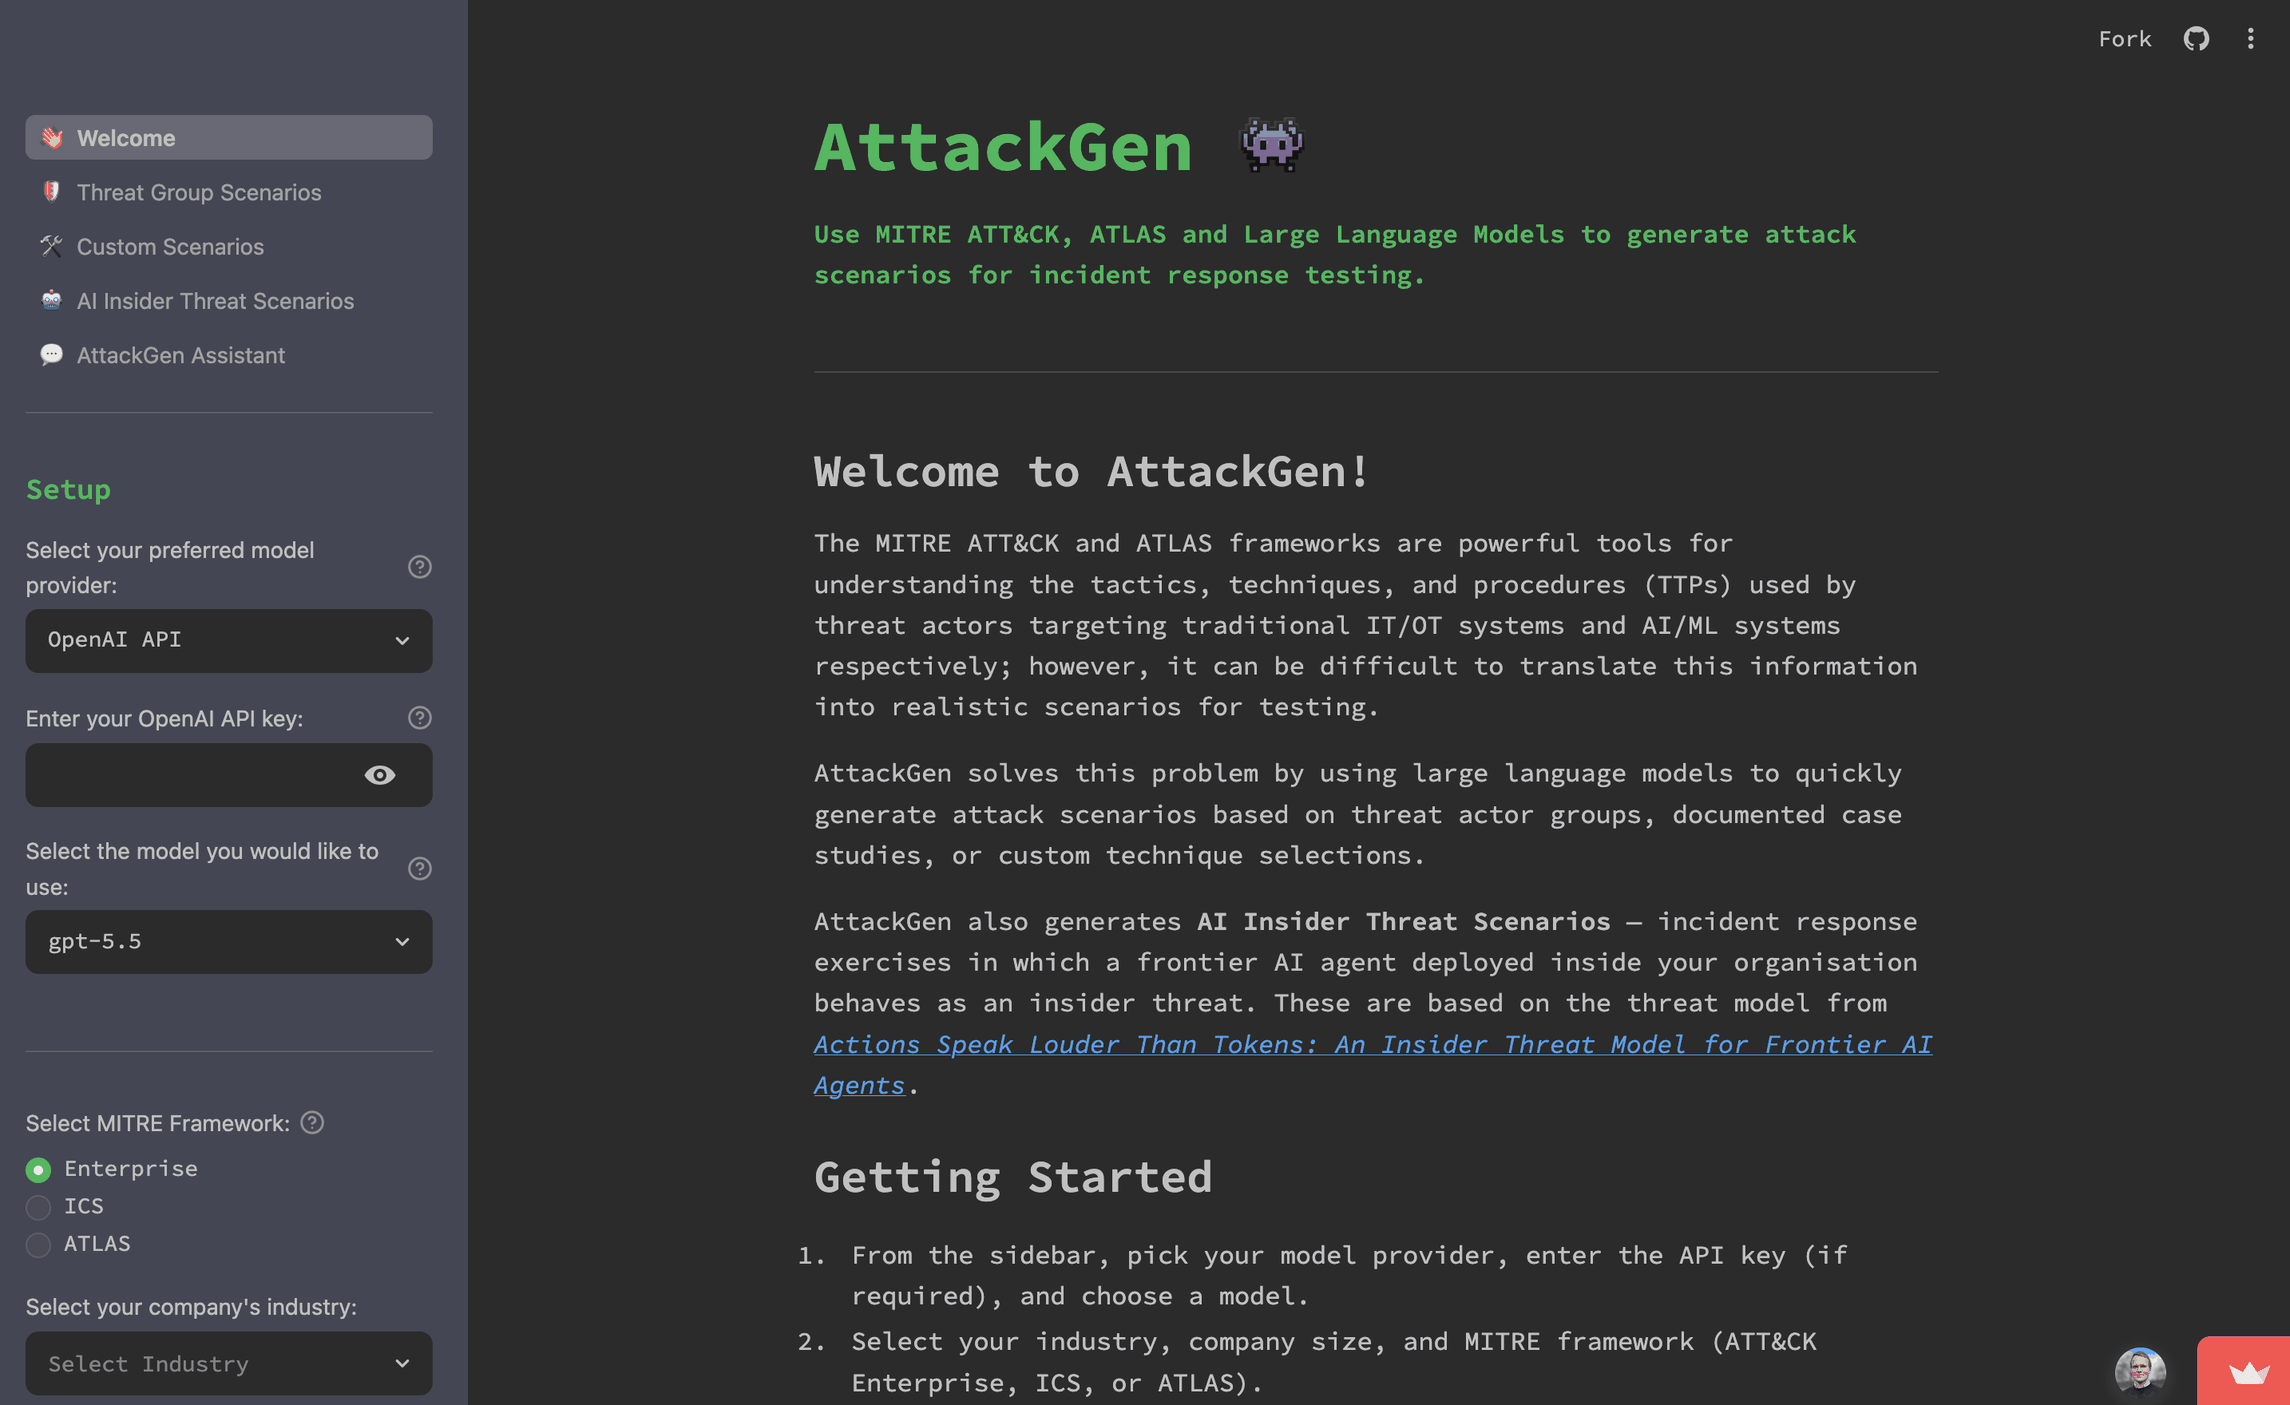 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
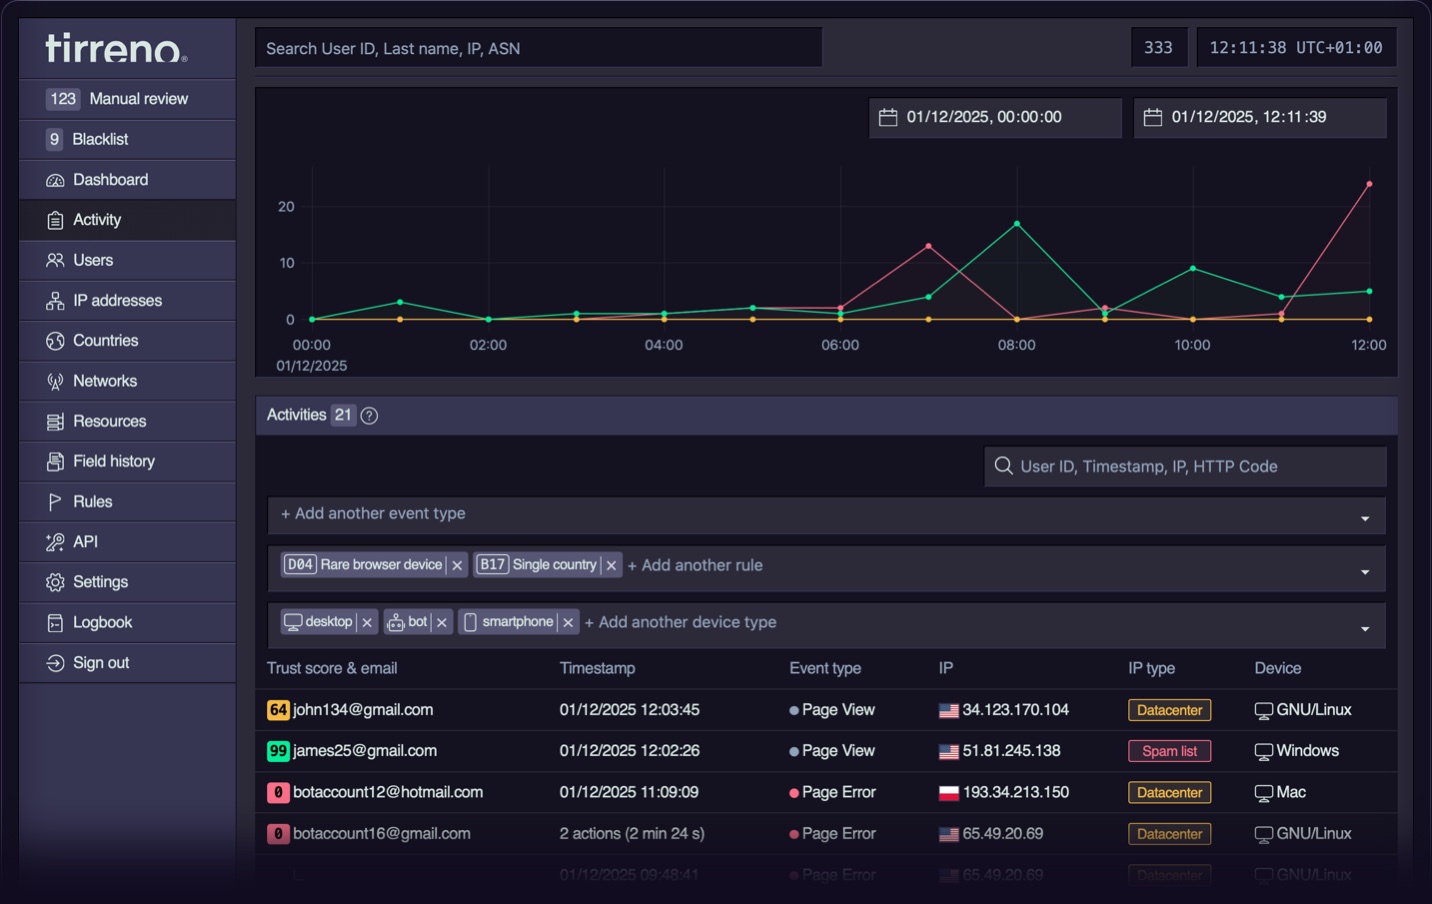 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 olafhartong/attackdatamap
A datasource assessment on an event level to show potential coverage or the MITRE ATT&CK framework