
buttinsky
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
information-gatheringintrusion-detectionmalware-analysis+2
82
mushorg/buttinskyBotnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
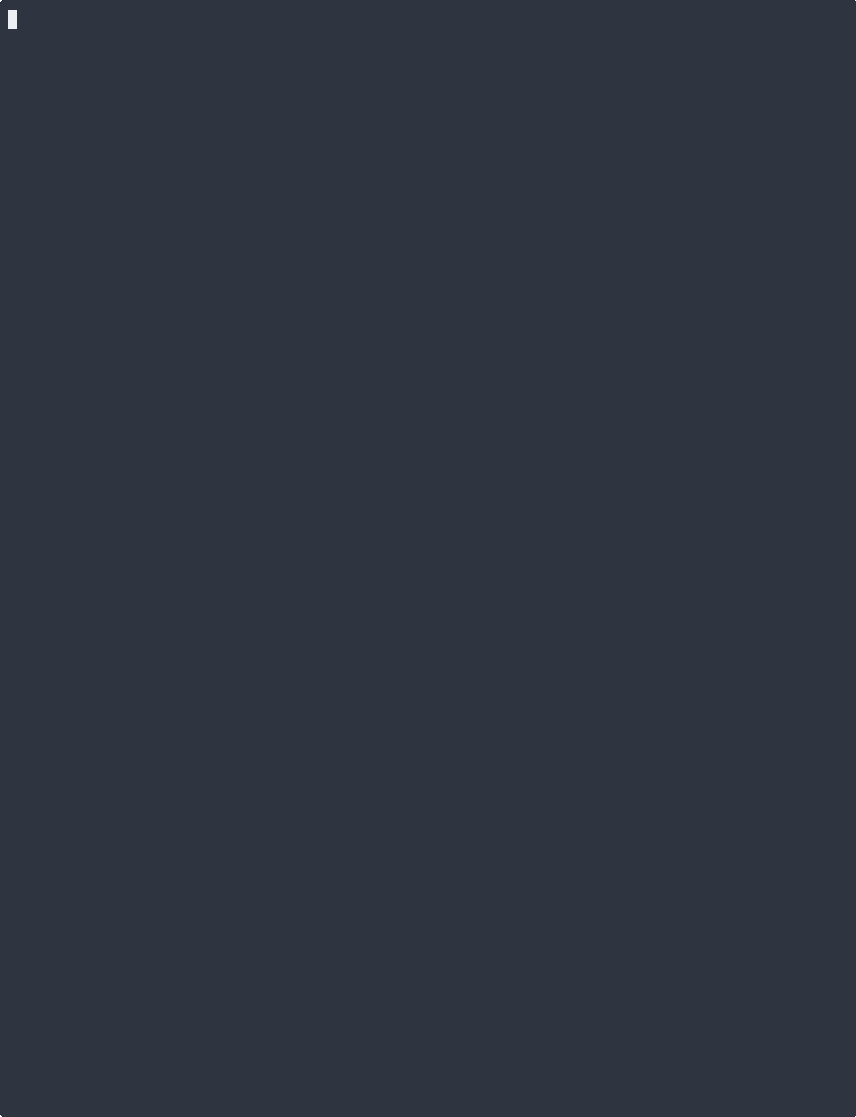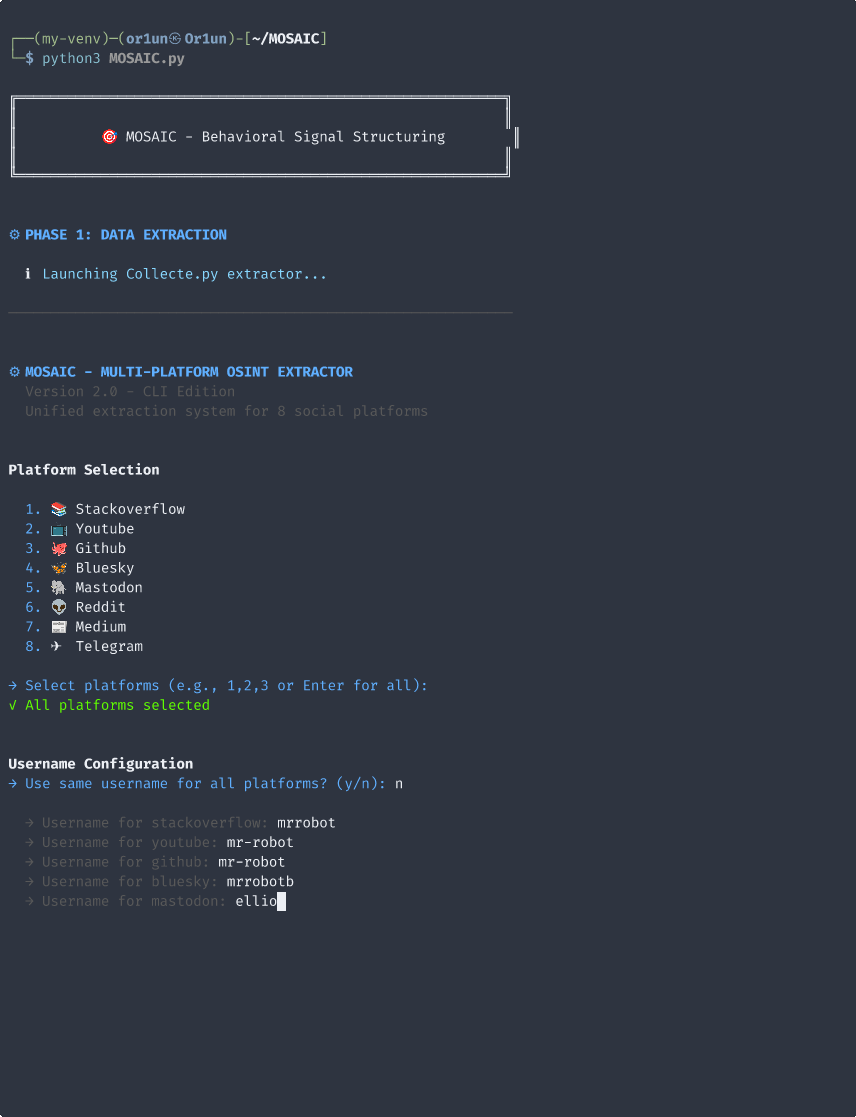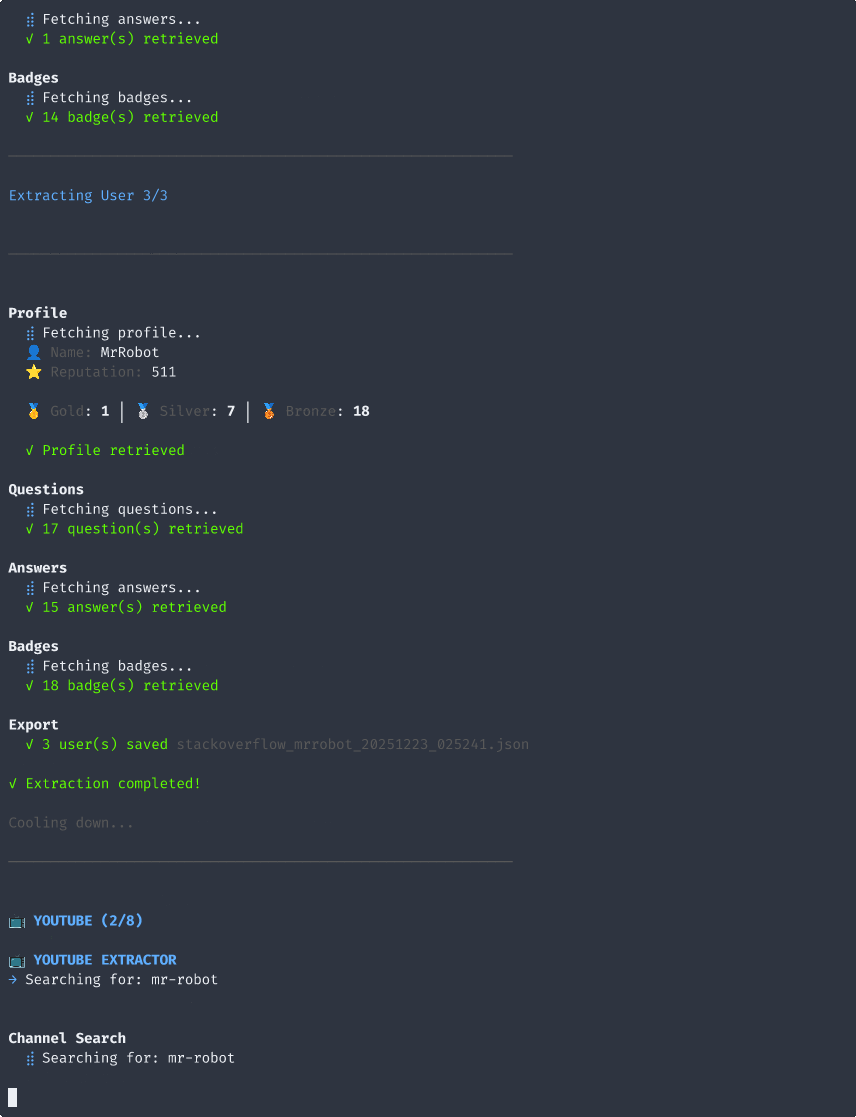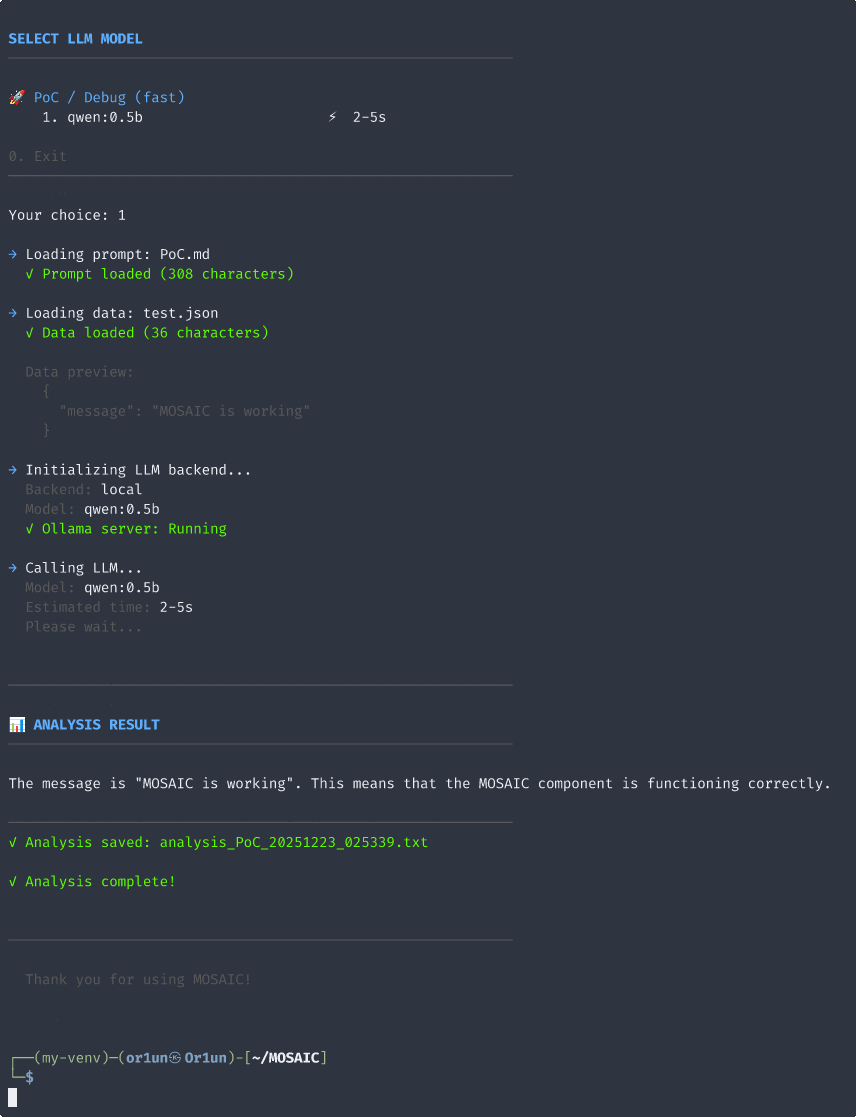 or1un/mosaic
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.
 expert21/hermes-osint
Hermes — an ephemeral, Docker-powered OSINT framework for testing, tinkering, and secure investigative automation.
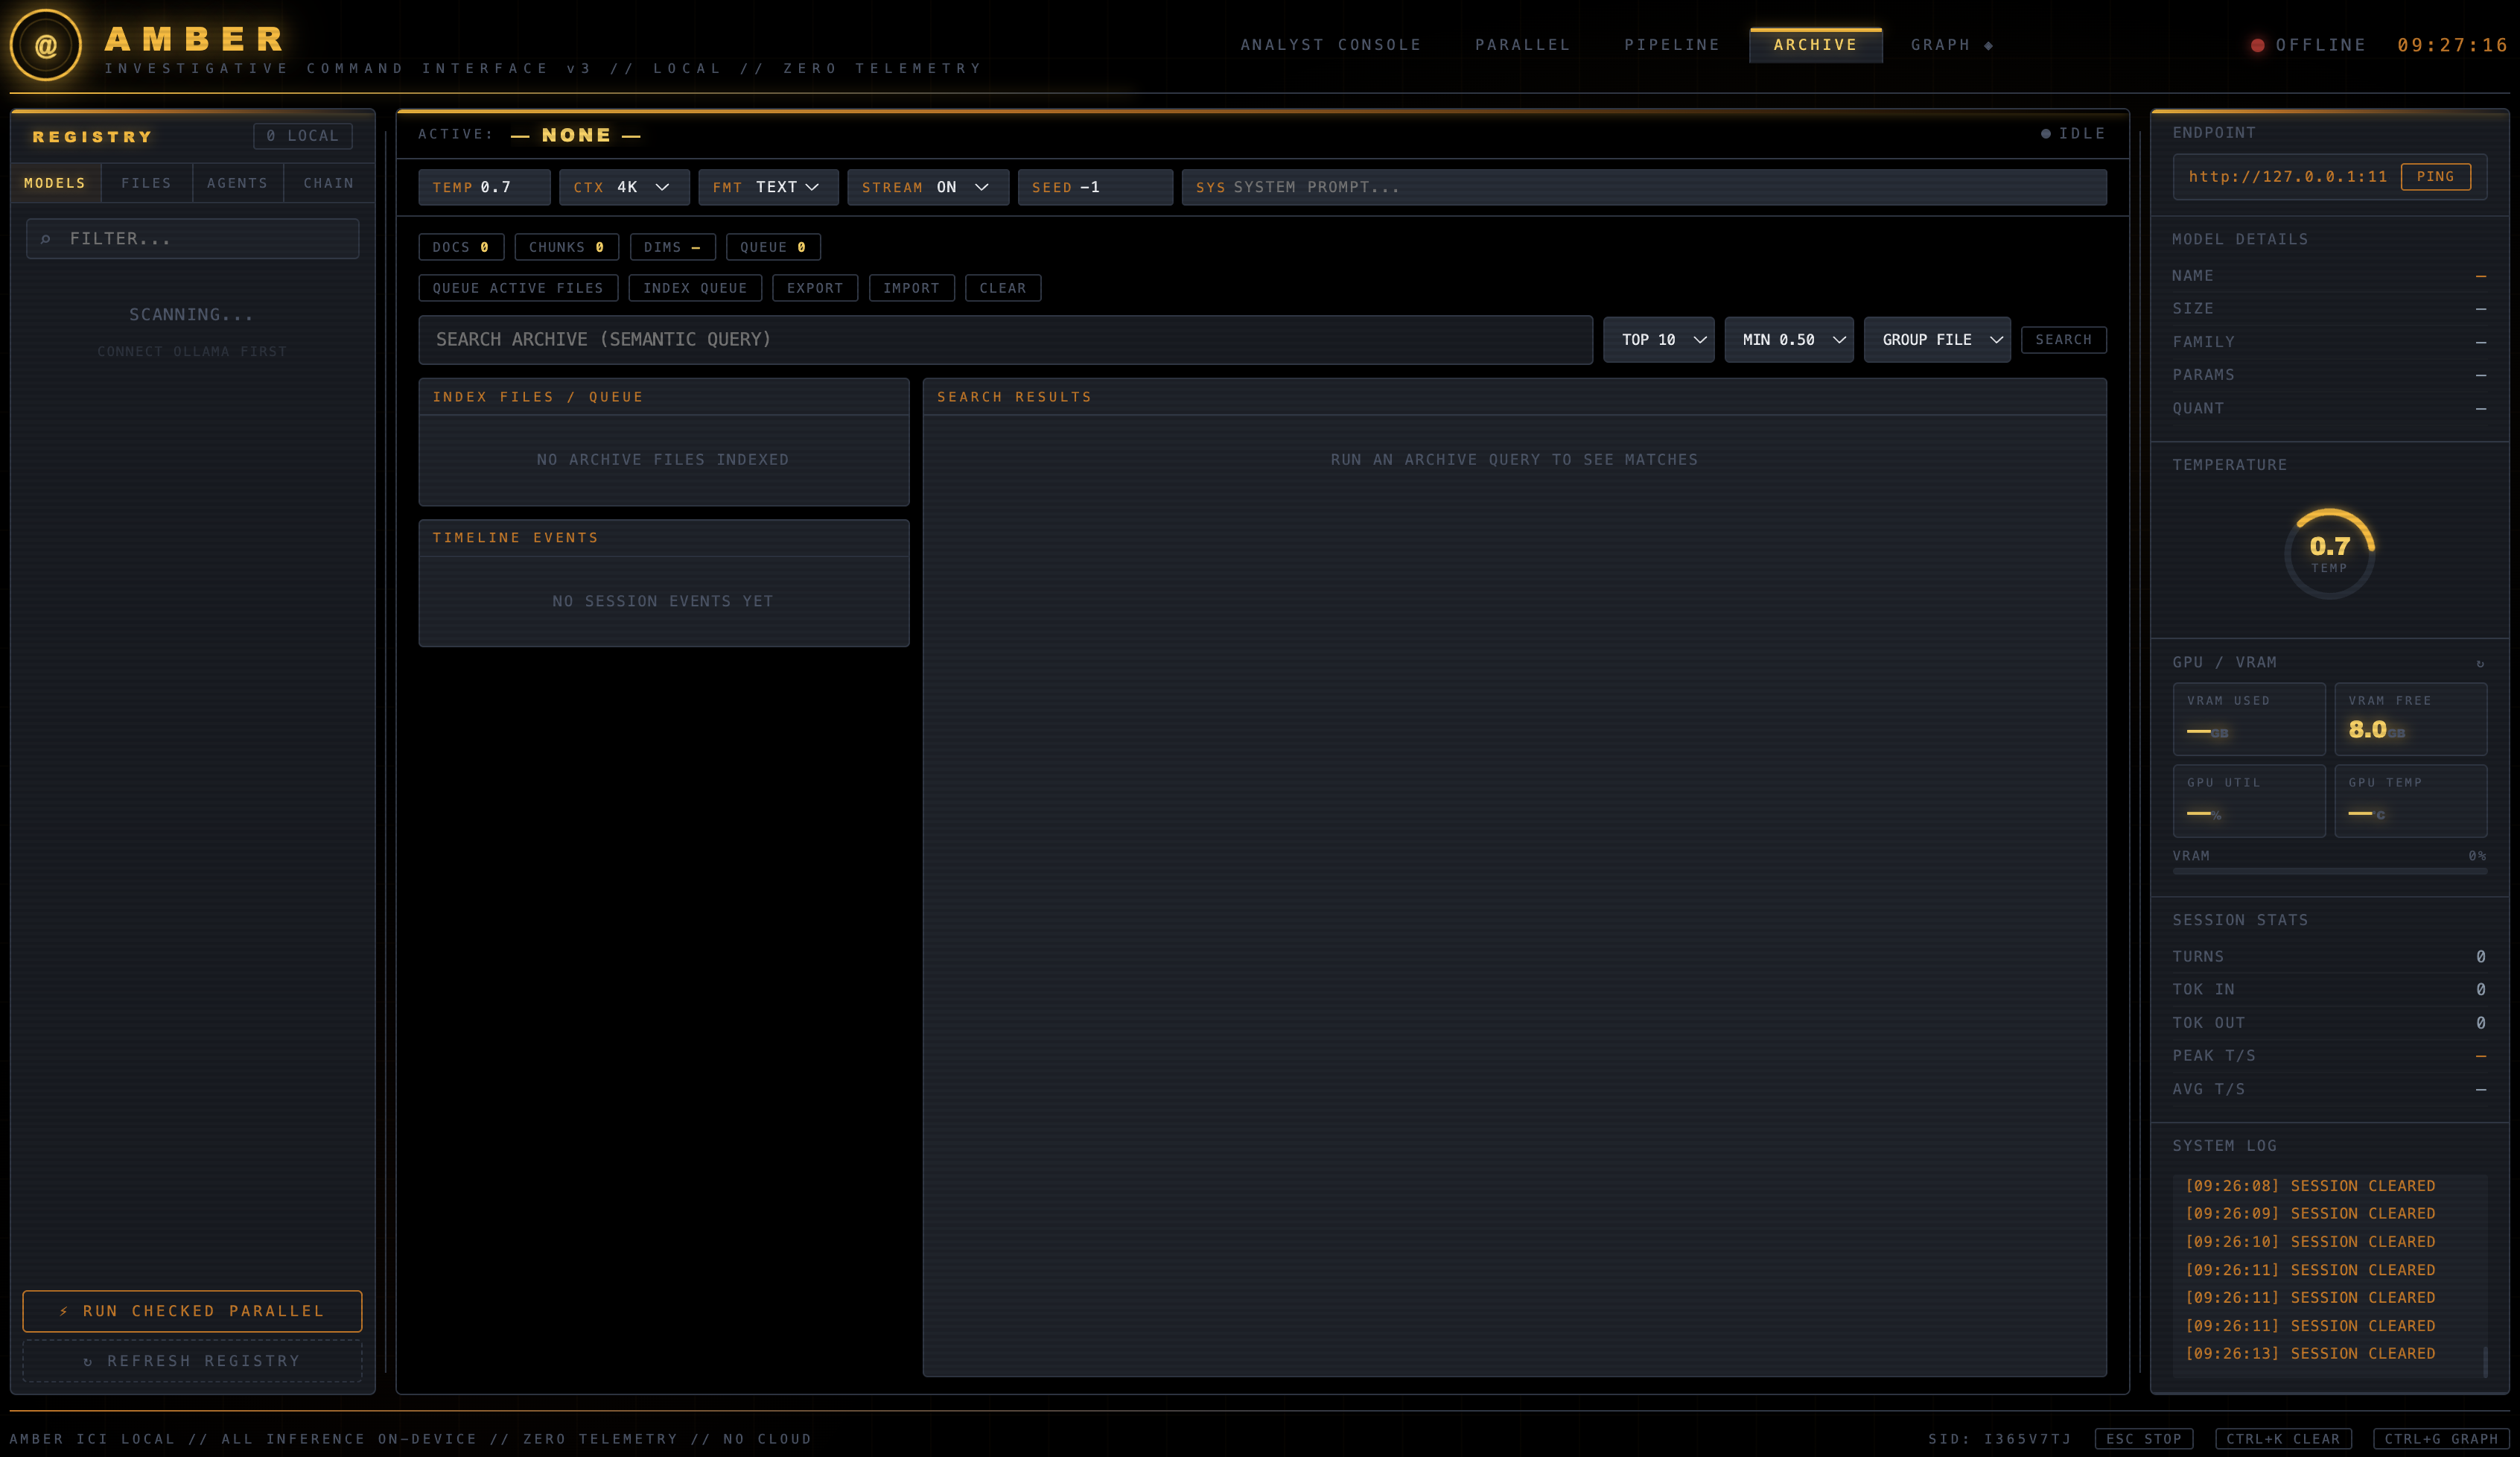 gs-ai/amber-ici
AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…
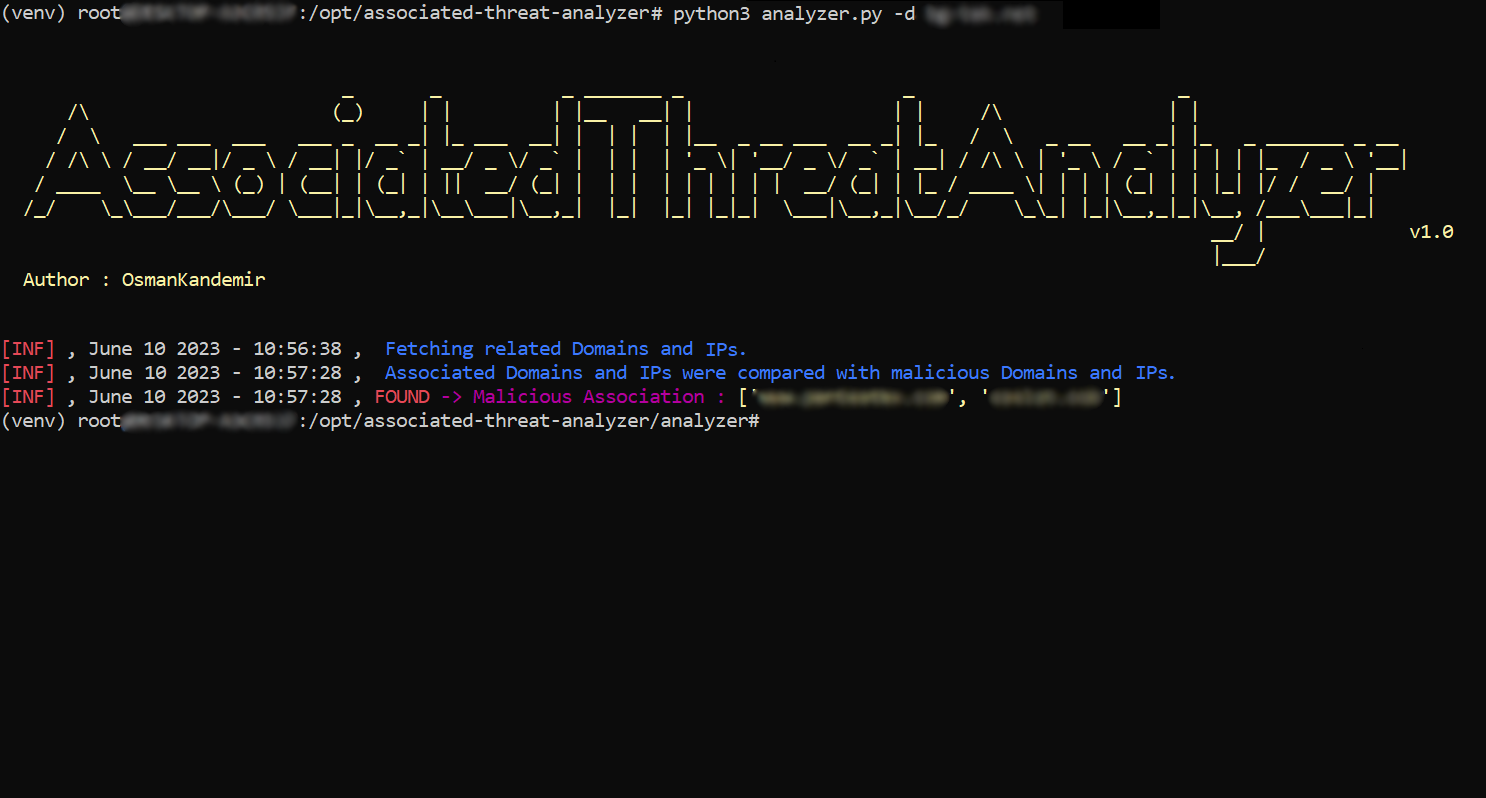 osmankandemir/associated-threat-analyzer
Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
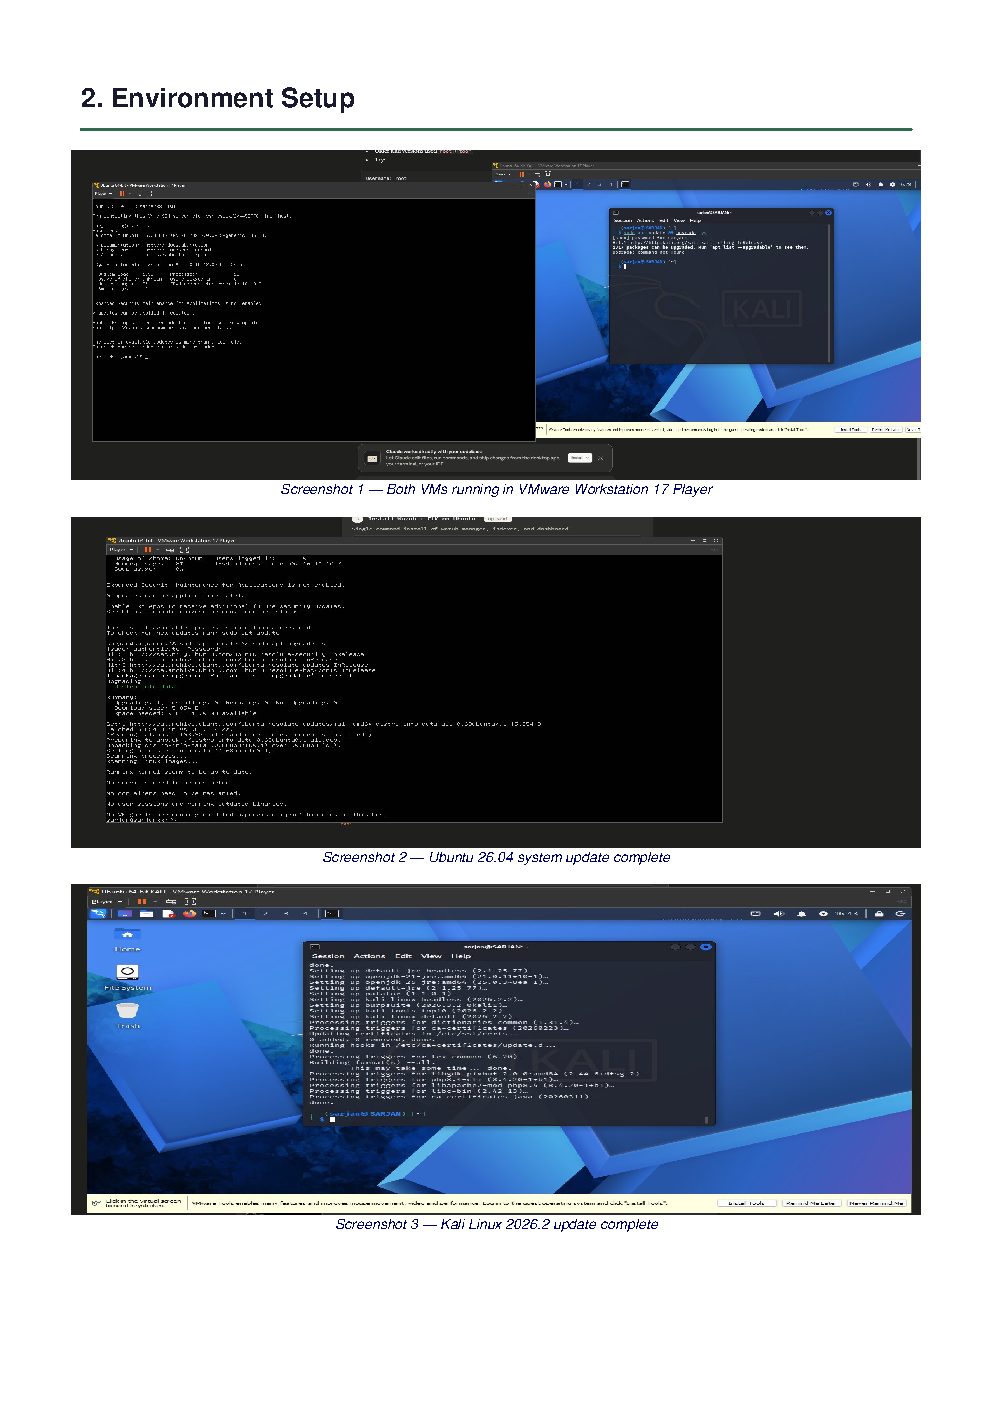 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…

 iitoneloc/sigint
Real-time OSINT intelligence dashboard: 7 live data sources (aircraft, AIS vessels, seismic, fires, weather, GDELT events, news) on an interactive…
 abdirisaq-ali-aynab/vulnerability-assessment
Professional cybersecurity assessment demonstrating vulnerability identification, CVSS severity scoring, MITRE ATT&CK framework application, and…
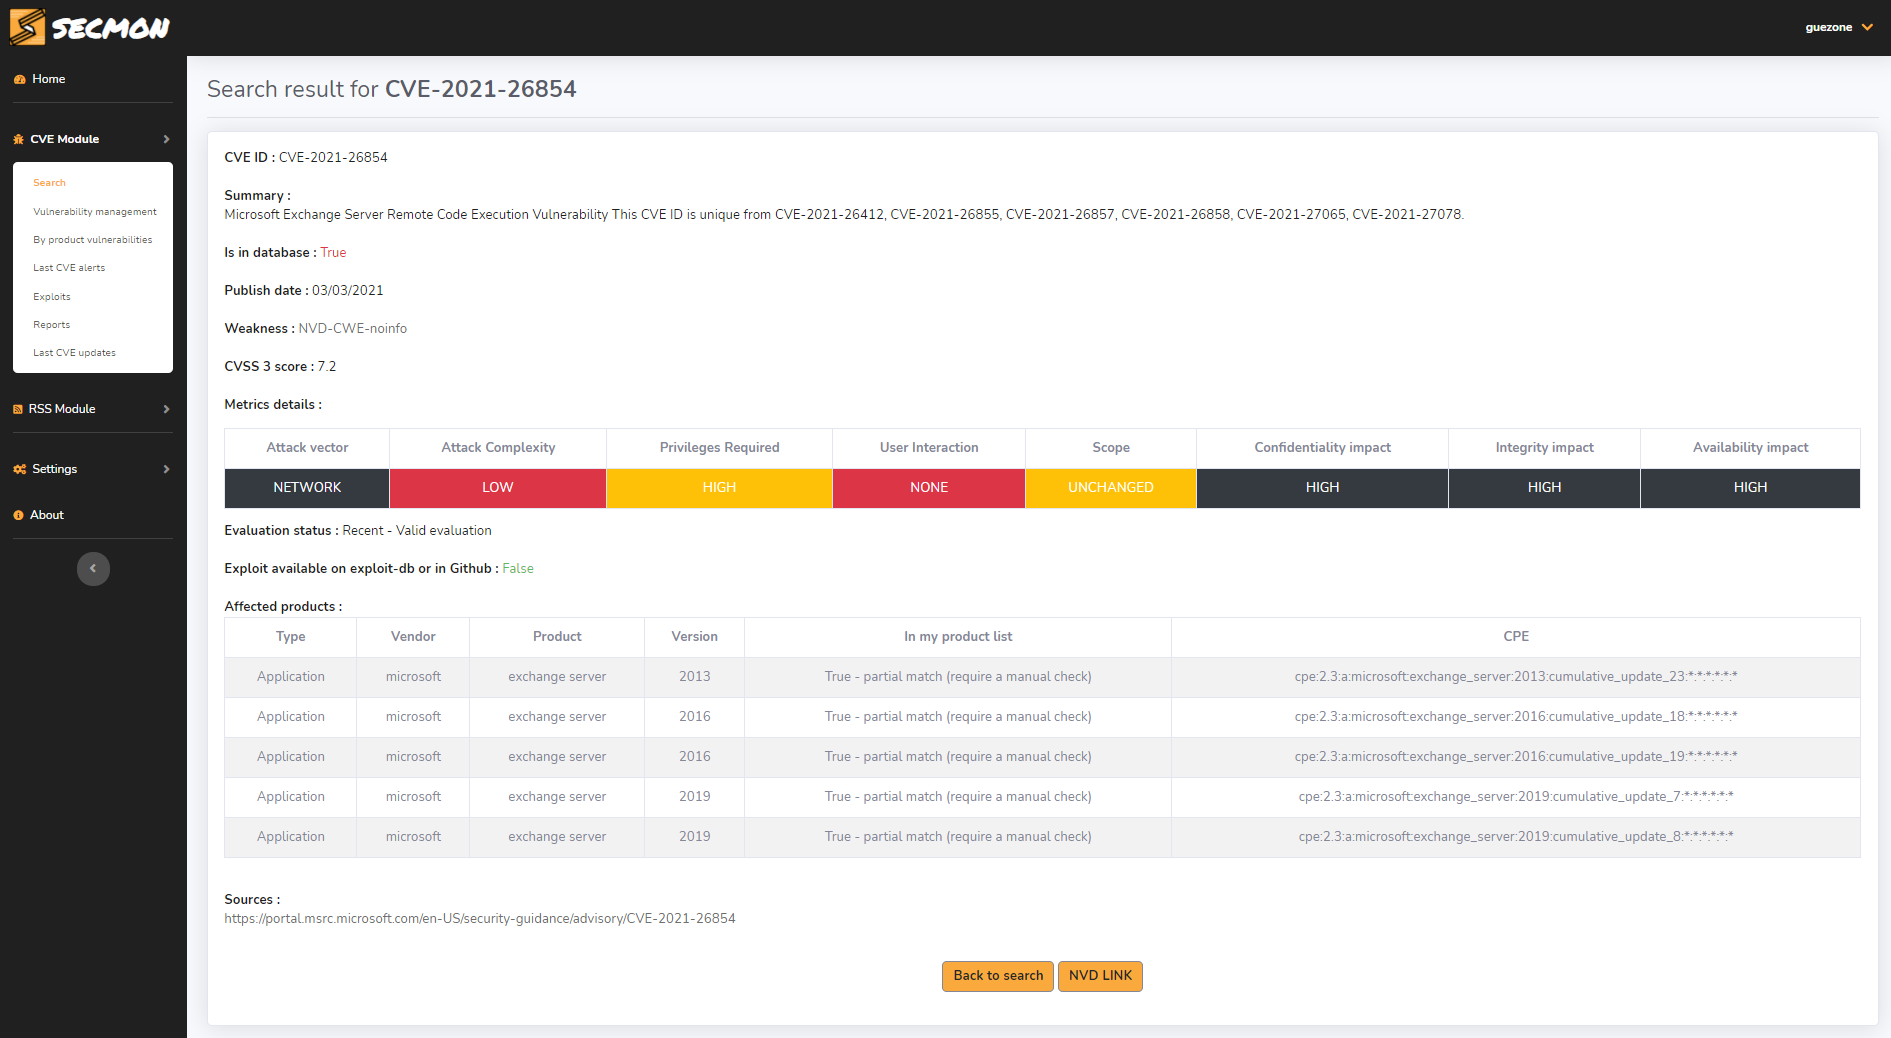 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
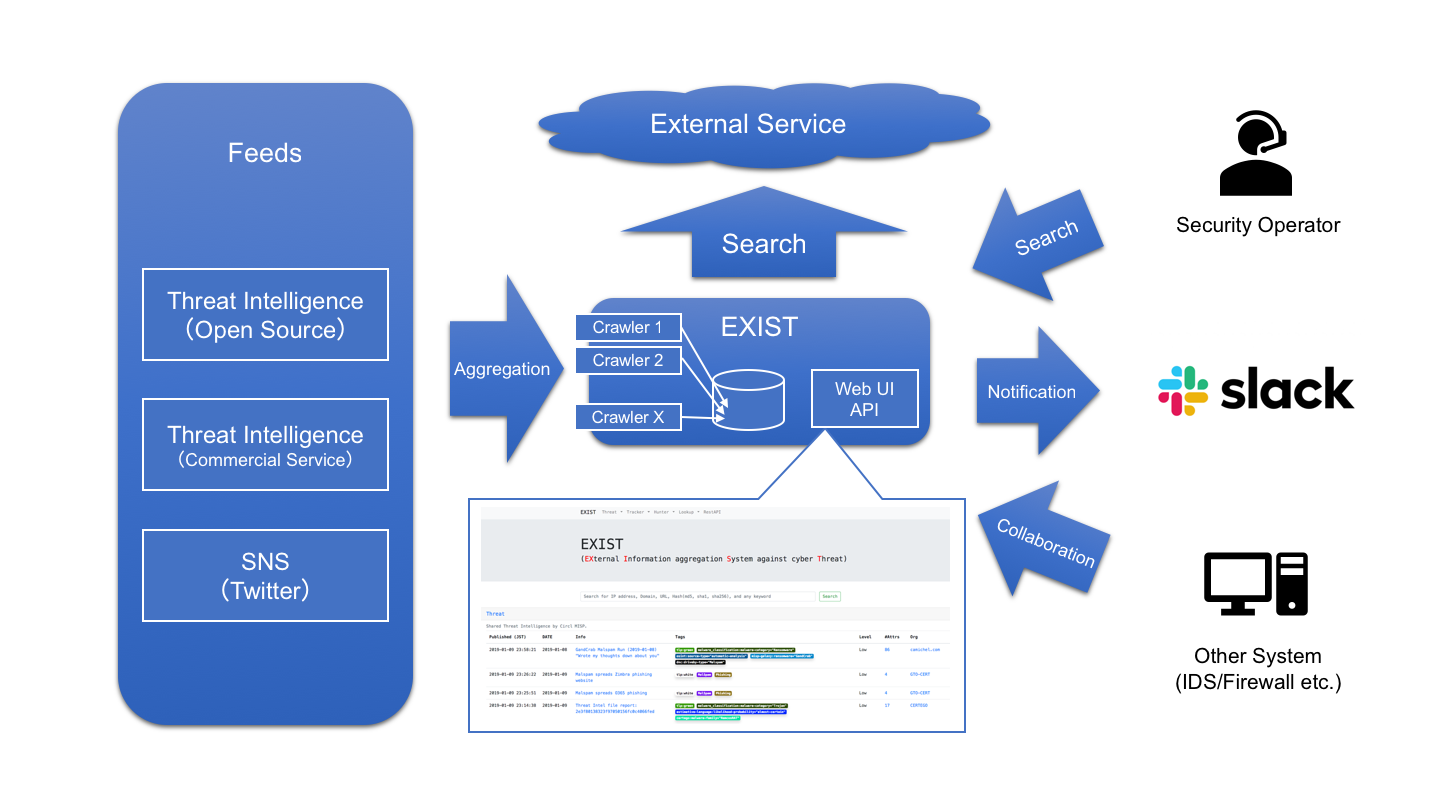 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
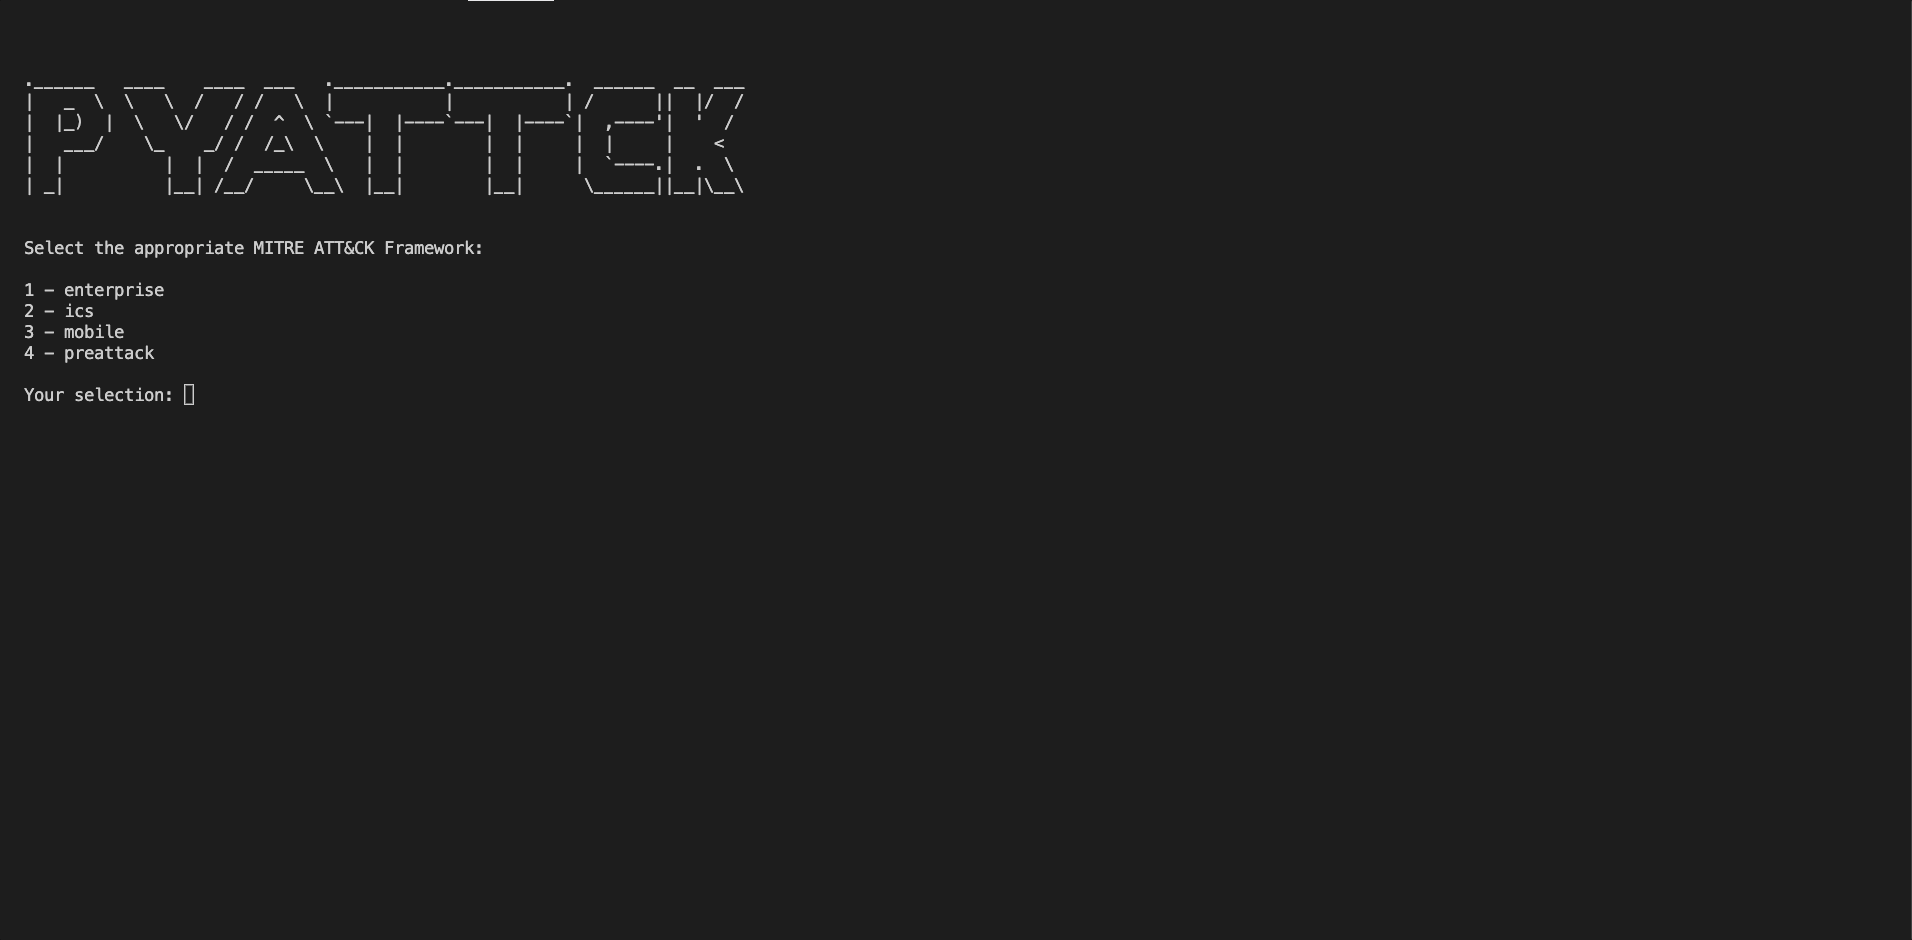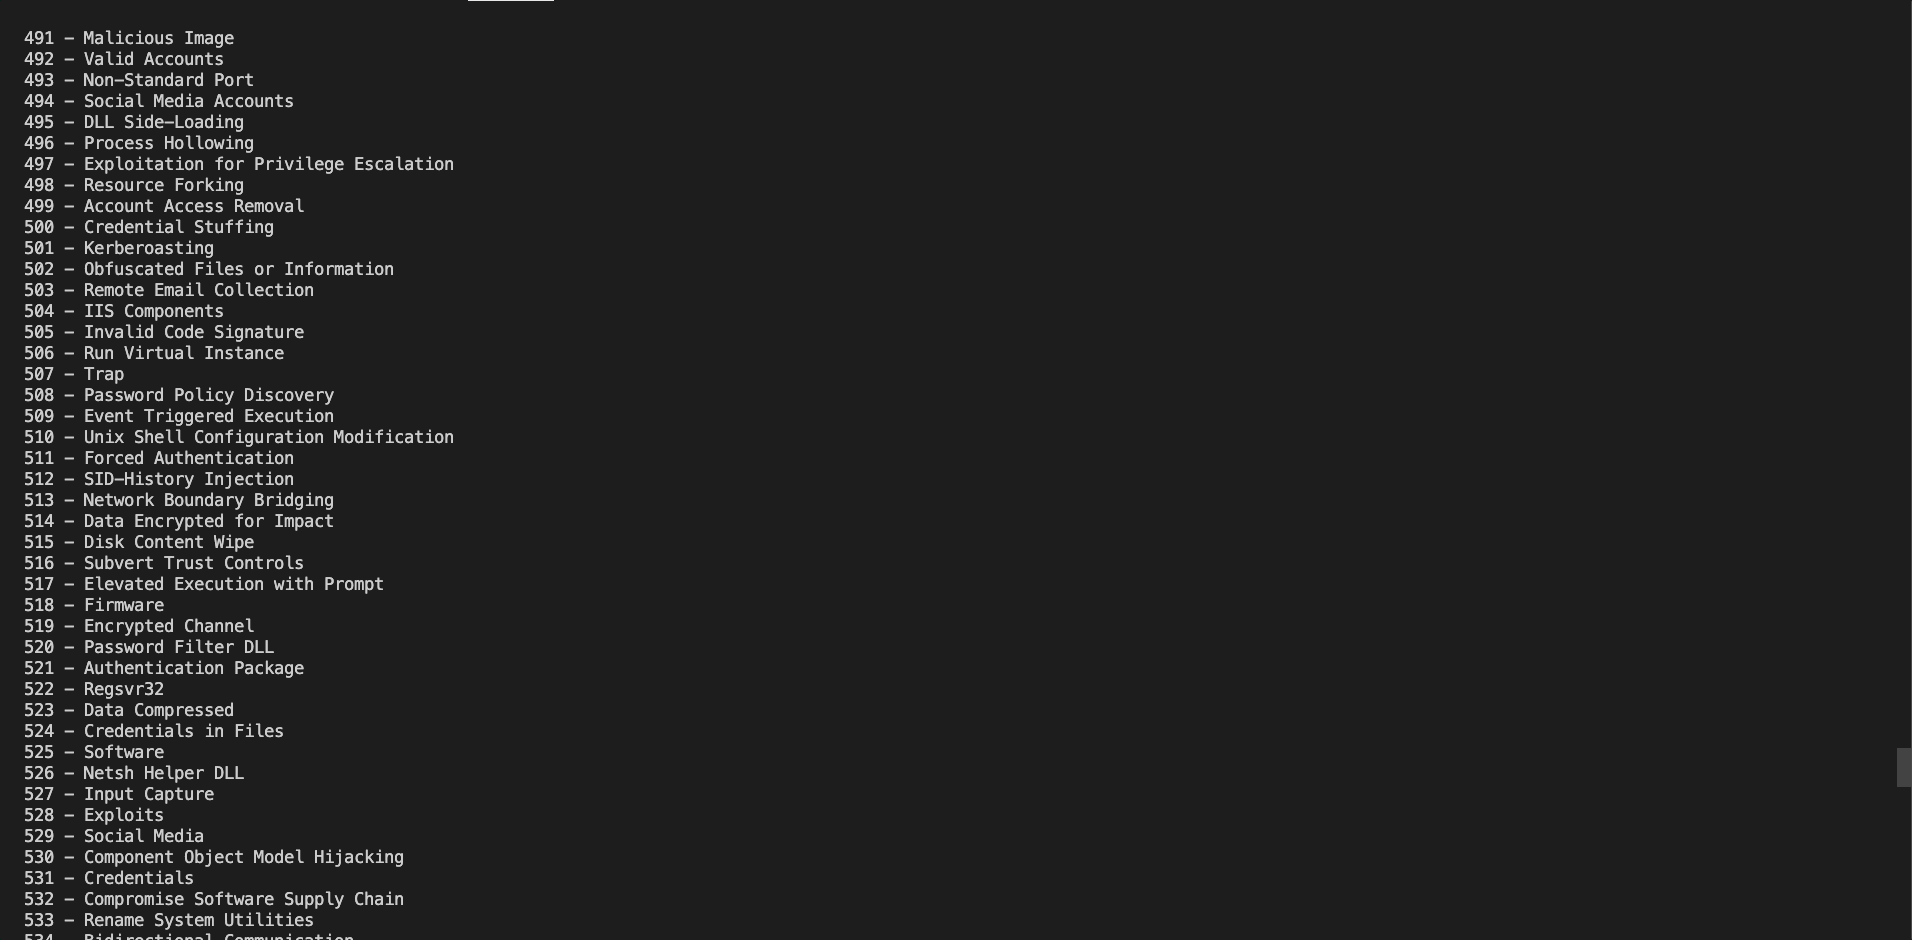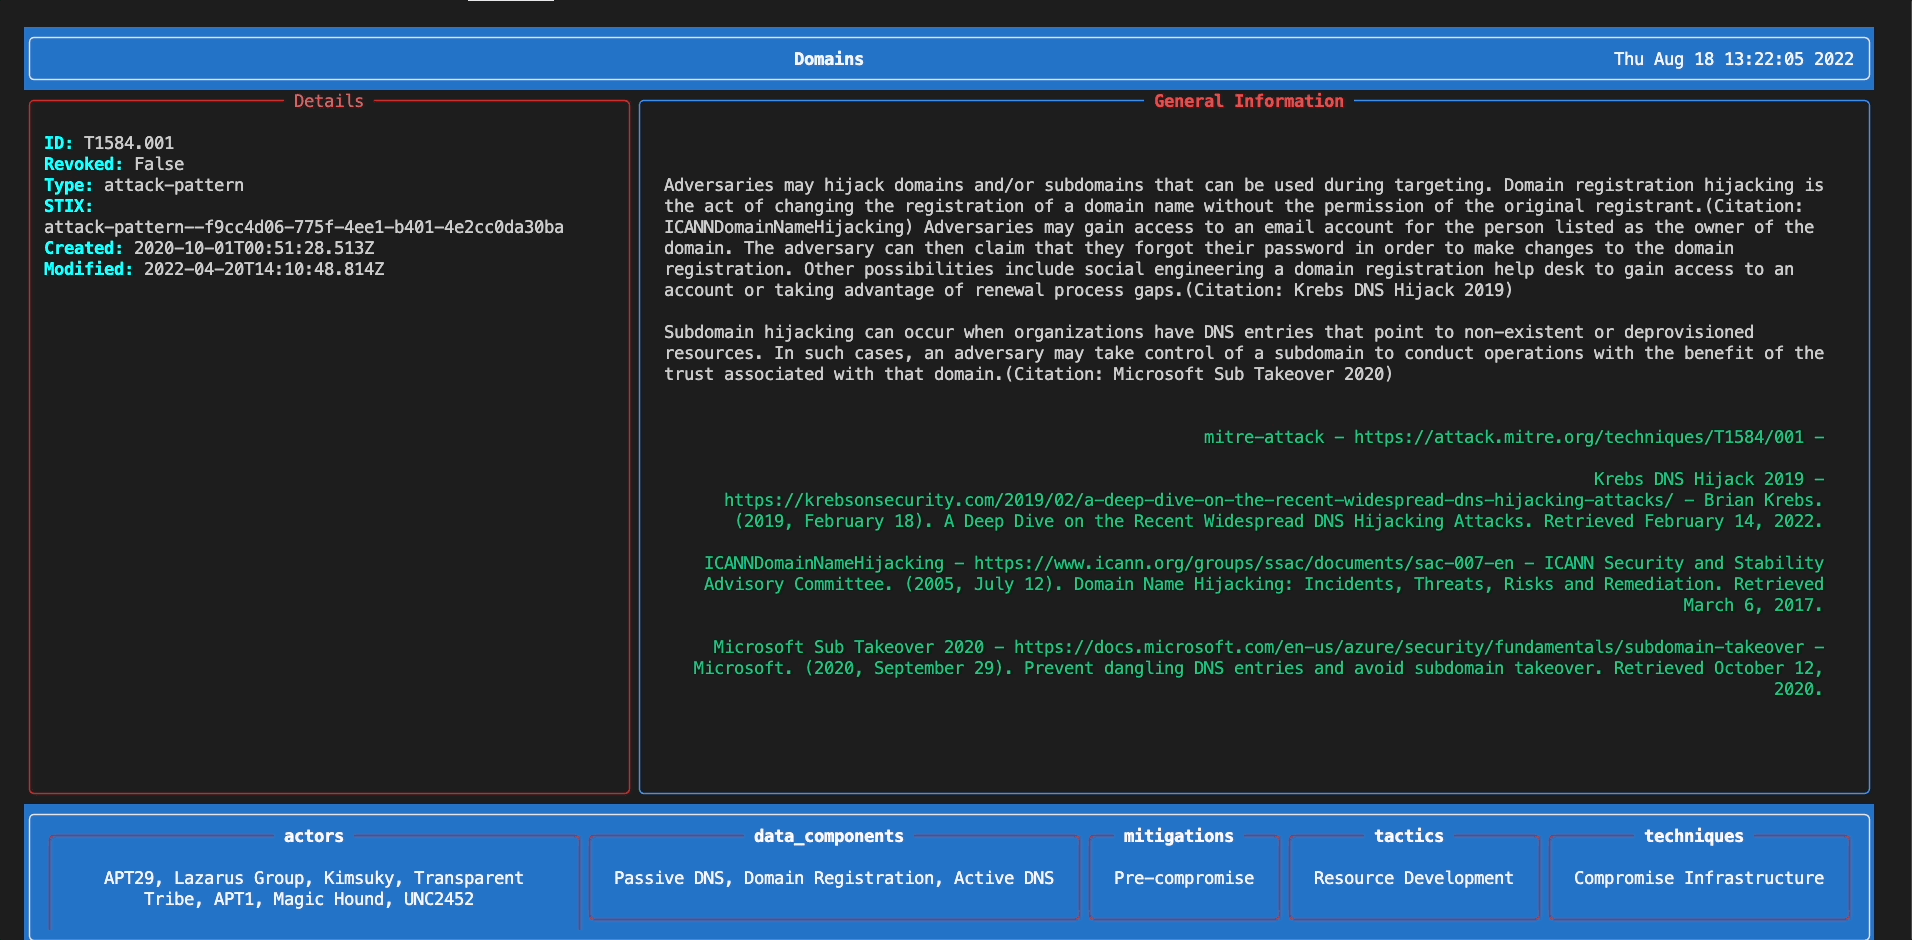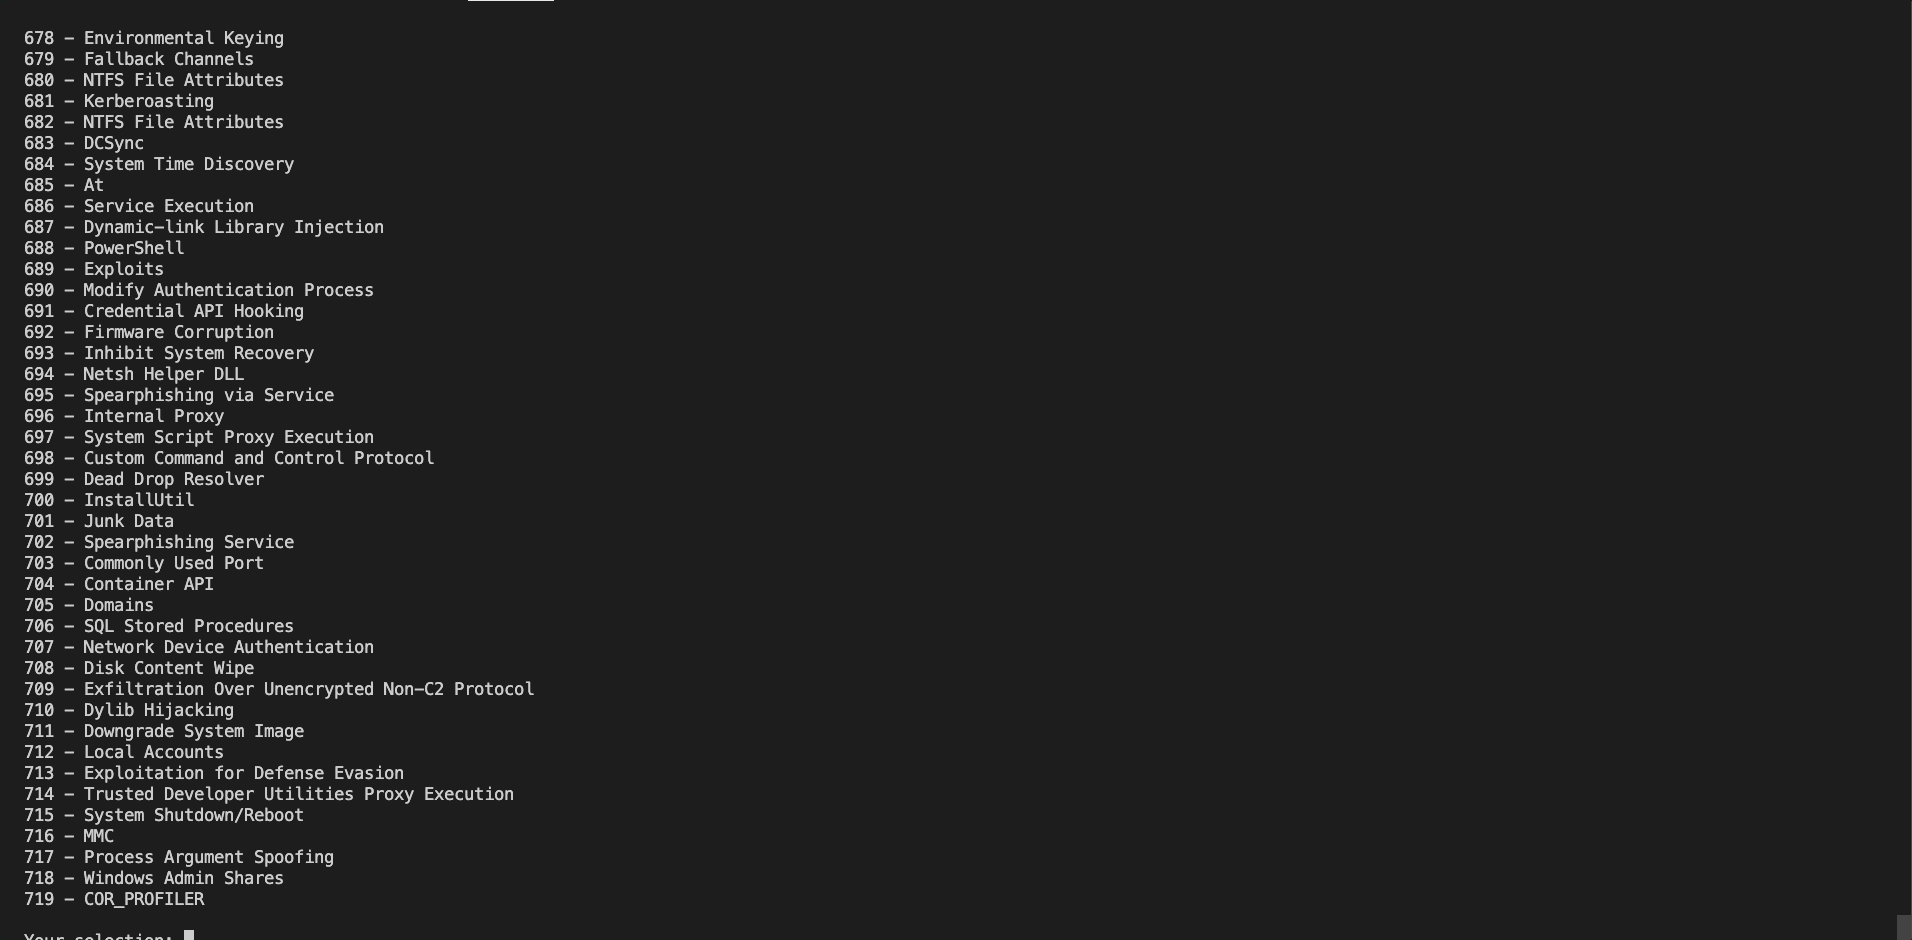 swimlane/pyattck
A Python package to interact with the Mitre ATT&CK Framework
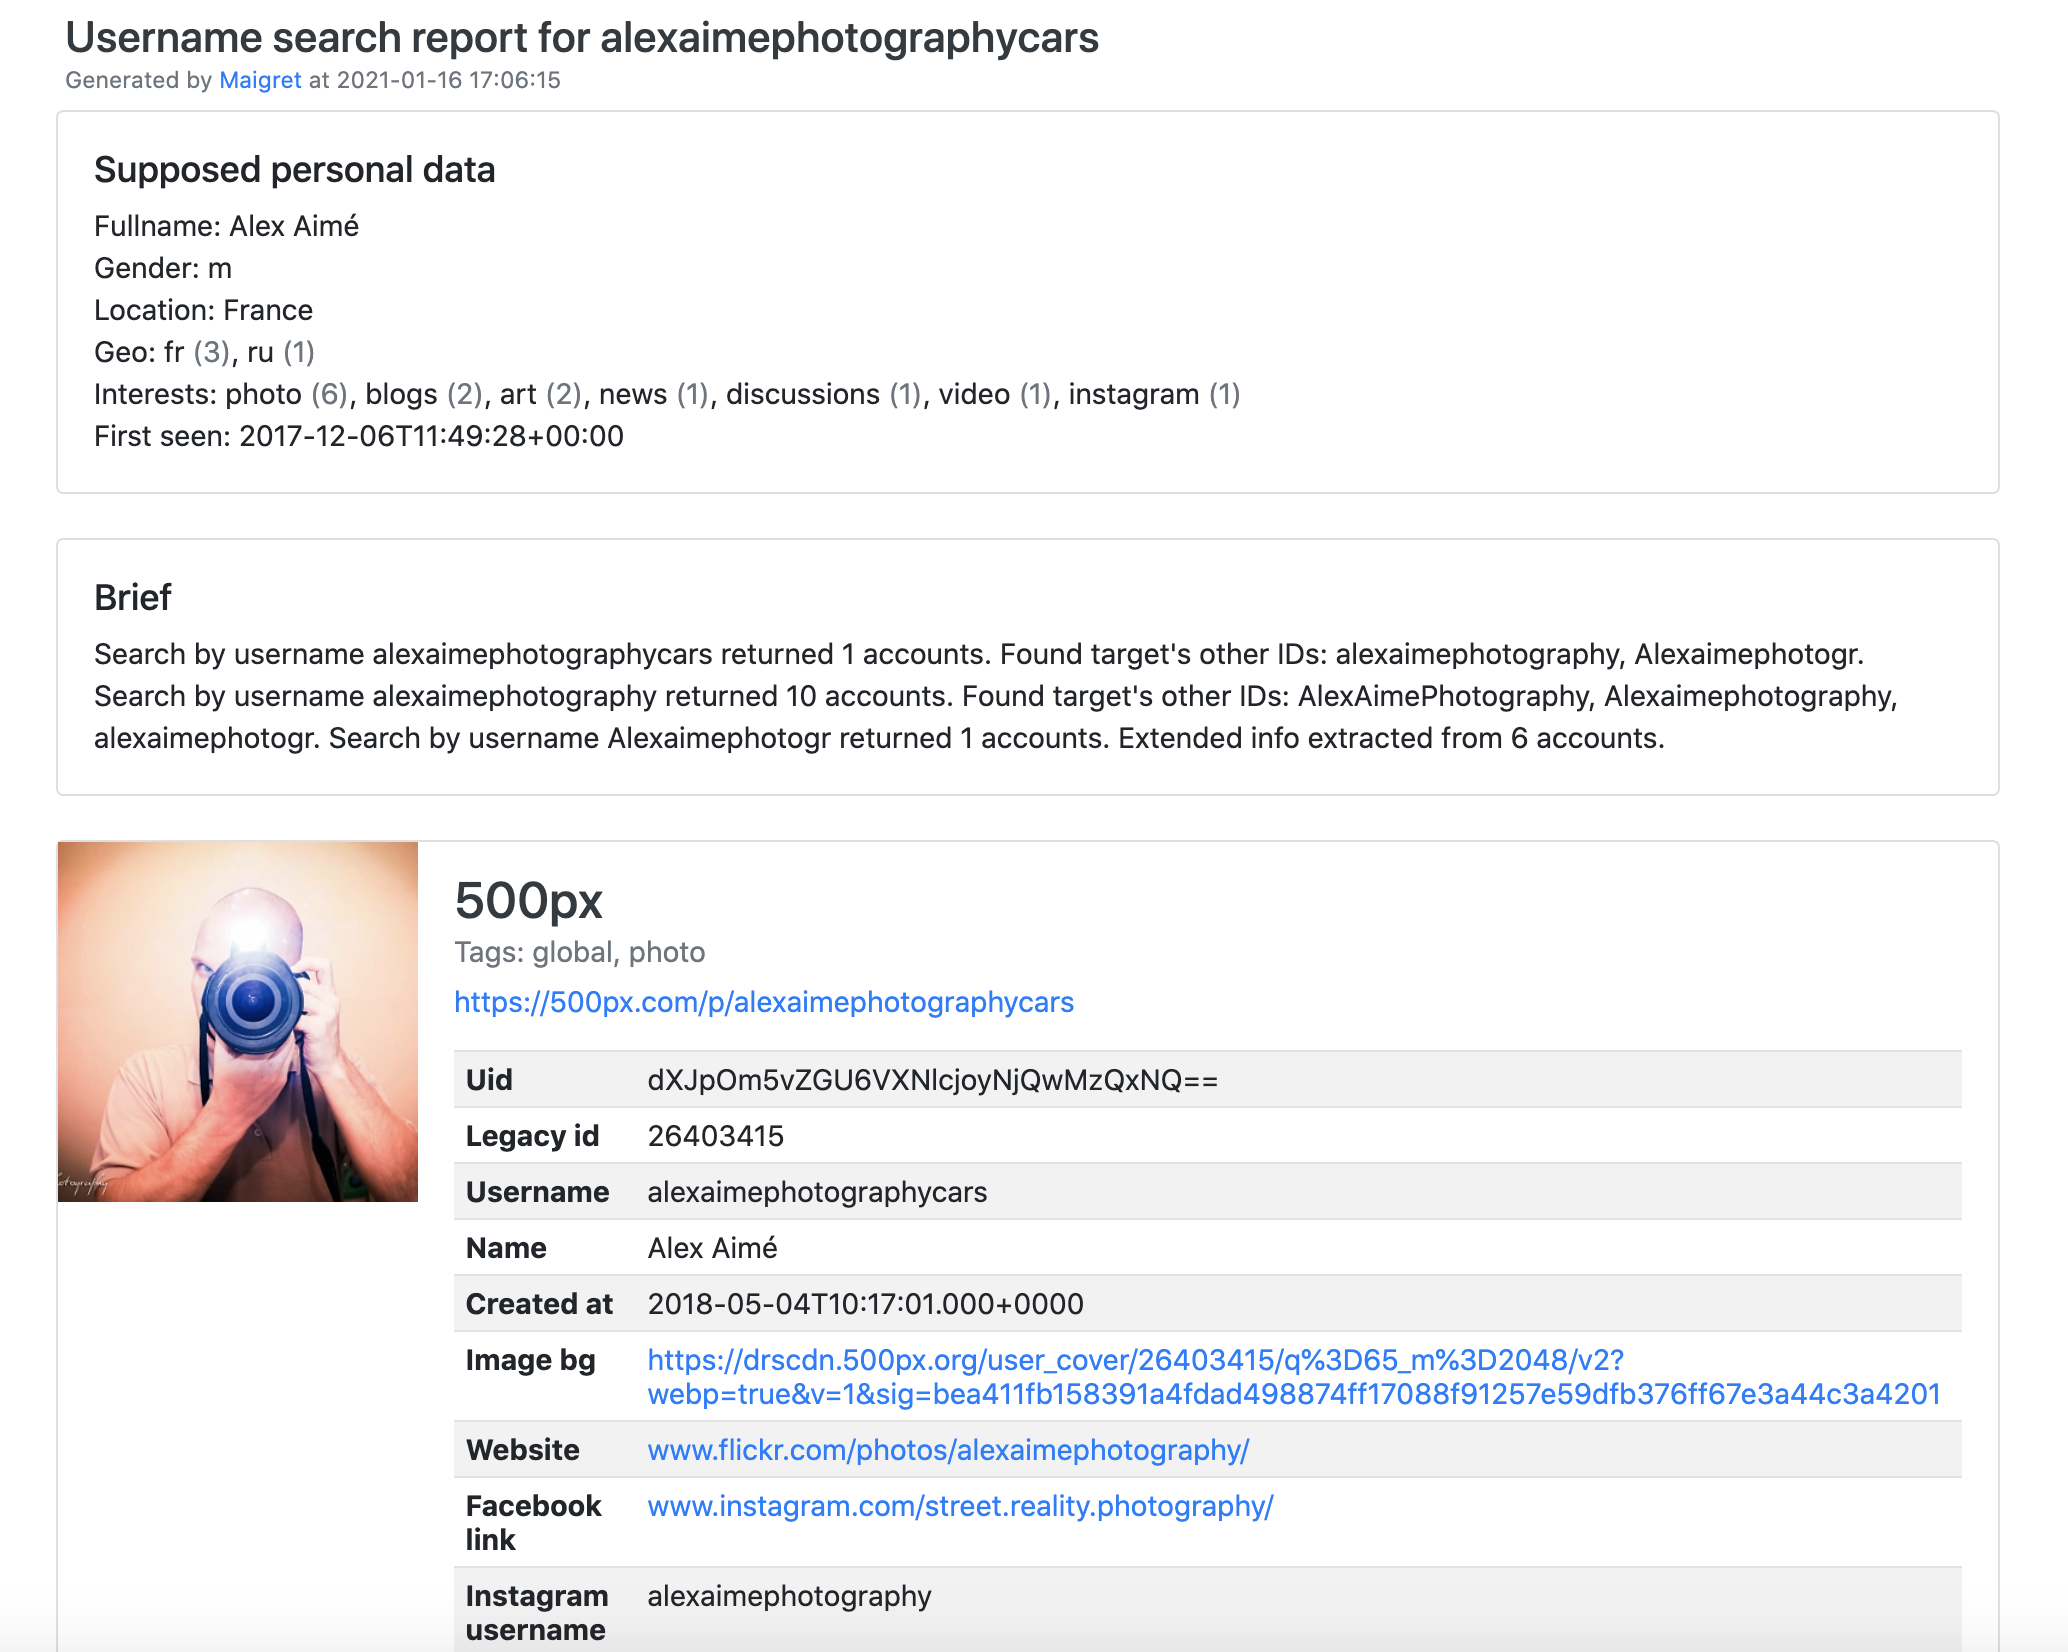 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites