
OSIPs
 ciprianster/osips
A Python script that gathers all valid IP addresses from all text files from a directory, and checks them against Whois database, TOR relays and…
information-gatheringnetwork-securityosint+1
29
ciprianster/osipsA Python script that gathers all valid IP addresses from all text files from a directory, and checks them against Whois database, TOR relays and…
 mhaggis/package-inferno
A Public Package Scanner for The Community
 corelight/extendintel
This package extends the Intel package to log more fields
 pascalasch/cve-2023-38831-kql
KQL Hunting for WinRAR CVE-2023-38831
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
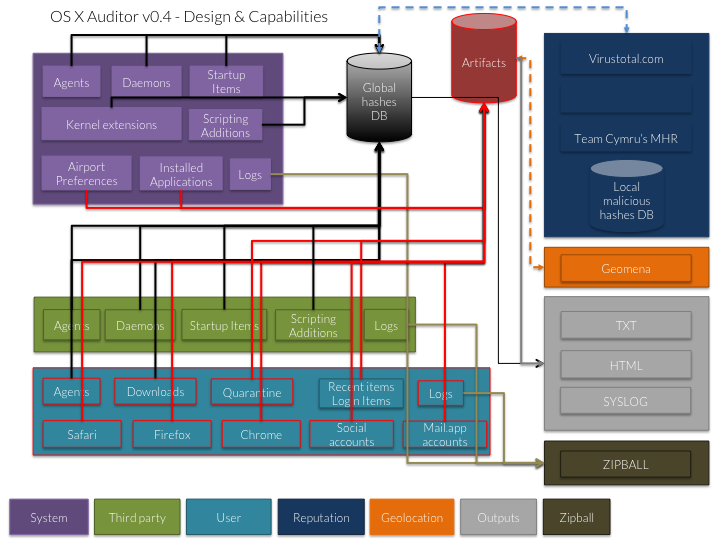 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
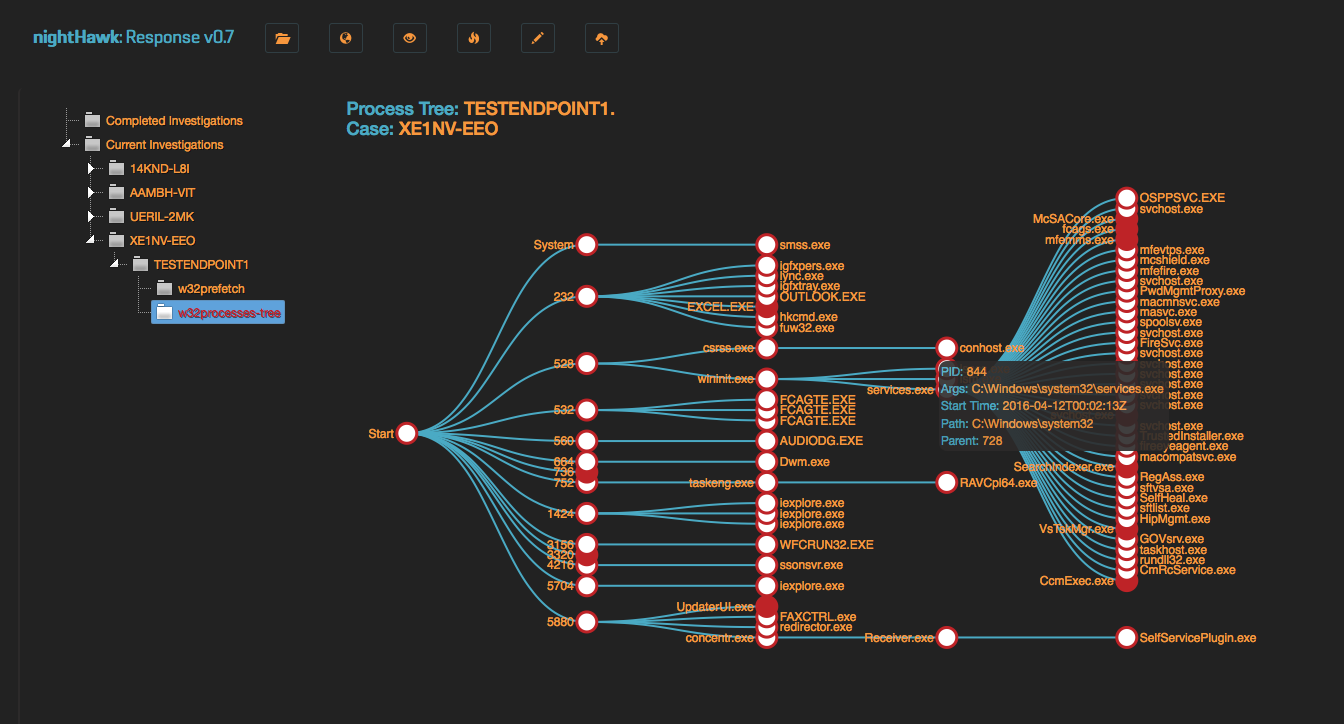 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
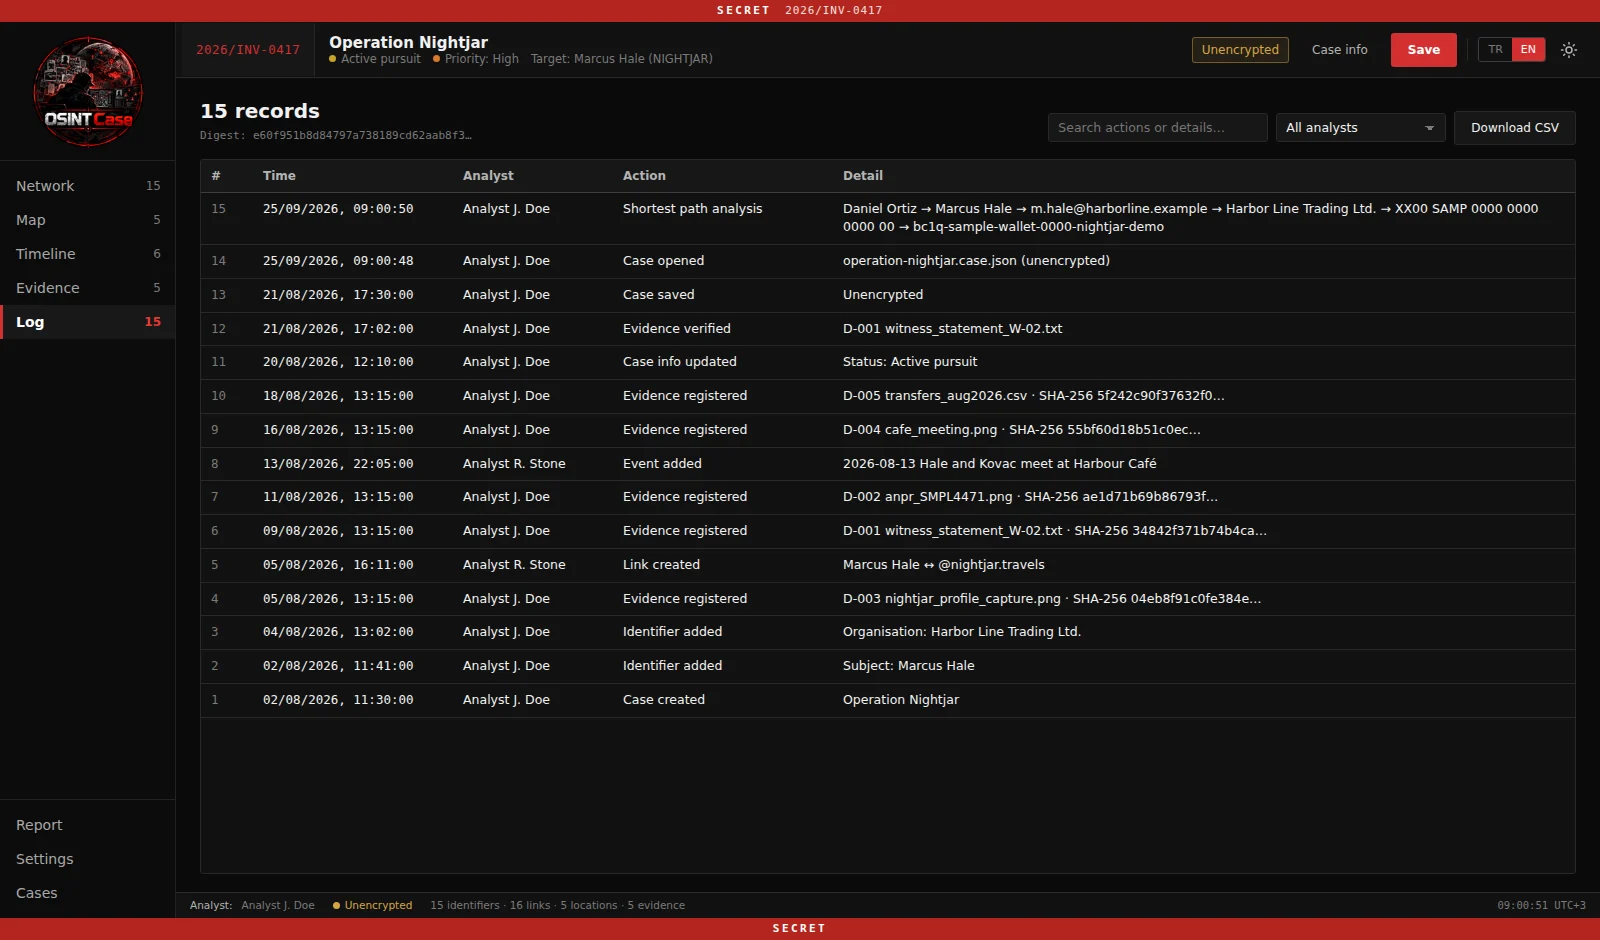 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.