
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
ThreatScraper preview

ThreatScraper

GitHubamorath/threatscraper

Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
information-gatheringmalware-analysisthreat-intelligence+1
7
3 years ago
openclaw-defender preview

openclaw-defender

GitHubnightfullstar/openclaw-defender

Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
ai-securitycode-analysiscurated-resources+8
37 months ago
Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation preview

Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation

GitHubzedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

digital-forensicseducationincident-response+7
11 month ago
ai-ide-config-guard preview

ai-ide-config-guard

GitHubtrerb/ai-ide-config-guard

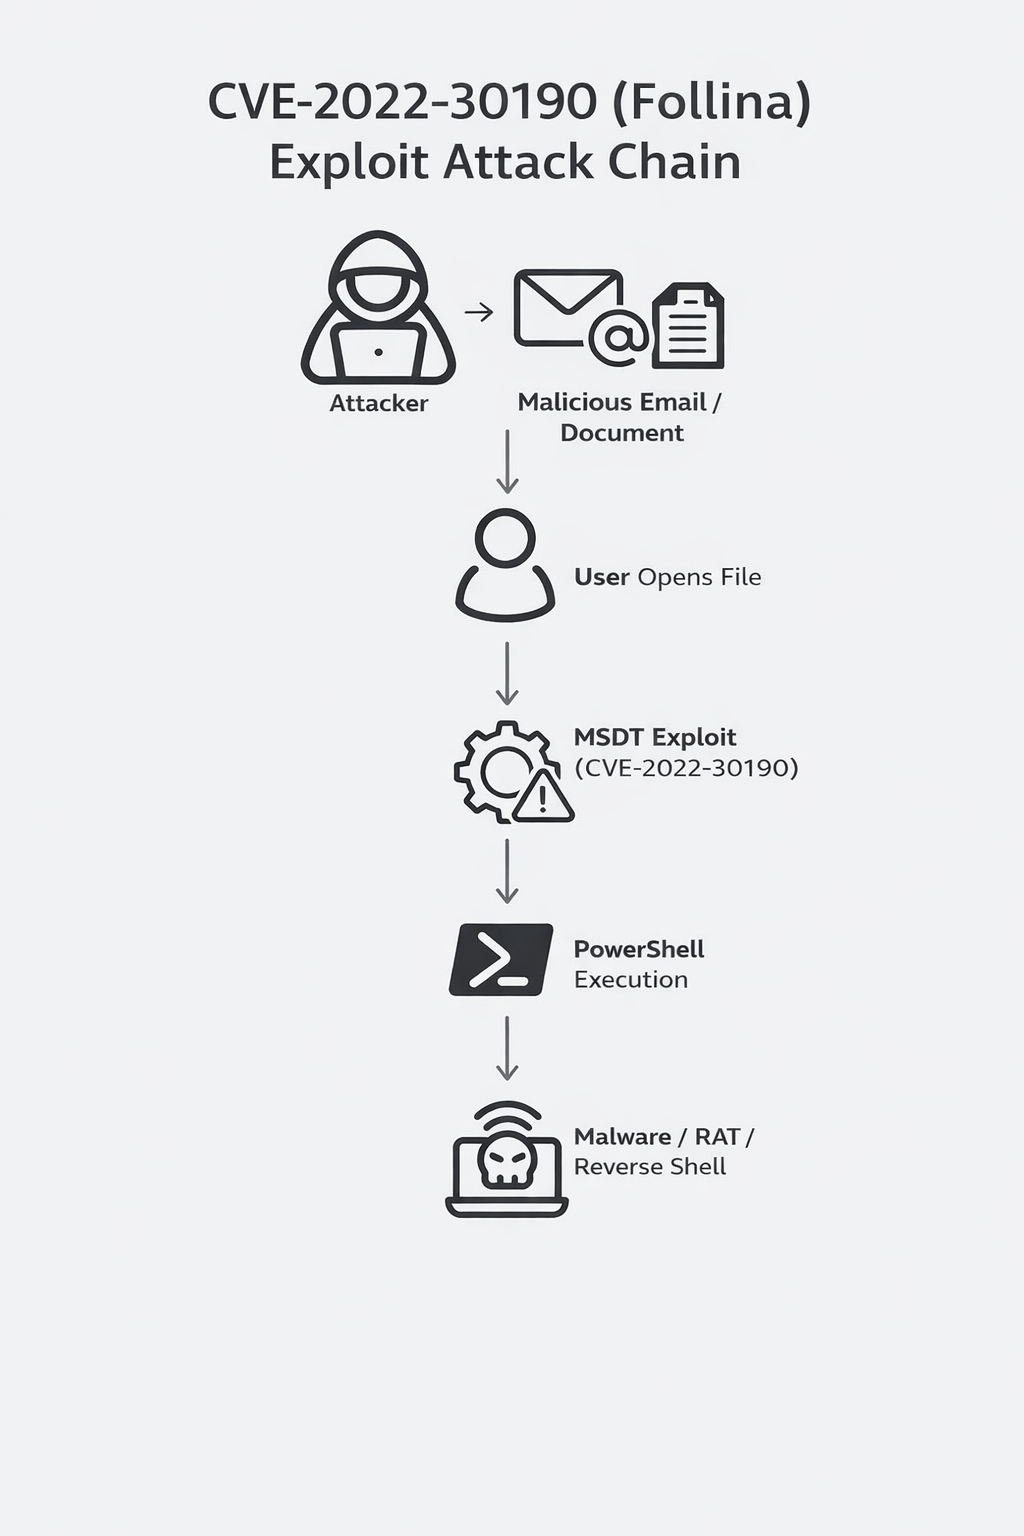
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
code-analysiseducationmisconfiguration+4
5 months ago
Malware-Analysis-Follina-CVE-2022-30190 preview

Malware-Analysis-Follina-CVE-2022-30190

GitHubnimesh895/malware-analysis-follina-cve-2022-30190

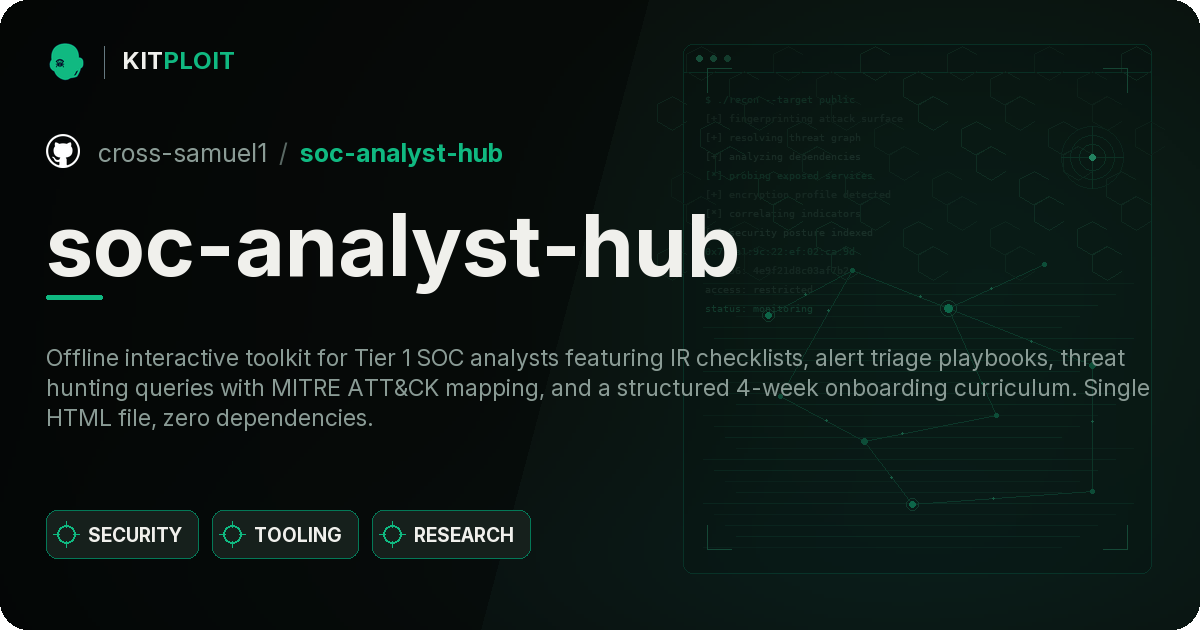
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
educationforensicsmalware-analysis+3
8 months ago
soc-analyst-hub preview

soc-analyst-hub

GitHubcross-samuel1/soc-analyst-hub

Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…

curated-resourceseducationincident-response+6
6 months ago
CVE-2021-1675_CarbonBlack_HuntingQuery preview

CVE-2021-1675_CarbonBlack_HuntingQuery

GitHubmrezqi/cve-2021-1675_carbonblack_huntingquery

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
defensive-toolsincident-responseioc-management+3
5 years ago
sysmon-config preview

sysmon-config

GitHubswiftonsecurity/sysmon-config

Commented Sysmon configuration template for high-quality Windows event tracing, threat hunting, and incident response. Designed as a tutorial for…
configuration-auditingeducationincident-response+1
5.7k4 years ago
machinae preview

machinae

GitHubhurricanelabs/machinae

Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…
information-gatheringosintthreat-feeds-aggregators+1
5363 months ago
hubble preview

hubble

GitHubhubblestack/hubble

Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…

configuration-auditingdevsecopsincident-response+2
3863 years ago
Anxun-isoon preview

Anxun-isoon

GitHubsoufianetahiri/anxun-isoon

I-SOON/Anxun leak related stuff
curated-resourcesosintthreat-intelligence
3412 years ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
defensive-toolsdigital-forensicsincident-response+2
3033 years ago
fileintel preview

fileintel

GitHubkeithjjones/fileintel

A modular Python application to pull intelligence about malicious files
hash-analysisinformation-gatheringmalware-analysis+2
1235 years ago
InfoHound preview

InfoHound

GitHubfundacio-i2cat/infohound

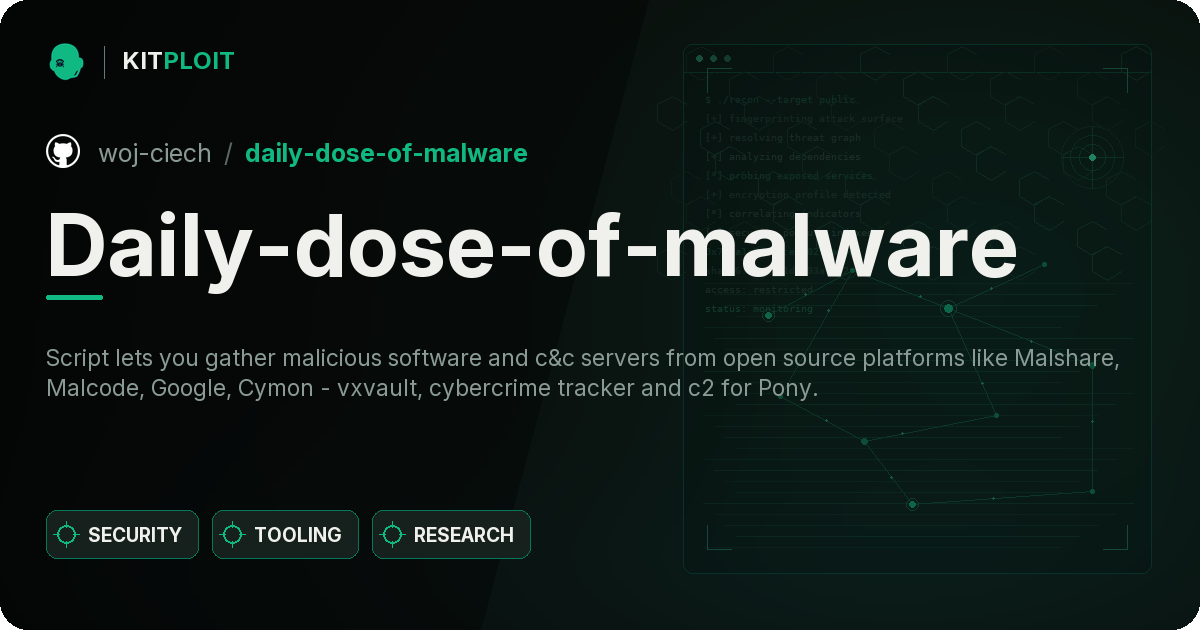
InfoHound is an OSINT to extract a large amount of data given a web domain name.
dns-analysiseducationemail-harvesting+8
1632 years ago
Daily-dose-of-malware preview

Daily-dose-of-malware

GitHubwoj-ciech/daily-dose-of-malware

Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…

command-and-controlinformation-gatheringmalware-analysis+2
408 years ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.

api-security-testingdynamic-analysis-sandboxingfuzzing+6
957 months ago
h0neytr4p preview

h0neytr4p

GitHubpbssubhash/h0neytr4p

Easy to configure Honeypot for Blue Team
defensive-toolsintrusion-detectionnetwork-security+2
441 year ago
sbomlyze preview

sbomlyze

GitHubrezmoss/sbomlyze

Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.

configuration-auditingdevsecopssecret-detection+5
2420 days ago
Previous1234Next