
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
68 results
Python-Honeypot preview

Python-Honeypot

GitHubowasp/python-honeypot

OWASP Honeypot, Automated Deception Framework.
api-securitycontainer-securitydefensive-tools+4
4832 years ago
galah preview

galah

GitHub0x4d31/galah

Galah: An LLM-powered web honeypot.
incident-responseintrusion-detectionthreat-intelligence+1
6741 year ago
IntRec-Pack preview

IntRec-Pack

GitHubnullarray/intrec-pack

Intelligence and Reconnaissance Package/Bundle installer.
information-gatheringosintpenetration-testing+2
2557 years ago
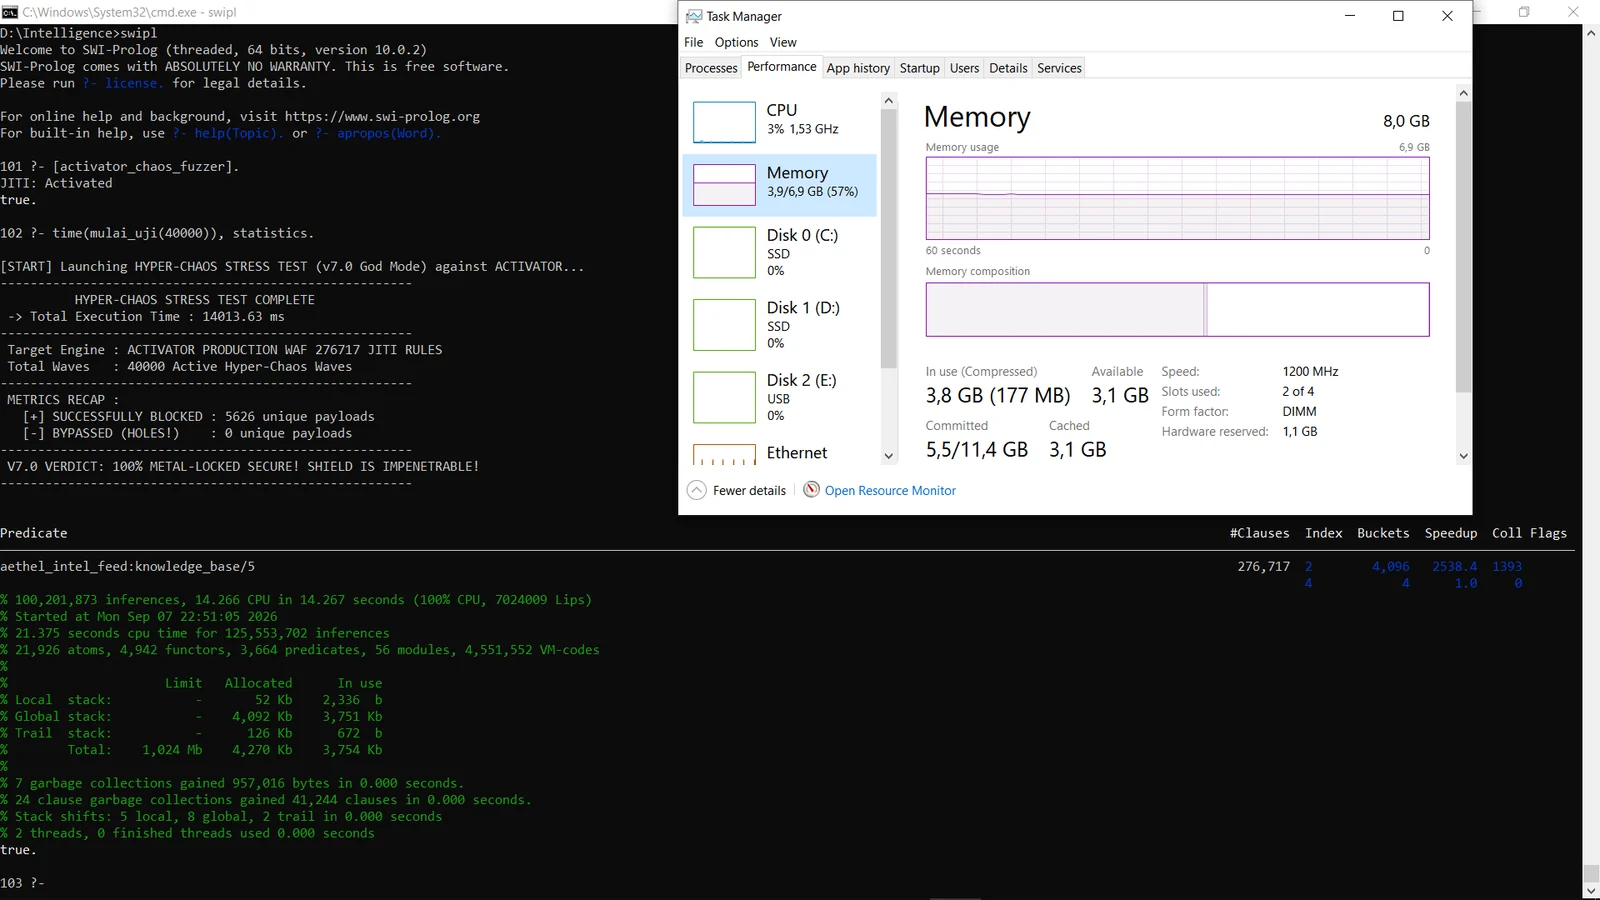
aethel_core preview

aethel_core

GitHublokinpendawa/aethel_core

Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…

ai-securityanomaly-detectionthreat-intelligence+3
81 month ago
SecureCivic preview

SecureCivic

GitLabroxanne_ardary/securecivic

SecureCivic is a citizen-built, open source identity verification platform designed for SSA adoption. It replaces private data brokers with a secure,…
api-securityauthentication-authorizationcloud-security+7
3 months ago
Watcher preview

Watcher

GitHubthalesgroup-cert/watcher

AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
ai-securitydata-exfiltrationdns-subdomain-enumeration+7
1.4k9 days ago
sysmon-config preview

sysmon-config

GitHubswiftonsecurity/sysmon-config

Commented Sysmon configuration template for high-quality Windows event tracing, threat hunting, and incident response. Designed as a tutorial for…
configuration-auditingeducationincident-response+1
5.7k5 years ago
EVTX-ATTACK-SAMPLES preview

EVTX-ATTACK-SAMPLES

GitHubsbousseaden/evtx-attack-samples

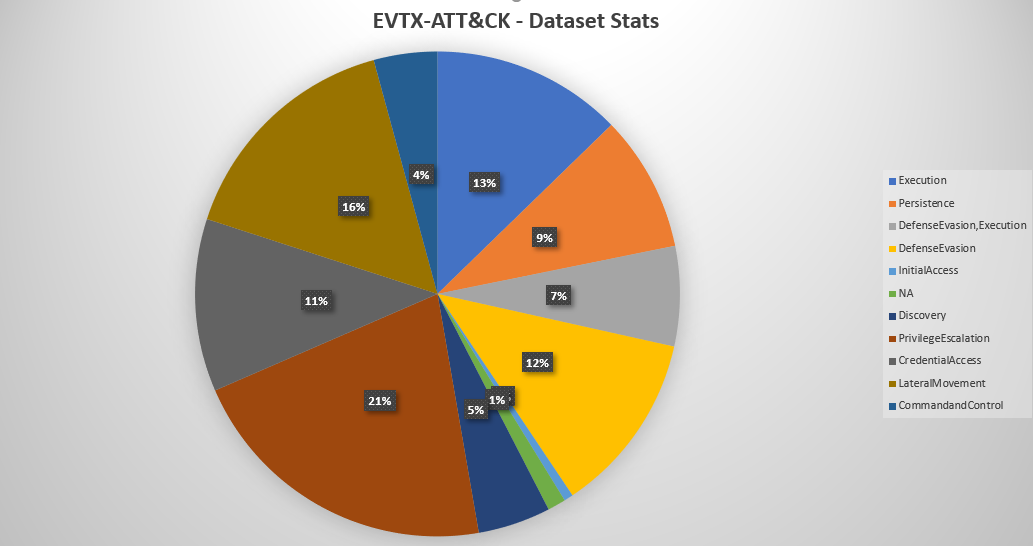
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
curated-resourcesdigital-forensicseducation+2
2.6k3 years ago
adversary_emulation_library preview

adversary_emulation_library

GitHubcenter-for-threat-informed-defense/adversary_emulation_library

An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
curated-resourcesdata-exfiltrationdefensive-tools+5
2.2k1 year ago
Malware-Bible preview

Malware-Bible

GitHubperkins-fund/malware-bible

Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…

digital-forensicseducationincident-response+4
6262 months ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
yara-rules-vt preview

yara-rules-vt

GitHubinquest/yara-rules-vt

Collection of YARA rules designed for usage through VirusTotal.com.
curated-resourcesdefensive-toolsmalware-analysis+2
923 years ago
Crawlector preview

Crawlector

GitHubmfmokbel/crawlector

Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
crawlerinformation-gatheringmalware-analysis+5
12310 months ago
my-little-honeypot preview

my-little-honeypot

GitHubpandipanda69/my-little-honeypot

Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
command-and-controliot-securitymalware-analysis+2
179 years ago
lazarus-sigma-rules preview

lazarus-sigma-rules

GitHubwithsecurelabs/lazarus-sigma-rules

Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
defensive-toolsincident-responseintrusion-detection+2
206 years ago
aimp preview

aimp

GitHubfabriziosalmi/aimp

A serverless networking protocol designed for resilient state synchronization between autonomous agents in fragmented, low-bandwidth networks
cryptographyeducationembedded-systems-security+6
525 days ago
Fake_CVE-2020-1350 preview

Fake_CVE-2020-1350

GitHubzoomerxsec/fake_cve-2020-1350

Fake exploit tool, designed to rickroll users attempting to actually exploit.
educationinformation-gatheringosint+1
76 years ago
Ivanti-Connect-Secure-Logs-Parser preview

Ivanti-Connect-Secure-Logs-Parser

GitHubhexastrike/ivanti-connect-secure-logs-parser

A Python script for examining Ivanti Secure Connect (ICS) event logs, designed to support investigations into vulnerabilities CVE-2025-0282,…

digital-forensicsforensicsincident-response+3
61 year ago
Previous1234Next