

RedHunt-OS
 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
educationexploit-frameworksforensics+7
1.3k
redhuntlabs/redhunt-osVirtual Machine for Adversary Emulation and Threat Hunting
 specterops/nemesis
Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
 fr0gger/awesome_malware_techniques
This is a repository of resource about Malware techniques
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 travisbgreen/hunting-rules
Suricata rules for network anomaly detection

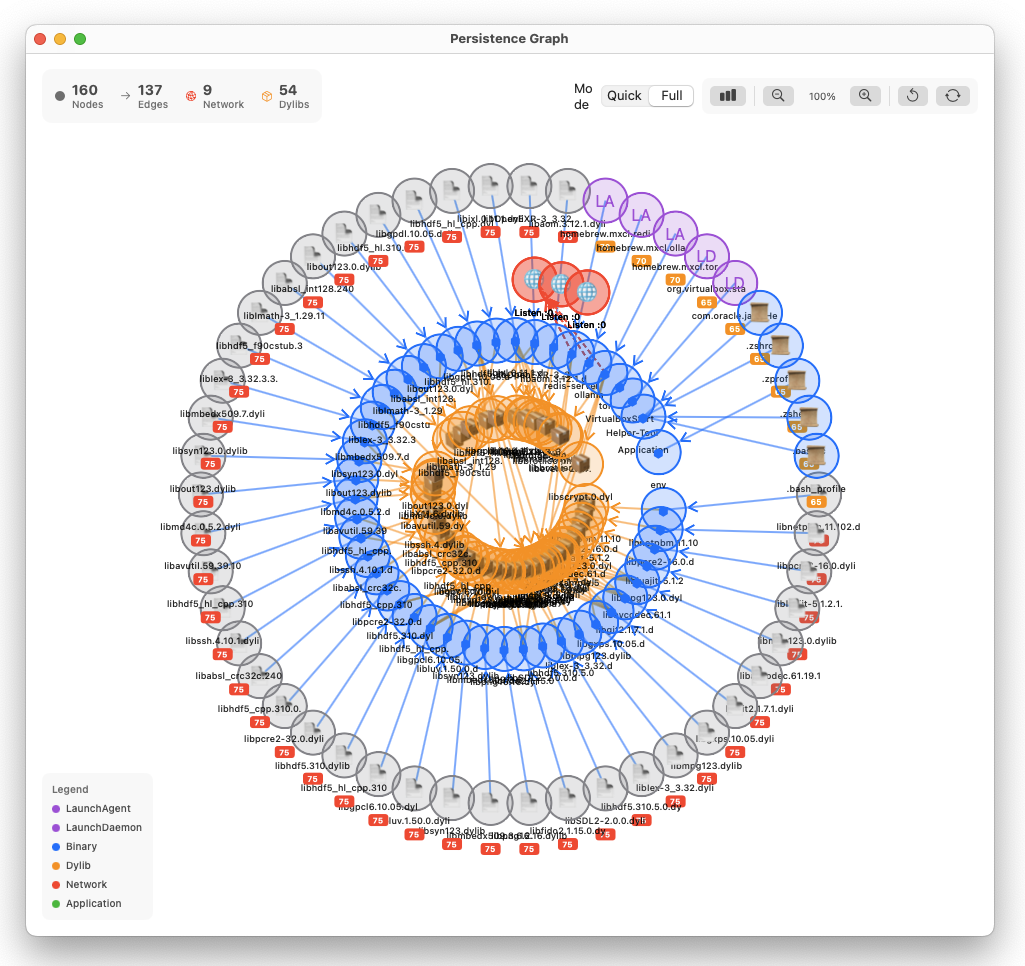 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
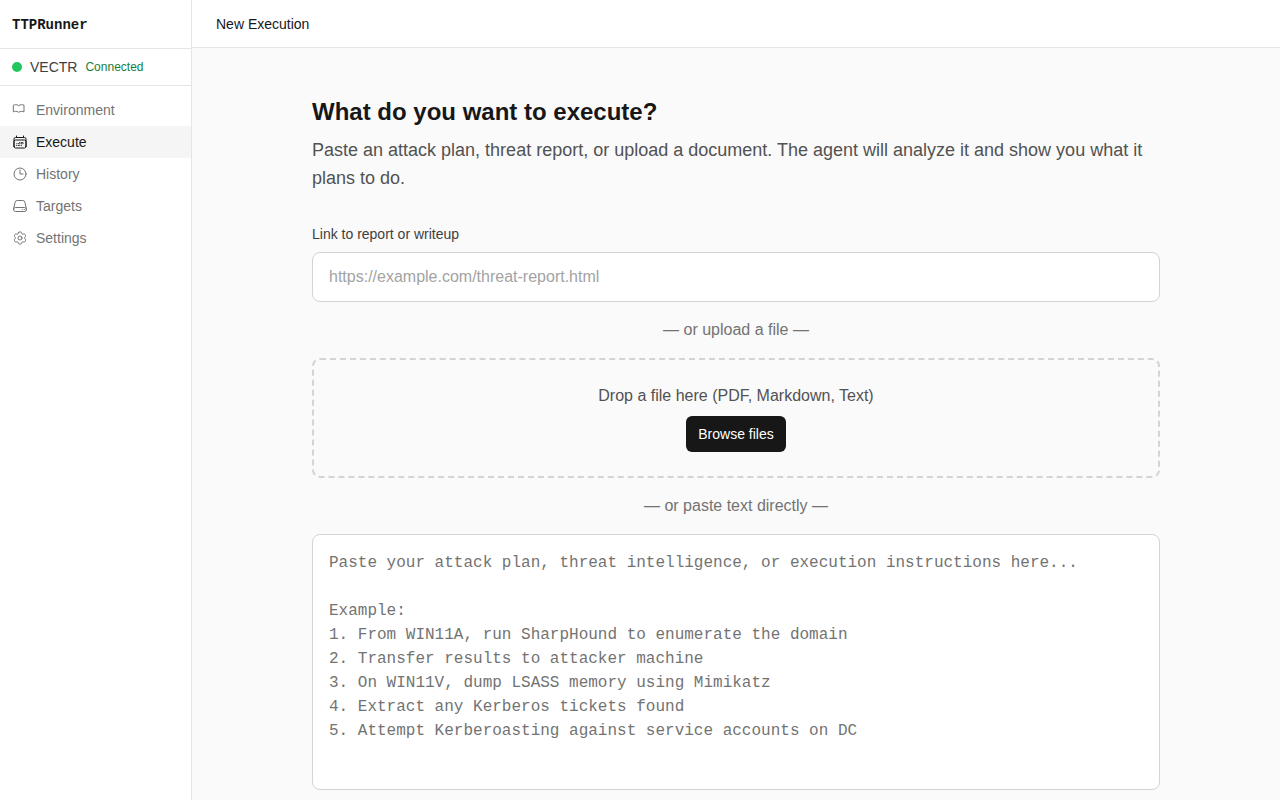
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
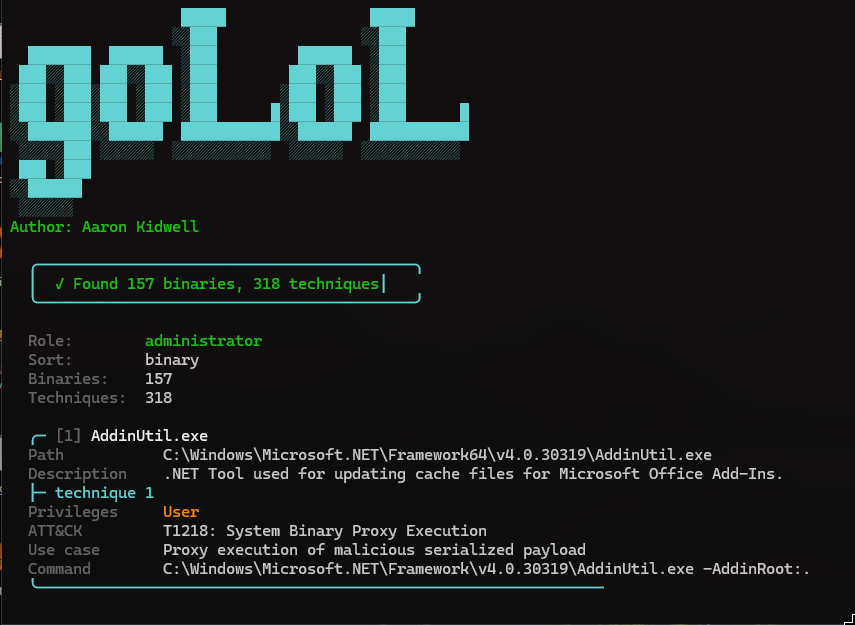 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…

 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
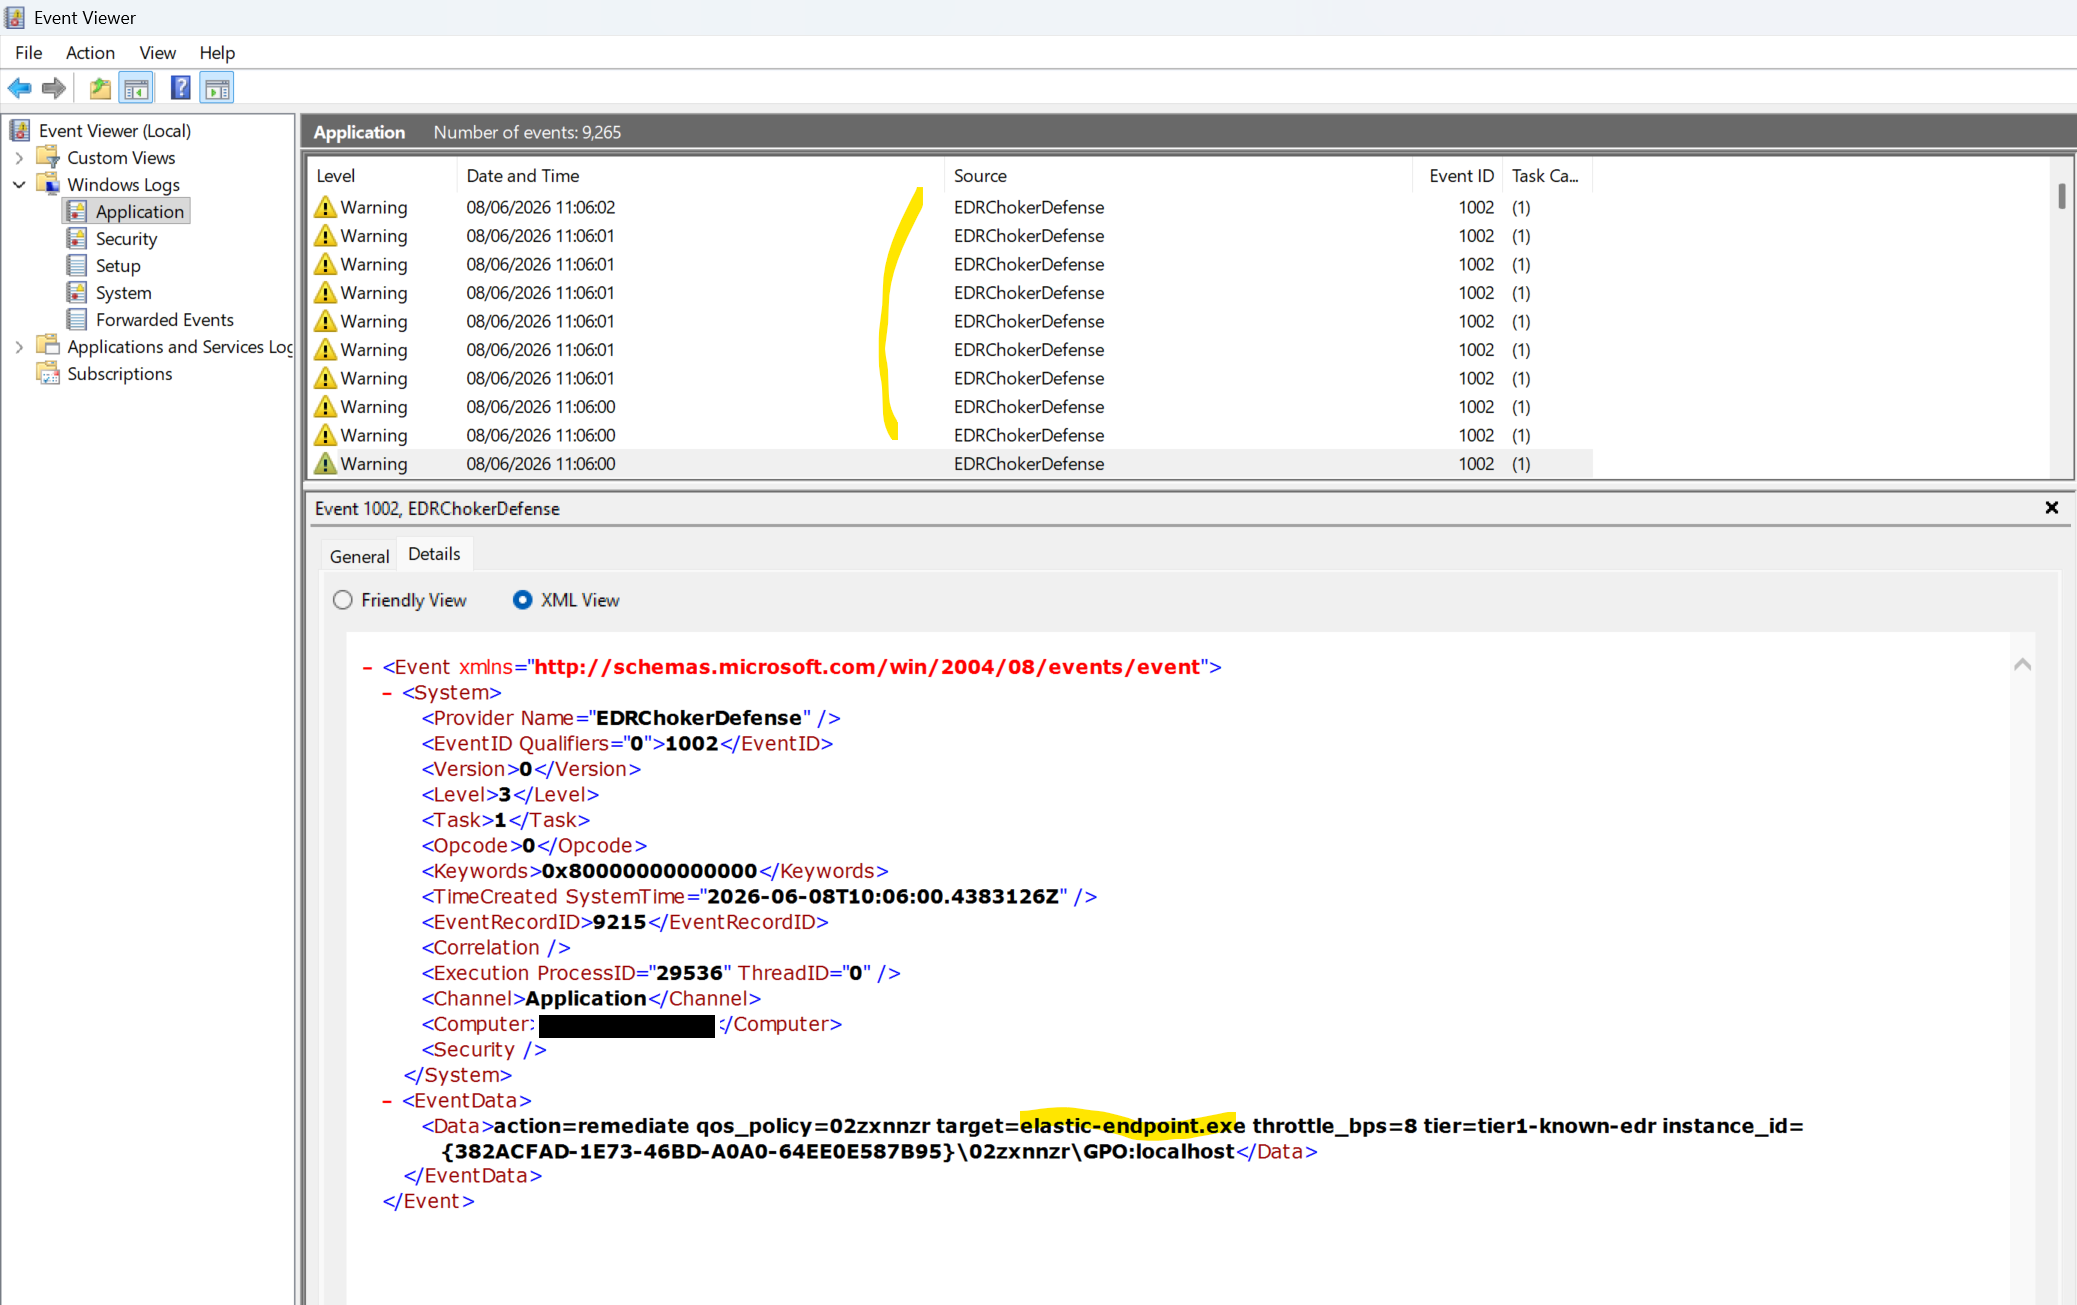 sbousseaden/edrunchoker
EDRUnChoker - fileless WMI defense that removes EDRChoker QoS throttling policies
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.