
CVE-2026-53266
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
defensive-toolsioc-managementthreat-intelligence+1
suominen/cve-2026-53266Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
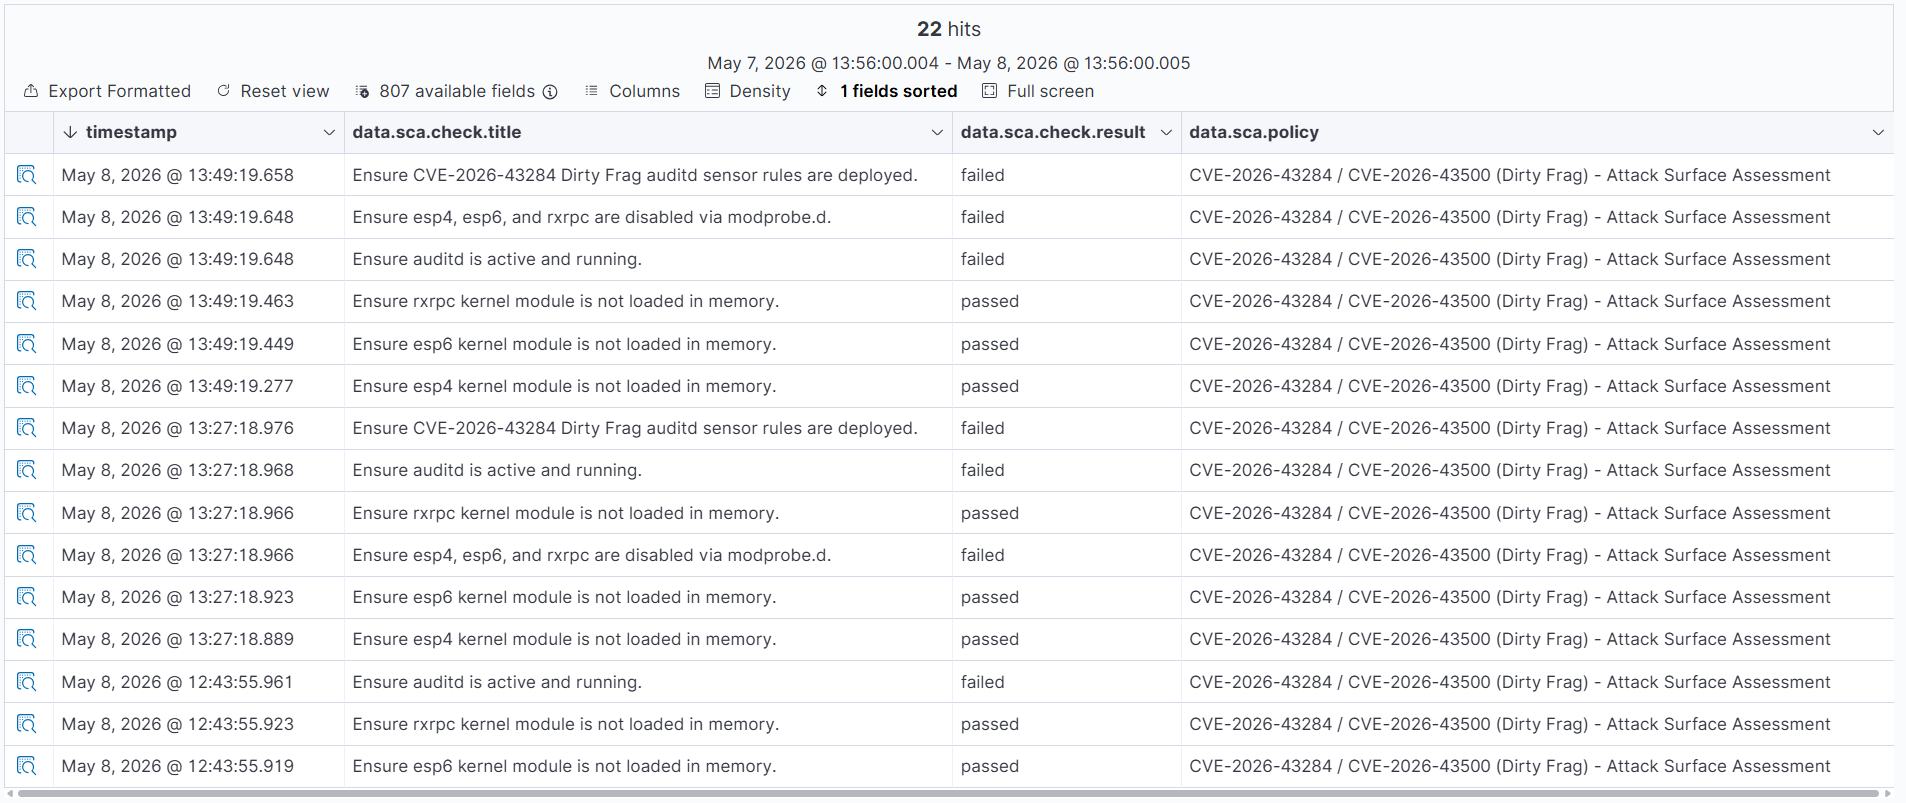 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…
 horizon-software-development/cve-2024-3094
Advisory and analysis repository for CVE-2024-3094, detailing a critical backdoor in Linux SSH library with mitigation steps for servers and Android…
 suominen/sctphantom
Tracking SCTPhantom (CVE-2026-64564), the Linux kernel SCTP ASCONF transport use-after-free
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 suominen/ovswrap
Tracking OVSwrap (CVE-2026-64531), the Open vSwitch datapath netlink overflow
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 suominen/januscape
Tracking Januscape (CVE-2026-53359), the KVM/x86 guest-to-host escape
 suominen/itscape
Tracking ITScape (CVE-2026-46316), the KVM/arm64 guest-to-host escape
 suominen/ghostlock
Tracking GhostLock (CVE-2026-43499), the rtmutex/futex stack use-after-free

 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 suominen/pintheft
Tracking PinTheft (CVE-2026-43494, CVE-2026-43502), the RDS zerocopy double-free privilege escalation
 suominen/cifswitch
Tracking CIFSwitch (CVE-2026-46243), the CIFS cifs.spnego key-origin privilege escalation
 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…