

arkime
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
defensive-toolsdigital-forensicsforensics+7
arkime/arkimeArkime is an open source, large scale, full packet capturing, indexing, and database system.
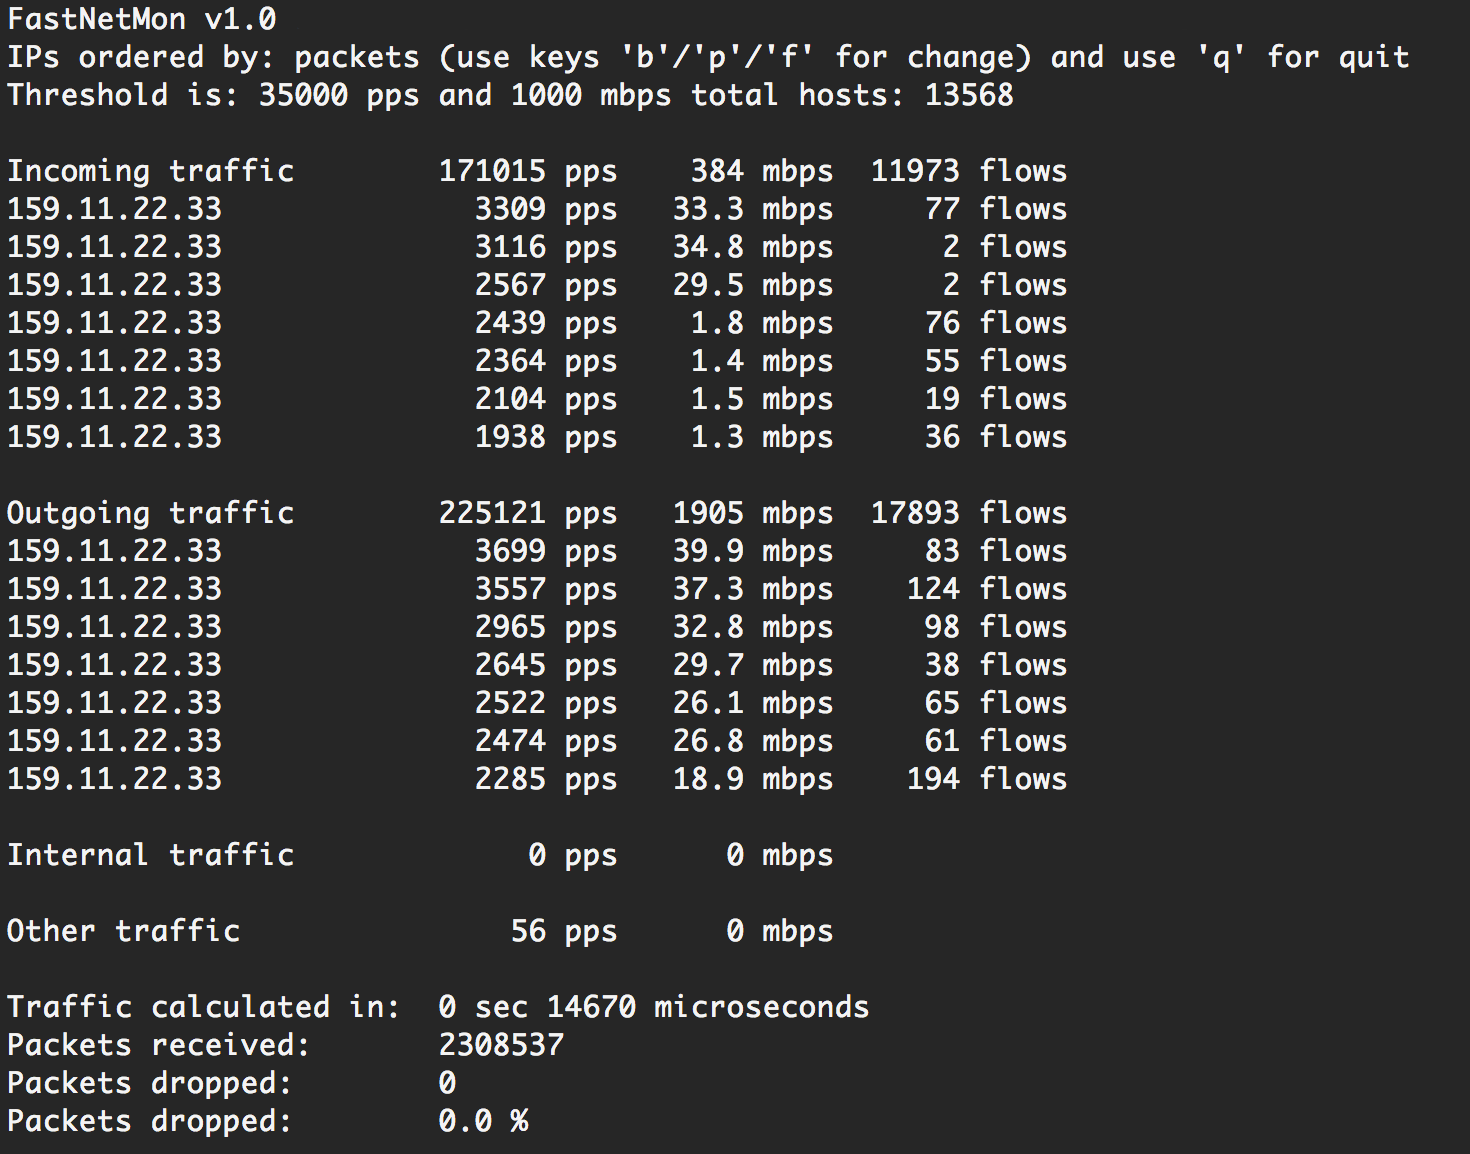 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
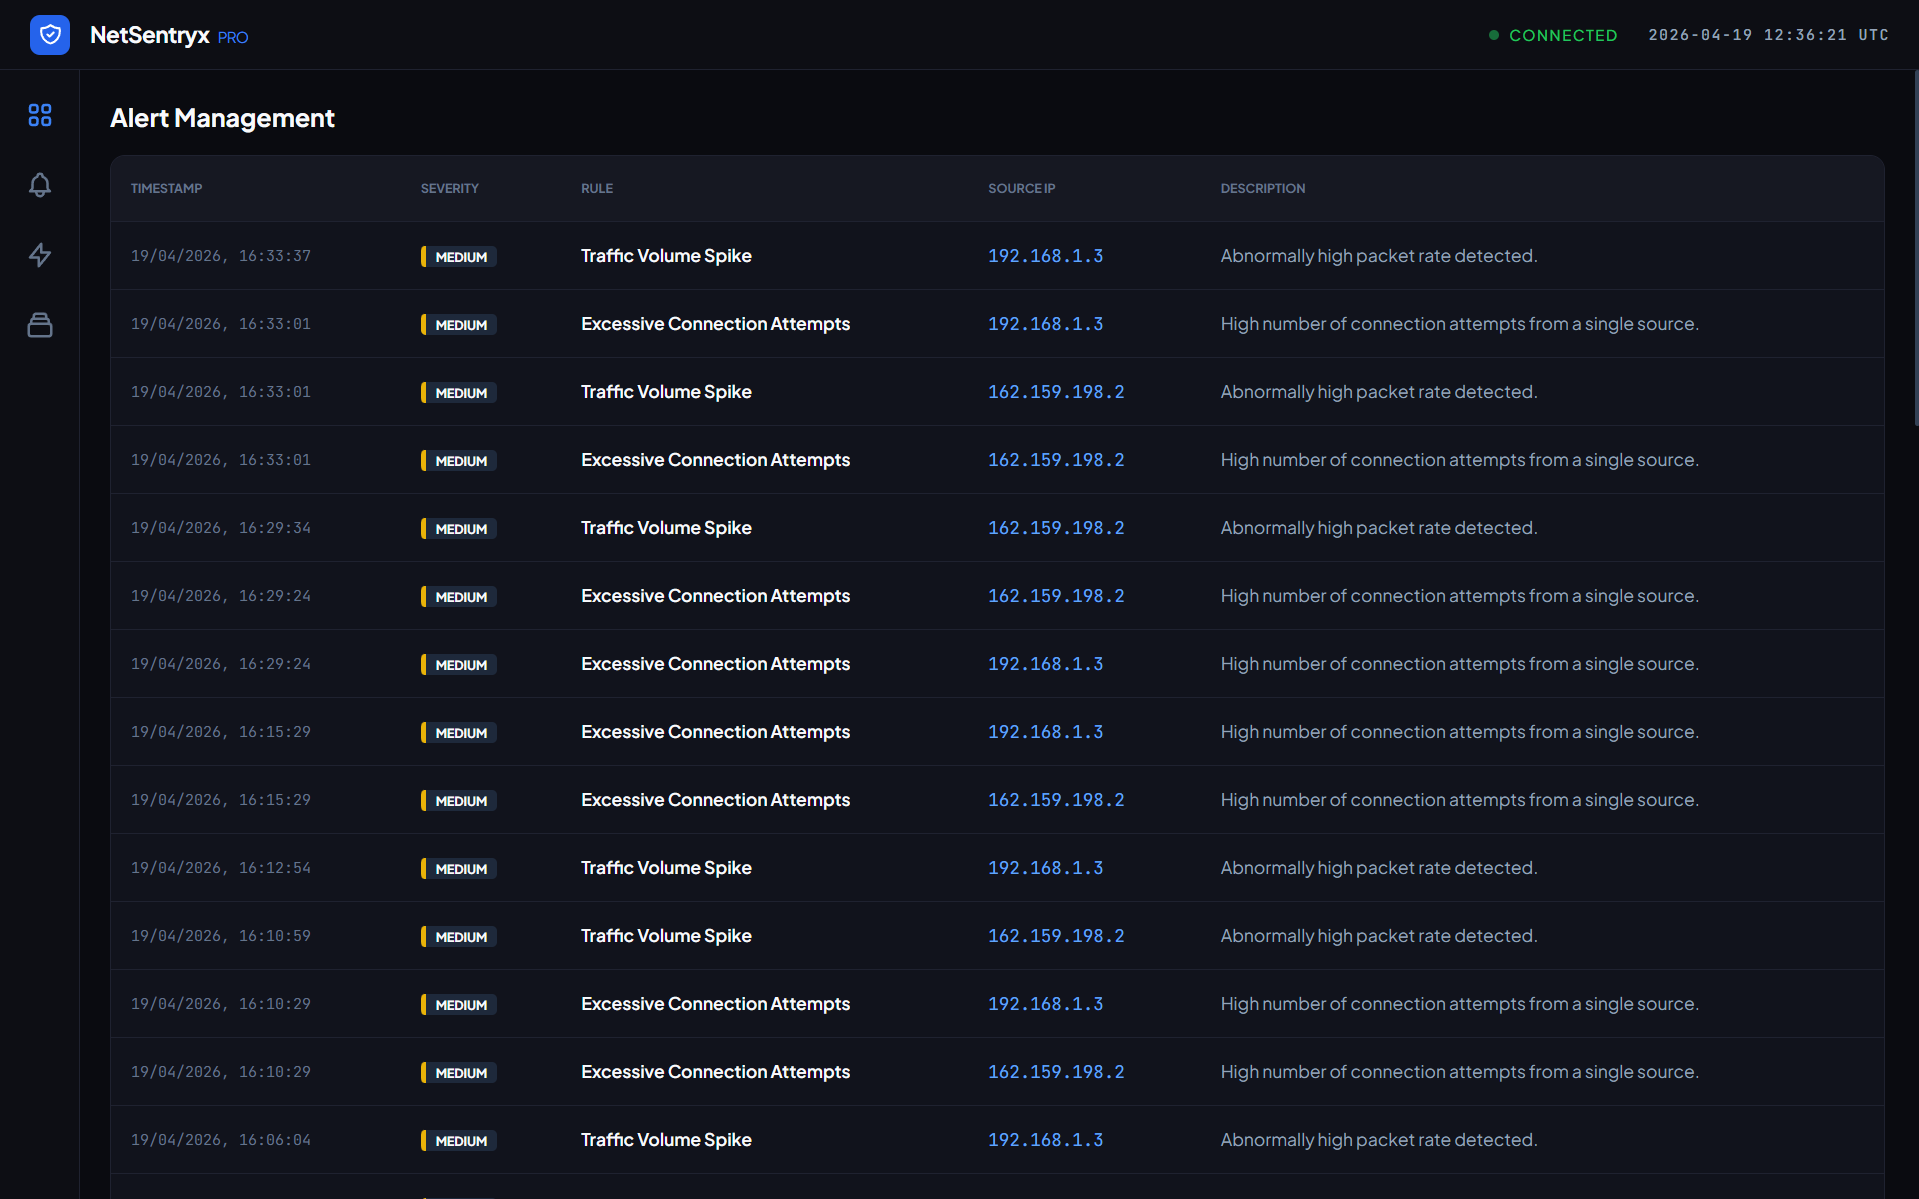 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
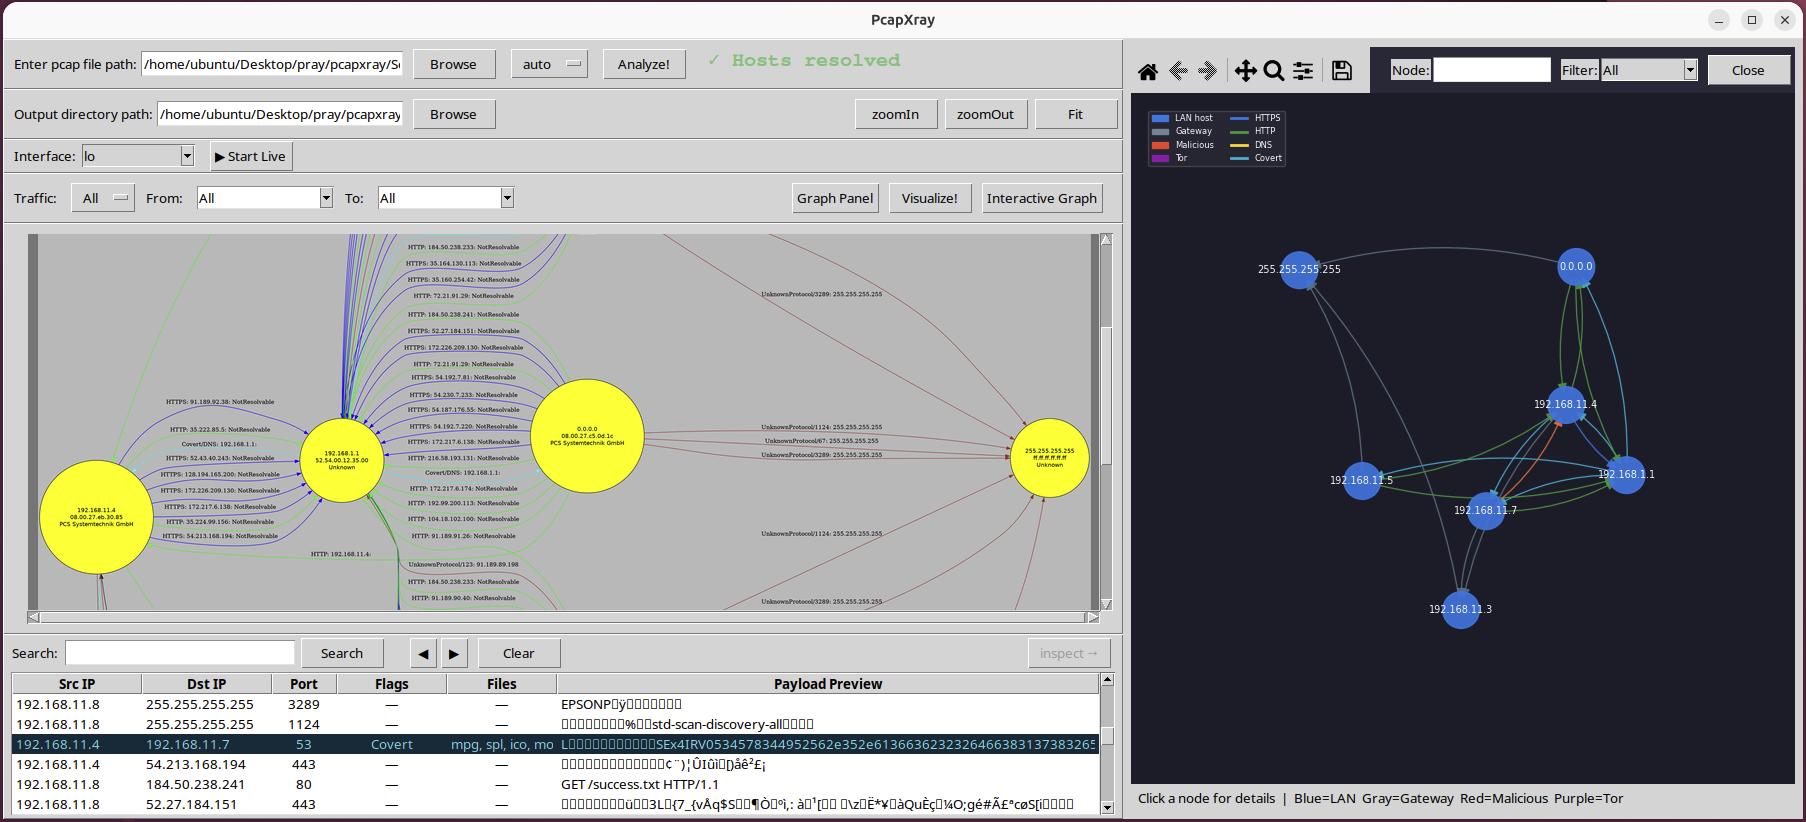 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 corelight/cve-2022-21907
Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.
 corelight/cve-2020-16898
A network detection package for CVE-2020-16898 (Windows TCP/IP Remote Code Execution Vulnerability)
 kirkdjohnson/wireshark
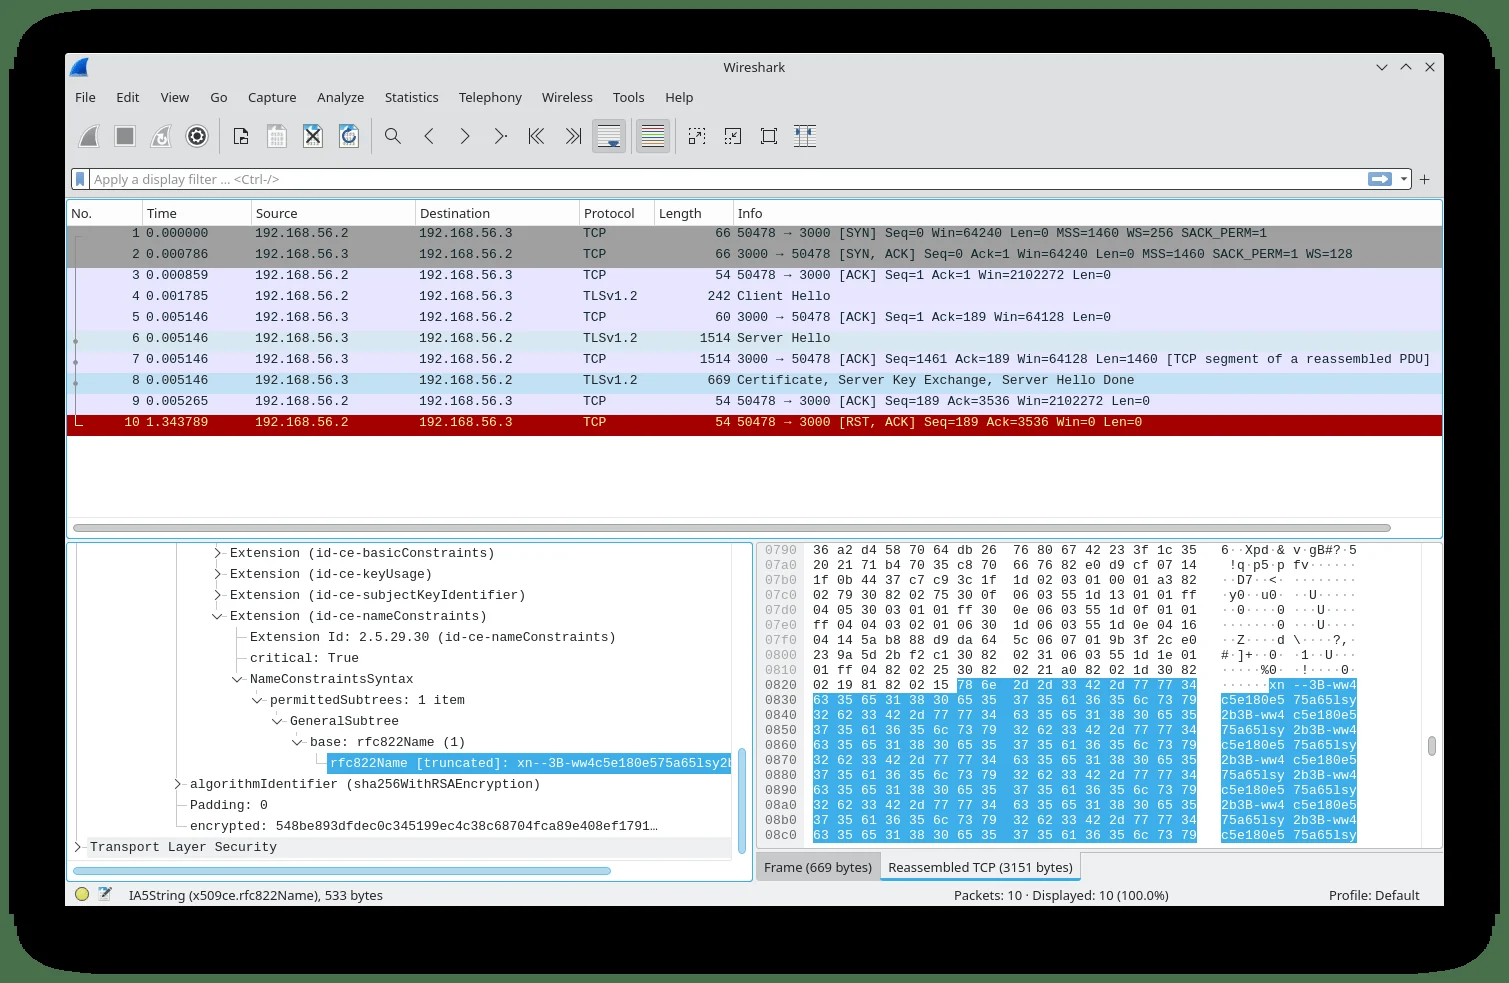
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 packetsifter/packetsiftertool
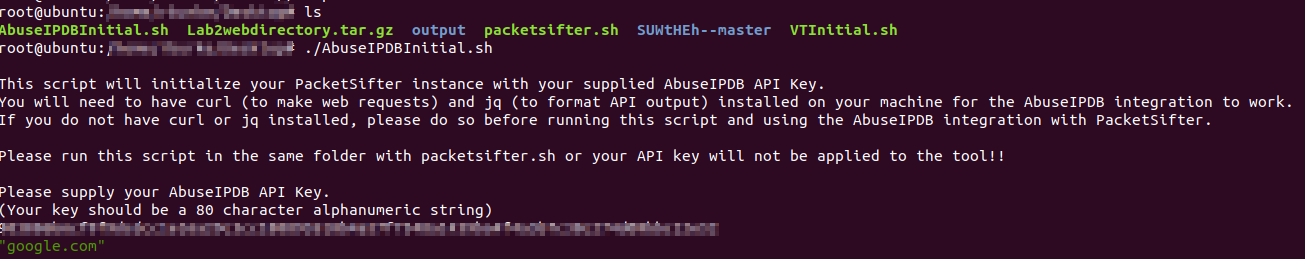
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 dlee35/curveball_lua
Repo containing lua scripts and PCAP to find CVE-2020-0601 exploit attempts via network traffic
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.