
openshield
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
cloud-securityconfiguration-auditingcryptography+4
63
owasp/openshieldOpen source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
 owasp/the-agents-epistemic-baggage
An audit-oriented risk model for how agent-generated inferences can change epistemic status, gain operational authority, and influence later…
 owasp/ai-threat-modeler
OWASP project for AI-assisted threat modeling, helping teams identify, analyze, and document security threats and mitigations in system designs.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/honeysap
HoneySAP: SAP Low-interaction research honeypot
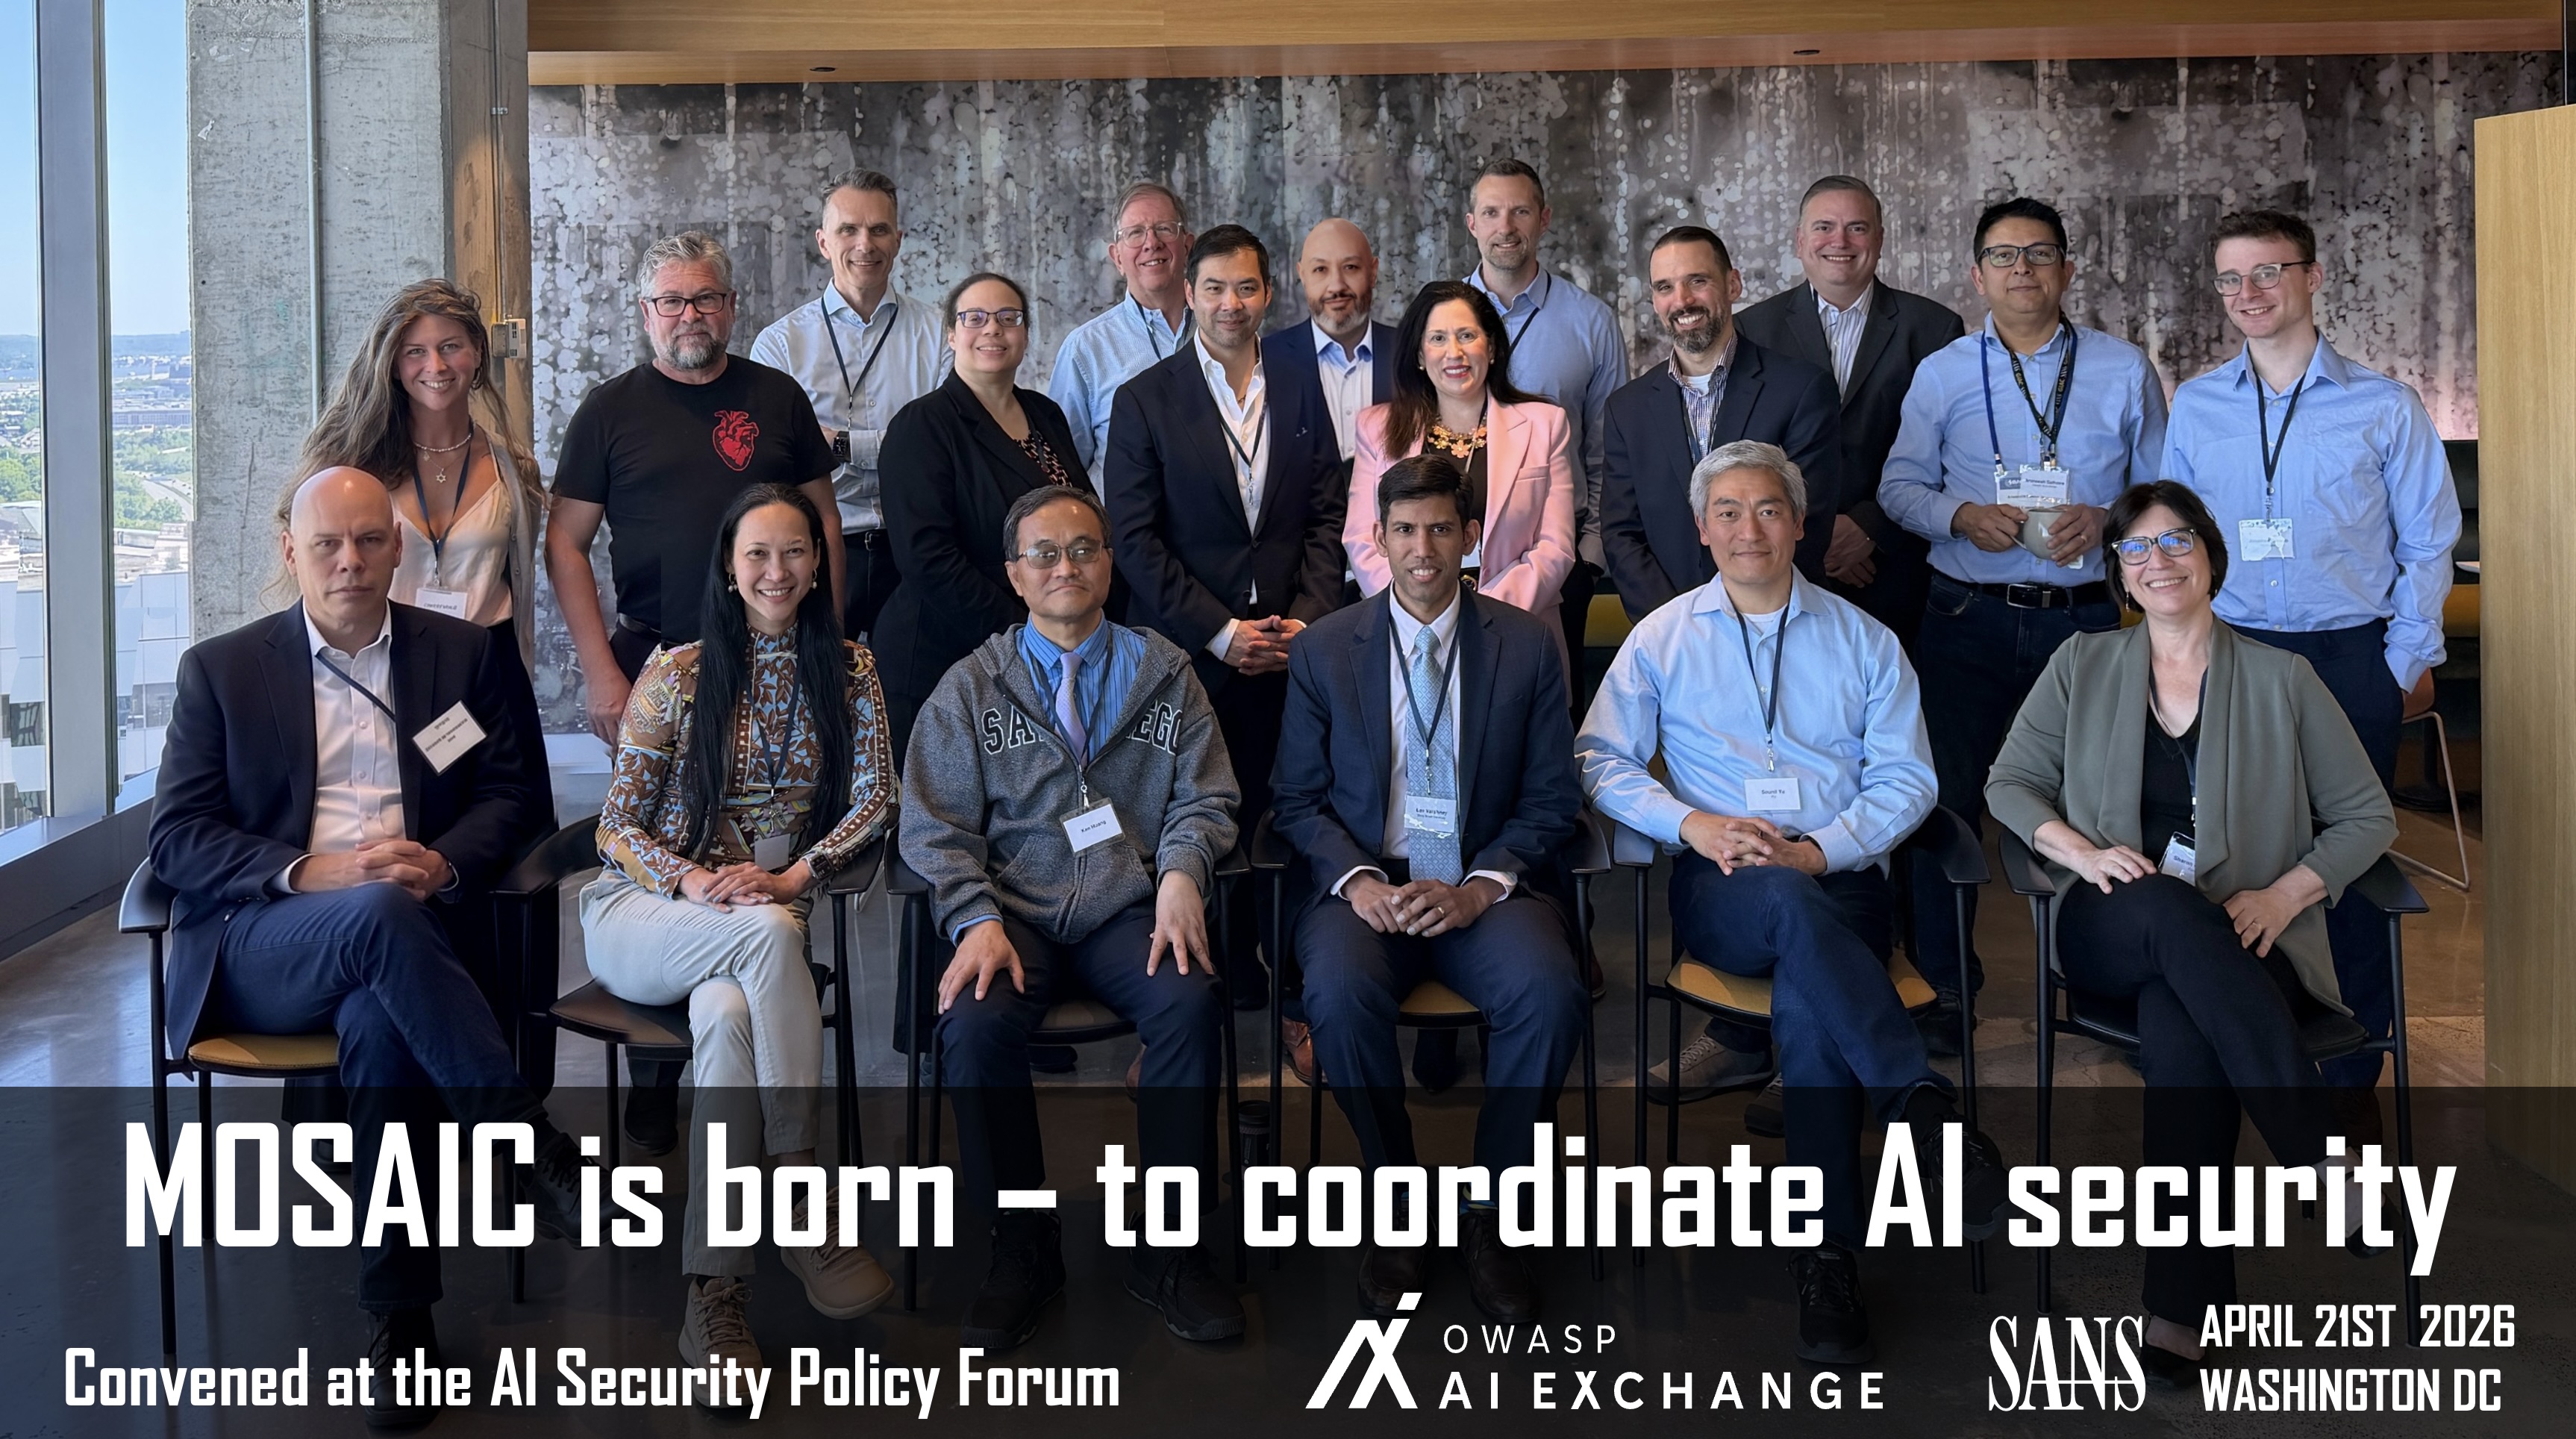 owasp/mosaic
Coordination structure for AI security standards and guidelines, reducing fragmentation and providing clear guidance for securing AI systems across…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 owasp/owasp-open-source-intelligence-standard
An open, vendor-neutral verification standard for traceable, reviewable, and rights-aware open-source intelligence. Current release: OOVS v0.1.0.
 owasp/german-owasp-day
German OWASP Day conference site & presentation archive
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 genai-security-project/genai-llm-top10
OWASP Top 10 for Large Language Model Applications