
chainsaw
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k
withsecureopensource/chainsawRapidly Search and Hunt through Windows Forensic Artefacts
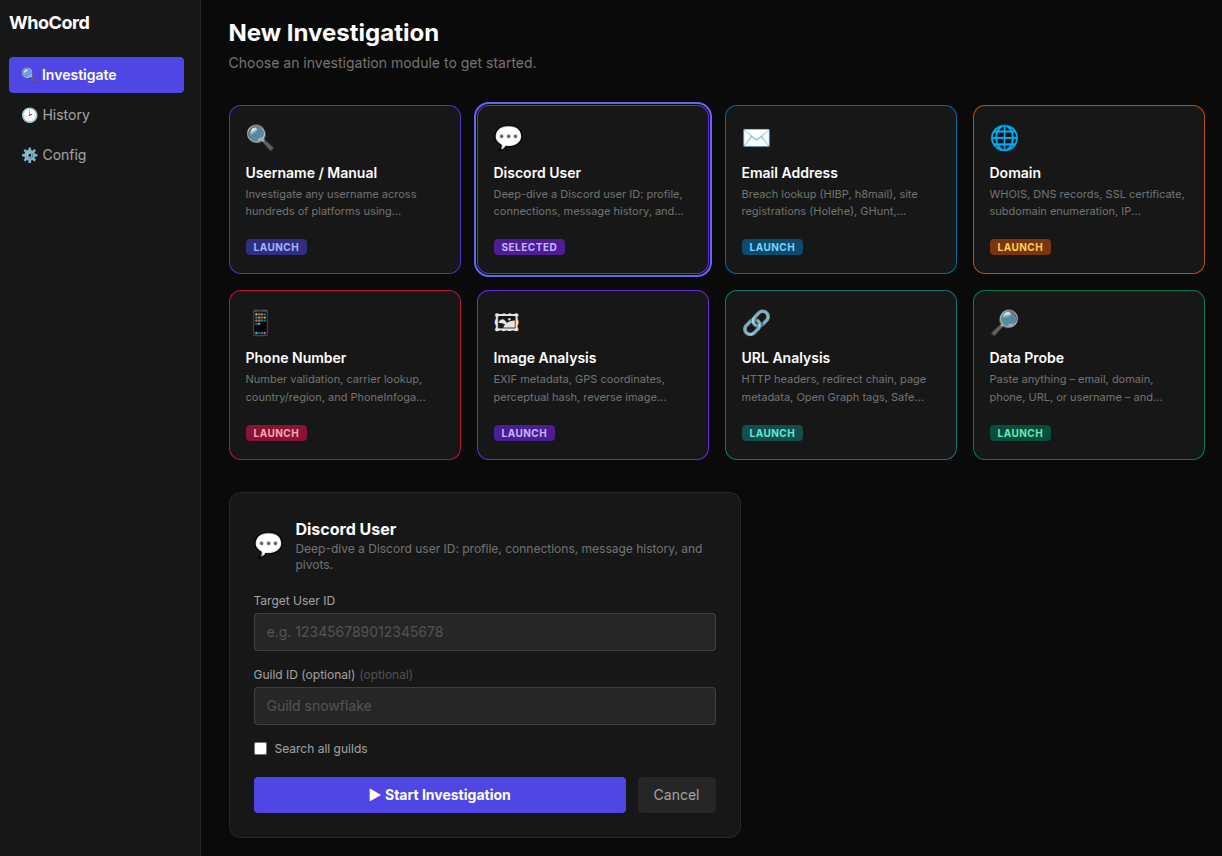 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
 0ggp4r1s/osint-pattern-analyzer
Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.
 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
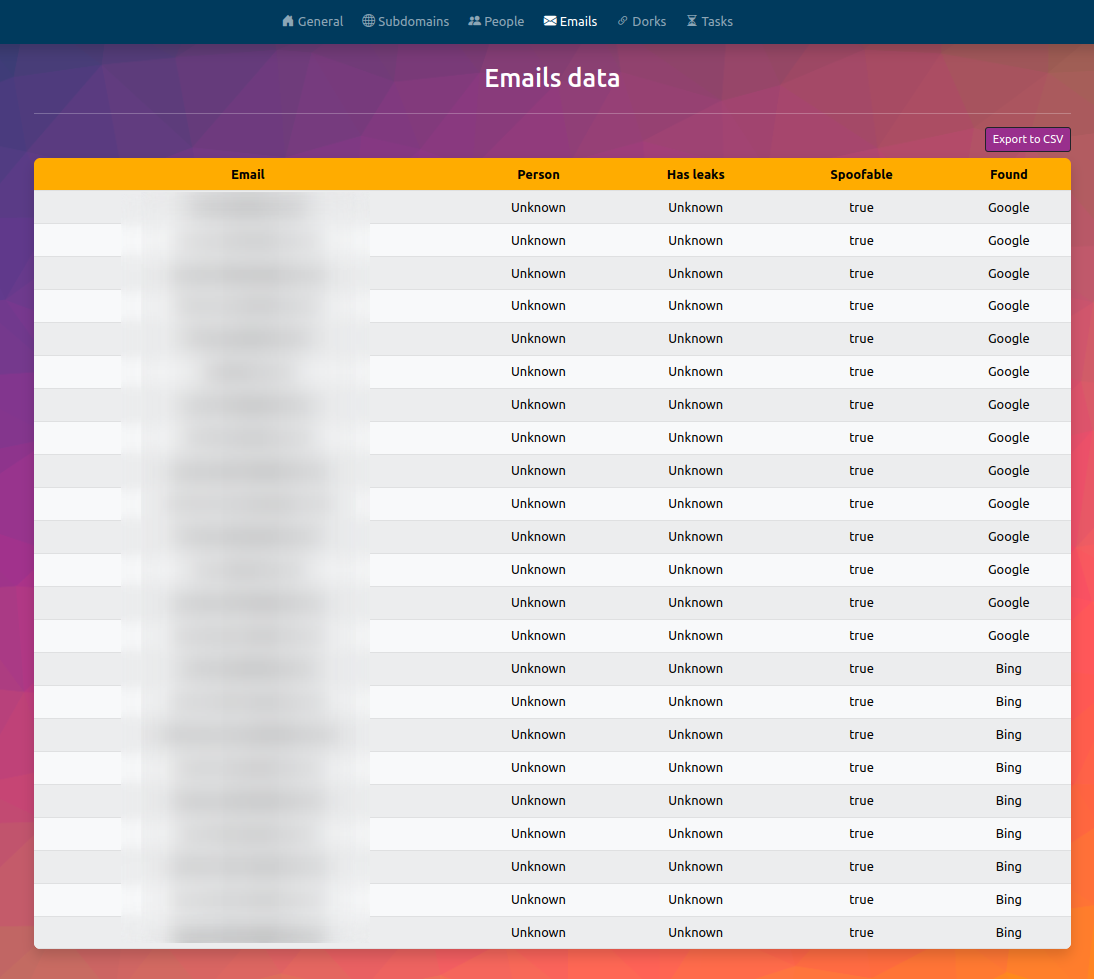 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
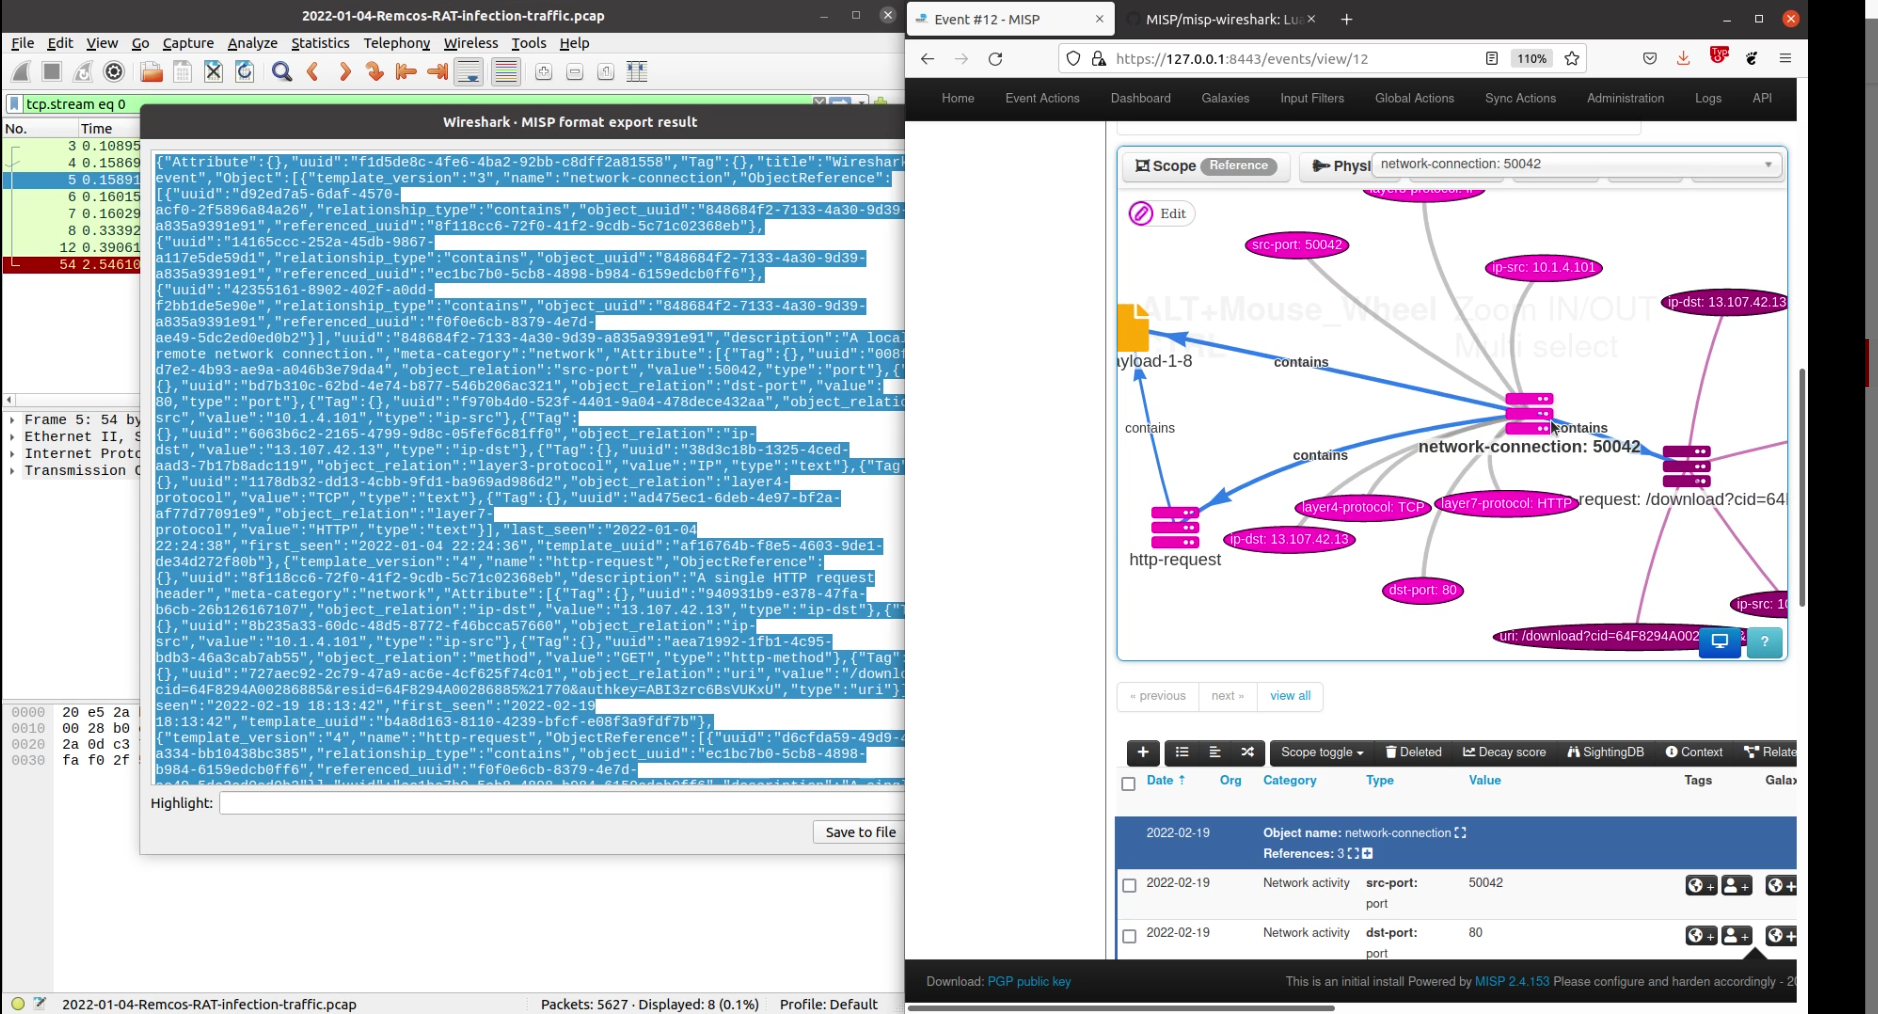 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 securityjoes/threatresearch
Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
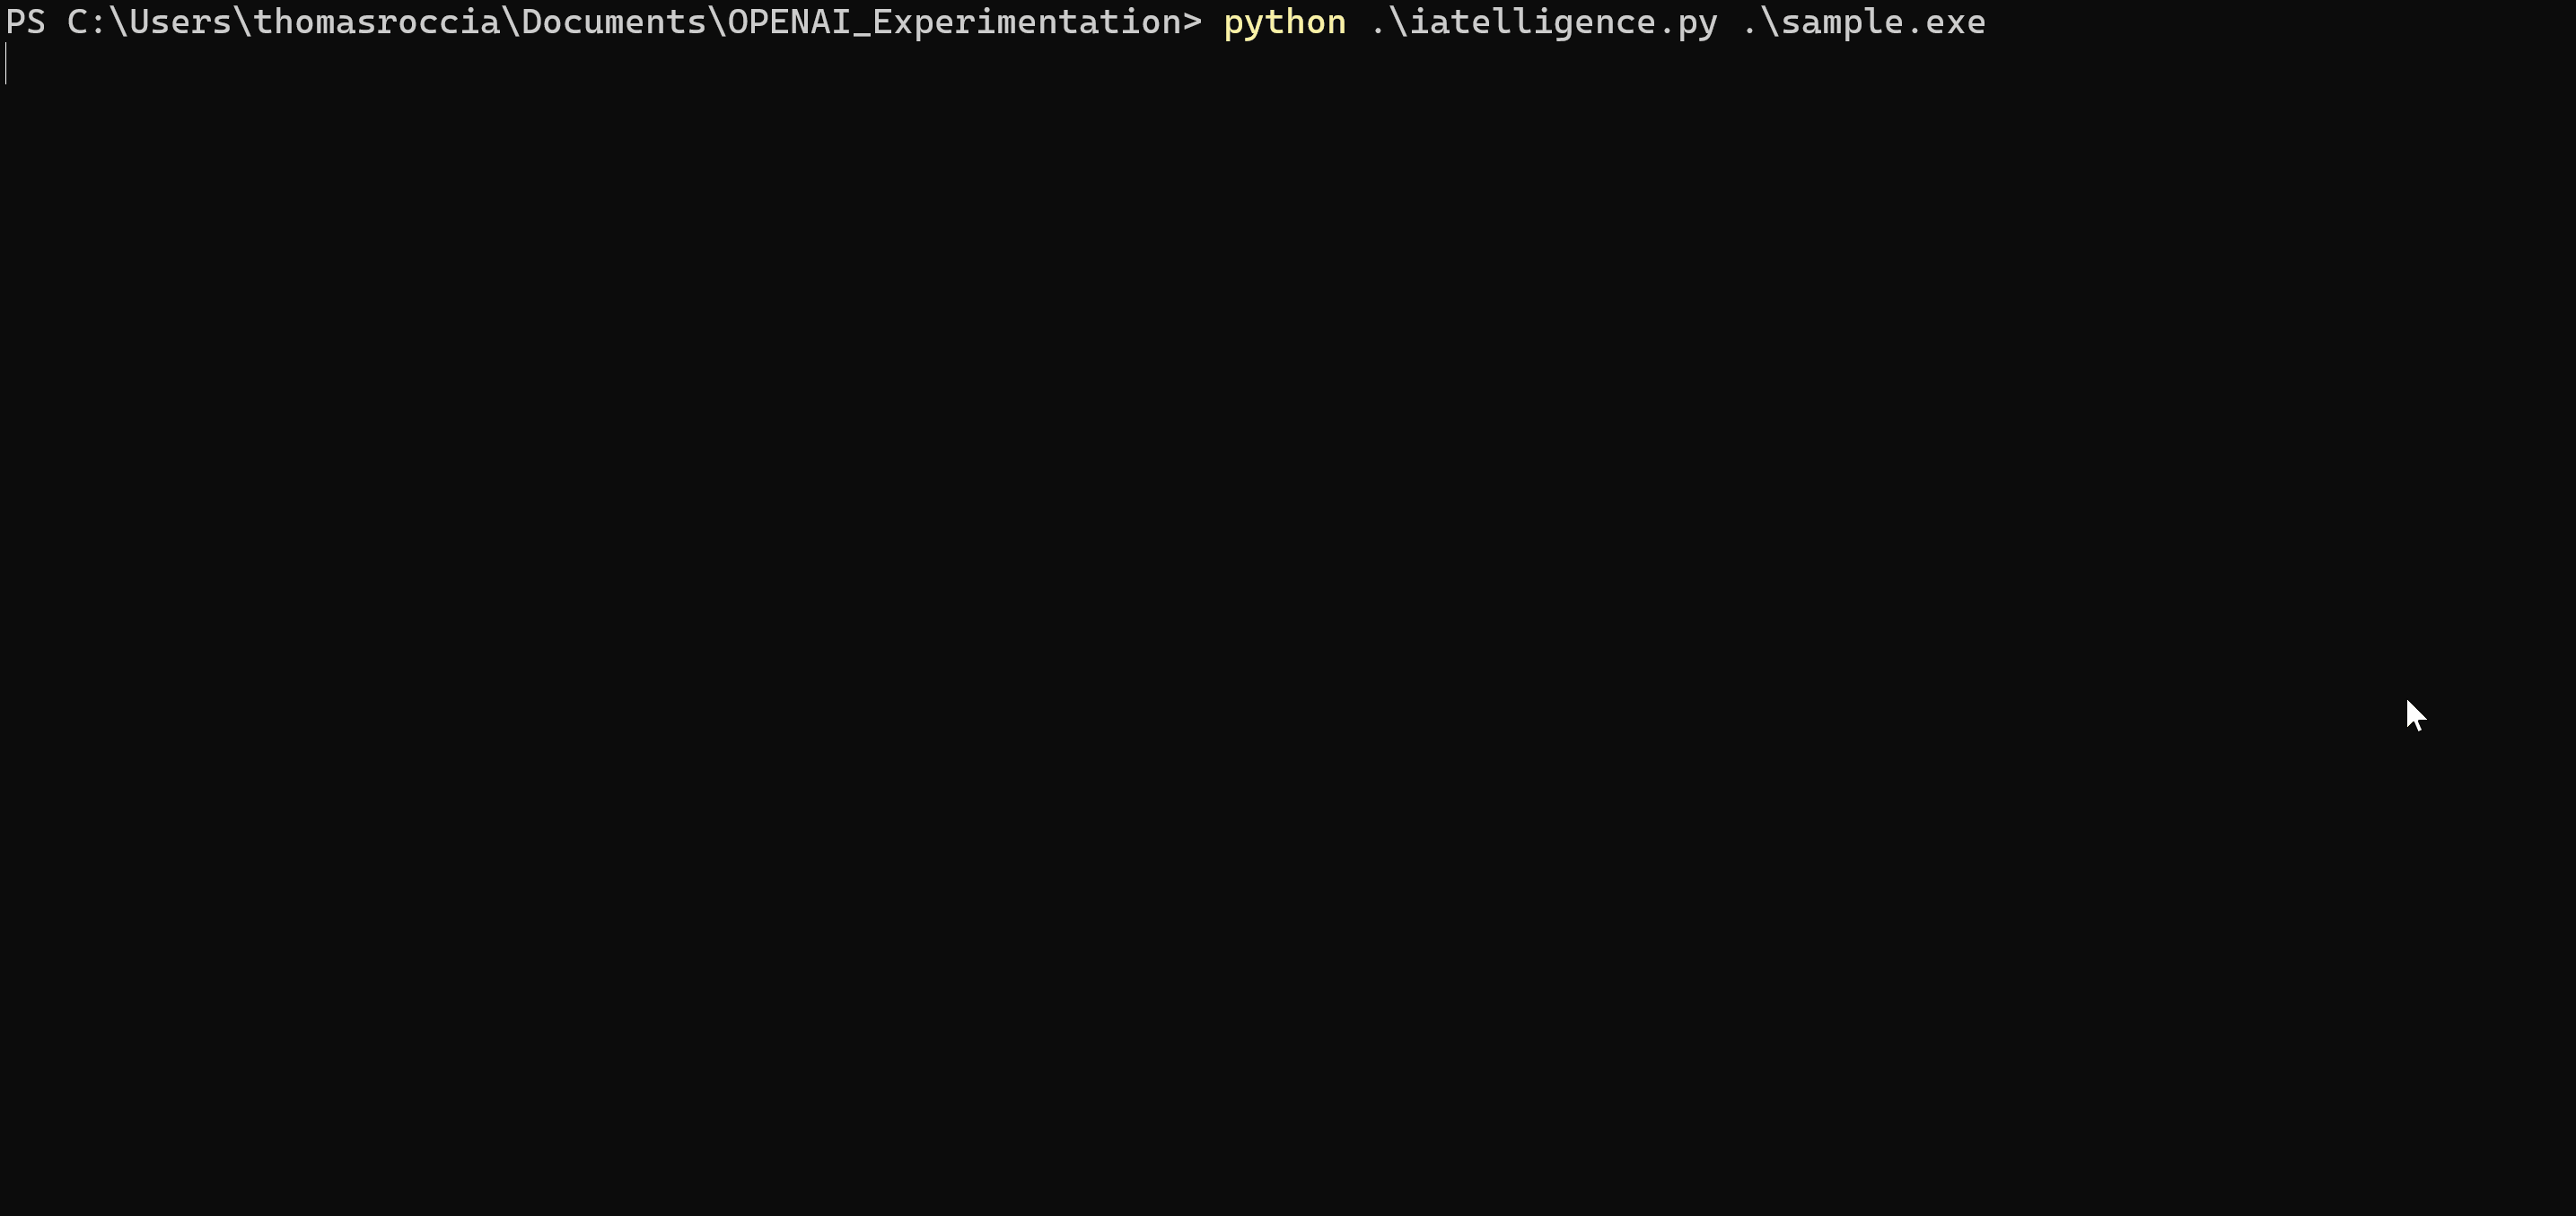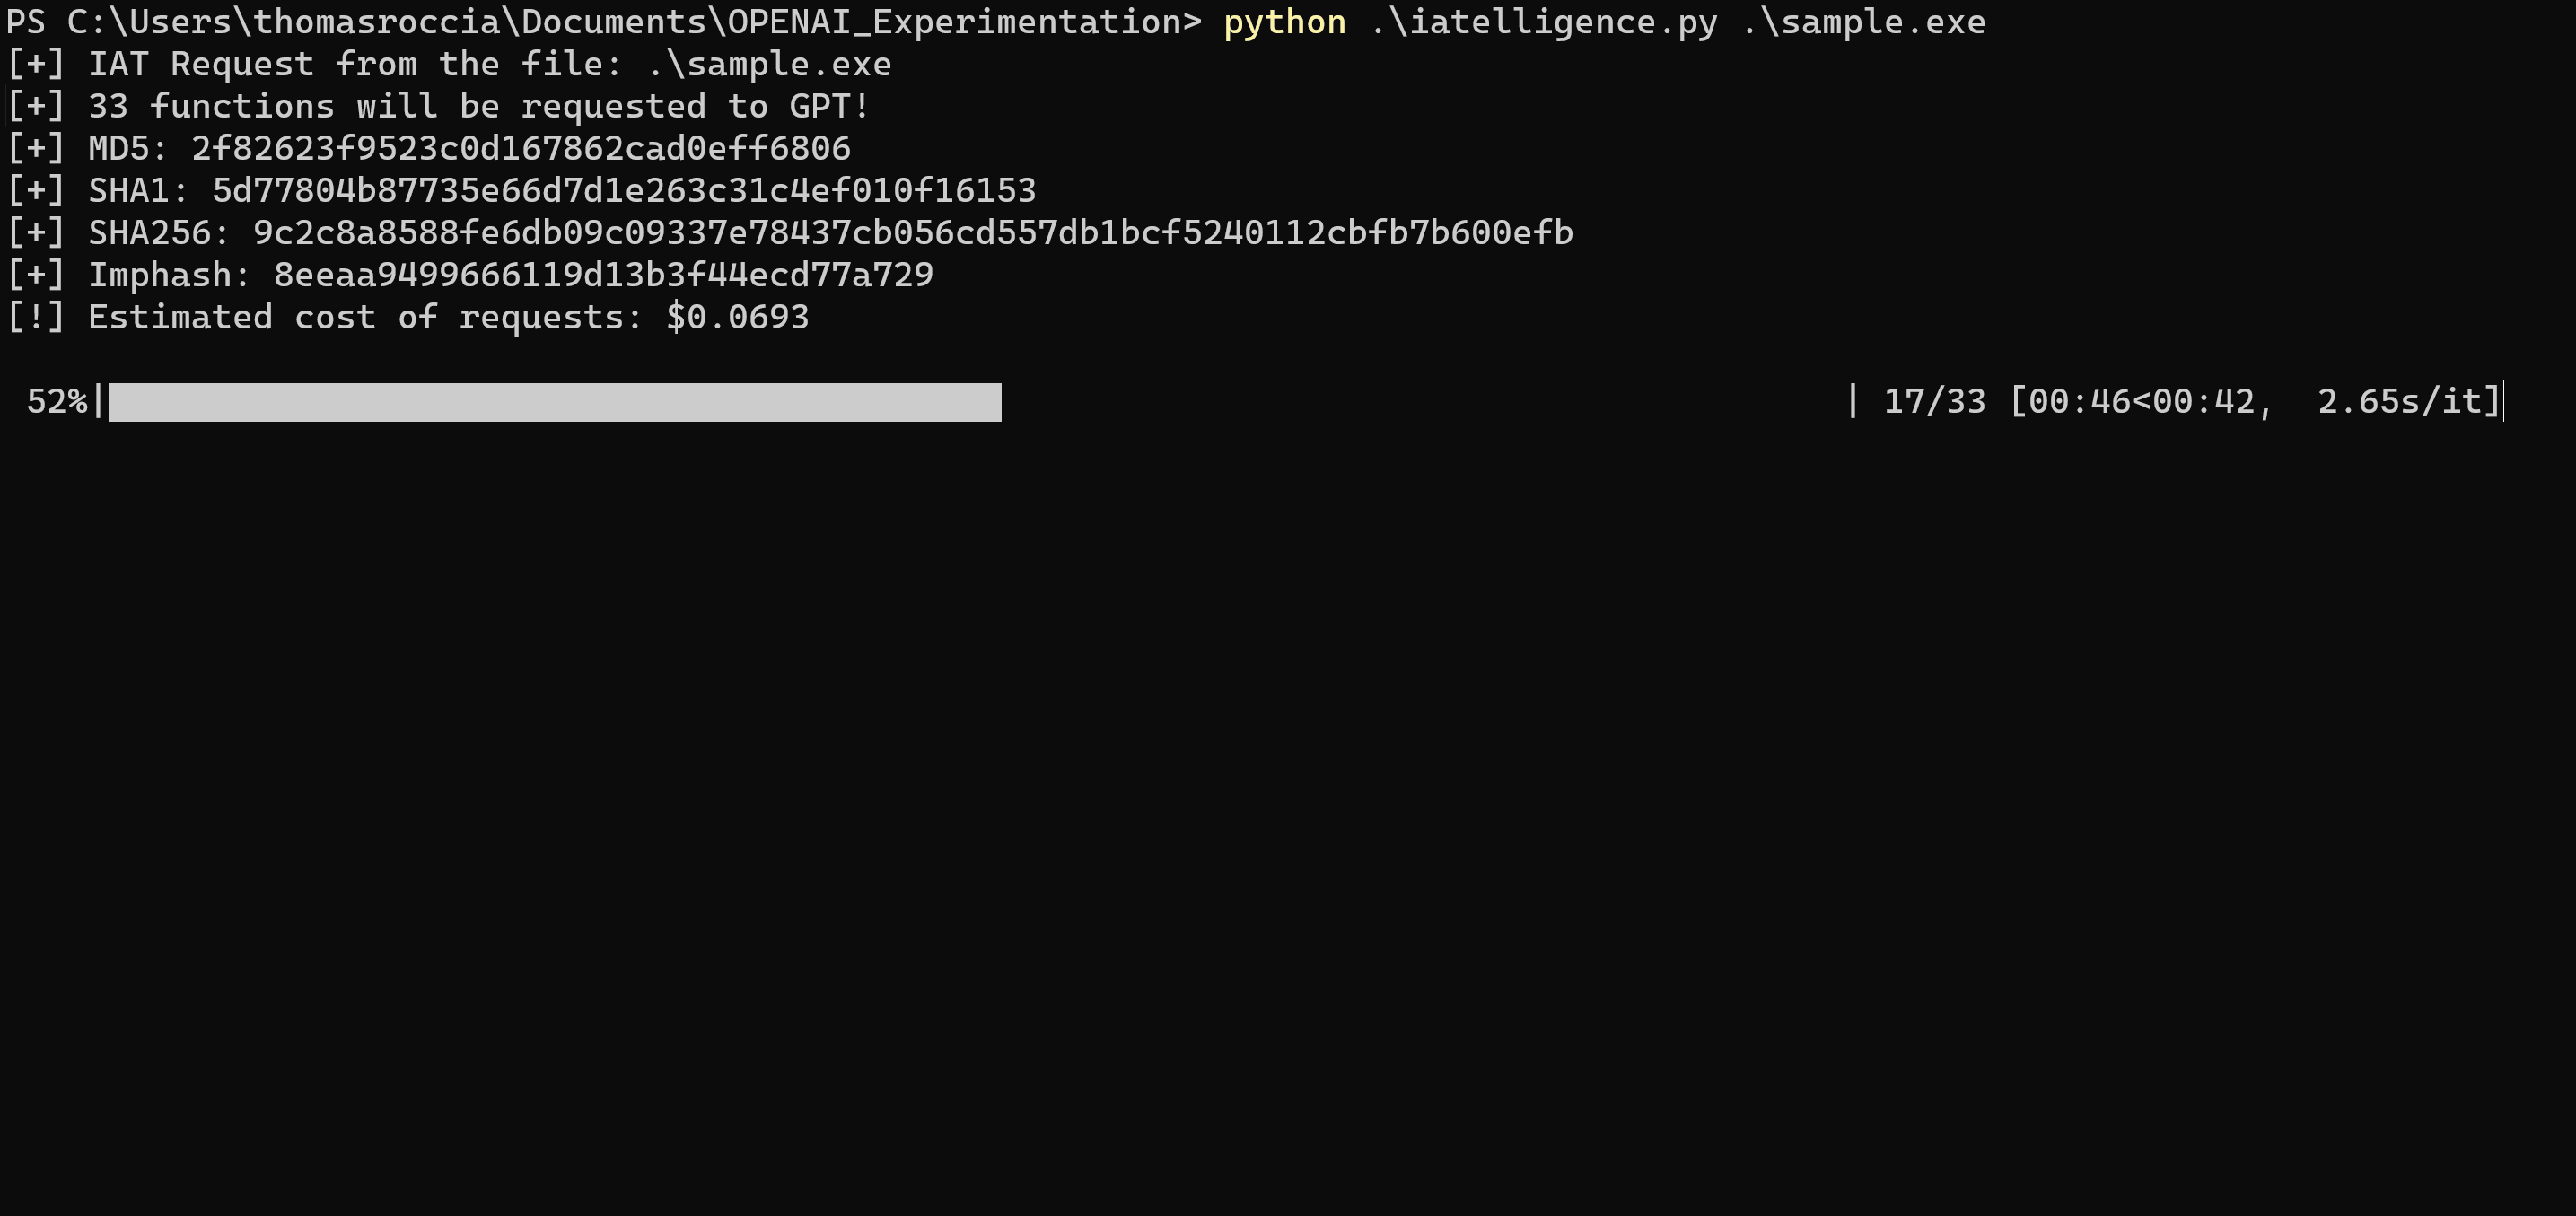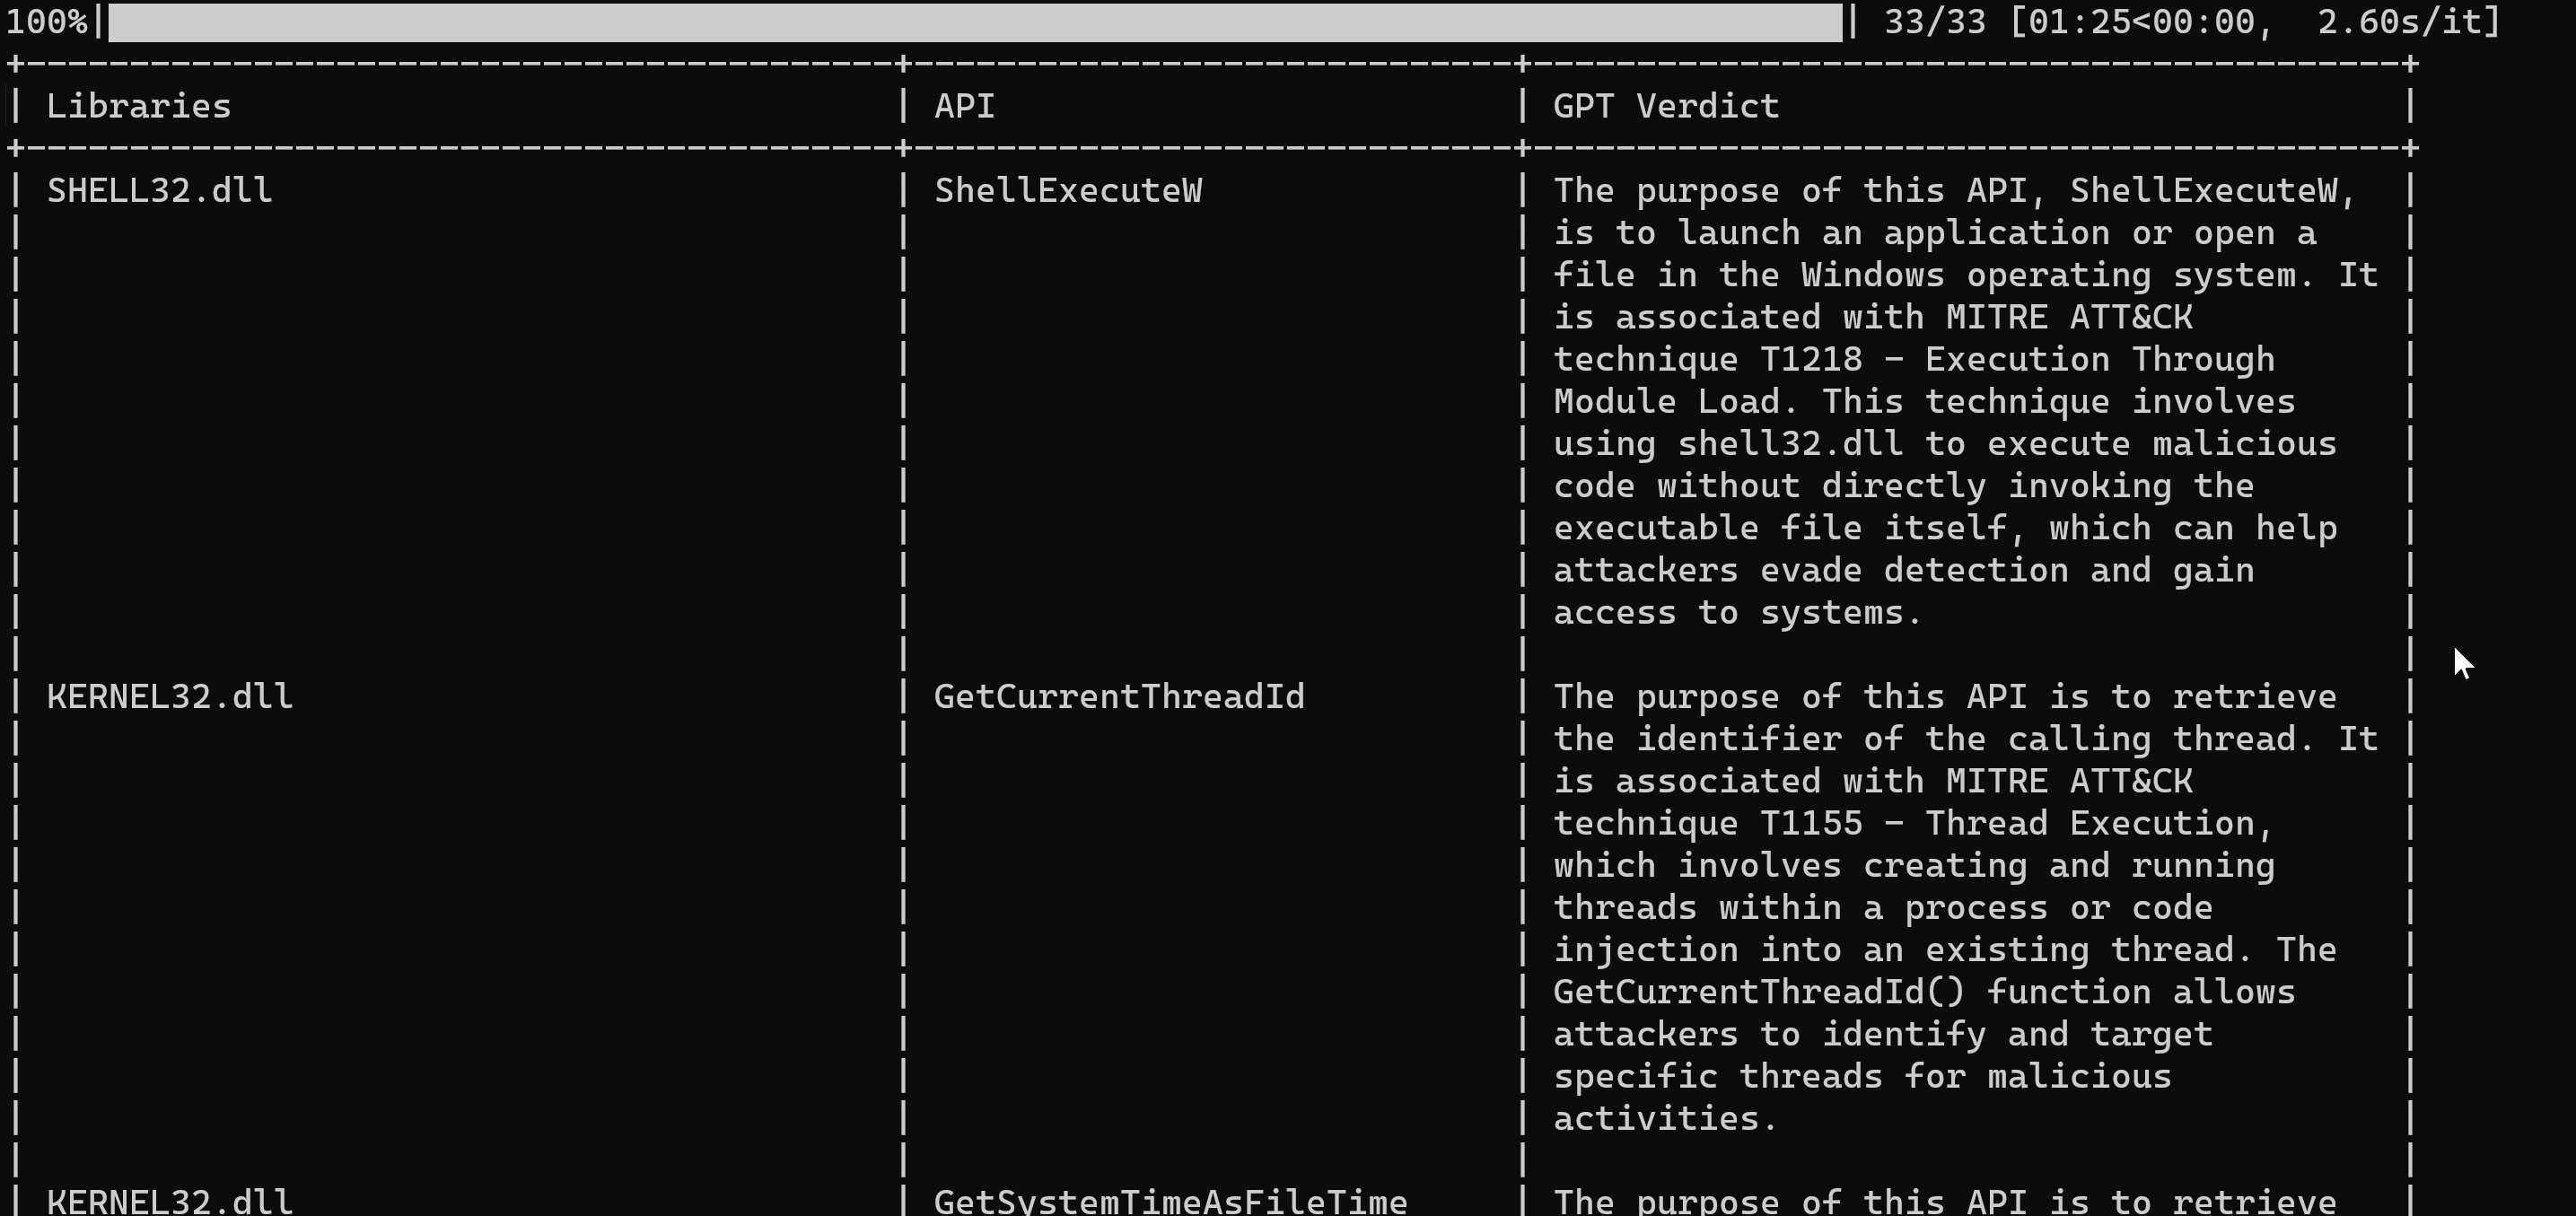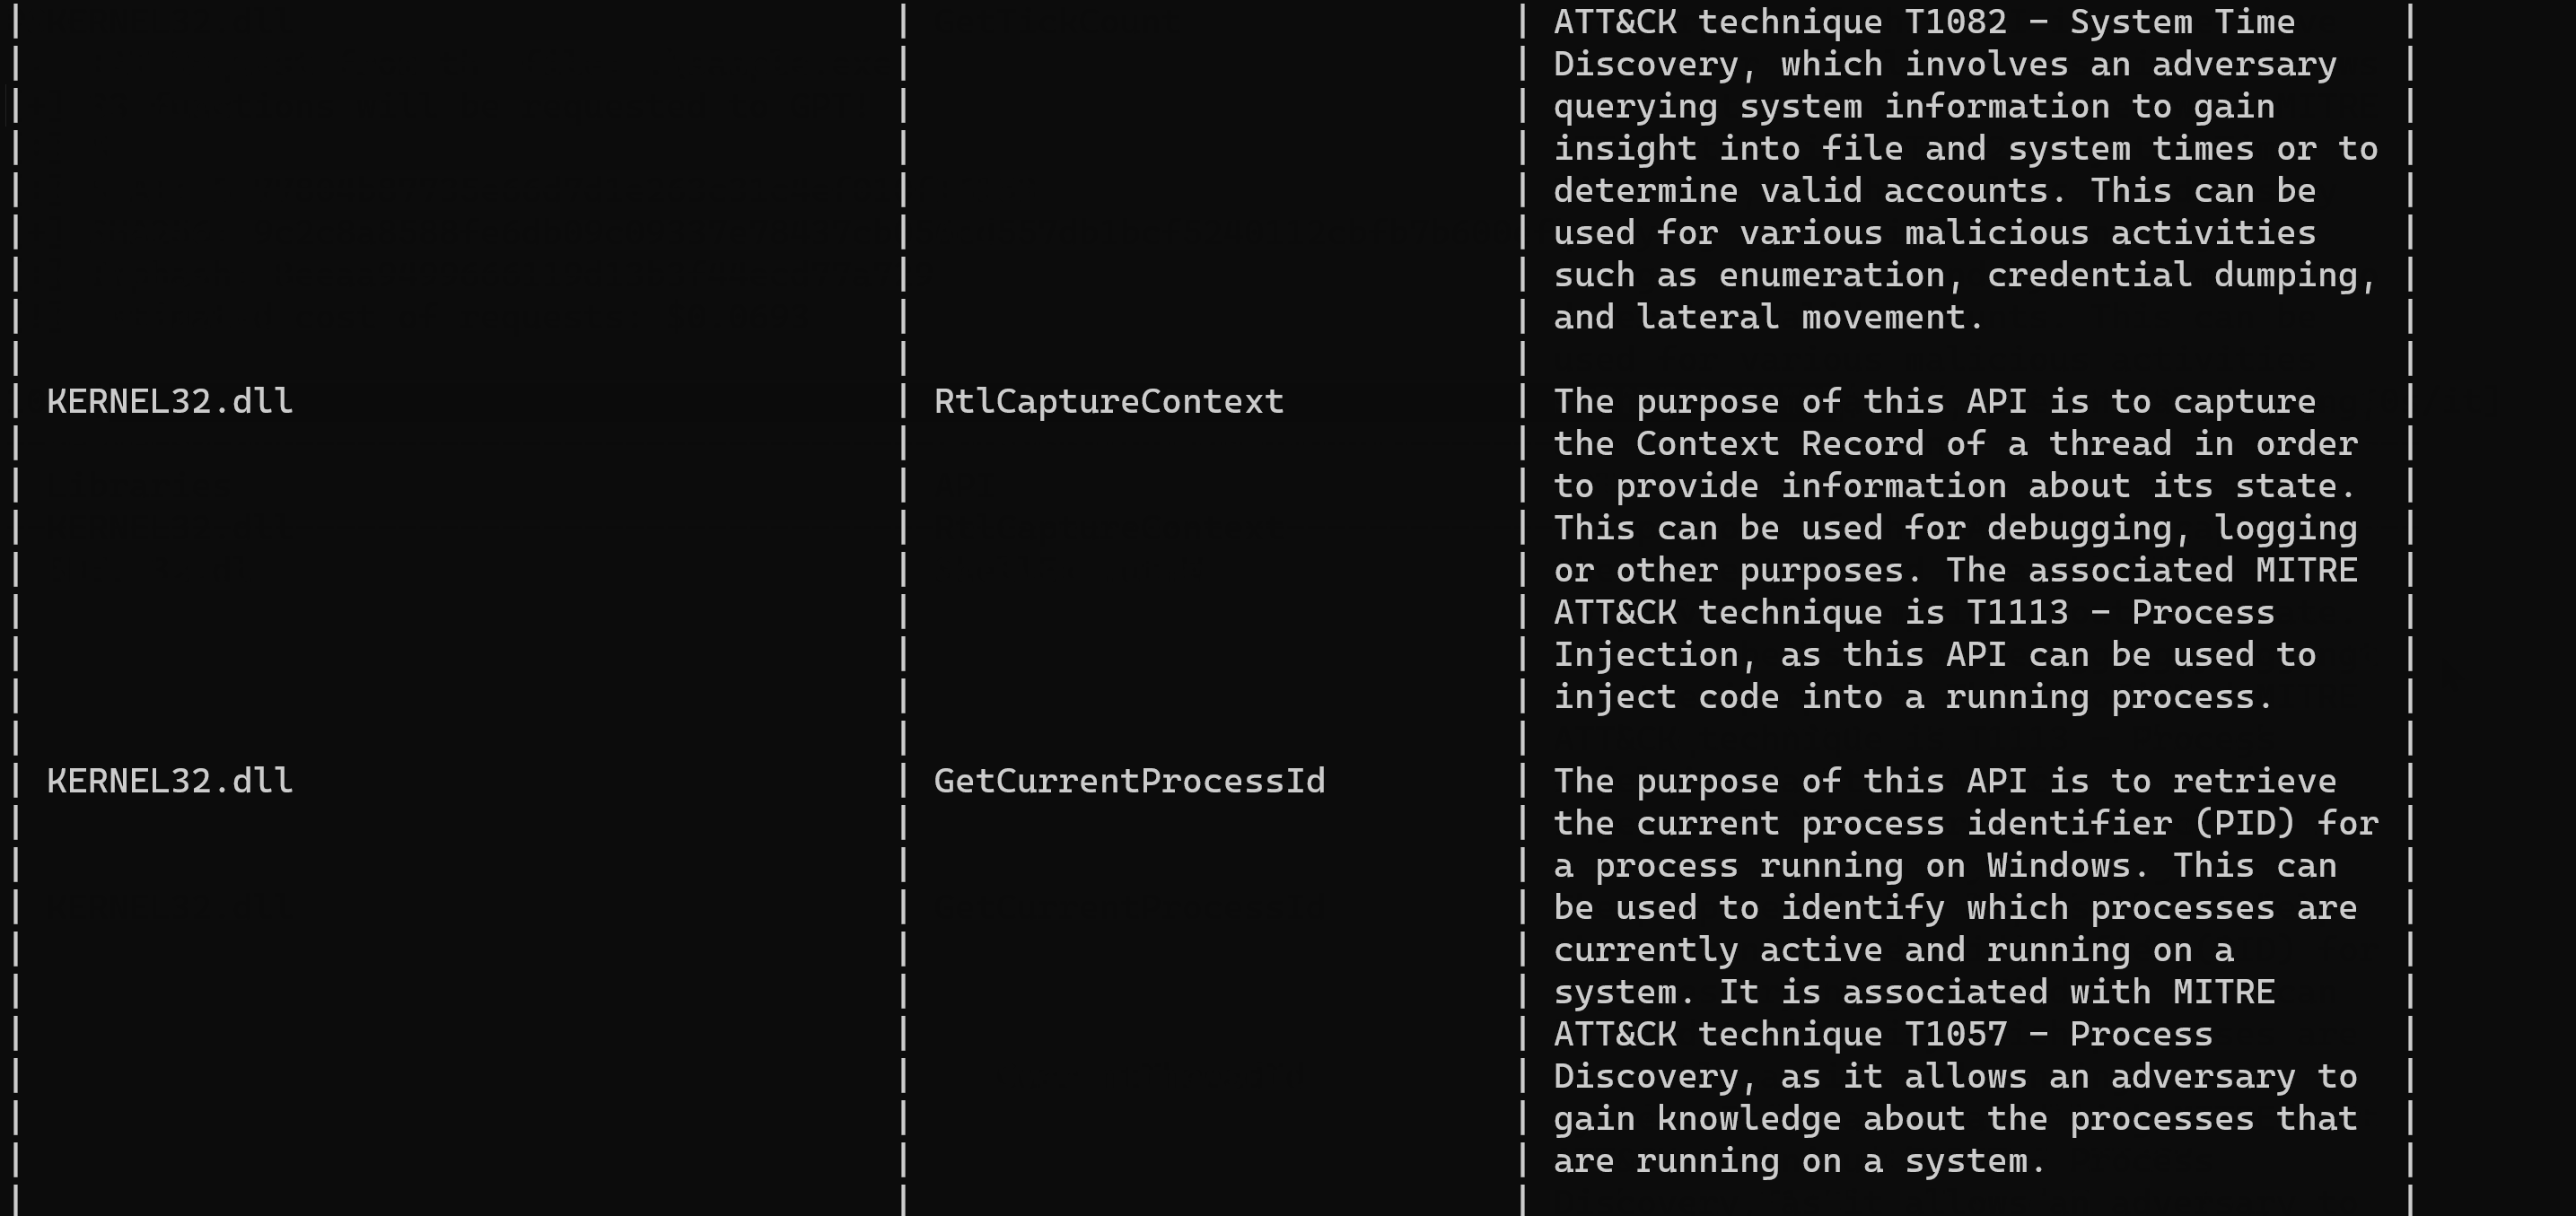 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
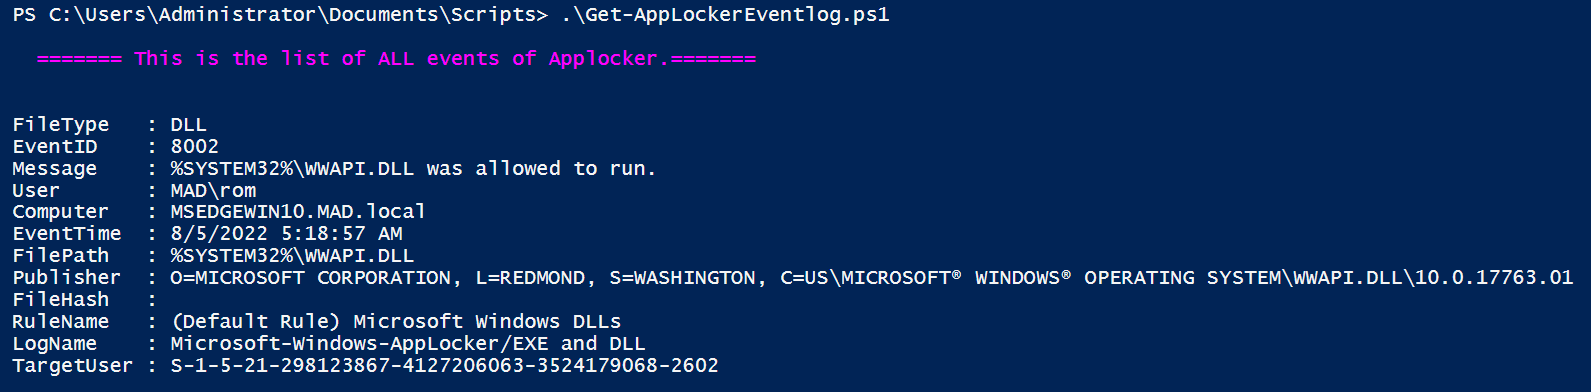 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 chaitanyakrishna/iocscraper
IOCPARSER.COM is a Fast and Reliable service that enables you to extract IOCs and intelligence from different data sources.
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
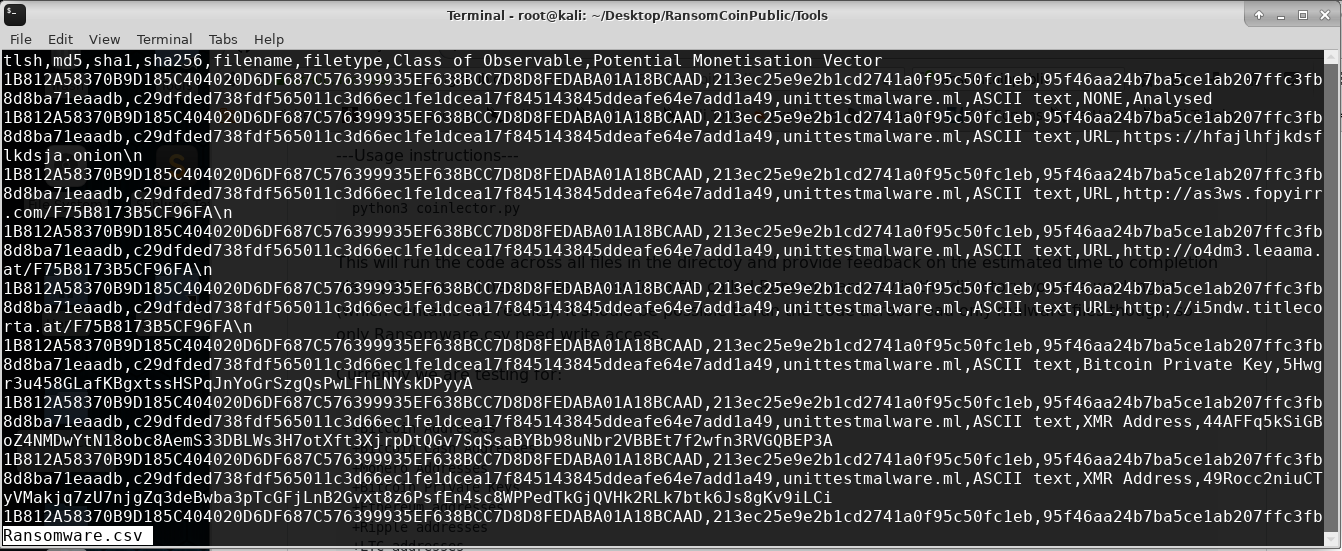 concinnity-risks/ransomcoinpublic
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.