
stride-gpt
 mrwadams/stride-gpt
An AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
ai-securityeducationpenetration-testing-frameworks+2
1.1k
mrwadams/stride-gptAn AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 0xblackash/cve-2026-72898
CVE-2026-72898
 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
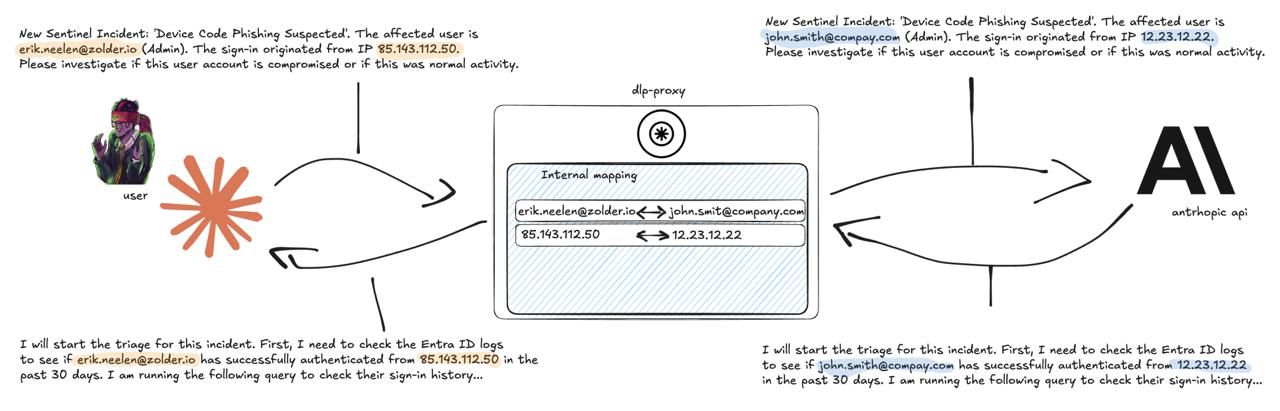 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…