
SSHintel
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
incident-responseintrusion-detectionlog-analysis+2
3
sonitbahl/sshintelSelf-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
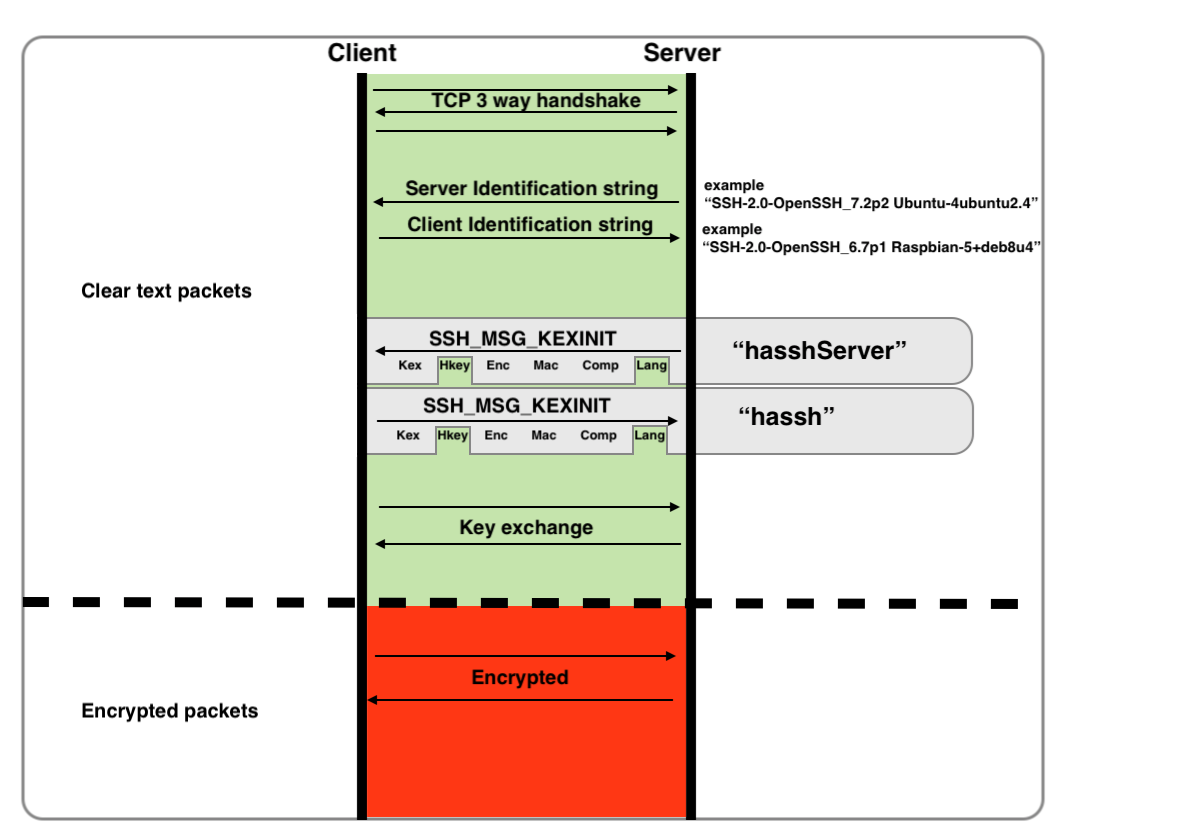 corelight/hassh
Fingerprint SSH clients and servers.
 d4vinci/ssh-honeypot
Create Basic SSH Honeypot With Python
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 horizon-software-development/cve-2024-3094
Advisory and analysis repository for CVE-2024-3094, detailing a critical backdoor in Linux SSH library with mitigation steps for servers and Android…
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
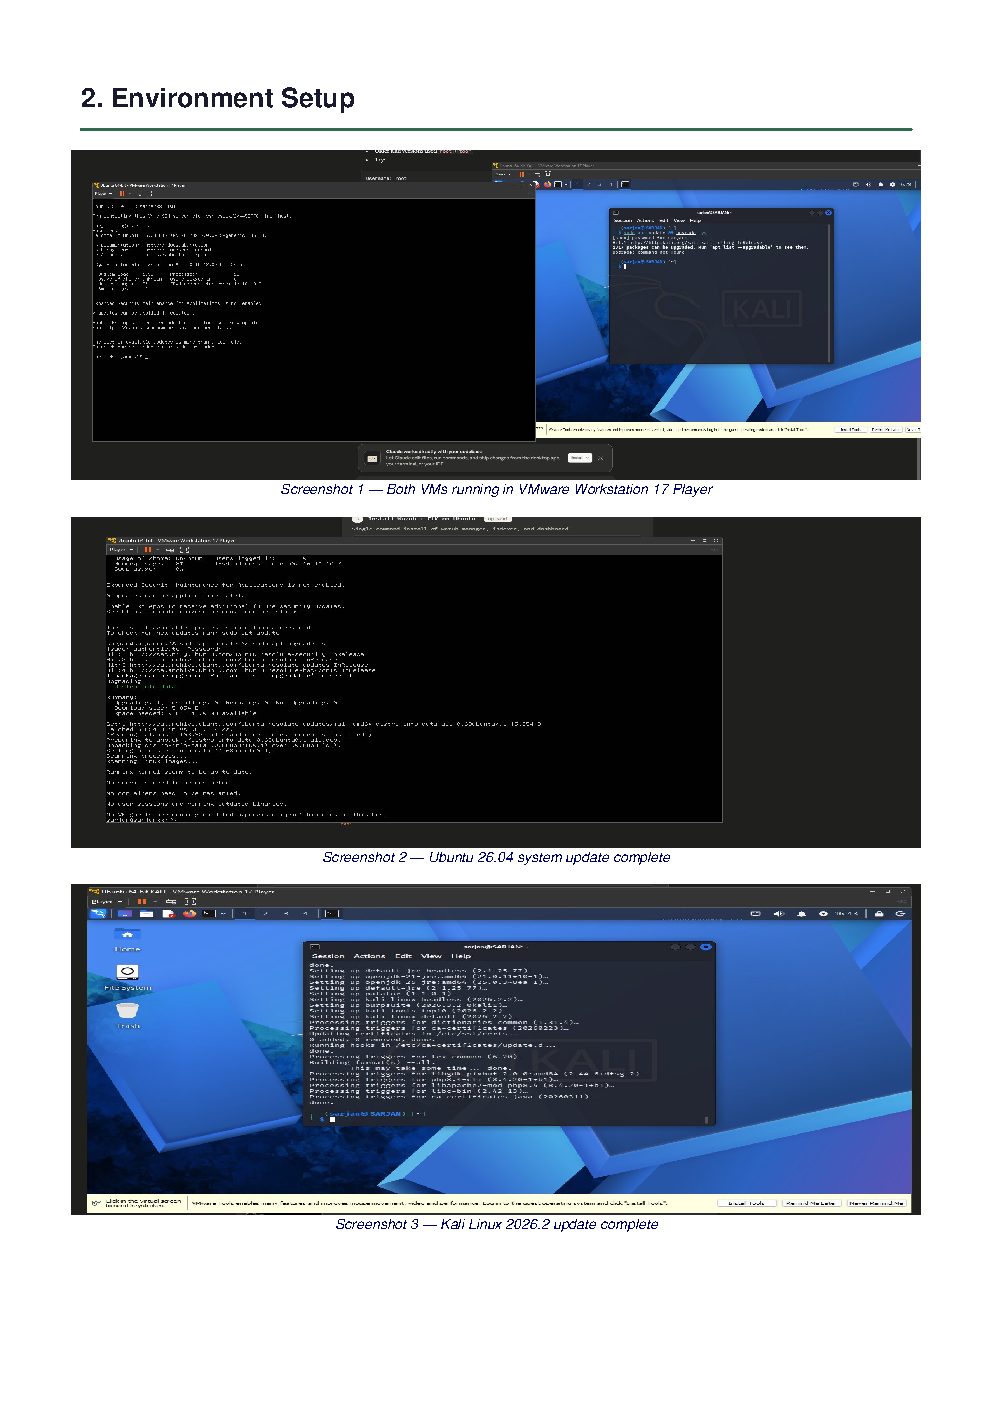 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
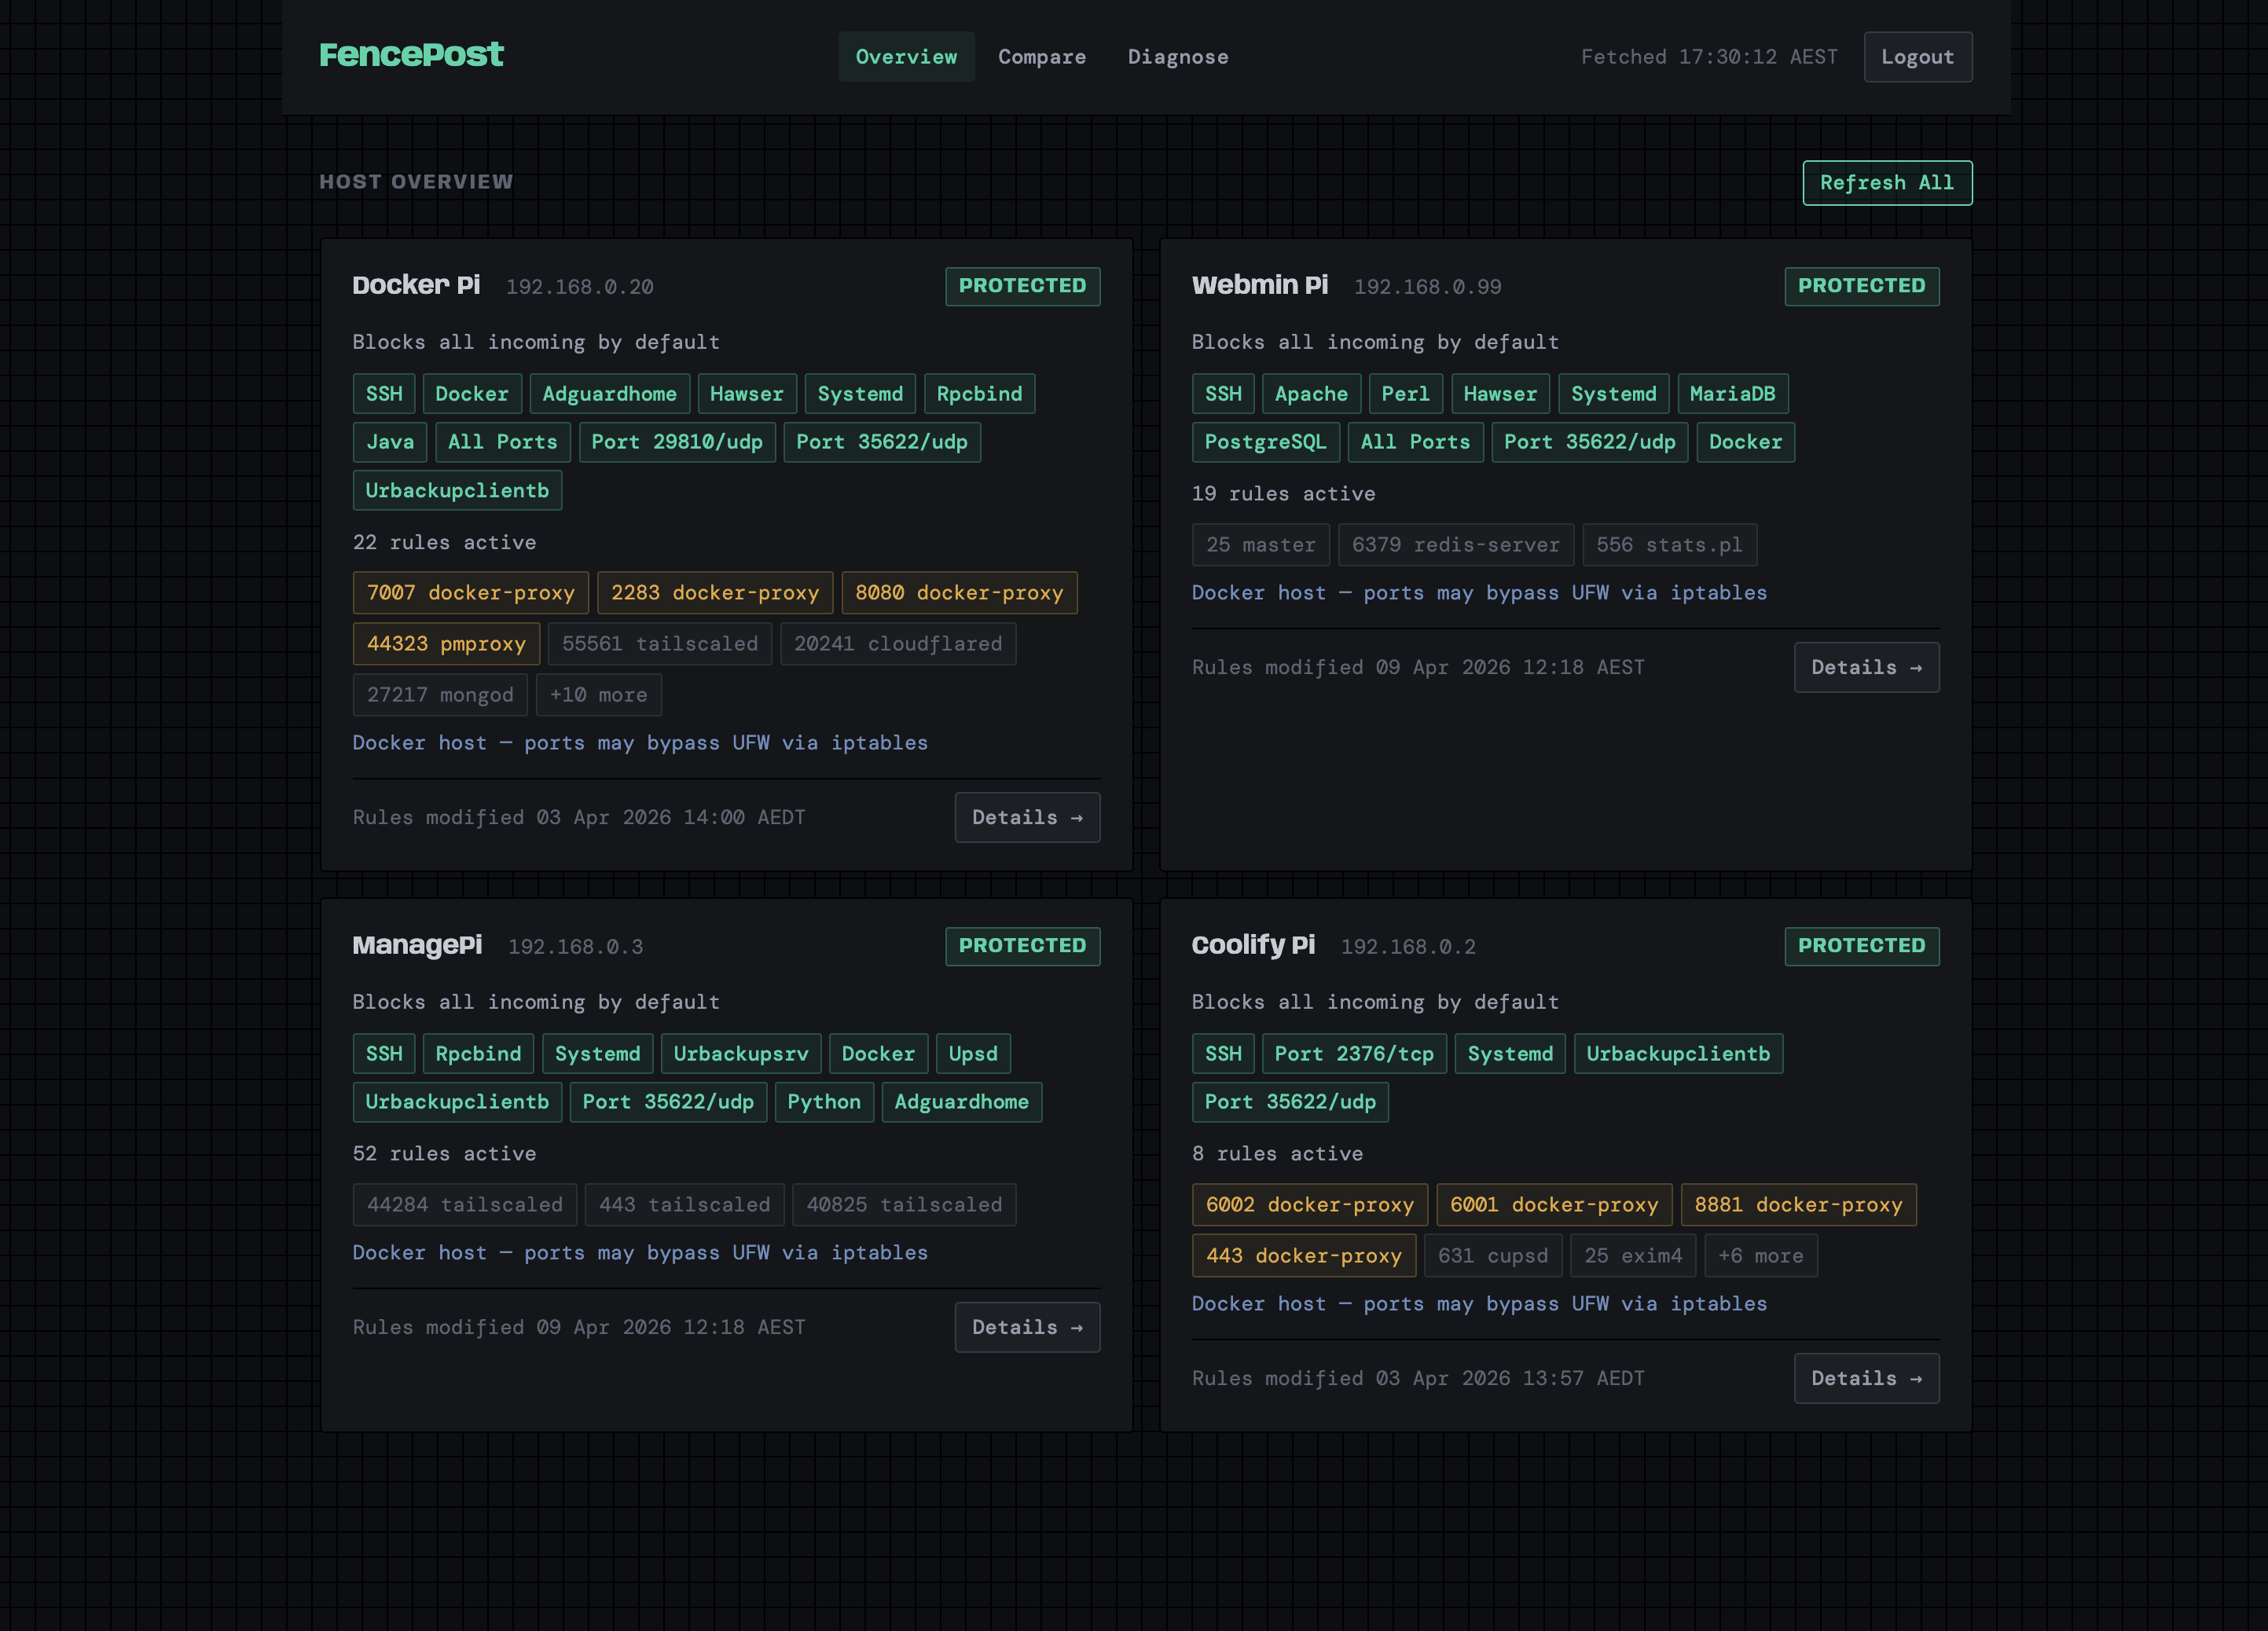 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
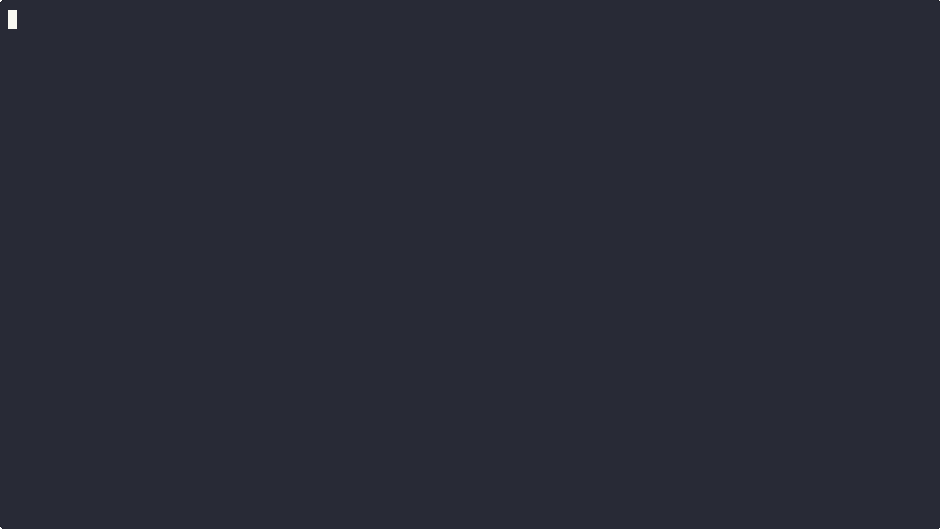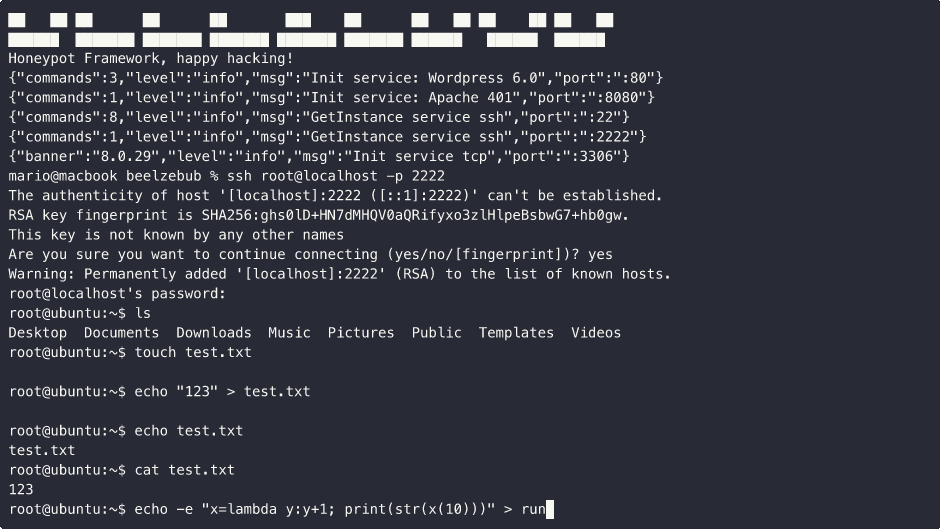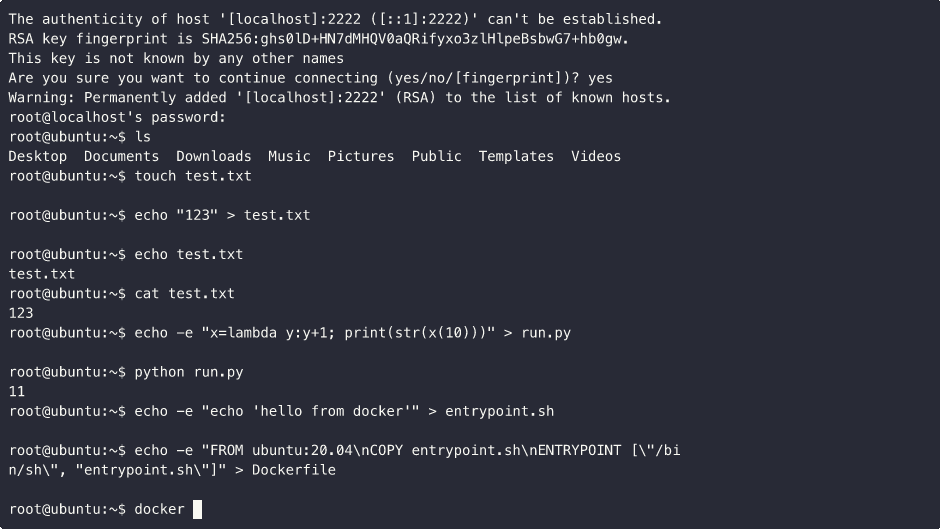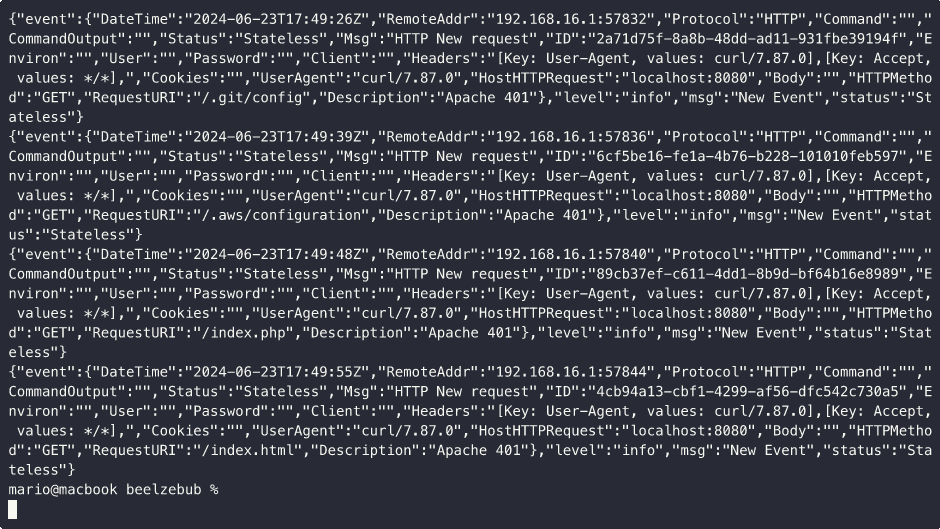 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 0x4d31/cve-2024-6387_hassh
HASSH fingerprints for identifying OpenSSH servers potentially vulnerable to CVE-2024-6387 (regreSSHion).
 secdev02/cyber-decoy
Experimental Decoy Broker
 ohmyadd/wetland
A high interaction SSH honeypot
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic