
DShield-SIEM
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
defensive-toolsincident-responseintrusion-detection+4
50
bruneaug/dshield-siemDShield Sensor Log Collection with ELK
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
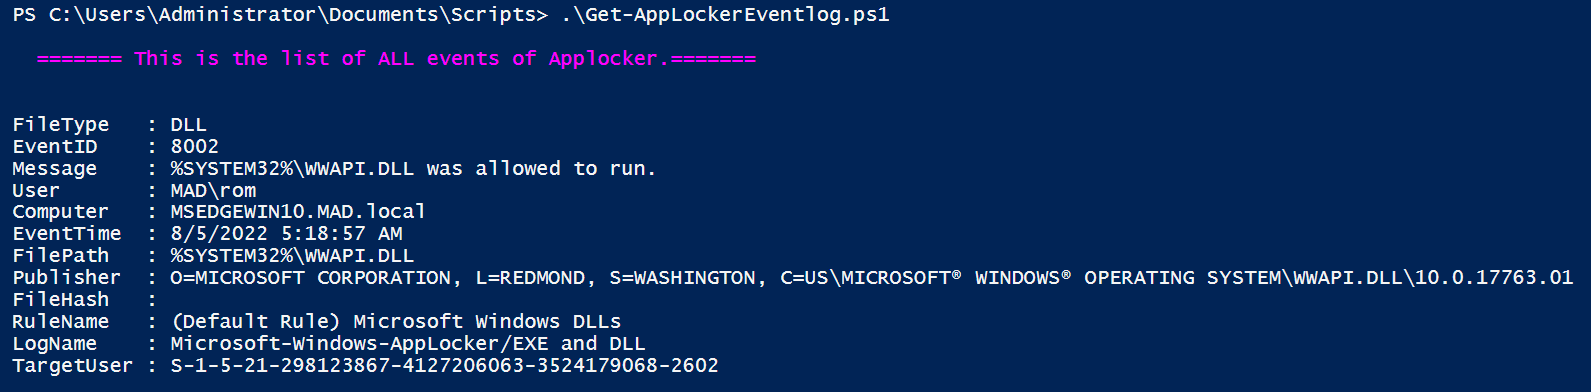 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log