
CVE-2025-39964
 suominen/cve-2025-39964
Patch-status tracker for CVE-2025-39964, a Linux AF_ALG race condition enabling local privilege escalation, recording per-distribution fix…
threat-intelligencevulnerability-analysis
suominen/cve-2025-39964Patch-status tracker for CVE-2025-39964, a Linux AF_ALG race condition enabling local privilege escalation, recording per-distribution fix…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
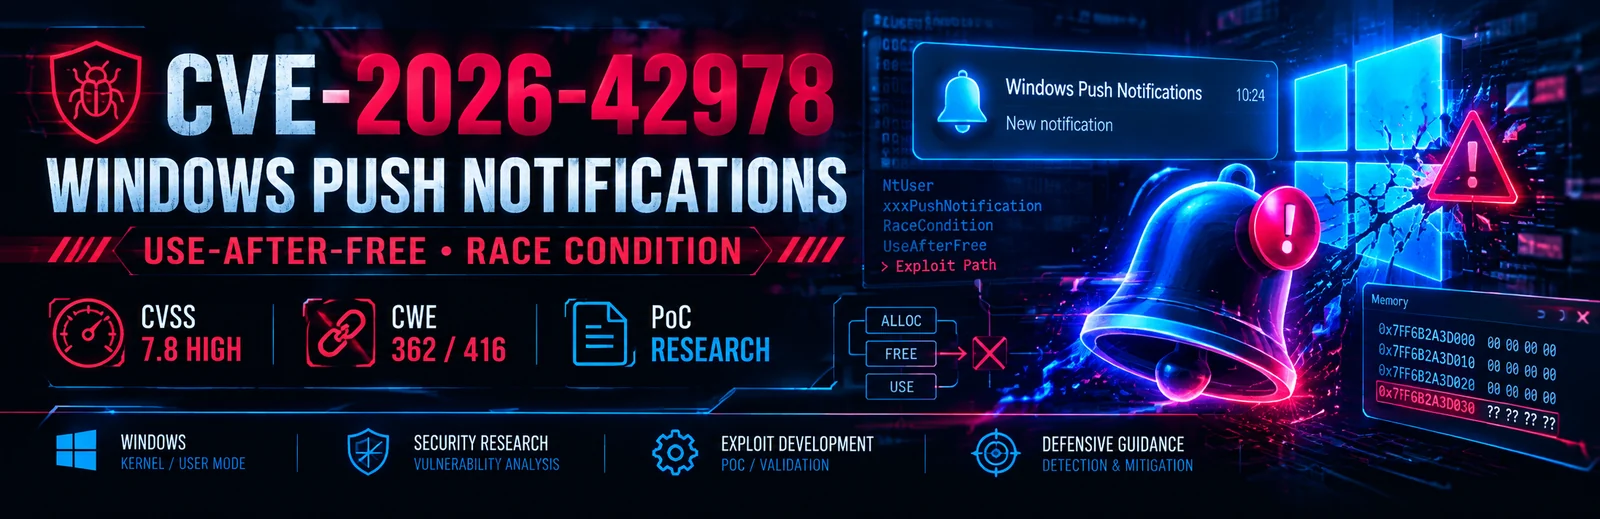 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
 lukeslp/redtail-ioc
IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
 mrk336/kernel-chaos-weaponizing-cve-2025-62215-for-system-privilege-escalation
Hands‑on analysis of CVE‑2025‑62215, a Windows Kernel race condition exploited in the wild. Demonstrates privilege escalation to SYSTEM, detection…
 zoomerxsec/fake_cve-2020-1350
Fake exploit tool, designed to rickroll users attempting to actually exploit.
 tg12/phantomstars
Automated detection and tracking of fake engagement on GitHub — daily CI, zero infrastructure
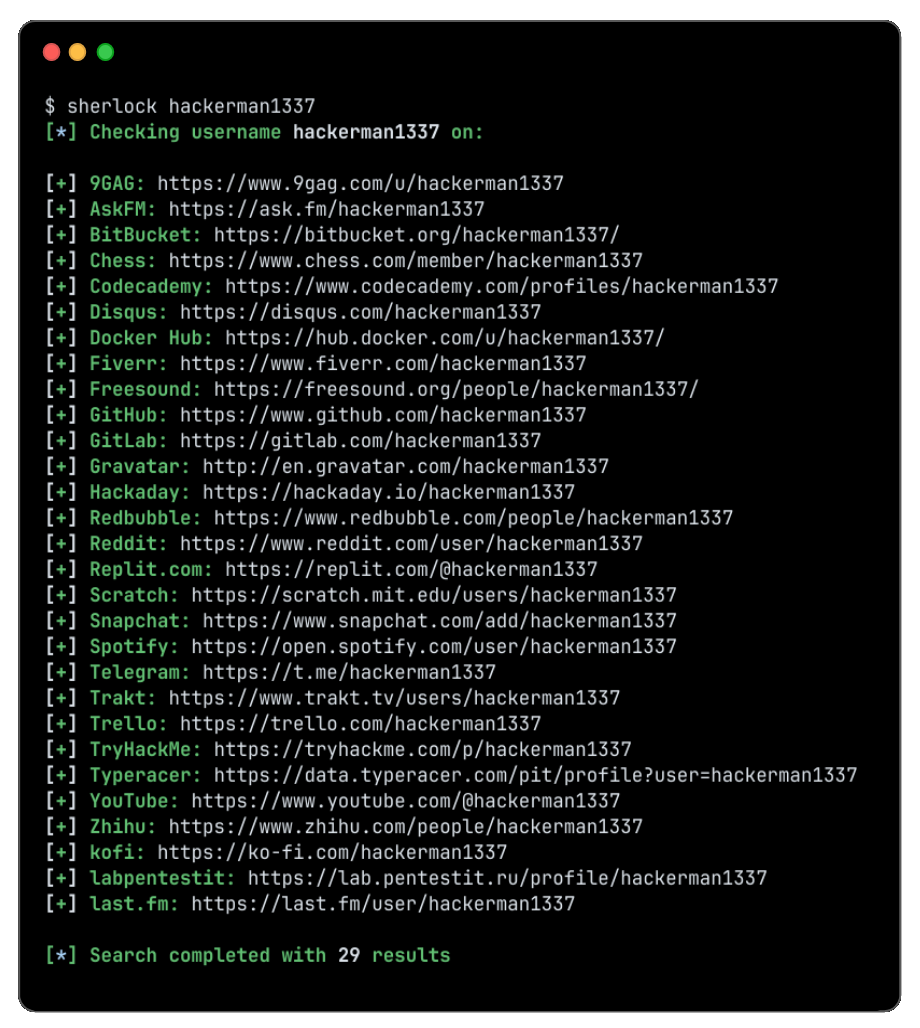 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 arch1m3d/miniplasma-detection
Sigma detection rule for MiniPlasma (CVE-2020-17103)
 adikso/minecraft-log4j-honeypot
Minecraft Honeypot for Log4j exploit. CVE-2021-44228 Log4Shell LogJam
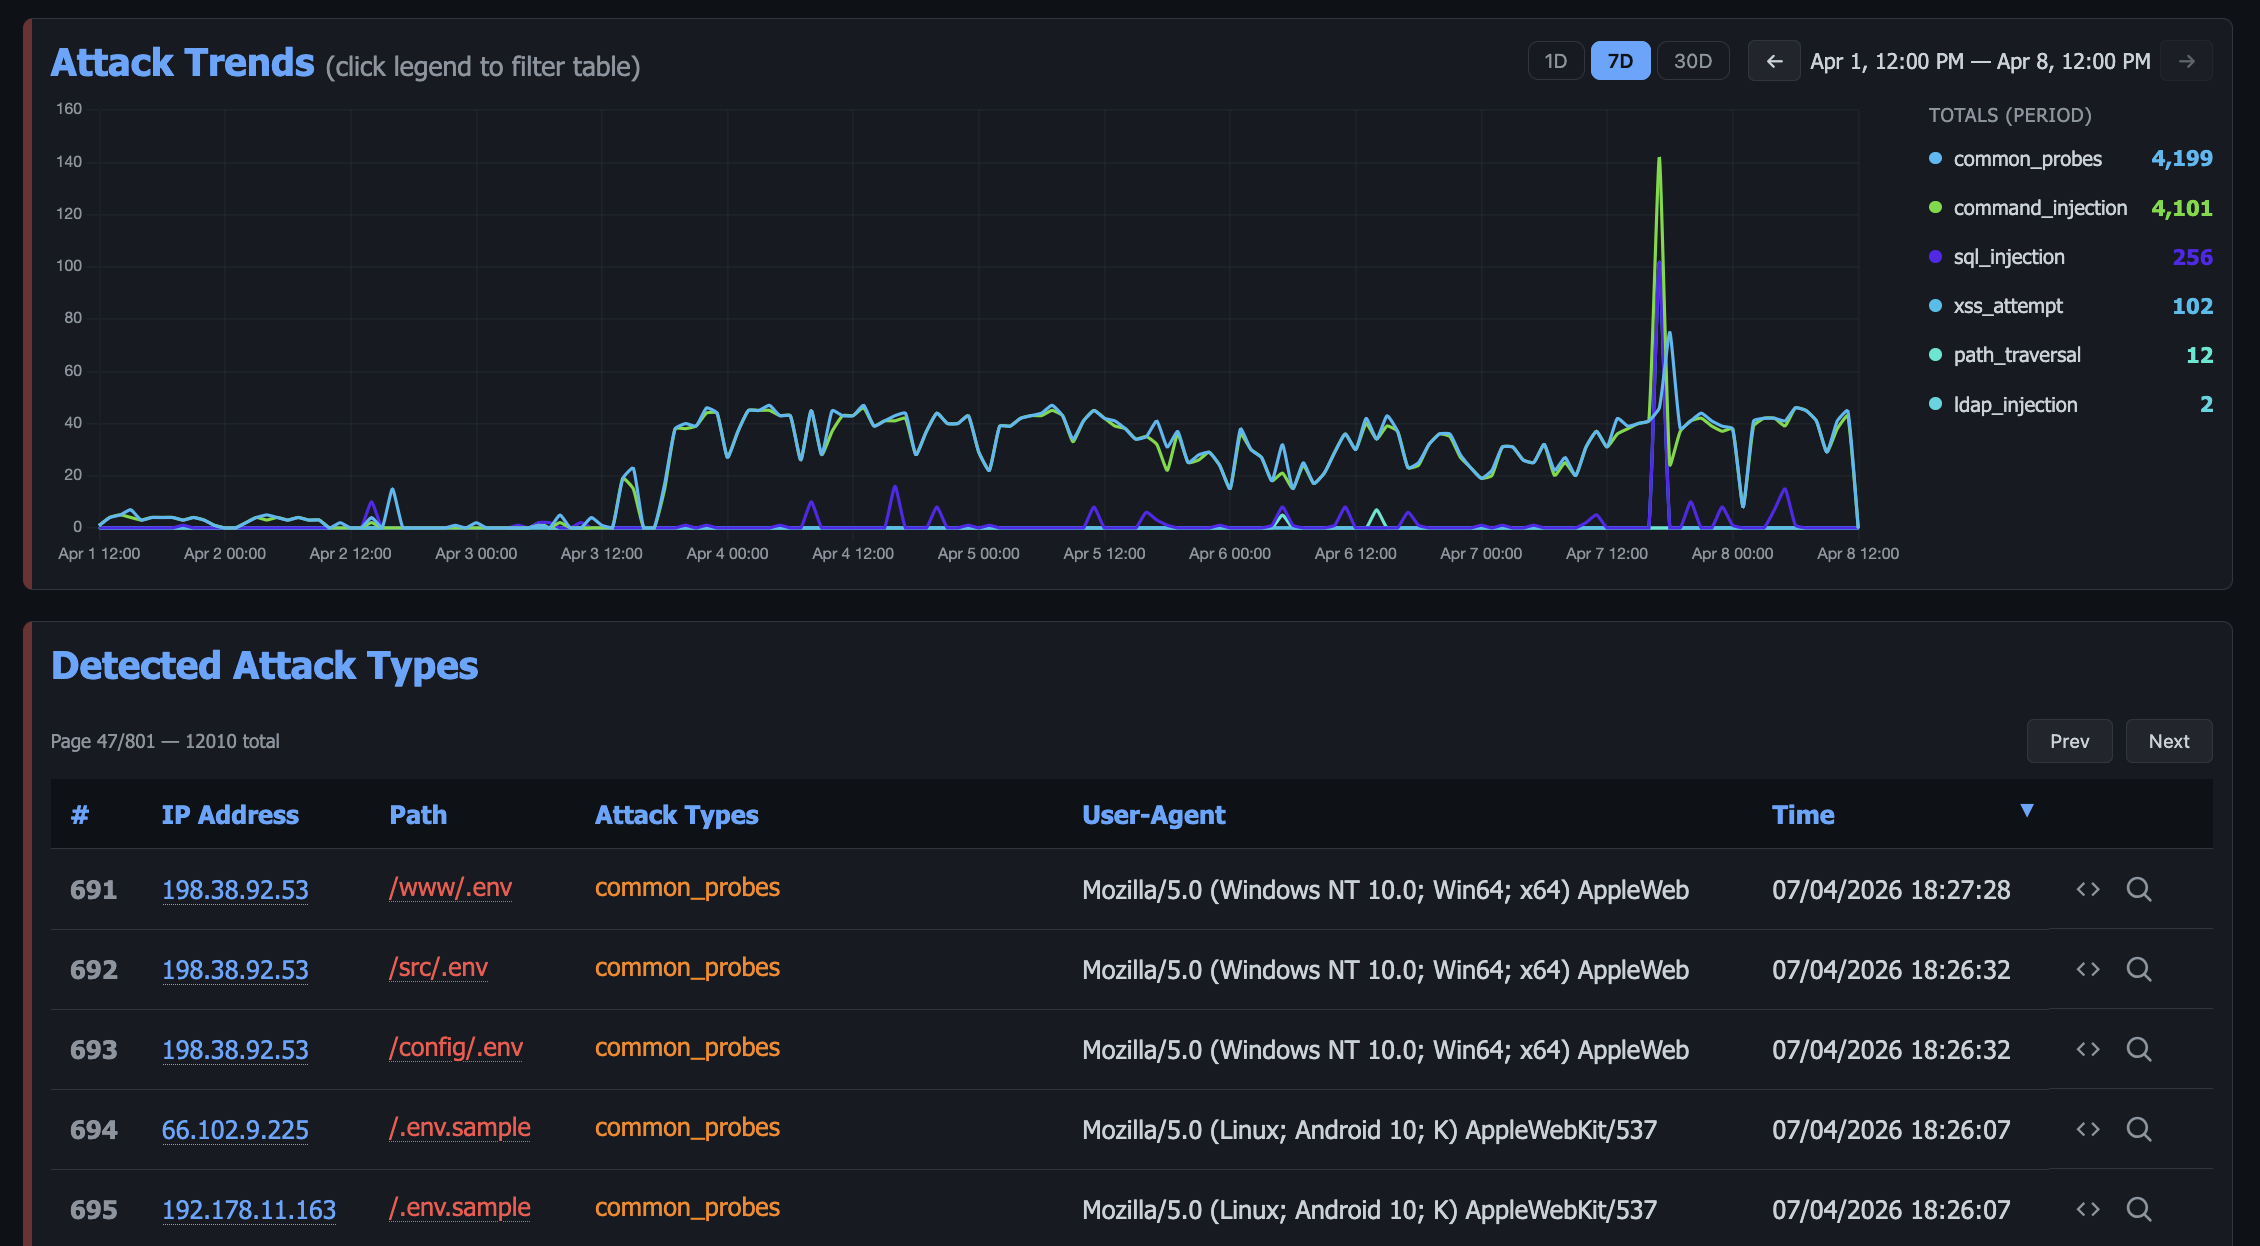 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
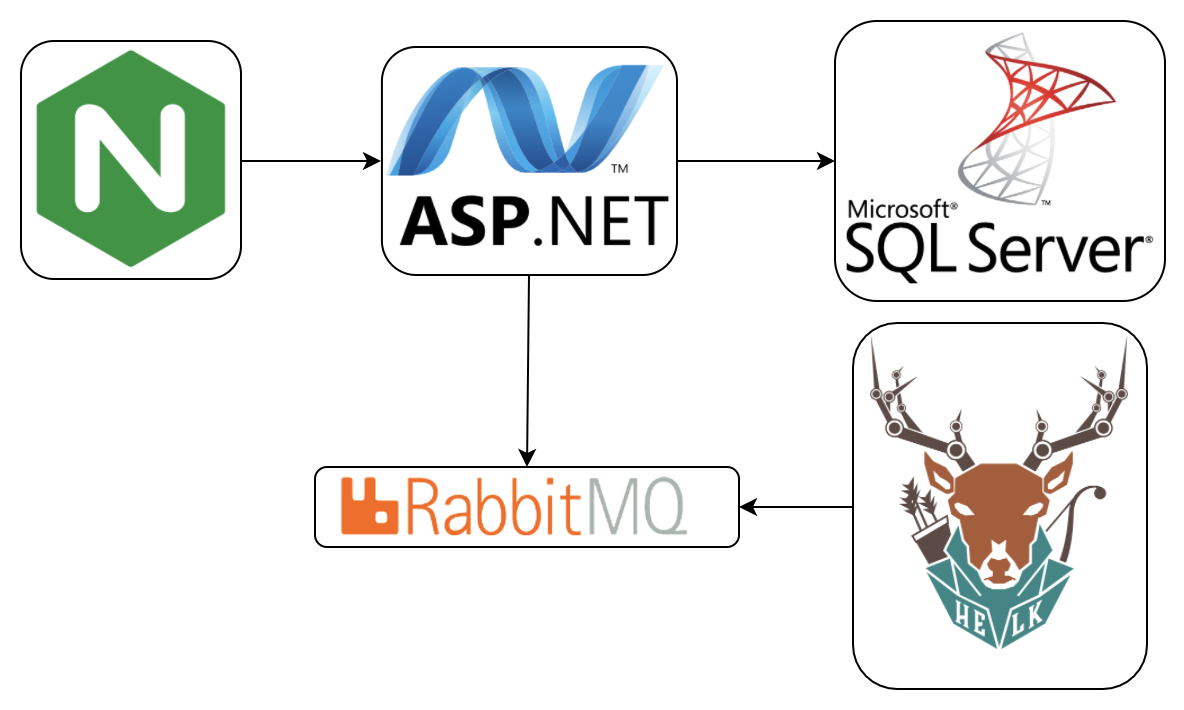 invoke-ir/ace
Automated, Collection, and Enrichment Platform
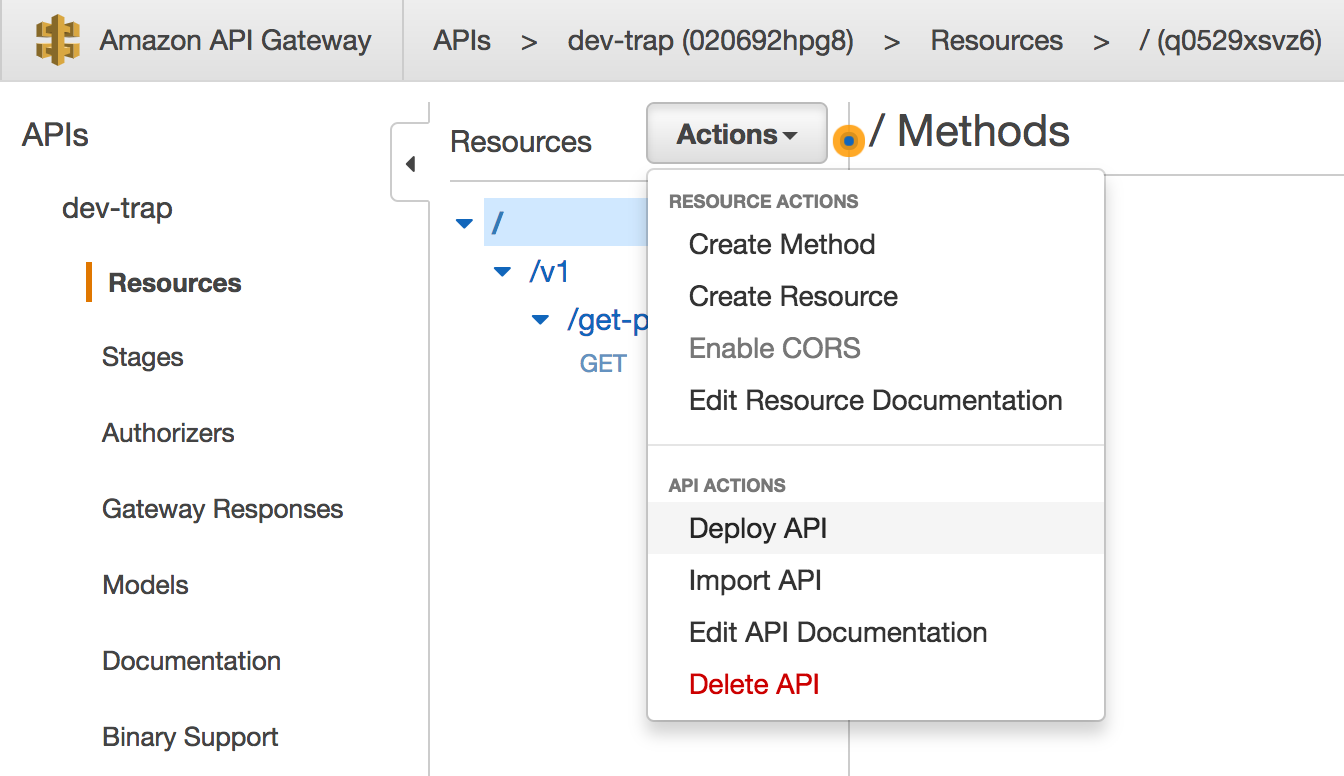 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.