

yara-rules
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
curated-resourcesdefensive-toolsincident-response+5
inquest/yara-rulesCollection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
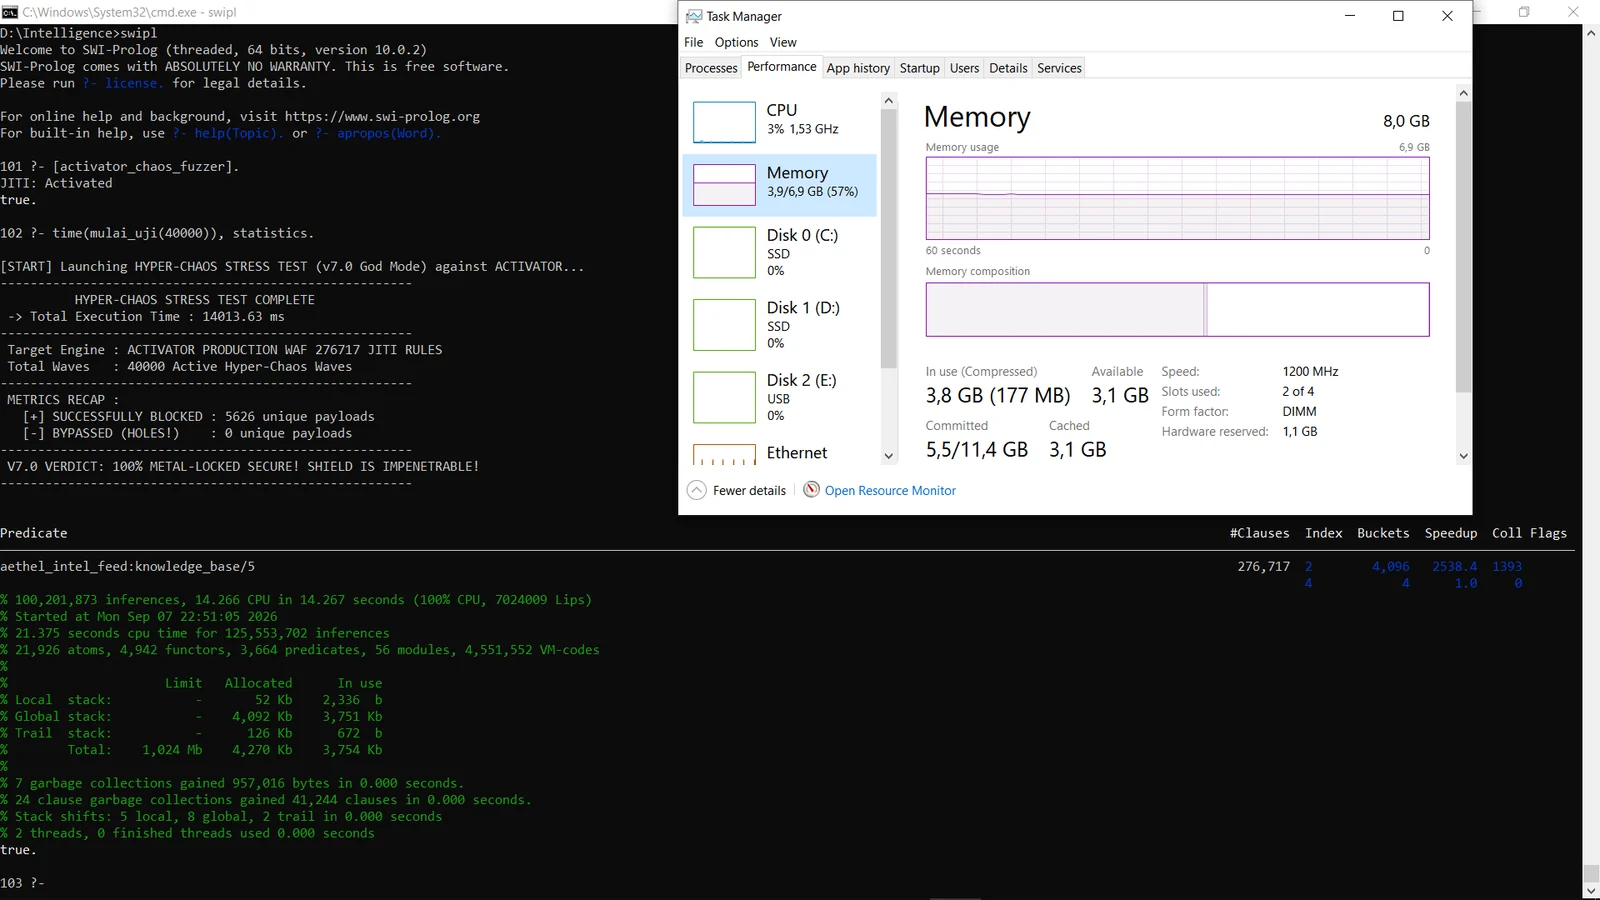 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 camgoering/solarview-ics-vulnerability-analysis
Threat model and vulnerability analysis of Contec SolarView Compact (CVE-2022-29303)
 ransomlook/ransomlook
Yet another Ransomware gang tracker
 embee-research/sigma
A repository to release detection rules to the public
 murataydemir/greyenergy-mini-module-malware-analysis
GreyEnergy Mini Module Malware Analysis (Turkish)
 google/security-research
This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
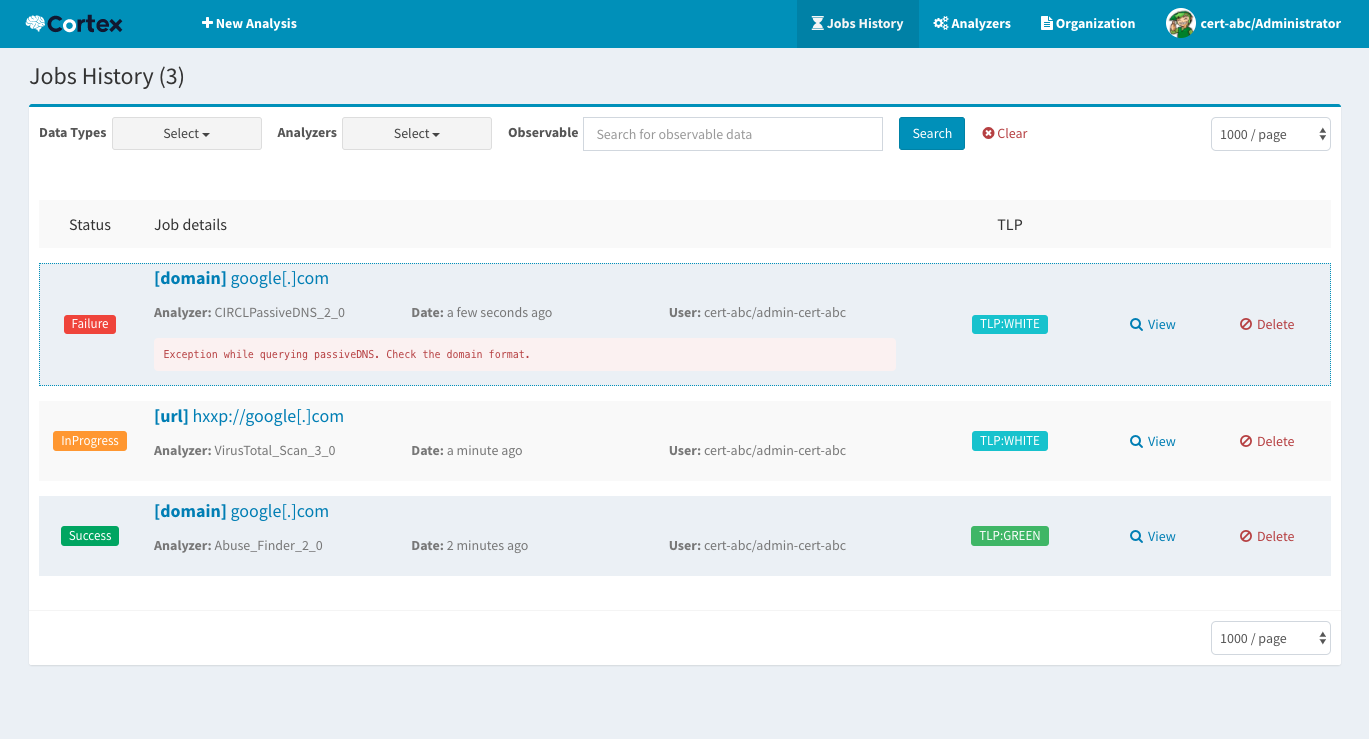 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 owasp/german-owasp-day
German OWASP Day conference site & presentation archive
 hasherezade/bunitu_tests
Scripts for communication with Bunitu Trojan C&Cs
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 opendns/dataviz
OpenDNS Data Visualization Framework