

dshield
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
defensive-toolsincident-responseinformation-gathering+5
536
dshield-isc/dshieldInstalls and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
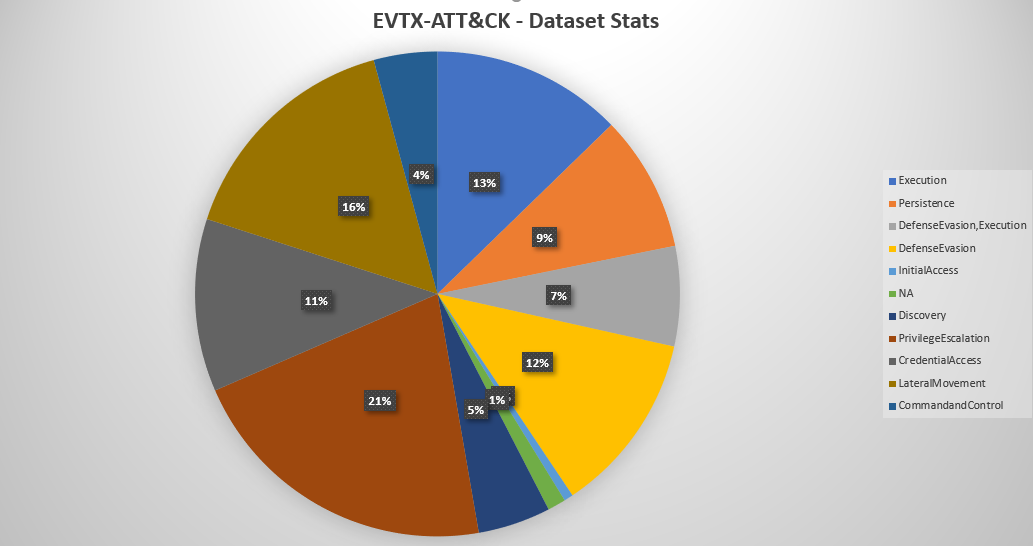 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 rxerium/rxerium-templates
Nuclei scripts created by @rxerium for zero days / actively exploited vulnerabilities.
 staaldraad/fastfluxanalysis
Scripts to detect Fast-Flux and DGA using DNS query responses
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
 shanelawrence/cve_manager
A collection of python apps and shell scripts to email an xlsx spreadsheet of new vulnerabilities in the NIST CVE database and their associated…
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.