ndaal_public_SBOM_Auditor

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

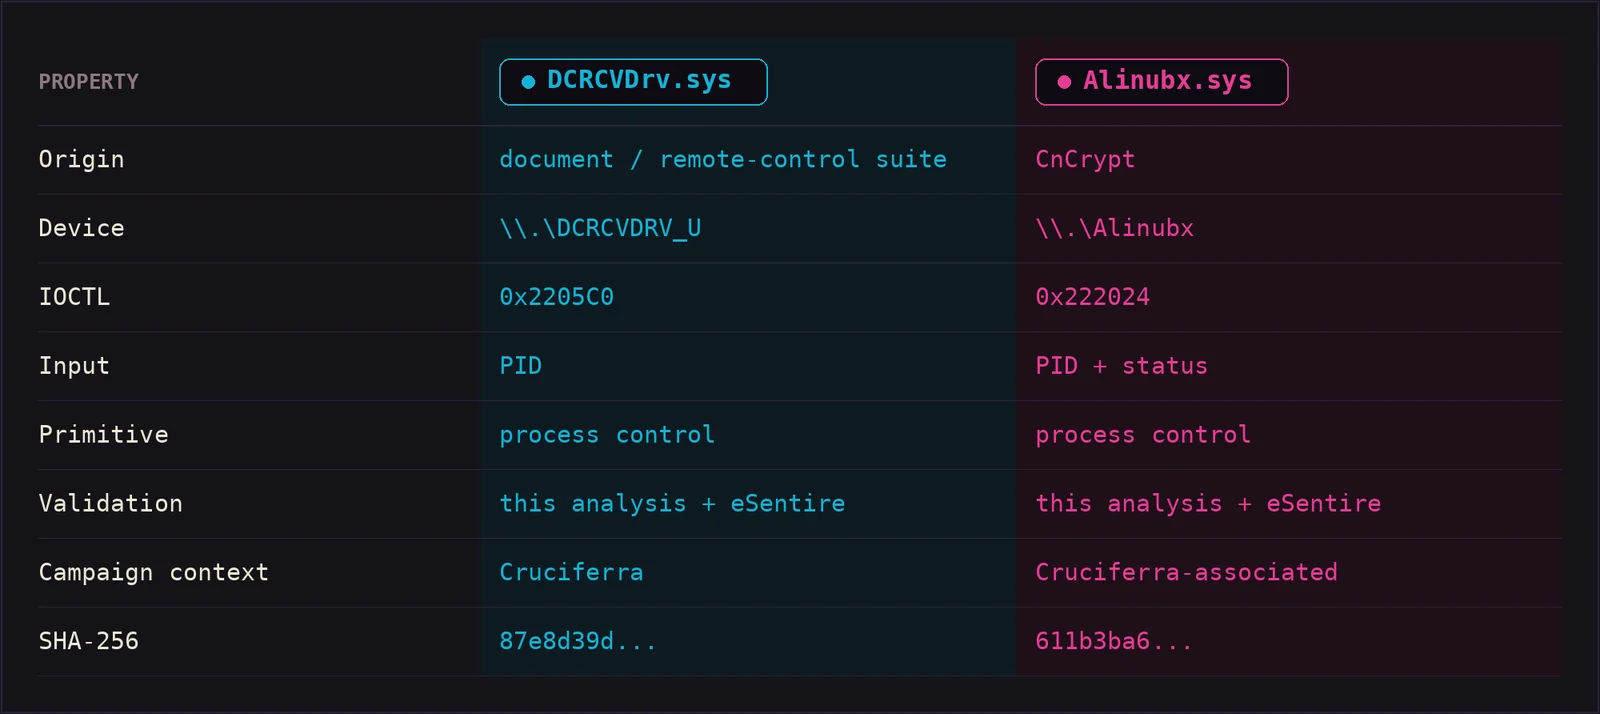
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.

SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…

Threat intelligence brief on CVE-2026-42208, a critical pre-auth SQL injection in BerriAI LiteLLM exploited within 36 hours of disclosure. Covers…

Searchable page for CISA Log4j (CVE-2021-44228) Affected Vendor & Software List

Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.

Provides rapid triage and summarization of malware samples and threat indicators, highlighting key behavioral and contextual details for analysts.

Collection of extracted Microsoft Defender data for security research purposes

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck

Daily collection of malicious samples originating from Vietnam for malware analysis, threat intelligence, and detection engineering research.


Interesting APT Report Collection And Some Special IOCs

Strelka Web UI for File Submission and Analysis

Just a git repo for the sleepmask detection rule i found in https://codex-7.gitbook.io/codexs-terminal-window/blue-team/detecting-cobalt-strike/sleep-…

Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…

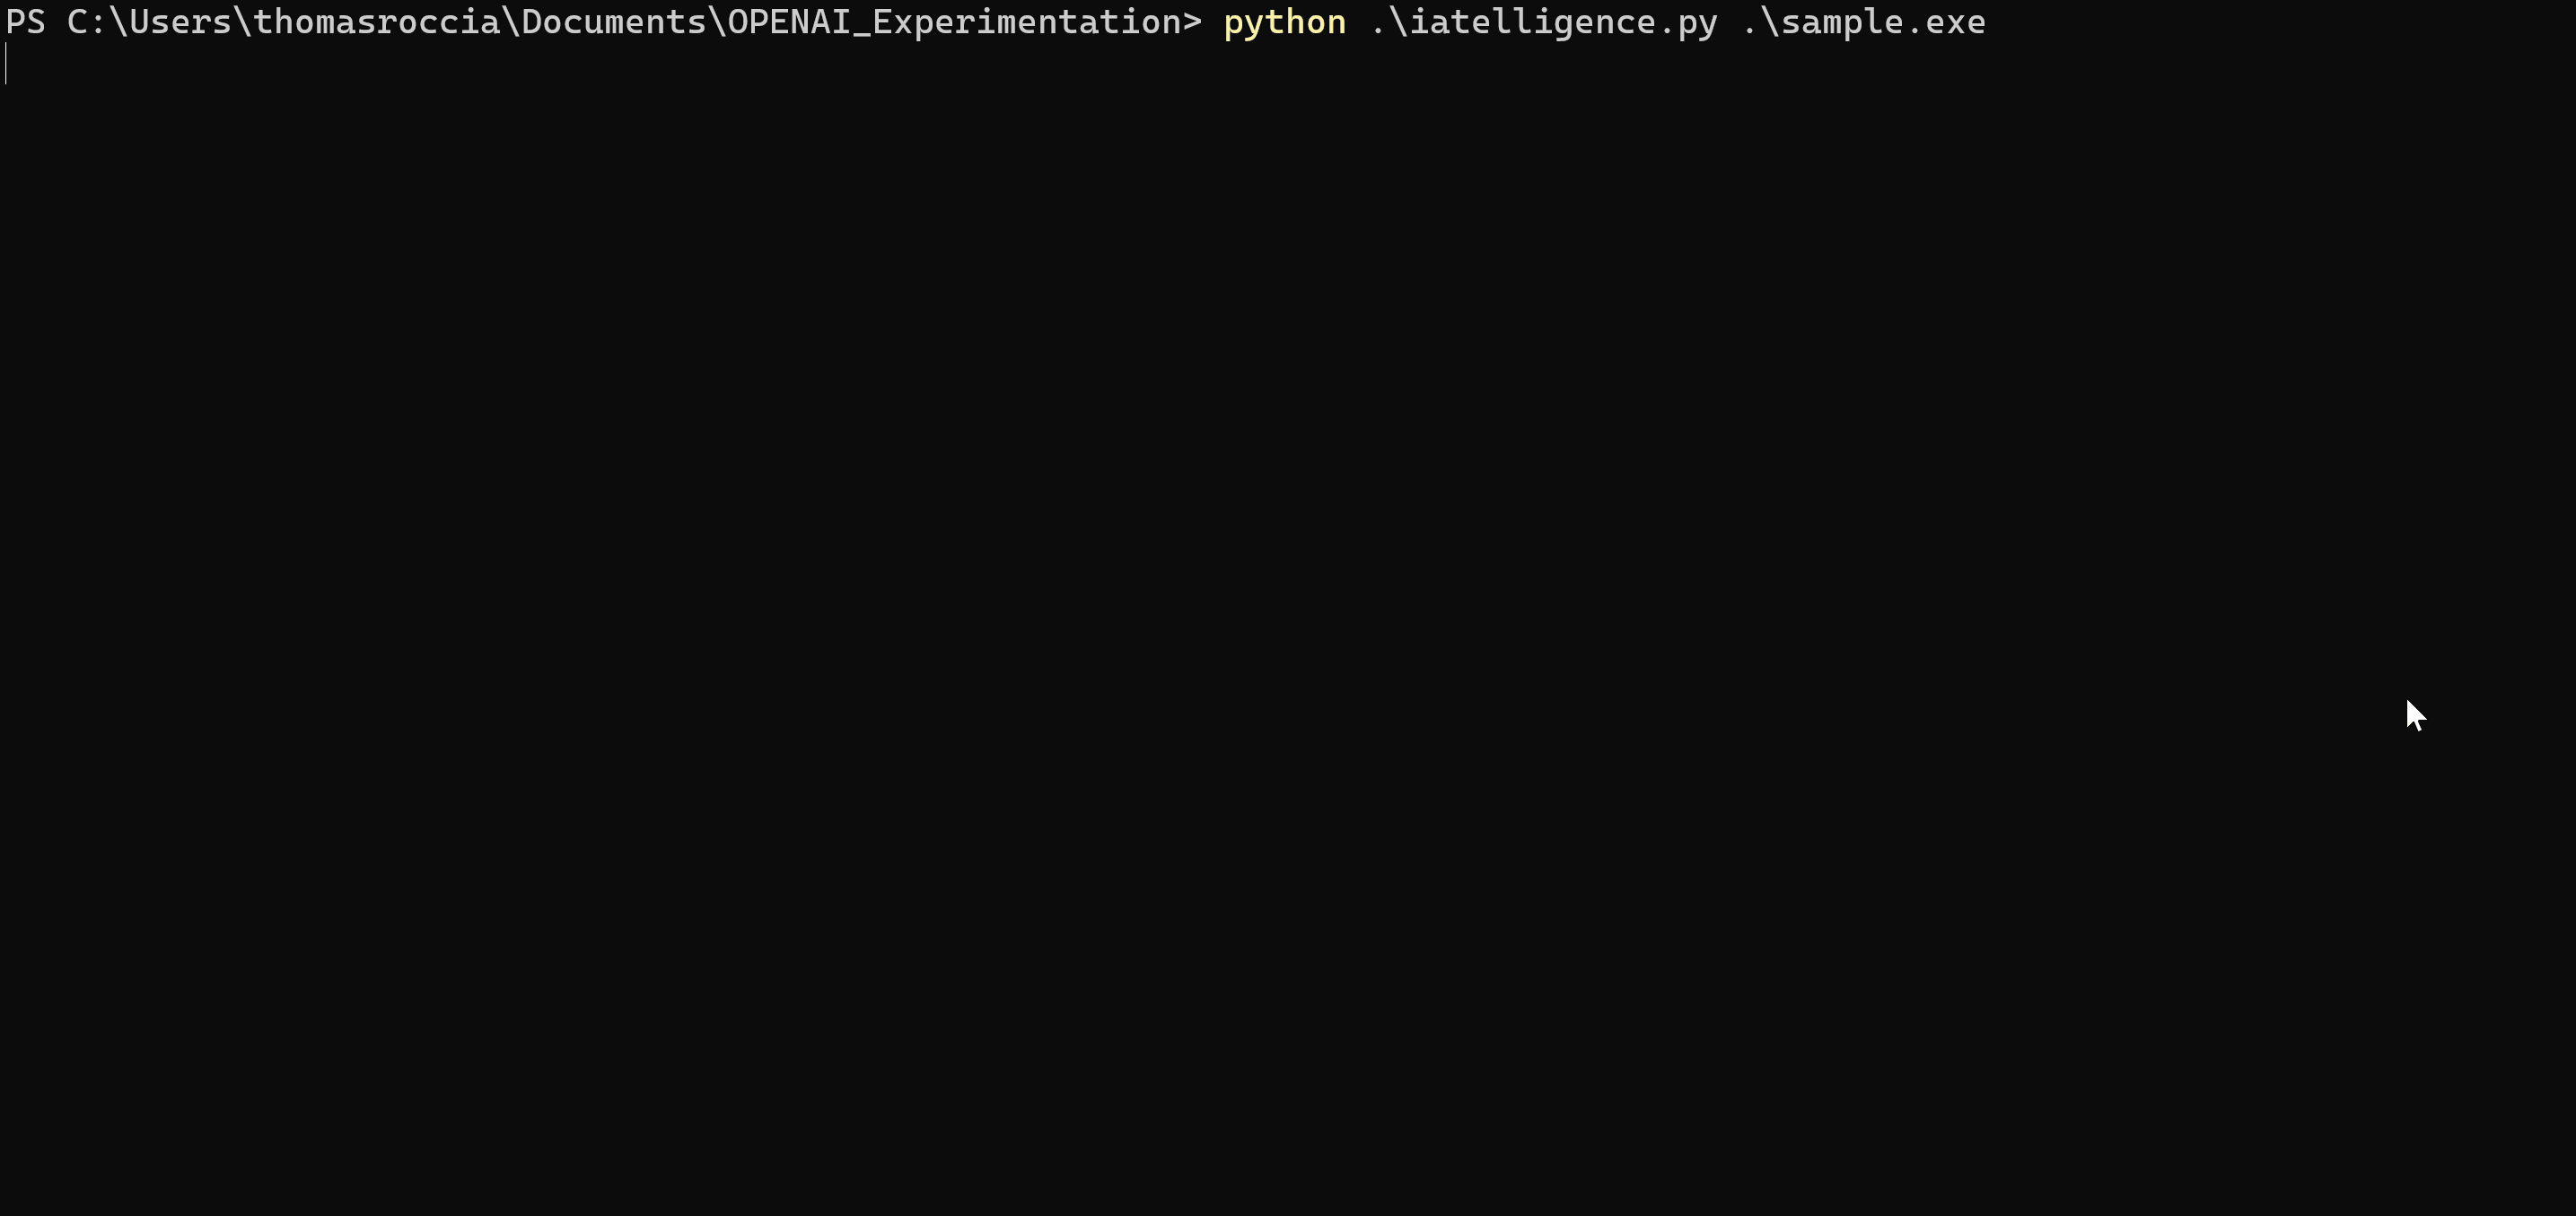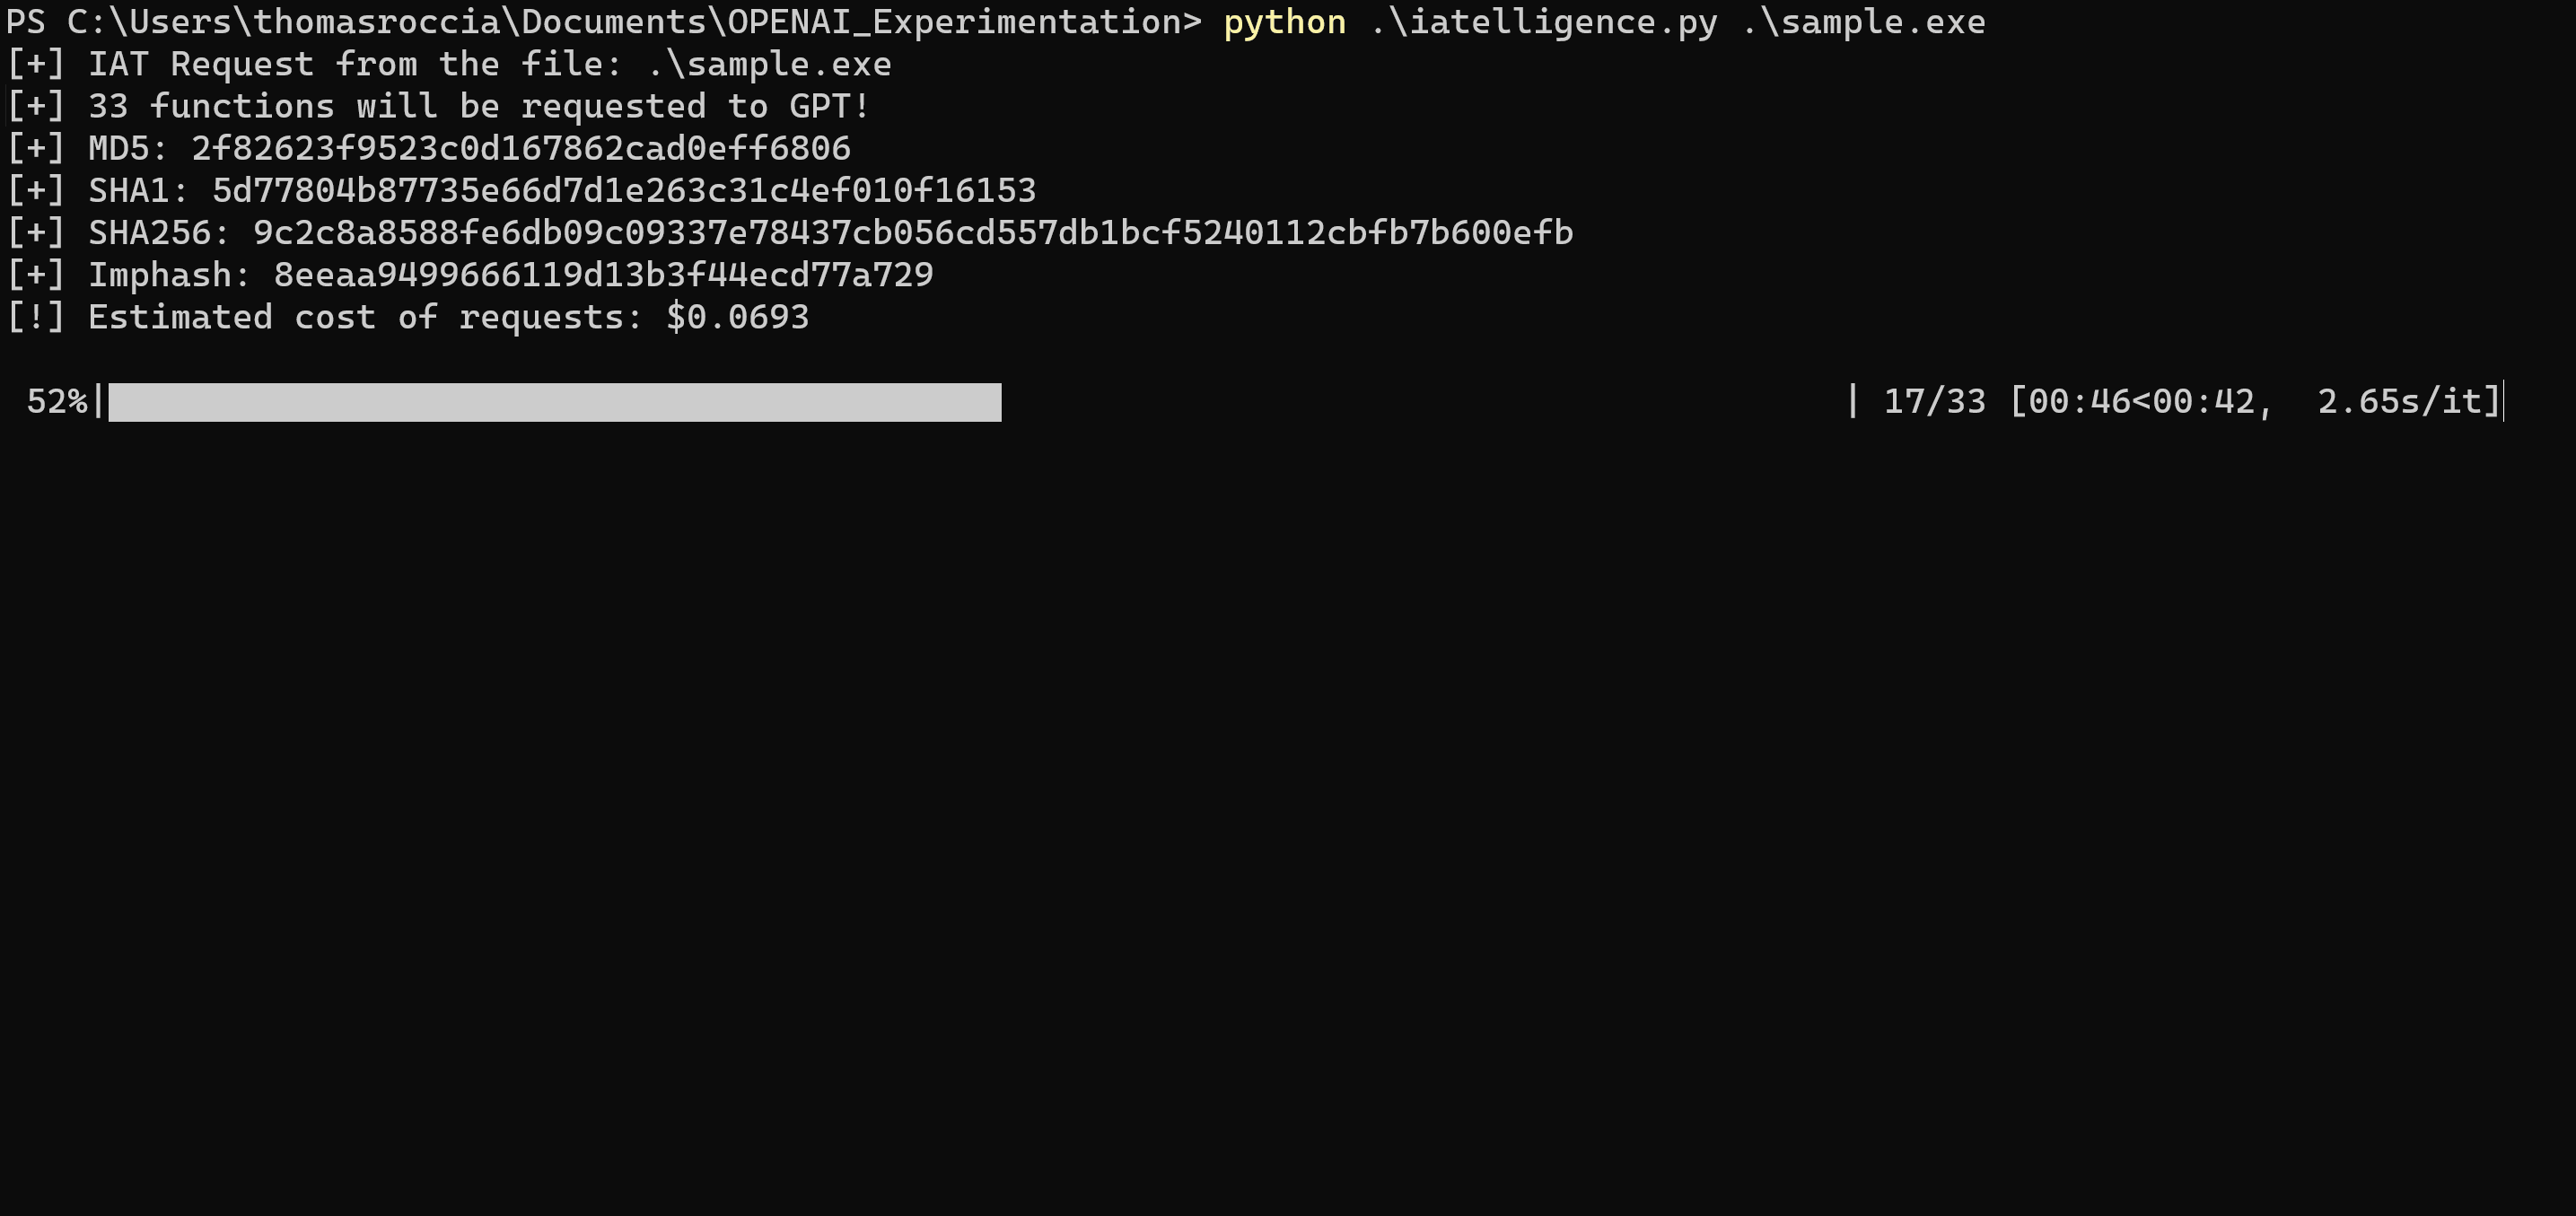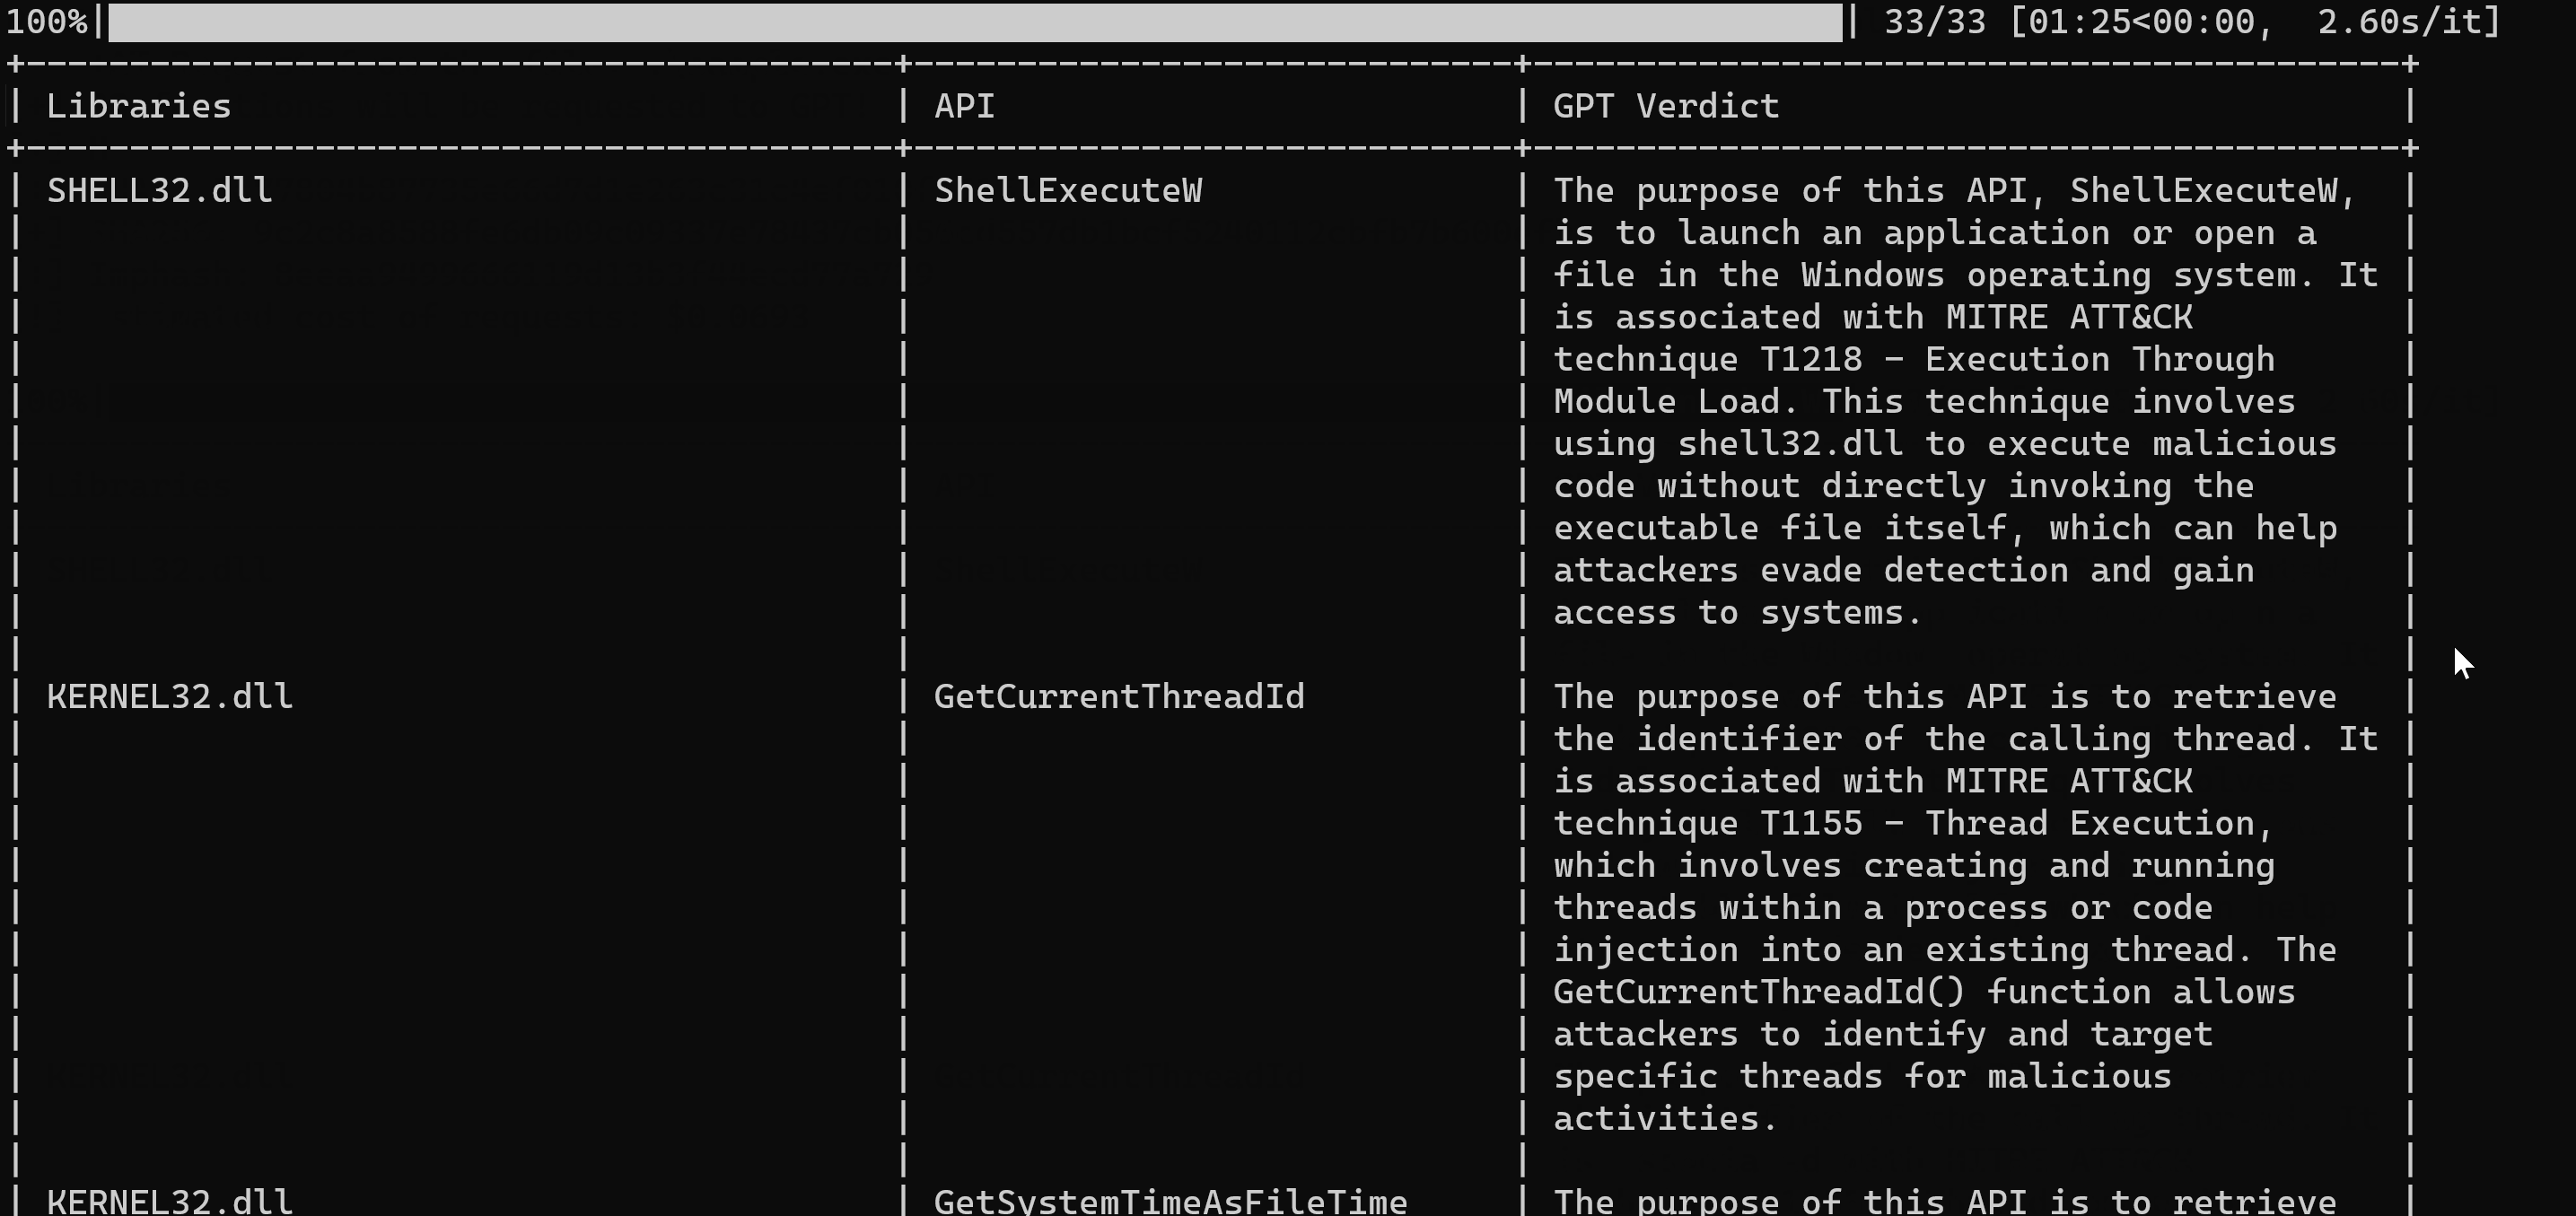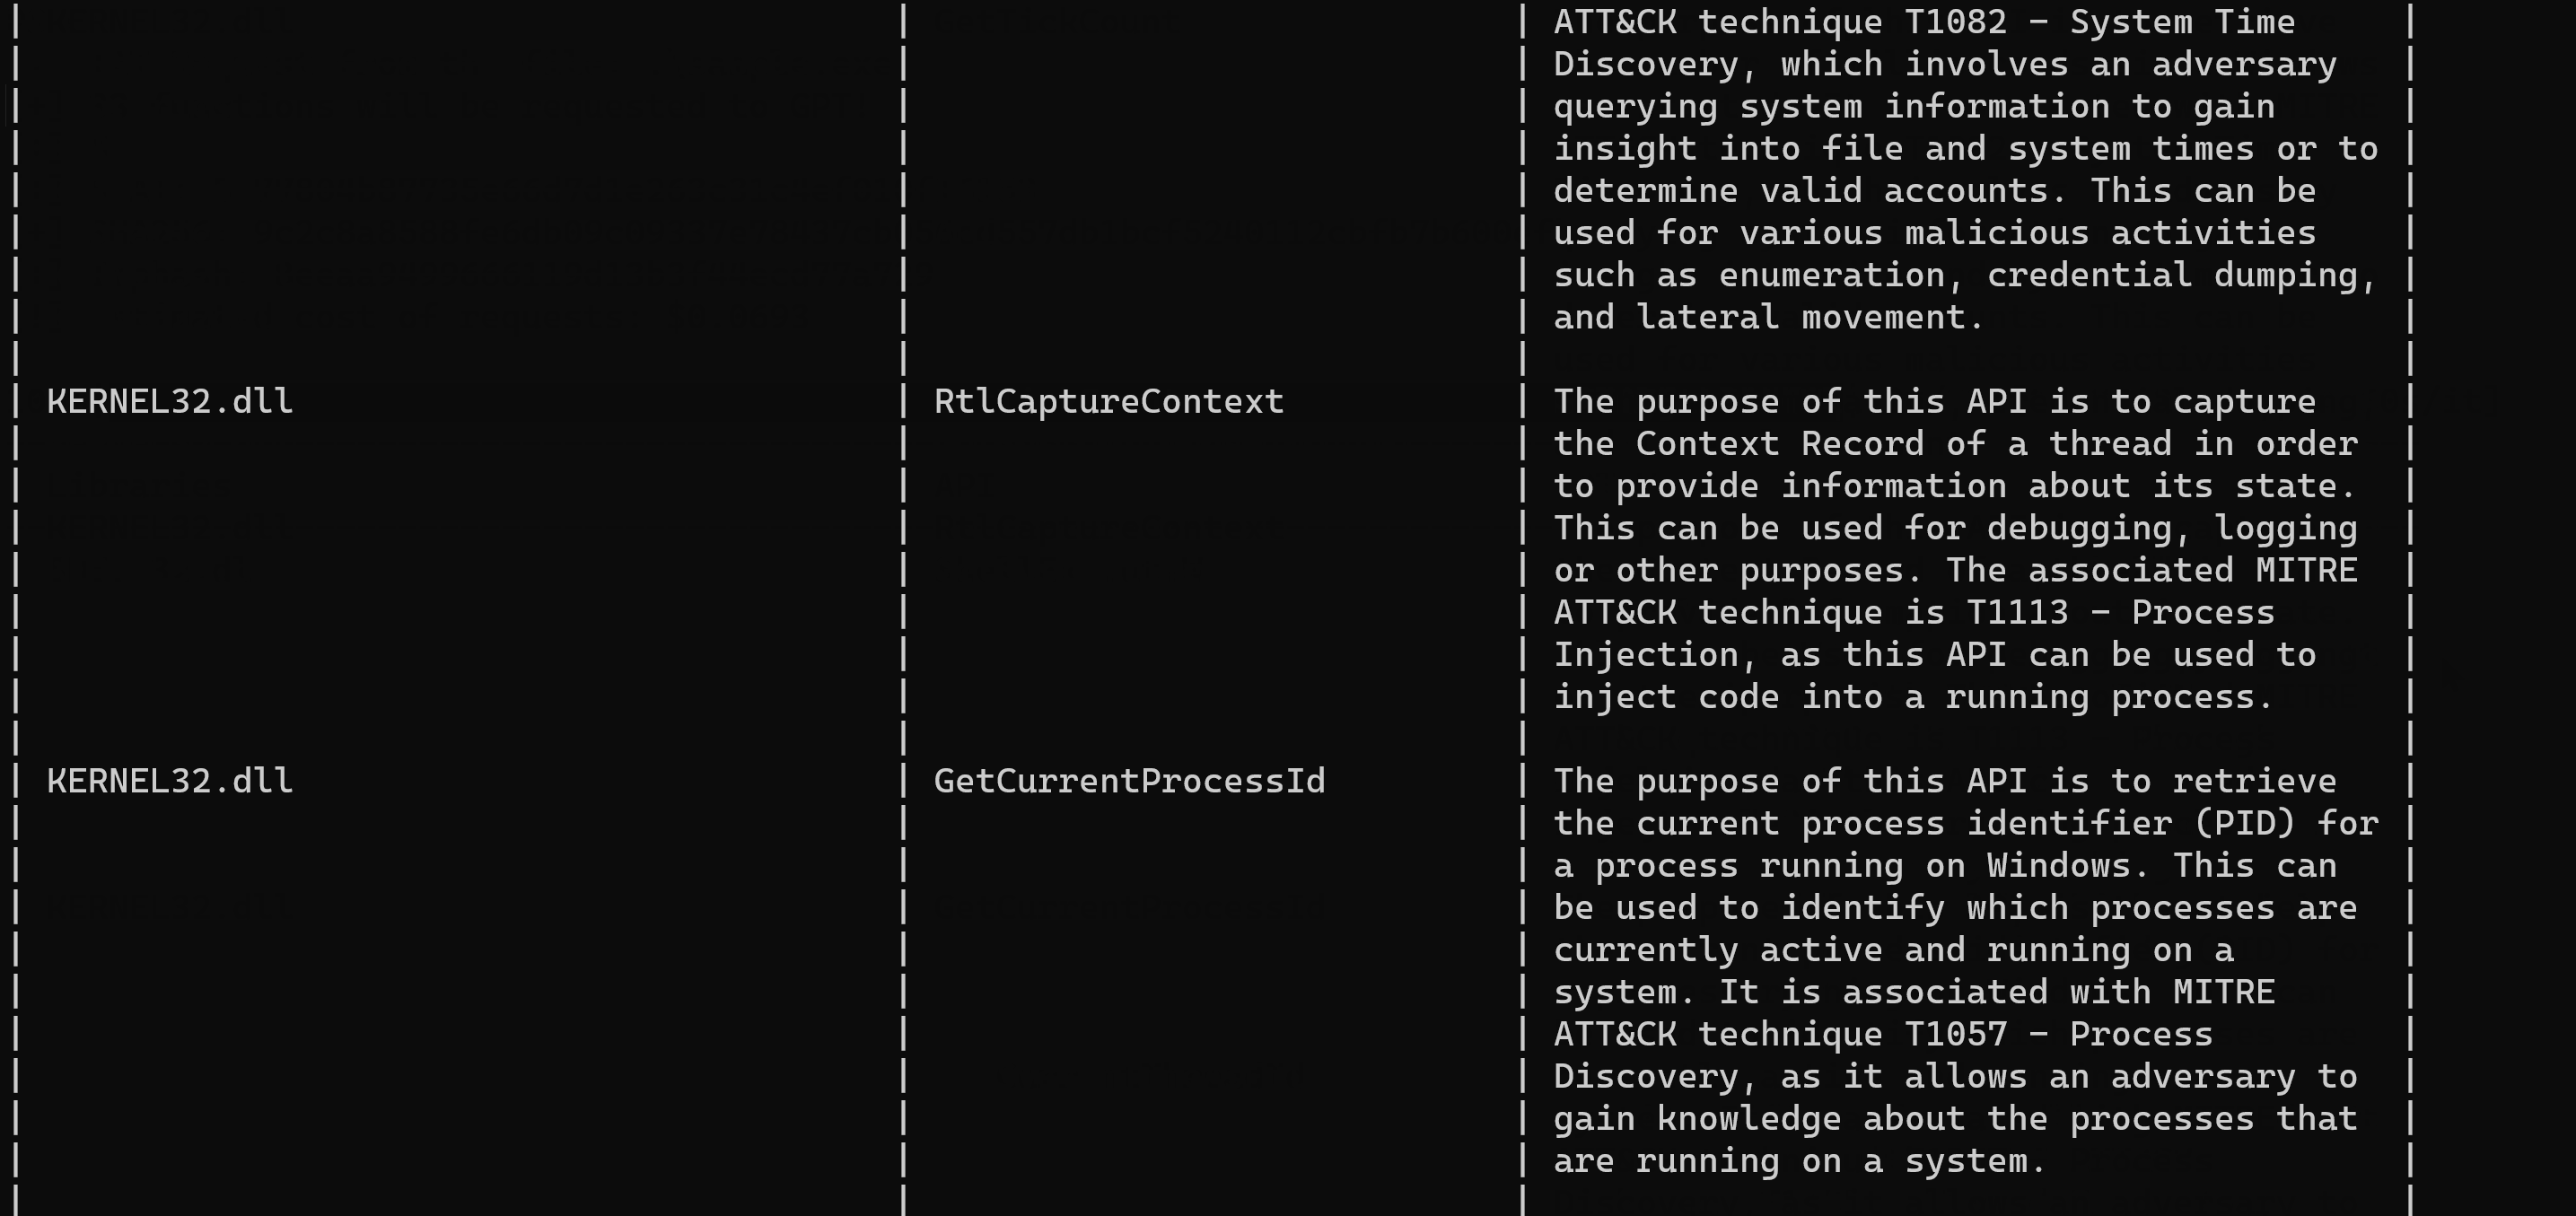
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…