

c2detect
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
command-and-controldefensive-toolsfingerprint-spoofing+8
43
cognis-digital/c2detectC2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 google/osv.dev
Open source vulnerability DB and triage service.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
 google/security-research
This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
 utkusen/jeopardize
a low(zero) cost threat intelligence&response tool against phishing domains
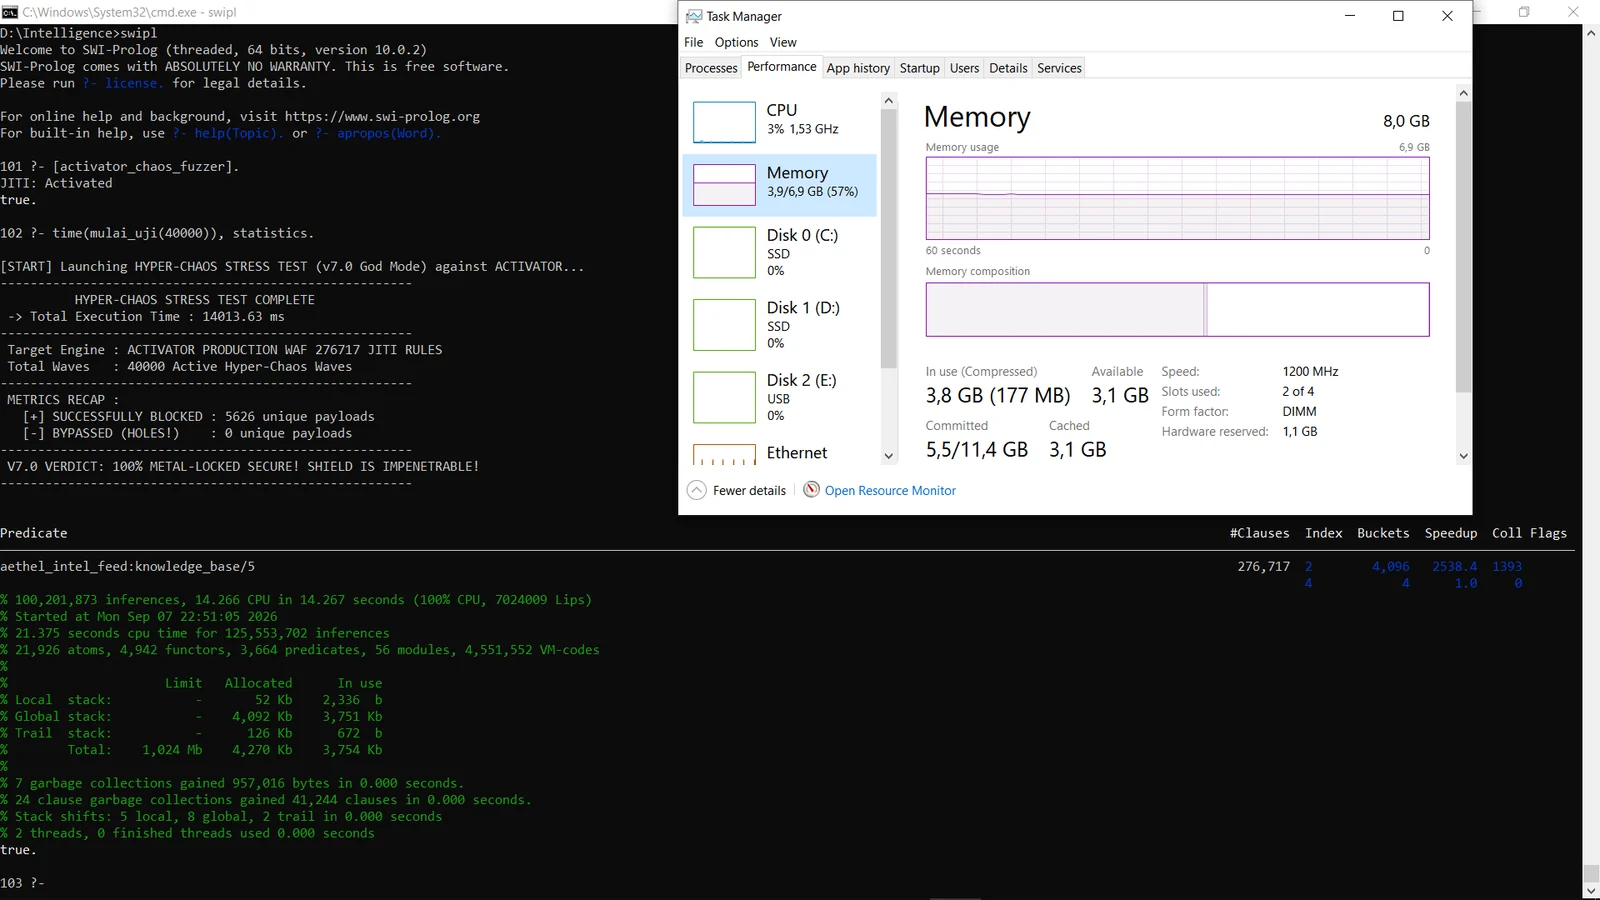 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 ransomlook/ransomlook
Yet another Ransomware gang tracker
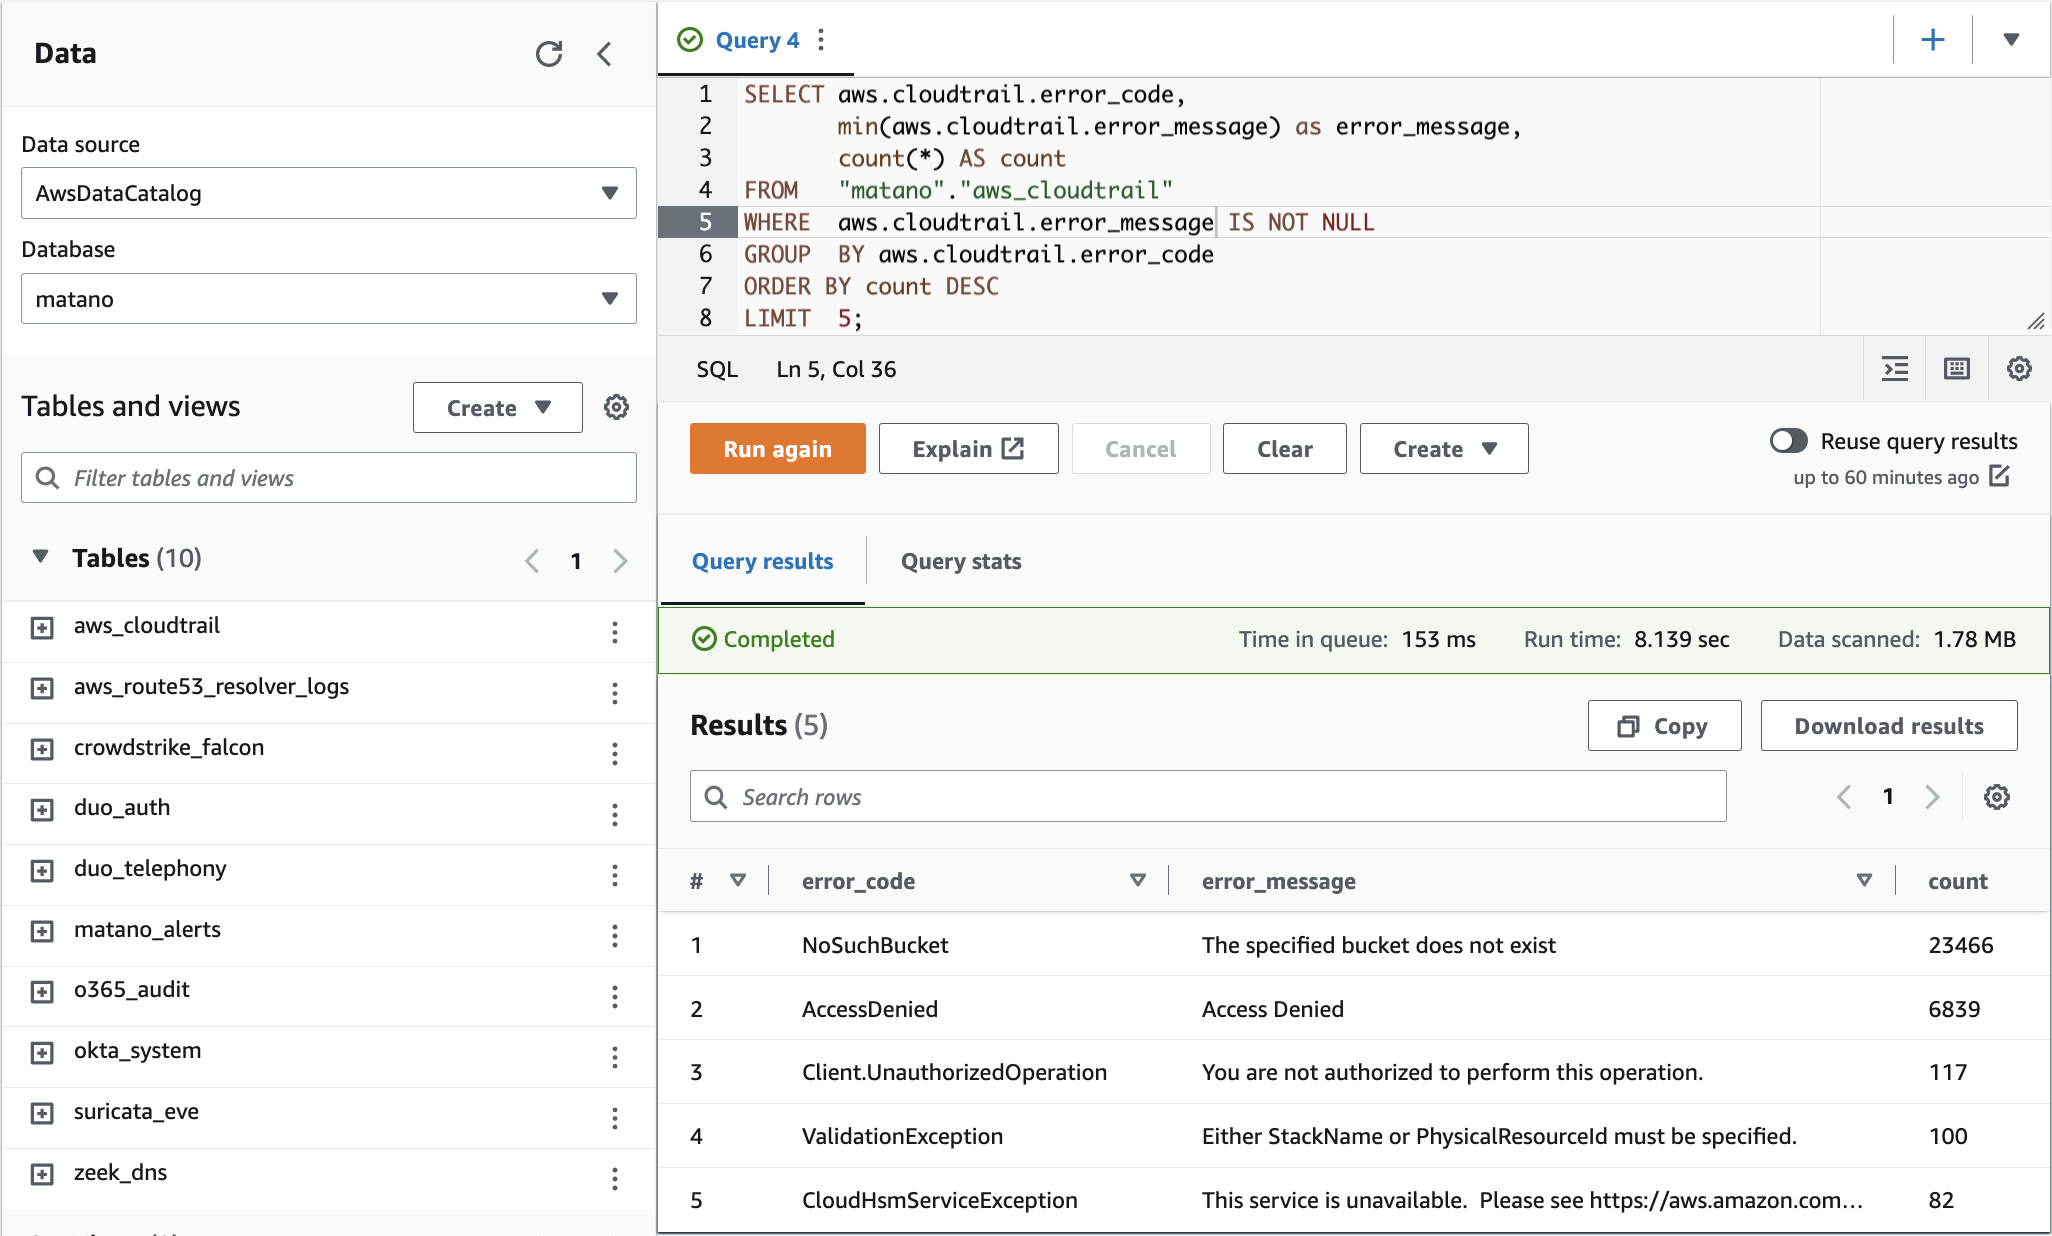 matanolabs/matano
Open source security data lake for threat hunting, detection & response, and cybersecurity analytics at petabyte scale on AWS
 camgoering/solarview-ics-vulnerability-analysis
Threat model and vulnerability analysis of Contec SolarView Compact (CVE-2022-29303)
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay